
 Global Security Orchestration Market | 2026-2036
Global Security Orchestration Market Size, Share, and Industry Trends Forecast 2026-2036
Global Security Orchestration Market Foresight
Platform bundling is restructuring buyer choice in security orchestration, as vendors merge SOAR capabilities with broader XDR and SIEM suites to reduce integration overhead. Palo Alto Networks leverages its platform breadth to anchor enterprise accounts seeking consolidated threat response. Cisco Systems, Inc. competes through native network telemetry integration that extends orchestration into switch and firewall infrastructure. Swimlane specializes in low-code automation workflows that differentiate its offering for mid-market security teams with limited engineering resources.
Security orchestration denotes the automated coordination of disparate security tools, threat intelligence feeds, and response workflows through standardized APIs and playbooks, enabling sub-minute containment actions across endpoint, network, and identity layers. The technology serves to collapse mean-time-to-response in security operations centers burdened by alert fatigue and tool sprawl. Incident Response and Automation & Orchestration solution types command the largest deployment bases, reflecting maturity in playbook-driven remediation. Cloud-Based deployment models are expanding fastest as organizations migrate security operations to elastic infrastructure, though Hybrid configurations retain margin strength in regulated sectors requiring data sovereignty controls.
The EU AI Act, NIS2 Directive, and GDPR collectively shape European procurement by mandating documented incident response timelines and cross-border threat notification protocols that only orchestrated platforms can reliably satisfy. In the United States, HIPAA, SEC cybersecurity disclosure rules, and FAA directives for aviation infrastructure create overlapping compliance obligations that drive standardization around FedRAMP-authorized orchestration stacks. Stakeholders must weigh whether to consolidate on single-vendor platforms or preserve multi-vendor interoperability as regulatory jurisdictions proliferate divergent automation audit requirements.
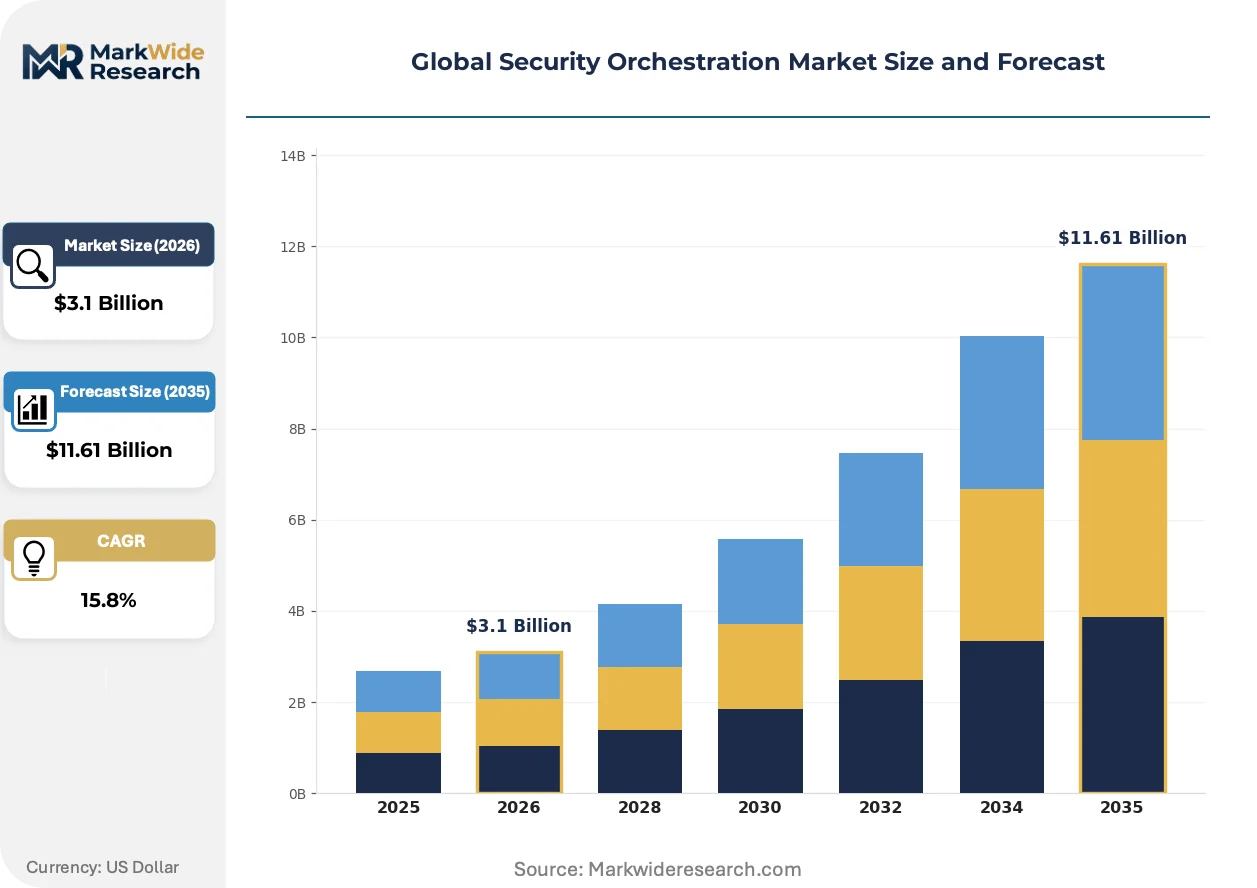
Market Dynamics
Platform consolidation is compressing vendor margins as buyers reject point solutions in favor of unified security stacks that collapse integration tax and staffing overhead. The EU AI Act and NIS2 Directive are accelerating this consolidation by mandating auditable response workflows that only integrated orchestration platforms can deliver.
Growth Catalysts
- Federal cybersecurity mandates:United States agencies and critical infrastructure operators face binding incident response timelines under SEC disclosure rules and FAA directives, forcing standardized orchestration procurement.
- Cloud migration elasticity:Financial services institutions are shifting security operations to cloud-based deployment models to achieve variable cost scaling during peak threat periods.
- Alert fatigue remediation:SOC teams drowning in false-positive volumes are driving demand for playbook-driven automation that filters noise before human analyst review.
Market Restraints
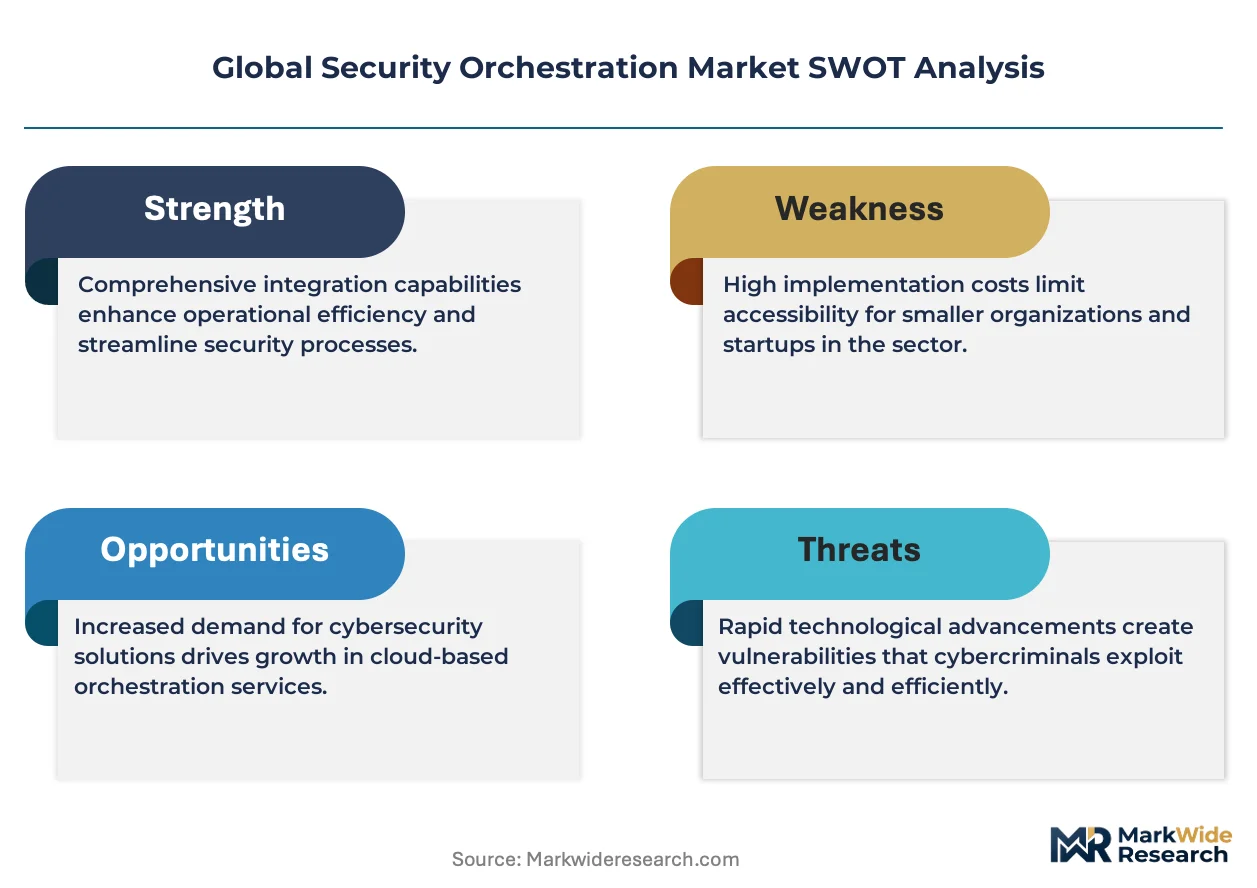
- Legacy SIEM sunk costs:Enterprises with multi-year Splunk or IBM QRadar contracts face contractual penalties and data migration complexity that delay orchestration platform switches.
- API standardization gaps:Proprietary vendor APIs fragment interoperability, forcing buyers to maintain expensive custom integration engineering for niche security tools.
- Skilled orchestration engineer scarcity:The talent pool for Python-based playbook development and SOAR architecture design remains concentrated in technology hubs, inflating implementation costs.
Strategic Opportunities
- Mid-market penetration:United States healthcare providers and municipal governments below enterprise scale represent underserved demand for low-code automation that reduces engineering dependency.
- XDR-SOAR convergence:Extended detection and response platforms are absorbing orchestration capabilities, creating white space for vendors that natively unify threat detection with response automation.
- GDPR Article 33 compliance:European enterprises face 72-hour breach notification mandates that only orchestrated platforms with pre-mapped response workflows can reliably satisfy.
Industry Challenges
- Multi-cloud configuration drift:Security teams struggle to maintain consistent orchestration playbooks across AWS, Azure, and Google Cloud environments with diverging native security APIs.
- Threat intelligence feed quality variance:SOC automation depends on high-fidelity indicator feeds, yet commercial threat intelligence providers deliver inconsistent context that corrupts automated blocking decisions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Security Orchestration Market |
| Market Size in 2026 | $3.1 Billion |
| Market Size in 2035 | $11.61 Billion |
| CAGR (2026 – 2036) | 15.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Incident Response, Threat Intelligence, Automation & Orchestration, Vulnerability Management, Compliance Management Deployment Model: Cloud-Based, On-Premises, Hybrid, Managed Services Application: Cybersecurity Monitoring, Risk Assessment, Security Analytics, Network Defense, Endpoint Protection, Identity Management End User Industry: Telecommunications, Manufacturing, Energy & Utilities, Government & Defense, Education |
| Companies Covered | IBM Corporation, Palo Alto Networks, Cisco Systems, Inc., Splunk Inc., Rapid7, Swimlane, Fortinet, Inc., ServiceNow, Microsoft Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Security Orchestration Market Shifts & Advancements
Artificial intelligence is compressing detection-to-response cycles by embedding predictive prioritization directly into orchestration workflows. This shift is eliminating the latency between alert generation and playbook execution that previously allowed threats to propagate laterally.
Generative AI is automating playbook authoring by translating natural language incident descriptions into executable response workflows. Mid-market security teams with limited Python expertise are adopting these tools fastest, collapsing the six-month implementation cycles typical of traditional SOAR deployments into weeks. This compression is democratizing orchestration access beyond Fortune 500 enterprises.
The EU AI Act is mandating human oversight requirements for automated security decisions affecting critical infrastructure. European energy and transportation operators must now document algorithmic rationale for containment actions, forcing orchestration vendors to embed explainability modules that trace playbook logic. German and French utilities are leading compliance investment, treating audit-ready automation as a procurement prerequisite.
Consolidated platform procurement is displacing best-of-breed tool assembly as the dominant buying pattern. CISOs at United States financial institutions are rejecting multi-vendor SOAR-SIEM-XDR stacks in favor of single-vendor suites that reduce integration engineering headcount. This concentration is visible most acutely in federal contractor segments where FedRAMP authorization costs favor platform breadth over point solution depth.
Global Security Orchestration Market Segmentation
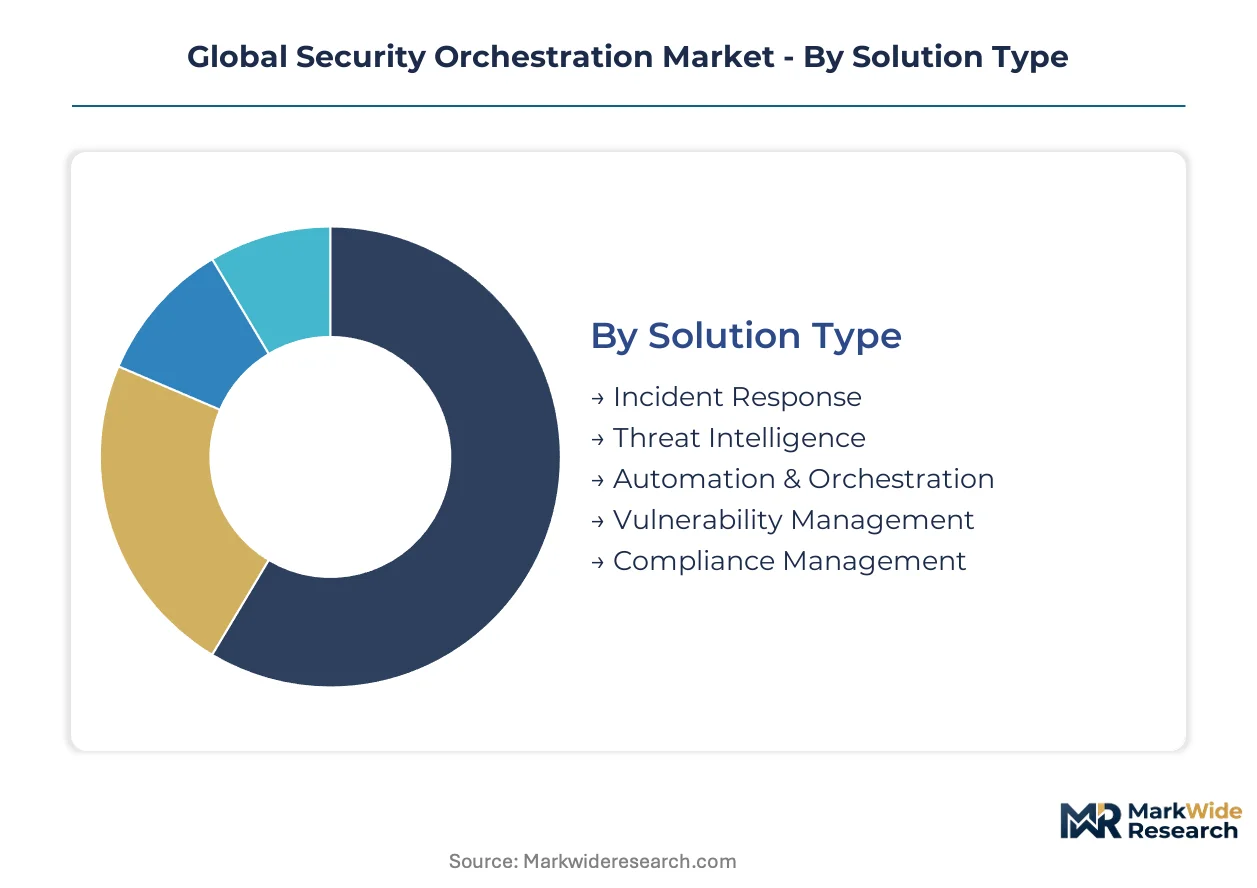
Security orchestration vendors configure platform architectures around distinct operational requirements. Buyers select solution types based on SOC maturity, deployment models based on data sovereignty constraints, applications based on threat surface coverage, and end-user industries based on regulatory exposure.
Solution Type:
Standardization dominates playbook-heavy segments while customization prevails in compliance-driven modules requiring jurisdictional tailoring.
- Incident Response:Pre-built containment playbooks automate quarantine, isolation, and forensic preservation workflows across endpoint and network layers. United States federal contractors deploy these capabilities to satisfy SEC disclosure timelines for material cybersecurity incidents. Leading the category by volume: Incident Response. Growing fastest: Compliance Management.
- Threat Intelligence:Automated ingestion and correlation of indicator feeds from commercial providers and government sources enables real-time enrichment of security alerts. Financial services institutions in Frankfurt and London prioritize this segment to meet EU AI Act documentation requirements for automated decision rationale.
- Automation & Orchestration:Low-code workflow engines connect disparate security tools through standardized APIs, collapsing mean-time-to-response metrics.
- Vulnerability Management:Orchestrated scanning and patching workflows prioritize critical exposures based on exploitability scoring.
- Compliance Management:Pre-mapped control frameworks automate evidence collection for GDPR Article 33, NIS2 Directive, and HIPAA audit trails.
Incident Response commands the largest deployment base. Compliance Management climbs the fastest as European regulatory deadlines approach.
Deployment Model:
Cost tier separation is pronounced: cloud-native deployments minimize capital expenditure while hybrid configurations preserve margin through professional services attach rates.
- Cloud-Based:Elastic infrastructure scales compute resources during peak threat periods without permanent hardware commitments. United States healthcare providers below enterprise scale favor this model to avoid datacenter capital constraints.
- Hybrid:Sensitive data processing remains on-premises while analytics and threat intelligence leverage cloud elasticity. German energy utilities mandate this architecture to satisfy BSI critical infrastructure requirements for operational technology isolation.
- On-Premises:Complete air-gapped operation for classified government networks and defense industrial base facilities.
- Managed Services:Outsourced SOC operations with vendor-managed orchestration platforms and analyst staffing.
Cloud-Based deployments dominate new procurement. Hybrid configurations retain pricing power in regulated European markets.
Application:
Maturity gradients separate established monitoring use cases from emerging identity-centric automation.
- Cybersecurity Monitoring:Real-time telemetry aggregation from SIEM, EDR, and network sensors with automated alert triage. United States critical infrastructure operators standardize on this application to satisfy FAA and FERC incident reporting mandates.
- Identity Management:Automated provisioning, deprovisioning, and access certification workflows integrated with privileged access management. French banking groups deploy these capabilities to meet ACPR operational resilience requirements for financial market infrastructure.
- Risk Assessment:Quantitative scoring of security posture with automated remediation prioritization.
- Security Analytics:Behavioral anomaly detection with orchestrated investigation workflows.
- Network Defense:Automated firewall rule updates and intrusion prevention system tuning.
- Endpoint Protection:Coordinated response across EDR, antivirus, and device control platforms.
Cybersecurity Monitoring represents the largest installed base. Identity Management shows the steepest expansion trajectory as zero-trust architectures mature.
End User Industry:
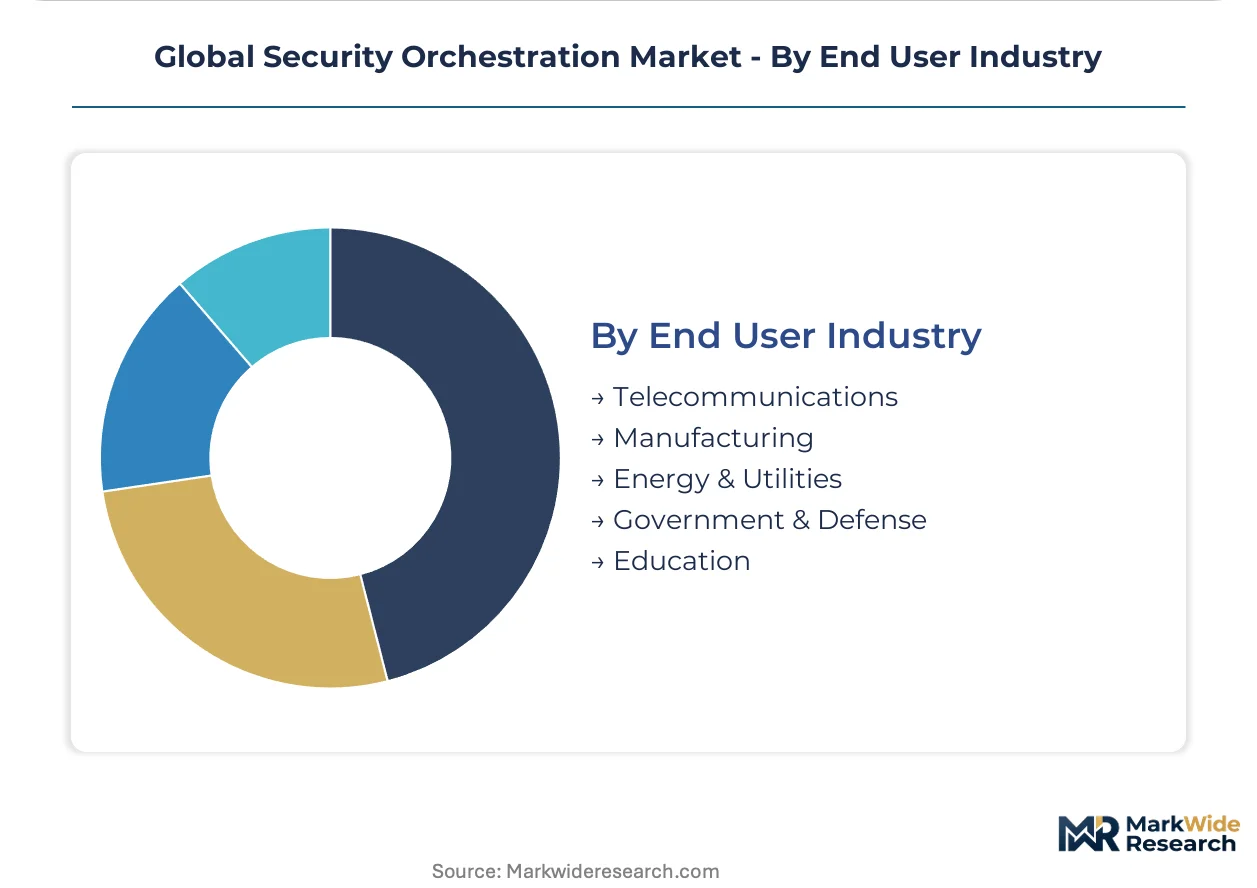
Supply concentration favors telecommunications and government sectors with centralized procurement authority and multi-year platform contracts.
- Government & Defense:Classified networks require FedRAMP-authorized orchestration with audit trails for chain-of-custody documentation. United States Department of Defense components mandate these platforms under CMMC 2.0 supply chain security requirements.
- Energy & Utilities:OT-IT convergence demands orchestration that bridges IT security tools with industrial control system monitoring. German transmission system operators invest heavily here to satisfy NIS2 Directive critical entity designations.
- Telecommunications:Massive subscriber data volumes and lawful intercept obligations drive scale requirements.
- Manufacturing:Intellectual property protection and operational continuity for smart factory environments.
- Education:Limited security staffing drives demand for fully managed orchestration services.
Government & Defense leads procurement value. Energy & Utilities gains share fastest as NIS2 implementation deadlines activate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States generates the largest security orchestration consumption while vendor development concentrates across North America and Europe. Platform procurement patterns diverge sharply between federal-mandated standardization and compliance-driven fragmentation.
United States
Federal contractors and critical infrastructure operators drive platform consolidation under CMMC 2.0 and SEC cybersecurity disclosure rules. The FAA mandates standardized incident response for aviation infrastructure, forcing orchestration procurement through FedRAMP-authorized channels. Washington DC and Northern Virginia host dense concentrations of government-focused security vendors.
Germany
Energy utilities and automotive manufacturers deploy hybrid orchestration architectures to satisfy BSI critical infrastructure requirements. The NIS2 Directive and EU AI Act impose auditable response workflows that only integrated platforms can deliver. Munich and Frankfurt banking clusters invest heavily in compliance-ready automation for ACPR-aligned operational resilience.
United Kingdom
Financial services institutions in the City of London unify fragmented SOC toolchains under post-Brexit regulatory pressure. The UK National Cyber Security Centre mandates standardized threat response for critical national infrastructure operators. London's cybersecurity vendor ecosystem specializes in cloud-native orchestration for mid-market enterprises.
France
Nuclear energy operators and defense contractors require air-gapped orchestration with algorithmic explainability under EU AI Act human-oversight provisions. The ANSSI imposes strict incident notification timelines that drive playbook automation adoption. Paris and Toulouse aerospace clusters prioritize audit-ready response workflows.
Japan
Manufacturing conglomerates and telecommunications providers integrate orchestration with operational technology security for smart factory environments. METI guidelines encourage automated threat response while preserving human oversight for critical decisions. Tokyo and Osaka metropolitan areas concentrate domestic platform development.
Global Security Orchestration Market Competitive Landscape
Diversified conglomerates compete with focused pure-play specialists across three distinct tiers. Platform breadth anchors enterprise accounts seeking collapsed integration tax, while low-code specialists capture mid-market demand with reduced engineering dependency. Strategic archetypes include consolidated security-stack vendors, workflow-automation pure-plays, and network-centric infrastructure providers. Competitive moves concentrate on XDR-SOAR convergence and cloud-native portfolio expansion.
Within the consolidated-platform tier, Palo Alto Networks and Cisco Systems occupy positions defined by infrastructure breadth and native telemetry integration. Swimlane exemplifies the pure-play automation archetype through specialized low-code workflow engines. These three companies represent the dominant competitive vectors reshaping procurement patterns: unified-stack consolidation, network-embedded orchestration, and accessible automation for resource-constrained security teams.
| Leading Market Players |
|---|
| IBM Corporation |
| Palo Alto Networks |
| Cisco Systems, Inc. |
| Splunk Inc. |
| Rapid7 |
| Swimlane |
| Fortinet, Inc. |
| ServiceNow |
| Microsoft Corporation |
| Others |
Supply & Pricing Matrix
Platform-tier divergence between consolidated security stacks and point solutions manifests in divergent pricing power and supply chain configurations. Premium unified-platform vendors command sustained margins through FedRAMP authorization scarcity and native telemetry integration, while workflow-automation specialists compete on implementation velocity and reduced engineering dependency.
Pricing Analysis
Margin tightening in the mid-market tier reflects buyer consolidation onto single-vendor suites that collapse integration engineering headcount. Three-tier pricing structure across enterprise, mid-market, and managed service levels separates FedRAMP-authorized platforms from cloud-native alternatives and white-label orchestration services. Price differentiation hinges on playbook library depth and cross-cloud API coverage. Healthcare providers below enterprise scale exhibit highest price sensitivity due to capital constraint pressures, while United States federal contractors absorb premium tiers to satisfy CMMC 2.0 compliance mandates.
Supply Chain Analysis
Freight cost insignificance characterizes software-dominant supply chains, yet professional services delivery creates geographic staffing dependencies. Development talent concentrates in the United States, Israel, and Ireland where cybersecurity engineering density supports platform innovation. Cloud infrastructure draws from hyperscaler networks across AWS, Azure, and Google Cloud regions. Single-source vulnerability sits with niche API middleware providers whose proprietary connectors fragment interoperability. Distribution runs through direct enterprise sales teams and channel partners serving mid-market segments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform consolidation is compressing vendor margins and forcing weaker point-solution providers toward acquisition or exit as buyers reject multi-vendor integration complexity.
For Market Incumbents: Deploy native XDR-SOAR convergence to anchor enterprise accounts seeking collapsed mean-time-to-response metrics. Defensive moves center on embedding orchestration into existing SIEM deployments and accelerating FedRAMP authorization timelines to lock out emerging competitors. The threat of generative AI playbook authoring tools demands rapid low-code capability investment to preserve mid-market positioning against automation democratization. For New Entrants and Emerging Players: Generative AI-powered playbook translation offers a technology-first wedge into mid-market security teams lacking Python engineering resources. White space targets include United States municipal governments and regional healthcare systems underserved by enterprise-focused platform vendors. Go-to-market positioning should emphasize weeks-long implementation cycles against traditional six-month SOAR deployments, with channel partnerships accelerating geographic reach. For Investors and Strategic Acquirers: Re-rating potential sits with workflow-automation pure-plays possessing low-code differentiation and established channel relationships given accelerating mid-market penetration. Long-term viability over the next decade hinges on platform breadth sufficient to satisfy converging XDR-SOAR procurement patterns. The signal to watch is federal contractor consolidation velocity as CMMC 2.0 implementation deadlines activate standardized orchestration mandates.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifying SOAR with XDR and SIEM collapses integration tax for federal contractors under CMMC 2.0 mandates. |
| Acquisition of Specialist Firm | Low-code workflow engines extend reach into engineering-constrained mid-market healthcare and municipal segments. |
| Geographic Expansion | FedRAMP-authorized cloud regions capture United States defense and critical infrastructure procurement flows. |
| Strategic Partnership | Hyperscaler alliances embed orchestration into native security services for cloud-migrating financial institutions. |
| Product Launch | Explainability modules satisfy EU AI Act human-oversight requirements for German and French energy utilities. |
Research Methodology
SEC filings, hyperscaler security service disclosures, and FedRAMP authorization databases formed the secondary backbone for vendor positioning and platform capability mapping. Primary interviews with CISOs at United States financial institutions, SOC managers at European energy utilities, and channel partners specializing in mid-market healthcare deployments validated procurement pattern assumptions. Bottom-up triangulation across deployment model adoption curves and top-down cross-checks against regulatory compliance spending produced convergent market estimates.
Historical trendline analysis of security operations center automation investment preceded forward projection across the modeling period. Segmentation dimensions included solution type, deployment model, organization size tier, vertical regulatory exposure, and geographic adoption pattern. CAGRs were derived from elasticity-adjusted spending trajectories incorporating cloud migration velocity and compliance deadline clustering. Industry-specific inputs encompassed NIS2 Directive implementation timelines and SEC cybersecurity disclosure rule adoption curves.
Several conditions sit outside the modeled scope, including black-swan cyber incidents triggering emergency procurement surges and geopolitical fragmentation of cloud infrastructure standards. Forecasts reflect assumptions about regulatory stability and API standardization progress that stakeholders should weight against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Global Security As a Service Market
Security and Surveillance
Asia-Pacific Security Screening Market
Security and Surveillance
Face Smart Lockers Market
Security and Surveillance
Alarm Monitoring Software Market
Security and Surveillance
Global Manned Security Service Market
Security and Surveillance
Night Vision Binoculars Market
Security and Surveillance
Forensic Technologies Market
Security and Surveillance
Airport Baggage Screening Systems Market
Security and Surveillance
Europe Anti-Piracy Protection Market
Security and Surveillance
Resale Authentication Services Market
Security and Surveillance
Manned Guarding Services Market
Security and Surveillance
Security System Integrators Market
Security and Surveillance
APAC Security Testing Market
Security and Surveillance
Riot Control System Market
Security and Surveillance
Global Threat Intelligence Management Market
Security and Surveillance
North America Urban Security Screening Market