
 Proactive Security Market | 2026-2036
Proactive Security Market Size, Share, and Industry Trends Forecast 2026-2036
Proactive Security Market Analysis
AI-driven threat detection is fragmenting traditional security architectures into modular, cloud-native components that demand continuous behavioral analysis. Palo Alto Networks leverages integrated platform consolidation to sustain enterprise-grade coverage across hybrid environments. CrowdStrike anchors endpoint protection with lightweight agent deployment, while Fortinet competes through hardware-software convergence at network perimeters.
Proactive security encompasses predictive threat identification, automated response orchestration, and continuous vulnerability assessment powered by real-time telemetry ingestion at millisecond latency. Its primary purpose is neutralizing adversarial campaigns before payload execution rather than remediating post-breach damage. Threat intelligence solutions lead margin capture by converting dark-web monitoring and indicator feeds into actionable defense parameters. Cloud security architectures represent the fastest-expanding technology layer as distributed workforces multiply attack surfaces beyond traditional perimeter controls. Endpoint security remains the most mature solution category, though AI-based detection modules are displacing signature-dependent approaches in enterprise procurement cycles.
The EU AI Act classifies autonomous security systems as high-risk applications, mandating human oversight and algorithmic transparency for market access. ETSI cybersecurity standards and the NIS2 Directive impose breach-notification timelines and supply-chain due diligence that reshape vendor qualification criteria. Stakeholders must monitor evolving conformity assessment pathways as regulatory fragmentation between Brussels and member-state implementations complicates cross-border service delivery.
Market Dynamics
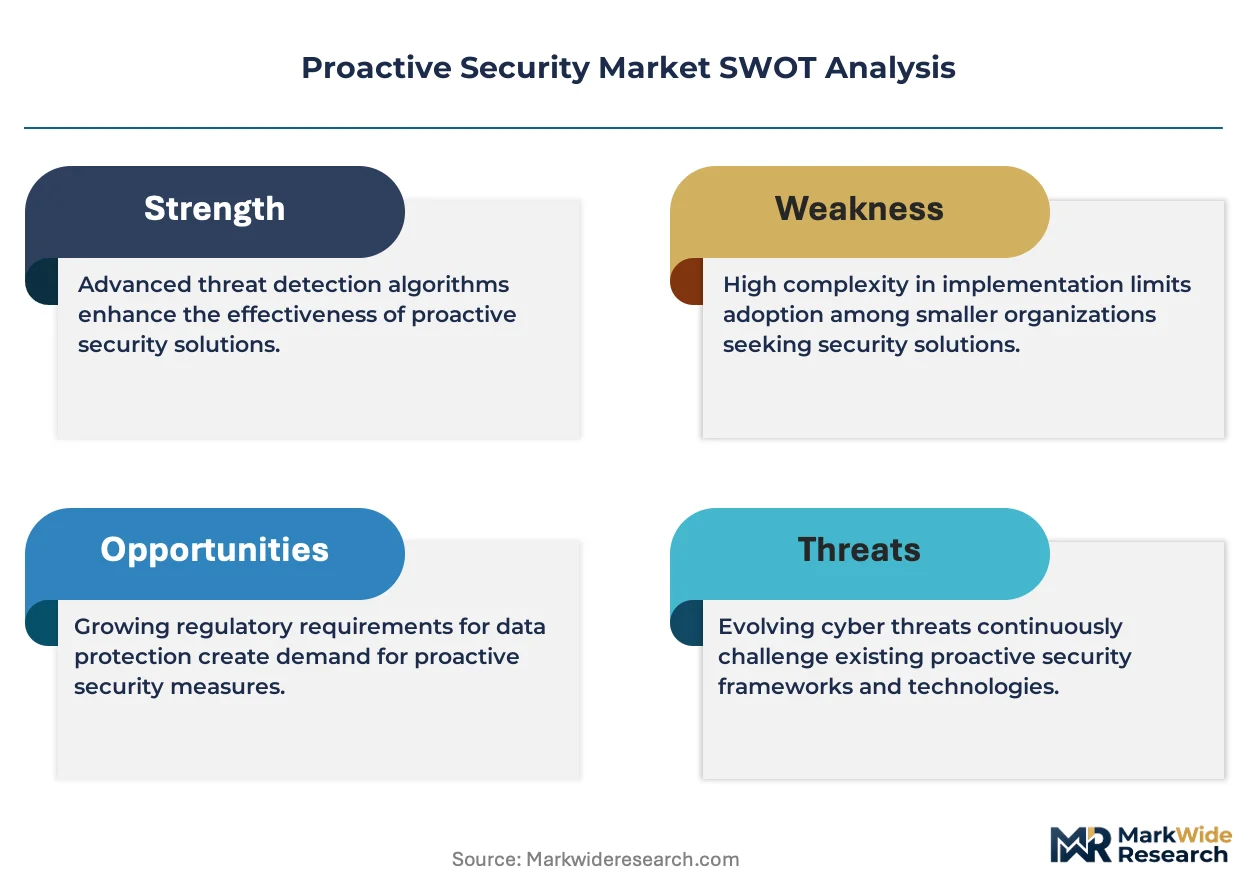
The EU AI Act and NIS2 Directive are forcing security vendors to re-architect autonomous systems around human-in-the-loop oversight, compressing development timelines while expanding compliance budgets across European deployments.
Growth Catalysts
- Critical Infrastructure Modernization:Germany, France, and the United Kingdom are accelerating replacement of legacy perimeter defenses with predictive threat platforms across energy grids and financial clearing systems.
- ETSI Cybersecurity Standards:Mandated certification pathways for high-risk AI applications are creating procurement pull for vendors with pre-validated conformity assessment documentation.
- Cloud-Native Telemetry Architectures:Millisecond-latency behavioral analysis engines are enabling real-time adversarial campaign neutralization before payload execution.
Market Restraints
- Algorithmic Transparency Requirements:The EU AI Act mandates explainable decision pathways for autonomous security systems, extending R&D cycles and inflating engineering headcount costs.
- Supply Chain Due Diligence Burden:NIS2 Directive breach-notification timelines and third-party liability provisions are disqualifying vendors without documented software bill of materials practices.
- Human Oversight Mandates:High-risk classification of autonomous response systems limits fully automated remediation, constraining labor cost reduction potential.
Strategic Opportunities
- Cross-Border Service Delivery:Regulatory fragmentation between Brussels and member-state implementations creates first-mover advantage for vendors with modular compliance architectures adaptable to national transpositions.
- Dark-Web Intelligence Monetization:Threat intelligence solutions converting indicator feeds into actionable defense parameters are capturing premium margins in financial services procurement cycles.
- Hardware-Software Convergence:Network perimeter appliances integrating AI inference engines at the edge are displacing standalone software licenses in enterprise firewall refresh programs.
Industry Challenges
- Adversarial ML Expertise Scarcity:Security engineering teams lack depth in poisoning attack detection and model extraction defense, forcing reliance on external red-team contractors.
- Legacy SIEM Integration Friction:Predictive platforms must maintain backward compatibility with decade-old log aggregation infrastructure, diluting real-time performance advantages.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Proactive Security Market |
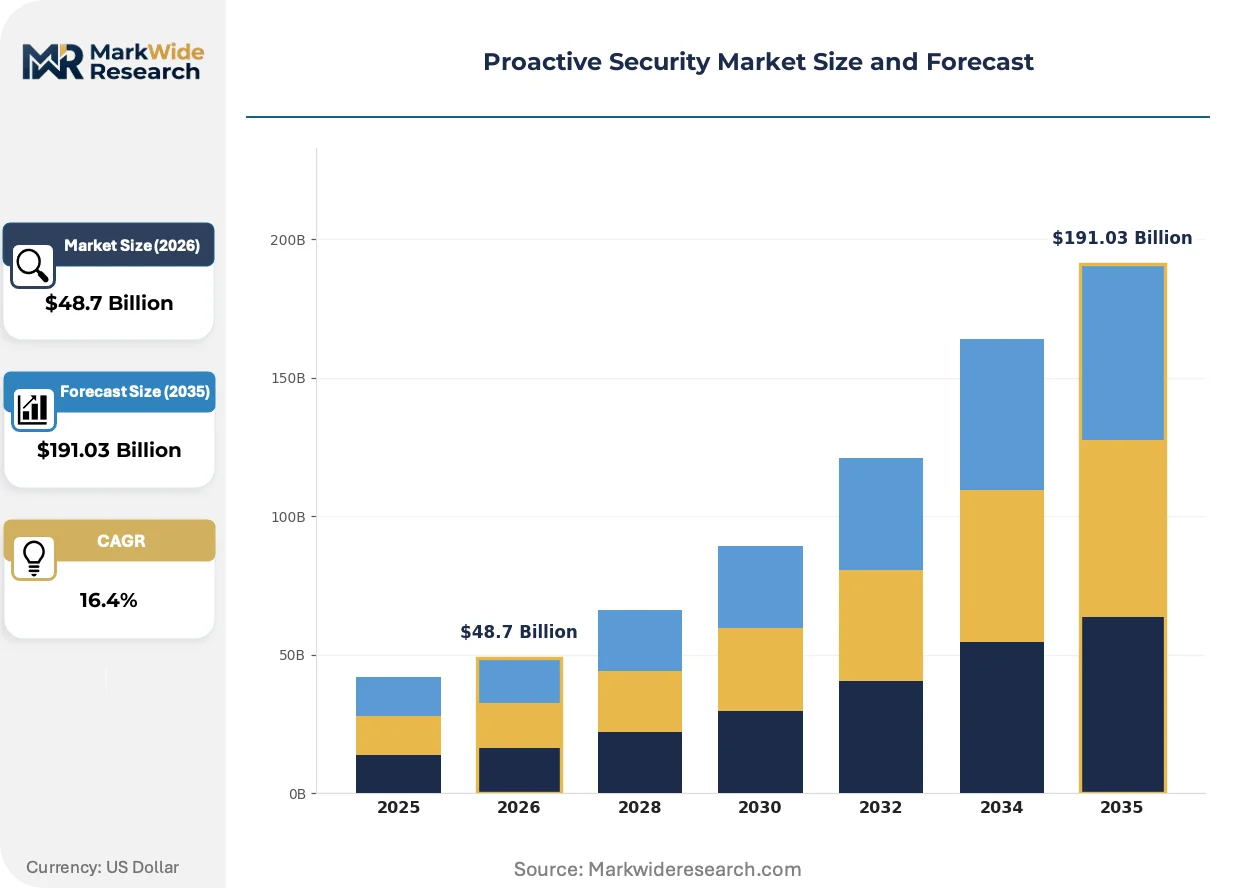
| Market Size in 2026 | $48.7 Billion |
| Market Size in 2035 | $191.03 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Intrusion Detection, Firewalls, Threat Intelligence, Endpoint Security Application Area: Enterprise, Government, Healthcare, Retail Technology: AI-Based, Machine Learning, Cloud Security, Blockchain End User: IT Companies, Financial Institutions, Telecommunication, Energy |
| Companies Covered | RSA Security LLC, Palo Alto Networks, Oracle Corp., Microsoft, CrowdStrike, FireEye Inc., Rapid7 Inc., Fortinet, IBM Corp., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Proactive Security Market Emerging Trajectories
Security architectures are fragmenting into modular, API-first components that demand continuous behavioral telemetry rather than periodic signature updates. This shift is compressing vendor consolidation timelines while elevating cloud-native engineering capabilities as primary competitive differentiators.
Extended detection and response platforms are virtualizing security operations center functions through containerized analytics engines and serverless threat-hunting workflows. Mid-market enterprises lacking dedicated SOC staffing are adopting these platforms fastest, compressing the addressable market for managed security service providers that rely on labor arbitrage models.
The EU AI Act's high-risk classification for autonomous security systems is mandating algorithmic transparency documentation and human oversight interfaces before market access. Vendors must now maintain technical file repositories and conformity assessment records that extend sales cycles but create defensible moats against unqualified competitors in European procurement.
Enterprise buyers are consolidating vendor relationships around integrated platforms rather than best-of-breed point solutions, compressing evaluation cycles and elevating total cost of ownership calculations over feature checklists. Financial institutions in Germany and the United Kingdom are driving this consolidation hardest, demanding unified endpoint, network, and cloud visibility from single procurement relationships.
Proactive Security Market Segmentation
Proactive security procurement patterns diverge sharply across organizational maturity levels, technology stacks, and regulatory exposure profiles. Segment-level analysis reveals where predictive threat platforms command premium pricing versus where legacy perimeter defenses retain residual demand.
Solution Type:
Mature endpoint and network perimeter categories coexist with emerging AI-native detection modules that redefine architectural requirements.
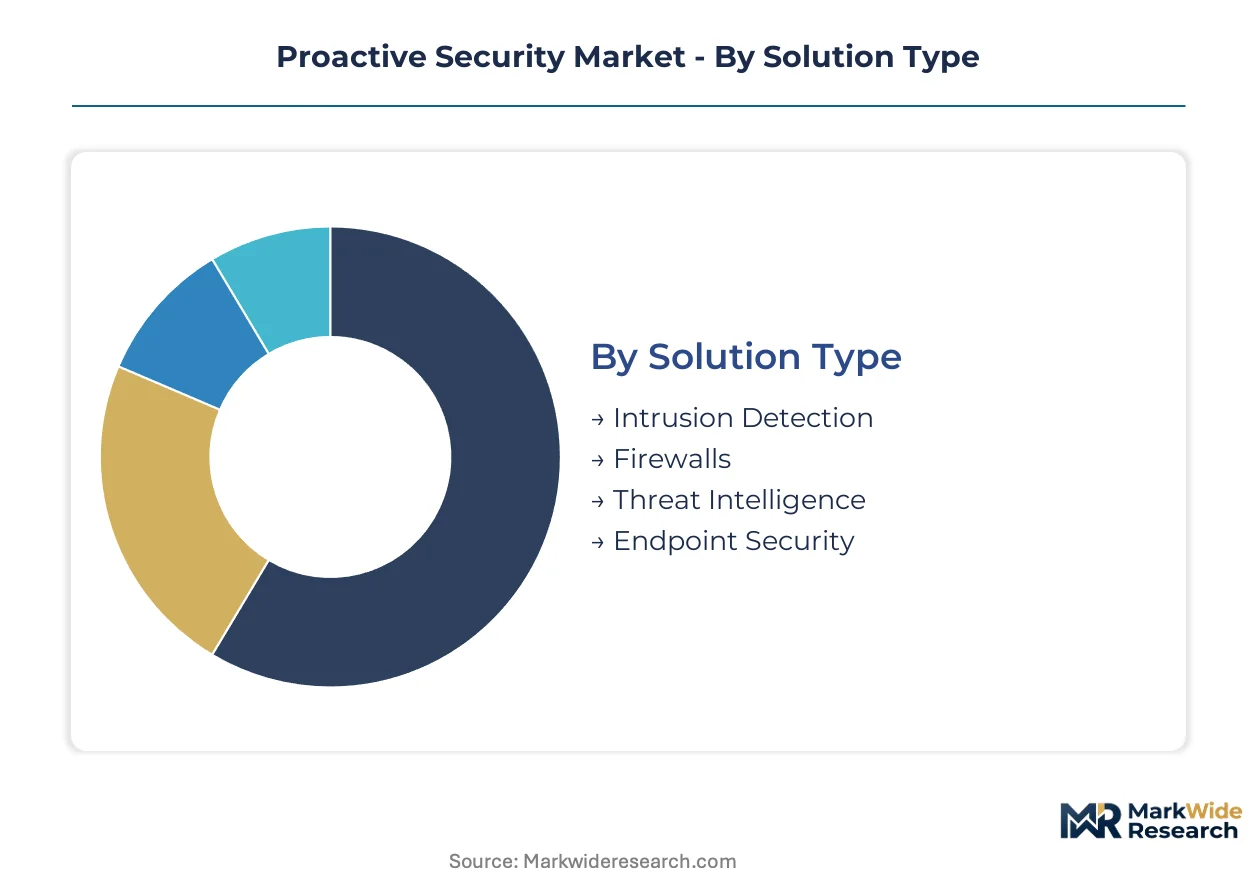
- Intrusion Detection:Signature-based network monitoring systems are ceding ground to behavioral analytics engines that process millisecond-latency telemetry for pre-execution threat neutralization. German energy grid operators and UK financial clearinghouses are prioritizing these upgrades amid NIS2 Directive compliance deadlines.
- Threat Intelligence:Dark-web monitoring platforms convert indicator feeds into actionable defense parameters, capturing disproportionate margins in financial services procurement cycles. The EU AI Act's high-risk classification mandates human oversight interfaces that extend sales cycles but create defensible vendor moats.
- Firewalls:Hardware-software convergence at network edges is displacing standalone software licenses in enterprise refresh programs.
- Endpoint Security:Lightweight agent deployment models are displacing signature-dependent approaches in enterprise procurement cycles.
Threat intelligence retains volume leadership; intrusion detection holds the steepest expansion curve.
Application Area:
Regulatory intensity and asset criticality stratify demand across institutional categories, with breach-notification obligations reshaping procurement urgency.
- Government:National security agencies and critical infrastructure authorities mandate predictive platforms with documented conformity assessment pathways under ETSI cybersecurity standards. France and the United Kingdom are accelerating replacement of legacy perimeter defenses across energy grids and defense networks.
- Healthcare:Patient data protection requirements intersect with medical device cybersecurity mandates, creating dual-compliance procurement complexity. German hospital networks are consolidating vendor relationships around integrated platforms rather than best-of-breed point solutions.
- Enterprise:Mid-market corporations lacking dedicated SOC staffing are adopting virtualized security operations center functions fastest.
- Retail:Payment card industry compliance and point-of-sale protection drive seasonal procurement patterns.
Enterprise commands absolute spending scale; healthcare is climbing the fastest as medical device connectivity expands attack surfaces.
Technology:
Deployment architecture choices determine latency profiles, scalability boundaries, and regulatory treatment under emerging AI governance frameworks.
- Cloud Security:Distributed workforces multiply attack surfaces beyond traditional perimeter controls, making this the fastest-expanding technology layer. Containerized analytics engines and serverless threat-hunting workflows are virtualizing SOC functions for mid-market adoption.
- AI-Based:Autonomous response systems face high-risk classification under the EU AI Act, mandating algorithmic transparency documentation and human-in-the-loop oversight before market access. Vendors must maintain technical file repositories that compress development timelines while expanding compliance budgets.
- Machine Learning:Behavioral anomaly detection modules are displacing signature-dependent approaches in enterprise procurement cycles.
- Blockchain:Distributed ledger applications for identity verification and audit trails remain niche in security-specific deployments.
Cloud security leads deployment velocity; AI-based systems face the steepest regulatory headwinds despite capability advantages.
End User:
Sector-specific risk appetites and regulatory exposure create divergent procurement patterns across critical infrastructure and commercial verticals.
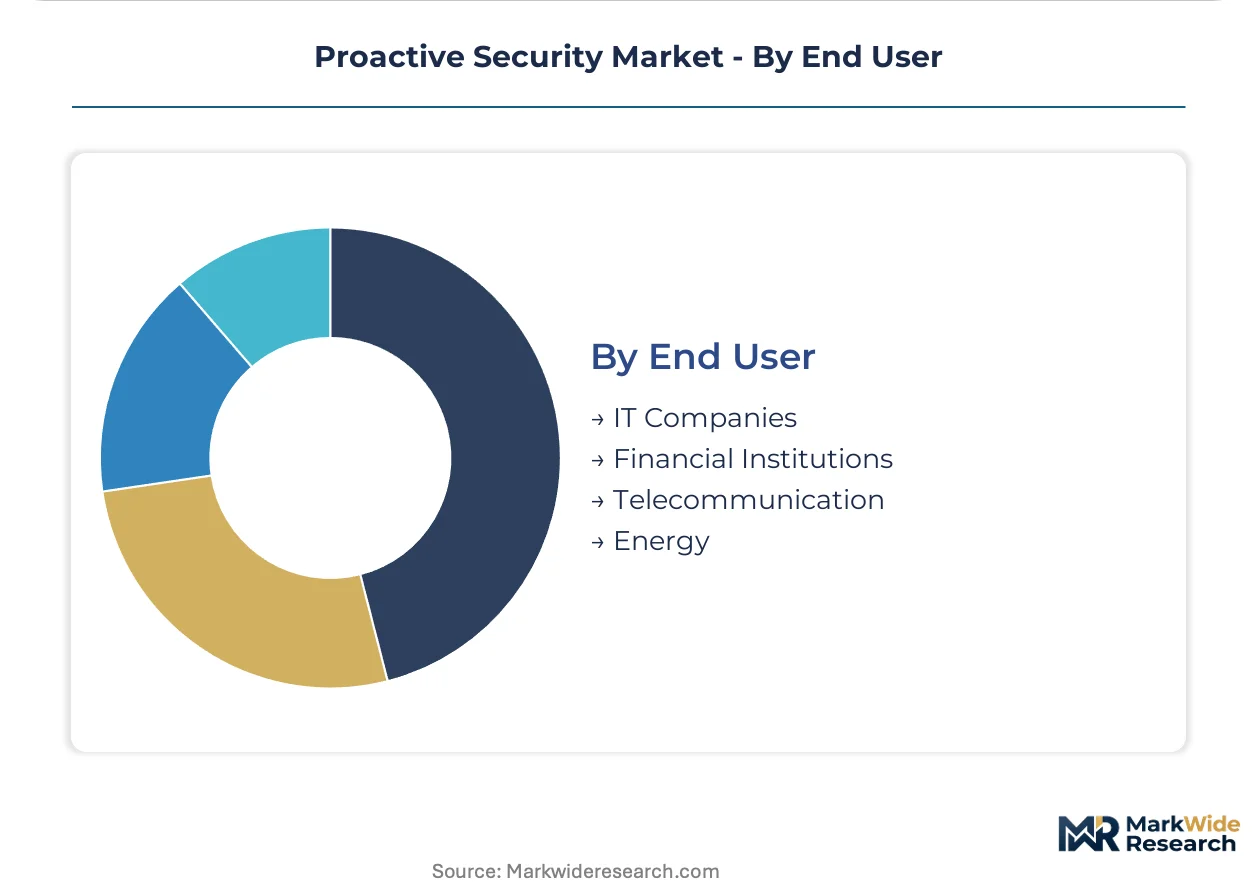
- Financial Institutions:Predictive threat platforms are expanding fastest across German, French, and UK banking networks as enterprises modernize critical infrastructure protection. Dark-web intelligence monetization and real-time adversarial campaign neutralization command premium pricing in this segment.
- Energy:Power grid operators face NIS2 Directive breach-notification timelines and supply-chain due diligence requirements that disqualify vendors without documented software bill of materials practices. Human oversight mandates for autonomous response systems constrain fully automated remediation.
- IT Companies:Cloud-native engineering capabilities serve as primary competitive differentiators in vendor selection.
- Telecommunication:Network equipment security and subscriber data protection drive procurement of integrated platform consolidation.
Financial institutions anchor procurement scale; energy is gaining share fastest as critical infrastructure modernization accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German cybersecurity vendors export predictive threat platforms to financial institutions across France and the United Kingdom, establishing a dominant trade corridor in European proactive security procurement.
Germany
Energy grid operators and automotive manufacturers drive demand for NIS2-compliant autonomous systems. The Federal Office for Information Security enforces ETSI certification pathways for critical infrastructure protection. Frankfurt's financial district anchors deployment of millisecond-latency behavioral analytics across banking networks.
France
National defense agencies and healthcare networks mandate predictive platforms with documented conformity assessments. ANSM and CNIL coordinate oversight of AI-driven medical device security under the EU AI Act. Paris-Saclay's cybersecurity cluster concentrates vendors specializing in algorithmic transparency documentation.
United Kingdom
Financial clearinghouses and telecom operators accelerate replacement of legacy perimeter defenses. The National Cyber Security Centre imposes breach-notification timelines that reshape vendor qualification criteria. London's fintech corridor demands unified endpoint, network, and cloud visibility from single procurement relationships.
United States
Cloud-native enterprises and federal agencies expand deployment of automated response orchestration. The SEC and CISA tighten disclosure requirements for critical infrastructure operators. Silicon Valley engineering clusters dominate development of containerized analytics engines for serverless threat-hunting workflows.
Japan
Manufacturing conglomerates and semiconductor fabricators prioritize continuous vulnerability assessment. METI promotes adoption of AI-native detection modules through industrial cybersecurity subsidies. Tokyo-Osaka industrial corridors concentrate procurement of hardware-software converged perimeter appliances.
Proactive Security Market Vendor Landscape
Channel-controlling players compete with product-specialist players across a consolidated vendor base where integrated platform consolidation displaces point-solution procurement. Enterprise buyers favor vendors offering unified endpoint, network, and cloud visibility from single relationships. Three archetypes dominate: integrated platform consolidators anchoring hybrid environment coverage, lightweight agent specialists capturing endpoint refresh cycles, and hardware-software converged players defending network perimeters. Dominant competitive moves include strategic partnerships for SIEM integration compatibility and portfolio diversification into dark-web intelligence monetization.
Within the integrated platform tier, Palo Alto Networks and CrowdStrike exemplify channel-controlling archetypes that enterprise buyers consolidate around. Fortinet occupies a position representing hardware-software convergence at network edges. These three vendors anchor competitive dynamics as procurement patterns shift from best-of-breed evaluation toward total cost of ownership calculations.
| Leading Market Players |
|---|
| RSA Security LLC |
| Palo Alto Networks |
| Oracle Corp. |
| Microsoft |
| CrowdStrike |
| FireEye Inc. |
| Rapid7 Inc. |
| Fortinet |
| IBM Corp. |
| Others |
Supply Flow & Price Mechanics
Silicon Valley engineering clusters concentrate AI inference chip production for security platforms, anchoring margin capture in threat intelligence modules and cloud-native detection engines downstream. This upstream concentration funnels pricing power toward vendors with captive semiconductor partnerships or direct foundry relationships.
Pricing Analysis
Next-generation AI-native detection modules command substantial premiums over signature-based intrusion detection systems and legacy perimeter appliances. Three-tier pricing structure across premium, standard, and economy levels segments buyers by deployment scale and compliance certification tier. Pricing pressure stems from mid-market enterprises consolidating around integrated platforms rather than point solutions, compressing evaluation cycles. Financial institutions exhibit lowest price sensitivity due to breach-notification liability exposure, while retail and mid-market healthcare networks drive hardest bargain negotiations.
Supply Chain Analysis
US export controls on advanced AI accelerators and EU dual-use technology restrictions constrain component flows for autonomous security systems. Taiwan, South Korea, and the United States anchor semiconductor fabrication for inference engines. Supply chains draw from specialized foundry capacity, high-bandwidth memory modules, and precision optics for photonic computing applications. Single-source vulnerability concentrates in advanced node chip production. Distribution runs through direct enterprise sales teams and hyperscaler marketplace integrations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Proactive security procurement is fragmenting into modular, API-first components, creating white-space opportunities for specialists in adversarial ML defense and algorithmic transparency tooling.
For Market Incumbents: Entrench platform consolidation advantages by deepening integration with legacy SIEM infrastructure and acquiring dark-web intelligence specialists. Cloud-native engineering talent scarcity threatens margin expansion. Prioritize backward integration into telemetry ingestion hardware to differentiate latency performance. For New Entrants and Emerging Players: Establish a beachhead in algorithmic transparency documentation services for EU AI Act compliance. Mid-market healthcare networks in Germany and France present the most penetrable buyer segment due to dual-compliance complexity. Pursue channel partnerships with managed security service providers lacking in-house AI governance expertise. For Investors and Strategic Acquirers: Capital is best deployed toward vendors with pre-validated ETSI conformity assessment pathways and documented software bill of materials practices. Long-term viability hinges on regulatory moat durability rather than feature velocity alone. Watch for NIS2 Directive enforcement variance across member states as inflection signal for cross-border service delivery winners.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and cloud visibility for German financial institutions consolidating vendor relationships. |
| Regulatory Compliance Investment | Builds defensible moats through EU AI Act technical file repositories and human oversight interface development. |
| Strategic Partnership | Accelerates SIEM compatibility for predictive platforms facing legacy infrastructure integration friction. |
| Acquisition of Specialist Firm | Captures dark-web intelligence monetization capabilities commanding premium margins in banking procurement. |
| Geographic Expansion | Exploits regulatory fragmentation between Brussels and member-state NIS2 implementations for first-mover positioning. |
Methodological Framework
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at financial institutions, energy grid operators, healthcare network administrators, and AI governance officers. Secondary validation drew from SEC cybersecurity disclosure filings, EU AI Act implementation guidance, ETSI certification databases, and NIS2 Directive transposition documents. Bottom-up deployment estimates and top-down market sizing were triangulated to anchor volume projections.
Calibration against historical procurement cycles and regulatory enforcement timelines shaped the analytical framework across the projection horizon. Segmentation dimensions modeled include solution type, application area, deployment architecture, organization size tier, and regional regulatory cluster. CAGRs were derived from technology adoption curve analysis and compliance deadline clustering. Forecast inputs incorporated adversarial ML capability maturity scores and cloud-native infrastructure penetration rates.
Stress conditions across algorithmic transparency enforcement intensity, semiconductor supply availability, and critical infrastructure modernization budget cycles were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions about regulatory harmonization and buyer consolidation trajectories. Material shifts in EU AI Act liability interpretation or NIS2 penalty structures would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
TSCM Equipment Market
Security and Surveillance
India CCTV Market
Security and Surveillance
Shock Sensor Market
Security and Surveillance
Global Security As a Service Market
Security and Surveillance
Forensic Technologies Market
Security and Surveillance
Face Smart Lockers Market
Security and Surveillance
North America Wireless Monitoring and Surveillance Market
Security and Surveillance
Situational Awareness System Market
Security and Surveillance
Global Wireless Monitoring and Surveillance Market
Security and Surveillance
Narcotics Scanner Market
Security and Surveillance
Global Bot Security Market
Security and Surveillance
Global Police and Law Enforcement Equipment Market
Security and Surveillance
Signal Jamming Systems Market
Security and Surveillance
Manned Guarding Services Market
Security and Surveillance
Speed Limit Radar Signs Market
Security and Surveillance
Home Security Solution Market