
 Security Intelligence Market | 2026-2036
Security Intelligence Market Size, Share, and Industry Trends Forecast 2026-2036
Security Intelligence Market Intelligence
Enterprise-grade threat intelligence platforms is reorganizing competitive dynamics across the Security Intelligence landscape. Palo Alto Networks leverages extensive firewall-to-cloud integration to anchor its position in network-centric deployments. CrowdStrike specializes in endpoint-native telemetry, while Fortinet competes through consolidated security fabric architectures spanning hardware and software layers.
Security intelligence encompasses the systematic collection, processing, and analysis of threat data to enable predictive defense postures, typically operating across SIEM correlation engines with sub-second ingestion latencies and multi-source indicator fusion. The solution offering dimension shows threat detection and incident response commanding established budget allocations, whereas user behavior analytics represents the fastest-expanding margin pool as insider risk programs mature. Deployment patterns reveal cloud-based and hybrid configurations displacing legacy on-premises stacks, with private cloud variants gaining traction among regulated European financial institutions.
FCC guidelines on communications infrastructure protection, EU NIS2 requirements for essential entities, and SEC disclosure rules for material cybersecurity incidents collectively reshape product roadmaps and procurement criteria across the sector. GDPR-aligned data residency specifications further constrain cross-border threat data architectures. Stakeholders must weigh sovereignty-compliant deployment models against the latency advantages of centralized cloud-native analytics.
Market Dynamics
Cloud-native security intelligence architectures are compressing deployment timelines from months to weeks, forcing incumbent vendors to reengineer delivery models or cede mid-market share to API-first competitors. This velocity shift is restructuring procurement criteria across financial services, critical infrastructure, and government sectors.
Growth Catalysts
- EU NIS2 Directive:Mandatory threat intelligence sharing among essential and important entities across European member states is institutionalizing platform procurement budgets.
- Behavioral biometrics fusion:Financial institutions in the United States are layering keystroke dynamics and mouse-movement analytics atop traditional SIEM correlation to reduce false-positive rates.
- OT-IT convergence:Manufacturing and energy operators are unifying operational technology monitoring with enterprise security operations centers, expanding addressable platform scope.
Market Restraints
- Specialized talent scarcity:Certified threat intelligence analysts command compensation premiums exceeding forty percent above standard security operations salaries, constraining platform utilization rates.
- Data residency fragmentation:GDPR-aligned sovereignty requirements prevent centralized cloud analytics for cross-border financial institutions, forcing redundant infrastructure investments.
- Open-source substitute proliferation:MISP and OpenCTI deployments among mid-tier enterprises reduce commercial platform attach rates in price-sensitive segments.
Strategic Opportunities
- India BIS cybersecurity framework:Mandatory incident reporting for critical information infrastructure operators is creating first-mover advantage for localized threat intelligence platforms.
- Healthcare IoT telemetry:Medical device manufacturers are embedding security intelligence agents at the firmware layer, opening embedded analytics contracts.
- API-first distribution:Native integration with SOAR platforms and DevSecOps pipelines is displacing traditional reseller channels for mid-market penetration.
Industry Challenges
- Multi-cloud telemetry normalization:Security teams struggle to correlate indicators across AWS, Azure, and Google Cloud native logging formats without custom parser development.
- Attribution standardization delays:Absence of unified threat actor naming conventions between MITRE ATT&CK, STIX/TAXII, and vendor-proprietary taxonomies complicates cross-platform intelligence exchange.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Intelligence Market |
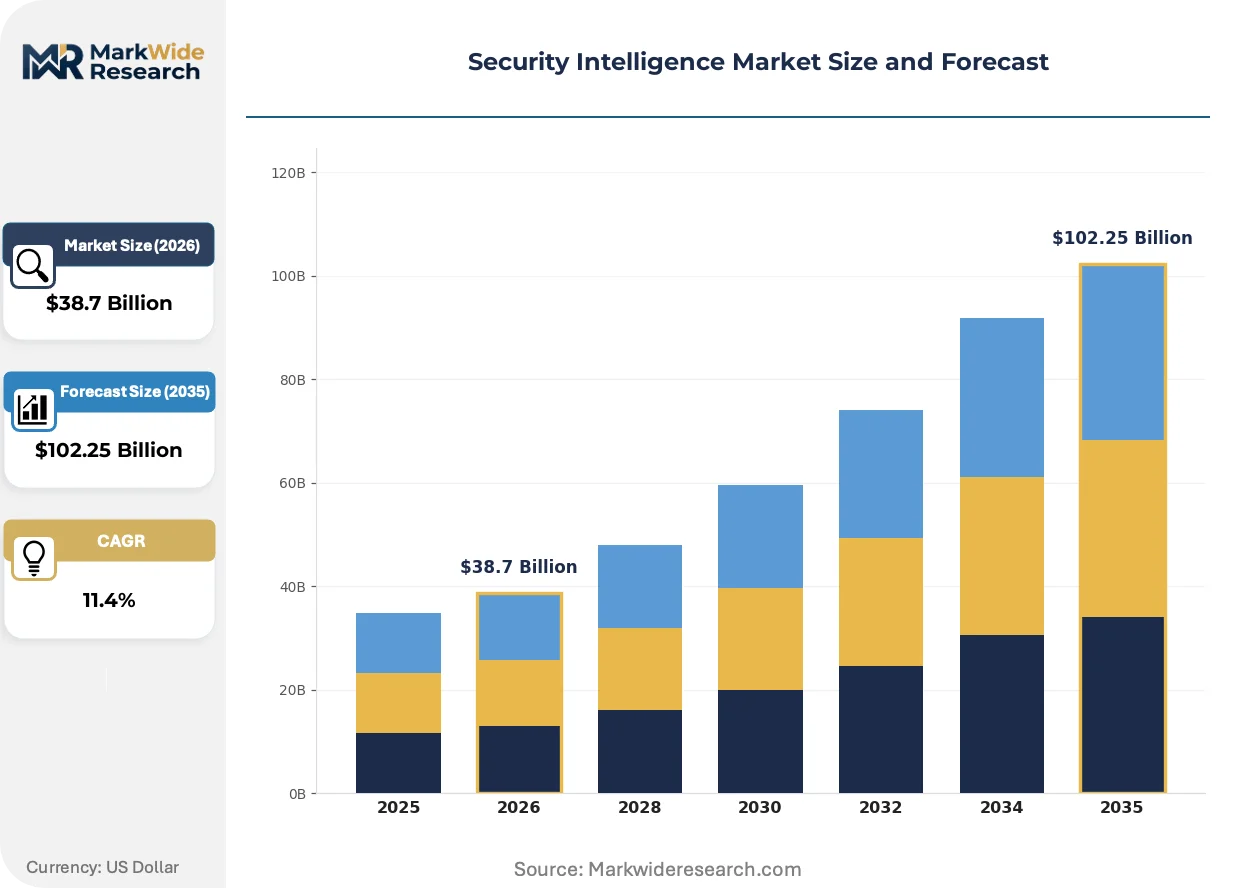
| Market Size in 2026 | $38.7 Billion |
| Market Size in 2035 | $102.25 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Private Cloud Solution Offering: Threat Detection, Incident Response, Data Analytics, Risk Management, User Behavior Analytics Application: Fraud Prevention, Network Security, Endpoint Protection, Compliance Monitoring, Insider Threat Detection End User: Information Technology Firms, Telecommunications Companies, Financial Institutions, Government Agencies, Energy Providers |
| Companies Covered | IBM, Palo Alto Networks, Cisco, CrowdStrike, Check Point Software Technologies, Recorded Future, Google, Fortinet, Trend Micro, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Intelligence Market Strategic Shifts & Innovations
Generative AI is infiltrating security operations workflows, compressing analyst investigation cycles while introducing new attack surfaces that vendors must simultaneously defend and exploit. This dual-use tension is redirecting R&D investment toward adversarial robustness and explainable detection logic.
Extended detection and response platforms with native AI-assisted investigation are displacing standalone SIEM deployments among enterprises exceeding five thousand endpoints. Financial services buyers in the United Kingdom and Germany are prioritizing these consolidated stacks to reduce mean-time-to-containment. The consolidation is compressing vendor count per security program from twelve to four primary platforms.
The SEC's cybersecurity disclosure rules for material incidents are mandating board-level visibility into threat intelligence operations. Publicly traded corporations in the United States are deploying dedicated executive dashboards translating technical indicators into business risk metrics. This regulatory pressure is accelerating procurement of natural language generation capabilities that contextualize threats for non-technical leadership.
Managed detection and response contracts with guaranteed response-time service level agreements are displacing in-house security operations center builds among mid-market healthcare and retail organizations. Buyers in Australia and Canada are favoring outcome-based arrangements over capital-intensive platform ownership. This shift is compressing traditional perpetual license revenue models toward recurring consumption-based pricing.
Security Intelligence Market Segmentation
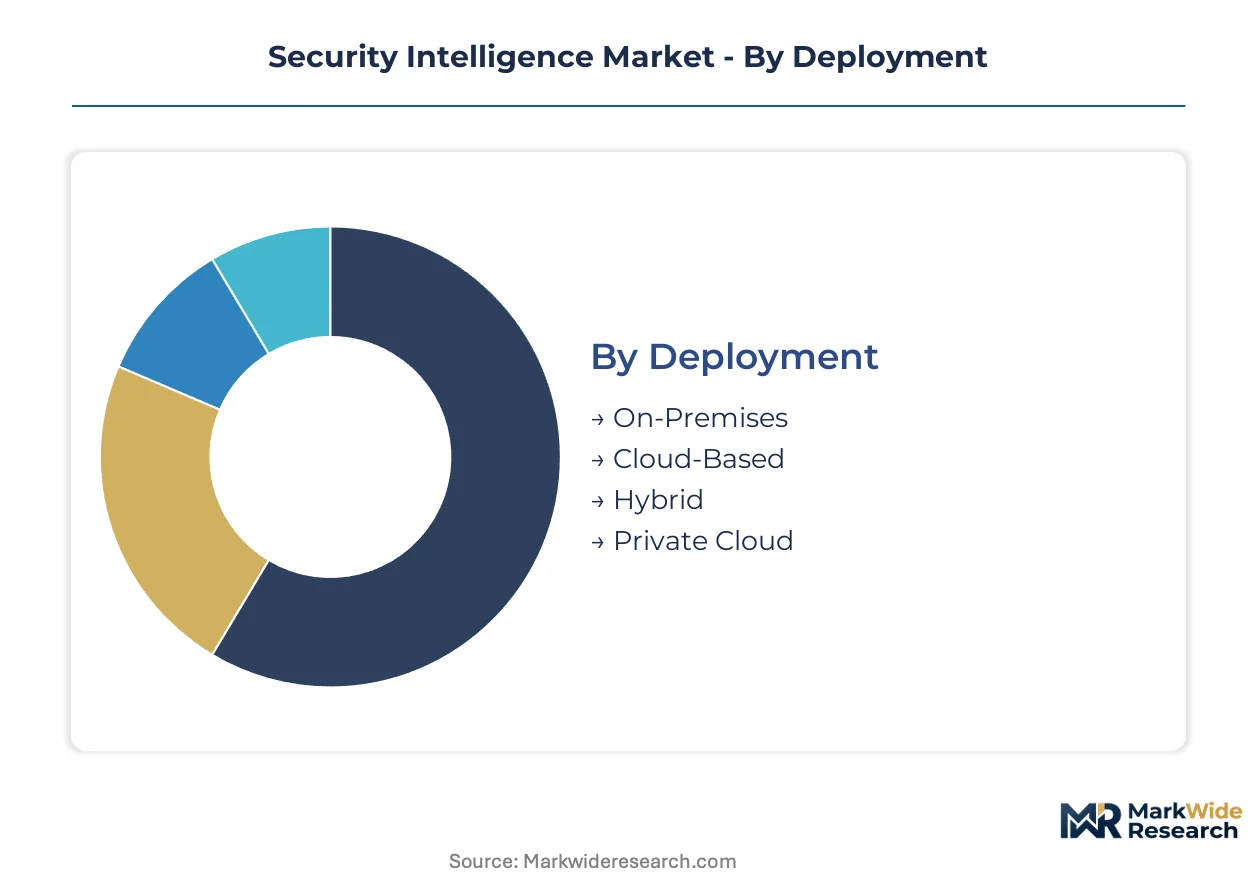
Security intelligence procurement patterns diverge sharply across deployment models and end-user maturity. Segment-specific compliance obligations and telemetry requirements reshape vendor selection criteria in each vertical.
Deployment:
Cloud-based architectures dominate North American financial services procurement, while European operators favor sovereign infrastructure. Hybrid configurations bridge legacy SIEM investments with modern analytics demands.
- Cloud-Based:Multi-tenant platforms with sub-second ingestion latencies serve mid-market enterprises lacking capital for infrastructure builds. United States healthcare systems favor these deployments for rapid SOC modernization without on-premises hardware cycles.
- Private Cloud:Single-tenant environments with dedicated compute isolation address GDPR data residency mandates. German banking consortiums and French energy operators mandate these configurations for cross-border threat data processing.
- On-Premises:Air-gapped deployments persist in classified government networks and critical infrastructure control centers.
- Hybrid:Tiered architectures with sensitive analytics on-premises and commodity processing in public cloud optimize cost for regulated manufacturers.
Cloud-based deployments hold the largest share; momentum sits with private cloud as NIS2 enforcement tightens.
Solution Offering:
Solution portfolios stratify by analyst workflow integration depth. Premium tiers bundle automated investigation playbooks; entry tiers deliver raw indicator feeds.
- User Behavior Analytics:Keystroke dynamics and entity behavioral modeling reduce insider threat false positives. Financial institutions in the United Kingdom deploy these capabilities for trader surveillance and privileged access monitoring.
- Threat Detection:Multi-source indicator fusion across SIEM, EDR, and network telemetry forms the core budget line. United States federal agencies mandate these platforms under continuous diagnostics and mitigation programs.
- Incident Response:Orchestrated containment workflows with SOAR integration accelerate mean-time-to-remediation.
- Data Analytics:Predictive risk scoring engines translate technical indicators into business impact metrics for board reporting.
- Risk Management:Quantified cyber exposure modeling aligns security investments with enterprise risk appetite frameworks.
Threat detection commands established budgets; user behavior analytics climbs the fastest as insider programs mature.
Application:
Application-specific modules concentrate development investment where procurement volumes justify dedicated engineering. Fraud prevention and endpoint protection attract disproportionate vendor R&D allocation.
- Fraud Prevention:Real-time transaction scoring with device fingerprinting and behavioral biometrics protects payment networks. Australian banks and Canadian credit unions prioritize these investments following credential stuffing campaign surges.
- Insider Threat Detection:Privileged user monitoring with data loss prevention correlation addresses intellectual property exfiltration risks. United States defense contractors deploy these capabilities under CMMC supply chain security mandates.
- Network Security:East-west traffic analysis within software-defined perimeters identifies lateral movement.
- Endpoint Protection:EDR-native threat intelligence reduces agent fatigue through automated indicator blocking.
- Compliance Monitoring:Continuous control validation against NIST, ISO 27001, and sector-specific frameworks automates audit preparation.
Fraud prevention absorbs the largest application spend; insider threat detection gains share fastest from regulatory pressure.
End User:
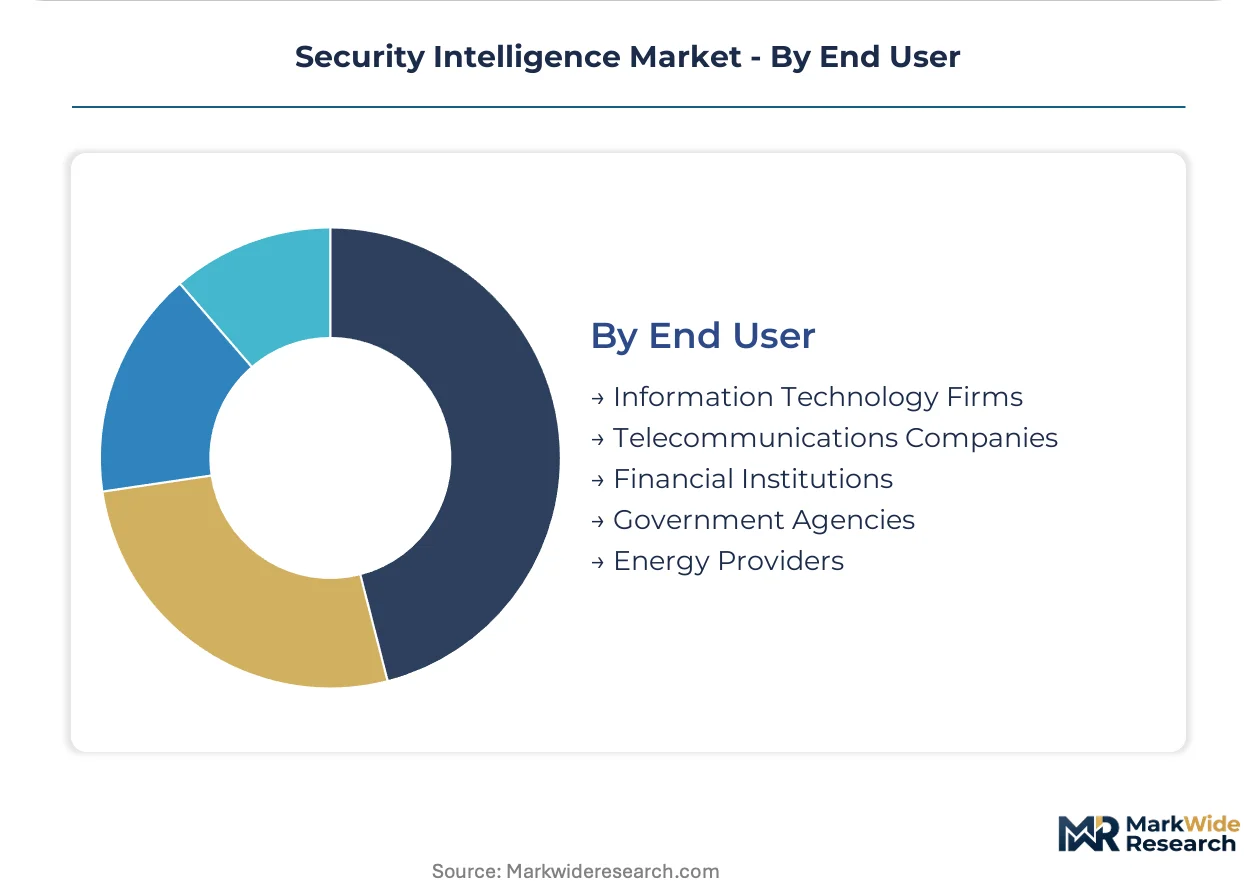
End-user procurement sophistication spans from commodity threat feeds to bespoke intelligence fusion programs. Government and financial verticals drive premium platform adoption with dedicated analyst teams.
- Financial Institutions:Real-time fraud intelligence sharing through FS-ISAC memberships complements proprietary analytics. United States banks layer behavioral biometrics atop traditional correlation to reduce authentication friction.
- Government Agencies:Classified threat actor attribution with nation-state campaign tracking demands cleared analyst workforces. Intelligence community procurement emphasizes STIX/TAXII interoperability and automated indicator distribution.
- Information Technology Firms:Managed security service providers consume bulk intelligence feeds for multi-tenant platform enrichment.
- Telecommunications Companies:Signaling network monitoring and subscriber identity protection address SS7 and Diameter protocol vulnerabilities.
- Energy Providers:OT-IT convergence security unifies ICS monitoring with enterprise SOC operations under NERC CIP obligations.
Financial institutions represent the deepest vertical; government agencies expand most quickly through defense and intelligence modernization programs.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Platform engineering talent clusters in the United States, Germany, and Israel, with cloud infrastructure density in Northern Virginia, Frankfurt, and Tel Aviv accelerating deployment velocity for native architectures.
United States
Federal cybersecurity mandates and defense spending drive platform procurement across government networks and enterprise systems. The SEC's disclosure rules for material cybersecurity incidents mandate board-level threat visibility. Northern Virginia's data center corridor hosts concentrated cloud-native security operations serving federal and financial clients.
Germany
Industrial manufacturing and automotive sectors demand OT-IT convergence security for unified operational technology monitoring. The EU NIS2 Directive tightens compliance obligations for critical infrastructure operators across member states. Bavaria's automotive engineering clusters and Baden-Württemberg's industrial automation hubs anchor specialized threat intelligence deployments.
United Kingdom
Financial services buyers prioritize consolidated extended detection and response stacks to reduce mean-time-to-containment. The National Cyber Security Centre mandates threat intelligence sharing standards for critical national infrastructure. London's financial district drives premium platform adoption with dedicated analyst teams and FS-ISAC integration.
Israel
Nation-state threat proximity cultivates advanced threat actor attribution capabilities and cleared analyst workforces. Military technology transfer programs accelerate commercial platform development. Tel Aviv's cybersecurity cluster generates specialized telemetry normalization tools for multi-cloud environments.
India
Critical information infrastructure operators face mandatory incident reporting under the BIS cybersecurity framework. The RBI and SEBI tighten financial sector cybersecurity guidelines for threat detection platforms. Bangalore's technology corridor and Mumbai's financial district drive localized platform development for domestic compliance requirements.
Security Intelligence Market Key Industry Players
Technology leadership and cost leadership are held by different player archetypes across the Security Intelligence landscape. Consolidated platform vendors with extensive firewall-to-cloud integration anchor enterprise procurement, while API-first specialists capture mid-market share through rapid deployment timelines. Three archetypes dominate: network-centric integrators, endpoint-native telemetry providers, and consolidated security fabric architects. Competitive moves concentrate on strategic partnerships with SOAR platforms and geographic expansion through localized compliance offerings.
Within the network-centric tier, Palo Alto Networks and Cisco occupy positions defined by infrastructure integration depth. CrowdStrike exemplifies the endpoint-native archetype with telemetry specialization. Fortinet anchors the consolidated fabric approach spanning hardware and software layers. IBM and Google represent cloud-scale platform providers with native AI-assisted investigation capabilities. Check Point Software Technologies and Trend Micro sit within the perimeter-defense heritage tier adapting to cloud-native demands. Recorded Future occupies a specialized position in threat actor attribution and automated indicator distribution.
| Leading Market Players |
|---|
| IBM |
| Palo Alto Networks |
| Cisco |
| CrowdStrike |
| Check Point Software Technologies |
| Recorded Future |
| Fortinet |
| Trend Micro |
| Others |
Cost & Logistics Intelligence
Take-or-pay capacity reservations with hyperscale cloud providers lock in both compute access and predictable unit economics for security intelligence platforms, compressing margin volatility for vendors serving European financial institutions under GDPR data residency mandates.
Pricing Analysis
The EU NIS2 Directive dictates the pricing tier structure across essential and important entity procurement, with mandatory threat intelligence sharing requirements pushing buyers toward premium subscription tiers bundled with automated distribution capabilities. Three-tier pricing structure across premium, standard, and economy levels separates cleared-analyst attribution services from commodity indicator feeds, with certification against ISO 27001 and SOC 2 Type II anchoring premium positioning. Pricing pressure stems from open-source MISP and OpenCTI deployments among mid-tier enterprises, forcing commercial vendors toward outcome-based consumption models. Mid-market healthcare and retail organizations exhibit highest price sensitivity, while government agencies and defense contractors prioritize capability over cost.
Supply Chain Analysis
The United States and Israel anchor threat intelligence platform engineering, with Northern Virginia and Tel Aviv clusters producing specialized telemetry normalization tools and cleared analyst workforces. Platform development draws from three critical inputs: cloud compute infrastructure, proprietary threat actor databases, and multi-source indicator ingestion pipelines. Single-source vulnerability concentrates in hyperscaler-dependent architectures, where AWS, Azure, or Google Cloud native logging format lock-in complicates multi-cloud deployments. Distribution runs through direct enterprise sales for large accounts, API-first channels for DevSecOps integration, and managed security service providers for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation opportunity persists as OT-IT convergence creates specialized deployment requirements that consolidated platform vendors struggle to address, opening niches for operational technology-native security intelligence providers.
For Market Incumbents: Secure exclusive integration partnerships with SOAR platforms and DevSecOps pipeline vendors to defend against API-first competitors compressing deployment timelines. Invest in backward integration into threat actor attribution databases to differentiate from open-source substitutes eroding attach rates in price-sensitive segments. Prioritize sovereign cloud infrastructure investments in Germany and France to preempt NIS2-aligned procurement preferences. For New Entrants and Emerging Players: Anchor in healthcare IoT telemetry, where medical device manufacturers seek firmware-embedded security intelligence agents absent from incumbent portfolios. Target the India BIS cybersecurity framework compliance segment, where mandatory incident reporting for critical information infrastructure operators creates first-mover advantage for localized platforms. Pursue API-first distribution through native SOAR and DevSecOps integration to bypass traditional reseller channel barriers. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed detection and response providers with guaranteed response-time service level agreements, as mid-market healthcare and retail organizations displace in-house security operations center builds. Long-term viability favors platforms with proven multi-cloud telemetry normalization capabilities, given structural buyer pain across AWS, Azure, and Google Cloud environments. Monitor SEC cybersecurity disclosure rule enforcement intensity as inflection indicator for executive dashboard and natural language generation capability demand.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Native SOAR and DevSecOps pipeline integration displaces traditional reseller channels for mid-market penetration. |
| Strategic Partnership | Hyperscale cloud alliances address GDPR data residency mandates for European financial institutions. |
| Acquisition of Specialist Firm | Threat actor attribution capabilities with cleared analyst workforces strengthen government agency positioning. |
| Geographic Expansion | Localized compliance offerings for India BIS framework capture mandatory incident reporting requirements. |
| Product Launch | Firmware-embedded security intelligence agents address healthcare IoT telemetry gaps in incumbent portfolios. |
Research Approach
Cross-validation between primary interviews with CISOs, SOC directors, threat intelligence analysts, and managed security service provider executives and secondary validation through SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, and FS-ISAC threat landscape reports anchors the qualitative findings. Bottom-up and top-down triangulation reconciles vendor-reported platform deployment metrics with enterprise procurement database tracking across financial services, government, and critical infrastructure verticals.
Sensitivity analysis across deployment model, organization size, vertical regulatory intensity, and integration complexity dimensions shapes the analytical framework over the projection horizon. CAGRs derive from segment-level adoption curve modeling and replacement cycle analysis, with inputs including federal cybersecurity mandate enforcement timelines and EU AI Act compliance cost estimates for automated detection systems.
Decision-makers should treat outputs as directional under sustained regulatory enforcement intensity and stable cloud infrastructure pricing; material deviation in either would warrant model refresh. Recalibration cycles align with material shifts in NIS2 implementation rigor and SEC disclosure rule precedent formation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Maritime Security Market
Security and Surveillance
Europe Security Services Market
Security and Surveillance
Destructible Security Labels Market
Security and Surveillance
Surveillance Radars Market
Security and Surveillance
5G-Enhanced Surveillance Market
Security and Surveillance
Global Traveler Security Services Market
Security and Surveillance
Lawful Interception Market
Security and Surveillance
Residential Security Market
Security and Surveillance
Global Security Assurance Market
Security and Surveillance
North America Urban Security Screening Market
Security and Surveillance
Global School and Campus Security Market
Security and Surveillance
Night Vision Scopes Market
Security and Surveillance
Underwater Security (Systems and Services) Market
Security and Surveillance
Mass Transit Security Market
Security and Surveillance
India Perimeter Intrusion Detection and Prevention Market
Security and Surveillance
Latin America Electronics Security Market