
 Global Breach and Attack Simulation Market | 2026-2036
Global Breach and Attack Simulation Market Size, Share, and Industry Trends Forecast 2026-2036
Global Breach and Attack Simulation Market Foresight
Open-source attack frameworks are recalibrating how vendors build simulation engines, compressing R&D cycles for commercial platforms. AttackIQ leverages continuous validation architectures to sustain technology leadership in automated purple-teaming workflows. Cymulate anchors its competitive position through modular breach-and-attack pathways that span network, endpoint, and cloud surfaces. SafeBreach differentiates via an extensive attack playbook library that covers documented adversary techniques across the MITRE ATT&CK matrix.
Breach and attack simulation comprises automated platforms that emulate real-world adversary tactics, techniques, and procedures against production environments without causing actual damage, typically operating through lightweight agents or agentless network probes that execute thousands of attack permutations to validate detective and preventive control efficacy. The primary commercial purpose is to provide continuous, measurable evidence of security posture gaps rather than point-in-time penetration test snapshots. Cloud-based deployment is capturing the fastest expansion as organizations prioritize elastic scalability and reduced infrastructure overhead for simulation workloads. Network simulation retains the largest solution-type footprint, though API security testing is gaining structural momentum as microservices architectures proliferate across financial institutions and technology providers.
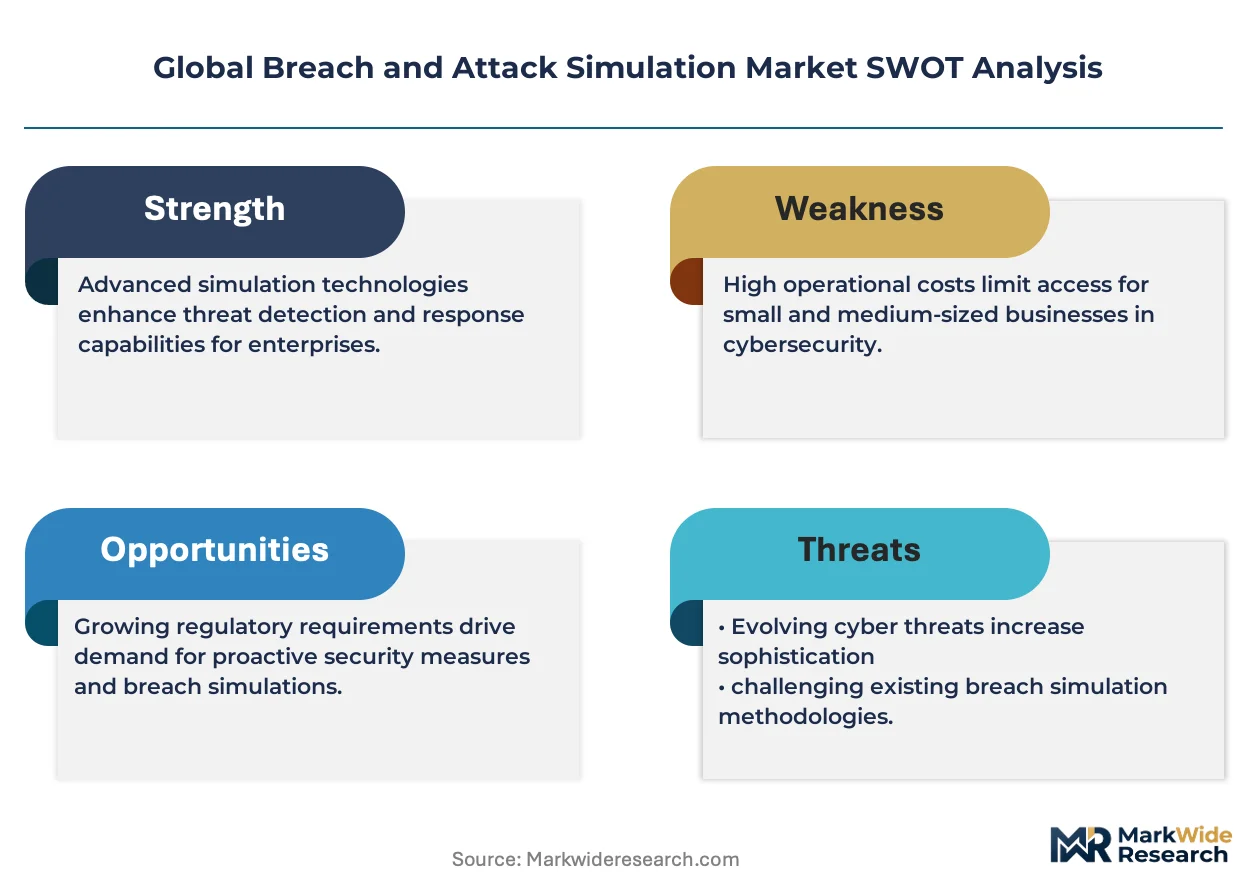
The U.S. Securities and Exchange Commission now mandates timely disclosure of material cybersecurity incidents, directly elevating demand for continuous validation evidence that boards can cite in regulatory filings. The EU NIS2 Directive expands covered entity categories and tightens incident reporting timelines, pushing European financial institutions and telecom operators toward automated compliance validation use cases. Stakeholders must monitor how converging disclosure regimes across the United States, European Union, and Japan reshape procurement criteria toward platforms that generate audit-ready documentation natively.
Market Dynamics
Continuous disclosure mandates from the SEC, EU NIS2 Directive, and Japan's cybersecurity framework are compressing procurement cycles toward platforms that generate audit-ready evidence natively. This regulatory convergence is restructuring vendor selection criteria away from point-in-time testing toward persistent validation architectures.
Growth Catalysts
- Zero-trust architecture mandates:United States federal agencies and defense contractors now require continuous control validation as a procurement precondition. Federal zero-trust strategies are forcing security teams to demonstrate persistent efficacy rather than annual compliance snapshots.
- EU NIS2 Directive:Expanded incident reporting obligations across European financial institutions and telecom operators are elevating demand for automated compliance documentation. Covered entities must validate security postures quarterly rather than annually.
- Cloud-native workload expansion:Financial services firms migrating microservices architectures require API-level simulation capabilities that legacy penetration testing cannot deliver. Elastic cloud deployment models favor agentless simulation probes over persistent endpoint agents.
Market Restraints
- Specialized talent scarcity:Purple-team expertise combining offensive security skills with defensive architecture knowledge commands premium compensation. Recruitment pipelines for adversary emulation specialists remain underdeveloped across all major markets.
- Legacy infrastructure integration friction:Mainframe and industrial control systems in critical infrastructure sectors resist agent-based deployment models. Air-gapped environments require costly on-premises simulation infrastructure that clouds cannot displace.
- Input cost volatility in cloud compute:Simulation workloads consume substantial elastic compute resources during large-scale attack permutations. Cloud provider pricing fluctuations directly compress margins for SaaS-delivered platforms.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy sectors are merging IT and OT security operations, creating demand for simulation platforms that span enterprise networks and industrial control systems. Vendors with ICS-specific attack chains can capture this whitespace.
- Japan's critical infrastructure protection framework:Designated infrastructure operators face tightened security assessment obligations. Domestic providers and global platforms with localized deployment options can establish early-mover positioning.
- API security testing integration:Microservices proliferation across German automotive and financial sectors is generating demand for simulation modules that validate OAuth, GraphQL, and REST API controls. Platforms embedding API-native attack permutations differentiate from network-centric competitors.
Industry Challenges
- Adversary technique velocity:MITRE ATT&CK matrix updates quarterly with new documented tactics. Simulation platforms require continuous content engineering to maintain coverage relevance against state-sponsored and criminal threat actors.
- False positive management at scale:Automated attack execution generates detection alerts that security operations centers must triage. Platforms lacking intelligent suppression mechanisms risk alienating buyers through alert fatigue.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Breach and Attack Simulation Market |
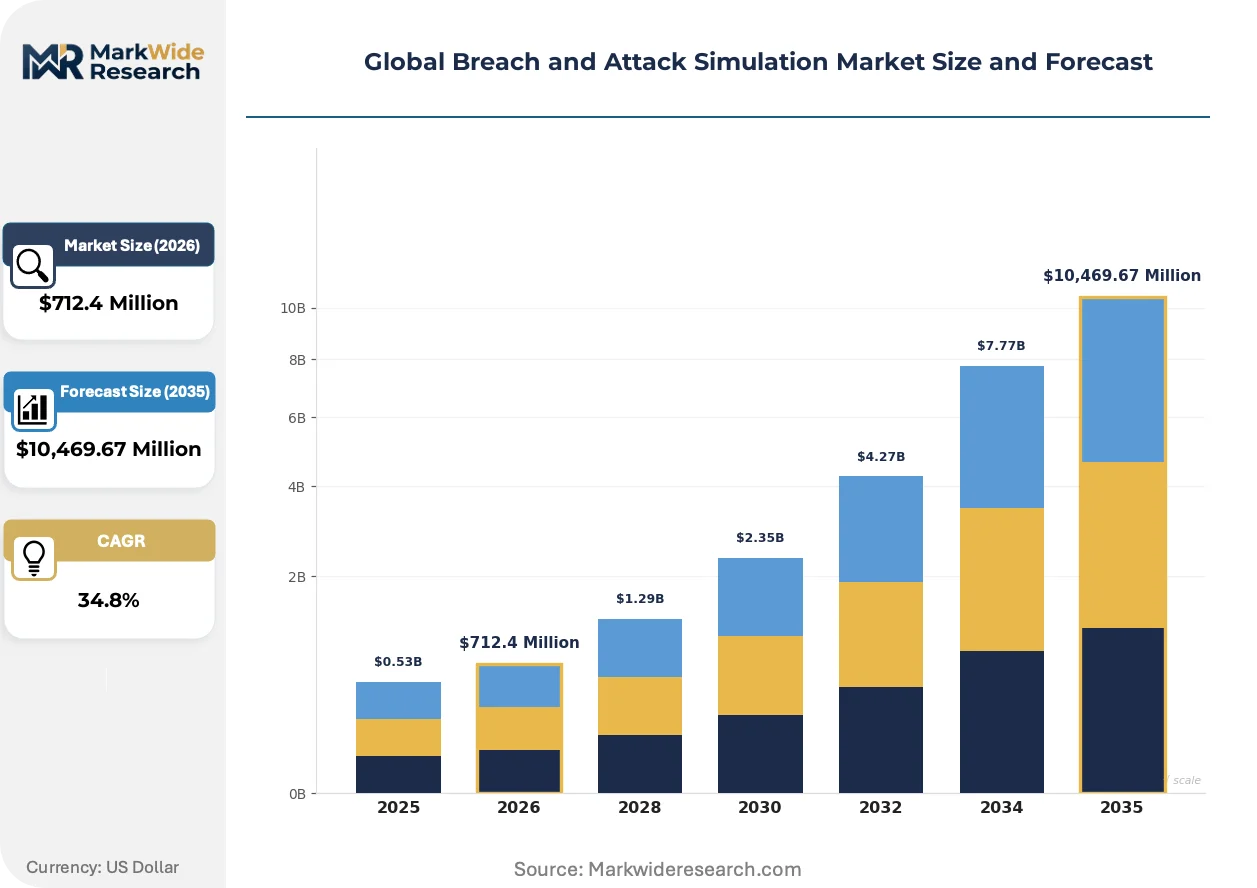
| Market Size in 2026 | $712.4 Million |
| Market Size in 2035 | $10,469.67 Million |
| CAGR (2026 – 2036) | 34.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Solution Type: Network Simulation, Endpoint Simulation, Web Application Simulation, API Security Testing Use Case: Threat Hunting, Compliance Validation, Red Teaming, Security Posture Assessment End User: Financial Institutions, Government Agencies, Telecommunication Firms, Technology Providers |
| Companies Covered | AttackIQ, Cymulate, XM Cyber, SafeBreach, Picus Security, Pentera, Qualys, Rapid7, Sophos, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Breach and Attack Simulation Market Shifts & Advancements
Agentless simulation architectures are displacing persistent endpoint deployments as organizations prioritize reduced infrastructure friction. This shift is compressing deployment timelines and expanding addressable markets toward regulated sectors with strict change-control protocols.
Large language models trained on adversary technique documentation are rewriting how simulation platforms generate novel attack chains. Financial institutions in Germany and Japan are piloting these systems to identify control gaps missed by static playbook libraries. The technology is compressing content development cycles from quarters to weeks.
The EU AI Act's risk classification framework for automated decision systems is tightening documentation requirements for AI-enabled security tools. Simulation vendors must demonstrate algorithmic transparency and human oversight mechanisms to serve European financial institutions. Compliance engineering investments are diverting R&D resources from feature expansion toward regulatory alignment.
Security procurement committees are consolidating vendor relationships around integrated validation platforms. Point solutions for network, endpoint, and cloud simulation face displacement from unified suites that reduce procurement overhead. United States enterprise buyers increasingly mandate single-platform coverage across attack surfaces to streamline budget justification and board reporting.
Global Breach and Attack Simulation Market Segmentation
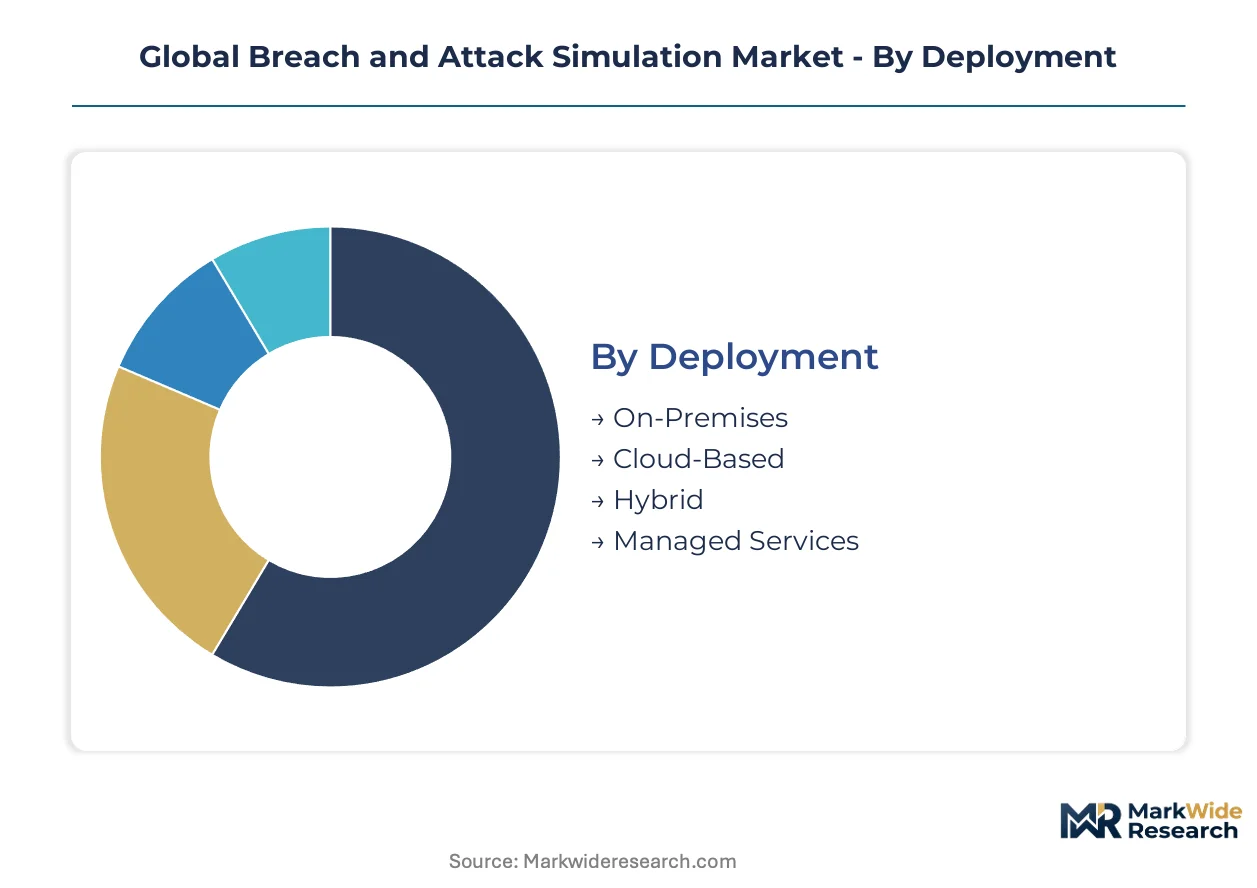
Segmentation in breach and attack simulation reveals how procurement priorities diverge across infrastructure maturity levels and regulatory exposure. Organizations replace legacy penetration testing contracts with automated validation platforms at different velocities depending on their cloud migration status and compliance obligations.
Deployment:
Upgrade cycles accelerate where legacy on-premises installations face cloud-native replacement pressure from security operations centers seeking elastic scalability.
- Cloud-Based:Agentless architectures execute simulation workloads across distributed environments without persistent endpoint footprint. Financial institutions in Germany and Japan favor this model for microservices validation where infrastructure overhead must stay minimal.
- Hybrid:Mixed deployment preserves on-premises simulation nodes for air-gapped segments while extending cloud probes to elastic workloads. Critical infrastructure operators in the United States adopt this pathway to bridge OT network isolation with IT cloud agility.
- On-Premises:Dedicated hardware installations serve classified environments and industrial control systems where external connectivity is prohibited.
- Managed Services:Third-party operated simulation platforms reduce internal purple-team staffing requirements for mid-market enterprises.
Cloud-Based sits at the top of the volume ranking, with Hybrid climbing the fastest.
Solution Type:
Margin structures favor specialized modules where technical complexity creates pricing power against commoditized network scanning tools.
- API Security Testing:Specialized probes validate OAuth flows, GraphQL endpoints, and REST authentication mechanisms against injection and broken object-level authorization attacks. German automotive manufacturers and fintech clusters drive demand as microservices architectures proliferate across connected vehicle platforms.
- Network Simulation:Core functionality emulates lateral movement, credential dumping, and command-and-control traffic across enterprise subnets. United States federal agencies mandate continuous network validation under zero-trust architecture directives.
- Endpoint Simulation:Lightweight agents or agentless execution test EDR efficacy against fileless malware and living-off-the-land techniques.
- Web Application Simulation:Automated OWASP Top Ten validation targets public-facing application layers with scheduled attack permutations.
Network Simulation retains the largest revenue base, though API Security Testing gains share fastest among solution categories.
Use Case:
Application intensity correlates with organizational security maturity, with automated compliance documentation displacing manual audit preparation in regulated sectors.
- Compliance Validation:Continuous control assessment generates audit-ready evidence for SEC disclosure mandates and EU NIS2 Directive reporting obligations. European financial institutions and telecom operators deploy this use case quarterly rather than annually.
- Threat Hunting:Proactive adversary emulation identifies detection gaps before incident response activation. United States defense contractors integrate this capability into persistent purple-team operations.
- Red Teaming:Full-scope attack simulation exercises test human response procedures alongside technical controls.
- Security Posture Assessment:Baseline measurement programs establish quantitative security metrics for board-level reporting.
Compliance Validation leads deployment volume, with Threat Hunting expanding most quickly as SOAR platform integration matures.
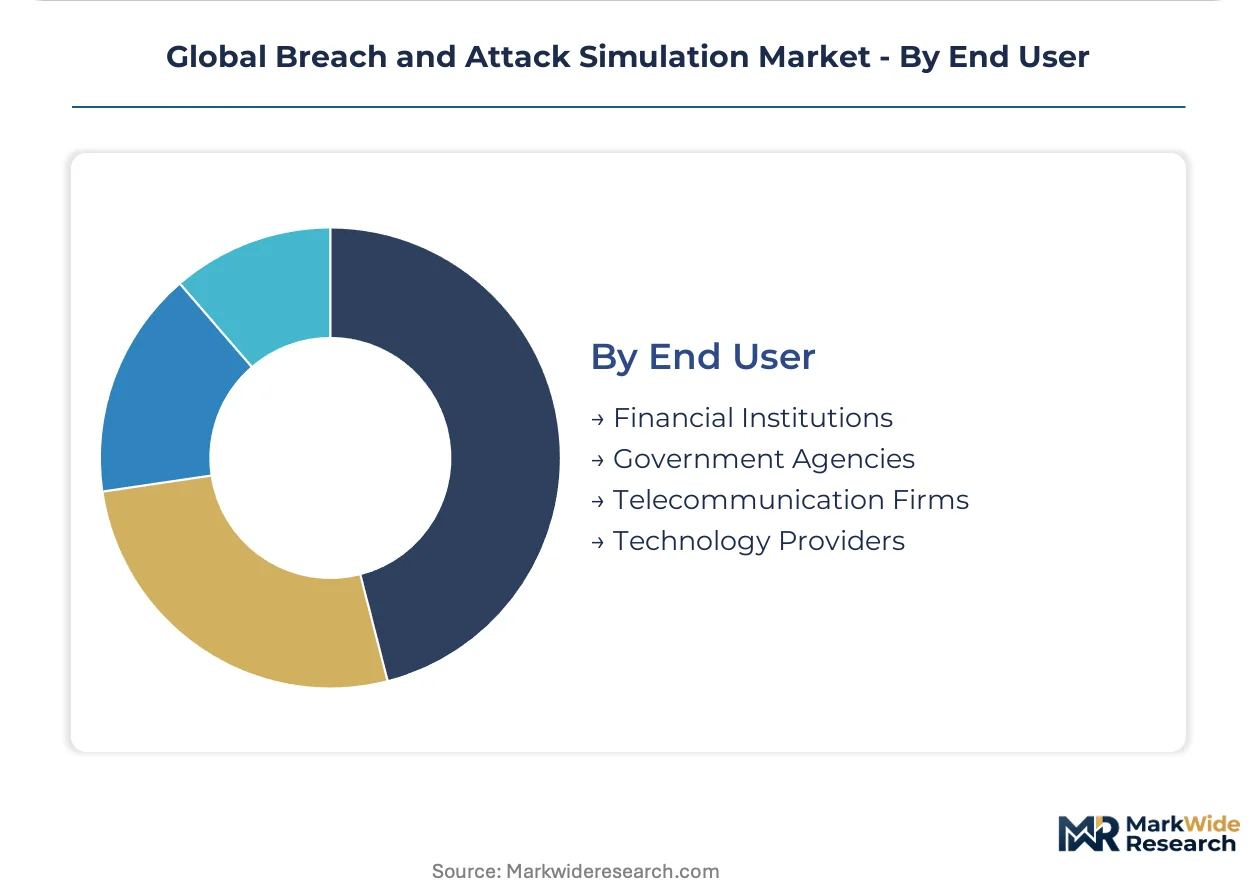
End User:
Customer concentration patterns reflect regulatory pressure gradients across critical infrastructure sectors and disclosure regimes.
- Financial Institutions:Banks, insurers, and payment processors face the strictest continuous validation requirements under SEC, EU NIS2, and Japan's cybersecurity framework. Automated evidence generation supports timely incident disclosure and quarterly board reporting.
- Government Agencies:Federal civilian and defense organizations mandate zero-trust validation as procurement precondition. United States agencies require persistent control efficacy demonstration rather than point-in-time compliance snapshots.
- Telecommunication Firms:Expanded NIS2 coverage subjects European operators to tightened security assessment and incident reporting timelines.
- Technology Providers:Cloud and SaaS vendors validate shared responsibility model controls across multi-tenant environments.
Financial Institutions occupy the highest volume position, with Government Agencies advancing fastest under federal zero-trust mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial services clusters in Frankfurt, New York, and Tokyo are driving procurement velocity for continuous security validation platforms as disclosure mandates tighten across jurisdictions.
United States
Federal zero-trust mandates and SEC disclosure rules are accelerating adoption among defense contractors and financial institutions. The Securities and Exchange Commission requires timely incident reporting that automated validation platforms support. Security operations centers in Northern Virginia and Manhattan are replacing annual penetration tests with persistent purple-team architectures.
Germany
Automotive manufacturers and fintech clusters demand API-level simulation for microservices architectures. The EU NIS2 Directive imposes quarterly security assessments on covered entities. Engineering teams in Stuttgart and Munich are integrating breach simulation into DevSecOps pipelines for connected vehicle platforms.
Japan
Designated critical infrastructure operators face tightened security assessment obligations under METI frameworks. Financial institutions in Tokyo and Osaka require localized deployment options for air-gapped segments. Domestic technology providers and global platforms compete for early-mover positioning in compliance validation use cases.
United Kingdom
Financial services regulators emphasize operational resilience testing for systemic institutions. The Bank of England and Prudential Regulation Authority scrutinize control efficacy demonstrations. London-based insurers and investment banks are consolidating vendor relationships around unified validation suites.
Singapore
Wealth management and trading infrastructure operators prioritize cloud-native simulation for elastic scalability. The Monetary Authority of Singapore mandates robust cyber risk management frameworks. Technology providers in the Marina Bay financial district are piloting agentless architectures for reduced infrastructure friction.
Global Breach and Attack Simulation Market Competitive Landscape
Global majors compete with regional champions across deployment flexibility and compliance documentation capabilities. The vendor landscape segments into three tiers: specialized pure-plays with deep adversary emulation expertise, diversified cybersecurity platforms extending into validation, and emerging regional providers with localized deployment strengths. Consolidation pressure favors integrated suites over point solutions as procurement committees reduce vendor counts. Strategic differentiation concentrates on MITRE ATT&CK coverage breadth and native audit trail generation.
Within the specialized pure-play tier, AttackIQ and Cymulate exemplify contrasting architectural philosophies—continuous validation versus modular pathway design—while SafeBreach anchors the extensive playbook library archetype. These three vendors represent distinct competitive positions: one emphasizing persistent purple-teaming workflows, another prioritizing cross-surface modularity, and the third leveraging documented adversary technique coverage. Their collective positioning illustrates how R&D investment allocation—between content engineering, platform scalability, and compliance feature development—determines market segmentation outcomes.
| Leading Market Players |
|---|
| AttackIQ |
| Cymulate |
| XM Cyber |
| SafeBreach |
| Picus Security |
| Pentera |
| Qualys |
| Rapid7 |
| Sophos |
| Others |
Supply & Pricing Matrix
Premium-mid-economy pricing differentiation across breach and attack simulation platforms reflects divergent R&D intensity and compliance engineering investments, with tier positioning tightly coupled to cloud infrastructure sourcing strategies and adversary content development pipelines. Vendors anchoring in high-automation, agentless architectures command pricing power through reduced deployment friction, while economy-tier providers compete on standardized network scanning modules with thinner margin structures.
Pricing Analysis
Elastic compute consumption in cloud-native simulation workloads passes through directly to SaaS subscription tiers, compressing margins for providers lacking reserved instance optimization. Three-tier pricing structure across premium, standard, and economy levels differentiates by MITRE ATT&CK coverage breadth and native audit trail generation capabilities. Price erosion runs through standardized network scanning modules as open-source frameworks commoditize basic attack emulation. Mid-market enterprises exhibit highest price sensitivity, while financial institutions under SEC and EU NIS2 mandates prioritize compliance documentation over cost minimization.
Supply Chain Analysis
Adversary emulation specialist availability concentrates in Israel, the United States, and the United Kingdom, where military cyber unit alumni and civilian threat intelligence clusters feed commercial platform engineering. Platform development draws from cloud infrastructure provisioning, large language model training pipelines, and continuous content engineering workflows. Single-source vulnerability in specialized purple-team talent creates recruitment bottlenecks that delay product roadmap execution. Distribution runs through direct enterprise sales teams and cybersecurity value-added resellers with compliance consulting capabilities.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The breach and attack simulation market compounds steadily as continuous validation mandates replace point-in-time compliance testing across financial and critical infrastructure sectors.
For Market Incumbents: Deepen adversary content engineering investments to maintain MITRE ATT&CK coverage velocity against quarterly matrix updates. Expand hybrid deployment architectures bridging air-gapped industrial control segments with cloud-native IT workloads. Consolidate procurement relationships by embedding native audit trail generation that satisfies SEC disclosure and EU NIS2 documentation requirements without third-party tooling. For New Entrants and Emerging Players: The gap between premium continuous validation suites and economy-tier network scanners offers white-space entry for API-native simulation modules targeting German automotive and Japanese financial microservices architectures. Operational technology convergence in manufacturing and energy sectors remains underpenetrated by incumbent cloud-centric platforms. Pursue managed services delivery models that reduce internal purple-team staffing requirements for mid-market enterprises lacking specialized talent pipelines. For Investors and Strategic Acquirers: Consolidation pressure builds where procurement committees demand unified attack surface coverage spanning network, endpoint, and cloud simulation. Platforms with fragmented point-solution positioning face displacement risk over the medium-term horizon. Monitor agentless architecture adoption rates as inflection indicator for vendor scalability and margin expansion potential.| Strategic Initiative | Industry Significance |
|---|---|
| Adversary Content Engineering Expansion | Accelerates MITRE ATT&CK coverage velocity against quarterly threat intelligence updates. |
| Hybrid Deployment Architecture Launch | Bridges air-gapped OT segments with elastic cloud probes for critical infrastructure operators. |
| Native Audit Trail Generation | Generates SEC and EU NIS2 compliant documentation without third-party compliance tooling. |
| API Security Module Development | Captures German automotive and Japanese fintech microservices validation demand. |
| Managed Services Capability Buildout | Reduces purple-team staffing barriers for mid-market enterprise market entry. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs, security operations center directors, purple-team leads, and cybersecurity procurement officers alongside secondary validation through SEC disclosure filings, EU NIS2 implementation guidance, and MITRE ATT&CK framework documentation. Bottom-up sizing of vendor bookings and top-down triangulation against enterprise security spending benchmarks anchored volume estimates.
Segment-weighting approaches distributed value across deployment models, solution types, use cases, and end-user industries, with additional stratification by regulatory exposure tier and cloud migration maturity. CAGRs derived from elasticity modeling of procurement cycle compression under disclosure mandates and zero-trust architecture directives. Forecast inputs incorporated adversary technique velocity, cloud compute pricing trajectories, and purple-team talent pipeline constraints.
Caveats apply where regulatory implementation delays, cloud provider pricing volatility, or adversary emulation talent scarcity could materially shift the outlook. Forecasts embed assumptions regarding continuous validation mandate expansion and open-source framework competitive pressure. Material deviation in named triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Vietnam Cybersecurity Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Global Online Fraud Detection and Prevention Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Domain Name System (DNS) Firewall Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Mainframe Security Market
Cybersecurity
Wireless Network Security Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
IoT Security Market