
 Global Sandboxing Market | 2026-2036
Global Sandboxing Market Size, Share, and Industry Trends Forecast 2026-2036
Global Sandboxing Market Foresight
Multi-source procurement of sandboxing engines is hardening across Fortune 500 security operations. Palo Alto Networks leverages integrated hardware-software bundles to dominate high-throughput data center deployments. Cisco Systems anchors its position through channel density and enterprise routing attach rates for cloud-delivered isolation. FireEye competes on malware intelligence fidelity, sustaining premium pricing for government and defense verticals.
Sandboxing executes suspicious code, files, and URLs within isolated virtual environments to observe behavioral indicators without risking production systems. The architecture typically employs hardware-assisted virtualization, kernel-level monitoring, and detonation chamber networks with controlled internet egress to capture full attack chains. Cloud-based deployment leads solution type revenue as elastic compute pools reduce capital intensity for variable threat volumes. Endpoint sandboxing registers the fastest expansion trajectory, driven by remote workforce device sprawl and EDR convergence requirements. Network sandboxing retains mature margin pools in carrier and ISP infrastructure, where latency-tolerant deep inspection sustains hardware refresh cycles.
The U.S. NIST Cybersecurity Framework, EU NIS2 Directive, and ISO 27001 controls collectively mandate layered execution isolation for critical infrastructure operators and regulated entities. FDA cybersecurity guidance for medical devices and FAA system safety standards extend sandboxing requirements into operational technology environments previously outside enterprise security scope. Stakeholders must weigh cloud-native versus on-premises isolation architectures against data sovereignty rulings from national regulators that fragment cross-border threat intelligence sharing.
Market Dynamics
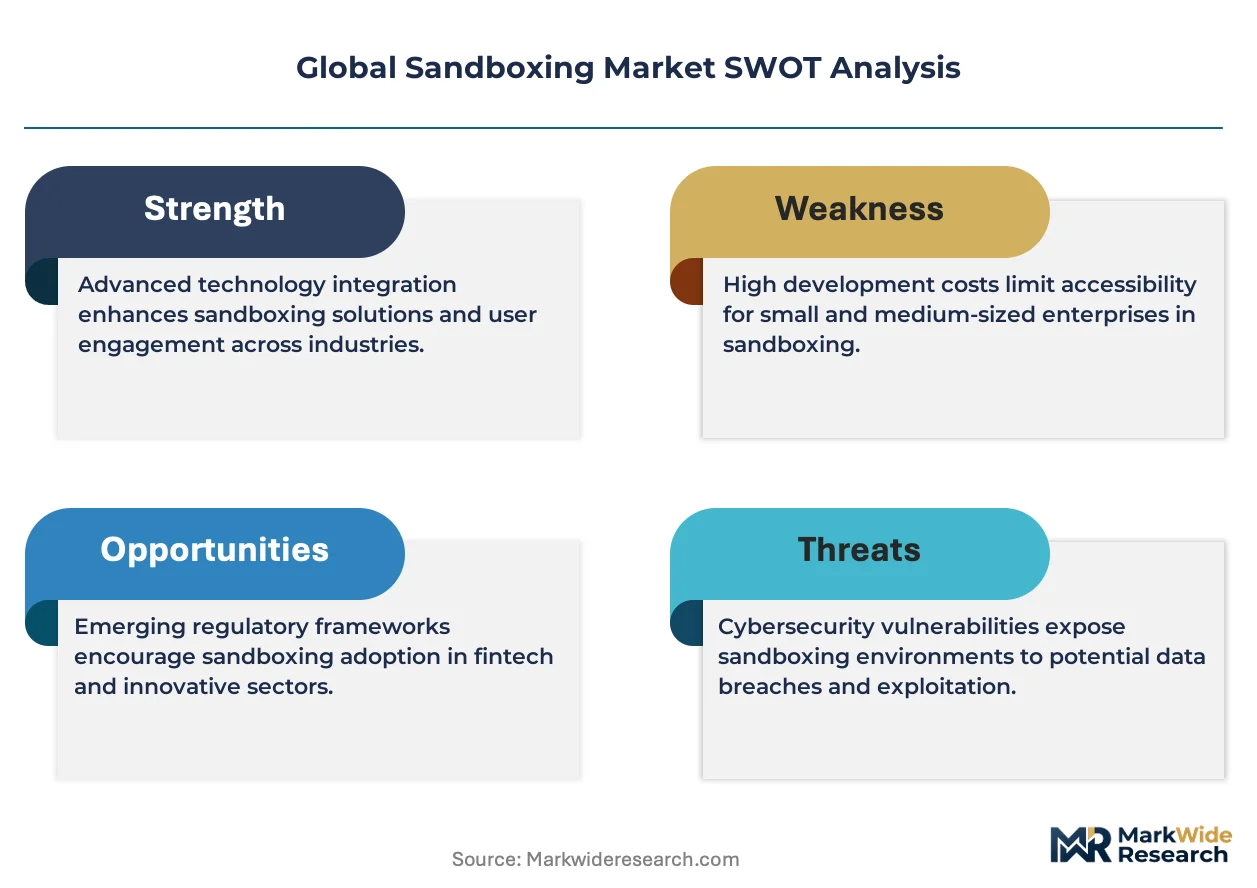
Zero-trust security mandates are compressing deployment cycles for isolation technologies as enterprises dismantle implicit trust models across hybrid infrastructure. Financial services and critical infrastructure operators now treat sandboxing as non-negotiable control layers rather than discretionary threat intelligence tools.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators across energy, transport, and healthcare must implement layered execution isolation, creating procurement pull for advanced detonation chambers with behavioral analytics.
- Cloud migration velocity:Enterprise workload redistribution into multi-tenant environments demands elastic sandboxing pools that scale with variable threat volumes without capital-intensive hardware refresh.
- Medical device cybersecurity:FDA guidance for premarket submission of connected devices mandates firmware sandboxing, extending isolation requirements into operational technology previously outside enterprise security scope.
Market Restraints
- Compute cost volatility:GPU-intensive behavioral analysis in cloud sandboxes exposes operators to hyperscaler pricing swings that erode margin predictability at scale.
- Threat intelligence fragmentation:Data sovereignty rulings from German, French, and Indian regulators fragment cross-border signature sharing, degrading detection efficacy for geographically distributed enterprises.
- Latency-versus-depth tradeoff:Carrier-grade network sandboxing cannot sustain sub-100-millisecond inspection without hardware acceleration, limiting addressable market in high-frequency trading and telco core networks.
Strategic Opportunities
- India's digital public infrastructure:UIDAI and NPCI security requirements for authentication systems create demand for sovereign-hosted sandboxing that processes biometric and payment data within national boundaries.
- EDR-sandbox convergence:Endpoint detection platforms are absorbing detonation capabilities, creating white space for vendors that unify device telemetry with cloud-isolated malware analysis.
- Operational technology expansion:IEC 62443 certification requirements for industrial control systems are pulling sandboxing into manufacturing floor networks previously isolated from IT security stacks.
Industry Challenges
- Malware analyst scarcity:Behavioral interpretation of sandbox outputs requires reverse engineering expertise concentrated in defense contractors and intelligence agencies, not commercial security operations.
- Legacy SIEM integration:Enterprises with decade-old security information platforms face API incompatibility when feeding sandbox telemetry into correlation engines, forcing expensive middleware development.
- Evasion technique arms race:Adversaries deploy sandbox-aware malware that detects virtualization artifacts and delays payload execution, forcing continuous architectural refresh of detection environments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Sandboxing Market |
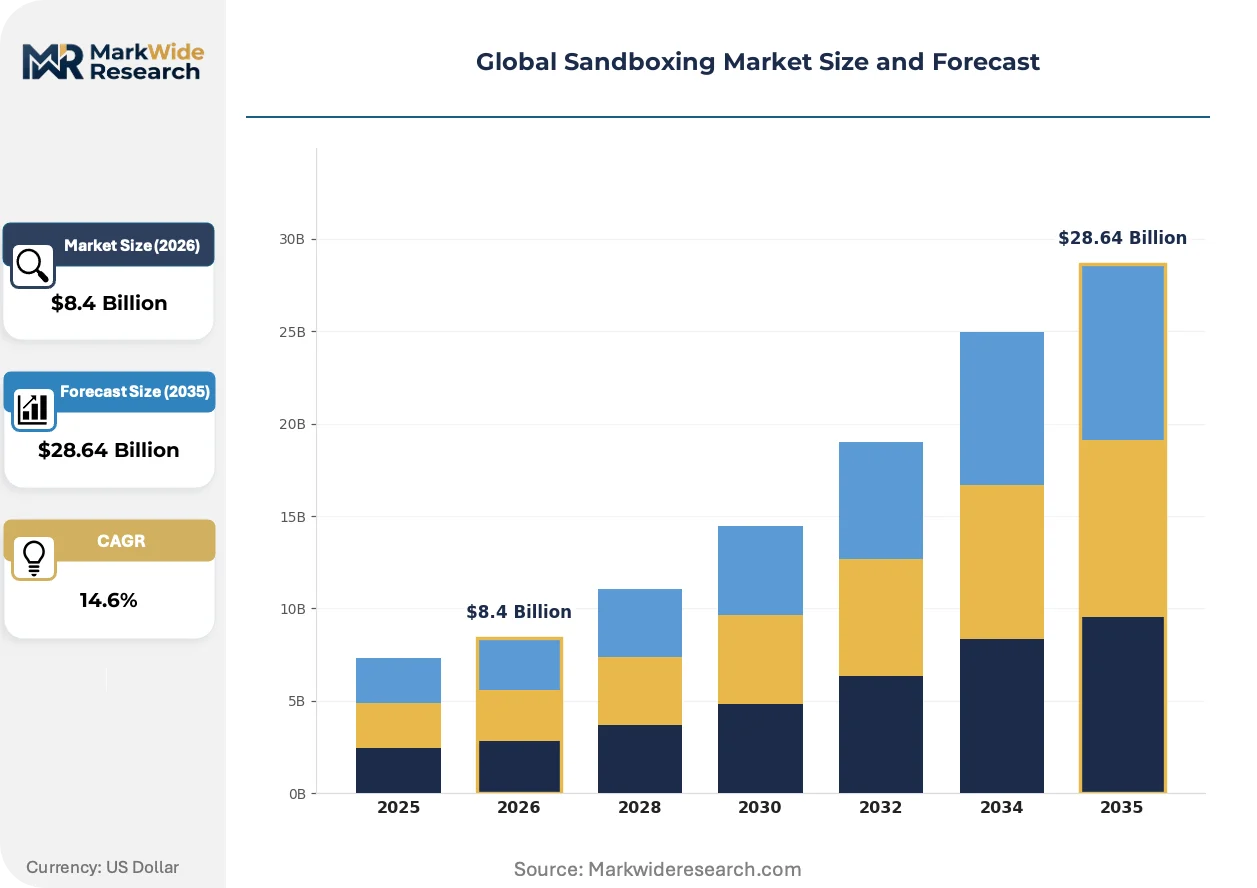
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $28.64 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Hosted, SaaS Solution Type: Network Sandboxing, Endpoint Sandboxing, Web Sandboxing, Mobile Sandboxing, API Sandboxing Application: Malware Analysis, Threat Detection, Security Testing, Forensics, Vulnerability Assessment Customer Type: Enterprises, Managed Security Service Providers, Government Bodies, Financial Institutions, Educational Institutes |
| Companies Covered | Cisco Systems, Palo Alto Networks, Fortinet, Sophos, Check Point Software Technologies, Juniper Networks, Symantec, FireEye, McAfee, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Sandboxing Market Shifts & Advancements
Isolation architectures are bifurcating between cloud-native elasticity and on-premises sovereignty as data residency rulings harden across jurisdictions. Vendors are racing to unify these deployment modes under common policy orchestration without sacrificing performance or compliance granularity.
Hardware-assisted virtualization with confidential computing extensions is consolidating trust boundaries for sandboxed execution. Financial institutions with quantitative trading operations are adopting AMD SEV-SNP and Intel TDX enclaves to process suspicious code without exposing decryption keys to the hypervisor layer. This consolidation eliminates the historical tradeoff between inspection depth and credential protection, compressing procurement cycles for high-assurance environments.
EU AI Act risk classification rules are reshaping automated threat detection procurement. Systems performing autonomous malware classification now face conformity assessment requirements for high-risk AI, forcing sandbox vendors to document training data provenance and decision explainability. Healthcare and finance verticals in Germany and France are prioritizing vendors with pre-submitted technical documentation to accelerate compliance timelines.
Security operations centers are unbundling sandboxing from bundled platform contracts. Large enterprises with mature threat intelligence functions are procuring best-of-breed detonation engines separately from endpoint and network platforms, then integrating via open APIs. This pattern is most visible in U.S. federal contracting, where FedRAMP authorization portability allows agencies to mix components from competing vendors without full-stack re-certification.
Global Sandboxing Market Segmentation
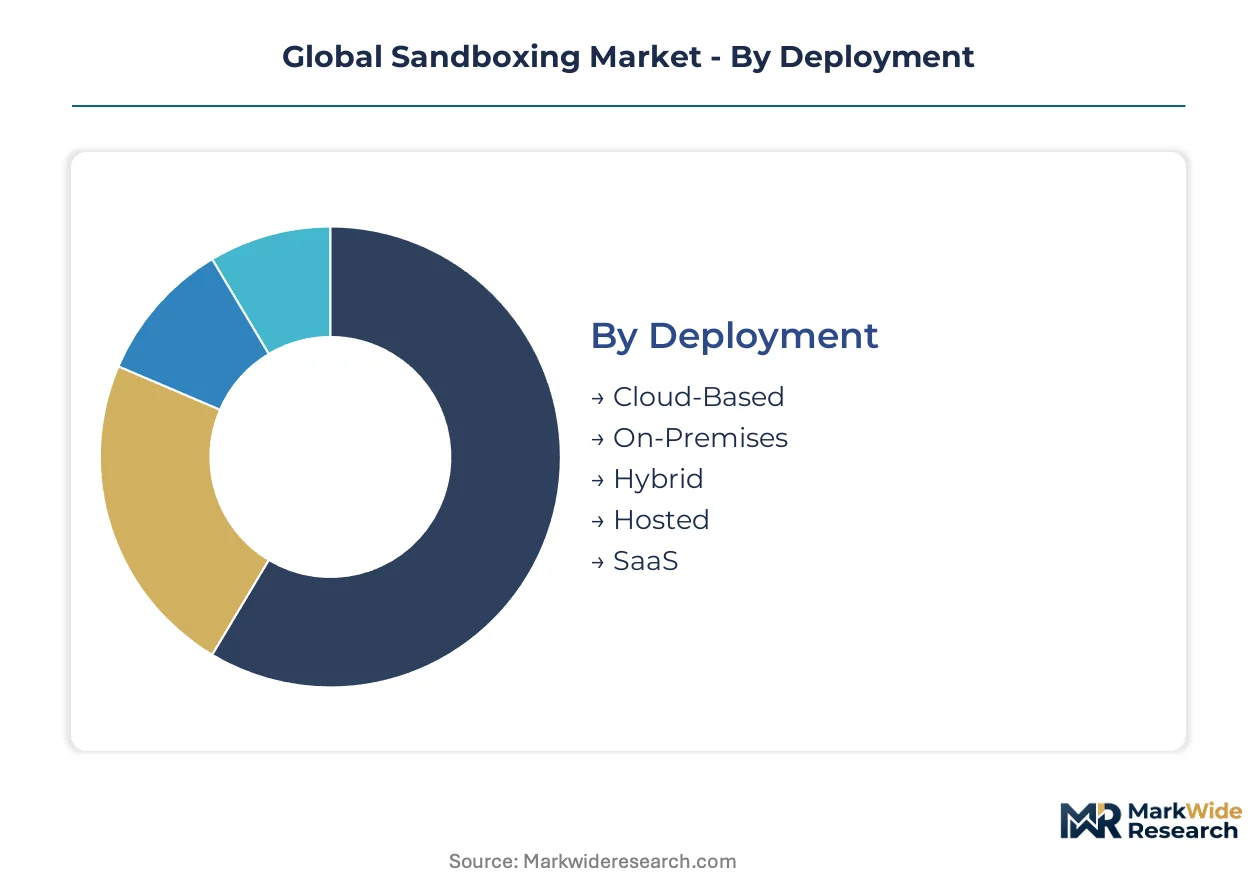
Sandboxing architectures fragment across deployment models, solution types, and operational use cases. Each dimension carries distinct margin profiles, integration complexity, and regulatory exposure that shape procurement decisions for security operations centers.
Deployment:
Standardization dominates at the elastic end of this spectrum, while sovereign requirements pull toward customized infrastructure stacks.
- Cloud-Based:Elastic compute pools isolate suspicious code without capital-intensive hardware procurement. Financial institutions in the United States favor this model for variable threat volumes during earnings cycles and merger integration periods.
- On-Premises:Air-gapped detonation chambers process classified malware samples without external connectivity. Defense contractors and German critical infrastructure operators mandate these deployments under national data sovereignty rulings.
- Hybrid:Tiered workloads split routine analysis to cloud pools while reserving sensitive samples for local execution.
- Hosted:Single-tenant appliances in third-party facilities balance control with outsourced facility management.
- SaaS:Browser-accessible sandboxes with API-first architectures enable rapid deployment for mid-market security teams.
Most installed capacity flows through Cloud-Based deployments. Expansion is steepest in Hybrid configurations as enterprises navigate data residency fragmentation.
Solution Type:
Application surface area determines architectural specialization, with network-layer inspection demanding fundamentally different latency profiles than device-bound isolation.
- Network Sandboxing:Carrier-grade appliances inspect traffic flows at peering points and ISP backbones. Deep packet inspection sustains hardware refresh cycles where latency tolerance exceeds 100 milliseconds.
- Endpoint Sandboxing:Detonation capabilities embedded within EDR agents analyze suspicious files on remote workforce devices. The convergence with device telemetry platforms drives fastest adoption across distributed enterprises.
- Web Sandboxing:Browser-isolation technologies render web content in remote containers before pixel streaming to local displays.
- Mobile Sandboxing:Containerized execution environments on iOS and Android devices isolate corporate data from personal applications.
- API Sandboxing:Microservice-specific isolation validates third-party integration payloads before production API gateway admission.
Revenue concentrates in Network Sandboxing for carrier infrastructure. Endpoint Sandboxing gains share fastest as EDR platforms absorb detonation functions.
Application:
Operational maturity separates diagnostic use cases from real-time protective functions, with distinct staffing and automation requirements.
- Malware Analysis:Reverse engineers dissect sandbox outputs to extract indicators of compromise and attribution signatures. Defense contractors and threat intelligence vendors concentrate demand for this labor-intensive function.
- Threat Detection:Automated behavioral scoring flags suspicious execution patterns for SOC analyst review. Financial institutions in the United States deploy these systems under SEC cybersecurity disclosure rules.
- Security Testing:Red teams and application security engineers validate exploitability of discovered vulnerabilities in controlled environments.
- Forensics:Post-incident reconstruction of attack chains relies on sandbox telemetry to establish timeline and lateral movement evidence.
- Vulnerability Assessment:Automated fuzzing and exploit generation test software builds before production deployment.
Threat Detection absorbs the largest deployment base. Malware Analysis expands most quickly as nation-state attribution requirements intensify.
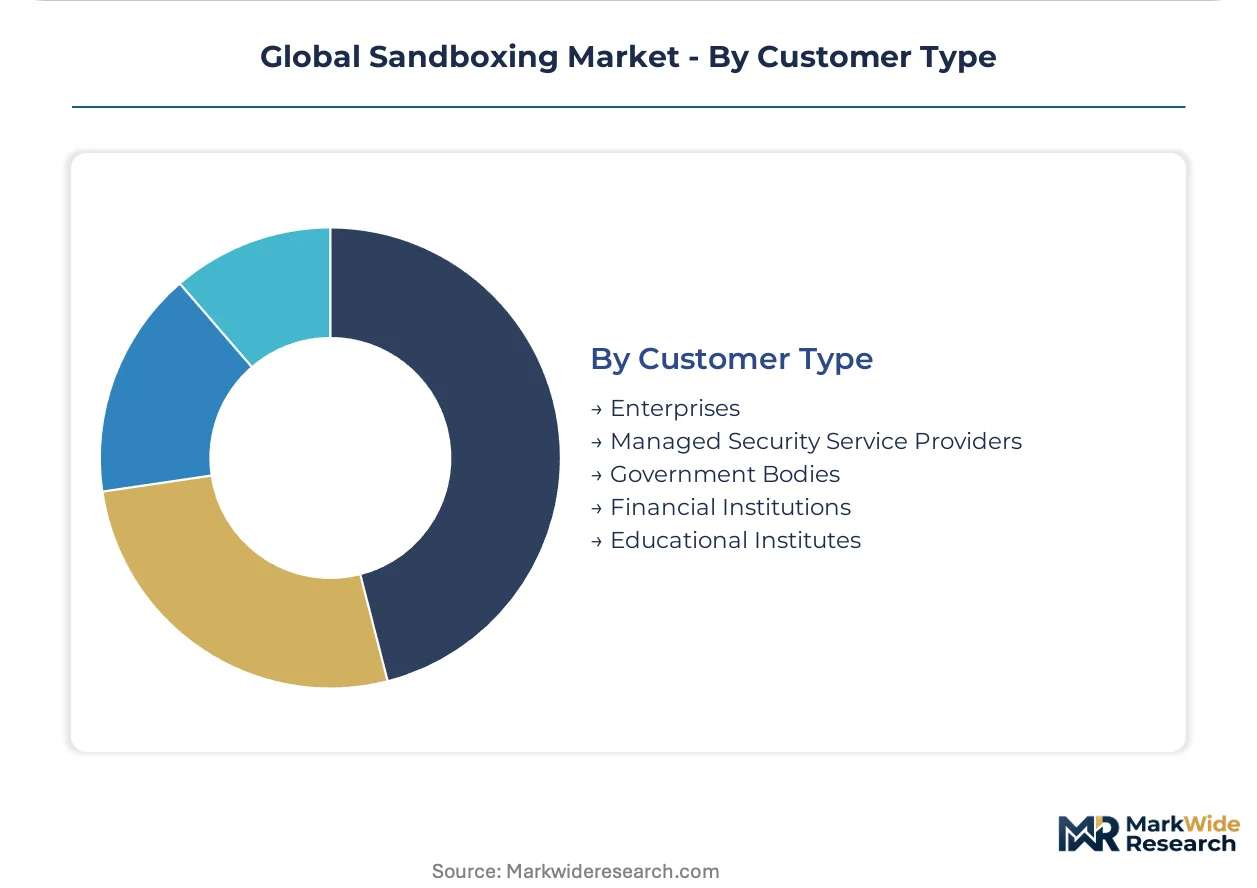
Customer Type:
Budget scale and procurement autonomy create tiered demand patterns, from centralized federal purchasing to decentralized educational procurement.
- Enterprises:Fortune 500 security operations maintain dedicated sandbox farms with custom detection rule development. Multi-source procurement of best-of-breed engines is hardening as SOCs unbundle from platform contracts.
- Managed Security Service Providers:Multi-tenant architectures serve mid-market clients without internal SOC capabilities. Elastic scaling aligns cost structures with client threat volume variability.
- Government Bodies:FedRAMP authorization requirements and classified processing mandates constrain vendor selection for U.S. federal agencies.
- Financial Institutions:Basel operational risk frameworks and PCI-DSS compliance drive layered isolation investments across trading floors and retail banking.
- Educational Institutes:Research universities deploy sandboxes for malware collection and academic cybersecurity training programs.
Enterprises command the largest installed base. Managed Security Service Providers climb fastest as mid-market outsourcing accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Washington DC-to-Boston corridor concentrates federal cybersecurity procurement and defense contractor sandboxing deployments. Regulatory fragmentation across data sovereignty rulings is reshaping vendor selection criteria. Cloud migration timelines vary dramatically by jurisdiction.
United States
Federal agencies accelerate FedRAMP-authorized sandboxing procurement under CISA zero-trust mandates. The SEC cybersecurity disclosure rules force Fortune 500 financial institutions into layered isolation investments. Silicon Valley clusters dominate cloud-native deployment innovation, while Virginia's defense corridor sustains air-gapped detonation chamber demand.
Germany
Critical infrastructure operators implement NIS2-mandated execution isolation across energy and transport sectors. The national data sovereignty framework restricts cross-border threat intelligence sharing, favoring on-premises deployments. Munich and Frankfurt financial centers drive demand for confidential computing extensions in high-assurance environments.
India
UIDAI and NPCI security requirements for authentication systems create sovereign-hosted sandboxing demand. The RBI operational risk guidelines extend isolation requirements into payment infrastructure. Bangalore and Hyderabad technology corridors absorb elastic cloud deployments, while Delhi-NCR concentrates government procurement.
United Kingdom
NCSC guidance on malware analysis capabilities shapes procurement for defense and intelligence contractors. The Financial Conduct Authority operational resilience rules mandate sandboxed testing for trading systems. London's financial district dominates high-throughput network sandboxing installations.
Japan
METI cybersecurity frameworks for critical manufacturing push sandboxing into operational technology environments. The national information security policy requires layered isolation for government systems. Tokyo and Osaka industrial clusters drive hybrid deployment architectures balancing cloud elasticity with local execution.
Global Sandboxing Market Competitive Landscape
Global majors compete with regional champions across deployment architecture and compliance specialization. The vendor base organizes around three tiers: integrated platform providers with routing and security convergence, best-of-breed detonation engine specialists, and cloud-native elasticity providers. Strategic moves center on API-first unbundling to capture SOC procurement autonomy and confidential computing partnerships to penetrate financial services quantitative trading floors.
Within the integrated platform tier, Cisco Systems exemplifies channel density strategies anchoring enterprise routing attach rates for cloud-delivered isolation. Palo Alto Networks occupies a position at the hardware-software convergence point for high-throughput data center deployments. FireEye represents the intelligence fidelity archetype, sustaining premium positioning through government and defense vertical specialization.
| Leading Market Players |
|---|
| Cisco Systems |
| Palo Alto Networks |
| Fortinet |
| Sophos |
| Check Point Software Technologies |
| Juniper Networks |
| Symantec |
| FireEye |
| McAfee |
| Others |
Supply & Pricing Matrix
Private-equity-rolled-up cybersecurity specialists have consolidated detonation engine portfolios across the United States and Israel, tightening pricing discipline through unified subscription packaging while compressing vendor diversity for enterprise procurement teams. This ownership concentration feeds directly into supply behavior, as portfolio companies share threat intelligence backends and hyperscaler contracting leverage that shapes margin allocation across cloud-native and on-premises deployment tiers.
Pricing Analysis
GPU and confidential computing hardware costs pass through directly to end-user subscription tiers, with hyperscaler pricing volatility compressing margins for behavioral analysis-intensive offerings. Pricing stratifies across FedRAMP-authorized premium tiers, standard enterprise bundles, and economy SaaS tiers for mid-market security teams. Price differentiation hinges on certification level—FedRAMP High versus Moderate—and integration depth with existing SIEM investments. Pricing pressure stems from unbundling trends as SOCs procure best-of-breed engines separately from platform contracts. Managed security service providers exhibit highest price sensitivity due to multi-tenant cost scaling, while defense contractors accept premium positioning for air-gapped sovereignty.
Supply Chain Analysis
Regional distribution centers in Ashburn, Frankfurt, and Singapore anchor hub-and-spoke delivery of sandboxing appliances and cloud edge nodes to enterprise data centers and carrier peering points. Supply concentrates in the United States for confidential computing silicon, Taiwan for advanced semiconductor packaging, and Ireland for EU data residency compliance. Raw material dependencies span AMD EPYC and Intel Xeon processors, NVIDIA GPU accelerators, and specialized network interface cards. Single-source vulnerability in confidential computing enclave technology creates concentration risk for financial services quantitative trading deployments. Distribution runs through direct enterprise sales for Fortune 500 accounts, with channel partners handling mid-market SaaS provisioning.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market compounds regulatory demand through the EU NIS2 Directive's mandatory execution isolation requirements, which pull procurement cycles forward for critical infrastructure operators across energy, transport, and healthcare verticals.
For Market Incumbents: To counter unbundling trends threatening platform attach rates, Cisco Systems and Palo Alto Networks should deepen API-first architectures that preserve integration flexibility while defending routing and security convergence positions. FedRAMP authorization portability investments will anchor federal contracting retention as agencies mix vendor components. For New Entrants and Emerging Players: Begin with India's sovereign-hosted sandboxing requirements for UIDAI and NPCI authentication systems, where data residency rulings exclude established Western vendors. Target mid-market MSSPs with elastic consumption models that align cost structures with variable client threat volumes, bypassing direct enterprise sales force requirements. For Investors and Strategic Acquirers: Valuations sit cheapest among on-premises appliance specialists with NIS2 compliance positioning but limited cloud-native elasticity, as buyers overweight SaaS growth narratives. The long-term viability window favors vendors unifying confidential computing extensions with behavioral analytics. Watch for CISA zero-trust mandate acceleration as the signal for federal procurement inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | AMD SEV-SNP and Intel TDX enclave integration eliminates hypervisor-layer credential exposure for financial trading floors. |
| FedRAMP Authorization Expansion | High baseline authorization unlocks classified processing opportunities across defense and intelligence agency deployments. |
| EDR Platform Integration | Unified device telemetry with cloud-isolated detonation captures endpoint sandboxing share fastest across distributed enterprises. |
| Sovereign Cloud Deployment | National data center partnerships in Germany, India, and UAE satisfy fragmentation in cross-border threat intelligence sharing. |
| API-First Architecture Unbundling | Open detonation engine interfaces enable SOC procurement autonomy without full-stack platform re-certification cycles. |
Research Methodology
Direct dialogue with CISOs at Fortune 500 financial institutions, federal cybersecurity procurement officers, threat intelligence vendors, and managed security service provider technical architects grounded qualitative findings in operational decision-making contexts. Secondary validation drew from CISA zero-trust implementation guidance, FedRAMP authorization databases, EU NIS2 implementation timelines, SEC cybersecurity disclosure filings, and hyperscaler infrastructure capex disclosures. Bottom-up deployment modeling across cloud, on-premises, and hybrid architectures triangulated against top-down regulatory mandate impact assessments.
Bottom-up segment sizing aggregated installed base estimates by deployment model, solution type, and customer tier, then cross-referenced against top-down IT security spending ratios from financial disclosures. Segmentation dimensions modeled encompass deployment architecture elasticity, application surface area from network to endpoint, operational use case maturity from detection to attribution, and regional regulatory cluster alignment. CAGRs derived from procurement cycle compression analysis under NIS2, FDA, and FAA mandates, with elasticity assumptions calibrated to cloud migration velocity and confidential computing adoption curves in quantitative trading.
Caveats apply where data sovereignty rulings from German, French, or Indian regulators could materially fragment cross-border threat intelligence sharing and degrade detection efficacy assumptions. Hyperscaler GPU pricing volatility and malware evasion technique acceleration present additional revision triggers. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Germany Endpoint Detection and Response Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
SSL VPN Market
Cybersecurity
Open RAN Security Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Saudi Arabia Cybersecurity Market
Cybersecurity
Data-Centric Security Market
Cybersecurity
Argentina Cybersecurity Market