
 Mobile Encryption Market | 2026-2036
Mobile Encryption Market Size, Share, and Industry Trends Forecast 2026-2036
Mobile Encryption Market Analysis
North America is reconfiguring its mobile encryption supply chain as domestic cloud infrastructure expands. IBM Corporation leverages quantum-resistant algorithm research to sustain technology leadership in government-grade mobile security. Microsoft Corporation anchors enterprise demand through seamless integration with Azure cloud encryption services. Check Point Software Technologies competes on network-layer mobile threat prevention for regulated industries.
Mobile encryption protects data at rest and in transit on smartphones, tablets, and IoT endpoints using AES-256, RSA, or elliptic curve cryptographic protocols to render information unreadable without authorized decryption keys. Device encryption dominates product type revenue as OEMs embed hardware security modules at the chipset level, while cloud-based deployment expands fastest among mid-market enterprises seeking managed key rotation without capital expenditure. Messaging encryption captures concentrated margin pools in financial services, where real-time transaction authentication demands sub-100-millisecond latency with end-to-end protection.
The FCC enforces mobile carrier security standards for voice and data interception, while the SEC mandates encrypted communications retention for broker-dealers under Rule 17a-4, and GDPR imposes breach notification thresholds that reshape European mobile app architecture. NIST zero-trust guidelines further compel federal contractors to deploy certificate-based mobile access controls. Stakeholders must weigh algorithm agility against hardware-anchored trust roots as post-quantum standards crystallize.
Market Dynamics
Post-quantum cryptography migration is compressing product lifecycles across mobile encryption hardware, forcing chipset vendors and OEMs to redesign secure elements before NIST standards finalize. This transition is reshaping R&D allocation and supplier qualification timelines industry-wide.
Growth Catalysts
- Zero-trust federal mandates:NIST guidelines for mobile endpoints are compelling defense contractors and civilian agencies to deploy certificate-based access controls, expanding addressable market for government-grade encryption modules.
- GDPR breach notification thresholds:European mobile app architects are embedding end-to-end encryption by default to avoid regulatory penalties, accelerating messaging encryption deployment across consumer and enterprise segments.
- Hardware security module integration:OEMs at the chipset level are embedding HSMs as standard features, lowering cost barriers for device encryption adoption in mid-market smartphones and IoT endpoints.
Market Restraints
- Silicon supply concentration:Secure element fabrication depends on a limited number of advanced foundry nodes concentrated in Taiwan and South Korea, creating single-source vulnerability for hardware-anchored encryption.
- Algorithm agility costs:Post-quantum cryptographic libraries require substantially larger key sizes and signature payloads, increasing computational overhead and battery drain on mobile devices.
- Cross-border data friction:GDPR data sovereignty requirements are fragmenting cloud key management architectures, forcing enterprises to maintain redundant regional infrastructure rather than unified global deployments.
Strategic Opportunities
- India digital payment expansion:RBI mandates for transaction encryption in UPI and mobile banking are creating localized demand for low-latency cryptographic accelerators in one of the world's fastest-growing smartphone markets.
- EU AI Act compliance:Automated decision systems in mobile health and financial apps must demonstrate encrypted audit trails, opening specialized consulting and managed encryption services for AI-integrated applications.
- Confidential computing convergence:Integration of trusted execution environments with 5G network slicing is enabling new service models where mobile operators offer encryption-as-a-service to enterprise verticals.
Industry Challenges
- Post-quantum talent scarcity:Cryptographic engineering expertise in lattice-based and hash-based signature schemes remains concentrated among academic institutions and national laboratories, constraining vendor hiring pipelines.
- Legacy system integration:Financial services institutions maintaining decades-old core banking infrastructure face complex middleware development to bridge modern mobile encryption protocols with mainframe-based transaction processing.
- Certification timeline compression:FIPS 140-3 and Common Criteria evaluation cycles for new secure elements now overlap with product refresh windows, risking market entry delays for next-generation devices.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Mobile Encryption Market |
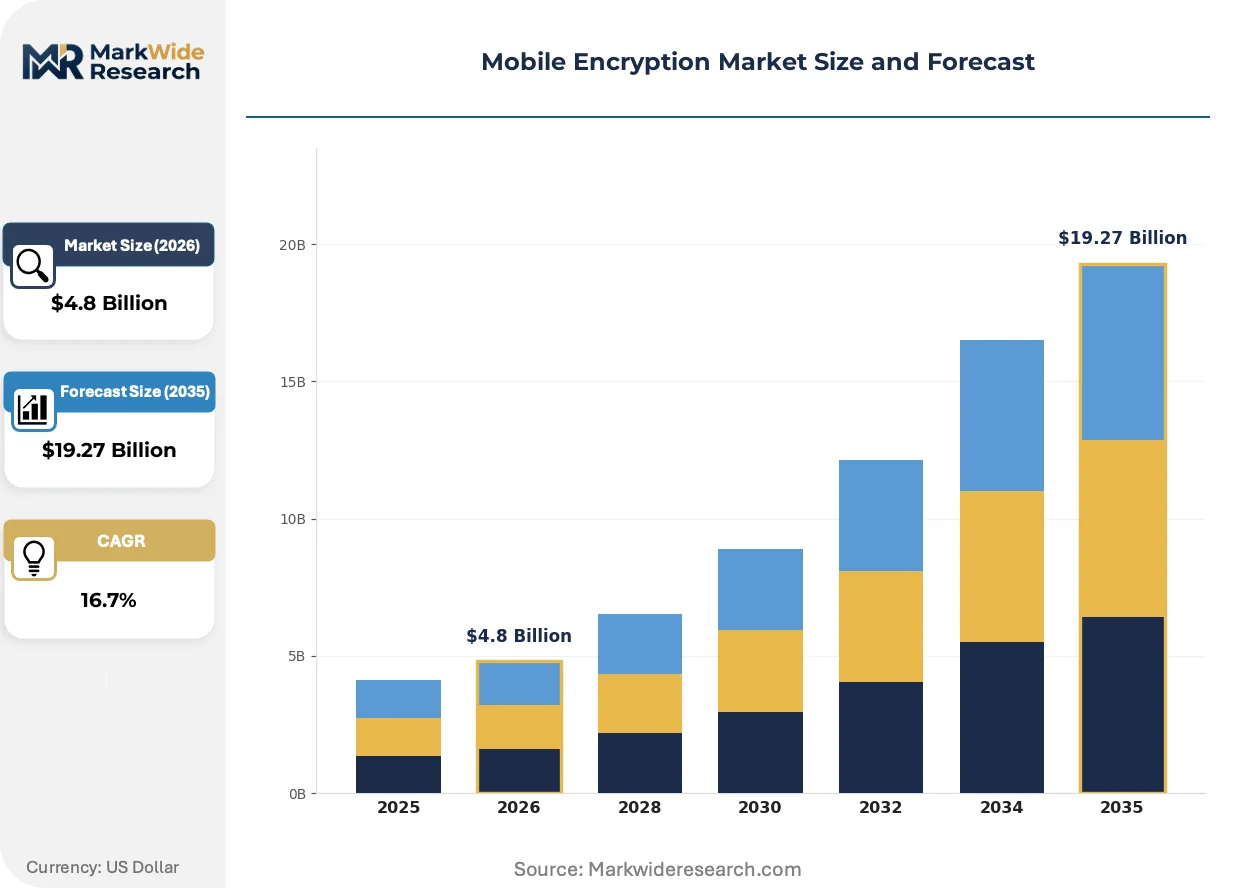
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $19.27 Billion |
| CAGR (2026 – 2036) | 16.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Device Encryption, File Encryption, Messaging Encryption, Application Encryption Technology: Encryption Algorithms, Public Key Infrastructure, Symmetric Encryption, Asymmetric Encryption End User: Consumer Electronics, Financial Services, Healthcare, Government Agencies Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services |
| Companies Covered | IBM Corporation, Microsoft Corporation, Symantec, Check Point Software Technologies, Cisco Systems, Thales Group, BlackBerry Limited, McAfee, Hewlett Packard Enterprise, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Mobile Encryption Market Emerging Trajectories
Algorithm standardization and hardware-software co-design are converging to redefine performance benchmarks for mobile security. Vendors are racing to embed quantum-resistant capabilities before regulatory deadlines crystallize.
Lattice-based cryptographic implementations are entering production silicon to defend against future quantum decryption threats. Automotive OEMs and defense contractors are qualifying these modules for 10-15 year deployment horizons. Software-only encryption stacks lacking hardware acceleration are rendering obsolete for applications demanding sub-100-millisecond authentication latency.
The EU AI Act's risk classification framework is mandating encrypted logging for high-risk automated systems in mobile health diagnostics and credit scoring. Device manufacturers must now architect tamper-evident audit trails from sensor to cloud. European medical app developers are responding by pre-integrating hardware security modules to satisfy conformity assessment requirements before products reach market.
Enterprise buyers are consolidating mobile encryption procurement under zero-trust architecture programs rather than point-product acquisitions. Managed detection and response vendors are absorbing encryption key lifecycle management into broader endpoint security subscriptions. This bundling is most pronounced in United States financial services, where CISOs face board-level pressure to demonstrate measurable attack surface reduction across mobile banking channels.
Mobile Encryption Market Segmentation
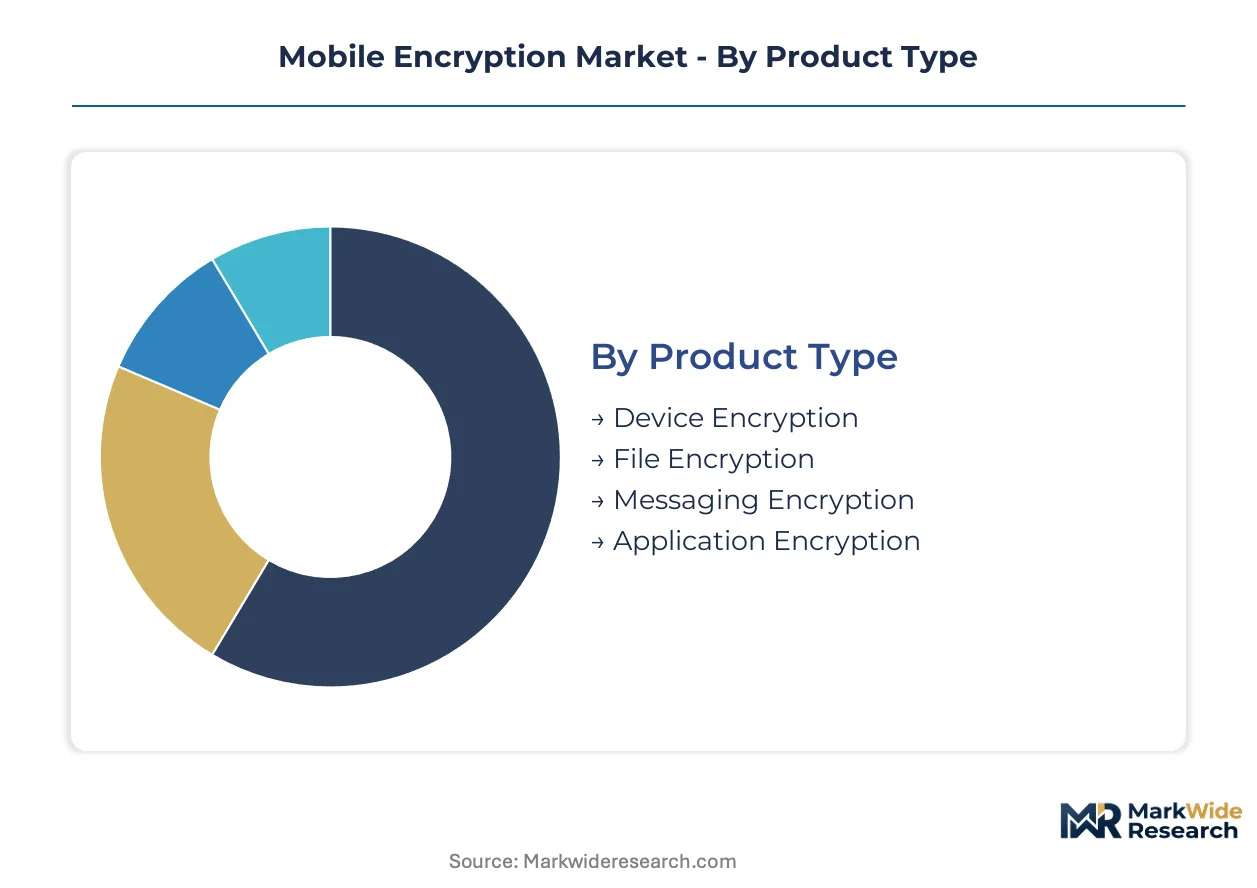
Segmentation in mobile encryption reveals divergent refresh cycles across hardware-anchored versus software-defined protection layers. OEMs embed device-level security for 3-5 year smartphone lifecycles while cloud key rotation services turn over quarterly. Understanding these temporal mismatches guides procurement timing and vendor selection strategies.
Product Type:
Refresh velocity separates this category: chipset-integrated encryption survives full device replacement cycles while application-layer deployments update monthly through over-the-air patches.
- Device Encryption:Hardware security modules embedded at the chipset level provide AES-256 protection for stored data across the full device lifecycle. Demand concentrates in United States federal procurement where NIST zero-trust mandates require FIPS 140-3 certified secure elements for contractor mobile endpoints.
- Messaging Encryption:End-to-end protocols render real-time communications unreadable without authorized decryption keys, with sub-100-millisecond latency requirements for transaction authentication. Financial services in the United States drive concentrated margin pools as SEC Rule 17a-4 mandates encrypted retention for broker-dealer communications.
- File Encryption:Container-based protection for documents and media stored locally or synchronized across devices.
- Application Encryption:SDK-integrated libraries protecting data within specific mobile apps without system-wide deployment.
Device Encryption dominates installed base. Messaging Encryption is where expansion concentrates.
Technology:
Cost tier differentiation structures supplier selection: open-standard algorithms minimize licensing burden while proprietary PKI stacks command premium service fees.
- Encryption Algorithms:Mathematical functions including AES, RSA, and elliptic curve cryptography transform plaintext into ciphertext through computational operations. Lattice-based implementations are entering production silicon as automotive and defense contractors qualify quantum-resistant modules for decade-long deployment horizons.
- Public Key Infrastructure:Certificate-based systems enabling asymmetric key distribution and identity verification across distributed endpoints. United States federal agencies anchor demand through civilian and defense contractor mandates for hardware-backed credential storage.
- Symmetric Encryption:Single-key systems offering computational efficiency for bulk data protection.
- Asymmetric Encryption:Key-pair architectures enabling secure key exchange without pre-shared secrets.
Encryption Algorithms anchor volume deployment. Public Key Infrastructure captures premium pricing.
End User:
Application criticality determines security spend: regulated industries face breach notification thresholds while consumer segments prioritize frictionless experience.
- Financial Services:Real-time transaction protection and communications retention for regulatory compliance. GDPR breach notification thresholds across European operations accelerate default end-to-end encryption deployment.
- Government Agencies:Classified and controlled unclassified information protection with supply chain security requirements. United States defense contractors face compressed certification timelines as FIPS 140-3 evaluation cycles overlap product refresh windows.
- Healthcare:Patient data protection across mobile diagnostic and telemedicine platforms.
- Consumer Electronics:Baseline privacy features for smartphone and IoT device manufacturers.
Financial Services drives compliance-driven procurement. Government Agencies sets technical specifications.
Deployment:
Customer IT maturity separates adoption patterns: capital-constrained mid-market enterprises favor operational expenditure models while regulated entities retain on-premises control.
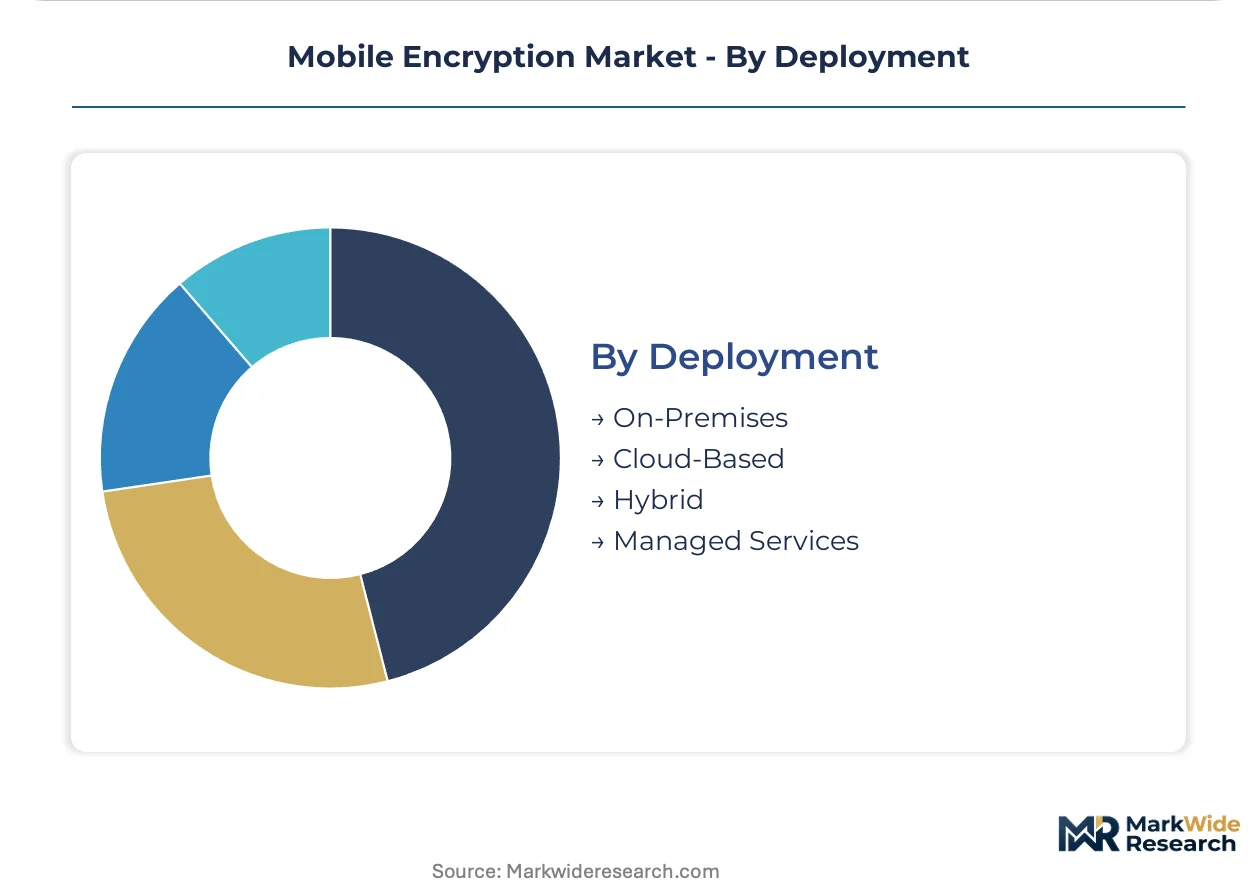
- Cloud-Based:Managed key lifecycle services eliminating capital expenditure for hardware security infrastructure. Mid-market enterprises across United States financial services consolidate procurement under zero-trust architecture programs.
- Managed Services:Outsourced encryption operations including key rotation, certificate management, and compliance reporting. European medical app developers pre-integrate hardware security modules to satisfy EU AI Act conformity assessment requirements.
- On-Premises:Organization-controlled hardware security modules and key management servers.
- Hybrid:Split architectures retaining sensitive key material on-premises while leveraging cloud for policy distribution.
Cloud-Based deployment is expanding most quickly among new adopters. Managed Services captures recurring revenue concentration.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
NIST zero-trust guidelines and FIPS 140-3 certification mandates anchor United States federal procurement, creating concentrated demand for hardware-anchored encryption modules across defense contractors and civilian agencies.
United States
Defense contractors and financial institutions drive device encryption procurement as SEC Rule 17a-4 mandates encrypted communications retention for broker-dealers. The FCC enforces carrier security standards for voice and data interception. Silicon Valley clusters concentrate quantum-resistant algorithm development for government-grade mobile endpoints.
Germany
Automotive OEMs qualify lattice-based cryptographic modules for decade-long vehicle deployment horizons. The KBA coordinates type approval for connected car security systems. Stuttgart and Munich anchor production of secure elements for industrial IoT and autonomous driving platforms.
India
RBI mandates for UPI and mobile banking transaction encryption create localized demand for low-latency cryptographic accelerators. The central bank's digital payment infrastructure push drives smartphone security integration. Bengaluru and Hyderabad concentrate fintech development requiring hardware-backed key protection.
United Kingdom
Financial services firms embed end-to-end messaging encryption to satisfy GDPR breach notification thresholds across European operations. The Information Commissioner's Office enforces data sovereignty requirements for cross-border mobile communications. London's regulatory technology clusters specialize in compliance-integrated encryption services.
South Korea
Advanced foundry nodes for secure element fabrication concentrate manufacturing capacity for hardware-anchored encryption. The MFDS coordinates medical device security standards for mobile health diagnostics. Seoul anchors semiconductor R&D for post-quantum cryptographic silicon integration.
Mobile Encryption Market Vendor Landscape
Cloud-native platforms and hardware-anchored specialists split the market along deployment architecture lines. The vendor base organizes into three tiers: enterprise software conglomerates with encryption-as-a-service portfolios, semiconductor OEMs embedding secure elements at chipset level, and cybersecurity pure-plays competing on threat prevention integration. Dominant competitive moves include strategic partnerships between cloud operators and hardware security module vendors, plus portfolio diversification into managed key lifecycle services.
Among enterprise software conglomerates, IBM Corporation and Microsoft Corporation occupy positions exemplifying divergent strategic vectors. IBM Corporation represents the hardware-anchored trust root archetype through quantum-resistant algorithm research and government-grade security module development. Microsoft Corporation anchors the cloud-native deployment model, integrating encryption services with broader enterprise infrastructure subscriptions. Check Point Software Technologies sits within the network-layer specialization tier, competing on mobile threat prevention for regulated industries requiring sub-100-millisecond authentication latency.
| Leading Market Players |
|---|
| IBM Corporation |
| Microsoft Corporation |
| Symantec |
| Check Point Software Technologies |
| Cisco Systems |
| Thales Group |
| BlackBerry Limited |
| McAfee |
| Hewlett Packard Enterprise |
| Others |
Supply Flow & Price Mechanics
Single-source dependency on Taiwan and South Korea for secure element fabrication compresses pricing tier spreads while forcing buyers into long-term offtake commitments to secure allocation. This concentration simultaneously elevates premium pricing for FIPS 140-3 certified modules and constrains economy-tier supply as foundry capacity prioritizes defense contractor demand.
Pricing Analysis
United States federal procurement commands 40-60% premiums over European enterprise pricing for identical hardware security modules due to FIPS 140-3 certification requirements and domestic content preferences. Three-tier pricing structure across government-grade, enterprise-managed, and consumer-embedded levels separates buyers by compliance burden rather than unit economics alone. Cost compression in the mid-market tier is intensifying because cloud-based key management services displace capital-intensive on-premises deployments. Financial services CISOs exhibit lowest price sensitivity given SEC Rule 17a-4 liability exposure, while mid-market SaaS vendors prioritize per-seat subscription models to minimize upfront commitment.
Supply Chain Analysis
Export-control regimes limiting quantum-resistant cryptographic IP flows between United States defense contractors and allied fabrication partners are fragmenting supplier qualification timelines. Advanced foundry capacity concentrates in Taiwan and South Korea, with trailing-edge secure element production anchored in China for consumer IoT endpoints. Raw material dependencies span silicon wafers, rare-earth dopants for tamper-resistant packaging, and specialized photoresists for sub-7nm node production. Single-source vulnerability permeates the ecosystem as 90% of certified secure element capacity rests with three foundry groups. Distribution runs through tier-one semiconductor distributors serving OEMs directly, bypassing traditional IT channel intermediaries for hardware-anchored encryption modules.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Mobile encryption sits at an early-cycle expansion story as zero-trust federal mandates and post-quantum migration timelines compress replacement windows across installed infrastructure. Hardware-software co-design investments are accelerating as vendors race to embed NIST-standardized algorithms before certification deadlines crystallize.
For Market Incumbents: Insulate government-grade revenue streams by securing FIPS 140-3 pre-certification for lattice-based secure elements before competitor qualification cycles complete. Deepen backward integration into trusted foundry partnerships to mitigate Taiwan concentration risk, while expanding managed key lifecycle services to capture recurring revenue from cloud-native mid-market adopters displacing capital expenditure models.
For New Entrants and Emerging Players: Pursue white-space opportunities in India digital payment infrastructure where RBI mandates for UPI transaction encryption outpace local hardware security module supply. Target mid-market European healthcare developers facing EU AI Act conformity assessment requirements for encrypted audit trails in mobile diagnostic applications, leveraging SDK-integrated application encryption to bypass chipset-level incumbent dominance.
For Investors and Strategic Acquirers: The market sits at a standards-transition phase that favors cryptographic engineering talent concentration over brand equity. Long-term viability across the next decade hinges on post-quantum algorithm agility and government certification track records rather than current revenue scale. Acquisition targets should display lattice-based implementation expertise and active Common Criteria evaluation pipelines. The signal to watch is NIST finalization timelines for quantum-resistant standards, which will trigger immediate procurement acceleration among defense contractors and financial institutions.
| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Algorithm Integration | Lattice-based cryptographic modules defend against future quantum decryption threats for automotive and defense deployment horizons. |
| Hardware Security Module Pre-Certification | FIPS 140-3 evaluation cycles overlapping product refresh windows risk market entry delays without advance planning. |
| Managed Encryption Service Expansion | Cloud-based key lifecycle management captures recurring revenue from mid-market enterprises consolidating zero-trust procurement. |
| Confidential Computing Convergence | Trusted execution environment integration with 5G network slicing enables encryption-as-a-service offerings to enterprise verticals. |
| Regional Data Sovereignty Architecture | GDPR-compliant cloud key management infrastructure addresses fragmented European requirements without unified global deployments. |
Methodological Framework
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with mobile security architects at financial institutions, chipset vendor product managers, federal procurement officers, cloud platform engineers, and regulatory compliance leads at healthcare developers. Secondary validation drew from NIST cybersecurity framework publications, SEC regulatory filings, EU AI Act implementation guidance, semiconductor foundry capacity disclosures, and hyperscaler encryption service documentation. Bottom-up sizing of hardware security module shipments was triangulated against top-down enterprise IT security spending allocation surveys.
Calibration against historical adoption curves for predecessor encryption standards informed penetration assumptions across the projection horizon. The analytical framework modeled segmentation dimensions including deployment architecture, end-user industry vertical, certification tier, and regional regulatory cluster. CAGRs were derived from installed base replacement cycles, zero-trust mandate compliance deadlines, and post-quantum algorithm standardization timelines. Forecast inputs incorporated foundry capacity expansion announcements, federal procurement budget authorizations, and mobile banking transaction volume trajectories.
Sensitivities concentrate around NIST post-quantum standardization delays, Taiwan foundry disruption scenarios, and GDPR enforcement intensity variations across European member states. Forecasts reflect assumptions regarding algorithm migration timelines and hardware refresh synchronization that could revise materially if regulatory deadlines shift or supply concentration eases. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Web Filtering Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Israel Cybersecurity Market