
 Deception Technology Market | 2026-2036
Deception Technology Market Size, Share, and Industry Trends Forecast 2026-2036
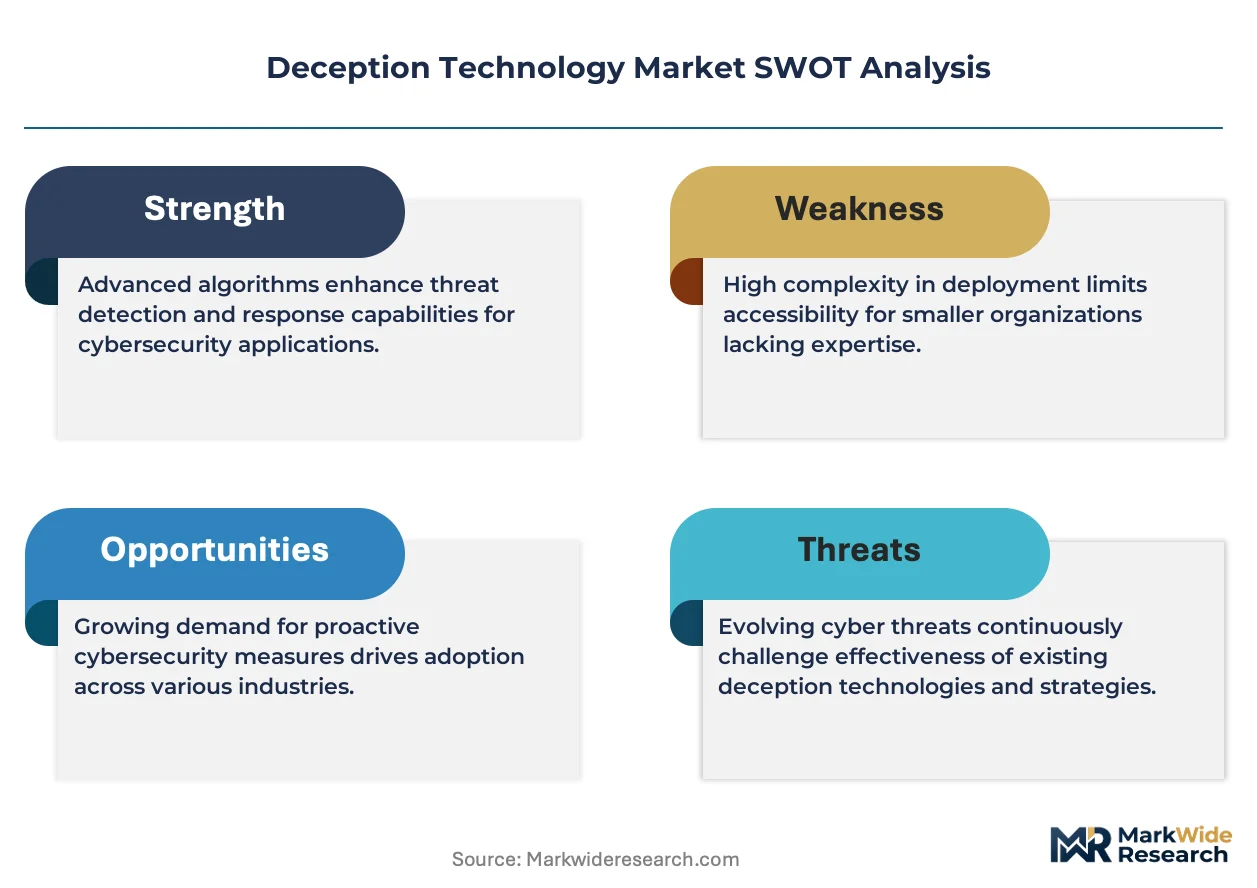
Deception Technology Market Analysis
A shortage of adversarial simulation specialists is redrawing competitive boundaries across the deception technology landscape. Rapid7, Inc. leverages its managed detection and response footprint to embed deception layers into existing security operations. Attivo Networks, Inc. anchors its position through deep credential and Active Directory deception capabilities. Illusive Networks specializes in agentless endpoint decoys that reduce deployment friction for enterprise buyers.
Deception technology deploys synthetic assets, decoy credentials, and behavioral lures to detect, divert, and analyze attacker movements within enterprise networks. The technology operates through distributed sensor grids that emulate authentic systems while isolating intruders from production environments. Network deception captures the largest share of current deployments as perimeter architectures fragment. Cloud-based delivery is expanding fastest where elastic infrastructure lets security teams spin decoy environments on demand. AI-based detection layers command premium pricing by reducing false positives that plague rule-driven alternatives.
NIST, ISO 27001, and sector-specific mandates from HIPAA shape product requirements by mandating continuous monitoring and documented incident response capabilities. The SEC's cybersecurity disclosure rules for publicly traded firms directly expand budget allocation toward active defense technologies. Buyers must weigh vendor telemetry integration against the operational burden of maintaining convincing decoy ecosystems.
Market Dynamics
Zero-trust architecture mandates from the US federal government are compressing sales cycles and forcing vendors to integrate deception layers into existing security stacks rather than standalone deployments.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Publicly traded firms must report material security incidents within four business days, accelerating budget allocation toward active detection technologies that shorten breach identification timelines.
- Healthcare Data Protection:HIPAA enforcement actions against covered entities for insufficient access controls are driving hospital systems to deploy credential deception to trap unauthorized internal lateral movement.
- Cloud-Native Infrastructure:Elastic compute environments enable security teams to instantiate ephemeral decoy workloads that automatically scale with production systems, reducing per-deployment operational overhead.
Market Restraints
- Specialized Talent Scarcity:Adversarial simulation expertise concentrates among practitioners with offensive security backgrounds, constraining vendor delivery capacity and inflating implementation costs.
- Decoy Maintenance Burden:Convincing deception ecosystems require continuous refresh of synthetic assets to avoid attacker recognition, creating persistent operational overhead that erodes ROI calculations.
- Rule-Driven Alert Fatigue:Legacy SIEM integrations without AI-based correlation layers generate excessive false positives, causing security operations centers to deprioritize deception-generated telemetry.
Strategic Opportunities
- Operational Technology Convergence:Industrial control systems in manufacturing and energy lack native deception capabilities, creating white space for vendors that adapt decoy protocols to Modbus and DNP3 traffic patterns.
- Managed Deception Services:Mid-market enterprises without dedicated threat hunting teams represent an underserved segment for fully managed deception-as-a-service offerings with guaranteed detection SLAs.
- EU NIS2 Directive:Expanded incident reporting obligations for critical infrastructure operators across European member states will mandate continuous network monitoring, directly expanding addressable demand for deception-based detection.
Industry Challenges
- Attivo-Illusive Integration Complexity:Organizations running heterogeneous deception estates from multiple vendors face telemetry normalization challenges that fragment incident response workflows.
- NIST 800-207 Certification Timelines:Zero-trust architecture compliance validation for federal contractors requires documented deception deployment patterns that extend procurement cycles by six to twelve months.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Deception Technology Market |
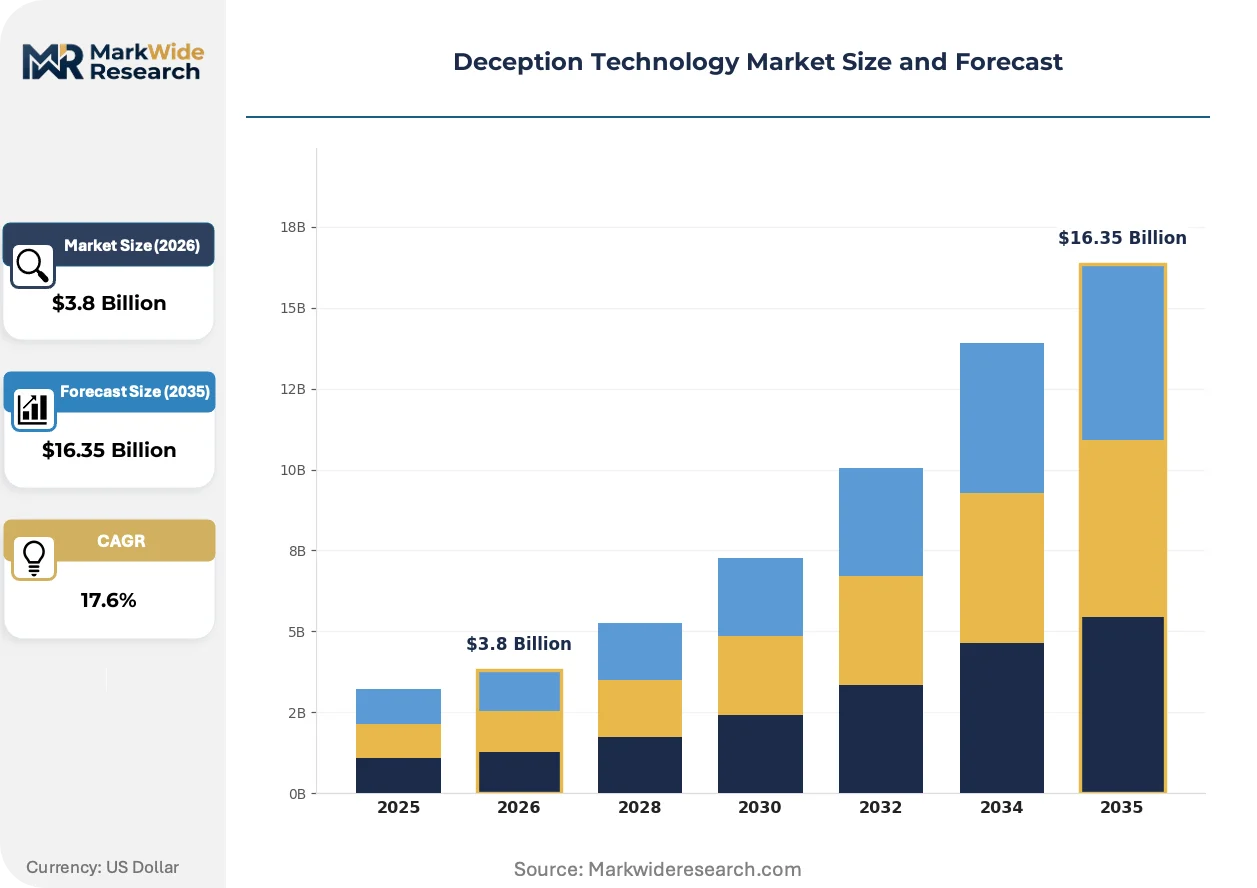
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $16.35 Billion |
| CAGR (2026 – 2036) | 17.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Deception, Network Deception, Application Deception, Data Deception Deployment: On-Premises, Cloud-Based, Hybrid, Virtualized End User: BFSI, Government, Telecom, Healthcare Technology: AI-Based, Machine Learning, Behavior Analytics, Threat Intelligence |
| Companies Covered | Acalvio Technologies, Rapid7, Inc., Attivo Networks, Inc., Illusive Networks, Guardicore, TrapX Security, LogRhythm, Inc., Smokescreen Technologies, Allure Security Technology, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Deception Technology Market Emerging Trajectories
Agentless deployment models and AI-generated decoy content are collapsing traditional friction points that previously limited deception technology to elite security operations.
Agentless endpoint deception is decomposing the historical trade-off between detection depth and deployment speed. Financial services institutions with strict change management protocols are adopting these solutions to bypass kernel-level software installation requirements. The technology is decomposing incumbent market segmentation between high-touch enterprise sales and automated product-led growth channels.
EU AI Act risk classification rules are forcing deception vendors to document algorithmic decision-making in threat detection workflows. High-risk system designations for autonomous security response functions trigger conformity assessment obligations that extend time-to-market for European deployments. Vendors are responding by separating human-in-the-loop approval gates from fully automated deception response mechanisms.
Security procurement teams are unbundling deception capabilities from bundled endpoint detection platforms and negotiating standalone contracts with specialized providers. This pattern disrupts incumbent vendors that positioned deception as a premium module within broader EDR suites. The unbundling trend is most visible among Fortune 500 manufacturers with mature security architecture functions that maintain separate vendor evaluation committees for detection technologies.
Deception Technology Market Segmentation
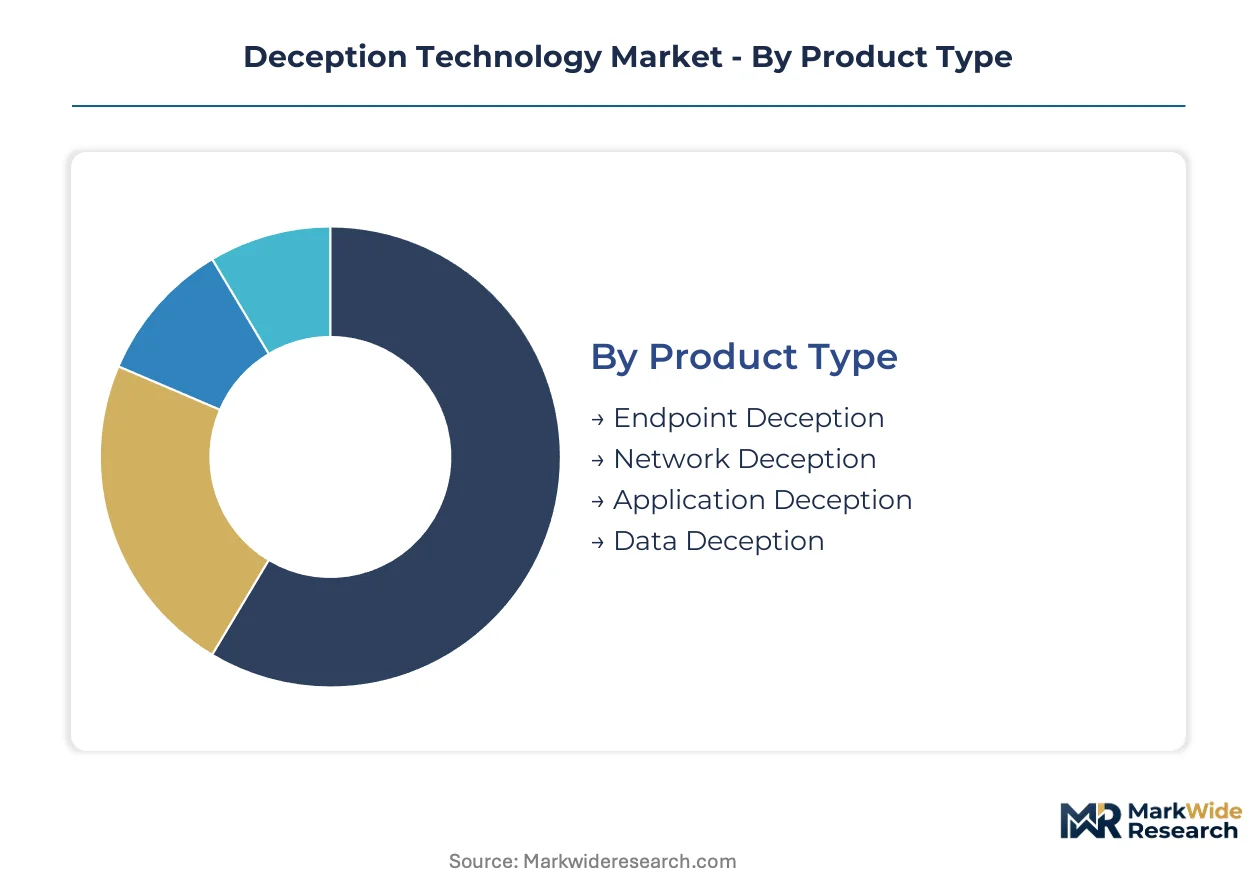
Deception technology vendors configure product architectures around distinct operational environments and threat surfaces. Channel strategies diverge sharply across deployment modes and end-user compliance requirements.
Product Type:
Network deception solutions flow through systems integrators with existing security operations relationships, while endpoint deception increasingly reaches buyers via product-led growth channels and self-service procurement.
- Network Deception:Distributed sensor grids emulate authentic infrastructure including switches, routers, and servers to isolate intruder lateral movement. Financial services institutions in the United States deploy these at scale to satisfy federal zero-trust mandates and SEC incident disclosure timelines.
- Endpoint Deception:Agentless decoys deploy without kernel-level installation, bypassing change management friction in regulated environments. Healthcare systems under HIPAA enforcement pressure adopt these to trap unauthorized credential access without disrupting clinical workflows.
- Application Deception:Synthetic application instances mimic production software interfaces to detect exploitation attempts against business-critical systems.
- Data Deception:Decoy databases and file repositories contain fabricated records that trigger alerts upon unauthorized access or exfiltration attempts.
By volume, network deception leads current deployments. By growth pace, endpoint deception is expanding most quickly as agentless architectures reduce procurement friction.
Deployment:
Cost tier separation shapes go-to-market approaches, with cloud-based offerings commanding premium subscription rates while on-premises deployments require professional services bundling.
- Cloud-Based:Elastic infrastructure enables security teams to instantiate ephemeral decoy workloads that automatically scale with production environments. Mid-market enterprises without dedicated threat hunting teams favor this model for its reduced operational overhead.
- Hybrid:Mixed architectures split deception workloads across on-premises legacy systems and cloud-native environments. Organizations with fragmented infrastructure footprints adopt this approach to maintain consistent detection coverage during multi-year cloud migration programs.
- On-Premises:Air-gapped deployments serve classified government networks and critical infrastructure operators with strict data sovereignty requirements.
- Virtualized:Container-native decoy instantiation supports DevSecOps pipelines in technology sector adopters with rapid deployment cycles.
Cloud-based delivery claims the steepest expansion trajectory as elastic compute reduces per-deployment operational burden. On-premises retains priority in federal contractor environments subject to NIST 800-207 certification timelines.
End User:
Application context dictates feature prioritization, with BFSI buyers emphasizing transaction-speed detection while healthcare procurement focuses on patient data protection workflows.
- BFSI:Banking, financial services, and insurance institutions deploy credential deception at scale to trap unauthorized access to payment systems and trading infrastructure. Breach cost escalation and SEC cybersecurity disclosure rules directly expand budget allocation toward active detection technologies.
- Government:Federal agencies and defense contractors integrate deception layers into zero-trust architecture mandates, with procurement cycles extended by documented deployment pattern requirements.
- Telecom:Network operators with distributed infrastructure footprints apply deception to protect signaling systems and subscriber databases.
- Healthcare:Hospital systems deploy deception to satisfy HIPAA enforcement actions for insufficient access controls, with demand concentrating on solutions that minimize clinical workflow disruption.
BFSI generates the highest absolute spending on deception technology. Healthcare is gaining share fastest as enforcement actions accelerate procurement timelines.
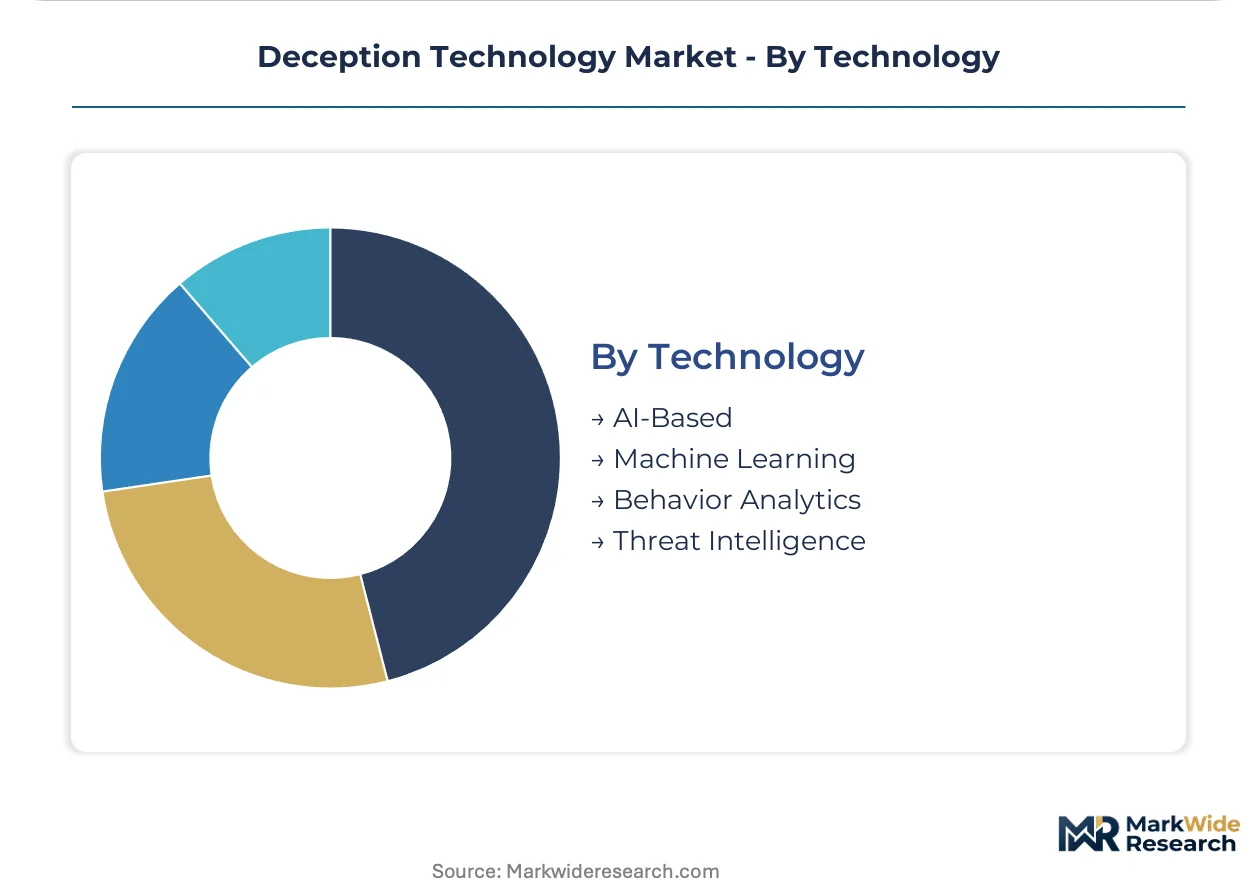
Technology:
Margin structure varies by algorithmic sophistication, with AI-based detection layers commanding premium pricing against rule-driven alternatives burdened by false positive overhead.
- AI-Based:Neural network classifiers reduce false positive rates that plague signature-driven detection, enabling security operations centers to prioritize deception-generated telemetry without alert fatigue. EU AI Act risk classification rules now mandate documented algorithmic decision-making for autonomous response functions.
- Behavior Analytics:Baseline deviation detection identifies anomalous patterns in user and entity behavior without predefined attack signatures. Financial institutions with mature security operations centers favor this approach for its reduced dependency on threat intelligence freshness.
- Machine Learning:Supervised learning models trained on historical breach data predict attacker progression paths through network topology.
- Threat Intelligence:Indicator-of-compromise feeds enrich deception deployments with adversary tactics, techniques, and procedures derived from external sources.
AI-based detection leads vendor R&D investment. Behavior analytics is climbing the fastest as buyers seek alternatives to signature-dependent approaches.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
SEC cybersecurity disclosure rules and federal zero-trust mandates anchor United States demand, while EU NIS2 Directive implementation and national data protection frameworks reshape procurement patterns across European member states.
United States
Financial services institutions in New York and Chicago deploy credential deception at scale to satisfy SEC four-day incident reporting windows. Federal zero-trust architecture mandates from OMB compress vendor sales cycles and force integration into existing security stacks. The Washington DC metro corridor concentrates government contractor procurement subject to NIST 800-207 certification timelines.
Germany
Industrial manufacturing clusters in Bavaria and Baden-Württemberg seek OT-native deception protocols for Modbus and DNP3 traffic protection. The country's national cybersecurity regulator BSI mandates continuous monitoring for critical infrastructure operators under expanded NIS2 transposition. Frankfurt's financial services hub drives demand for transaction-speed detection layers that minimize false positive overhead.
United Kingdom
London-based banking groups unbundle deception capabilities from bundled EDR platforms to negotiate standalone contracts with specialized providers. The National Cyber Security Centre guidance on active cyber defense shapes vendor evaluation criteria for FTSE 350 firms. Manchester and Birmingham healthcare trusts deploy agentless endpoint decoys to satisfy NHS Digital compliance requirements without disrupting clinical workflows.
Japan
Tokyo financial institutions favor behavior analytics approaches that reduce dependency on threat intelligence freshness in mature security operations centers. METI cybersecurity framework revisions emphasize documented incident response capabilities that align with deception technology feature sets. Osaka manufacturing conglomerates pilot OT deception for industrial control system protection in automotive and electronics supply chains.
Singapore
Monetary Authority of Singapore operational resilience guidelines drive banking sector procurement of managed deception services with guaranteed detection SLAs. The city-state's data sovereignty requirements favor hybrid deployment architectures spanning on-premises legacy systems and cloud-native environments. Regional headquarters of multinational corporations concentrate security architecture decisions that cascade across Asia-Pacific subsidiaries.
Deception Technology Market Vendor Landscape
Technology leadership and cost leadership are held by different player archetypes, with AI-based detection specialists commanding premium pricing against rule-driven alternatives burdened by false positive overhead. The vendor base separates into three strategic tiers: managed security service providers embedding deception into broader detection portfolios, pure-play specialists with deep credential and Active Directory capabilities, and agentless endpoint innovators reducing deployment friction. Dominant competitive moves include adversarial simulation talent acquisition to constrain delivery capacity constraints, and cloud-native platform development to capture mid-market managed service demand.
Among pure-play deception specialists, Attivo Networks, Inc. and Illusive Networks occupy positions defined by deployment architecture differentiation, while Rapid7, Inc. exemplifies the managed detection and response provider archetype embedding deception layers into existing security operations footprints. These three companies represent distinct strategic postures: credential-centric depth, agentless friction reduction, and platform-integrated breadth.
| Leading Market Players |
|---|
| Acalvio Technologies |
| Rapid7, Inc. |
| Attivo Networks, Inc. |
| Illusive Networks |
| Guardicore |
| TrapX Security |
| LogRhythm, Inc. |
| Smokescreen Technologies |
| Allure Security Technology, Inc. |
| Others |
Supply Flow & Price Mechanics
Agentless deployment architectures are displacing kernel-dependent sensor stacks across enterprise security operations, simultaneously collapsing implementation timelines and redrawing vendor margin structures as professional services revenue gives way to self-service SaaS tiers. This substitution dynamic concentrates pricing power with vendors that eliminate deployment friction while compressing margins for legacy players tethered to high-touch implementation models.
Pricing Analysis
North American buyers face subscription rates 15-25% above Asia-Pacific equivalents for equivalent AI-based detection layers, reflecting both compliance premium burdens and concentrated federal demand. The market runs on a three-tier pricing structure across premium, standard, and economy levels, with differentiation anchored in algorithmic sophistication and guaranteed detection SLAs. Cost compression in the standard tier intensifies because mid-market enterprises negotiate volume discounts for managed deception services. Healthcare procurement committees demonstrate highest price sensitivity due to constrained capital budgets, while BFSI security architects show least sensitivity given breach cost escalation and regulatory disclosure timelines.
Supply Chain Analysis
Adversarial simulation talent concentration in Israel, the United States, and the United Kingdom creates a human capital chokepoint that constrains vendor delivery capacity and inflates implementation costs across all deployment modes. Software development draws from cloud infrastructure providers, specialized threat intelligence feeds, and certified security hardware manufacturers as core input categories. Single-source vulnerability in adversarial research talent pools exposes vendors to wage inflation and poaching risk that directly feeds through to service pricing. Distribution runs through systems integrators with existing security operations relationships for network deception, while endpoint solutions increasingly reach buyers via direct digital channels and self-service procurement platforms.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The market rewards vendors that control scarce offensive security expertise, as adversarial simulation capabilities constrain delivery capacity across all deployment archetypes. Buyers must weigh vendor telemetry integration against the operational burden of maintaining convincing decoy ecosystems.
For Market Incumbents: Compound defensive positioning through adversarial simulation talent acquisition to constrain competitor delivery capacity, and deepen credential deception capabilities to anchor switching costs in Active Directory environments. Threat from agentless endpoint innovators demands response through certification investment in NIST 800-207 compliance patterns that extend procurement cycles for federal contractors. For New Entrants and Emerging Players: Managed deception services for mid-market enterprises without dedicated threat hunting teams represent the most penetrable white space, with guaranteed detection SLAs as the critical go-to-market angle. Operational technology convergence in manufacturing and energy offers second entry path through Modbus and DNP3 protocol adaptation. Target European critical infrastructure operators preparing for NIS2 Directive compliance deadlines as the fastest-expanding geographic demand pool. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors pure-play specialists with deep credential capabilities over managed security service providers embedding deception as a module. Long-term viability over the next decade rests on AI-based detection layer differentiation and cloud-native platform architecture. Monitor EU AI Act conformity assessment timelines as the critical signal for European deployment velocity and vendor compliance burden.| Strategic Initiative | Industry Significance |
|---|---|
| Adversarial Simulation Talent Acquisition | Offensive security expertise concentration constrains vendor delivery capacity and anchors competitive differentiation. |
| Cloud-Native Platform Development | Elastic infrastructure enables mid-market managed service capture with reduced operational overhead. |
| NIST 800-207 Certification Investment | Documented deployment patterns extend federal procurement cycles and create incumbent protection. |
| OT Protocol Adaptation | Modbus and DNP3 deception capabilities open industrial control system white space in manufacturing and energy. |
| Managed Deception Service Launch | Guaranteed detection SLAs address underserved mid-market enterprises without threat hunting teams. |
Methodological Framework
Operator-level perspectives from CISOs, SOC directors, threat hunting team leads, and deception technology procurement officers anchored the qualitative base for this analysis. Primary interviews combined with secondary validation from SEC cybersecurity disclosure filings, NIST framework documentation, HIPAA enforcement records, and vendor telemetry integration specifications. Bottom-up deployment volume estimates triangulated against top-down security budget allocation surveys across BFSI, healthcare, and government verticals.
Sensitivity analysis tested forecast outputs against variable adoption rates for agentless endpoint architectures and divergent NIS2 implementation timelines across European member states. The analytical framework modeled segmentation across product type, deployment mode, end-user vertical, and detection technology sophistication throughout the forecast period. CAGRs derived from historical deception technology procurement patterns projected forward using security operations center staffing ratio benchmarks and regulatory compliance deadline clustering.
Underlying assumptions cover sustained federal zero-trust mandate enforcement, stable adversarial simulation talent supply, and cloud infrastructure cost trajectories, with deviation risk concentrated in EU AI Act risk classification rulings and HIPAA enforcement intensity variation. Practitioners should keep alternative scenarios live as SEC disclosure rule interpretation and NIST certification timeline evolution reshape procurement patterns.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Digital Immune System Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
Taiwan Cybersecurity Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Europe Mobile Security Market