
 Virtualization Security Tools Market | 2026-2036
Virtualization Security Tools Market Size, Share, and Industry Trends Forecast 2026-2036
Virtualization Security Tools Market Analytics
North American cybersecurity infrastructure investment is decoupling from traditional hardware-bound security models. VMware leverages its hypervisor dominance to anchor enterprise virtualization security stacks. Palo Alto Networks competes through cloud-native security platform integration. Check Point Software Technologies specializes in multi-tenant threat prevention for virtualized data centers.
Virtualization security tools are software solutions that monitor, isolate, and protect virtual machines, containers, and software-defined networks through hypervisor introspection, micro-segmentation, and encrypted east-west traffic inspection. These tools enforce policy across ephemeral workloads where physical network boundaries no longer exist. Hypervisor security and container security represent the fastest-expanding technology categories as organizations adopt Kubernetes and serverless architectures. Cloud-based and multi-cloud deployment models are capturing disproportionate investment as distributed workforces require consistent policy enforcement across AWS, Azure, and private infrastructure.
The National Institute of Standards and Technology, the Federal Risk and Authorization Management Program, and ISO 27017 cloud security standards collectively shape product certification requirements and procurement eligibility for virtualization security vendors. Compliance Management solutions within the solution type segment are gaining traction as automated audit and continuous monitoring capabilities become mandatory for FedRAMP authorization. Stakeholders must evaluate whether their architectures can maintain deterministic security guarantees as virtualized environments scale beyond traditional perimeter visibility.
Market Dynamics
Zero-trust architecture mandates from NIST and FedRAMP authorization requirements are forcing enterprises to replace perimeter-based security with hypervisor-native controls that inspect east-west traffic between ephemeral workloads.
Growth Catalysts
- FedRAMP Authorization Requirements:Federal cloud-first policies mandate continuous monitoring capabilities for agencies migrating to AWS, Azure, and private infrastructure, creating baseline demand for compliance automation tools.
- Kubernetes Orchestration:Container adoption across financial services and healthcare verticals requires micro-segmentation policies that follow workloads across multi-cloud deployments.
- Critical Infrastructure Designation:CISA's expansion of critical infrastructure categories to cloud service providers triggers mandatory cybersecurity investment from designated operators.
Market Restraints
- Hypervisor Vendor Concentration:VMware's dominance in enterprise virtualization creates dependency risk for security vendors building on proprietary introspection APIs.
- Skill Scarcity in Container Security:Shortage of engineers proficient in eBPF-based monitoring and service mesh policy configuration limits deployment velocity at mid-market enterprises.
- Latency Overhead from Deep Packet Inspection:East-west traffic inspection at 100Gbps line rates introduces performance degradation that trading floors and high-frequency finance cannot tolerate.
Strategic Opportunities
- Serverless Security Posture Management:AWS Lambda and Azure Functions lack persistent runtime agents, creating white space for event-driven security orchestration tools.
- State-Level Privacy Fragmentation:California's CPRA and Virginia's VCDPA impose data residency requirements that favor regional cloud deployments with localized policy enforcement.
- Confidential Computing Integration:AMD SEV-SNP and Intel TDX hardware enclaves enable encryption of memory during active processing, converging with virtualization security stacks.
Industry Challenges
- Legacy SIEM Integration:Security teams struggle to correlate hypervisor-level telemetry with decades-old Splunk and QRadar deployments that lack native container parsing.
- Multi-Cloud Policy Drift:Inconsistent API implementations across AWS, Azure, and Google Cloud force security engineers to maintain parallel policy languages.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Virtualization Security Tools Market |
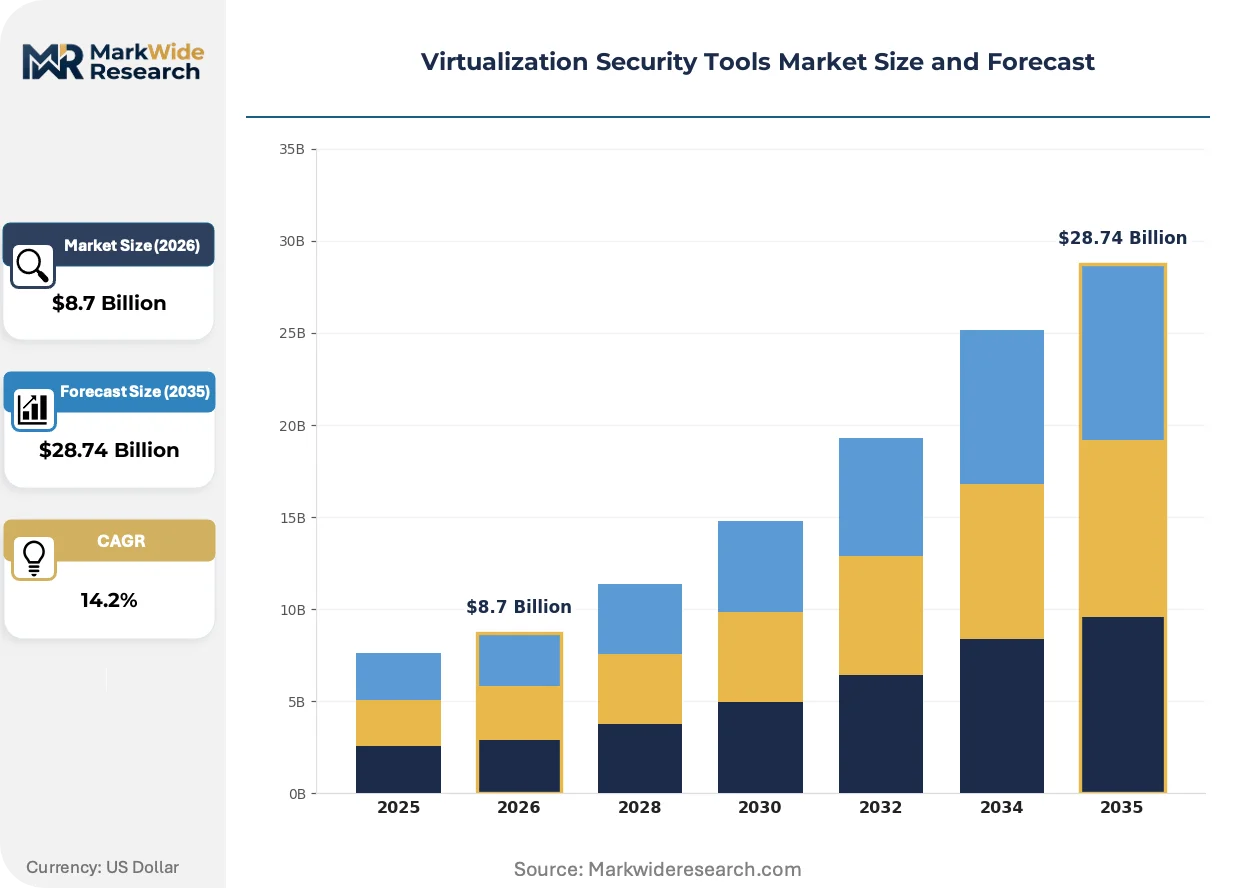
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $28.74 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Hypervisor Security, Container Security, Network Security, Endpoint Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Multi-Cloud End User: SMEs, Large Enterprises, Government Agencies, Managed Service Providers Solution Type: Antivirus, Firewall, Intrusion Detection, Compliance Management |
| Companies Covered | VMware LLC, Trend Micro, Cisco Systems, Juniper Networks, Microsoft Corporation, Fortinet, Check Point Software Technologies, Palo Alto Networks, IBM Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Virtualization Security Tools Market Evolving Landscape
Security instrumentation is migrating from network appliances into the virtualization layer itself, collapsing the traditional boundary between infrastructure and security operations teams.
eBPF-based kernel observability is rewriting how security teams monitor container runtime behavior without modifying application code or deploying sidecar proxies. Financial services firms in New York and London are deploying these tools at production scale to capture process execution and network flows with sub-millisecond overhead. The technology is compressing the vendor stack by eliminating separate agent-based monitoring products.
NIST's Cybersecurity Framework 2.0 introduces explicit supply chain risk management requirements that virtualization security vendors must document for federal procurement eligibility. Cloud service providers are restructuring their compliance documentation to map hypervisor controls directly to framework subcategories. European firms preparing for DORA operational resilience mandates are adopting these mappings ahead of January 2025 deadlines.
Enterprise buyers are consolidating vendor relationships through platform procurement rather than point-solution acquisition, with CISOs mandating unified consoles for virtual machine, container, and serverless security. Value-added resellers and systems integrators are displacing direct vendor relationships as primary contract holders. This pattern is most visible among Fortune 500 manufacturers in the Midwest and Southeast United States consolidating security spend under single master service agreements.
Virtualization Security Tools Market Segmentation
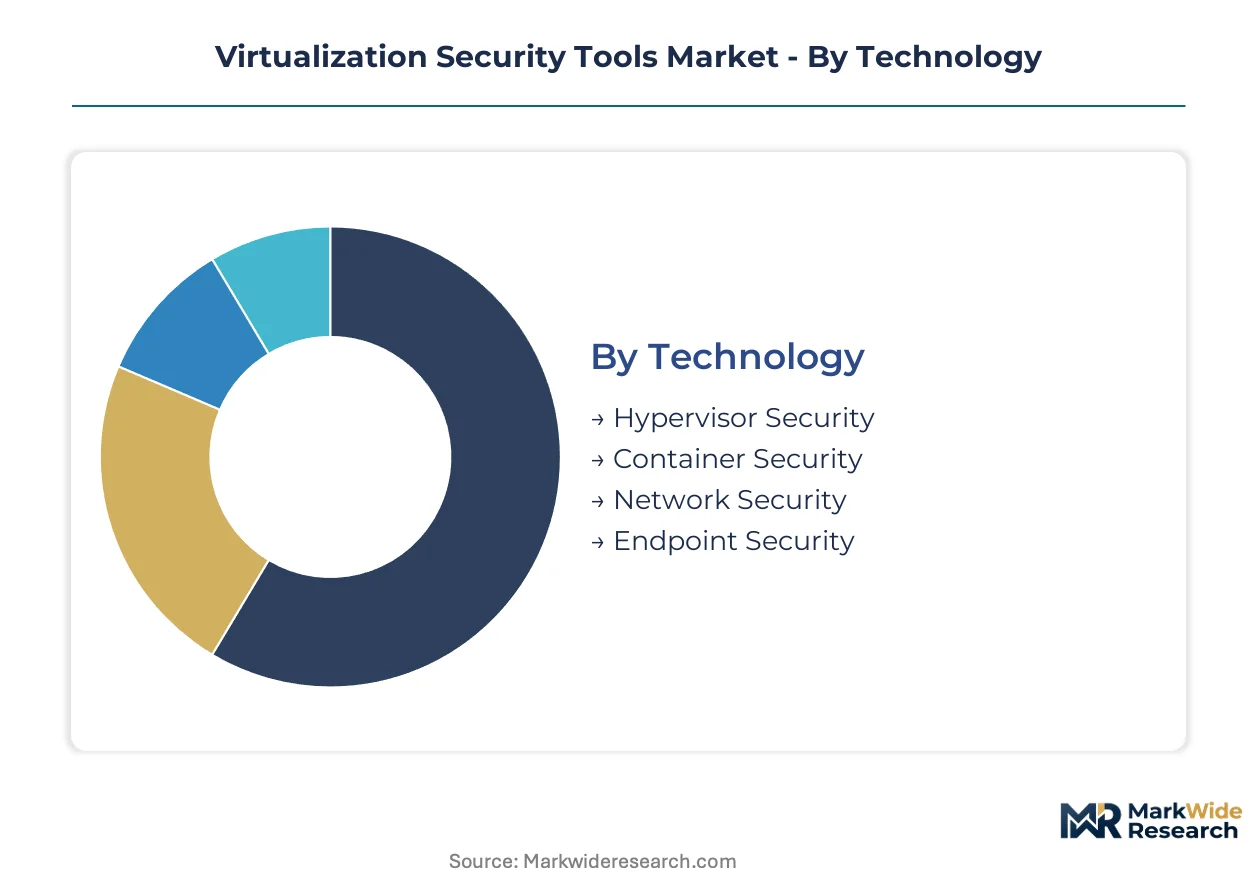
Virtualization security procurement patterns diverge sharply across technology stacks and operational models. Understanding where security budgets concentrate within each dimension enables vendors to align R&D investment with actual deployment trajectories rather than aspirational architectures.
Technology:
Supply concentration tilts toward vendors controlling hypervisor introspection APIs, creating asymmetric competitive moats around core platform technologies.
- Hypervisor Security:Enforces policy through direct memory introspection and virtual machine isolation at the kernel level. Financial services firms in New York and London deploy these controls to satisfy regulatory mandates for workload separation in multi-tenant environments.
- Container Security:Monitors runtime behavior across ephemeral Kubernetes pods using eBPF instrumentation and admission controllers. Healthcare providers migrating patient data platforms to containerized architectures drive procurement velocity for runtime protection tools.
- Network Security:Micro-segmentation and encrypted east-west traffic inspection for software-defined networks.
- Endpoint Security:Agent-based protection for virtual desktop infrastructure and remote worker access.
Hypervisor Security absorbs the bulk of installed capacity; Container Security is expanding most quickly.
Deployment Model:
Cost tier stratification separates enterprise-grade multi-cloud orchestration from mid-market single-cloud deployments, with hybrid architectures commanding premium pricing for complexity management.
- Multi-Cloud:Unified policy enforcement across AWS, Azure, and private infrastructure through centralized control planes. Federal agencies under cloud-first mandates require consistent security posture across disparate provider environments, driving demand for abstraction layers.
- Cloud-Based:Native security services integrated with single-provider IaaS platforms. Regional banks in the United States favor this model to minimize operational overhead while satisfying FFIEC examination expectations.
- Hybrid:Split workloads across on-premises virtualization and public cloud resources.
- On-Premises:Self-managed security stacks for air-gapped or data-sovereignty-constrained environments.
Cloud-Based deployments hold the largest revenue base; Multi-Cloud configurations are climbing the fastest as workload distribution accelerates.
End User:
Application intensity varies by organizational scale, with government procurement cycles creating predictable demand windows that vendors align product roadmaps to capture.
- Government Agencies:FedRAMP-authorized security tools with continuous monitoring and audit automation. CISA's critical infrastructure designations compel designated operators to maintain hypervisor-level visibility for threat hunting and incident response.
- Large Enterprises:Platform consolidation across virtual machine, container, and serverless security through unified consoles. Fortune 500 manufacturers in the Midwest United States consolidate vendor relationships under single master service agreements.
- Managed Service Providers:Multi-tenant security delivery for client workloads.
- SMEs:Simplified agent-based protection with minimal operational complexity.
Large Enterprises dominate current spending; Government Agencies are gaining share fastest as federal cloud migration deadlines approach.
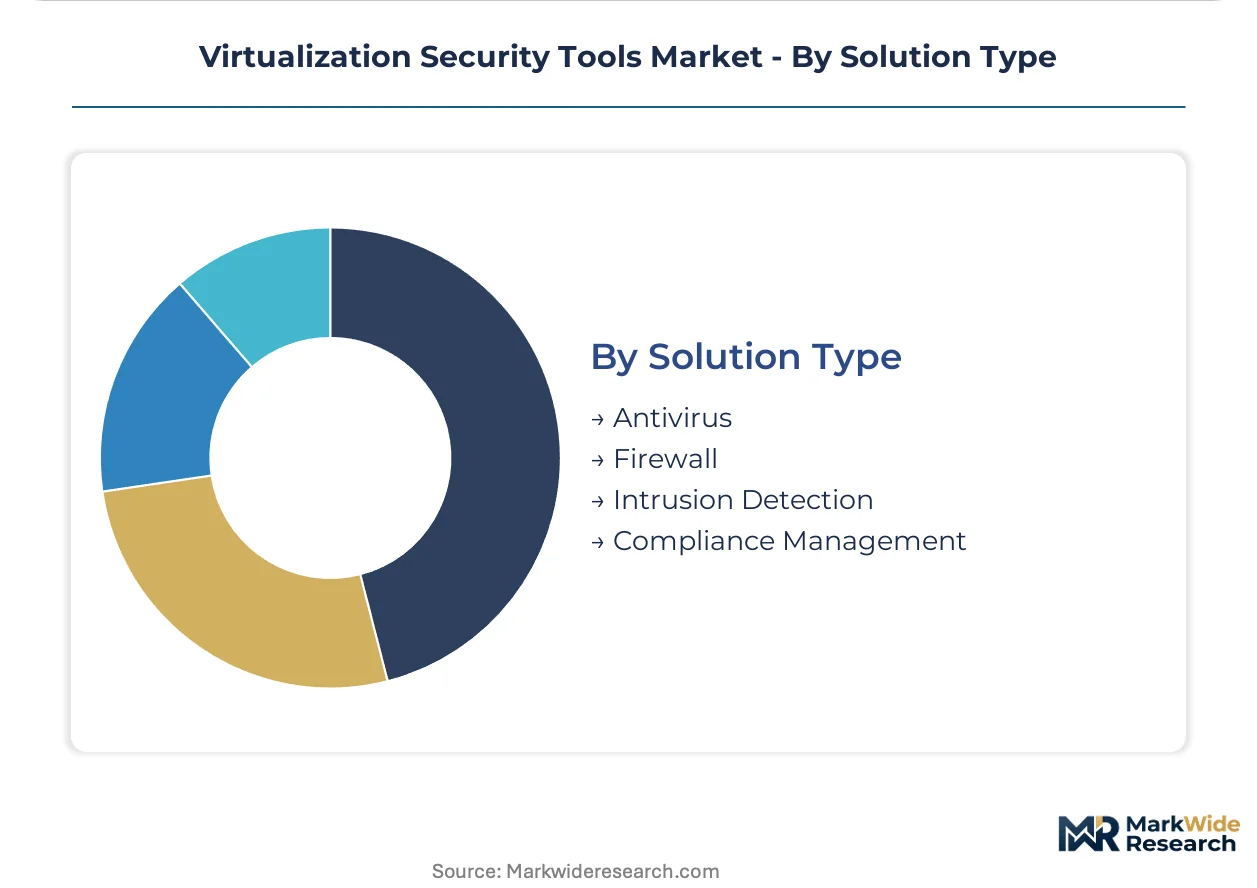
Solution Type:
Margin structures favor compliance automation over commodity antivirus, with audit-ready documentation commanding pricing multiples against baseline threat prevention.
- Compliance Management:Automated evidence collection, continuous control monitoring, and framework mapping for NIST, FedRAMP, and ISO 27017. Cloud service providers restructure documentation to map hypervisor controls directly to framework subcategories ahead of European DORA deadlines.
- Intrusion Detection:Behavioral analysis and anomaly detection for virtualized workloads using machine learning classifiers. Trading floors tolerate detection latency in exchange for reduced false positive rates that minimize analyst alert fatigue.
- Firewall:Virtualized perimeter and east-west traffic filtering between workloads.
- Antivirus:Signature and heuristic-based malware scanning for virtual machines.
Firewall solutions retain the broadest installed base; Compliance Management is gaining share fastest as regulatory automation becomes mandatory for federal eligibility.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's data center density anchors North American virtualization security procurement. Federal cloud-first mandates and financial services migration to hybrid infrastructure concentrate demand in specific metropolitan clusters.
United States
FedRAMP authorization requirements and CISA critical infrastructure designations compel federal agencies to procure hypervisor-level security tools. The National Institute of Standards and Technology Cybersecurity Framework 2.0 reshapes vendor qualification criteria. New York financial services firms and Washington DC federal contractors represent the densest deployment clusters for compliance-automated solutions.
Germany
DORA operational resilience mandates drive European banks to adopt continuous monitoring capabilities ahead of January 2025 deadlines. The EU AI Act and GDPR impose data residency requirements that favor localized policy enforcement engines. Frankfurt's financial district and Munich's automotive engineering hubs concentrate procurement for multi-cloud security orchestration.
United Kingdom
NCSC cloud security guidance and Bank of England operational resilience expectations shape vendor selection for financial institutions. Post-Brexit data sovereignty concerns accelerate investment in hybrid deployment models. London's fintech corridor and Edinburgh's banking sector anchor demand for container security platforms.
Japan
METI cybersecurity framework updates mandate supply chain risk documentation for critical infrastructure operators. Financial Services Agency guidelines require continuous monitoring for cloud-migrated banking workloads. Tokyo's financial district and Osaka's manufacturing technology clusters drive procurement of hypervisor-native controls.
India
RBI cybersecurity directives for scheduled commercial banks mandate workload isolation in multi-tenant cloud environments. MeitY's data localization requirements favor regional cloud deployments with embedded security stacks. Mumbai's banking headquarters and Bangalore's SaaS development corridors concentrate demand for Kubernetes-native protection tools.
Virtualization Security Tools Market Competitive Landscape
Global majors compete with regional champions across hypervisor API access and cloud-native platform integration. The vendor base organizes into three tiers: infrastructure incumbents controlling virtualization layers, cybersecurity pure-plays with cloud-native architectures, and systems integrators consolidating procurement relationships. Dominant competitive moves include strategic API partnerships with cloud service providers and vertical integration into compliance automation documentation.
Within the infrastructure-anchored tier, VMware LLC occupies a position as the hypervisor incumbent whose API control shapes security vendor roadmaps. Trend Micro and Palo Alto Networks exemplify the cybersecurity pure-play archetype, competing through cloud-native platform breadth rather than infrastructure ownership. Check Point Software Technologies sits within the specialized threat prevention segment, representing vendors that concentrate on multi-tenant data center environments.
| Leading Market Players |
|---|
| VMware LLC |
| Trend Micro |
| Cisco Systems |
| Juniper Networks |
| Microsoft Corporation |
| Fortinet |
| Check Point Software Technologies |
| Palo Alto Networks |
| IBM Corporation |
| Others |
Value Network & Pricing Analysis
Federal agencies under FedRAMP authorization requirements anchor demand for compliance-automated virtualization security stacks, driving subscription-based pricing models that bundle continuous monitoring with audit documentation. This buyer concentration shifts pricing power toward vendors capable of mapping hypervisor controls directly to NIST framework subcategories.
Pricing Analysis
Service bundling separates FedRAMP-ready compliance automation from baseline threat detection, with continuous control monitoring and framework mapping unbundled as premium tiers. Three-tier pricing structure across premium, standard, and economy levels stratifies by certification depth and audit support scope. Pricing pressure stems from open-source eBPF tooling commoditizing runtime observability at the container layer. Mid-market enterprises exhibit highest price sensitivity, while federal contractors tolerate premium pricing for authorization eligibility.
Supply Chain Analysis
Hypervisor introspection API access rests on VMware's control of enterprise virtualization infrastructure, creating asymmetric dependency for security vendors building on proprietary interfaces. Specialized engineering talent concentrates in the United States, Israel, and Estonia, with eBPF kernel development expertise remaining scarce. Single-source vulnerability around dominant hypervisor platforms threatens vendor roadmap autonomy. Distribution runs through value-added resellers and systems integrators consolidating Fortune 500 procurement under master service agreements.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a cost-of-compliance story where FedRAMP authorization requirements erect barrier-to-entry moats that favor incumbent vendors with existing federal certification pathways.
For Market Incumbents: Extend API control into adjacent container runtime layers through strategic partnerships with Kubernetes distribution vendors. VMware's hypervisor dominance faces erosion from cloud-native alternatives; incumbents should deepen backward integration into eBPF-based kernel instrumentation to capture telemetry previously served by separate agent products. Certification investment in ISO 27017 and DORA mappings ahead of European deadlines preserves pricing power. For New Entrants and Emerging Players: Capture serverless security posture management white space where AWS Lambda and Azure Functions lack persistent runtime agents. The most penetrable segment comprises regional banks seeking FFIEC-compliant cloud security without federal-grade complexity. A channel-centric go-to-market approach through managed service providers bypasses direct competition with platform-integrated incumbents. For Investors and Strategic Acquirers: Distressed-cycle entries favor cybersecurity pure-plays with existing eBPF engineering teams in Tel Aviv and Tallinn as valuation multiples compress. Long-term viability hinges on convergence with confidential computing hardware enclaves from AMD and Intel. Monitor CISA critical infrastructure designation expansions as inflection signals for mandatory procurement volume.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unified consoles spanning VM, container, and serverless security displace point-solution vendors. |
| Compliance Automation Investment | Automated FedRAMP evidence collection commands pricing multiples over baseline threat prevention. |
| Strategic Partnership | API agreements with AWS, Azure, and Google Cloud reduce multi-cloud policy drift for customers. |
| Acquisition of Specialist Firm | eBPF-native startups compress vendor stacks by eliminating separate agent-based monitoring products. |
| Geographic Expansion | Localized policy enforcement engines in Frankfurt and Mumbai satisfy data residency mandates. |
Research Methodology
Multi-period observation of hyperscaler capex disclosures, FedRAMP authorization timelines, and container adoption metrics anchored the trend analysis, supplemented by interviews with CISOs at Fortune 500 manufacturers, federal procurement officers, platform engineers at cloud service providers, and compliance specialists at systems integrators. Secondary validation drew from NIST cybersecurity framework documentation, SEC 10-K filings of publicly traded security vendors, CISA critical infrastructure designations, and European DORA regulatory texts. Bottom-up deployment modeling and top-down market sizing triangulated volume estimates.
Segment-weighting across deployment model, organization scale, vertical industry, and integration complexity shaped the analytical framework over the projection horizon. Technology category CAGRs derived from elasticity-adjusted adoption curves calibrated to Kubernetes penetration data and serverless deployment velocity. Continuous monitoring automation intensity and hardware enclave integration timelines served as industry-specific forecast inputs.
The model holds under stable regulatory authorization timelines and sustained federal cloud-first policy enforcement; deviation in NIST framework revision schedules or FedRAMP reciprocity agreements would shift vendor eligibility and procurement velocity. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
SSL VPN Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Web Filtering Market
Cybersecurity
Taiwan Cybersecurity Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
Global Email Encryption Market
Cybersecurity
Global Sensitive Data Discovery Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Cyber Warfare Market