
 Network Access Control Market | 2026-2036
Network Access Control Market Size, Share, and Industry Trends Forecast 2026-2036
Network Access Control Market Analysis
The capital-intensity divergence between hardware-centric and cloud-native vendors is unwinding competitive dynamics across the sector. Cisco Systems leverages its integrated switching and security stack to dominate enterprise campus deployments. Fortinet sustains aggressive R&D cadence in converged network and access platforms. Portnox competes through pure-cloud delivery models that reduce customer infrastructure overhead.
Network Access Control constitutes a cybersecurity framework that authenticates and authorizes every device attempting to connect to a corporate network, enforcing policies through 802.1X protocols, MAC authentication bypass, or agent-based posture assessment before granting resource access. The architecture inspects endpoint health status, patch levels, and security configuration to block non-compliant devices from lateral movement. Cloud deployment models are capturing fastest expansion as distributed workforces eliminate perimeter-centric designs. Policy Management solutions anchor the largest margin pools given recurring configuration complexity across heterogeneous device fleets. Healthcare end users are driving urgent upgrades as connected medical equipment proliferates beyond traditional IT visibility.
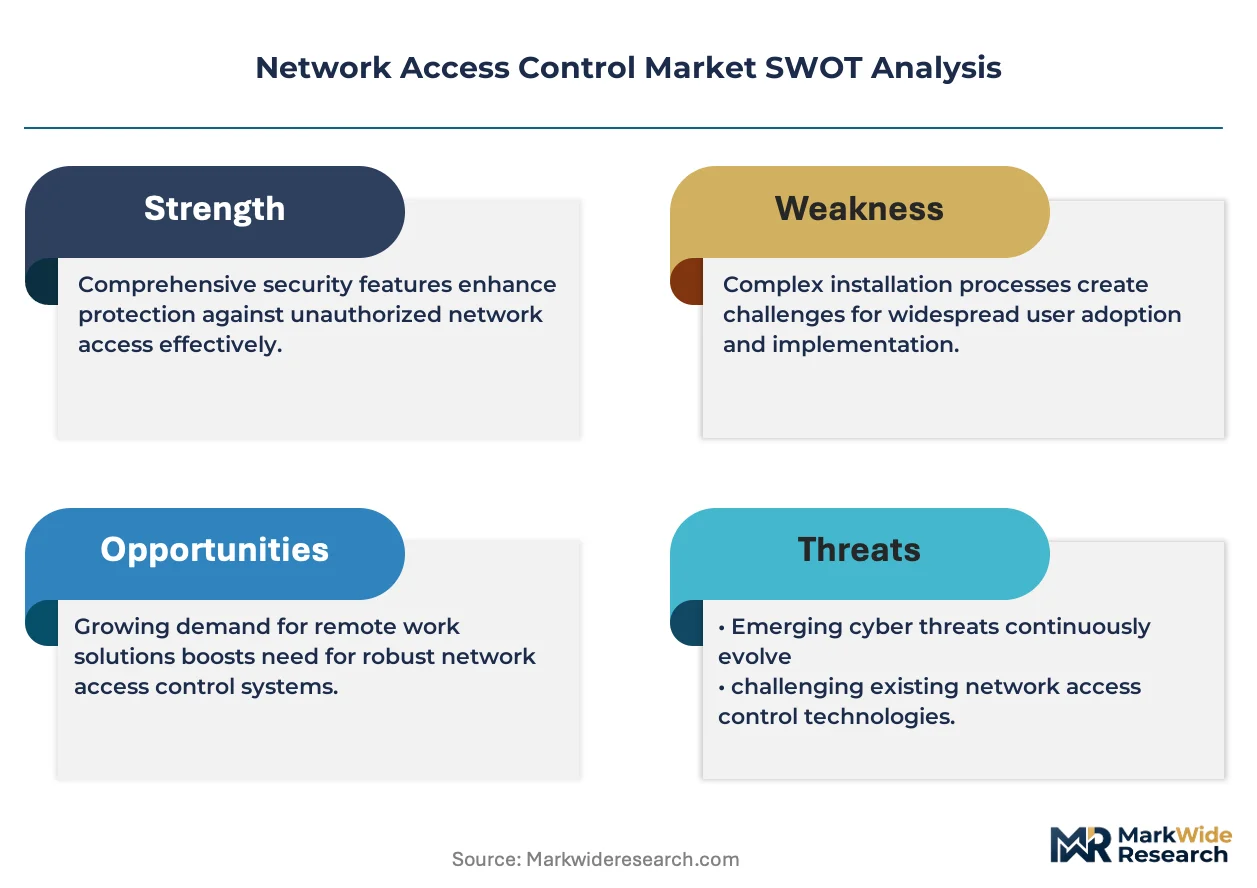
NIST, HIPAA, and the EU Cybersecurity Act are tightening mandatory controls for device visibility and continuous compliance verification across critical infrastructure operators. These frameworks compel organizations to replace passive VLAN segmentation with active, identity-driven admission policies. Stakeholders must monitor how zero-trust mandates reshape procurement criteria toward API-integrated, multi-tenant platforms that unify access governance across cloud and on-premises assets.
Market Dynamics
Zero-trust security mandates are compressing procurement cycles across enterprise IT, forcing buyers to abandon perimeter-centric architectures in favor of continuous verification models that authenticate every device session independently.
Growth Catalysts
- Ransomware proliferation in healthcare:Hospital networks face intensified extortion campaigns targeting unpatched medical devices, accelerating 802.1X deployment for connected imaging and monitoring equipment.
- NIST SP 800-207 framework adoption:Federal contractors must implement continuous compliance monitoring by 2027, mandating API-integrated access platforms across critical infrastructure operators.
- Agentless cloud-native assessment:Pure-cloud NAC delivery eliminates on-premises appliance overhead, reducing total cost of ownership for mid-market enterprises with distributed workforces.
Market Restraints
- Silicon supply concentration:Specialized ASICs for high-throughput policy enforcement engines depend on TSMC fabrication capacity in Taiwan, creating delivery volatility for hardware-centric vendors.
- Certificate management complexity:Device authentication at scale requires automated PKI infrastructure that many organizations lack, delaying production deployments despite purchased licenses.
- Passive VLAN substitution:Flat network segmentation using existing switch infrastructure offers zero capital expenditure for budget-constrained buyers, slowing active admission control adoption.
Strategic Opportunities
- Operational technology convergence:Manufacturing floors and energy utilities seek unified platforms that bridge IT and industrial control system access governance, collapsing separate procurement silos.
- EU Cybersecurity Act certification:Mandatory conformity assessment for critical infrastructure creates preference pull toward pre-certified vendors, accelerating market consolidation.
- API-first ecosystem integration:SIEM and SOAR platform connectivity enables automated incident response workflows, differentiating vendors through security orchestration depth.
Industry Challenges
- Identity fabric fragmentation:Heterogeneous IdP environments spanning Active Directory, Okta, and Azure AD complicate unified policy enforcement, requiring expensive professional services for integration.
- Medical device visibility gaps:Biomedical engineering teams lack asset discovery tools for legacy equipment running embedded operating systems, leaving authentication blind spots in clinical networks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Network Access Control Market |
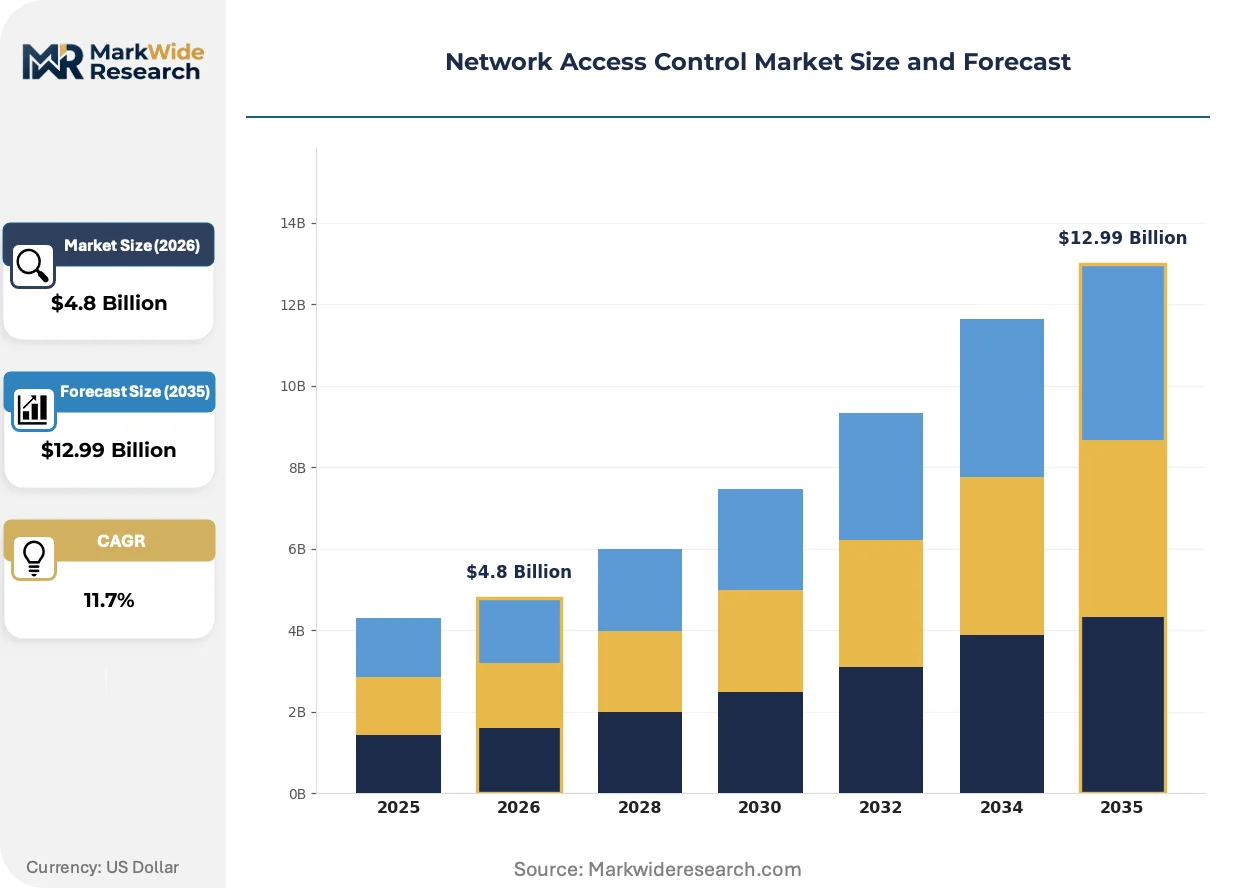
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $12.99 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premises, Cloud, Hybrid, Managed Solution Type: Policy Management, Device Authentication, Compliance Management, Threat Detection End User: Healthcare, Education, Retail, Government Integration Level: Standalone, API-Integrated, Third-Party, Multi-Tenant |
| Companies Covered | Cisco Systems, Inc., Hewlett Packard Enterprise Company, Fortinet, Inc., Forescout Technologies, Inc., Juniper Networks, Inc., Palo Alto Networks, Inc., Portnox, Extreme Networks, Inc., Arista Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Network Access Control Market Emerging Trajectories
Artificial intelligence inference at the network edge is compressing threat detection latency, enabling real-time device behavior analysis without backhauling telemetry to centralized security stacks.
Software-defined perimeter architectures are supplanting hardware-bound NAC appliances in enterprise campus environments. Financial services firms and technology companies deploy cloud-native access brokers that authenticate users and devices through identity-aware proxies rather than switch-embedded 802.1X enforcement. This shift collapses capital expenditure requirements while enabling seamless policy portability across multi-cloud footprints.
HIPAA Security Rule updates issued by the Department of Health and Human Services tighten audit logging mandates for covered entities, compelling hospitals to replace passive network monitoring with active admission controls that generate immutable access records. Rural health systems lacking dedicated security operations centers outsource continuous compliance verification to managed NAC providers.
Subscription-based consumption models displace perpetual licensing in mid-market procurement, with buyers preferring annual contracts that bundle policy management, threat intelligence feeds, and vendor-managed infrastructure. Value-added distributors in North America and Western Europe consolidate this shift through managed security service provider programs that handle deployment complexity for resource-constrained customers.
Network Access Control Market Segmentation
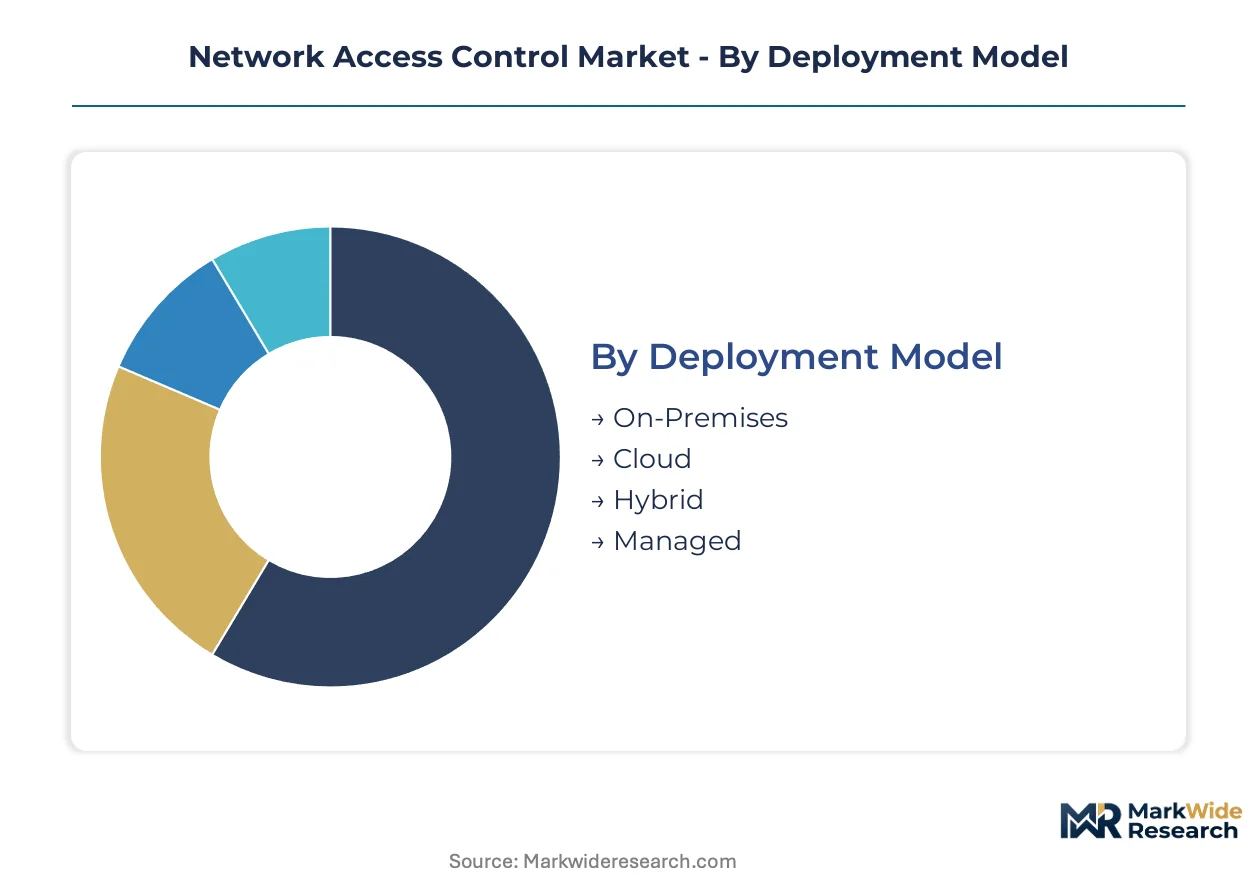
NAC procurement splits sharply between capital-heavy campus installations and lightweight cloud subscriptions. Buyers weigh compliance mandates against operational complexity when selecting across deployment models, solution architectures, and integration depths.
Deployment Model:
On-premises deployments concentrate in domestic regulated sectors with data sovereignty requirements. Cloud-native delivery dominates cross-border enterprise rollouts where distributed workforces outnumber headquarters staff.
- On-Premises:Hardware appliances enforce 802.1X at network switches with dedicated policy engines. Demand clusters in United States federal agencies and German automotive manufacturing campuses subject to strict data localization. NIST SP 800-207 mandates compress procurement timelines for these installations.
- Cloud:Pure-software delivery eliminates appliance procurement cycles through browser-managed policy orchestration. Financial services firms in Singapore and technology companies across Ireland deploy these for rapid multi-site expansion without capital expenditure. Agentless posture assessment reduces helpdesk burden for bring-your-own-device environments.
- Hybrid:Split architectures anchor policy management in cloud consoles while retaining on-premises enforcement nodes. Japanese industrial conglomerates favor this model for factory-floor segmentation with centralized governance.
- Managed:Outsourced NAC operations include vendor-staffed security operations centers handling certificate lifecycle and incident response. Australian healthcare networks and Canadian provincial governments procure these to compensate for internal cybersecurity staffing gaps.
On-premises commands the established base. The steepest expansion runs through Cloud.
Solution Type:
Margin concentration follows configuration complexity rather than threat detection novelty. Policy engines generate recurring professional services revenue where authentication modules commoditize faster.
- Policy Management:Centralized rule engines govern device admission across heterogeneous switch fabrics and wireless controllers. United States hospital systems and United Kingdom university networks drive renewal cycles as device diversity outstrips manual configuration capacity. HIPAA audit logging mandates tighten specification requirements.
- Device Authentication:Certificate-based 802.1X and MAC authentication bypass validate endpoint identity before network admission. French banking consortiums and Swiss pharmaceutical campuses deploy these for zero-trust segmentation of research networks.
- Compliance Management:Automated posture assessment verifies patch status, encryption presence, and antivirus currency against regulatory baselines. German critical infrastructure operators under EU Cybersecurity Act certification requirements prioritize these modules for audit readiness.
- Threat Detection:Behavioral analytics identify anomalous device traffic patterns indicating compromise or lateral movement. Expansion concentrates in managed security service provider bundles rather than standalone procurement.
Policy Management anchors recurring revenue streams. Compliance Management climbs fastest as regulatory deadlines approach.
End User:
Sector-specific risk profiles reshape feature prioritization across buyer categories. Healthcare urgency contrasts with education budget constraints and government procurement rigidity.
- Healthcare:Connected medical equipment proliferation demands agentless discovery for embedded devices running legacy operating systems. United States rural hospital systems and National Health Service trusts in England accelerate replacement of passive VLAN segmentation. Ransomware targeting imaging equipment compresses deployment schedules.
- Government:Federal contractors and civilian agencies mandate continuous compliance monitoring with immutable access logging. United States defense industrial base suppliers and Australian critical infrastructure operators face binding procurement specifications. Certification requirements favor pre-qualified vendor lists.
- Education:Bring-your-own-device density and limited security staffing drive preference for cloud-native, vendor-managed deployments. State university systems in California and technical colleges in Ontario balance open network access against copyright enforcement obligations.
- Retail:Point-of-sale network segmentation and guest Wi-Fi isolation dominate use cases. Franchise operators in Brazil and shopping mall networks in the United Arab Emirates prioritize rapid deployment over deep integration.
Healthcare absorbs premium pricing for specialized medical device capabilities. Government procurement expands through regulatory mandate diffusion.
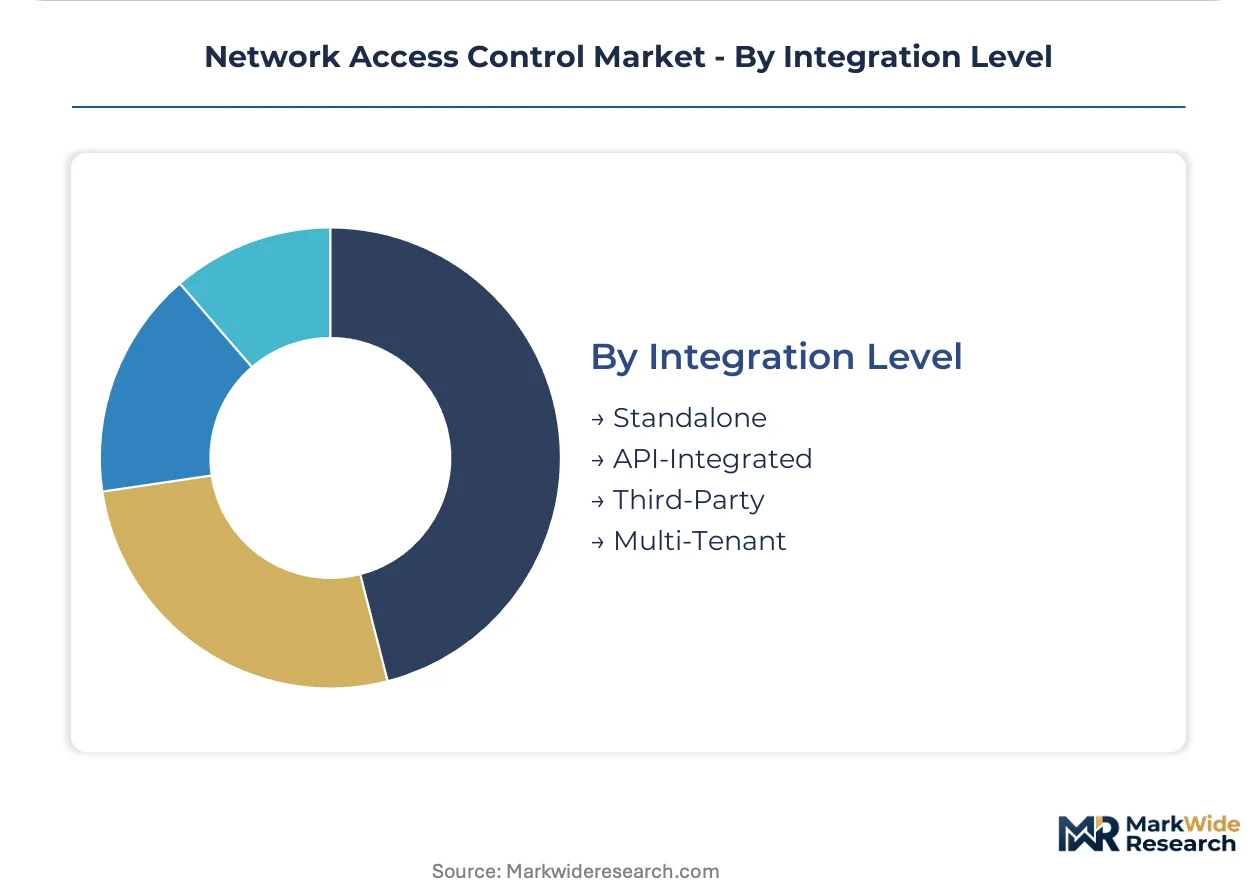
Integration Level:
Architecture choices determine ecosystem lock-in and migration flexibility. API maturity separates modern platforms from legacy appliance generations.
- API-Integrated:RESTful interfaces enable bidirectional data flow with SIEM, SOAR, and identity provider platforms. United States Fortune 500 enterprises and Netherlands-headquartered multinational manufacturers demand these for security orchestration automation. Real-time telemetry ingestion accelerates incident response workflows.
- Multi-Tenant:Isolated policy domains within shared infrastructure serve managed security service provider customer bases. Cloud-native vendors compete through these architectures for mid-market enterprises lacking dedicated security operations.
- Standalone:Self-contained appliances operate without external platform dependencies. Legacy installations in Eastern European industrial facilities and Southeast Asian port authorities persist where internet connectivity remains intermittent.
- Third-Party:Embedded NAC modules within broader network management suites sacrifice depth for administrative consolidation. Small and medium enterprises in Italy and Spain accept functional limitations for reduced vendor management overhead.
API-Integrated deployments capture enterprise commitment. Multi-Tenant architectures scale most efficiently for service provider channels.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics favor domestic software vendors over hardware-dependent suppliers across major economies. The United States runs a substantial trade surplus in cloud-native NAC platforms while importing specialized enforcement ASICs from Asian fabrication centers. European Union member states balance cross-border data flows against localization mandates under the Cybersecurity Act.
United States
Federal contractors and defense industrial base suppliers drive concentrated procurement volume under binding NIST SP 800-207 implementation deadlines. HIPAA Security Rule enforcement by the Department of Health and Human Services compels hospital systems toward continuous compliance architectures. Silicon Valley technology clusters and Boston-area cybersecurity hubs host the dominant vendor development centers for cloud-native access brokers.
Germany
Automotive manufacturing campuses and critical infrastructure operators anchor European demand for on-premises appliance deployments with strict data localization. EU Cybersecurity Act certification requirements filter vendor eligibility toward pre-qualified platforms with conformity assessment documentation. Industrial conglomerates in Bavaria and Baden-Württemberg favor hybrid architectures combining factory-floor enforcement nodes with centralized cloud governance consoles.
Japan
Industrial control system convergence and operational technology security mandates reshape procurement across manufacturing and energy utilities. METI guidelines on critical infrastructure protection tighten device visibility requirements for sector operators. Tokyo-based enterprise headquarters and Osaka-Kobe industrial corridors concentrate deployment activity for unified IT-OT access governance platforms.
Singapore
Financial services firms and regional headquarters operations drive cloud-native NAC adoption for rapid multi-site expansion across Southeast Asian footprints. Monetary Authority of Singapore cybersecurity notices mandate immutable access logging for banking and insurance sector entities. Marina Bay financial district technology clusters host managed security service providers delivering subscription-based access governance to regional mid-market enterprises.
Australia
Healthcare networks and provincial government agencies outsource continuous compliance verification to managed NAC providers compensating for internal cybersecurity staffing gaps. Critical infrastructure security obligations under federal legislation compel energy and water utilities toward active admission controls. Sydney and Melbourne metropolitan areas concentrate procurement activity for vendor-staffed security operations center deployments.
Network Access Control Market Vendor Landscape
Concentration sits with integrated networking vendors possessing embedded switching and security stack capabilities. The vendor base stratifies across three tiers: diversified technology conglomerates with campus-to-cloud portfolios, pure-play cybersecurity specialists with deep protocol expertise, and cloud-native challengers delivering agentless assessment through browser-managed consoles. Strategic moves center on API ecosystem expansion and managed service provider channel development as primary growth vectors.
Among diversified networking incumbents, Cisco Systems exemplifies the integrated platform archetype spanning enterprise switching infrastructure through cloud-delivered access brokers. Fortinet occupies a position within the converged security fabric tier, while Portnox represents the pure-cloud delivery model reducing customer infrastructure overhead. These three anchors illustrate the competitive spectrum from capital-intensive hardware bundling toward lightweight subscription consumption.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Hewlett Packard Enterprise Company |
| Fortinet, Inc. |
| Forescout Technologies, Inc. |
| Juniper Networks, Inc. |
| Palo Alto Networks, Inc. |
| Portnox |
| Extreme Networks, Inc. |
| Arista Networks |
| Others |
Supply Flow & Price Mechanics
Capacity reservation agreements with TSMC fabrication facilities lock in ASIC supply for hardware-centric vendors while anchoring price visibility across multi-year procurement cycles. These contractual structures tether enforcement engine costs to semiconductor wafer allocation queues, compressing margin flexibility for appliance-dependent suppliers.
Pricing Analysis
Industrial OEM buyers anchor subscription-based SaaS pricing across mid-market cloud-native deployments. Three-tier pricing structure across premium, standard, and economy levels separates API-integrated enterprise platforms from standalone appliance bundles. Pricing pressure stems from certificate management complexity delaying production rollouts despite purchased licenses. Healthcare networks demonstrate lowest price sensitivity given ransomware exposure, while education sector procurement exhibits acute budget constraint responsiveness.
Supply Chain Analysis
Strategic stockpile preferences dominate hardware appliance procurement as vendors buffer against TSMC fabrication queue volatility. Specialized ASIC supply concentrates in Taiwan, South Korea, and United States foundry capacity. Component sourcing draws from silicon wafers, network processor units, and embedded security modules. Single-source vulnerability around TSMC advanced node access creates delivery volatility. Distribution runs through value-added distributors consolidating managed security service provider programs.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Zero-trust mandate acceleration constitutes a high-growth disruption as NIST SP 800-207 deadlines compress federal procurement timelines toward continuous verification architectures.
For Market Incumbents: Compound switching infrastructure dominance through deeper API ecosystem integration with SIEM and SOAR platforms. Cloud-native challengers threaten appliance-dependent revenue streams; vertical integration into cloud-delivered access brokers defends margin pools. For New Entrants and Emerging Players: Differentiate on agentless medical device discovery capabilities targeting United States rural hospital systems with outsourced security operations center staffing gaps. Managed NAC services for Australian provincial governments and Canadian healthcare networks represent the most penetrable white-space. Lead with subscription consumption models bundling policy management and threat intelligence feeds. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among cloud-native vendors with multi-tenant architectures serving managed security service provider channels. Five-to-ten year viability favors platforms with pre-certified EU Cybersecurity Act documentation. Acquisition targets should demonstrate API-first integration depth. The signal to watch is NIST framework adoption diffusion beyond federal contractors into state-level procurement mandates.| Strategic Initiative | Industry Significance |
|---|---|
| API Ecosystem Expansion | SIEM and SOAR platform connectivity accelerates incident response automation for Fortune 500 enterprises. |
| Managed Security Service Provider Channel Development | Value-added distributors in North America consolidate subscription bundling for resource-constrained mid-market buyers. |
| EU Cybersecurity Act Certification Investment | Pre-qualified vendor status filters competitive eligibility for German critical infrastructure operators. |
| Medical Device Discovery Capability Buildout | Agentless assessment tools address visibility gaps in United States hospital embedded equipment fleets. |
| Cloud-Native Access Broker Launch | Software-defined perimeter architectures displace hardware appliances in Singapore financial services deployments. |
Methodological Framework
Findings reconcile primary fieldwork against secondary review of regulatory filings, vendor technical documentation, and procurement database records. Chief information security officers, network operations directors, and healthcare biomedical engineers provided deployment timeline and budget allocation perspectives. Federal contracting officers and managed security service provider channel managers supplied procurement specification and pricing trend insights. SEC 10-K disclosures, NIST framework implementation guidance, and hospital GPO contract databases furnished secondary validation. Bottom-up installation tracking and top-down market sizing triangulate volume estimates.
Segmentation dimensions modeled span deployment model, solution architecture, end-user vertical, and integration complexity across the analysis window. Cloud-native versus on-premises mix, healthcare versus government procurement intensity, and API-integrated versus standalone architecture penetration inform value projections. CAGRs derive from installation run-rate extrapolation against compliance deadline schedules. Policy management renewal cycles and medical device discovery tool attach rates constitute industry-specific forecast inputs.
The analysis sits within stated boundaries; outcomes outside NIST implementation adherence or TSMC capacity allocation stability would require recalibration. Forecasts reflect assumptions around regulatory enforcement continuity and semiconductor supply normalization. Revision becomes warranted when ransomware campaign intensity or federal procurement freeze thresholds cross materiality levels.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Access Control Systems
Programmable Safety Systems Market
Access Control Systems
Airport Passenger Screening System Market
Access Control Systems
Padlock Smart Lock Market
Access Control Systems
Global Industrial Security Systems Market
Access Control Systems
Automatic Gate and Door Opening System Market
Access Control Systems
Global Home Security Systems Market
Access Control Systems
North America Proximity Access Control Market
Access Control Systems
Global Smart Lock Market
Access Control Systems
France Access Control Market
Access Control Systems
Middle East and Africa Pin-Based Access Control Market
Access Control Systems
Bluetooth Smart Lock Market
Access Control Systems
Asia Pacific Access Control Software Market
Access Control Systems
Latin America Proximity Access Control Market
Access Control Systems
Australia Industrial Barrier Systems Market
Access Control Systems
Europe Home Security System Market
Access Control Systems
North America Pin-Based Access Control Market