
 Antivirus Software Package Market | 2026-2036
Antivirus Software Package Market Size, Share, and Industry Trends Forecast 2026-2036
Antivirus Software Package Market Intelligence
Modular subscription tiers is decoupling antivirus features from monolithic enterprise suites, letting buyers mix endpoint detection, VPN, and identity tools. Microsoft Corporation leverages its Windows install base to bundle Defender capabilities at no incremental cost. Kaspersky Lab competes through deep specialization in government-grade threat intelligence. Bitdefender SRL anchors its position via channel control across European managed service providers.
An antivirus software package comprises signature-based scanners, heuristic engines, behavioral monitors, and cloud-connected threat intelligence feeds engineered to detect, quarantine, and neutralize malicious code across endpoints. The product serves commercial and institutional buyers by preventing data exfiltration, ransomware encryption, and unauthorized system access before payload execution. Enterprise deployments dominate value generation as CIOs consolidate endpoint, server, and mobile protection under single-vendor contracts with managed service overlays. Cloud-based delivery is expanding fastest among SMBs lacking dedicated security operations centers, while on-premises installations retain favor in regulated sectors where data residency rules block external telemetry transmission.
The EU AI Act and NIS2 Directive compel critical infrastructure operators to deploy certified endpoint protection with mandatory incident reporting, directly lifting enterprise antivirus procurement budgets. The U.S. Cybersecurity and Infrastructure Security Agency issues binding operational directives that federal agencies patch vulnerabilities within strict windows, sustaining demand for automated patch-management-integrated suites. Japan's METI cybersecurity framework pushes manufacturers toward JIS-compliant supply chain security audits, widening antivirus deployment beyond traditional IT perimeters. Stakeholders must weigh whether cloud-native architectures or sovereign-hosted instances better satisfy diverging cross-border compliance obligations.
Market Dynamics
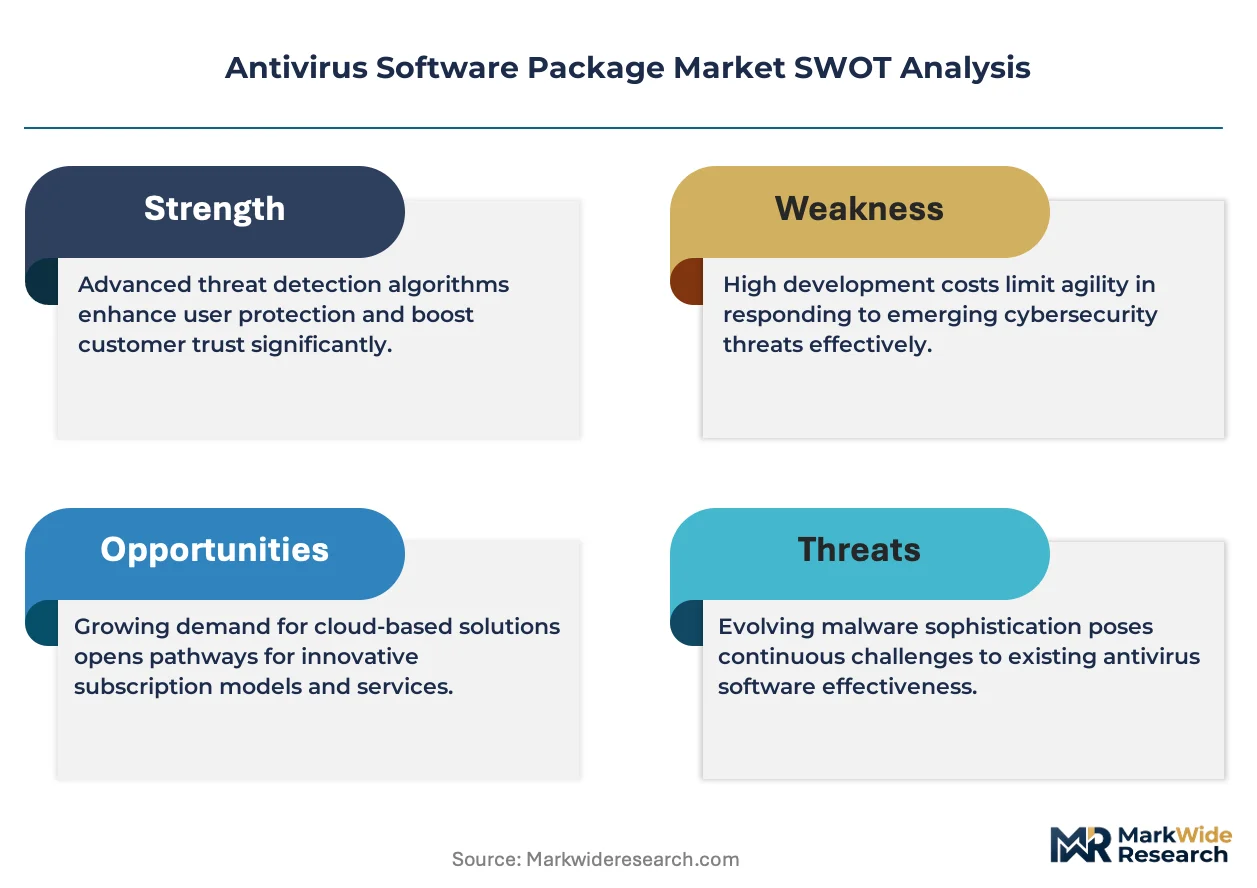
Regulatory fragmentation across the United States, Germany, and Japan is forcing antivirus vendors to architect parallel compliance stacks, inflating R&D overhead while compressing time-to-market for unified product releases.
Growth Catalysts
- EU AI Act certification mandates:Critical infrastructure operators in Germany must deploy certified endpoint protection with automated incident reporting, directly expanding enterprise procurement budgets for compliant suites.
- Cloud-native delivery architectures:SMBs lacking dedicated security operations centers are adopting browser-administered endpoint protection fastest, bypassing on-premises hardware constraints entirely.
- Japan METI supply chain audits:Manufacturers across automotive and electronics verticals now face JIS-compliant cybersecurity requirements, extending antivirus deployment to operational technology networks previously unsecured.
Market Restraints
- Telemetry residency conflicts:Diverging data sovereignty rules between the EU AI Act and U.S. CLOUD Act create architectural paralysis for vendors attempting single-stack global delivery.
- Skilled analyst scarcity:Managed service providers report 18-month backlogs for certified security operations engineers capable of tuning behavioral detection engines.
- Signature database latency:Air-gapped installations in regulated sectors cannot match cloud-connected threat intelligence refresh rates, leaving persistent vulnerability windows.
Strategic Opportunities
- Operational technology convergence:Antivirus vendors integrating industrial control system protocols with endpoint detection capture manufacturing plant networks previously served by segmented niche players.
- India BIS cybersecurity standards:Upcoming mandatory certification for financial institutions creates first-mover advantage for vendors pre-positioning sovereign-hosted threat intelligence nodes.
- Channel-native bundling:European managed service providers are white-labeling modular endpoint protection into broader IT outsourcing contracts, displacing direct enterprise sales cycles.
Industry Challenges
- False positive tuning at scale:Behavioral engines generating excessive quarantine events erode IT administrator trust and drive uninstall rates among commercial buyers.
- Legacy system integration friction:Enterprises running Windows Server 2012 and earlier releases face patch dependency conflicts with modern endpoint agents, forcing parallel maintenance contracts.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Antivirus Software Package Market |
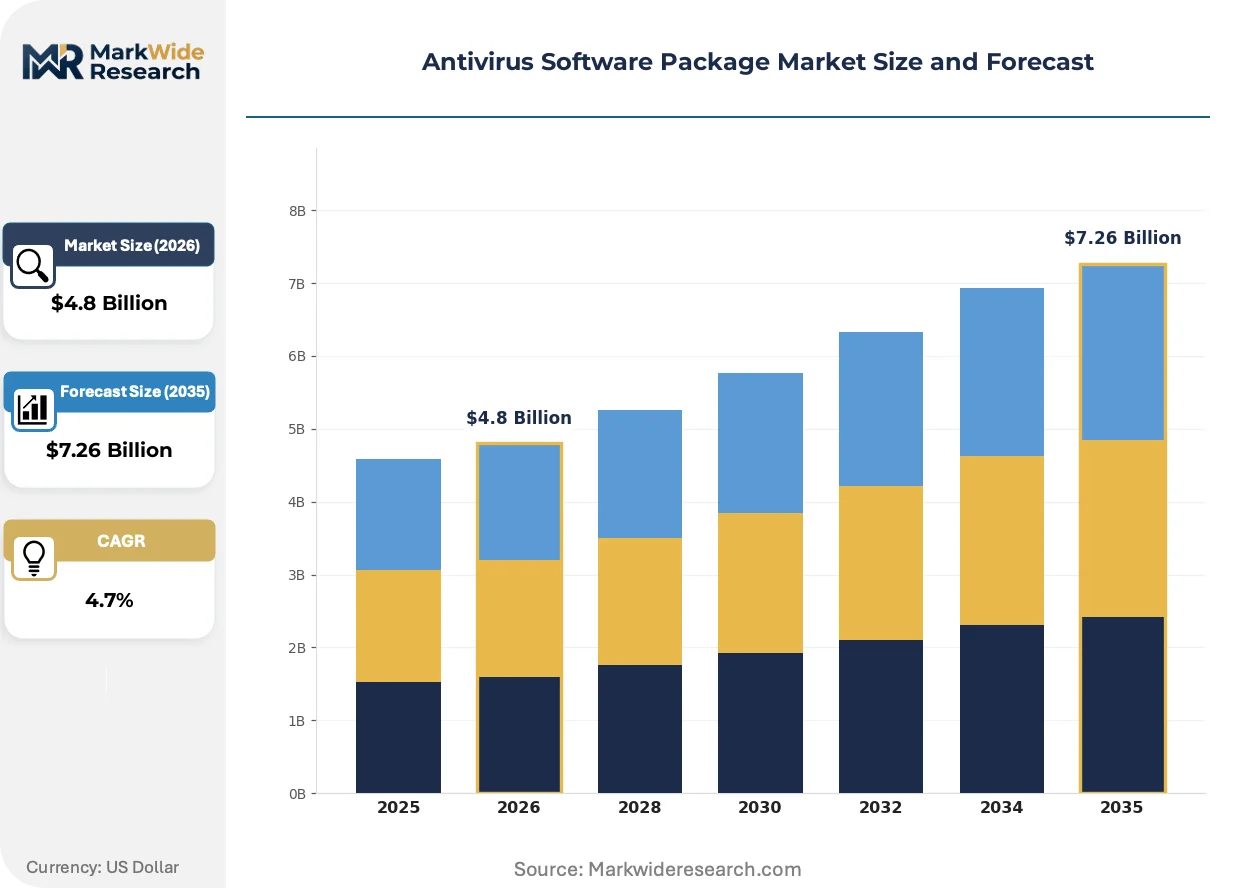
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $7.26 Billion |
| CAGR (2026 – 2036) | 4.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Basic, Premium, Enterprise, Cloud-based Deployment: On-premises, Cloud, Hybrid, Virtual End User: Individuals, SMBs, Enterprises, Government Service Type: Managed, DIY, Standalone, Subscription |
| Companies Covered | Bitdefender SRL, Avast Software s.r.o., McAfee LLC, Kaspersky Lab, Microsoft Corporation, Symantec Corporation, F-Secure Oyj, AVG Technologies CZ, Avira Operations GmbH & Co. KG, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Antivirus Software Package Market Strategic Shifts & Innovations
Antivirus architecture is fragmenting from monolithic suites into composable security primitives, with buyers assembling protection stacks from specialized vendors rather than accepting vendor-locked bundles.
Extended detection and response platforms are modularizing signature scanning, behavioral analytics, and threat hunting into API-connected components. Mid-market enterprises lacking security operations centers now subscribe to managed detection services that stitch these modules together without internal engineering headcount. This decomposition is compressing pricing power for traditional suite vendors while elevating specialist players with best-of-breed telemetry quality.
The EU AI Act's mandatory conformity assessments for high-risk AI systems now encompass automated threat detection engines deployed in critical infrastructure. Vendors must document training data provenance and algorithmic decision explainability to maintain market access in Germany and France. Financial services institutions are responding by demanding sovereign-hosted model inference to satisfy both regulatory audit trails and internal risk committee requirements.
Buyer preference is hardening around consumption-based licensing tied to actual endpoint counts rather than upfront enterprise agreements. Channel partners in the United States are displacing direct vendor relationships by offering month-to-month elasticity with embedded professional services. This shift is most pronounced among healthcare delivery networks facing unpredictable merger activity and fluctuating device populations.
Antivirus Software Package Market Segmentation
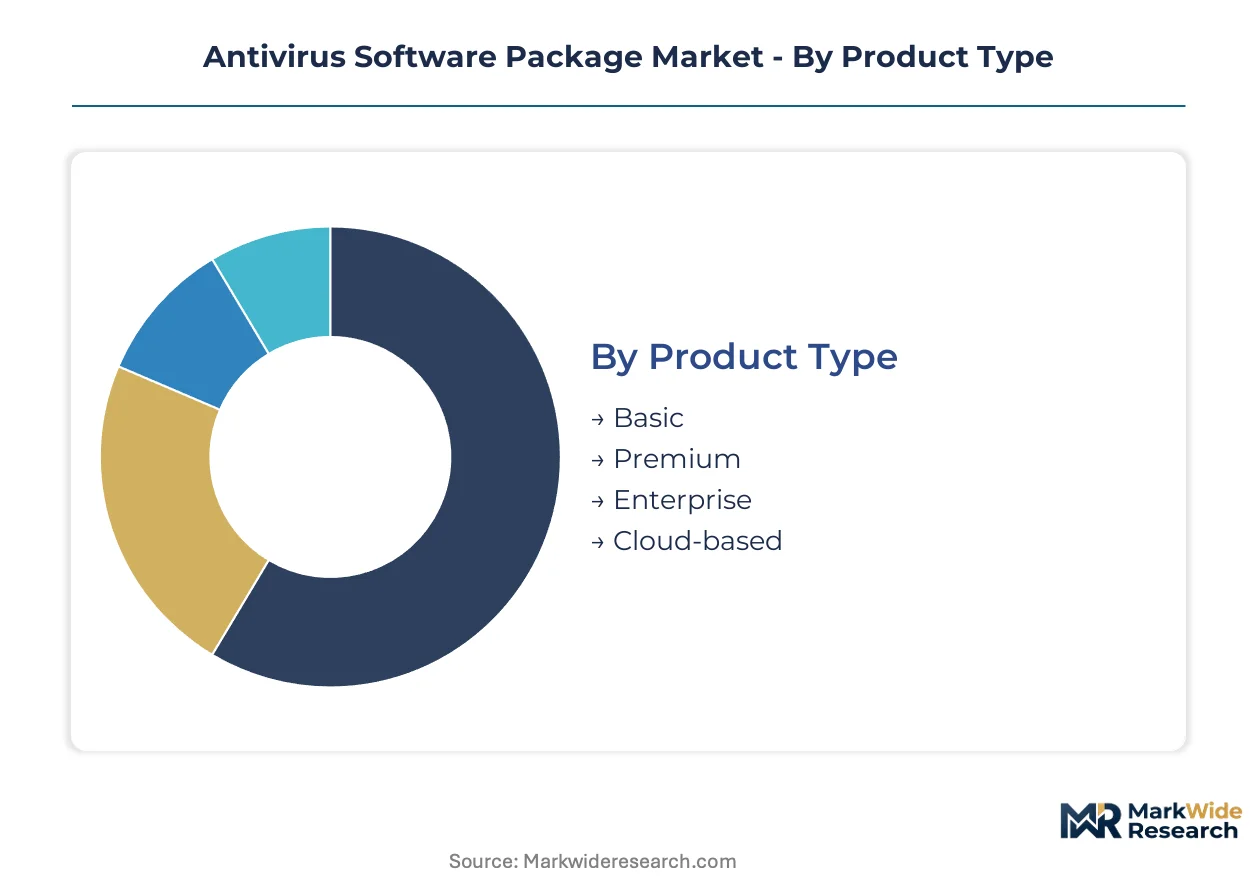
Segmentation in the antivirus software package market reveals divergent capital requirements across deployment modes and customer tiers. Enterprise buyers consolidate spending under multi-year contracts while cloud-native delivery reshapes cost structures for smaller buyers.
Product Type:
Capital intensity varies sharply across product tiers, with enterprise suites demanding the heaviest upfront engineering investment in behavioral analytics engines and threat intelligence infrastructure.
- Enterprise:Comprehensive endpoint protection suites integrate endpoint detection and response, extended detection and response, and managed threat hunting capabilities. Demand concentrates among German critical infrastructure operators facing EU AI Act certification mandates for automated incident reporting systems. CIOs consolidate server, mobile, and operational technology protection under single-vendor contracts with service overlays.
- Cloud-based:Browser-administered protection layers deliver signature scanning and behavioral monitoring without on-premises hardware. United States healthcare delivery networks lacking dedicated security operations centers adopt this tier fastest, drawn by month-to-month elasticity during unpredictable merger activity. Vendors architect sovereign-hosted instances to satisfy diverging data residency rules.
- Premium:Mid-market bundles add VPN, identity protection, and password management to core scanning functions.
- Basic:Signature-based scanners target price-sensitive individual buyers with minimal heuristic capabilities.
Enterprise absorbs the bulk of installed capacity; cloud-based is expanding most quickly.
Deployment:
Deployment architecture determines ongoing operational expenditure more than initial licensing, with air-gapped installations imposing perpetual maintenance overhead.
- Cloud:Telemetry-connected agents stream endpoint data to vendor-operated security operations centers for real-time threat correlation. Japanese manufacturers facing METI supply chain audits extend cloud protection to operational technology networks previously unsecured. SMBs bypass hardware procurement entirely through this model.
- On-premises:Self-hosted management consoles and signature databases operate within buyer data centers. Regulated sectors in Germany enforce this mode under data sovereignty rules blocking external telemetry transmission. Air-gapped installations suffer signature database latency against cloud-connected refresh rates.
- Hybrid:Split architectures retain sensitive scanning on-premises while leveraging cloud analytics for non-critical endpoints.
- Virtual:Containerized agents protect virtual desktop infrastructure and serverless computing environments.
On-premises retains the largest installed base; cloud is climbing the fastest as channel-native bundling displaces direct enterprise sales cycles.
End User:
Customer scale dictates procurement complexity, with government tenders imposing the most stringent certification and audit requirements.
- Enterprises:Multi-thousand endpoint deployments consolidate under managed service provider contracts with embedded professional services. United States federal agencies sustain demand through CISA binding operational directives mandating automated patch management integration. Procurement teams negotiate consumption-based licensing tied to actual device counts.
- Government:National security and critical infrastructure operators demand government-grade threat intelligence feeds with documented training data provenance. German authorities enforce EU AI Act conformity assessments for high-risk automated detection engines. Vendors must document algorithmic decision explainability to maintain market access.
- SMBs:Resource-constrained buyers subscribe to modular endpoint protection without internal engineering headcount.
- Individuals:Single-license purchases respond to consumer awareness campaigns and bundled operating system offerings.
Enterprises command the dominant share of contract value; government is gaining share fastest amid tightening cybersecurity mandates.
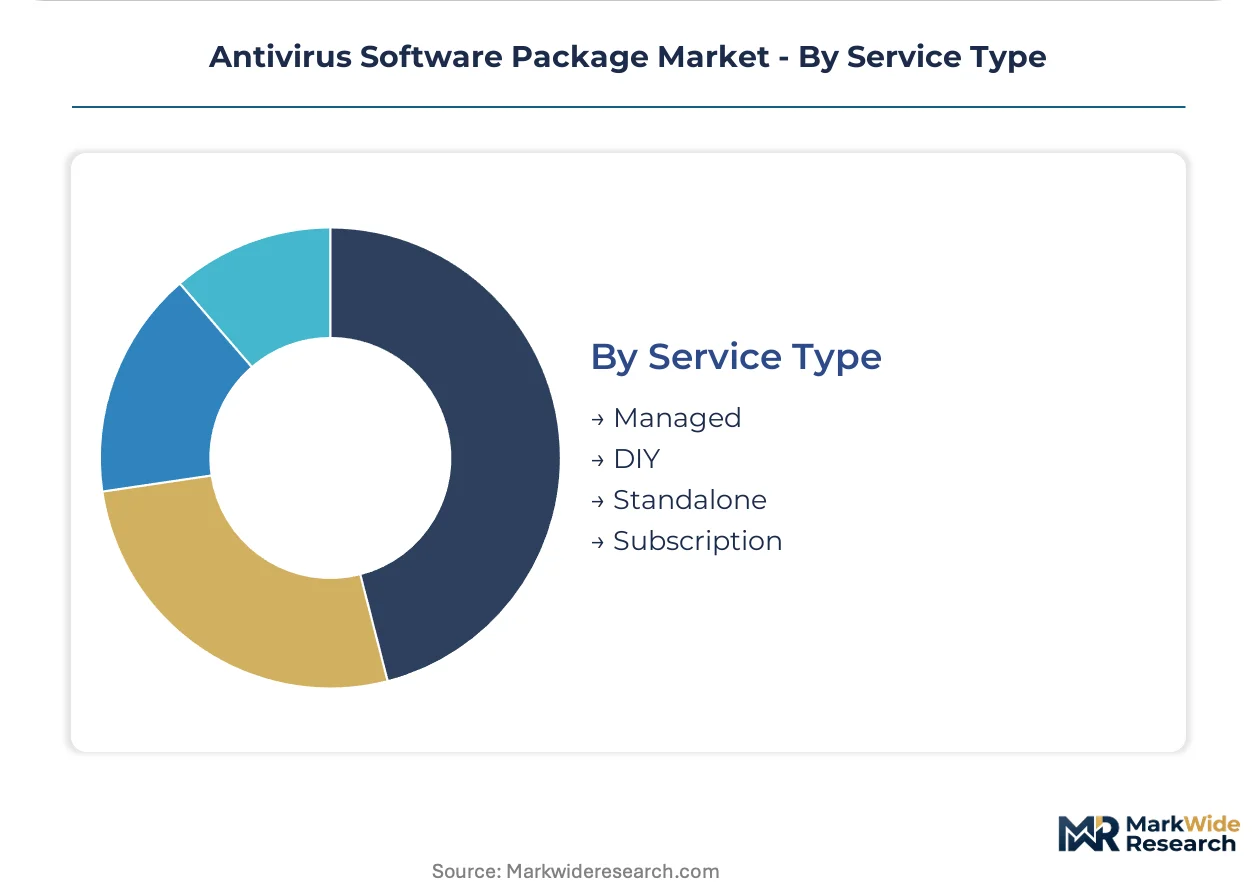
Service Type:
Service configuration determines margin structure, with managed offerings capturing recurring revenue at higher retention rates.
- Managed:Vendor or partner-operated security operations centers deliver 24/7 threat monitoring, incident response, and tuning of behavioral detection engines. European managed service providers white-label modular endpoint protection into broader IT outsourcing contracts. Eighteen-month backlogs for certified security analysts constrain expansion capacity.
- Subscription:Recurring licensing models replace perpetual licenses across all customer tiers, with monthly elasticity preferred by buyers facing fluctuating device populations.
- DIY:Self-administered consoles place configuration burden on buyer IT staff.
- Standalone:Unbundled point products serve buyers assembling composable security stacks from specialized vendors.
Managed services generate the highest contract values; subscription is scaling most rapidly as preference hardens around consumption-based pricing.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Antivirus software production concentrates in technology hubs across Germany, the United States, and Japan, while consumption spreads through regulated critical infrastructure networks in each market. Enterprise procurement flows toward vendors with certified compliance stacks for local data sovereignty rules.
United States
Federal agencies drive enterprise endpoint protection spending through binding operational directives from CISA mandating automated patch management integration. Healthcare delivery networks in the Northeast Corridor and California subscribe to cloud-native suites with month-to-month elasticity during merger activity. The Department of Defense sustains demand for government-grade threat intelligence feeds with documented training data provenance.
Germany
Critical infrastructure operators under the EU AI Act must deploy certified endpoint protection with automated incident reporting, directly expanding procurement budgets for compliant suites. Industrial manufacturers in Bavaria and Baden-Württemberg extend antivirus deployment to operational technology networks previously unsecured. Data sovereignty rules block external telemetry transmission, favoring on-premises installations with sovereign-hosted management consoles.
Japan
Automotive and electronics manufacturers face METI cybersecurity framework mandates pushing JIS-compliant supply chain security audits. Production facilities in the Chubu region around Nagoya and Kansai industrial belt around Osaka now require endpoint protection for operational technology networks. Cloud delivery is expanding fastest among SMBs in the Tokyo Capital Area lacking dedicated security operations centers.
India
Financial institutions anticipate mandatory BIS cybersecurity standards creating first-mover advantage for vendors pre-positioning sovereign-hosted threat intelligence nodes. IT services clusters in Bangalore and Hyderabad drive managed detection service adoption among mid-market enterprises. Channel partners white-label modular endpoint protection into broader IT outsourcing contracts, displacing direct vendor sales cycles.
United Kingdom
Financial services institutions in the City of London demand sovereign-hosted model inference to satisfy regulatory audit trails and internal risk committee requirements. NHS trusts consolidate endpoint protection under single-vendor contracts with managed service overlays. The National Cyber Security Centre issues guidance sustaining procurement for automated threat hunting capabilities across critical national infrastructure.
Antivirus Software Package Market Key Industry Players
Diversified conglomerates compete with focused pure-play specialists across a market structure that fragments between bundled platform vendors and modular component suppliers. Microsoft leverages its operating system install base to distribute protection at no incremental cost, compressing pricing power for standalone suite vendors. Three archetypes dominate: platform bundlers with captive distribution channels, threat intelligence specialists serving government-grade requirements, and channel-native providers embedding protection in managed service contracts. Competitive moves concentrate on M&A to acquire behavioral analytics engines and strategic partnerships with European managed service providers to bypass direct enterprise sales cycles.
Within the threat intelligence specialist tier, Kaspersky Lab and Bitdefender SRL exemplify divergent geographic anchoring strategies. Microsoft Corporation occupies a position as the platform bundler archetype, leveraging captive distribution through its operating system dominance. Among European channel-native providers, F-Secure Oyj sits within the managed service integration segment, embedding endpoint protection in broader IT outsourcing frameworks. These three companies represent the primary competitive vectors shaping procurement patterns across enterprise, government, and mid-market tiers.
| Leading Market Players |
|---|
| Bitdefender SRL |
| Avast Software s.r.o. |
| McAfee LLC |
| Kaspersky Lab |
| Microsoft Corporation |
| Symantec Corporation |
| F-Secure Oyj |
| AVG Technologies CZ |
| Avira Operations GmbH & Co. KG |
| Others |
Cost & Logistics Intelligence
Certification-grade divergence between EU AI Act-compliant enterprise suites and commodity signature scanners splits both pricing power and engineering investment across parallel supply chains. German critical infrastructure operators pay premiums for automated incident reporting capabilities while SMBs in the United States subscribe to browser-administered tiers with month-to-month elasticity, forcing vendors to maintain dual cost structures.
Pricing Analysis
Margin tightening in cloud-native tiers reflects Microsoft Defender's zero-incremental-cost bundling through Windows install bases. Subscription-SaaS models dominate, with consumption-based licensing tied to actual endpoint counts displacing upfront enterprise agreements. Price differentiation rests on certification level—EU AI Act conformity assessments command premiums—and volume scale, with healthcare delivery networks negotiating elasticity clauses. Cost compression accelerates in basic signature-scanning tiers as channel partners white-label modular components. SMBs exhibit highest price sensitivity; government buyers prioritize documented training data provenance over cost.
Supply Chain Analysis
EU data sovereignty mandates and U.S. CLOUD Act telemetry residency rules reshape vendor sourcing toward sovereign-hosted threat intelligence nodes in Germany, the United States, and India. Engineering talent draws from Bangalore, Tel Aviv, and Tallinn clusters; behavioral analytics engines hinge on specialized machine learning infrastructure. Single-source vulnerability concentrates in cloud-connected signature database refresh systems. Distribution runs through European managed service providers embedding protection in broader IT outsourcing contracts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical-integration momentum centers on captive threat intelligence infrastructure as vendors race to control upstream data provenance and downstream channel relationships.
For Market Incumbents: Cement channel control across European managed service providers before modular decomposition erodes pricing power. Acquire behavioral analytics specialists to close engineering talent gaps. Defend against Microsoft's operating system bundling by emphasizing government-grade certification depth. For New Entrants and Emerging Players: Mid-market manufacturers in Japan's Chubu region present an underserved buyer archetype facing METI supply chain audit mandates without dedicated security operations centers. Target operational technology convergence opportunities in automotive electronics. Pursue white-label partnerships with Indian IT services clusters in Bangalore and Hyderabad. For Investors and Strategic Acquirers: Re-rating potential sits with threat intelligence specialists possessing sovereign-hosted inference capabilities given EU AI Act conformity assessment requirements. Long-term viability favors vendors with documented algorithmic explainability and JIS-compliant supply chain security positioning. Watch India BIS cybersecurity standard implementation timing as inflection indicator for financial institution procurement cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Sovereign-Hosted Threat Intelligence Node Deployment | Satisfies EU AI Act and CLOUD Act telemetry residency conflicts for German and U.S. government buyers. |
| Operational Technology Protocol Integration | Captures manufacturing plant networks in Japan's automotive belt previously served by niche players. |
| Channel-Native MSP Partnership | Displaces direct enterprise sales cycles through European managed service provider white-label embedding. |
| Behavioral Analytics Engine Acquisition | Closes eighteen-month certified security analyst backlogs constraining managed service expansion. |
| Consumption-Based Licensing Platform | Delivers month-to-month elasticity for U.S. healthcare networks facing unpredictable merger activity. |
Research Approach
Trade association data, regulatory filings, and customs records anchored secondary inputs for this antivirus software package market analysis. Primary interviews with chief information security officers, managed service provider operations leads, channel partner sales directors, and regulatory compliance officers combined with bottom-up and top-down triangulation. Secondary sources encompassed EU AI Act implementation guidance, CISA binding operational directives, METI cybersecurity framework documentation, SEC 10-K disclosures from listed vendors, and hyperscaler security capex breakdowns.
Data-stream reconciliation across deployment mode, organization size, vertical sector, integration complexity, and regional regulatory cluster shaped the analytical framework. CAGRs derived from segment-level endpoint count projections and average revenue per user trajectories across the analysis window. Industry-specific forecast inputs included EU AI Act certification rollout schedules and Japan METI supply chain audit implementation phases.
Revisions become necessary when regulatory divergence between EU AI Act and U.S. CLOUD Act intensifies, sovereign data localization mandates proliferate, or behavioral detection engine false positive rates trigger enterprise uninstall cascades. Forecasts reflect documented assumptions regarding certification timeline adherence and channel partner conversion rates. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Risk-Based Authentication (RBA) Market
Security Software
Key Management Service Market
Security Software
Data Leakage Prevention Product Market
Security Software
Europe User Provisioning Market
Security Software
Global User Activity Monitoring Market
Security Software
United States Lawful Interception Market
Security Software
Global Reputation Protection Software Market
Security Software
Global SMS Firewall Market
Security Software
Passwordless Authentication Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Spain Endpoint Detection and Response Market
Security Software
Global Optical Encryption Market
Security Software
Security Software for Consumers Market
Security Software
Hardware Encryption Market
Security Software
US Evidence Management Market
Security Software
Single Sign-On Market