
 AI in Security Market | 2026-2036
AI in Security Market Size, Share, and Industry Trends Forecast 2026-2036
AI in Security Market Analysis
Behavioral analytics tier upgrades is reorganizing competitive dynamics across the AI in security landscape. CrowdStrike leverages endpoint detection algorithms to sustain technology leadership in threat identification. Palo Alto Networks anchors its position through integrated network security platforms that span cloud and on-premises environments. Darktrace differentiates via self-learning immune system architectures that operate autonomously against novel attack vectors.
AI in security encompasses machine intelligence systems engineered to detect, predict, and neutralize cyber and physical threats through pattern recognition, anomaly detection, and automated response protocols operating at sub-second latency thresholds. These systems process multi-modal data streams including network traffic, biometric signals, and video feeds to protect organizational assets and critical infrastructure from unauthorized access or disruption. Threat detection applications command the largest deployment base due to enterprise urgency around zero-day vulnerability identification, while fraud prevention segments in financial services exhibit the steepest adoption curves as real-time transaction monitoring becomes mandatory. Computer vision solutions within surveillance systems concentrate margin pools where edge-AI hardware and cloud inference services converge.
The EU AI Act imposes strict conformity requirements on biometric identification and emotion recognition systems, compelling vendors to redesign training pipelines and documentation practices for European market access. In the United States, NIST cybersecurity frameworks and SEC disclosure rules are hardening accountability standards for AI-driven risk management tools. Stakeholders must weigh compliance investments against the fragmentation risk of divergent regulatory regimes as jurisdictions race to establish sovereign AI governance models.
Market Dynamics
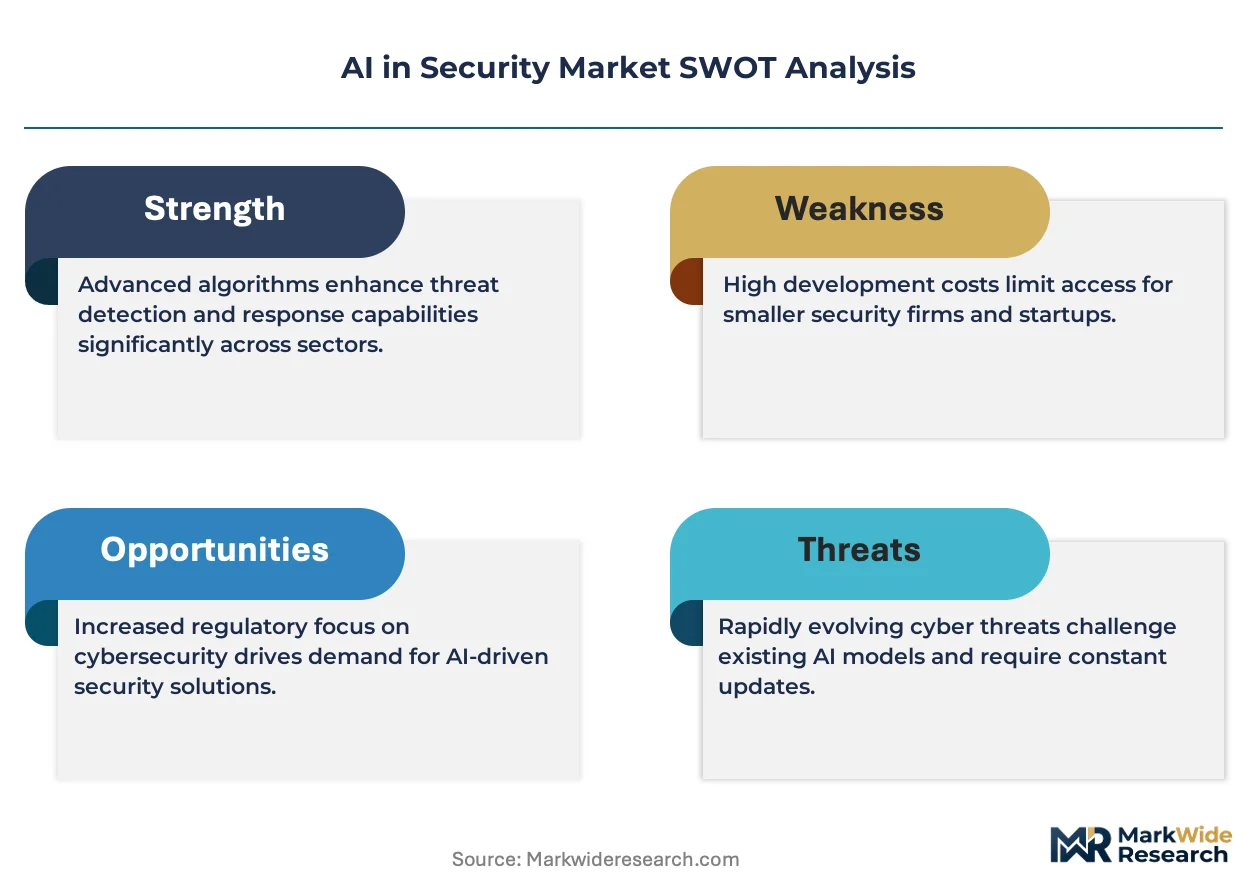
The EU AI Act's biometric surveillance restrictions are compressing vendor margins while redirecting R&D investment toward explainable detection algorithms that satisfy conformity assessment requirements.
Growth Catalysts
- Zero-day detection urgency:Enterprise security teams prioritize autonomous threat identification systems that operate below human response thresholds. Financial institutions mandate real-time transaction monitoring.
- EU AI Act compliance mandates:Automated surveillance system vendors redesign training pipelines to access European markets, creating replacement demand for conformant biometric solutions.
- Edge-AI hardware convergence:Computer vision surveillance systems integrate on-device inference chips with cloud orchestration, enabling sub-50 millisecond response latencies for critical infrastructure protection.
Market Restraints
- GPU supply concentration:Training pipeline scaling depends on Taiwan semiconductor fabrication capacity, exposing vendors to single-source foundry risk.
- Biometric false-positive technical ceiling:Facial recognition accuracy plateaus in low-light conditions, limiting deployment confidence for law enforcement applications.
- Fragmented sovereign AI governance:Divergent NIST, EU AI Act, and China's algorithmic accountability requirements force redundant certification investments.
Strategic Opportunities
- Operational technology security:Manufacturing and energy infrastructure operators deploy AI-driven anomaly detection for industrial control systems, a segment with minimal incumbent saturation.
- SEC disclosure rule tailwinds:Material cybersecurity incident reporting requirements accelerate board-level procurement of AI risk quantification tools.
- Federated learning architectures:Privacy-preserving model training across decentralized data sources enables financial consortium deployments previously blocked by data residency constraints.
Industry Challenges
- Adversarial machine learning expertise scarcity:Security operations centers lack personnel capable of red-teaming evasion-resistant detection models.
- ISO/IEC 27001 AI extension timelines:Certification bodies struggle to operationalize audit criteria for continuously learning systems, delaying enterprise procurement cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | AI in Security Market |
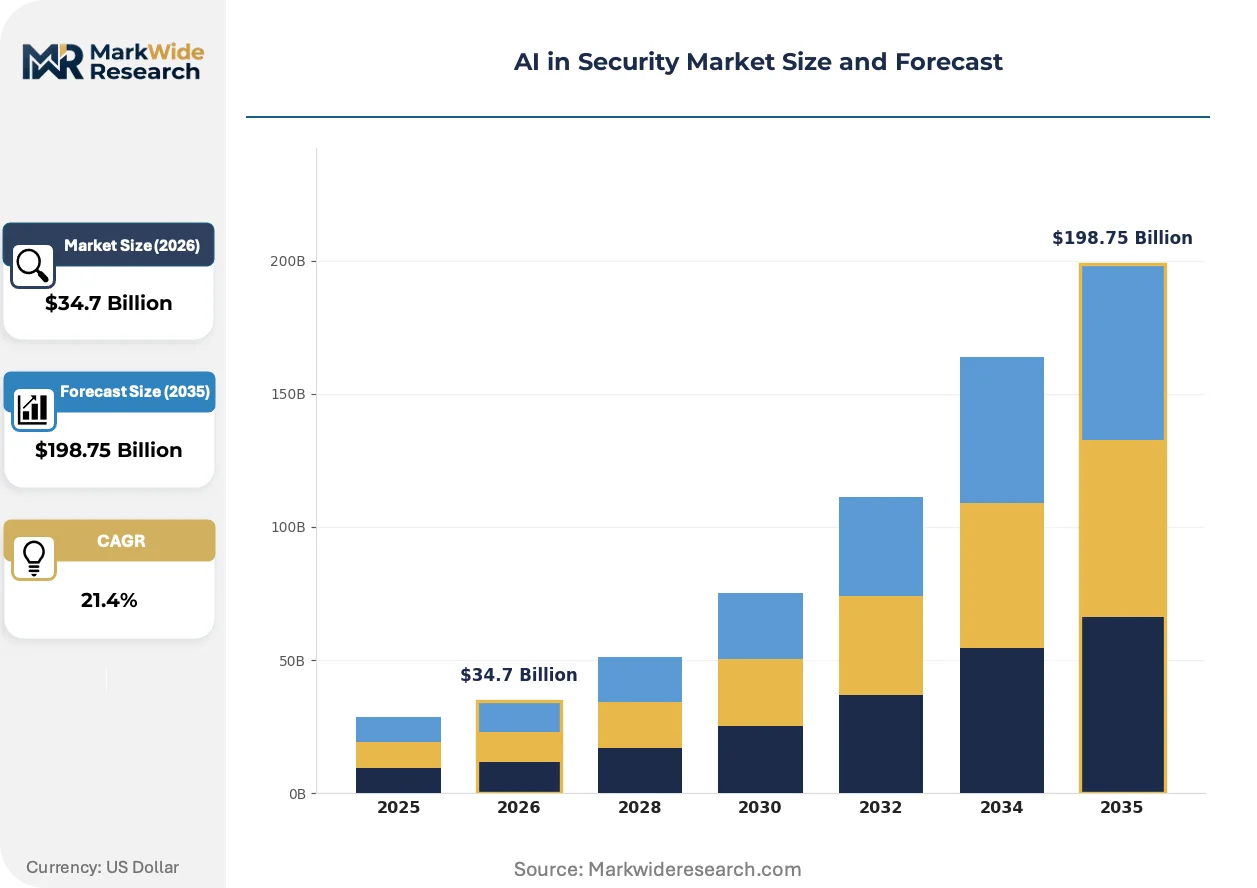
| Market Size in 2026 | $34.7 Billion |
| Market Size in 2035 | $198.75 Billion |
| CAGR (2026 – 2036) | 21.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Deep Learning, Machine Learning, Neural Networks, Computer Vision Application: Threat Detection, Risk Assessment, Incident Response, Fraud Prevention End User: Government, Financial Institutions, Retail, Healthcare Solution: Surveillance Systems, Identity Management, Data Protection, Access Control |
| Companies Covered | Palo Alto Networks, CrowdStrike, Microsoft, Google, AWS, Fortinet, Check Point Software Technologies, SentinelOne, Darktrace, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
AI in Security Market Emerging Trajectories
Foundation model architectures are compressing development timelines for specialized security applications while simultaneously intensifying vendor differentiation pressures around proprietary training data and domain-specific fine-tuning capabilities.
Self-supervised learning for threat detection is bifurcating the endpoint security market. Large enterprises adopt foundation-model-based systems that generalize across attack patterns without signature updates. Mid-market buyers retain supervised learning solutions due to interpretability requirements and audit trail mandates. This technology divergence is fragmenting vendor R&D roadmaps and compressing pricing power for signature-dependent incumbents.
The EU AI Act's prohibited practices list reclassifies emotion recognition in workplace and educational settings as high-risk. Vendors serving human resources and school security segments must obtain third-party conformity assessments or exit those applications entirely. German and French data protection authorities are already enforcing documentation requirements that exceed baseline CE marking obligations.
Security procurement committees now require algorithmic impact assessments before AI tool adoption. Chief information security officers negotiate model cards and bias testing protocols as standard contract terms. This behavioral shift is most pronounced in United States federal contracting, where NIST AI Risk Management Framework alignment determines bid eligibility for critical infrastructure projects.
AI in Security Market Segmentation
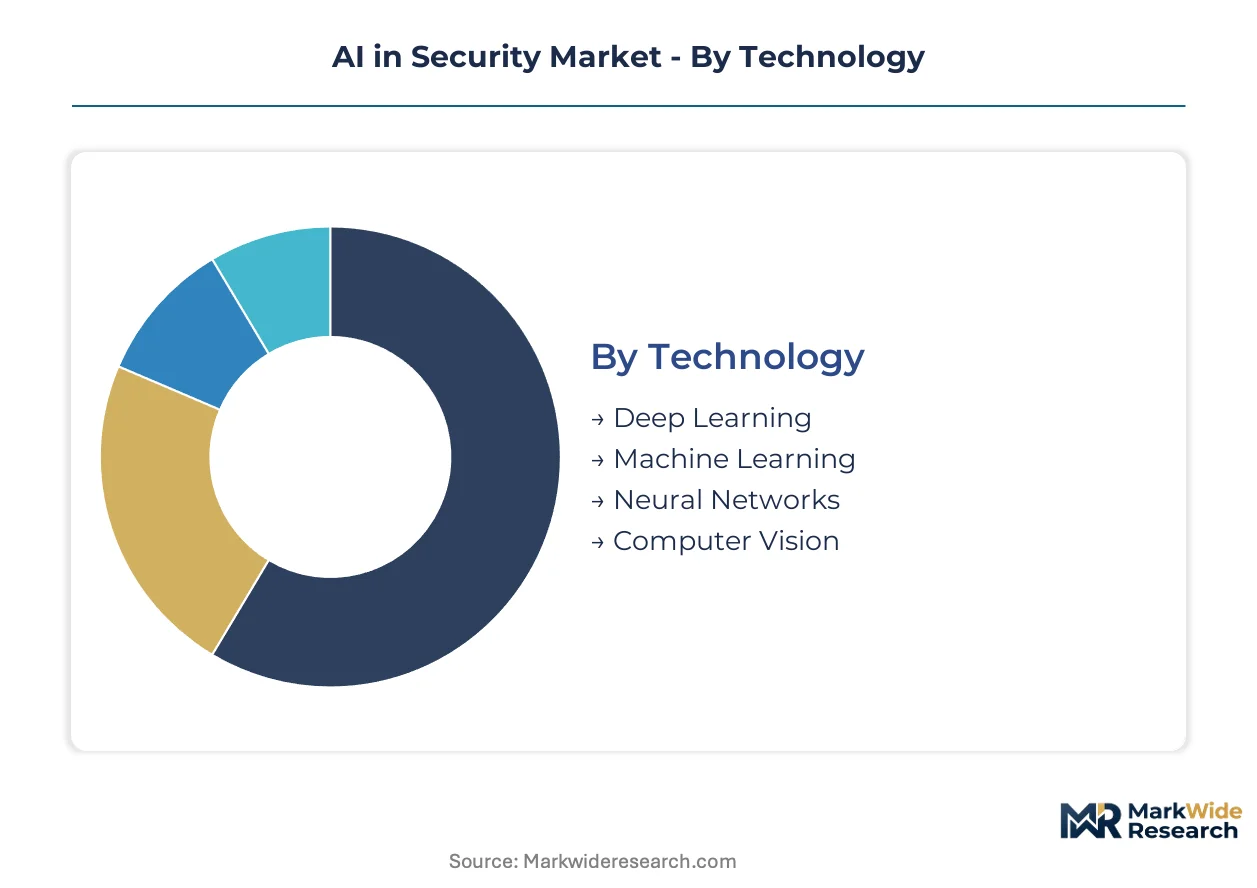
AI in security deployments fragment across four structural dimensions. Technology selection determines latency and accuracy trade-offs. Application focus shapes procurement committee composition and budget authority.
Technology:
EU AI Act conformity requirements differentiate deployment viability across algorithmic architectures, with biometric applications facing mandatory third-party assessment.
- Deep Learning:Multi-layer neural architectures process unstructured threat intelligence at scale. Financial institutions in the United States prioritize these systems for real-time transaction anomaly detection where sub-second inference is mandatory.
- Machine Learning:Supervised and unsupervised statistical models dominate endpoint detection deployments. Government agencies favor interpretable decision boundaries that satisfy NIST AI Risk Management Framework documentation requirements for critical infrastructure contracts.
- Neural Networks:Feedforward and recurrent architectures enable pattern recognition in network traffic analysis.
- Computer Vision:Edge-AI inference pipelines process video feeds for physical security applications.
Machine Learning handles the majority of throughput; Deep Learning is expanding most quickly on share.
Application:
Procurement urgency varies by incident consequence severity, with financial penalties and operational disruption driving budget allocation.
- Threat Detection:Autonomous identification of zero-day vulnerabilities and advanced persistent threats through behavioral baselining. United States federal cybersecurity spending mandates accelerate deployment across civilian and defense agencies.
- Fraud Prevention:Real-time transaction scoring and synthetic identity detection. Retail banks face SEC disclosure rule pressures that elevate board-level procurement authority for these tools.
- Risk Assessment:Quantitative scoring of cyber exposure and control maturity.
- Incident Response:Automated containment and forensic preservation workflows.
Threat Detection commands the largest installed base; Fraud Prevention is climbing the fastest on adoption curves.
End User:
Regulatory exposure and asset criticality determine willingness to pay for autonomous versus human-in-the-loop architectures.
- Financial Institutions:Real-time payment system protection and anti-money laundering compliance. United States banks face overlapping SEC, FFIEC, and state regulator expectations that mandate explainable model outputs for audit defense.
- Government:National security and critical infrastructure protection mandates. Federal procurement committees require NIST framework alignment as bid eligibility criteria.
- Healthcare:HIPAA-covered entities deploy patient data access monitoring.
- Retail:Loss prevention and payment card industry compliance automation.
Financial Institutions concentrate the highest per-seat spending; Government is gaining share fastest on contract volume.
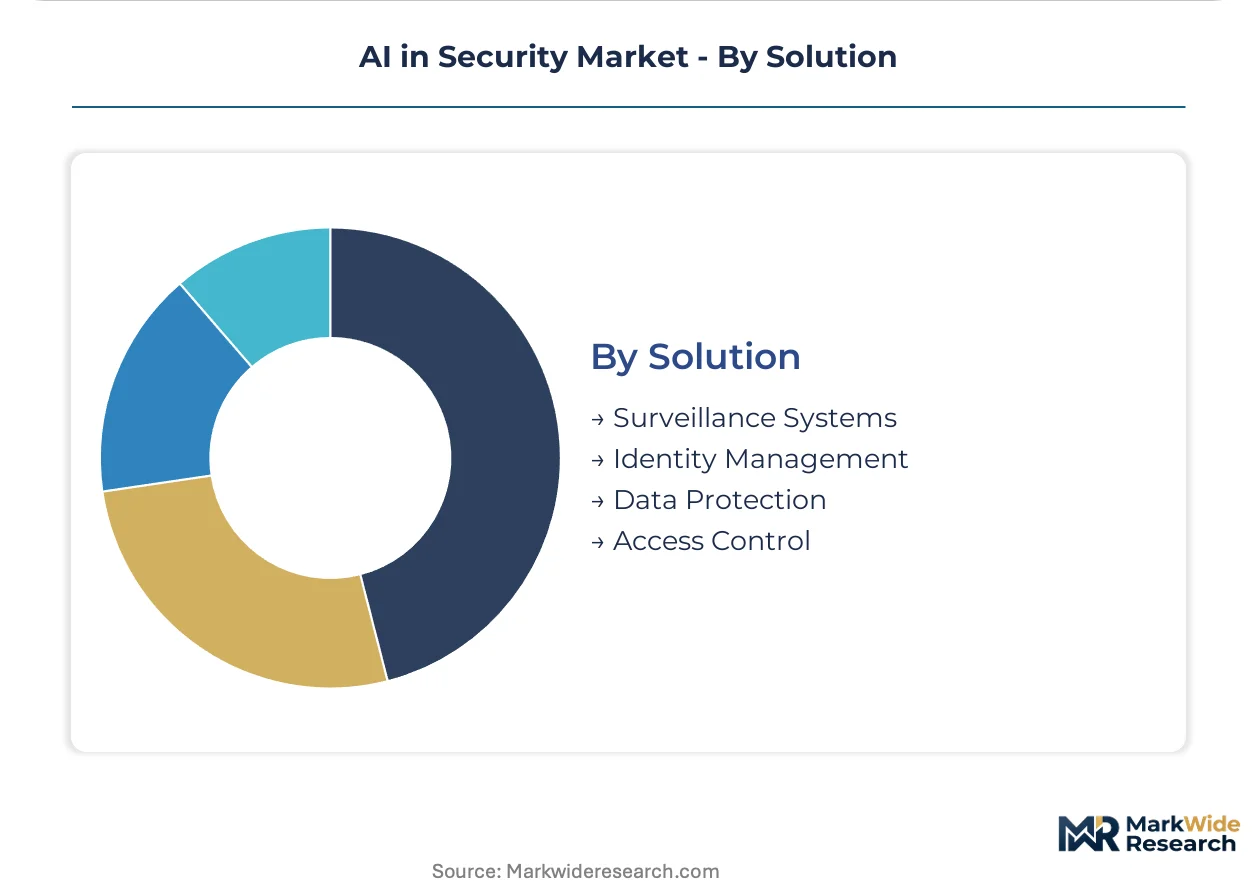
Solution:
Hardware-software integration depth separates margin pools, with edge-device manufacturers capturing value that pure software vendors cannot access.
- Surveillance Systems:Computer vision platforms with on-device inference and cloud orchestration. EU AI Act biometric restrictions compress margins for emotion recognition features while redirecting R&D toward explainable detection algorithms.
- Identity Management:Biometric authentication and privileged access orchestration. German and French data protection authorities enforce documentation requirements exceeding baseline CE marking obligations.
- Data Protection:Classification, encryption, and exfiltration prevention automation.
- Access Control:Physical and logical perimeter enforcement with behavioral verification.
Surveillance Systems generates the largest revenue pool; Identity Management is expanding fastest on compliance-driven replacement cycles.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import balances in AI security technologies favor the United States and China as net exporters of threat detection platforms, while European markets absorb compliance-heavy biometric surveillance imports. Germany and Japan maintain specialized component trade positions in edge-AI hardware.
United States
Federal cybersecurity spending and SEC disclosure rules drive procurement urgency across civilian and defense agencies. NIST AI Risk Management Framework alignment determines bid eligibility for critical infrastructure contracts. Silicon Valley clusters concentrate autonomous threat detection R&D, while Washington DC metro anchors federal security procurement committees.
China
MIIT algorithmic accountability requirements and dual carbon goals shape domestic deployment patterns for surveillance and industrial control security. National AI development plans prioritize sovereign capability in computer vision and network traffic analysis. Beijing-Tianjin-Hebei corridor hosts concentrated edge-AI hardware manufacturing for physical security applications.
Germany
Industrial control system protection mandates from the country's federal cybersecurity authority accelerate operational technology security adoption. EU AI Act conformity requirements exceed baseline CE marking obligations for biometric identification systems. Bavaria's Munich-Stuttgart corridor concentrates automotive and manufacturing security deployments.
United Kingdom
Financial services regulators mandate real-time fraud detection capabilities across retail banking networks. National Cyber Security Centre guidance hardens procurement standards for AI-driven risk management tools. London's fintech cluster drives steepest adoption curves for transaction monitoring platforms.
Japan
METI industrial security directives prioritize anomaly detection for manufacturing infrastructure protection. JIS standards alignment shapes vendor qualification for critical infrastructure operators. Tokyo-Osaka corridor concentrates financial institution procurement of biometric authentication systems.
AI in Security Market Vendor Landscape
Concentration sits with cloud-native platform providers and endpoint detection specialists that have achieved scale in autonomous threat identification. The vendor landscape organizes around three strategic archetypes: integrated network security platforms, self-learning immune system architectures, and cloud-delivered endpoint protection services. Competitive dynamics intensify through strategic partnerships between hardware manufacturers and inference software vendors, alongside portfolio diversification into adjacent fraud prevention segments.
Within the endpoint detection tier, CrowdStrike and SentinelOne exemplify cloud-native architectures that displace signature-dependent incumbents. Palo Alto Networks anchors the integrated platform archetype spanning network, cloud, and on-premises environments. Darktrace occupies a distinct position in autonomous response systems, representing self-learning detection models that operate without human-tuned rules.
| Leading Market Players |
|---|
| Palo Alto Networks |
| CrowdStrike |
| Microsoft |
| AWS |
| Fortinet |
| Check Point Software Technologies |
| SentinelOne |
| Darktrace |
| Others |
Supply Flow & Price Mechanics
Edge-AI inference chip substitution for cloud-only processing is redrawing supply geography toward Taiwan and South Korea fabrication centers while compressing pricing power for pure-software security vendors unable to capture hardware margin pools.
Pricing Analysis
Industrial OEM buyers anchor three-tier pricing structure across premium, standard, and economy levels in AI security procurement. Premium tiers bundle edge hardware with autonomous response capabilities; standard tiers offer cloud-delivered threat detection; economy tiers provide signature-based monitoring. Price differentiation hinges on NIST framework certification grade and after-sales incident response SLAs. Pricing pressure stems from GPU supply constraints elevating training costs for foundation-model vendors. Mid-market enterprises exhibit highest price sensitivity due to constrained security budgets, while United States federal agencies demonstrate lowest sensitivity given critical infrastructure protection mandates.
Supply Chain Analysis
TSMC advanced node allocation for AI accelerators underwrites competitive positioning across the endpoint security tier. Taiwan and South Korea concentrate semiconductor fabrication for inference chips; China maintains assembly capacity for surveillance hardware. Raw material dependencies span silicon wafers, high-bandwidth memory modules, and rare earth elements for magnetics. Single-source foundry vulnerability exposes vendors to geopolitical disruption. Distribution runs through hyperscaler marketplaces and direct enterprise sales teams with embedded professional services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Open-source foundation models threaten proprietary detection algorithm margins, compelling incumbents to defend through data moat deepening and vertical capability integration.
For Market Incumbents: Secure exclusive threat intelligence data partnerships with financial institutions and government agencies to maintain model accuracy differentiation. Invest in backward integration into edge-AI hardware design to capture margin pools escaping pure-software competitors. The EU AI Act conformity assessment bottleneck favors vendors with pre-positioned documentation capabilities. For New Entrants and Emerging Players: Anchor in operational technology security for manufacturing and energy infrastructure, a segment with minimal incumbent saturation and urgent regulatory pressure from NERC CIP mandates. Target mid-market enterprises seeking NIST framework alignment without enterprise-grade procurement complexity. Lead with federated learning architectures that circumvent data residency constraints blocking incumbent deployments. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors platform consolidators with cross-vertical data network effects. Long-term viability rests on proprietary training data access and continuous learning system architectures. Monitor EU AI Act enforcement intensity as inflection indicator for biometric surveillance vendor restructuring opportunities.| Strategic Initiative | Industry Significance |
|---|---|
| Edge-AI Hardware Co-Design | Captures inference latency advantages for critical infrastructure protection contracts requiring sub-50 millisecond response. |
| Federated Learning Platform Launch | Unlocks financial consortium deployments previously blocked by HIPAA and GDPR data residency constraints. |
| EU AI Act Conformity Pre-Certification | Accelerates European market access as German and French authorities enforce documentation requirements exceeding baseline CE marking. |
| Operational Technology Security Acquisition | Addresses manufacturing and energy infrastructure segments with minimal incumbent saturation and urgent NERC CIP compliance pressure. |
| Strategic Partnership with Hyperscaler | Distributes threat detection models through AWS and Azure marketplaces with embedded professional services attach. |
Methodological Framework
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at financial institutions, federal procurement officers, endpoint security engineering leads, and OT security directors at energy utilities. Secondary validation drew from SEC cybersecurity disclosure filings, NIST framework implementation guidance, EU AI Act conformity assessment documentation, and hyperscaler capex disclosures for AI infrastructure. Bottom-up deployment estimates triangulated against top-down addressable market calculations across technology, application, end-user, and solution dimensions.
Across the analysis window, projections modeled technology adoption curves by deployment latency requirements, regulatory compliance burden by jurisdiction, and vertical penetration rates by incident consequence severity. Segmentation dimensions spanned algorithmic architecture, application urgency, end-user regulatory exposure, and solution hardware-software integration depth. CAGRs derived from S-curve technology diffusion patterns calibrated to historical endpoint security and fraud prevention adoption benchmarks. Forecast inputs incorporated EU AI Act implementation timelines and United States federal cybersecurity spending authorization trajectories.
Decision-makers should treat outputs as directional under sustained GPU supply constraints and stable geopolitical conditions; material deviation in Taiwan semiconductor fabrication capacity would warrant model refresh. Practitioners should keep alternative scenarios live as EU AI Act enforcement intensity and NIST framework revision cycles evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Enterprise Key Management Market
Security Software
Facial Recognition Market
Security Software
Doorbell Camera Market
Security Software
Global Digital Identity Solutions Market
Security Software
Risk-Based Authentication (RBA) Market
Security Software
Global Data Masking Market
Security Software
Global Automatic Number Plate Recognition (ANPR) System Market
Security Software
Information Rights Management Market
Security Software
Global Hardware Security Modules (HSM) Market
Security Software
Global Data Breach Notification Software Market
Security Software
DNS Protection Software Market
Security Software
Global Secure Mobile Communications Software Market
Security Software
Network Security Appliance Market
Security Software
Data Leakage Prevention Product Market
Security Software
Digital Credential Management Software Market
Security Software
Communication Encryption Software Market