
 Network Security Appliance Market | 2026-2036
Network Security Appliance Market Size, Share, and Industry Trends Forecast 2026-2036
Network Security Appliance Market Outlook
Next-generation firewall specifications with deep packet inspection and TLS decryption capabilities is rotating procurement priorities toward hardware that inspects encrypted traffic at line rate. Palo Alto Networks leverages in-house silicon development to sustain throughput advantages in high-density data center deployments. Fortinet anchors mid-market expansion through integrated SD-WAN and security fabric bundles. Check Point Software Technologies differentiates via software-defined perimeter architectures that compete directly with cloud-native alternatives.
A network security appliance is a dedicated hardware or virtualized device engineered to enforce security policies through packet filtering, stateful inspection, and application-layer visibility, typically operating at throughput thresholds from 1 Gbps to 400 Gbps depending on form factor. These systems serve the primary commercial purpose of segmenting trusted from untrusted network zones while logging traffic metadata for forensic analysis. Firewall appliances retain the largest installed base but face margin compression as cloud-based secure access service edge solutions capture remote workforce deployments. Unified Threat Management platforms dominate small enterprise budgets by consolidating multiple security functions at price points below discrete point-product stacks. Machine Learning-enhanced threat detection represents the fastest-expanding technology segment as vendors train models on proprietary telemetry feeds to reduce false-positive rates.
FCC guidelines for communications infrastructure security, NIST Cybersecurity Framework mandates for federal contractors, and SEC disclosure rules for material cybersecurity incidents collectively reshape product roadmaps and certification requirements for domestic vendors. The EU AI Act further constrains automated threat-response systems deployed within European jurisdictions by requiring risk-classification documentation. Stakeholders must evaluate whether appliance-centric architectures or cloud-delivered security service edge platforms better align with evolving procurement standards and cross-border data sovereignty obligations.
Market Dynamics
The migration of enterprise workloads to distributed cloud architectures is fragmenting network perimeters and forcing wholesale replacement of hardware-centric security stacks with hybrid appliance-cloud deployments.
Growth Catalysts
- NIS2 Directive transposition:European critical infrastructure operators face mandatory security audits and must upgrade to intelligent threat-detection platforms, accelerating replacement cycles in Germany, France, and the Netherlands.
- TLS 1.3 encryption proliferation:Over 95% of web traffic now uses encrypted protocols, compelling financial services institutions to procure appliances with line-rate decryption and deep packet inspection capabilities.
- Edge computing densification:Manufacturing and energy sector deployments of operational technology networks at remote sites are driving demand for ruggedized, low-latency security appliances.
Market Restraints
- Semiconductor supply concentration:Custom ASIC and FPGA production for high-throughput appliances depends on Taiwan-based foundry capacity, creating 26-40 week lead times for specialized silicon.
- Cloud-native substitution:Secure access service edge platforms from cloud providers are capturing remote workforce and branch office deployments, compressing addressable market for physical appliances in sub-10 Gbps throughput tiers.
- EU AI Act compliance friction:Automated threat-response systems deployed in European jurisdictions require risk-classification documentation and human oversight protocols, extending sales cycles by 4-6 months.
Strategic Opportunities
- India digital infrastructure expansion:Data localization mandates under the Digital Personal Data Protection Act and PLI scheme incentives for electronics manufacturing are creating localized production and procurement pathways for security appliance vendors.
- Operational technology convergence:IT-OT network integration in utilities and transportation creates demand for appliances with IEC 62443 certification and protocol-aware inspection for Modbus and DNP3 traffic.
- Subscription-based hardware refresh:Appliance-as-a-service models with embedded threat intelligence subscriptions are penetrating mid-market enterprises previously priced out of enterprise-grade security stacks.
Industry Challenges
- Embedded systems security expertise scarcity:Vendors struggle to hire firmware engineers capable of hardening appliance operating systems against supply chain attacks and side-channel exploits.
- Cross-certification timeline compression:Federal contractors must simultaneously achieve FIPS 140-3, Common Criteria, and FedRAMP authorization, requiring 18-24 month investment before market access.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Network Security Appliance Market |
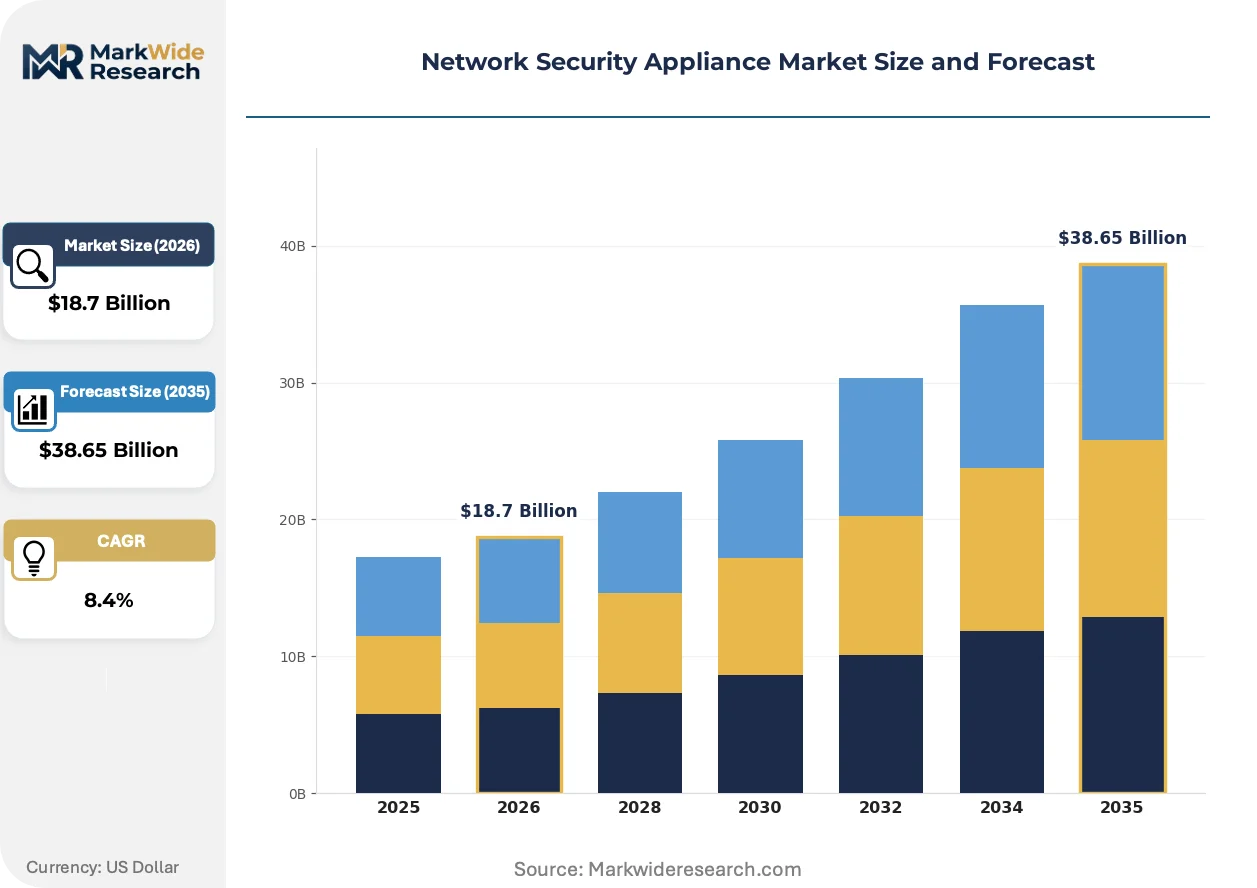
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $38.65 Billion |
| CAGR (2026 – 2036) | 8.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Intrusion Detection System, Unified Threat Management, Secure Web Gateway Deployment Model: On-premises, Cloud-based, Hybrid, Managed Services End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Technology: Machine Learning, Artificial Intelligence, Virtualization, Encryption |
| Companies Covered | Check Point Software Technologies, Sophos, Palo Alto Networks, WatchGuard, Hewlett Packard Enterprise Company, Fortinet, Juniper Networks, SonicWall, Cisco Systems, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Network Security Appliance Market Strategic Shifts
Hardware security architectures are converging with cloud-native management planes, enabling unified policy orchestration across physically distributed appliances while preserving local enforcement latency.
Inline machine learning inference engines embedded in network processors are displacing signature-based detection for zero-day exploit identification. Large financial institutions in Singapore and Switzerland are deploying these appliances at 100 Gbps core network junctions. The shift is compressing margins for vendors lacking proprietary silicon or trained model telemetry.
The EU AI Act's risk-based classification system for automated decision-making is forcing appliance vendors to document algorithmic transparency in threat-response modules. German critical infrastructure operators now require algorithmic impact assessments before procurement authorization. This regulatory layer is favoring European vendors with established compliance documentation over faster-moving competitors.
Enterprise buyers are consolidating vendor relationships and demanding security fabric architectures that unify firewall, SD-WAN, and zero-trust network access under single management consoles. Mid-market enterprises in Australia and Canada are abandoning best-of-breed point products for integrated bundles. This concentration is elevating procurement importance of professional services and post-deployment support quality.
Network Security Appliance Market Segmentation
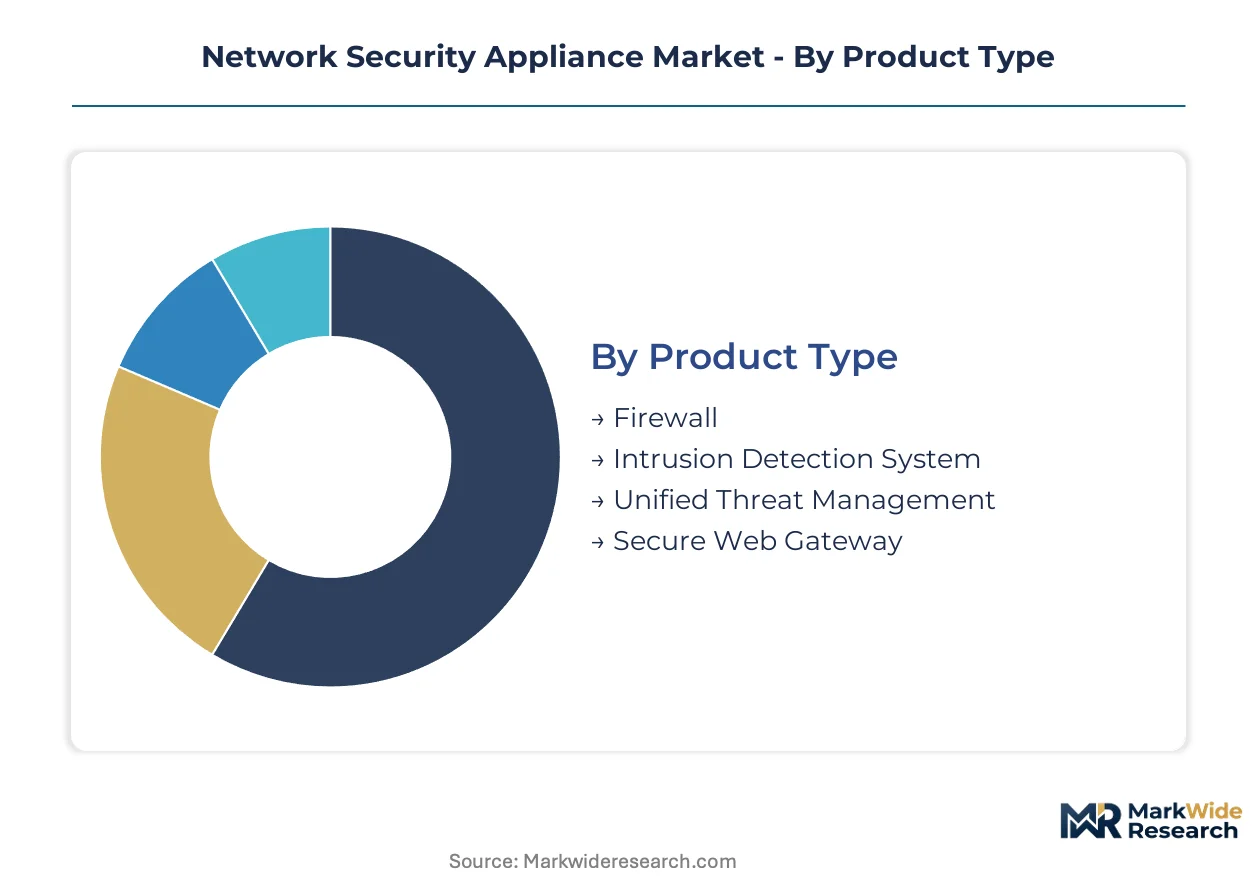
Network security appliance procurement patterns diverge sharply across product architectures and operational contexts. Segmentation reveals where cloud-native substitution pressures physical hardware most intensely and which deployment models retain durable insulation from displacement.
Product Type:
Firewall appliances face the most acute substitution threat as secure access service edge platforms capture remote workforce deployments, while specialized inspection hardware maintains defensibility in high-throughput data center environments.
- Firewall:Stateful inspection and application-layer visibility appliances process traffic at 1 Gbps to 400 Gbps thresholds depending on form factor. Financial services institutions in Germany and Singapore are expanding procurement of next-generation specifications with TLS decryption capabilities to protect distributed transaction infrastructure against encrypted threat vectors.
- Unified Threat Management:Consolidated platforms integrate firewall, intrusion prevention, antivirus, and content filtering at price points below discrete point-product stacks. Small and medium enterprises in Australia and Canada are abandoning best-of-breed configurations for these bundles, elevating procurement importance of embedded threat intelligence subscription quality.
- Intrusion Detection System:Signature and anomaly-based monitoring appliances feed telemetry to security operations centers for forensic correlation.
- Secure Web Gateway:Cloud-delivered alternatives dominate this category, compressing hardware addressable market to regulated industries with data sovereignty constraints.
Firewall anchors the volume base while Unified Threat Management gains share at the steepest rate among hardware-centric categories.
Deployment Model:
Cost tier stratification determines competitive dynamics, with capital-intensive on-premises deployments ceding ground to operational expenditure models that reduce upfront procurement barriers for mid-market buyers.
- On-premises:Dedicated hardware appliances enforce policies with sub-millisecond latency at network boundaries. Critical infrastructure operators in Germany face mandatory security audits under NIS2 Directive transpositions, preserving demand for locally deployed inspection platforms that satisfy data residency requirements.
- Cloud-based:Virtualized appliance instances scale throughput elastically without hardware refresh cycles. Large enterprises with distributed cloud architectures are fragmenting network perimeters and adopting these deployments for branch office substitution.
- Hybrid:Policy orchestration unifies physical and virtual enforcement points under single management consoles.
- Managed Services:Appliance-as-a-service models embed threat intelligence subscriptions and professional support, penetrating enterprises previously priced out of enterprise-grade security stacks.
On-premises retains the largest installed base though Cloud-based deployments are expanding most quickly among net-new procurement decisions.
End User:
Customer type segmentation tracks organizational scale and procurement sophistication, with government and large enterprise segments driving certification requirements that smaller buyers cannot satisfy.
- Large Enterprises:Multi-site organizations demand security fabric architectures unifying firewall, SD-WAN, and zero-trust network access under single consoles. Federal contractors in the United States must simultaneously achieve FIPS 140-3, Common Criteria, and FedRAMP authorization, requiring 18-24 month investment before market access.
- Government:National security and civilian agencies impose the most stringent supply chain verification and algorithmic transparency mandates. The EU AI Act constrains automated threat-response systems deployed within European jurisdictions by requiring risk-classification documentation and human oversight protocols.
- Medium Enterprises:Consolidated vendor relationships favor integrated bundles over point-product complexity.
- Small Enterprises:Budget constraints concentrate demand in Unified Threat Management platforms with simplified deployment.
Large Enterprises anchor the volume base while Government procurement climbs the fastest amid regulatory mandate acceleration.
Technology:
Maturity differentiation separates proven virtualization and encryption foundations from emerging inference capabilities that vendors are racing to productize.
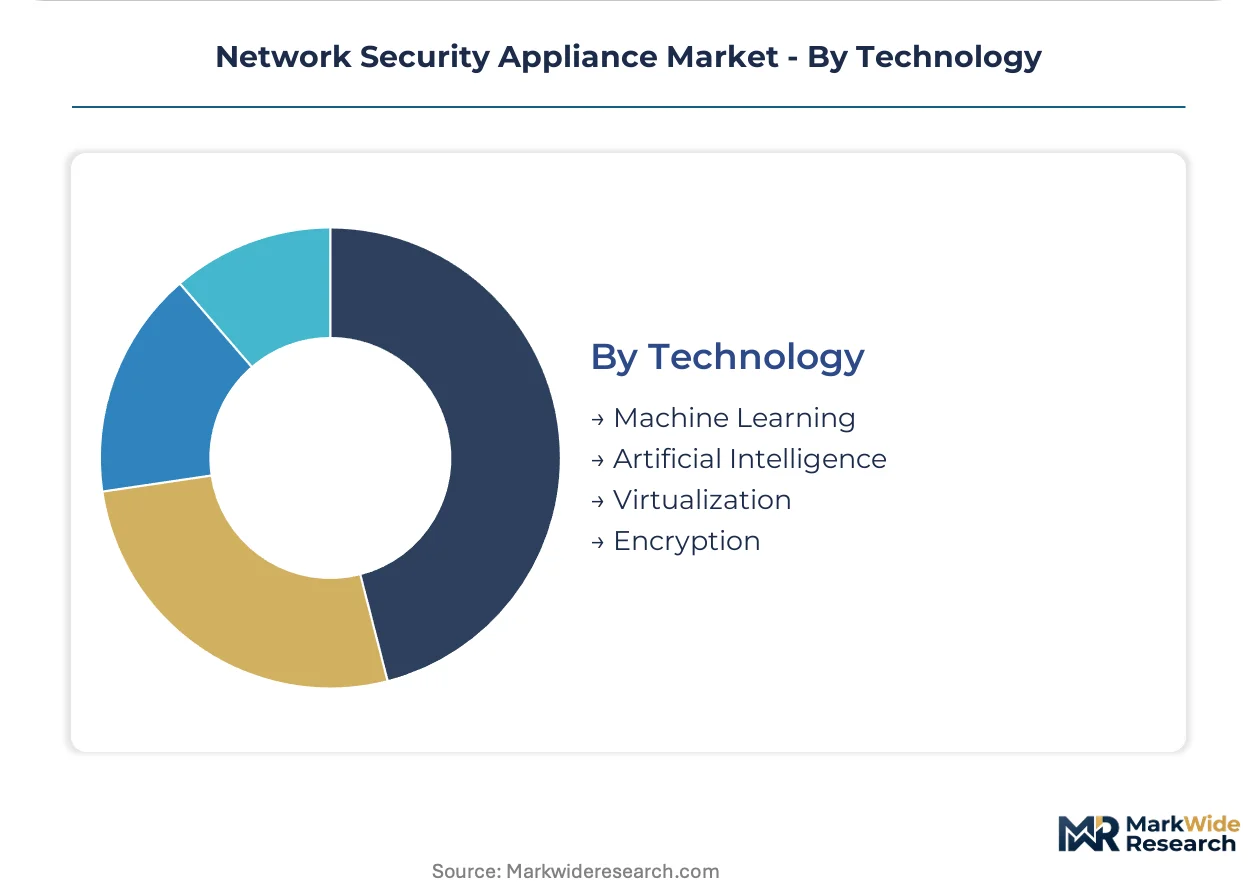
- Machine Learning:Inline inference engines embedded in network processors identify zero-day exploits without signature dependency. Large financial institutions in Singapore and Switzerland are deploying these appliances at 100 Gbps core network junctions, compressing margins for vendors lacking proprietary silicon or trained model telemetry.
- Artificial Intelligence:Automated threat-response modules require algorithmic impact assessments under German critical infrastructure procurement rules, extending sales cycles by 4-6 months but favoring vendors with established compliance documentation.
- Virtualization:Software-defined appliance instances abstract enforcement from physical hardware constraints.
- Encryption:Line-rate TLS 1.3 decryption capabilities are rotating procurement priorities toward hardware that inspects encrypted traffic without throughput degradation.
Encryption underpins universal deployment requirements while Machine Learning shows the steepest expansion trajectory as vendors differentiate on false-positive reduction.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli security appliance vendors export specialized threat-detection hardware to financial institutions across Western Europe and North America. This trade corridor channels innovation from Tel Aviv's cybersecurity cluster into Frankfurt and London banking infrastructure.
United States
Federal contractors drive demand for FIPS 140-3 certified appliances under NIST Cybersecurity Framework mandates. The SEC requires disclosure of material cybersecurity incidents, accelerating procurement cycles for next-generation firewalls. Silicon Valley data center operators deploy 400 Gbps inspection hardware at core network junctions.
Germany
Critical infrastructure operators face mandatory security audits under national transpositions of the EU NIS2 Directive. The EU AI Act constrains automated threat-response systems by requiring algorithmic impact assessments. Munich and Frankfurt banking clusters procure TLS decryption appliances for encrypted transaction inspection.
Singapore
Monetary Authority of Singapore guidelines compel financial institutions to deploy inline machine learning inference engines at 100 Gbps throughput thresholds. The city-state's data sovereignty requirements preserve demand for locally deployed hardware over cloud alternatives. Marina Bay financial district anchors regional procurement volume.
India
Data localization mandates under the Digital Personal Data Protection Act create localized production pathways. PLI scheme incentives for electronics manufacturing attract assembly investment from multinational vendors. Bengaluru and Hyderabad technology corridors drive mid-market enterprise adoption of unified threat management platforms.
Switzerland
FINMA operational resilience requirements mandate encrypted traffic inspection for private banking infrastructure. Swissmedic and federal data protection authorities enforce strict data residency rules favoring on-premises appliance deployment. Zurich's financial district concentrates demand for high-throughput inspection hardware with algorithmic transparency documentation.
Network Security Appliance Market Competitive Environment
Listed leaders compete with private specialists across certification depth and silicon architecture. The vendor base stratifies into three tiers: multinational platform providers with proprietary ASIC development, mid-market integrated security fabric vendors, and specialized threat-intelligence boutiques. Consolidation pressures favor vendors with FedRAMP and Common Criteria pre-authorization. Dominant competitive moves include strategic partnerships with hyperscale cloud providers and backward integration into custom network processor design.
Within the platform-provider tier, Palo Alto Networks and Fortinet exemplify scale-driven architectural approaches. Check Point Software Technologies occupies a position emphasizing software-defined perimeter differentiation. These three vendors anchor the competitive set referenced in procurement evaluations across German critical infrastructure and U.S. federal contracting channels.
| Leading Market Players |
|---|
| Check Point Software Technologies |
| Sophos |
| Palo Alto Networks |
| WatchGuard |
| Hewlett Packard Enterprise Company |
| Fortinet |
| Juniper Networks |
| SonicWall |
| Cisco Systems |
| Others |
Value Chain & Pricing Dynamics
Twenty-six to forty week lead times for specialized ASIC and FPGA silicon concentrate pricing power with Taiwan-based foundry operators and compress margin flexibility for appliance vendors serving European critical infrastructure procurement channels.
Pricing Analysis
Industrial OEM buyers anchor a three-tier pricing structure across premium, standard, and economy levels in the network security appliance market. Premium tiers command substantial markups based on FIPS 140-3 and Common Criteria certification depth alongside proprietary silicon architectures, while mid-market bundles face cost compression from cloud-native SASE substitution. Price erosion runs through sub-10 Gbps throughput tiers as hyperscaler platforms capture remote workforce deployments. Small enterprises exhibit highest price sensitivity and concentrate procurement in Unified Threat Management bundles with embedded subscription models.
Supply Chain Analysis
Taiwan and South Korea anchor wafer fabrication for custom network processors that enable line-rate TLS decryption at 100 Gbps throughput thresholds. High-performance appliances draw from concentrated foundry capacity for ASIC development, FPGA programming, and specialized network interface controllers. Single-source vulnerability in Taiwan-based semiconductor manufacturing exposes vendors to geopolitical disruption and extended procurement cycles. Distribution runs through direct enterprise sales teams for large contracts and authorized channel partners serving mid-market buyers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Firmware engineering expertise for embedded systems hardening has become the constraining asset in network security appliance development, with vendors competing for scarce talent capable of securing appliance operating systems against supply chain attacks.
For Market Incumbents: Consolidate certification pre-authorization advantages by accelerating FIPS 140-3 and FedRAMP investments before federal contracting windows tighten. Deepen backward integration into custom network processor design to sustain throughput differentiation against cloud-native SASE platforms that threaten hardware margins in branch office segments. For New Entrants and Emerging Players: FedRAMP authorization fast-tracks offer the most penetrable pathway into U.S. federal contracting channels where incumbent pre-certification creates artificial scarcity. Target operational technology convergence opportunities in utilities and transportation requiring IEC 62443 certification and protocol-aware inspection for Modbus and DNP3 traffic. Pursue appliance-as-a-service subscription models to bypass capital expenditure barriers in mid-market enterprises. For Investors and Strategic Acquirers: Long-term, this sits as a consolidation play because certification depth and silicon architecture differentiation favor scale economics over fragmentation. Acquisition targets should demonstrate pre-existing Common Criteria or FedRAMP authorization to compress 18-24 month market access timelines. Watch for inflection when EU AI Act compliance documentation becomes a procurement gate for automated threat-response systems in German critical infrastructure.| Strategic Initiative | Industry Significance |
|---|---|
| Proprietary Silicon Development | In-house ASIC design sustains throughput advantages against merchant silicon competitors at 400 Gbps data center junctions. |
| Certification Pre-Authorization | Early FIPS 140-3 and FedRAMP investment secures federal contracting access before compliance timelines extend further. |
| Appliance-as-a-Service Launch | Subscription embedding threat intelligence penetrates mid-market buyers previously priced out of enterprise security stacks. |
| Operational Technology Certification | IEC 62443 compliance opens utilities and transportation sectors where IT-OT convergence creates specialized demand. |
| Hyperscaler Partnership | Strategic alignment with cloud providers bridges hybrid appliance-cloud deployments for distributed enterprise architectures. |
Study Parameters
Two parallel data streams informed the analysis: structured conversations with CISOs, federal procurement officers, critical infrastructure security directors, and channel distribution partners; and secondary validation through SEC 10-K filings, NIST certification databases, EU regulatory transposition documents, and hyperscaler capex disclosures. Bottom-up appliance shipment estimates triangulated against top-down enterprise IT security spending allocations.
Across the analysis window, forecasts modeled segmentation by product architecture, deployment model, end-user scale, and technology maturity tier. CAGRs derived from installation base erosion rates for legacy perimeter hardware and net-new procurement for machine learning-enhanced platforms. Industry-specific inputs included NIS2 Directive transposition timelines, TLS 1.3 adoption curves, and semiconductor foundry capacity utilization.
Decision-makers should treat outputs as directional under assumptions of sustained regulatory mandate acceleration and stable Taiwan-based foundry capacity; material deviation in either would warrant model refresh. Recalibration cycles align with material shifts in EU cybersecurity directive enforcement and federal contracting authorization standards.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Consumer IAM Market
Security Software
Communication Encryption Software Market
Security Software
DNS Protection Software Market
Security Software
Mobile Threat Management Security Software Market
Security Software
Privileged Identity Management Market
Security Software
Global Reputation Protection Software Market
Security Software
Device Vulnerability Management Market
Security Software
Confidential Computing Market
Security Software
Endpoint Security Solutions Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Secaas Market
Security Software
Device-Embedded Biometric Authentication Market
Security Software
Data Loss Prevention Market
Security Software
North America Video Management System Market
Security Software
Global Data Classification Market
Security Software
Next-Generation Intrusion Prevention System (NGIPS) Market