
 Extended Detection and Response Market | 2026-2036
Extended Detection and Response Market Size, Share, and Industry Trends Forecast 2026-2036
Extended Detection and Response Market Analysis
The EU Cyber Resilience Act is realigning vendor roadmaps toward continuous monitoring and automated response capabilities. Microsoft leverages its cloud-native architecture to anchor enterprise deployments across hybrid environments. CrowdStrike competes through AI-native endpoint detection that extends into identity and cloud workloads. Palo Alto Networks differentiates via platform consolidation, integrating XDR with its broader security service edge portfolio.
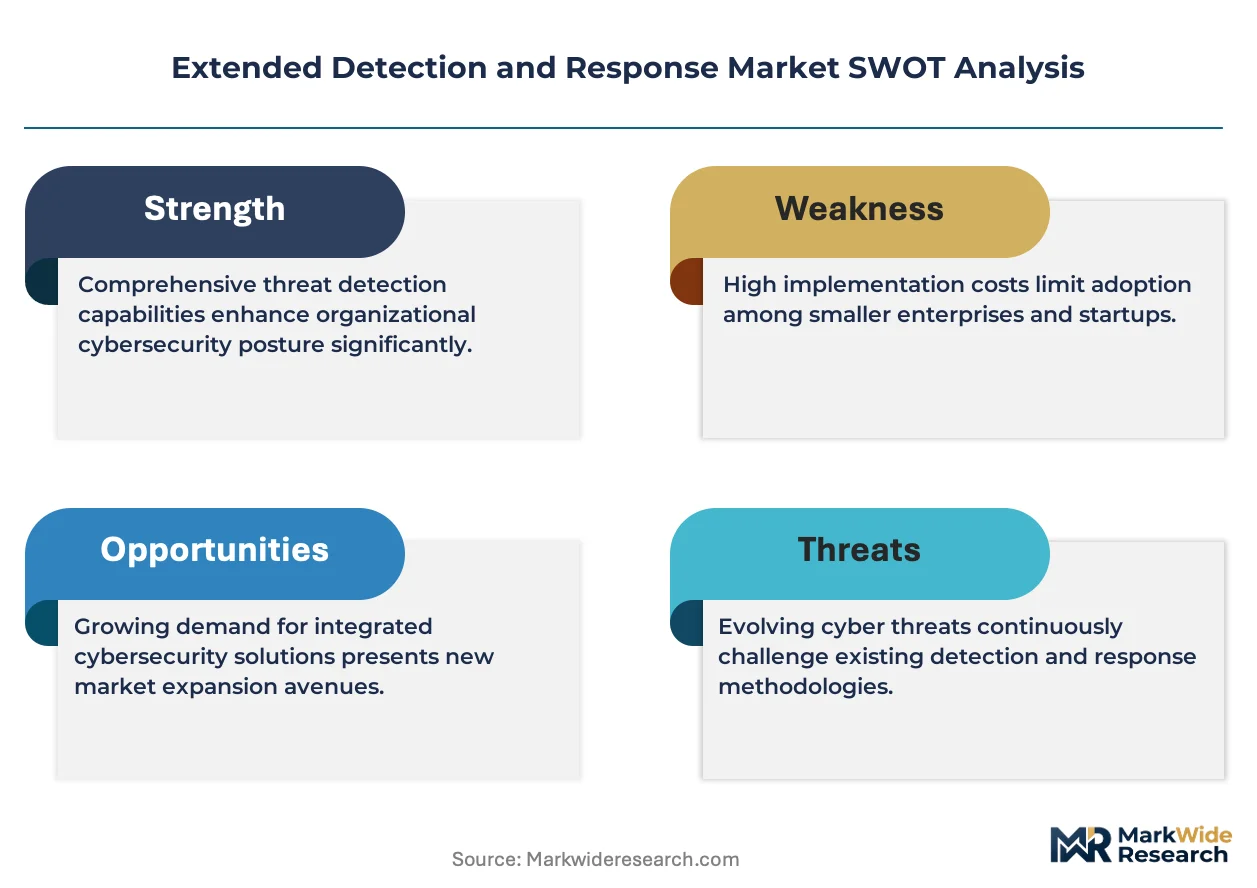
Extended Detection and Response (XDR) denotes a unified security platform that correlates telemetry across endpoints, networks, cloud workloads, and email systems through normalized data schemas and automated threat analytics. Its primary purpose is collapsing siloed security operations into coherent incident narratives that accelerate mean-time-to-response. Cloud Security deployments within the Product Type dimension are capturing disproportionate investment as organizations migrate detection logic to elastic infrastructure. The Managed Service deployment model is expanding fastest among mid-market buyers lacking dedicated security operations centers. Healthcare Providers under the End User segment face acute compliance pressure, driving demand for XDR platforms with built-in audit trails and patient data access monitoring.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) mandates federal agencies adopt zero-trust architectures that privilege integrated detection platforms over point solutions. The EU NIS2 Directive compels critical infrastructure operators across member states to implement coordinated threat detection with cross-border reporting protocols. Japan's METI has issued operational technology security guidelines that explicitly reference consolidated detection and response frameworks for industrial control systems. Stakeholders must evaluate whether their current tooling satisfies emerging cross-sector certification requirements before procurement windows narrow.
Market Dynamics
Zero-trust architecture mandates from CISA are collapsing fragmented security toolchains into unified detection platforms, forcing enterprises to retire point solutions in favor of correlated telemetry systems that span endpoints, cloud workloads, and identity infrastructure.
Growth Catalysts
- CISA Zero-Trust Mandates:Federal agencies must consolidate detection tools under unified platforms by fiscal deadlines, accelerating procurement cycles for integrated XDR systems.
- Healthcare Compliance Pressure:HIPAA audit requirements and patient data access monitoring needs drive hospital systems toward platforms with built-in forensic trails.
- AI-Native Detection Engines:Machine learning correlation across normalized data schemas compresses mean-time-to-response from hours to minutes.
Market Restraints
- Legacy SIEM Sunk Costs:Enterprises with multi-year Splunk or IBM QRadar contracts face contractual friction and data migration complexity when transitioning to XDR architectures.
- Skills Concentration:Security operations centers with SOAR playbook expertise cluster in metropolitan technology corridors, leaving mid-market buyers dependent on managed service overlays.
- Data Residency Requirements:EU GDPR and national sovereignty rules fragment cloud-hosted detection logic, complicating cross-border telemetry correlation for multinational deployments.
Strategic Opportunities
- Operational Technology Convergence:XDR platforms that ingest industrial control system telemetry from manufacturing and energy infrastructure address a protection gap left by IT-centric vendors.
- Japan METI Guidelines:Explicit references to consolidated detection frameworks for critical infrastructure create procurement tailwinds for vendors with OT-native sensor integration.
- Managed Service Channel:Mid-market buyers without dedicated SOCs represent an underserved segment where monthly subscription models displace capital-intensive appliance purchases.
Industry Challenges
- Multi-Cloud Telemetry Normalization:AWS, Azure, and GCP each emit distinct log formats, forcing vendors to maintain expensive parsing pipelines that delay threat correlation.
- Threat Intelligence Integration:Feeds from CISA, commercial providers, and industry ISACs require continuous tuning to reduce false-positive rates without missing novel attack patterns.
- API Rate Limiting:Cloud service providers throttle data extraction volumes, creating ingestion bottlenecks during high-velocity incidents.
Report Scope
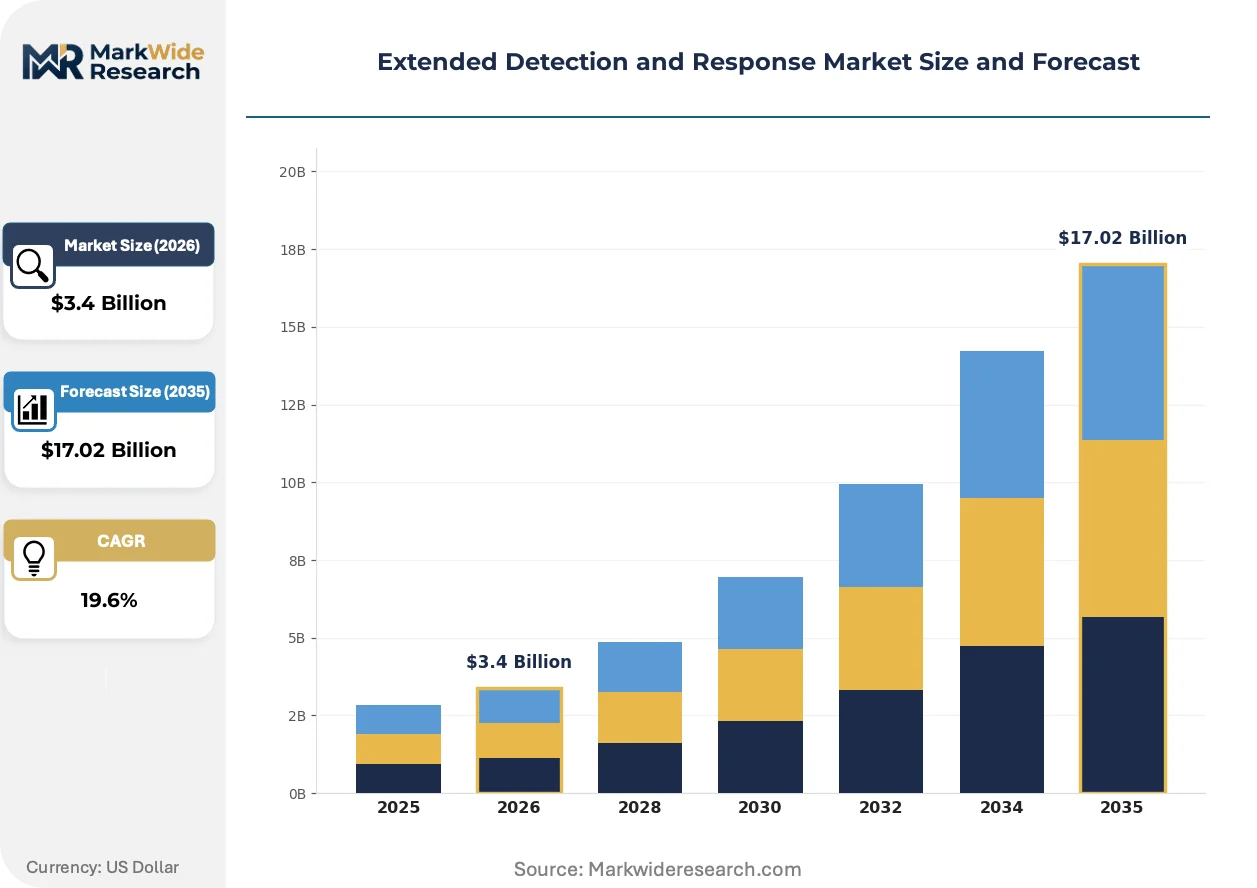
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Extended Detection and Response Market |
| Market Size in 2026 | $3.4 Billion |
| Market Size in 2035 | $17.02 Billion |
| CAGR (2026 – 2036) | 19.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Security, Network Security, Email Security, Cloud Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Healthcare Providers, Financial Institutions, Retail Chains, Government Agencies Integration Level: APIs, SIEM Tools, Incident Response Platforms, Threat Intelligence |
| Companies Covered | Microsoft, Trend Micro, CrowdStrike, Broadcom, Cisco Systems, Palo Alto Networks, Sophos, Trellix, SentinelOne, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Extended Detection and Response Market Emerging Trajectories
Detection logic is migrating from on-premises appliances to elastic cloud infrastructure, enabling correlation across geographically dispersed assets while reducing hardware refresh cycles.
Extended detection platforms are converging with identity threat detection and response (ITDR) capabilities, embedding user behavior analytics directly into incident narratives. Financial institutions with hybrid workforce models deploy these converged stacks fastest, compressing the vendor selection cycle from eighteen months to under six. Security teams now demand single-pane visibility where compromised credentials trigger automated endpoint isolation without human intervention.
The EU NIS2 Directive compels critical infrastructure operators to implement coordinated threat detection with mandatory cross-border reporting protocols. Energy and transport sector procurement specifications now require evidence of automated incident handoff to national computer security incident response teams. German and French operators face the tightest compliance deadlines, driving preference for vendors with pre-certified EU data residency architectures.
Security procurement committees now weight total cost of ownership over initial license fees, unbundling implementation services from perpetual software contracts. Large enterprises negotiate outcome-based arrangements where vendor fees scale with measured mean-time-to-containment improvements. This preference shift is most pronounced among US healthcare systems operating under constrained capital budgets and accelerated HIPAA audit schedules.
Extended Detection and Response Market Segmentation
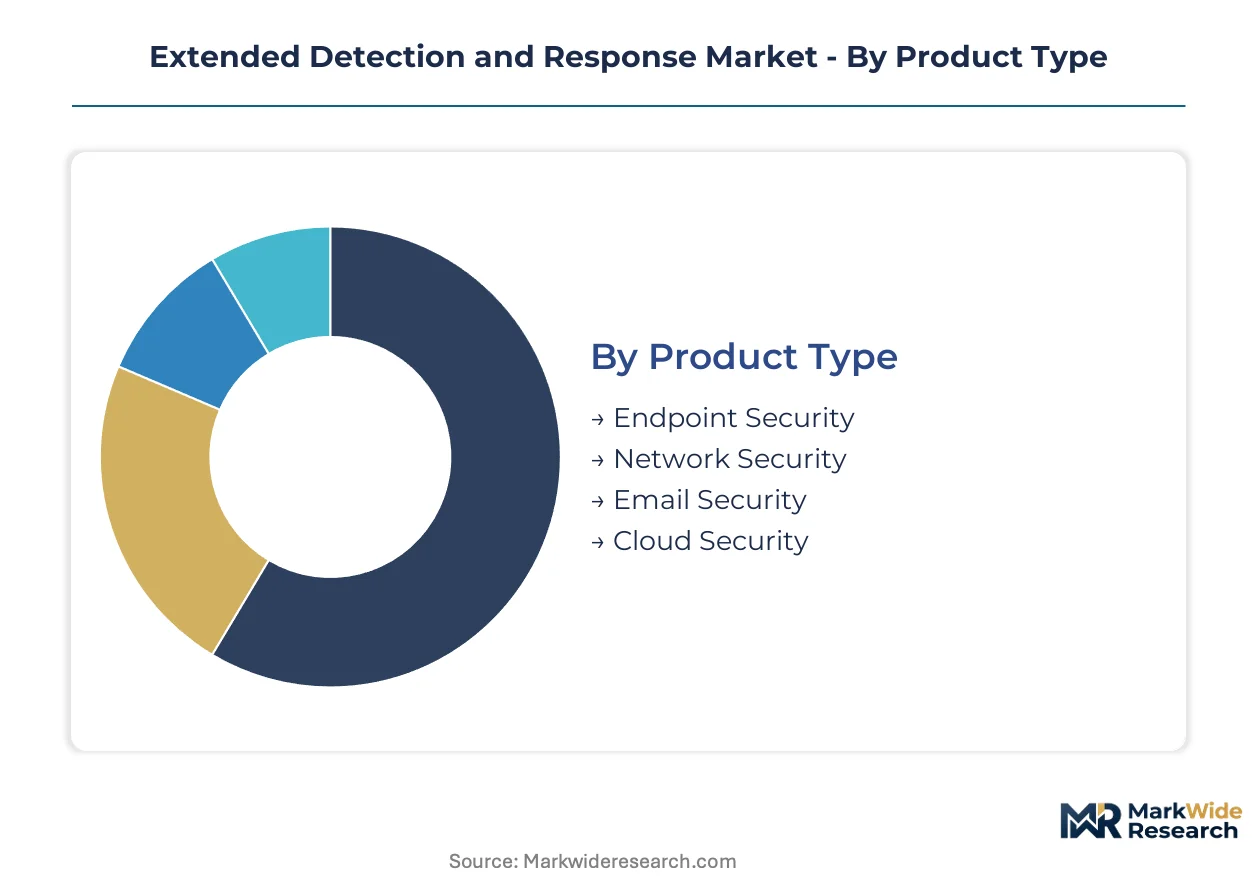
XDR procurement patterns diverge sharply across deployment architectures and integration requirements, with upgrade cycles from legacy SIEM systems driving category prioritization. Organizations map segmentation choices against existing security infrastructure debt and compliance deadlines rather than greenfield preferences.
Product Type:
Replacement cycles from standalone point solutions to unified platforms concentrate investment in telemetry-rich categories that collapse visibility gaps.
- Endpoint Security:Agent-based telemetry collection from laptops, servers, and mobile devices forms the foundational data layer for correlation engines. Financial institutions in the United States prioritize this segment for ransomware containment and insider threat detection.
- Cloud Security:Native integration with AWS, Azure, and GCP control planes enables detection logic to follow workload migration. Healthcare providers expanding telehealth infrastructure drive disproportionate procurement volume for container and serverless monitoring.
- Network Security:Flow analysis and deep packet inspection feed east-west traffic visibility into XDR correlation pipelines.
- Email Security:Phishing detection and business email compromise prevention supply initial compromise indicators to broader incident narratives.
Endpoint Security sits at the top of the volume ranking, with Cloud Security climbing the fastest.
Deployment Model:
Operational maturity and capital availability stratify buyer preferences across ownership structures and operational responsibility models.
- Managed Service:Outsourced security operations centers deliver 24/7 monitoring through subscription economics that displace capital-intensive appliance procurement. Mid-market retail chains without dedicated security staff represent the most concentrated demand pool for this model.
- Cloud-Based:Elastic infrastructure eliminates hardware refresh cycles while enabling correlation across geographically dispersed assets. German and French critical infrastructure operators facing NIS2 deadlines favor this architecture for automated cross-border reporting.
- Hybrid:Split deployments retain sensitive data processing on-premises while leveraging cloud analytics for capacity bursts.
- On-Premises:Air-gapped environments in classified government facilities and regulated healthcare settings sustain residual demand despite cloud migration trends.
Managed Service claims the steepest expansion trajectory among deployment options, while Cloud-Based deployments hold the largest installed base.
End User:
Regulatory enforcement intensity and breach notification requirements create divergent procurement urgency across sectoral risk profiles.
- Financial Institutions:Real-time transaction monitoring and SWIFT network protection mandate sub-minute detection latencies. CISA zero-trust mandates accelerate federal credit union modernization timelines.
- Government Agencies:Classified network segmentation and supply chain security requirements drive preference for vendors with FedRAMP authorization.
- Healthcare Providers:HIPAA audit trails and patient data access monitoring impose forensic logging requirements that XDR platforms consolidate.
- Retail Chains:Payment card industry compliance and point-of-sale protection shape detection priorities without the same regulatory enforcement velocity.
Financial Institutions command the largest addressable spend, with Government Agencies gaining share fastest under federal modernization mandates.
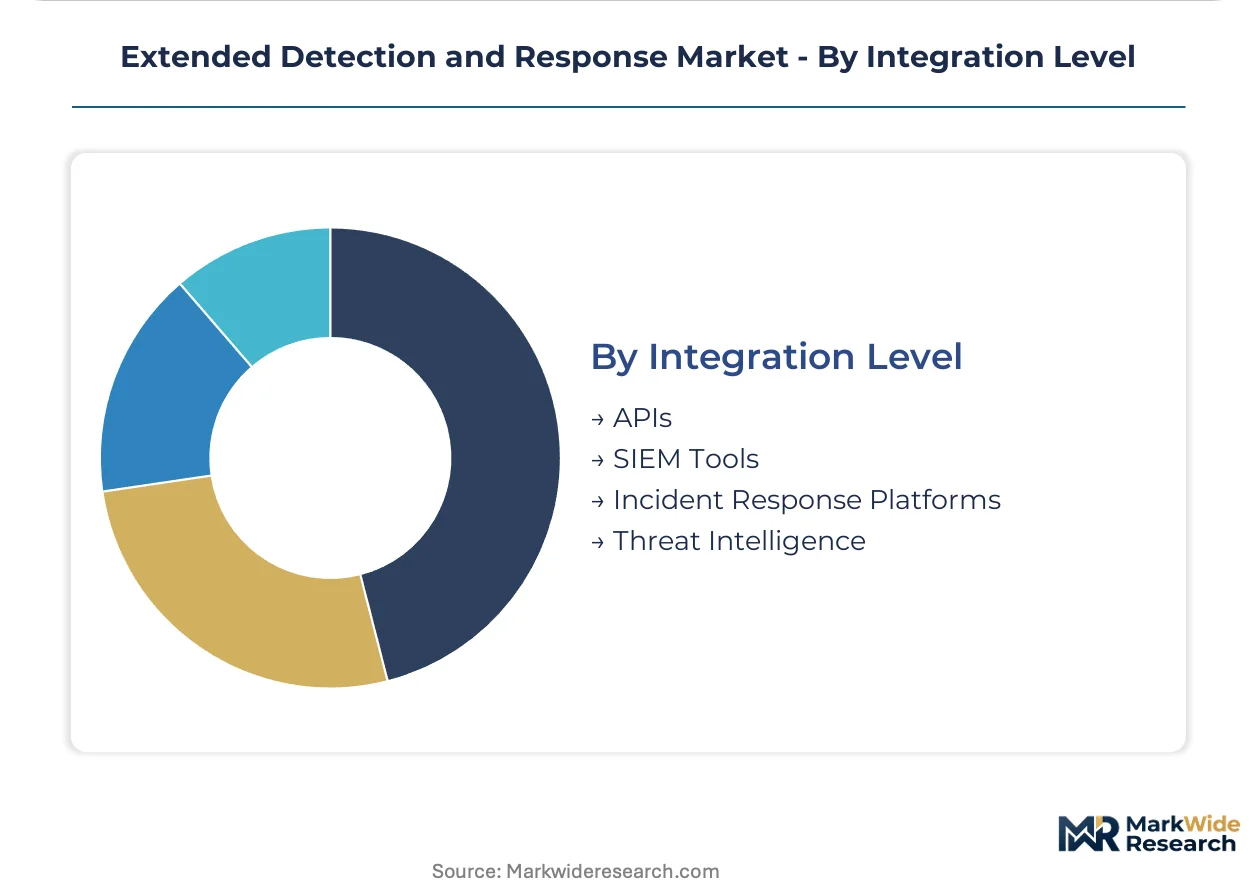
Integration Level:
Technical debt from existing security investments forces buyers to prioritize interoperability pathways that preserve sunk costs while enabling correlation.
- SIEM Tools:Bi-directional data flow with Splunk, IBM QRadar, and Microsoft Sentinel allows phased migration rather than rip-and-replace. Healthcare systems with multi-year SIEM contracts leverage this pathway most heavily.
- Threat Intelligence:Structured feeds from CISA, commercial providers, and industry ISACs enrich detection rules with adversary infrastructure indicators.
- Incident Response Platforms:Automated ticket creation and playbook triggering compress handoff delays between detection and containment teams.
- APIs:Custom webhook and REST integrations enable bespoke connections to proprietary security tools and business systems.
SIEM Tools integration attracts the highest implementation priority, with Threat Intelligence gaining momentum as feed standardization matures.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Extended Detection and Response industry originated within United States cybersecurity R&D corridors, where early threat correlation engines emerged from defense contractor spin-offs and Silicon Valley endpoint protection vendors during the 2010s.
United States
Federal zero-trust procurement mandates and critical infrastructure protection rules drive concentrated XDR deployment across civilian agencies and defense contractors. CISA's binding operational directives compel unified detection platforms by fiscal deadlines, accelerating replacement of fragmented point solutions. The Washington DC-Baltimore corridor hosts the densest concentration of FedRAMP-authorized vendors serving government buyers.
Germany
Industrial manufacturing conglomerates and automotive OEMs demand OT-native XDR platforms for converged IT-ICS environments. The EU NIS2 Directive imposes cross-border reporting obligations on critical infrastructure operators, favoring vendors with automated CSIRT handoff capabilities. The Rhine-Ruhr industrial belt generates disproportionate procurement volume for managed detection services serving mid-market Mittelstand firms.
Japan
Operational technology security guidelines from METI explicitly reference consolidated detection frameworks for industrial control systems in energy and manufacturing sectors. Domestic semiconductor and automotive supply chains prioritize XDR platforms with on-premises data residency options. The Chubu region around Nagoya anchors deployment activity among precision machinery and automotive component manufacturers.
United Kingdom
Financial services regulators in London mandate sub-minute threat detection latencies for real-time payment systems and SWIFT network protection. The National Cyber Security Centre's guidance on security architecture consolidation pressures banks and insurers toward correlated telemetry platforms. The Square Mile and Canary Wharf clusters represent Europe's densest concentration of financial institution XDR procurement committees.
India
IT services exporters and domestic fintech platforms drive cloud-native XDR adoption as remote workforce models persist across Bangalore and Hyderabad technology corridors. RBI cybersecurity guidelines for scheduled commercial banks emphasize integrated threat detection with audit trail capabilities. The Mumbai-Pune industrial belt generates expanding demand among manufacturing enterprises modernizing legacy security operations centers.
Extended Detection and Response Market Vendor Landscape
Capital-heavy platform vendors compete with asset-light specialists across the Extended Detection and Response landscape, creating a bifurcated structure where cloud-native architectures challenge incumbent appliance-based portfolios. The vendor base organizes into three strategic archetypes: hyperscale cloud platforms with native security stacks, endpoint-native vendors extending into identity and cloud workloads, and network-security incumbents consolidating via platform integration. Dominant competitive moves include strategic acquisitions to fill telemetry gaps and API ecosystem expansion to embed third-party detection logic.
Among cloud-native platform providers, Microsoft and CrowdStrike occupy positions exemplifying divergent architectural philosophies—one leveraging infrastructure dominance for integrated deployment, the other representing AI-native endpoint specialization. Palo Alto Networks anchors the network-security-incumbent archetype pursuing platform consolidation. These three entities collectively illustrate the competitive tension between born-in-cloud agility and established enterprise relationships.
| Leading Market Players |
|---|
| Microsoft |
| Trend Micro |
| CrowdStrike |
| Broadcom |
| Cisco Systems |
| Palo Alto Networks |
| Sophos |
| Trellix |
| SentinelOne |
| Others |
Supply Flow & Price Mechanics
Private-equity-rolled-up managed detection specialists anchor supply concentration among mid-market buyers, translating fragmented vendor consolidation into subscription pricing discipline that resists commoditization pressure.
Pricing Analysis
Outcome-based subscription contracts with measured mean-time-to-containment guarantees dominate enterprise procurement, displacing perpetual licensing. Price differentiation rests on FedRAMP authorization tier and managed SOC coverage hours. Cost compression in mid-market tiers intensifies because CrowdStrike and Microsoft anchor competitive benchmarks. Healthcare systems with constrained capital budgets exhibit highest price sensitivity, while defense contractors with classified mandates show lowest.
Supply Chain Analysis
Direct-to-enterprise channels handle hyperscale federal and financial buyer demand, while managed service providers aggregate mid-market volume. Telemetry ingestion infrastructure concentrates in the United States, Ireland, and Singapore to satisfy data residency rules. Cloud compute and threat intelligence feeds constitute primary input dependencies. Single-source vulnerability in AI-native detection engines from NVIDIA GPU clusters creates supply risk. Distribution runs through VARs and systems integrators for complex hybrid deployments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion in XDR platforms derives from cloud-native architecture eliminating hardware refresh cycles and shifting buyer preference toward premium-tier managed services with guaranteed response SLAs.
For Market Incumbents: Extend platform consolidation into operational technology sensor networks before industrial vendors lock out IT-centric competitors. Acquire OT-native telemetry providers to fill manufacturing and energy protection gaps. Prioritize FedRAMP High authorization investment to defend federal procurement position against cloud-native challengers.
For New Entrants and Emerging Players: The pricing gap between premium AI-native platforms and economy-tier legacy SIEM bundles creates white-space opportunity in mid-market healthcare and retail chains. Target German Mittelstand manufacturers under NIS2 compliance deadlines with managed detection services priced below CrowdStrike Enterprise. Lead with API-first architecture enabling rapid SIEM co-existence rather than rip-and-replace positioning.
For Investors and Strategic Acquirers: Hyperscale cloud platforms are the most active acquirer in this space, seeking telemetry breadth to anchor security service edge portfolios. Long-term viability favors vendors with native identity threat detection and cross-cloud normalization engines. Watch CISA binding operational directive expansion beyond federal agencies into critical infrastructure as inflection indicator for procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, cloud, and identity telemetry into single correlation engine for financial institutions. |
| Acquisition of Specialist Firm | Fills OT sensor gaps for manufacturing and energy infrastructure protection under METI guidelines. |
| Geographic Expansion | Establishes EU data residency architecture for NIS2 cross-border reporting compliance. |
| Product Launch | Introduces managed detection service tier priced for mid-market buyers without dedicated SOCs. |
| Strategic Partnership | Embeds threat intelligence from CISA and sector ISACs into automated response playbooks. |
Methodological Framework
Bottom-up healthcare and financial institution modeling reconciled against top-down cloud infrastructure and threat intelligence tracking forms the analytical core. Primary interviews with CISOs, SOC directors, federal procurement officers, and managed detection service architects combined with secondary validation from CISA binding operational directives, FedRAMP authorization databases, EU NIS2 implementation guidance, and SEC cybersecurity disclosure filings. Top-down hyperscaler capex and endpoint protection vendor revenue tracking triangulates against bottom-up deployment surveys.
Input-output matrices map telemetry ingestion volumes, analyst labor costs, and compliance-driven procurement urgency across deployment model, end-user vertical, and integration complexity dimensions. CAGRs derive from regression analysis of historical SIEM replacement cycles and zero-trust mandate implementation timelines. Forecast inputs include CISA directive expansion scenarios and EU Cyber Resilience Act enforcement intensity gradients.
Caveats apply where CISA mandate delays or EU NIS2 deadline extensions could materially shift the outlook. Forecasts reflect documented assumptions around cloud migration velocity and threat actor sophistication trajectories. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Data Masking Market
Security Software
Asia-Pacific Encryption Software Market
Security Software
US Hardware OTP Token Authentication Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
Application Control Market
Security Software
Global Digital Vehicle Forensics Market
Security Software
Global Email Verification Tools Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Banking Encryption Software Market
Security Software
Cloud Encryption Software Market
Security Software
Door Phone Market
Security Software
Online Background Check Market
Security Software
ATM Security Market
Security Software
Global Mobile Identification Market
Security Software
Passport Reader Market
Security Software
Stalkerware Market