
 Europe Cyber Weapons Market | 2026-2036
Europe Cyber Weapons Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Cyber Weapons Market Insights
Defense ministry procurement is shifting toward integrated offensive-defensive cyber platforms across NATO-aligned European states. BAE Systems leverages its UK sovereign security clearance to dominate national cyber ranges and military training environments. Thales Group anchors its position through deep relationships with French defense procurement agencies and specialized encryption-grade malware development. Leonardo competes in Southern European markets by sustaining dual-use R&D pipelines that bridge military and critical infrastructure applications.
Europe cyber weapons encompass software-based tools engineered to exploit vulnerabilities, disrupt networks, or extract intelligence from adversarial systems, typically requiring kernel-level access or zero-day exploit chains for operational effectiveness. These instruments serve national security objectives including signals intelligence, critical infrastructure protection, and strategic deterrence in contested digital domains. Malware and spyware categories command the dominant share of institutional budgets due to their versatility across surveillance and cyber espionage missions. Cloud-based deployment models are expanding fastest among corporations seeking scalable threat emulation for red-team exercises, though on-premises architectures retain preference within military and intelligence agencies where air-gapped operational security remains non-negotiable.
EU NIS2 Directive and CE marking frameworks for dual-use technologies are tightening vendor compliance burdens, while national regulators including Germany's BSI and France's ANSSI impose additional certification layers that filter market access. The EU Cyber Defence Policy coordinates member-state offensive capability development, creating pooled procurement mechanisms that favor established European suppliers over non-regional entrants. Stakeholders must monitor how forthcoming EU AI Act provisions classify autonomous cyber tools, as algorithmic targeting systems may trigger prohibited-technology thresholds that reshape product roadmaps and export licensing requirements.
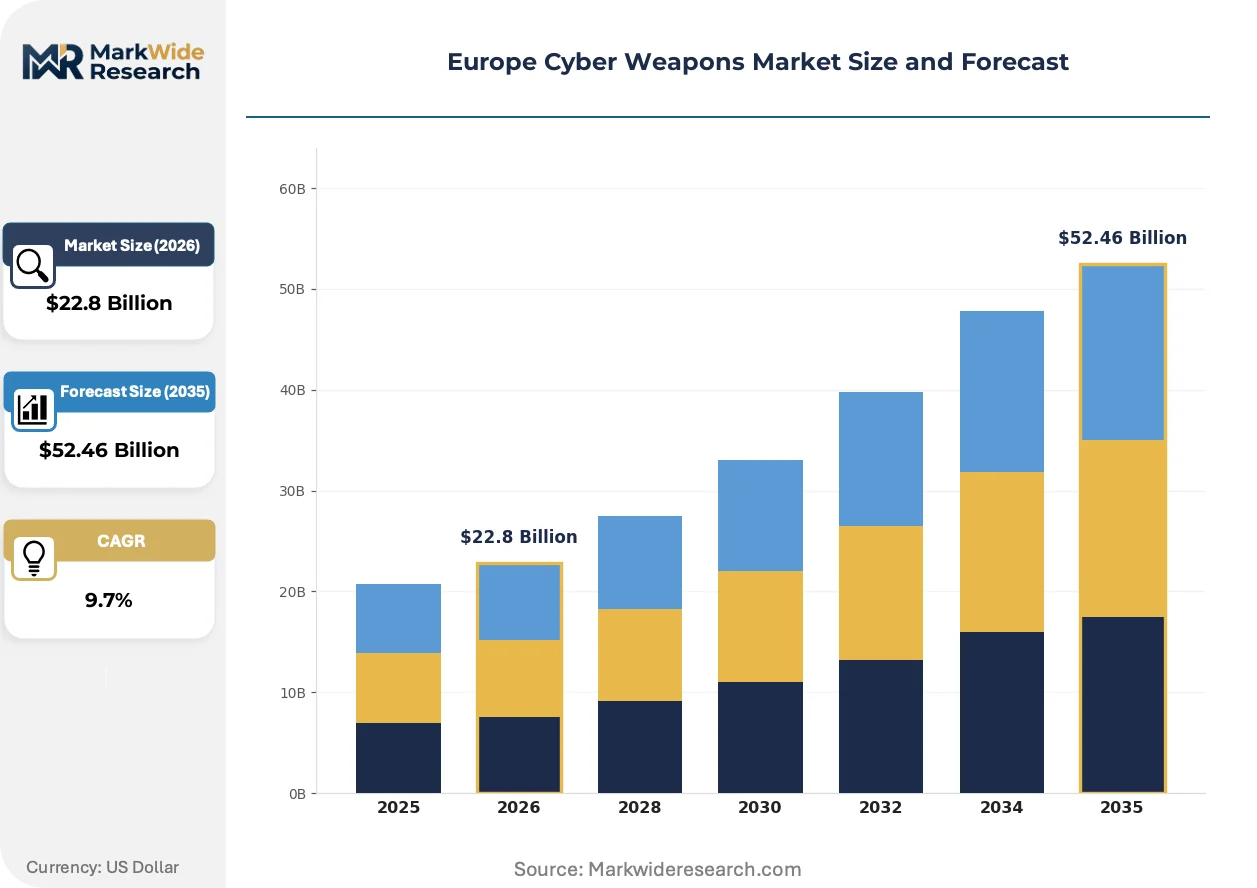
Market Dynamics
Defense procurement across NATO-aligned European states is consolidating around integrated offensive-defensive cyber platforms, compressing vendor ecosystems and elevating certification barriers under the EU Cyber Defence Policy framework.
Growth Catalysts
- EU NIS2 Directive:Mandatory security requirements for critical infrastructure operators are expanding the addressable market for certified cyber defense tools across energy, transport, and financial sectors.
- Offensive capability pooling:The EU Cyber Defence Policy coordinates member-state investments in collective cyber operations, creating standardized procurement channels that favor compliant vendors.
- Munich-Berlin cyber cluster:Germany's concentrated R&D ecosystem around BSI-certified facilities is accelerating technology transfer from academic research to deployable military tools.
Market Restraints
- Dual-use export controls:CE marking and EU dual-use technology frameworks impose multi-layer compliance timelines that delay product commercialization by 18-24 months for non-European suppliers.
- Zero-day vulnerability scarcity:The finite supply of undisclosed software exploits concentrates pricing power among a handful of specialized brokers, inflating input costs for advanced persistent threat capabilities.
- Air-gapped operational requirements:Military and intelligence agencies demand on-premises deployment architectures that prevent vendors from capturing recurring SaaS revenue streams available in corporate segments.
Strategic Opportunities
- Poland and Baltic states:These frontline NATO members are accelerating cyber defense investments under collective security frameworks, creating entry points for vendors with sovereign security clearances.
- AI-augmented targeting systems:Machine learning integration with exploit automation is converging with traditional malware development, opening product categories not yet classified under EU AI Act prohibitions.
- Red-team-as-a-service:Cloud-native threat emulation platforms are penetrating corporate security budgets in France and the Netherlands, displacing in-house penetration testing teams.
Industry Challenges
- Kernel-level engineering talent:The scarcity of developers with operating system internals expertise and active security clearance constrains product development velocity for European vendors.
- BSI-ANSSI certification divergence:Incompatible national certification requirements between Germany and France force vendors to maintain parallel compliance tracks, fragmenting R&D investment.
- Legacy system integration:Military platforms built on decades-old architectures require custom exploit adaptation, extending delivery timelines and eroding margin structures on fixed-price contracts.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Cyber Weapons Market |
| Market Size in 2026 | $22.8 Billion |
| Market Size in 2035 | $52.46 Billion |
| CAGR (2026 – 2036) | 9.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Malware, Ransomware, Spyware, DDoS Tools End User: Government Agencies, Military, Corporations, Hacktivists Deployment Model: On-Premises, Cloud-Based, Hybrid, Mobile Application: Surveillance, Data Theft, Infrastructure Disruption, Cyber Espionage |
| Companies Covered | BAE Systems, Airbus, Thales Group, Leonardo, Atos, Avast Software, Avira Operations, secunet Security Networks, Stormshield, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Cyber Weapons Market Trends and Innovations
Autonomous cyber capabilities and sovereign cloud architectures are restructuring how European defense agencies procure and deploy offensive tools. These shifts are compressing vendor selection criteria toward integrated platform providers with multi-national security clearances.
AI-driven exploit generation is converging with traditional vulnerability research workflows. French defense procurement agencies are piloting these systems for automated red-team operations. The technology is converging with legacy malware development pipelines, enabling faster adaptation to patched vulnerabilities while raising questions under forthcoming EU AI Act liability provisions.
REACH and RoHS compliance frameworks are extending into cyber hardware components, particularly for air-gapped deployment appliances. Industrial consequence includes mandatory substance disclosure for circuit boards and memory modules used in classified environments. Military procurement in Germany and Sweden is most affected, with vendors restructuring supply chains to exclude restricted materials.
Buyer concentration among defense ministries is consolidating vendor relationships around multi-year framework agreements. Traditional point-solution suppliers are losing access to procurement channels as France, Germany, and the United Kingdom favor platform integrators with sovereign facility clearance. This pattern is most visible in UK cyber range contracts, where national security vetting has become a non-negotiable qualification threshold.
Europe Cyber Weapons Market Segmentation
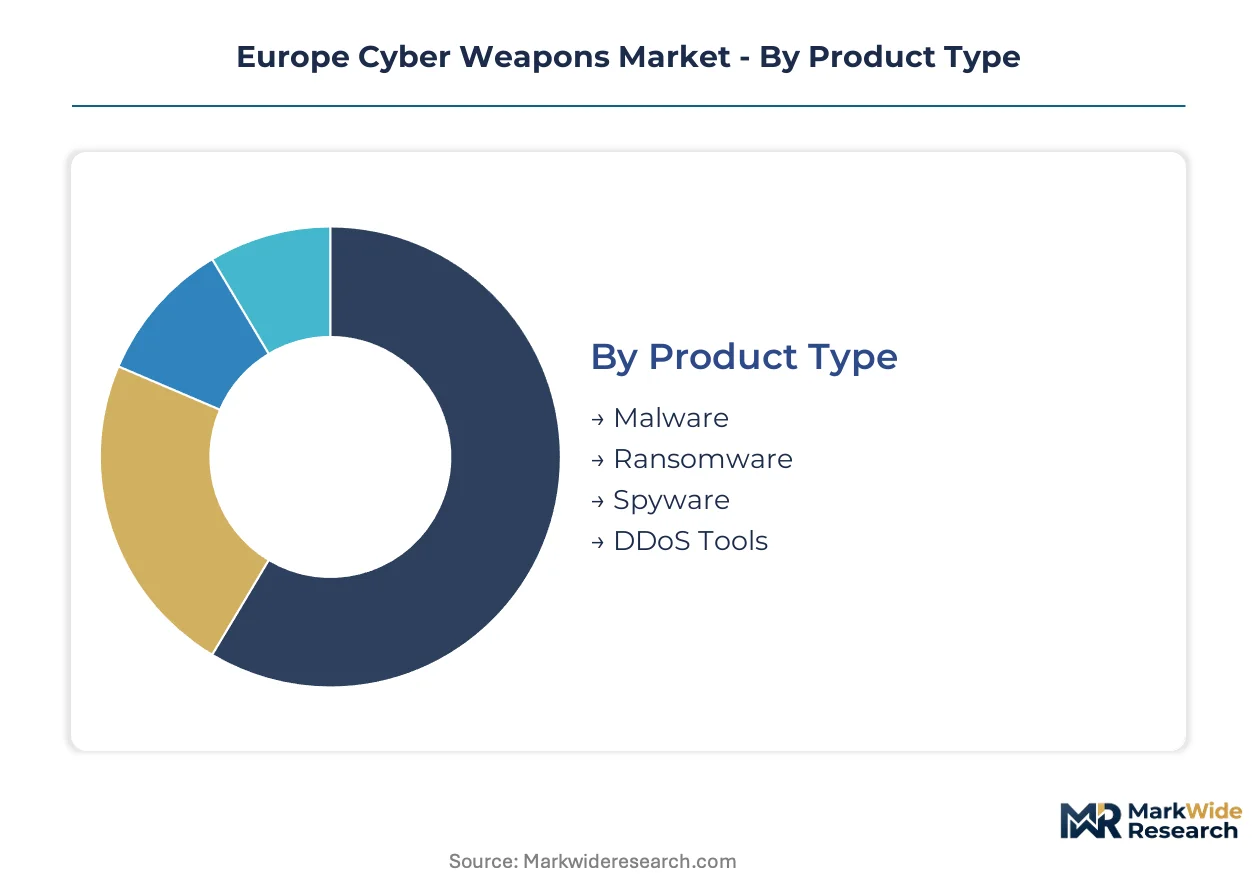
Segmentation in the Europe cyber weapons market reflects divergent procurement priorities across sovereign defense agencies, critical infrastructure operators, and intelligence services. Each dimension carries distinct certification requirements and deployment constraints that shape vendor product roadmaps and compliance investments.
Product Type:
Malware and spyware command premium pricing due to their technical sophistication and restricted supply chains, while ransomware and DDoS tools occupy higher-volume, lower-margin segments accessible to broader institutional buyers.
- Malware:Kernel-level exploit chains and zero-day delivery mechanisms constitute the core technology stack. Defense ministries in France and Germany concentrate procurement here for strategic deterrence capabilities under national security frameworks.
- Spyware:Encryption-grade surveillance tools with persistent access architectures dominate signals intelligence budgets. ANSSI and BSI certification requirements filter vendor participation to cleared European suppliers with sovereign facility access.
- Ransomware:Encryption-based disruption tools serve dual-use scenarios across military exercises and corporate red-team operations.
- DDoS Tools:Network-layer flooding capabilities support infrastructure stress testing and defensive preparedness validation.
Mature deployment sits with Malware. Newer deployment is concentrated in Spyware as AI-augmented targeting systems expand surveillance automation.
End User:
Government and military buyers impose sovereign security clearance requirements that exclude non-European vendors, while corporate and hacktivist segments drive demand for commercial-grade tools with faster procurement cycles.
- Government Agencies:Intelligence services and law enforcement bodies procure through classified procurement channels with multi-year framework agreements. Germany's BSI and France's DGSE shape technical specifications and vendor qualification criteria.
- Military:NATO-aligned defense ministries require air-gapped deployment architectures and on-premises operational control. The EU Cyber Defence Policy coordinates pooled procurement that favors established European platform integrators.
- Corporations:Critical infrastructure operators under NIS2 Directive mandates seek certified defensive tools with threat emulation capabilities.
- Hacktivists:Non-state actors access commercial-grade tools through gray-market channels outside formal procurement frameworks.
Procurement maturity clusters with Military end users. Fastest expansion is occurring in Corporations as regulatory compliance deadlines accelerate security investments.
Deployment Model:
On-premises architectures retain preference where operational security demands air-gapped isolation, while cloud-based models gain traction in corporate segments prioritizing scalability and rapid deployment.
- On-Premises:Physical appliance deployment within classified facilities satisfies military and intelligence agency security protocols. German cyber ranges and UK sovereign cloud environments mandate this architecture for offensive capability development.
- Cloud-Based:Scalable threat emulation platforms serve corporate red-team exercises and security validation workflows. French and Dutch enterprises are expanding adoption here for penetration testing automation.
- Hybrid:Split architectures balance sensitive operation isolation with scalable analytics processing.
- Mobile:Portable deployment kits support field operations and tactical cyber capabilities.
Established deployment concentrates in On-Premises. Steepest expansion trajectory is occurring in Cloud-Based models as corporate security budgets shift toward as-a-service consumption.
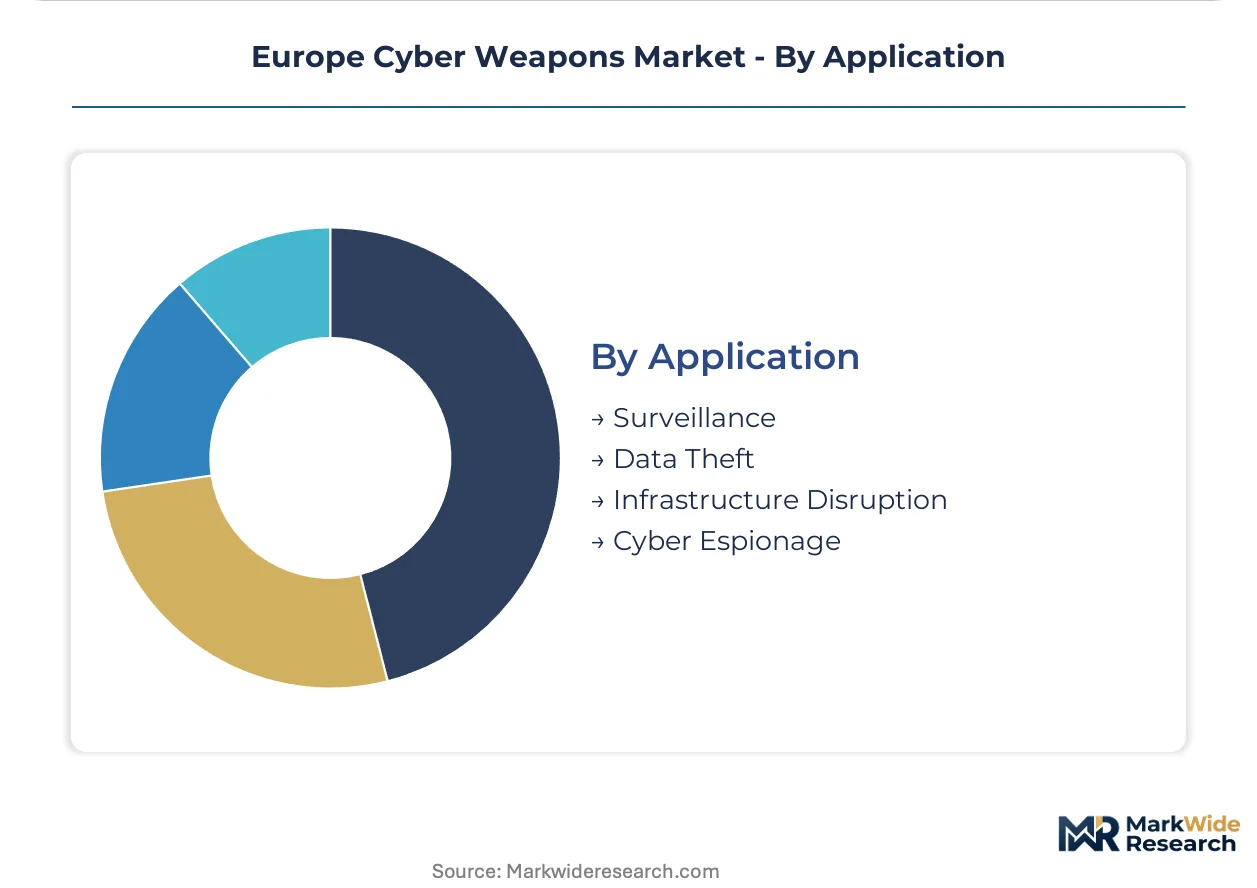
Application:
Surveillance and cyber espionage applications attract sustained defense investment, while infrastructure disruption tools face tighter export control scrutiny under EU dual-use technology frameworks.
- Surveillance:Persistent network monitoring and communications interception capabilities serve domestic intelligence and military signals operations. UK Government Communications Headquarters and Bundesnachrichtendienst procurement shapes technical requirements.
- Cyber Espionage:Targeted intelligence extraction from adversarial systems demands sophisticated exploit development and operational security. France's ANSSI coordinates national capability investments in this segment.
- Data Theft:Exfiltration-focused tools support economic intelligence and competitive advantage objectives.
- Infrastructure Disruption:Offensive capabilities targeting critical systems face enhanced regulatory classification under forthcoming EU AI Act provisions.
Institutional maturity resides with Surveillance. Emerging deployment is concentrating in Cyber Espionage as automated targeting systems reduce operational manpower requirements.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Production concentrates in Germany's BSI-certified cyber clusters, while consumption spreads across NATO-aligned defense ministries seeking sovereign clearance capabilities.
Germany
Bundeswehr cyber defense investments and BSI certification mandates drive procurement concentration. The NIS2 Directive imposes mandatory security standards on critical infrastructure operators. Munich-Berlin corridor hosts the continent's densest R&D ecosystem for kernel-level exploit development.
France
DGSE and ANSSI coordinate offensive capability investments through classified procurement channels. The EU Cyber Defence Policy positions French agencies as standard-setters for pooled NATO cyber operations. Île-de-France anchors encryption-grade malware development with sovereign facility requirements.
United Kingdom
Government Communications Headquarters procurement shapes signals intelligence technical specifications. National cyber range contracts now require UK sovereign security vetting as non-negotiable qualification. London-Southeast corridor dominates military training environment deployments.
Poland
Frontline NATO positioning accelerates cyber defense spending under collective security frameworks. The EU Cyber Defence Policy channels pooled procurement toward compliant European vendors. Warsaw cyber cluster attracts investment for tactical capability development.
Sweden
REACH and RoHS compliance frameworks extend into classified hardware components for air-gapped systems. Military procurement mandates substance disclosure for circuit boards in sensitive deployments. Stockholm-Uppsala region concentrates dual-use R&D bridging defense and critical infrastructure applications.
Europe Cyber Weapons Market Competitive Landscape
Top-tier vendors anchor sovereign-cleared platform integration, while mid-tier specialists compete for point-solution contracts. The vendor ecosystem compresses around multi-year framework agreements that favor established European suppliers. Three archetypes dominate: defense conglomerates with national security clearance, cybersecurity pure-plays with BSI-ANSSI certification, and aerospace-industrial hybrids leveraging dual-use R&D pipelines. Competitive moves concentrate on M&A for clearance acquisition and strategic partnerships for technology licensing.
Within the defense conglomerate tier, BAE Systems, Thales Group, and Leonardo exemplify positioning strategies. BAE Systems occupies a UK-centric anchor role through sovereign facility access. Thales Group exemplifies French procurement channel depth. Leonardo represents Southern European market penetration through dual-use capability bridging.
| Leading Market Players |
|---|
| BAE Systems |
| Airbus |
| Thales Group |
| Leonardo |
| Atos |
| Avast Software |
| Avira Operations |
| secunet Security Networks |
| Stormshield |
| Others |
Pricing and Supply Chain Analysis
Zero-day exploit broker indices cascade through vendor cost structures, compressing margins for mid-tier suppliers while concentrating pricing power among cleared platform integrators serving NATO defense ministries.
Pricing Analysis
Margin tightening in spyware and malware tiers reflects scarcity premiums on kernel-level engineering talent and sovereign facility clearance. Three-tier pricing structure across premium, standard, and economy levels separates encryption-grade surveillance tools from commercial red-team platforms. Cost-down pressure on cloud-native threat emulation accelerates because corporate buyers prioritize scalable subscription models over perpetual licensing. Government agencies exhibit lowest price sensitivity due to national security mandates, while critical infrastructure operators under NIS2 compliance deadlines drive hardest negotiation on certified defensive tools.
Supply Chain Analysis
Single-source vulnerability sits with Israeli and US-based zero-day brokers who dominate undisclosed exploit availability. European vendors draw from Germany, France, and the United Kingdom for cleared engineering talent and sovereign facility access. Raw material dependencies center on specialized semiconductor components for air-gapped deployment appliances, encryption-grade hardware security modules, and restricted substance-compliant circuit boards. Tariff exposure runs through dual-use technology export classifications that delay cross-border component transfers. Distribution runs through classified procurement channels and multi-year framework agreements rather than open commercial markets.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Defense procurement consolidation around integrated platform providers is squeezing point-solution vendors, with BSI-ANSSI certification divergence accelerating exits among undercapitalized specialists.
For Market Incumbents: Cement multi-year framework positions by acquiring cleared engineering teams in the Munich-Berlin corridor and Île-de-France region. Deepen sovereign facility access through national security vetting investments that match BAE Systems and Thales Group clearance levels. Kernel-level talent scarcity threatens product velocity—lock specialized developers through equity retention structures before competitors exhaust the finite cleared labor pool. For New Entrants and Emerging Players: AI-augmented exploit automation offers entry into cyber espionage segments not yet classified under EU AI Act prohibitions. Poland and Baltic states present the most penetrable geography—frontline NATO positioning accelerates procurement without incumbent relationship entrenchment. Pursue red-team-as-a-service cloud platforms for Dutch and French corporate security budgets, displacing legacy penetration testing providers through faster deployment cycles. For Investors and Strategic Acquirers: Distressed-cycle entries favor mid-tier cybersecurity pure-plays with BSI or ANSSI certification but insufficient scale for framework agreement competition. Long-term viability hinges on conversion from point-solution revenue to recurring platform income through military cyber range contracts. Watch EU AI Act implementation timelines as the critical inflection signal—autonomous targeting classifications may render entire product categories non-compliant overnight.| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Cleared engineering teams in Germany's cyber clusters accelerate sovereign facility access for platform integrators. |
| Strategic Partnership | Technology licensing with French DGSE channels opens classified procurement pathways for encryption-grade malware. |
| Product Launch | AI-augmented targeting systems penetrate cyber espionage before EU AI Act prohibitions crystallize. |
| Platform Integration | Unified offensive-defensive architectures satisfy NATO defense ministry consolidation mandates under EU Cyber Defence Policy. |
| Geographic Expansion | Poland and Baltic state presence captures frontline NATO cyber defense investments outside incumbent strongholds. |
Research Methodology
Document review covered EU NIS2 Directive implementation guidance, NATO cyber defense policy frameworks, and national procurement registers, complemented by interviews with defense ministry procurement officers, BSI certification auditors, ANSSI technical directors, and sovereign facility security officers. Secondary validation drew from CE marking databases, dual-use technology export classifications, and academic exploit research publications. Bottom-up vendor revenue estimates triangulated against top-down defense budget allocations across the analysis window.
Cross-referencing historical capability investment patterns with expert panel input shaped the analytical framework across product type, end user, deployment model, and application segments. CAGRs derived from regression against defense spending trajectories and regulatory compliance deadline acceleration. Industry-specific forecast inputs included zero-day broker pricing trends and sovereign clearance processing timelines.
Several conditions sit outside the modeled scope, including classified program budgets, undisclosed exploit transaction volumes, and potential EU AI Act reclassifications of autonomous cyber tools. Forecasts reflect documented procurement patterns and regulatory implementation schedules. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Europe Automotive Cybersecurity Market
Defense Cybersecurity
Ballistics Targeting Software Market
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Defence Cybersecurity Market
Defense Cybersecurity
Automotive Cyber Security Market
Defense Cybersecurity
Military Cybersecurity Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Electronic Warfare Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Blockchain Technology in Aerospace and Defense Market
Defense Cybersecurity
Mine and IED Detection System Market
Defense Cybersecurity
Aviation Cyber Security Market
Defense Cybersecurity
Military Sensors Cybersecurity Solutions Market
Defense Cybersecurity
Defensive Cyber Weapons Market
Defense Cybersecurity
Anti-Drone Defense System Market