
 Defensive Cyber Weapons Market | 2026-2036
Defensive Cyber Weapons Market Size, Share, and Industry Trends Forecast 2026-2036
Defensive Cyber Weapons Market Outlook
CMMC certification is redrawing vendor eligibility for Pentagon contracts. Lockheed Martin Corporation leverages its classified program heritage to sustain prime contractor status. BAE Systems anchors UK sovereign cyber capabilities through deep integration with GCHQ.
Defensive cyber weapons encompass software and hardware systems engineered to detect, intercept, and neutralize hostile network intrusions through real-time packet inspection, automated threat signature matching, and adaptive deception protocols. These systems serve military commands and critical infrastructure operators seeking active protection beyond passive perimeter monitoring. Cloud-based deployment is accelerating fastest as agencies migrate sensitive workloads to federated environments, while on-premises solutions retain dominance in air-gapped defense networks where physical isolation overrides operational flexibility. AI-based Security commands premium positioning due to adversarial training requirements, whereas Signature-based Detection remains a volume category servicing legacy enterprise refresh cycles.
NIST frameworks, CMMC maturity levels, and the EU Cyber Solidarity Act collectively shape procurement specifications and vendor qualification pathways. The US Department of Defense mandates CMMC Level 3 minimums for contract eligibility, while European operators face parallel conformity pressures under ENISA-coordinated certification schemes. Stakeholders must track divergence between US and European assurance standards when architecting transatlantic product portfolios.
Market Dynamics
Active defense platforms are displacing passive perimeter monitoring as NATO member states mandate real-time neutralization capabilities over detection-only architectures.
Growth Catalysts
- CMMC Level 3 Mandates:Pentagon contractors must achieve certification for eligibility, forcing capability upgrades across the defense industrial base.
- AI-based Security:Adversarial training protocols enable autonomous threat neutralization without human-in-the-loop delays.
- Cloud Migration:Federated environments demand portable defensive cyber weapons deployable across hybrid infrastructure.
Market Restraints
- Classified Program Access:Prime contractor status requires security clearances that bar mid-tier vendors from Pentagon procurement channels.
- Air-gapped Network Dominance:On-premises solutions retain preference in defense networks, limiting SaaS penetration despite operational advantages.
- Signature Library Latency:Legacy detection systems require constant updates that lag zero-day exploit emergence windows.
Strategic Opportunities
- EU Cyber Solidarity Act:Coordinated response frameworks create procurement pools for cross-border threat sharing platforms.
- Critical Infrastructure Operators:Energy and transportation sectors face NIS2 Directive compliance deadlines without mature defensive capabilities.
- Deception Protocol Convergence:Honeypot integration with automated response systems opens new product categories beyond detection.
Industry Challenges
- Cleared Workforce Scarcity:Polygraph and background investigation backlogs extend hiring timelines for classified program teams.
- CMMC Audit Bottlenecks:Limited third-party assessor capacity creates certification queues that delay contract eligibility.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Defensive Cyber Weapons Market |
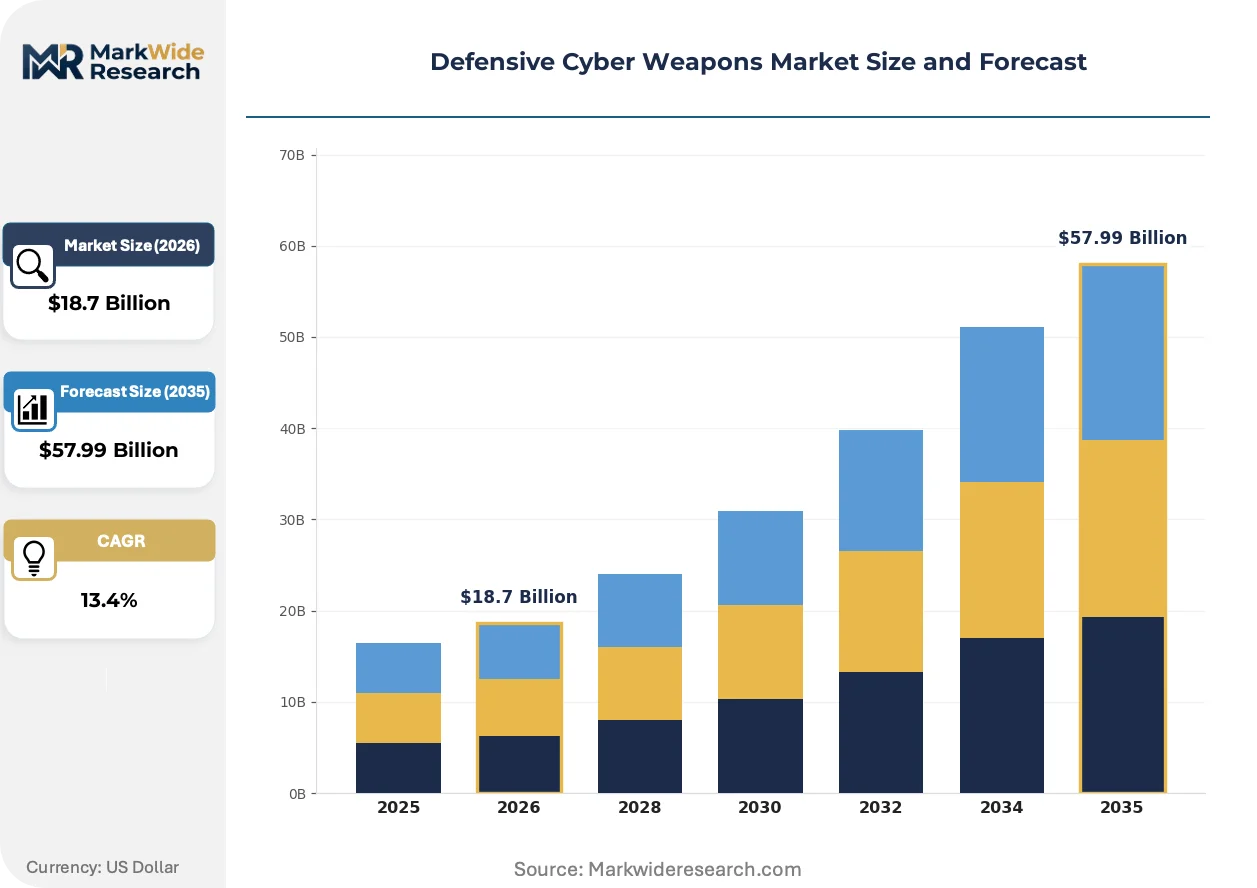
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $57.99 Billion |
| CAGR (2026 – 2036) | 13.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Intrusion Detection Systems, Firewalls, Anti-Malware Tools, Encryption Software Deployment: On-premises, Cloud-based, Hybrid, Managed Services End User: Government Agencies, Financial Institutions, Healthcare Providers, Retail Corporations Technology: AI-based Security, Machine Learning Algorithms, Behavioral Analytics, Signature-based Detection |
| Companies Covered | BAE Systems, Lockheed Martin Corporation, Raytheon Technologies Corporation, General Dynamics Corporation, Booz Allen Hamilton Inc., Cisco Systems, Northrop Grumman, IBM Corporation, Thales, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Defensive Cyber Weapons Market Strategic Shifts
Real-time packet inspection architectures are redefining performance benchmarks as agencies reject signature-dependent latency in favor of behavioral anomaly detection.
Automated deception protocols are supplanting static honeypot deployments. Military commands in classified environments deploy adaptive decoys that morph in response to adversary reconnaissance tactics. This capability compression eliminates the gap between intrusion detection and active neutralization that previously required human analyst intervention.
The EU Cyber Solidarity Act establishes joint procurement mechanisms for member states facing systemic threats. Industrial consequence includes standardized technical specifications that reduce vendor customization overhead. ENISA-coordinated certification schemes are most affected, with operators consolidating vendor relationships to satisfy mutual recognition requirements.
Defense agencies now require continuous authorization models rather than point-in-time compliance attestations. The Pentagon's Platform One initiative exemplifies this shift, with DevSecOps pipelines replacing waterfall acquisition cycles. This behavioral pivot is most visible in United States federal contracting, where traditional RFP processes compress into iterative software factory engagements.
Defensive Cyber Weapons Market Segmentation
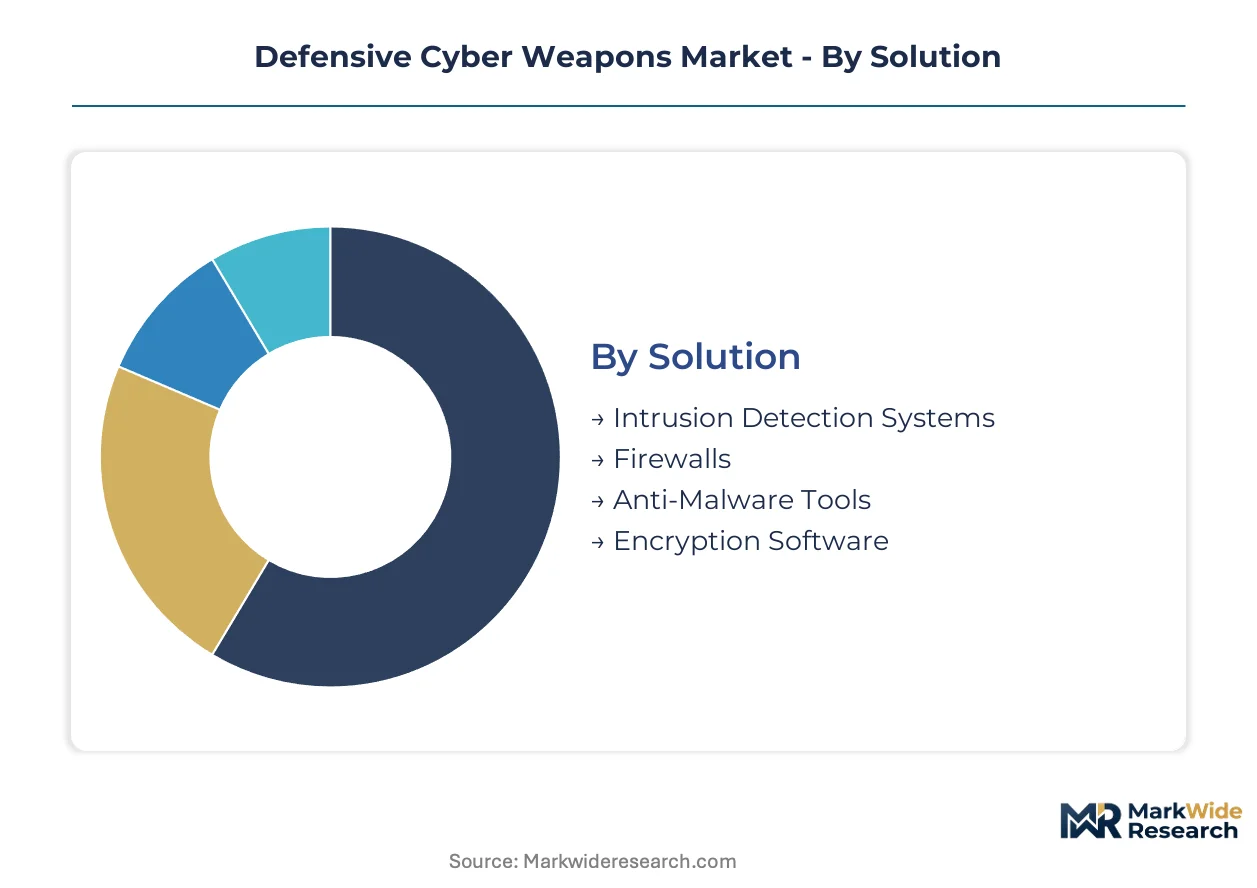
Defensive cyber weapons segment across four intersecting dimensions that determine procurement pathways and vendor positioning. Solution architecture dictates integration complexity with legacy defense infrastructure. Deployment modality shapes operational tempo for classified versus commercial workloads.
Solution:
Intrusion Detection Systems face substitution pressure from AI-driven behavioral platforms that collapse detection-response latency into single-cycle operations.
- Intrusion Detection Systems:Network traffic analysis engines employing deep packet inspection and protocol anomaly detection. Pentagon contracting channels concentrate procurement of hardware-appliance variants for SIPRNet perimeter defense under CMMC Level 3 mandates.
- Firewalls:Stateful inspection gateways with application-layer filtering and zero-trust segmentation capabilities. NATO member state procurement pools favor next-generation firewall deployments for coalition network interoperability.
- Anti-Malware Tools:Endpoint agents with sandbox detonation and memory forensics.
- Encryption Software:Quantum-resistant key management and hardware security module orchestration.
Firewalls retain volume leadership; Intrusion Detection Systems hold the steepest expansion curve.
Deployment:
Cost tier stratification separates sovereign-class air-gapped installations from commodity cloud subscriptions.
- On-premises:Hardware appliances deployed within physically isolated facility boundaries with no external connectivity. United States Department of Defense networks mandate on-premises deployment for collateral and above-categorized workloads, preserving prime contractor dominance through cleared integration teams.
- Cloud-based:Federated defensive platforms with containerized sensor deployment across multi-tenant infrastructure. European critical infrastructure operators under NIS2 Directive deadlines are migrating sensitive workloads to EU-sovereign cloud regions.
- Hybrid:Policy-orchestrated split between classified on-premises cores and unclassified cloud analytics tiers.
- Managed Services:Outsourced security operations with 24/7 analyst coverage and threat intelligence integration.
On-premises deployments retain volume leadership; Cloud-based configurations hold the steepest expansion curve.
End User:
Application criticality separates nation-state grade requirements from enterprise compliance baselines.
- Government Agencies:Military commands and intelligence services requiring active defense capabilities with automated neutralization protocols. United States federal contracting channels dominate procurement volume through classified program offices.
- Financial Institutions:Payment system operators and central banks facing systemic risk designation under national cyber frameworks.
- Healthcare Providers:Hospital networks and medical device manufacturers with patient safety implications from ransomware disruption.
- Retail Corporations:Consumer-facing payment processors with cardholder data environment obligations.
Government Agencies retain volume leadership; Financial Institutions hold the steepest expansion curve.
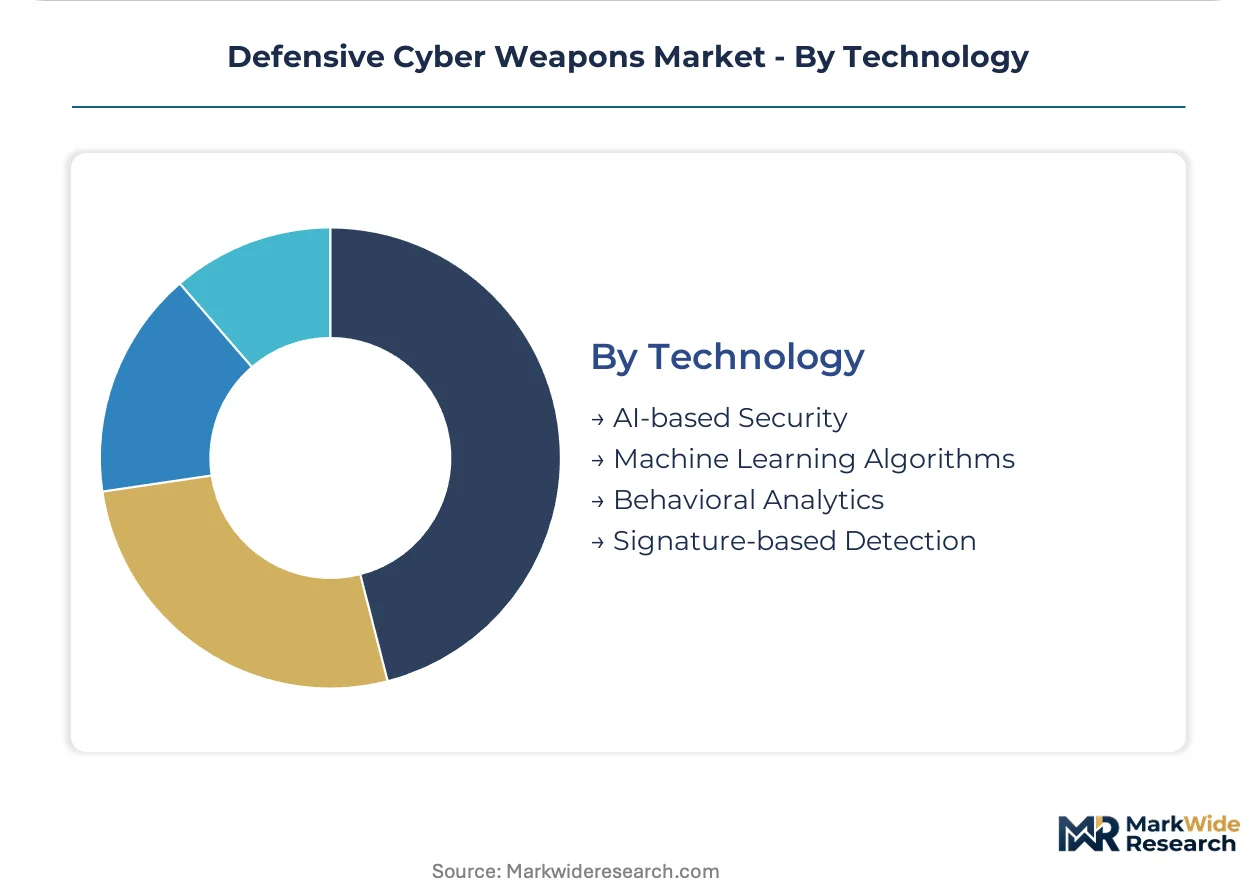
Technology:
Customer type maturity separates early-adopter military commands from legacy enterprise refresh cycles.
- AI-based Security:Neural network architectures trained on adversarial examples for autonomous threat neutralization without human-in-the-loop authorization delays. Pentagon research funding concentrates development through DARPA's AI exploration programs.
- Machine Learning Algorithms:Supervised and unsupervised models for anomaly detection in encrypted traffic streams.
- Behavioral Analytics:User and entity behavior analytics establishing deviation baselines for insider threat identification.
- Signature-based Detection:Pattern-matching engines dependent on continuously updated threat intelligence feeds.
Signature-based Detection retains volume leadership; AI-based Security holds the steepest expansion curve.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The EU Cyber Solidarity Act and CMMC mandates in the United States are redirecting procurement flows toward certified vendors. National security classifications fragment vendor eligibility across NATO member states. Sovereign cloud requirements in Europe accelerate localized deployment architectures.
United States
Pentagon contracting channels concentrate procurement volume through classified program offices. The Department of Defense mandates CMMC Level 3 minimums for contract eligibility under NIST frameworks. The National Capital Region anchors prime contractor headquarters, with cleared integration teams servicing SIPRNet perimeter defense installations.
Germany
Bundeswehr cyber commands expand active defense platform procurement under NATO cooperative frameworks. The country's national cyber regulator coordinates ENISA certification schemes with EU Cyber Solidarity Act implementation timelines. Munich and Stuttgart host defense industrial clusters where BAE Systems anchors sovereign capability integration.
United Kingdom
GCHQ deep integration requirements shape vendor qualification pathways for classified programs. The National Cyber Security Centre mandates baseline capabilities for critical national infrastructure operators. Cheltenham and London concentrate cleared workforce pools servicing intelligence community procurement channels.
France
DGA procurement pools favor European vendor consortiums for sovereign cyber weapon systems. The country's national cyber regulator enforces certification convergence with EU-wide mutual recognition frameworks. Paris-Saclay and Toulouse host defense research clusters developing autonomous threat neutralization protocols.
Israel
Military intelligence unit alumni seed specialized vendors with adversarial training expertise. The country's national cyber directorate coordinates offensive-defensive capability convergence for active defense platforms. Tel Aviv and Beersheba concentrate startup ecosystems commercializing military-developed deception protocols.
Defensive Cyber Weapons Market Competitive Environment
Player mix skews toward classified-cleared defense primes with legacy program heritage. The vendor base concentrates around firms sustaining security clearances that bar mid-tier competitors from Pentagon procurement. Two strategic archetypes dominate: sovereign-anchored systems integrators with intelligence agency integration, and dual-use technology vendors commercializing military-developed platforms. Competitive moves center on cleared workforce acquisition and CMMC audit capacity expansion.
Within the classified prime tier, Lockheed Martin Corporation and BAE Systems exemplify archetype positioning through sustained intelligence community relationships. Raytheon Technologies Corporation occupies a parallel position in NATO cooperative procurement channels. Booz Allen Hamilton Inc. represents the advisory-integrator hybrid model combining consulting heritage with cleared technical delivery. These three firms anchor competitive dynamics around CMMC certification timelines and polygraph-cleared hiring pipelines.
| Leading Market Players |
|---|
| BAE Systems |
| Lockheed Martin Corporation |
| Raytheon Technologies Corporation |
| General Dynamics Corporation |
| Booz Allen Hamilton Inc. |
| Cisco Systems |
| Northrop Grumman |
| IBM Corporation |
| Thales |
| Others |
Value Chain & Pricing Dynamics
CMMC certification tiers gate both vendor qualification and price differentiation simultaneously, with Level 3 mandates forcing capability investments that compress margins for mid-tier suppliers while primes capture premium positioning through cleared program heritage.
Pricing Analysis
Certification level creates the primary spread across vendor tiers. Three-tier pricing structure across CMMC Level 3, Level 2, and uncertified levels separates Pentagon-eligible primes from restricted contractors and commercial-only suppliers. Pricing pressure stems from audit backlog delays that extend certification timelines and defer contract eligibility revenue. Government agencies demonstrate lowest price sensitivity given mission-critical procurement mandates, while commercial critical infrastructure operators face capital constraints under NIS2 compliance deadlines.
Supply Chain Analysis
Polygraph-cleared workforce pipelines in the United States, United Kingdom, and Israel concentrate specialized engineering talent for classified program delivery. Semiconductor fabrication for packet inspection hardware draws from Taiwan and South Korea, while quantum-resistant cryptographic modules source from domestic foundries under ITAR restriction. Single-source vulnerability runs through cleared integration teams with active security clearances. Distribution runs through prime contractor channel partnerships with established SIPRNet access credentials.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics now governs competitive outcomes as DevSecOps pipelines displace waterfall procurement, with interoperability standards under Platform One creating winner-take-most dynamics for containerized defensive cyber weapons.
For Market Incumbents: Secure cleared workforce pipelines through polygraph-ready hiring partnerships and university recruitment pipelines with active security clearance sponsorship programs. Expand CMMC audit capacity investments to reduce certification queue exposure for subcontractor networks. Vertical integration into adversarial AI training datasets preserves differentiation against commercial AI vendors lacking classified program heritage. For New Entrants and Emerging Players: Lead with deception protocol specialization targeting European critical infrastructure operators under NIS2 Directive compliance deadlines, where sovereign cyber capabilities lack mature active defense platforms. The EU Cyber Solidarity Act joint procurement mechanisms offer the most penetrable entry channel. Partner with national cyber regulators for ENISA certification pre-qualification to accelerate vendor list inclusion. For Investors and Strategic Acquirers: EU NIS2 enforcement reshapes the acquisition landscape toward compliance-automation platforms with pre-built regulator relationships. Long-term viability centers on vendors bridging the gap between commercial cybersecurity tooling and sovereign-grade active defense requirements. Acquisition target archetype: mid-tier deception protocol specialists with cleared leadership teams. Watch CMMC assessor capacity expansion as inflection indicator for contract eligibility velocity.| Strategic Initiative | Industry Significance |
|---|---|
| CMMC Audit Capacity Expansion | Reduces certification bottlenecks that delay Pentagon contract eligibility for vendor networks. |
| Adversarial AI Training Investment | Builds autonomous threat neutralization capabilities through DARPA-funded research pipelines. |
| EU Sovereign Cloud Partnership | Positions containerized defensive platforms for NIS2-mandated critical infrastructure migration. |
| Cleared Workforce Acquisition | Secures polygraph-ready engineering teams for classified program office procurement channels. |
| Deception Protocol Commercialization | Translates military-developed honeypot architectures into dual-use critical infrastructure products. |
Study Parameters
The analysis maps active defense platforms, intrusion detection systems, and deception protocol architectures, each validated through program managers at classified procurement offices, cleared systems integrators, ENISA certification coordinators, and critical infrastructure CISOs. Primary interviews with defense industrial base contractors and European national cyber regulators combined with secondary validation against Pentagon budget justification documents, EU Cyber Solidarity Act implementation timelines, and NIST framework revision records. Bottom-up vendor revenue triangulation against top-down government procurement database aggregation ensured cross-verification.
Consistency checks against external benchmarks validated output ranges across the projection horizon. Segmentation dimensions modeled include solution architecture, deployment modality, end-user criticality tier, and technology maturity level. CAGRs derived from historical contract award velocity and policy mandate implementation schedules. Forecast inputs incorporated CMMC certification penetration curves and EU member state NIS2 transposition timelines.
Forecasts assume regulatory continuity in CMMC implementation and EU Cyber Solidarity Act procurement pools; material policy shifts would require re-modeling. Specific risks include classified program budget reallocation and ENISA certification scheme divergence across member states. Practitioners should keep alternative scenarios live as NATO cooperative framework priorities evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Europe Cyber Weapons Market
Defense Cybersecurity
Maritime Cybersecurity Market
Defense Cybersecurity
Asia-Pacific Cyber Weapons Market
Defense Cybersecurity
Vehicle Cybersecurity Market
Defense Cybersecurity
Aviation Cyber Security Market
Defense Cybersecurity
Military Computers Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Automotive Cybersecurity Service Market
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Automotive Cyber Security Market
Defense Cybersecurity
Mine and IED Detection System Market
Defense Cybersecurity
Railway Cyber Security Market
Defense Cybersecurity
Anti-Drone Defense System Market
Defense Cybersecurity
Ballistics Targeting Software Market
Defense Cybersecurity
Electronic Warfare Market