
 Military Cybersecurity Market | 2026-2036
Military Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Military Cybersecurity Market Outlook
CMMC 2.0 is recalibrating the cost-of-entry calculus for defense contractors by imposing tiered cybersecurity maturity requirements that disqualify unprepared vendors from Pentagon contracts. Lockheed Martin Corporation leverages its classified facility infrastructure to sustain prime contractor status across all five CMMC levels. Booz Allen Hamilton anchors its position through deep intelligence community relationships and cleared workforce scale that competitors struggle to replicate.
Military cybersecurity encompasses the technologies, protocols, and operational practices designed to protect defense networks, weapons systems, and command infrastructure from unauthorized access, disruption, or exploitation by state and non-state actors. Core functional parameters include real-time threat detection latency under one millisecond, AES-256 encryption standards for data at rest, and air-gapped segmentation for nuclear command-and-control systems. Network Security applications dominate current procurement budgets as legacy infrastructure undergoes hardening against supply-chain intrusions, while Cloud-based deployment represents the fastest-expanding segment as classified cloud environments achieve provisional authorization. Threat Intelligence services command premium margins due to scarce analyst talent and specialized linguistics requirements.
The US Department of Defense, NIST, and NSA collectively shape market demand through the CMMC framework, SP 800-171 controls, and Commercial Solutions for Classified program requirements that vendors must satisfy before contract eligibility. European defense ministries reference NATO STANAG standards and EDF cybersecurity clauses that create parallel but non-identical compliance burdens for transatlantic suppliers. Stakeholders must monitor whether allied certification reciprocity agreements materialize or fragment procurement into geographically siloed vendor pools.
Market Dynamics
Zero-trust architecture mandates are compressing procurement timelines across NATO defense ministries, forcing contractors to reengineer network segmentation before contract eligibility rather than after award.
Growth Catalysts
- CMMC 2.0 tiered compliance:The US Department of Defense's framework creates a qualified vendor pool by disqualifying contractors below specified maturity levels, concentrating contract flow toward prepared suppliers.
- Offensive cyber operations doctrine:Pentagon units conducting active defense missions require hardened command infrastructure that sustains operational tempo under persistent adversary probing.
- Classified cloud provisional authorizations:Intelligence community data center migrations to IL6-accredited environments are accelerating demand for compliant managed security services.
Market Restraints
- TS/SCI-cleared workforce scarcity:Security clearance processing backlogs at the Defense Counterintelligence and Security Agency limit vendor scaling regardless of technical capability.
- Specialized hardware supply concentration:Trusted foundry requirements for military-grade semiconductors restrict component sourcing to domestic facilities with DoD accreditation.
- Air-gapped system integration friction:Legacy nuclear command-and-control infrastructure resists seamless overlay with modern threat detection architectures.
Strategic Opportunities
- Five Eyes intelligence sharing protocols:Interoperable cybersecurity standards between US, UK, Canadian, Australian, and New Zealand defense agencies open cross-border contract pipelines for qualified vendors.
- AI-augmented threat hunting convergence:Machine learning inference at the tactical edge combined with human analyst triage addresses analyst-to-alert ratio imbalances in security operations centers.
- European Defence Fund cyber clauses:EDF procurement guidelines embedding resilience requirements create parallel certification pathways for transatlantic suppliers seeking EU member state contracts.
Industry Challenges
- CMMC third-party assessment organization bottlenecks:Limited accredited C3PAO audit capacity stretches certification timelines to 18-24 months for mid-tier contractors.
- Cross-domain solution engineering complexity:Moving data between classified and unclassified networks requires specialized guard technology that few vendors integrate at scale.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Military Cybersecurity Market |
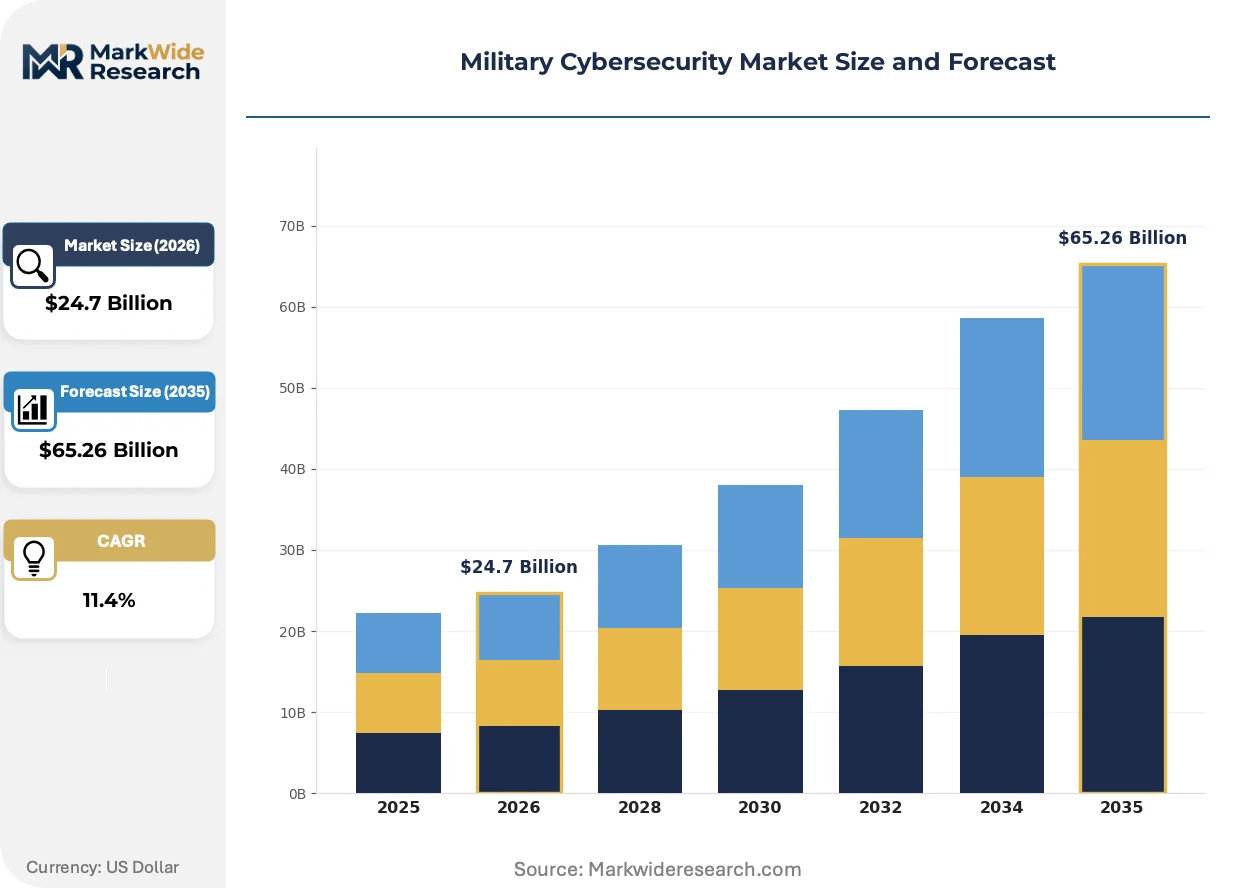
| Market Size in 2026 | $24.7 Billion |
| Market Size in 2035 | $65.26 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Intrusion Detection, Firewall, Encryption, Endpoint Security End User: Defense Agencies, Military Branches, Contractors, Intelligence Services Application: Threat Intelligence, Network Security, Data Protection, Risk Management Deployment: On-premises, Cloud-based, Hybrid, Managed Services |
| Companies Covered | Lockheed Martin Corporation, Northrop Grumman Corporation, BAE Systems, Raytheon Technologies Corporation, Booz Allen Hamilton, General Dynamics Corporation, Thales Group, Cisco Systems, Inc., IBM Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Military Cybersecurity Market Strategic Shifts
Defense procurement is pivoting from perimeter-based security models to continuous verification architectures that assume network compromise and limit lateral movement through microsegmentation.
Secure access service edge (SASE) frameworks are consolidating network security functions into unified cloud-delivered stacks. US Cyber Command and service cyber components are piloting these architectures for distributed tactical units requiring policy-enforced connectivity. This consolidation is collapsing the traditional boundary between WAN optimization and security point solutions, compressing vendor stacks into integrated platform plays.
NATO STANAG 4774/4778 encryption standards are mandating sovereign cryptographic modules for allied communications interoperability. European defense ministries are procuring national variants that satisfy both NATO technical requirements and domestic classification authority rules. French, German, and Italian cyber commands are driving this alignment through joint exercise validation of cross-border secure voice and data protocols.
Continuous monitoring contracts are displacing periodic compliance attestation as the dominant procurement vehicle. Defense agencies now demand real-time visibility into contractor security postures through automated scorecarding rather than annual audits. This behavioral shift is most pronounced in US Navy and Air Force supply chains, where program offices terminate contracts within 72 hours of critical control degradation.
Military Cybersecurity Market Segmentation
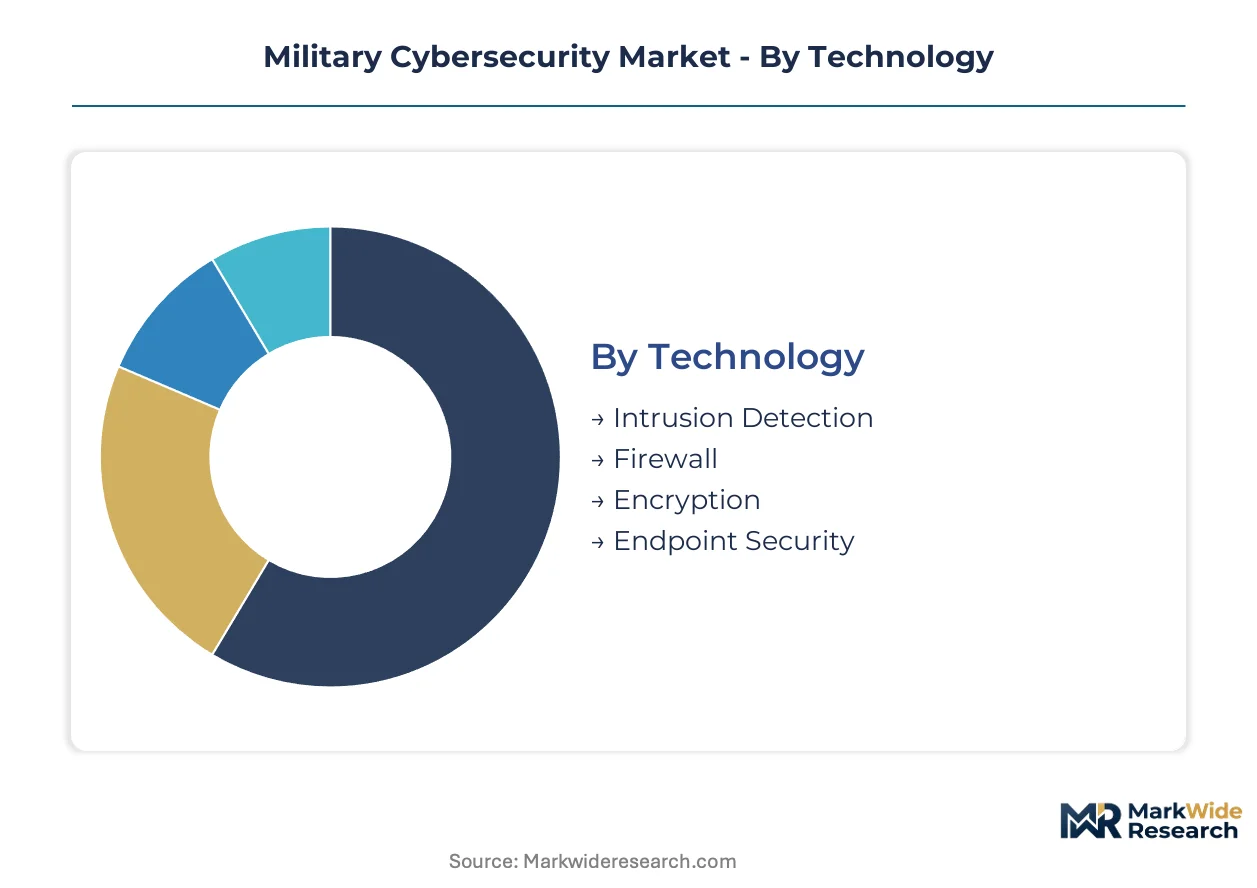
Military cybersecurity procurement fractures across technology generations, user security clearances, and operational tempo requirements. Understanding these segment boundaries reveals where compliance costs concentrate and where vendor margins expand.
Technology:
Volume concentrates in perimeter defenses with established procurement channels. Premium margins attach to detection and response capabilities requiring cleared analyst integration.
- Intrusion Detection:Real-time anomaly identification systems processing sub-millisecond telemetry from classified networks. Demand clusters at US Cyber Command and NSA facilities where operational tempo mandates continuous monitoring. CMMC 2.0 mandates are accelerating replacement of signature-based tools with behavioral analytics.
- Encryption:AES-256 and quantum-resistant algorithm implementations for data at rest and in transit. NATO STANAG 4774 compliance drives procurement across Five Eyes defense ministries, with sovereign cryptographic module requirements fragmenting vendor pools by nationality.
- Firewall:Next-generation perimeter controls with deep packet inspection for military-grade protocols.
- Endpoint Security:Device-level protection hardened against supply-chain compromise vectors.
Mature deployment sits with Firewall installations across legacy command networks. Newer deployment is concentrated in Intrusion Detection architectures at cyber mission force facilities.
End User:
Contractor ecosystems absorb the bulk of CMMC compliance expenditure while intelligence services command premium service tiers.
- Defense Agencies:Pentagon service-level cyber components and combatant command infrastructure requiring IL6-accredited environments. Procurement prioritizes cross-domain solutions for moving data between classification levels, with US Cyber Command driving requirements for tactical edge connectivity.
- Intelligence Services:CIA, NSA, and allied foreign intelligence apparatus with specialized linguistics and counterintelligence demands. Scarcity of TS/SCI-cleared analysts creates vendor lock-in for incumbent providers with existing facility clearances.
- Military Branches:Service-specific cyber protection teams across Army, Navy, Air Force, and Marine Corps.
- Contractors:Defense industrial base suppliers navigating tiered CMMC maturity assessments.
Established spending patterns characterize Military Branches. Intelligence Services represent the segment expanding most quickly as classified cloud migrations accelerate.
Application:
Network hardening commands current budget priority while threat intelligence services capture disproportionate margin.
- Network Security:Segmentation, microsegmentation, and zero-trust overlay implementations for legacy command infrastructure. NATO allies are compressing procurement timelines following Russian cyberattacks on Ukrainian civilian-military networks, with Poland and Baltic states driving near-term demand spikes.
- Threat Intelligence:Adversary tracking, indicator sharing, and attribution services combining technical telemetry with human analyst tradecraft. Premium pricing reflects scarcity of Russian and Mandarin linguistics expertise alongside cleared security researchers.
- Data Protection:Backup, recovery, and resilience architectures for mission-critical systems.
- Risk Management:Continuous monitoring and compliance automation for contractor supply chains.
Legacy procurement dominates Data Protection. Threat Intelligence shows the steepest expansion trajectory as offensive cyber operations doctrine matures.
Deployment:
On-premises retains nuclear command-and-control mandate while cloud architectures gain provisional authorization traction.
- Cloud-based:IL6-accredited classified environments and C2S (Commercial Cloud Services) equivalents for intelligence community workloads. NSA's Commercial Solutions for Classified program is expanding vendor eligibility, with Microsoft, Amazon, and Google competing for accreditation.
- Managed Services:Security operations center outsourcing and continuous monitoring contracts displacing periodic compliance attestation. US Navy and Air Force program offices now demand real-time contractor scorecarding with 72-hour termination clauses for control degradation.
- On-premises:Air-gapped installations for nuclear command-and-control and isolated tactical systems.
- Hybrid:Architectures bridging classified and unclassified enclaves with cross-domain guards.
Regulatory-mandated deployment characterizes On-premises systems. Managed Services are gaining share fastest as defense agencies shift from capital to operational expenditure models.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Defense cybersecurity procurement concentrates near classified facility zones and national security innovation corridors. The United States anchors volume through Pentagon spending corridors. European allies accelerate parallel investments following NATO cyber defense directives.
United States
Pentagon service-level cyber components and US Cyber Command drive procurement of IL6-accredited cloud environments and cross-domain solutions. The CMMC 2.0 framework mandates tiered contractor compliance that disqualifies unprepared vendors from defense contracts. Northern Virginia's intelligence corridor hosts cleared facility concentrations where Booz Allen Hamilton and Northrop Grumman maintain proximity to NSA and CIA campuses.
United Kingdom
UK Strategic Command and GCHQ shape demand for sovereign cryptographic modules and Five Eyes interoperable systems. National Cyber Force operational requirements accelerate procurement of offensive cyber infrastructure hardened against persistent adversary probing. London and Cheltenham anchor vendor presence where BAE Systems and Thales Group maintain cyber divisions serving British intelligence services.
Germany
Bundeswehr Cyber and Information Domain Service compresses procurement timelines following Russian attacks on Ukrainian infrastructure. NATO STANAG 4774 compliance mandates drive encryption procurement with domestic classification authority requirements. Munich and Cologne host industrial cybersecurity clusters where Siemens and Rheinmetall adjacent vendors serve defense ministry contracts.
France
French Cyber Command and Direction Générale de la Sécurité Extérieure demand national cryptographic variants satisfying both NATO and domestic classification rules. European Defence Fund cyber clauses create certification pathways for transatlantic suppliers. Paris-Saclay and Toulouse defense aerospace corridors concentrate Thales Group and Dassault adjacent cybersecurity operations.
Australia
Australian Signals Directorate and Defence Cyber Command drive Five Eyes intelligence sharing protocol implementations. AUKUS technology transfer agreements accelerate demand for interoperable secure communications with US and UK counterparts. Canberra and Melbourne host cleared vendor operations where Australian subsidiaries of US primes anchor regional cyber service delivery.
Military Cybersecurity Market Competitive Environment
US primes anchor the top tier; European specialists hold adjacent positions in national procurement pools. Market structure concentrates around cleared facility infrastructure and existing intelligence community relationships that resist rapid competitive entry. Three archetypes dominate: classified facility operators leveraging air-gapped infrastructure, cleared workforce scale players, and commercial technology vendors seeking provisional authorizations. Consolidation through classified facility acquisitions and strategic partnerships with intelligence agencies represent the dominant competitive vectors.
Within the classified facility operator tier, Lockheed Martin Corporation and Northrop Grumman Corporation occupy positions sustained by prime contractor status across all CMMC maturity levels. Booz Allen Hamilton exemplifies the cleared workforce archetype through intelligence community relationships that competitors struggle to replicate. These three anchors represent the structural barriers—facility clearances, personnel security infrastructure, and agency proximity—that define competitive positioning in defense cybersecurity procurement.
| Leading Market Players |
|---|
| Lockheed Martin Corporation |
| Northrop Grumman Corporation |
| BAE Systems |
| Raytheon Technologies Corporation |
| Booz Allen Hamilton |
| General Dynamics Corporation |
| Thales Group |
| Cisco Systems, Inc. |
| IBM Corporation |
| Others |
Value Chain & Pricing Dynamics
Cleared analyst labor costs cascade through three distinct pricing tiers as defense contractors translate TS/SCI-cleared workforce scarcity into contract premiums. CMMC 2.0 certification timelines stretching to 24 months compress vendor pools and concentrate pricing power among accredited C3PAO-audited suppliers serving Pentagon procurement offices.
Pricing Analysis
Short lead-time premiums dominate contract negotiations as defense agencies compress procurement cycles following Russian cyberattacks on Ukrainian infrastructure. Three-tier pricing structure across premium, standard, and economy levels reflects CMMC maturity certification grade and cleared facility infrastructure access. Price differentiation centers on after-sales continuous monitoring capabilities versus periodic compliance attestation. Cost compression in mid-tier contractor services is intensifying because C3PAO audit bottlenecks extend vendor qualification timelines. Intelligence services exhibit lowest price sensitivity due to scarce Russian and Mandarin linguistics expertise, while defense industrial base suppliers face acute margin pressure from tiered compliance mandates.
Supply Chain Analysis
Freight logistics for classified hardware components face specialized handling requirements that restrict sourcing to domestic accredited facilities. Trusted foundry concentration in the United States, with limited qualified alternatives in the United Kingdom and Germany, constrains military-grade semiconductor availability. Raw material dependencies center on gallium nitride substrates, radiation-hardened processors, and sovereign cryptographic modules. Single-source vulnerability pervades TS/SCI-cleared personnel pipelines where DCSA processing backlogs limit vendor scaling. Distribution runs through prime contractor networks with direct agency relationships rather than open procurement channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Zero-trust architecture mandates are displacing perimeter-based security models across NATO defense ministries, creating a technology-transition phase where continuous verification platforms replace legacy signature-based detection systems.
For Market Incumbents: Anchor competitive position through classified facility infrastructure acquisitions that extend CMMC Level 5 certification coverage across all Pentagon service branches. Consolidate cleared workforce pipelines by partnering with DCSA on expedited security processing programs. Counter emerging cloud-native entrants by emphasizing air-gapped system integration capabilities that resist seamless overlay with modern architectures.
For New Entrants and Emerging Players: Systems integrators lacking prime contractor status represent the most accessible channel partner type for penetrating defense industrial base contractor ecosystems. Target European Defence Fund cyber clause procurement pathways where transatlantic certification reciprocity agreements remain incomplete. Focus go-to-market efforts on managed security services for mid-tier contractors facing 18-24 month C3PAO certification bottlenecks.
For Investors and Strategic Acquirers: Distressed-cycle entries favor mid-tier cybersecurity specialists with provisional IL6 cloud authorizations in the United Kingdom and Australia. Long-term viability hinges on Five Eyes intelligence sharing protocol alignment and sovereign cryptographic module development capabilities. Watch for NSA Commercial Solutions for Classified program accreditation expansions as inflection indicators for cloud-native vendor market entry.
| Strategic Initiative | Industry Significance |
|---|---|
| Classified Facility Acquisition | CMMC Level 5 certification coverage extends prime contractor eligibility across Pentagon cyber components. |
| Cleared Workforce Pipeline Investment | DCSA partnership programs reduce TS/SCI processing timelines for scarce analyst talent pools. |
| Cross-Domain Solution Development | Guard technology integration capabilities address intelligence community data movement requirements. |
| European Defence Fund Certification | EDF cyber clause compliance opens EU member state procurement channels for transatlantic suppliers. |
| AI-Augmented Threat Hunting Platform | Machine learning inference at tactical edge addresses analyst-to-alert ratio imbalances in security operations centers. |
Study Parameters
Multi-period observation of CMMC certification timelines, cleared facility accreditation expansions, and Pentagon procurement award patterns anchored the trend analysis, supplemented by interviews with defense agency cyber procurement officers, C3PAO audit organization executives, prime contractor security directors, and intelligence community technology adoption leads. Secondary validation drew from DoD budget justification documents, NSA Commercial Solutions for Classified program disclosures, NATO STANAG implementation directives, and European Defence Fund procurement guidelines. Bottom-up vendor revenue triangulation against top-down agency expenditure estimates ensured cross-verification of market sizing.
Input-output matrices mapped technology deployment rates across intrusion detection, encryption, and cloud-based segments against end-user security clearance requirements and operational tempo demands. Segmentation dimensions modeled included technology generation, user clearance tier, application criticality, and deployment architecture across the projection horizon. CAGRs were derived from regression analysis of historical procurement cycles and policy mandate acceleration effects. Forecast inputs incorporated C3PAO audit capacity constraints and Five Eyes intelligence sharing protocol adoption trajectories.
Several conditions sit outside the modeled scope, including classified program budget reclassifications, sudden shifts in allied certification reciprocity negotiations, and breakthrough developments in quantum-resistant cryptography rendering existing encryption procurement obsolete. Forecasts reflect documented assumptions regarding CMMC 2.0 implementation timelines and DCSA security clearance processing throughput. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Automotive Cyber Security Market
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Electronic Countermeasures Market
Defense Cybersecurity
Global Defense Tactical Radio Market
Defense Cybersecurity
Mine and IED Detection System Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Asia-Pacific Missiles and Missile Defense Systems Market
Defense Cybersecurity
Military Computers Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Anti-Drone Defense System Market
Defense Cybersecurity
Europe Cyber Weapons Market
Defense Cybersecurity
Electronic Warfare Market
Defense Cybersecurity
Aviation Cyber Security Market
Defense Cybersecurity
Europe Automotive Cybersecurity Market
Defense Cybersecurity
Blockchain Technology in Aerospace and Defense Market