
 Europe Automotive Cybersecurity Market | 2026-2036
Europe Automotive Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Automotive Cybersecurity Market Insights
Modular cybersecurity bundling is expanding across European OEM procurement frameworks, with tiered service packages replacing standalone software licenses. Continental AG leverages embedded security modules to anchor its position in hardware-integrated protection systems. Robert Bosch GmbH sustains R&D intensity across intrusion detection architectures for powertrain controllers. NXP Semiconductors dominates secure element manufacturing for vehicle-to-everything communication stacks.
Europe automotive cybersecurity encompasses hardware, software, and services engineered to protect electronic control units, in-vehicle networks, and external connectivity interfaces from unauthorized access, data exfiltration, and functional manipulation, with AES-256 encryption and hardware security modules serving as baseline technical specifications for ECU authentication protocols. The primary commercial purpose centers on ensuring functional safety integrity, preserving consumer privacy, and maintaining manufacturer liability shields across software-defined vehicle lifecycles. Endpoint protection solutions lead current revenue pools as OEMs prioritize ECU-level hardening, while cloud security architectures represent the fastest-expanding segment as over-the-air update frequencies multiply. Deployment models increasingly favor hybrid configurations that balance on-premises gateway control with cloud-based threat intelligence feeds.
The EU Cybersecurity Act establishes baseline certification schemes for connected vehicle components, while UNECE WP.29 R155 mandates type approval for cybersecurity management systems across all new vehicle categories sold in Europe. ESA and ENISA guidelines further shape technical standards for secure satellite navigation and fleet telematics infrastructure. Stakeholders must monitor evolving type-approval timelines and harmonize engineering roadmaps with delegated acts under the EU AI Act as automated driving functions deepen software dependency.
Market Dynamics
Software-defined vehicle architectures are compressing development cycles across European OEMs, forcing cybersecurity integration upstream into electronic control unit design phases rather than retrofitting post-production. Tier-1 suppliers now embed hardware security modules at silicon level to meet UNECE WP.29 R155 type-approval deadlines.
Growth Catalysts
- UNECE WP.29 R155:Mandatory cybersecurity management system certification for all new vehicle categories sold in Europe creates compliance-driven procurement volume across OEM supply chains.
- Connected fleet platforms:Commercial vehicle operators in Germany and France prioritize real-time intrusion detection to protect telematics data streams and remote diagnostic interfaces.
- Over-the-air update proliferation:Software-defined vehicle lifecycles multiply cloud security architecture deployments as automakers push firmware patches to powertrain and infotainment controllers.
Market Restraints
- Semiconductor supply concentration:Secure element manufacturing clusters in Taiwan and South Korea create single-source vulnerability for European ECU authentication hardware.
- Certification cost escalation:EU Cybersecurity Act evaluation schemes impose six-figure assessment fees on tier-2 component suppliers with limited R&D budgets.
- Legacy vehicle incompatibility:Pre-2021 vehicle fleets lack hardware security module slots, blocking retrofit cybersecurity service penetration in used-car channels.
Strategic Opportunities
- Poland and Czech Republic manufacturing corridors:Greenfield automotive electronics facilities in Central Europe seek localized cybersecurity engineering partnerships to serve Volkswagen Group and Stellantis supply chains.
- EU AI Act delegated acts:Automated driving function approval pathways create demand for AI-specific threat modeling and adversarial attack simulation services.
- Vehicle-to-grid integration:Bidirectional charging protocols for electric fleets in the Netherlands and Denmark require new authentication stacks at the energy-cybersecurity intersection.
Industry Challenges
- Embedded systems security engineering scarcity:European universities produce insufficient graduates with combined automotive electronics and cryptography expertise to staff tier-1 R&D centers.
- Multi-domain integration complexity:Powertrain, chassis, and infotainment ECUs run incompatible operating systems, fragmenting unified threat management deployment across vehicle networks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Automotive Cybersecurity Market |
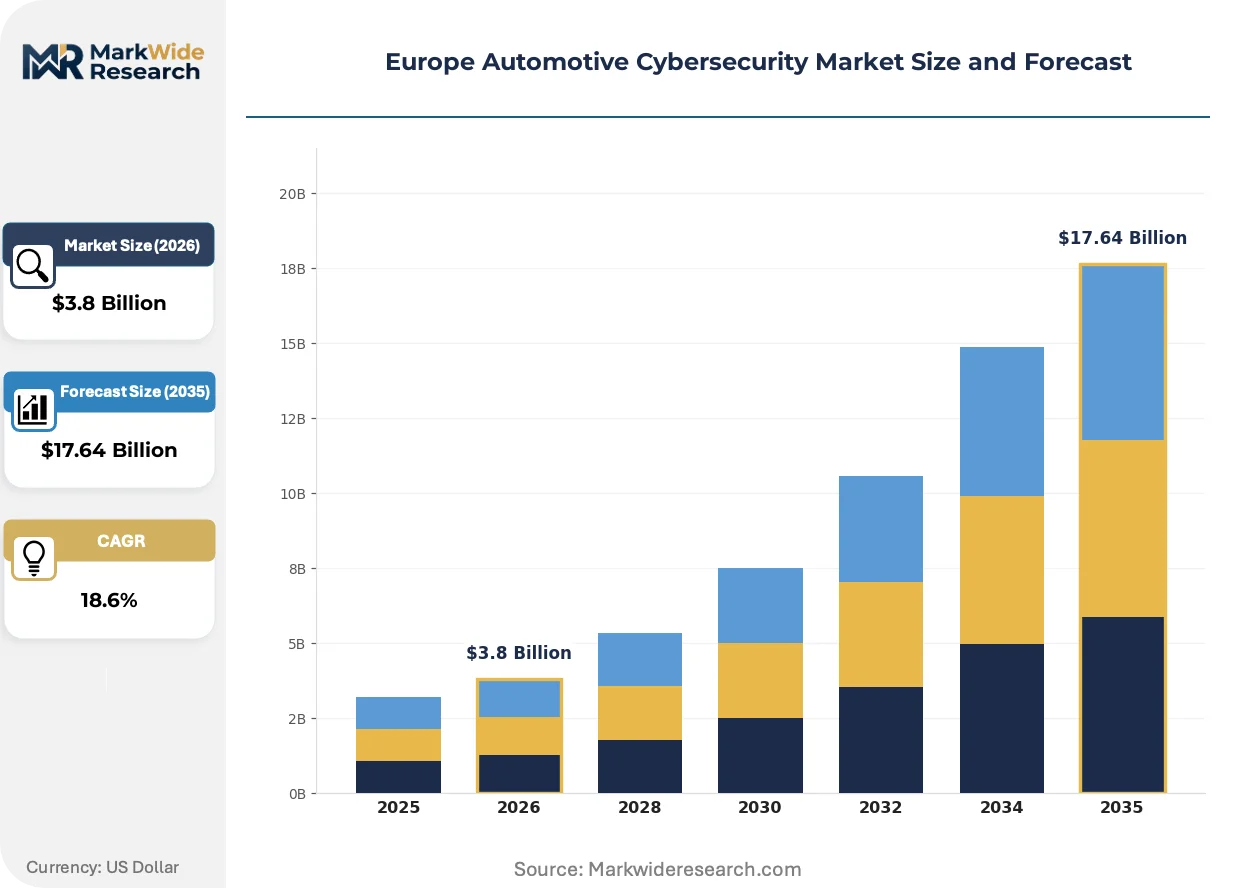
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.64 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Protection, Network Security, Application Security, Cloud Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: OEMs, Tier-1 Suppliers, Aftermarket Providers, Fleet Operators Technology: Intrusion Detection System, Antivirus Software, Encryption Solutions, Firewall |
| Companies Covered | Continental AG, Robert Bosch GmbH, NXP Semiconductors, Infineon Technologies AG, Vector Informatik GmbH, Aptiv PLC, Harman International, ESCRYPT GmbH, Denso Corporation, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Automotive Cybersecurity Market Trends and Innovations
Post-quantum cryptographic migration is accelerating across European automotive semiconductor roadmaps as NIST standardization timelines converge with long vehicle lifecycle security requirements. Suppliers now face dual-track engineering for classical and quantum-resistant implementations.
Hardware security modules with embedded AES-256 and ECC acceleration are overtaking software-only cryptographic implementations in gateway ECU designs. Continental AG and Robert Bosch GmbH procurement specifications now mandate HSM integration for all new platform wins. This shift is compressing margins for pure-play software cybersecurity vendors unable to certify at silicon level.
The EU Cybersecurity Act's Common Criteria certification schemes are reshaping supplier qualification workflows across German and French OEMs. Evaluation facilities in BSI-licensed German labs face 18-month backlogs, forcing component makers to front-load certification spending. Powertrain controller suppliers bear the heaviest burden as their products fall under mandatory high-assurance evaluation levels.
Fleet operators in the United Kingdom and Scandinavia now specify outcome-based cybersecurity service level agreements rather than perpetual software licenses. Subscription pricing for threat monitoring and incident response is displacing upfront capital expenditure models in commercial vehicle procurement. This behavioral shift concentrates revenue predictability with integrated platform vendors possessing 24/7 security operations center capabilities.
Europe Automotive Cybersecurity Market Segmentation
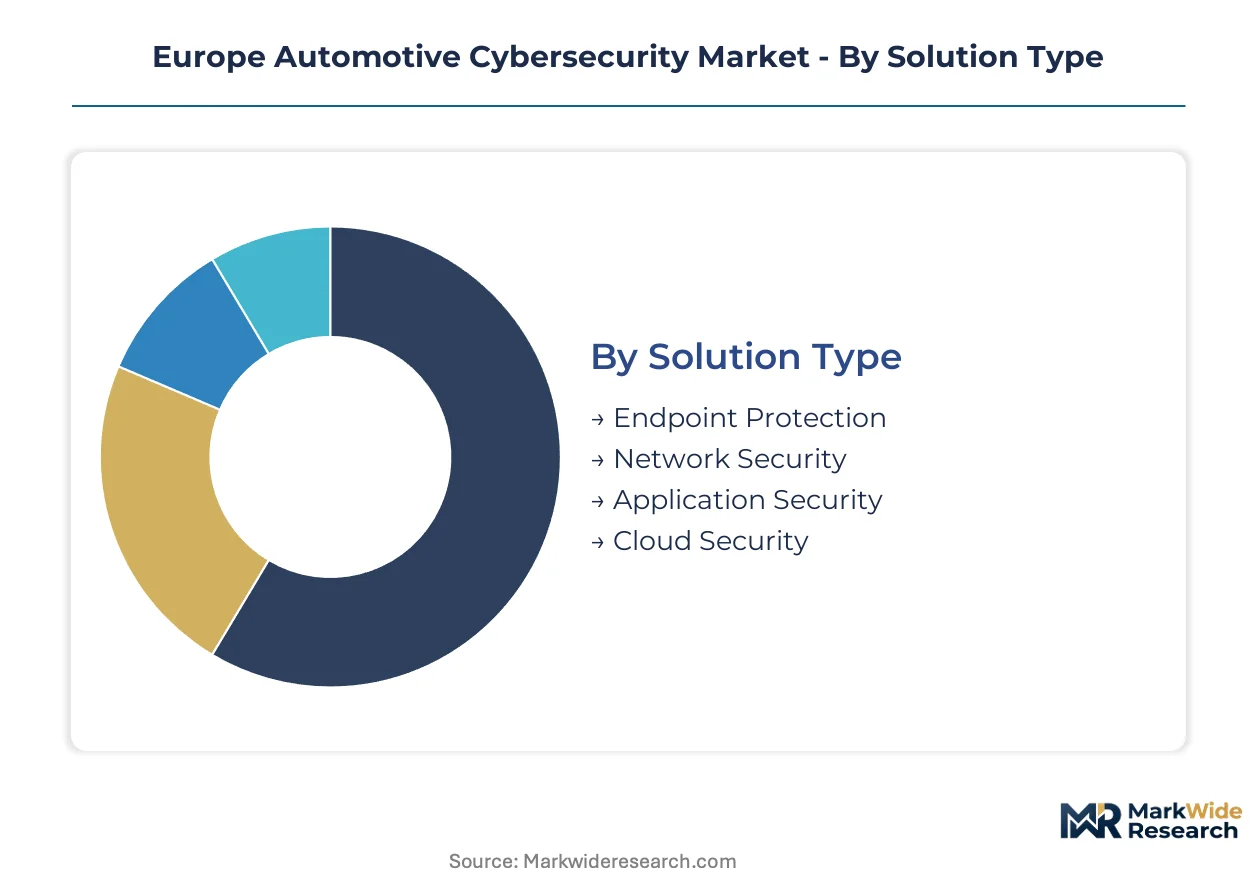
Segmentation in European automotive cybersecurity reveals divergent capital requirements across solution architectures. Hardware-integrated deployments demand silicon-level certification spending that software-only vendors cannot match. Procurement patterns increasingly favor bundled offerings that span multiple categories simultaneously.
Solution Type:
Capital intensity peaks in hardware-anchored segments requiring Common Criteria certification at component level.
- Endpoint Protection:Embedded security modules authenticate ECU communications through hardware security module integration. German and French OEM procurement specifications now mandate AES-256 encryption baseline for all new platform wins. Tier-1 suppliers embed these modules at silicon design phase to compress type-approval timelines.
- Cloud Security:Architectures securing over-the-air update channels and fleet telematics backbones scale through subscription pricing models. Demand concentrates among Scandinavian fleet operators specifying outcome-based service level agreements rather than perpetual licenses.
- Network Security:Gateway controllers with intrusion detection capabilities protect CAN-FD and Ethernet vehicle networks.
- Application Security:Runtime protection for infotainment and ADAS software stacks addresses code injection vulnerabilities.
Most installed capacity flows through Endpoint Protection. Expansion is steepest in Cloud Security.
Deployment Model:
Customer procurement sophistication determines deployment complexity, with hybrid configurations capturing mid-market transitions.
- Hybrid:Combines on-premises gateway control with cloud-based threat intelligence feeds, balancing latency requirements against update velocity. Volkswagen Group and Stellantis specify hybrid architectures for software-defined vehicle platforms.
- Managed Service:24/7 security operations center capabilities deliver threat monitoring and incident response under subscription contracts. United Kingdom commercial vehicle fleets drive adoption through outcome-based pricing acceptance.
- On-Premises:Air-gapped installations serve military and critical infrastructure vehicle applications with zero external connectivity.
- Cloud-Based:Pure cloud deployments suit telematics service providers managing multi-tenant fleet environments.
Hybrid deployments dominate current procurement volumes. Managed Service contracts are climbing the fastest as fleet operators outsource security operations.
End User:
Supply chain position dictates cybersecurity spending authority and technical specification control.
- OEMs:Volkswagen Group, BMW, and Mercedes-Benz aggregate procurement power to mandate hardware security module integration across tier-1 supply bases. Internal cybersecurity engineering teams now exceed 200 professionals at major German manufacturers.
- Fleet Operators:Commercial vehicle and logistics companies in the Netherlands and Denmark prioritize real-time intrusion detection for telematics data protection. Bidirectional charging authentication for electric fleets creates new procurement categories.
- Tier-1 Suppliers:Continental AG and Robert Bosch GmbH face certification cost escalation under EU Cybersecurity Act evaluation schemes.
- Aftermarket Providers:Retrofit cybersecurity services face hardware incompatibility barriers in pre-2021 vehicle fleets.
OEMs command the largest procurement budgets. Fleet Operators are expanding most quickly as subscription models penetrate commercial vehicle channels.
Technology:
Regulatory mandates reshape technology prioritization, with encryption solutions becoming non-negotiable baseline specifications.
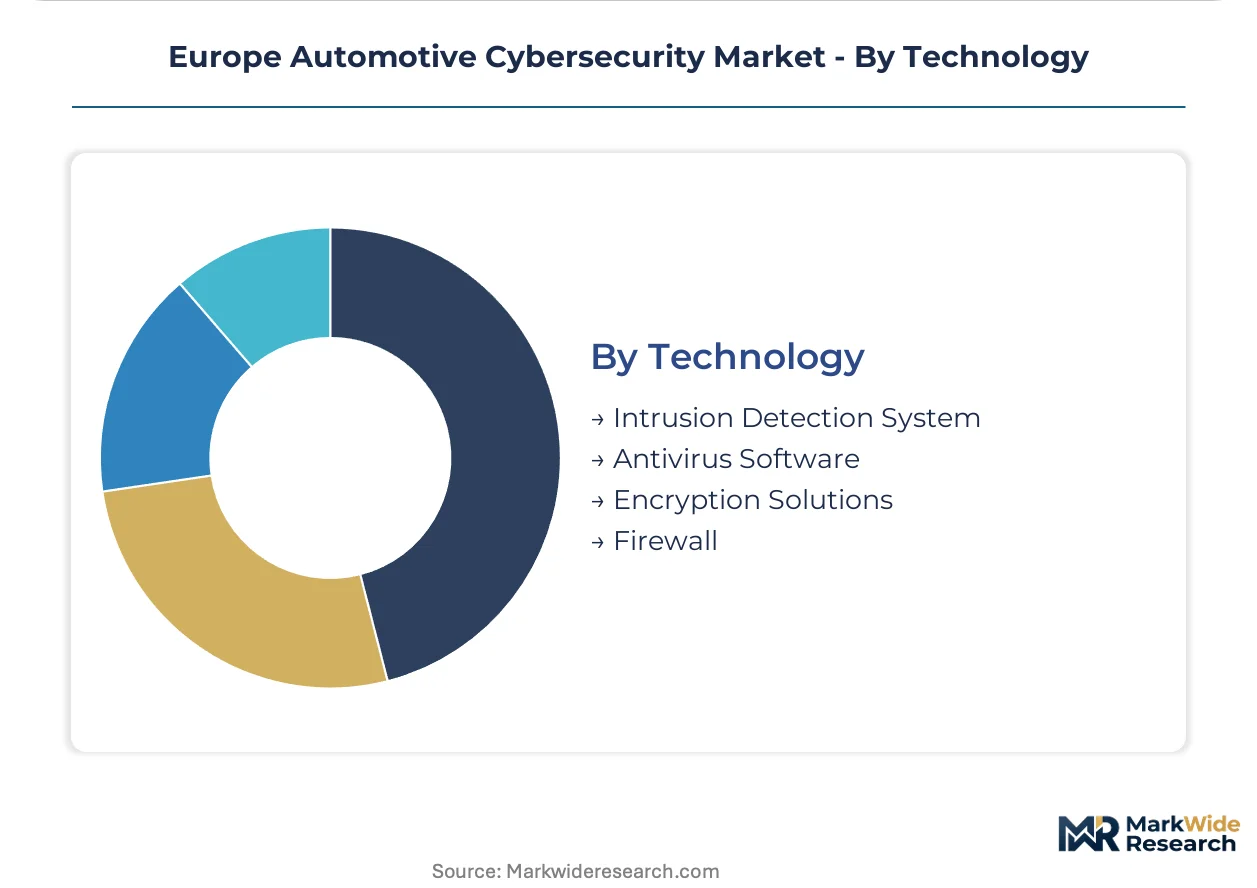
- Encryption Solutions:AES-256 and ECC acceleration in hardware security modules protect vehicle-to-everything communication stacks. NXP Semiconductors dominates secure element manufacturing for European OEM supply chains.
- Intrusion Detection System:Behavioral monitoring algorithms identify anomalous traffic patterns across CAN, LIN, and Ethernet networks. Powertrain controller suppliers embed these systems to meet UNECE WP.29 R155 requirements.
- Firewall:Perimeter controls segment infotainment domains from safety-critical vehicle networks.
- Antivirus Software:Signature and heuristic scanning protects infotainment operating systems from malware injection.
Encryption Solutions anchor baseline procurement specifications. Intrusion Detection Systems are gaining share fastest as behavioral analytics mature for automotive network architectures.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Automotive cybersecurity engineering originated in German industrial corridors during the 1990s ECU standardization era. The sector now distributes across Central and Western European manufacturing belts. Regulatory harmonization under UNECE WP.29 R155 accelerates cross-border procurement alignment.
Germany
Volkswagen Group and BMW procurement mandates drive hardware security module integration across tier-1 supply chains. KBA enforces type-approval deadlines under WP.29 R155 with BSI-licensed certification labs in Munich and Berlin facing 18-month evaluation backlogs. Stuttgart and Ingolstadt anchor Continental AG and Robert Bosch GmbH R&D centers for powertrain intrusion detection systems.
France
Stellantis software-defined vehicle platforms compress cybersecurity development cycles at silicon design phase. ANSM and CNIL guidelines shape data protection requirements for connected fleet telematics. Paris-Saclay and Grenoble clusters concentrate secure element engineering partnerships serving Renault and Peugeot supply bases.
United Kingdom
Commercial vehicle fleet operators specify outcome-based cybersecurity service level agreements displacing perpetual licenses. Department for Transport aligns domestic type-approval with UNECE frameworks post-Brexit transition. Milton Keynes and Coventry host managed security service centers for 24/7 threat monitoring contracts.
Netherlands
Bidirectional charging authentication for electric fleets creates procurement categories at the energy-cybersecurity intersection. RVO and TNO coordinate vehicle-to-grid security standards with Danish and German regulators. Eindhoven Brainport corridor attracts NXP Semiconductors secure element manufacturing for V2X communication stacks.
Poland
Greenfield automotive electronics facilities seek localized cybersecurity engineering partnerships to serve Volkswagen Group and Stellantis supply chains. Polish Investment and Trade Agency incentives target tier-2 component suppliers establishing Common Criteria certification capabilities. Wrocław and Katowice manufacturing zones attract embedded security module assembly operations.
Europe Automotive Cybersecurity Market Competitive Landscape
Premium-margin players sit above commodity-margin players across certification-grade segmentation, with hardware-integrated vendors commanding price premiums over software-only alternatives. The vendor base clusters into three tiers: semiconductor manufacturers with captive secure element production, tier-1 suppliers embedding security at ECU design phase, and pure-play software vendors facing margin compression. Dominant competitive moves include strategic partnerships for silicon-level integration and geographic expansion into Central European manufacturing corridors.
Within the semiconductor tier, NXP Semiconductors and Infineon Technologies AG occupy anchor positions for secure element supply. Among tier-1 system integrators, Continental AG and Robert Bosch GmbH exemplify hardware-embedded protection architectures. ESCRYPT GmbH represents the specialized cybersecurity engineering segment focused on automotive certification workflows.
| Leading Market Players |
|---|
| Continental AG |
| Robert Bosch GmbH |
| NXP Semiconductors |
| Infineon Technologies AG |
| Vector Informatik GmbH |
| Aptiv PLC |
| Harman International |
| ESCRYPT GmbH |
| Denso Corporation |
| Others |
Pricing and Supply Chain Analysis
EU Cybersecurity Act certification tiers gate qualified supply and premium-tier pricing access, as component vendors without BSI-licensed lab clearance cannot bid for German OEM platform wins. This regulatory filter compresses margins for uncertified software vendors while concentrating pricing power with semiconductor manufacturers possessing captive secure element production.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels segments the European automotive cybersecurity market by certification grade and hardware integration depth. Price differentiation rests on Common Criteria evaluation level and silicon-level HSM integration, with premium tiers commanding multiples over software-only alternatives. Cost compression in the standard tier is intensifying as tier-2 suppliers absorb six-figure certification fees. Fleet operators in the United Kingdom and Scandinavia show least price sensitivity due to outcome-based SLA acceptance, while aftermarket retrofit providers face acute buyer resistance from pre-2021 vehicle incompatibility.
Supply Chain Analysis
Dual-sourcing requirements from Volkswagen Group and Stellantis mandate multi-supplier qualification for secure element procurement, yet geographic supply concentration in Taiwan, South Korea, and the Netherlands limits true diversification. Raw material dependencies span silicon wafers, cryptographic co-processor IP, and automotive-grade packaging substrates. Single-source vulnerability persists for advanced node secure element manufacturing. Distribution runs through tier-1 system integrators embedding security modules at ECU design phase, with direct OEM contracting for high-assurance powertrain components.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Europe automotive cybersecurity functions as a stable compounder, with regulatory mandates under UNECE WP.29 R155 creating durable compliance-driven procurement volume across OEM supply chains.
For Market Incumbents: Cement silicon-level certification advantages by accelerating post-quantum cryptographic migration ahead of NIST standardization timelines. Prioritize backward integration into secure element manufacturing to defend against pure-play software vendors undercutting hardware-integrated pricing. Expand R&D headcount in Stuttgart and Grenoble clusters to address embedded systems security engineering scarcity threatening tier-1 delivery capacity. For New Entrants and Emerging Players: The mid-tier price-point gap between Continental AG premium offerings and uncertified economy software creates white-space for specialized intrusion detection vendors targeting Polish and Czech manufacturing corridors. Fleet operator managed services in the Netherlands and Denmark represent the most penetrable segment given subscription pricing acceptance. Pursue partnership-first go-to-market angles with greenfield automotive electronics facilities seeking localized cybersecurity engineering capabilities. For Investors and Strategic Acquirers: Roll-up economics work for specialized automotive cybersecurity engineering boutiques because certification backlog at BSI-licensed labs creates captive customer relationships resistant to switching. Five-to-ten year viability hinges on AI-specific threat modeling capabilities as EU AI Act delegated acts reshape automated driving approval pathways. Watch for inflection where tier-1 suppliers begin acquiring semiconductor packaging capabilities to secure HSM supply.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptographic Migration | NIST standardization timelines converge with long vehicle lifecycles, forcing dual-track engineering investments. |
| Silicon-Level Certification Investment | BSI-licensed lab partnerships compress type-approval timelines for German OEM platform competitions. |
| Central European Engineering Expansion | Polish and Czech manufacturing corridors attract localized cybersecurity partnerships serving Volkswagen Group supply chains. |
| Managed Security Service Buildout | 24/7 SOC capabilities capture outcome-based SLA demand from United Kingdom commercial vehicle fleets. |
| AI Threat Modeling Capability Acquisition | EU AI Act delegated acts create demand for adversarial attack simulation services in automated driving. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with OEM platform engineers, tier-1 supplier procurement leads, BSI-licensed certification lab directors, and fleet operator telematics managers. Secondary validation drew from UNECE WP.29 regulatory filings, ENISA automotive cybersecurity guidelines, vehicle production databases, and semiconductor customs records. Bottom-up segment sizing and top-down market triangulation cross-checked projections across hardware, software, and services categories.
Comparable-period anchoring linked the projection horizon to historical ECU shipment trajectories and cybersecurity content-per-vehicle trends across German, French, and United Kingdom manufacturing clusters. The analytical framework modeled segmentation across solution type, deployment model, end user, and technology dimensions, with vehicle propulsion architecture and software-defined vehicle platform generation as automotive-specific overlays. CAGRs were derived from regression analysis against regulatory mandate implementation timelines and fleet telematics penetration curves.
Caveats apply where semiconductor supply disruptions, certification lab capacity constraints, or legacy vehicle fleet turnover rates could materially shift the outlook. Forecasts reflect assumptions about UNECE WP.29 R155 enforcement consistency and EU AI Act delegated act timing. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Asia-Pacific Cyber Weapons Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Military Cybersecurity Market
Defense Cybersecurity
Aviation Cyber Security Market
Defense Cybersecurity
Military Sensors Cybersecurity Solutions Market
Defense Cybersecurity
Railway Cyber Security Market
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Military Computers Market
Defense Cybersecurity
Electronic Countermeasures Market
Defense Cybersecurity
Cyber Weapons Market
Defense Cybersecurity
Automotive Cybersecurity Service Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Vehicle Cybersecurity Market
Defense Cybersecurity
Europe Cyber Weapons Market
Defense Cybersecurity
Ballistics Targeting Software Market