
 Defence Cybersecurity Market | 2026-2036
Defence Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Defence Cybersecurity Market Insights
Zero-trust architecture is tilting defense procurement toward continuous verification models and away from perimeter-based security. Lockheed Martin Corporation leverages its classified systems integration heritage to anchor multi-domain command contracts. BAE Systems plc sustains transatlantic market presence through sovereign capability requirements in the United Kingdom and Australia. Northrop Grumman Corporation specializes in space-ground cyber resilience for satellite constellations.
Defence cybersecurity encompasses technologies, protocols, and operational frameworks engineered to protect military networks, weapons systems, and command infrastructure from unauthorized access, disruption, or exploitation, typically employing AES-256 encryption, cross-domain guards, and hardware roots of trust to maintain operational continuity under contested conditions. Network security solutions dominate procurement budgets due to legacy infrastructure hardening requirements across classified enclaves. Cloud security represents the fastest-expanding deployment category as militaries adopt hybrid architectures for non-sensitive workloads while retaining air-gapped systems for nuclear command and strategic assets. Identity and access management concentrates margin pools through biometric multi-factor authentication mandates for cleared personnel.
The United States Department of Defense enforces CMMC compliance through the Defense Industrial Base, while NATO's CCDCOE shapes collective cyber defense standards and response protocols for member nations. The EU NIS2 Directive tightens supply chain security obligations for defense contractors operating across European jurisdictions. Stakeholders must weigh sovereign data residency requirements against interoperability demands in coalition warfare environments.
Market Dynamics
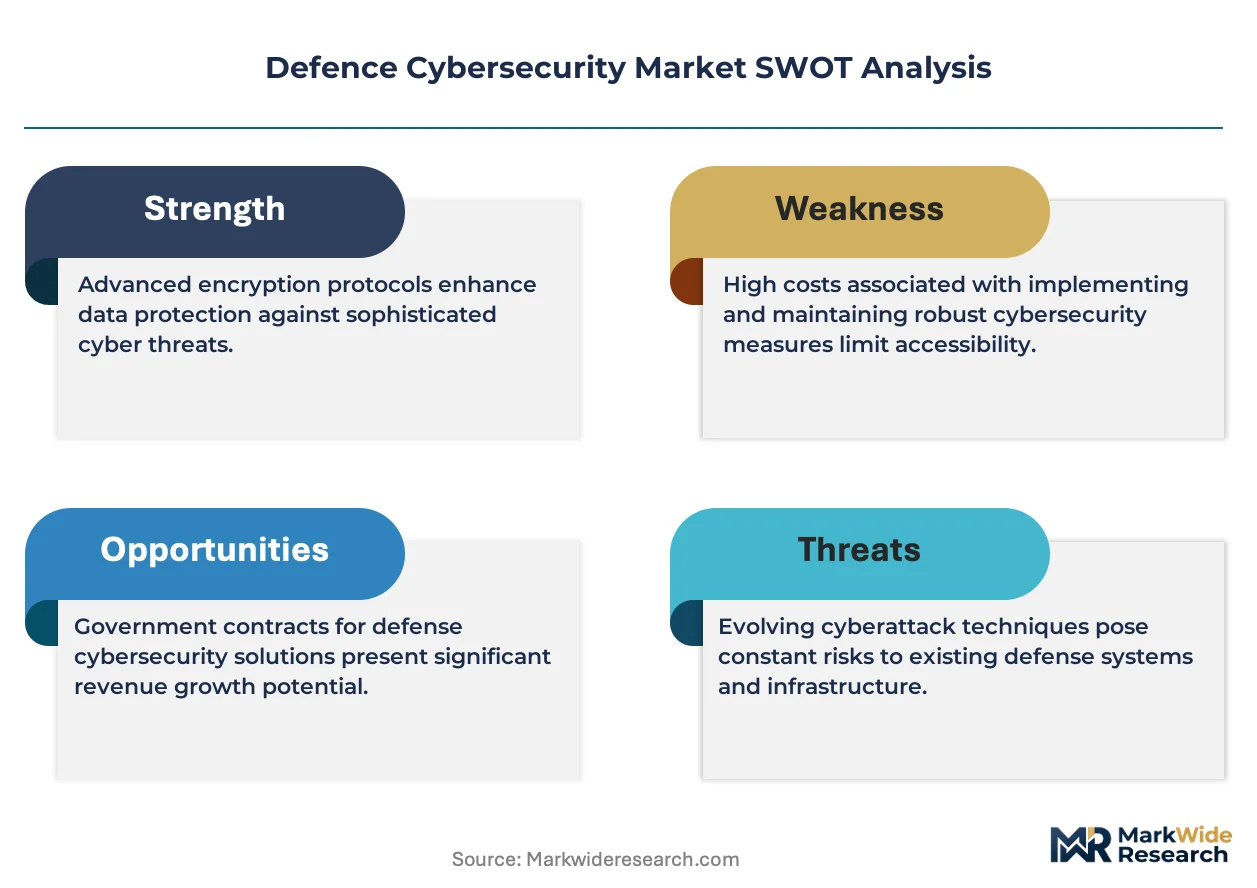
Zero-trust architecture mandates across NATO member states are dismantling perimeter-based security models and forcing defense contractors to re-engineer classified network infrastructure around continuous verification protocols.
Growth Catalysts
- CMMC 2.0 Mandates:The United States Department of Defense now requires tiered cybersecurity certification for all Defense Industrial Base contractors, creating immediate compliance-driven procurement across the supply chain.
- Space-Ground Convergence:Satellite constellation operators demand hardened cyber resilience for orbital assets, expanding addressable market beyond terrestrial military networks.
- Quantum-Resistant Cryptography:NIST post-quantum standards are accelerating hardware root-of-trust upgrades across nuclear command and strategic weapons systems.
Market Restraints
- Semiconductor Supply Concentration:Trusted foundry capacity for radiation-hardened chips concentrates in a single geography, creating single-point-of-failure risk for critical hardware components.
- Cross-Domain Integration Costs:Air-gapped legacy systems require expensive middleware development to interface with cloud-native security platforms, compressing contractor margins.
- Personnel Security Bottlenecks:TS/SCI clearance backlogs extend 18-24 months, constraining workforce scalability for classified program execution.
Strategic Opportunities
- Five Eyes Sovereign Cloud:Australia, Canada, and the United Kingdom are building domestic classified cloud infrastructure, opening procurement channels for alliance-certified vendors.
- AI-Driven Threat Hunting:Machine learning anomaly detection converges with behavioral biometrics to create autonomous security operations centers for forward-deployed units.
- NATO CCDCOE Procurement Harmonization:Standardized cyber defense frameworks across member nations enable modular platform sales with reduced country-specific customization.
Industry Challenges
- Zero-Trust Architecture Integration:Legacy perimeter-based systems in nuclear command infrastructure resist continuous verification without operational disruption.
- CMMC Certification Timeline Compression:Third-party assessment organization capacity constraints delay contractor compliance, threatening program eligibility.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Defence Cybersecurity Market |
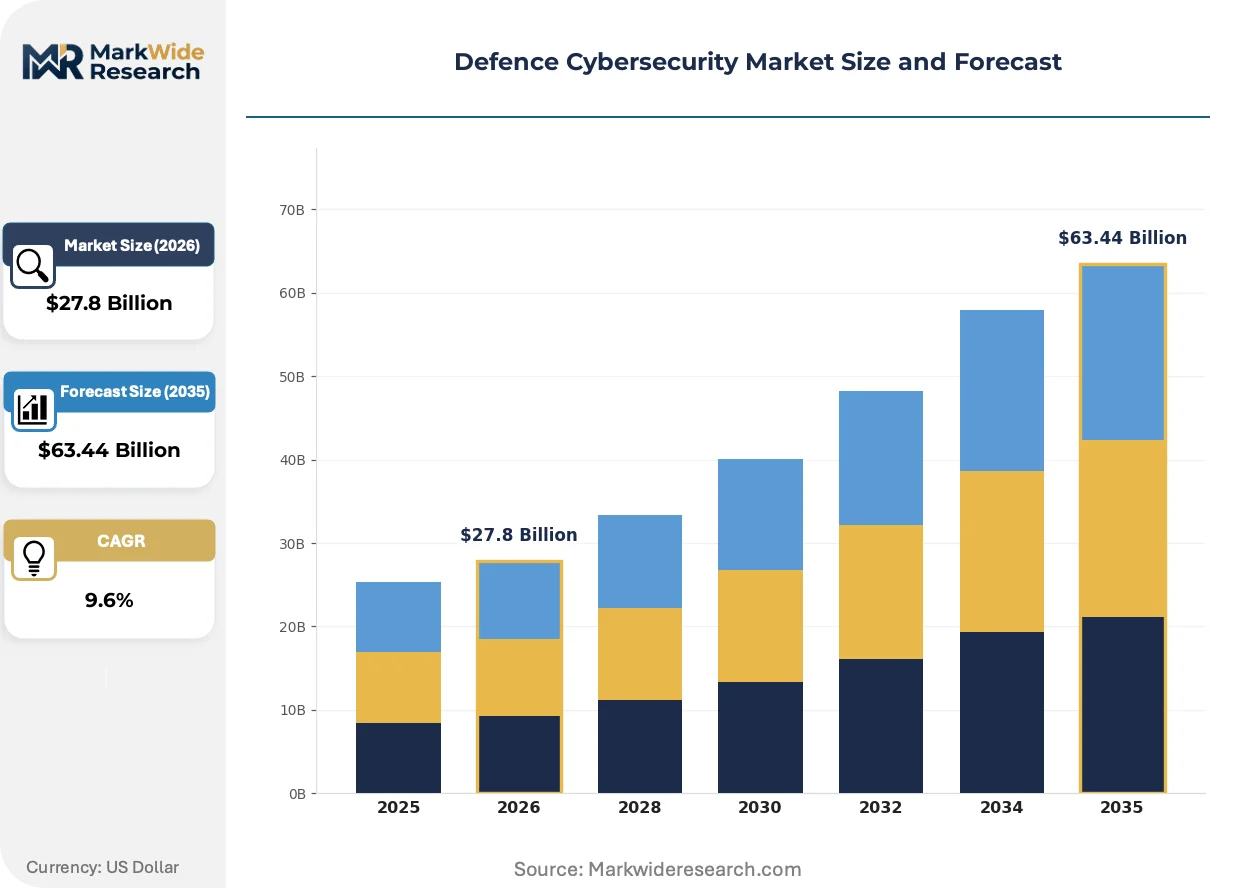
| Market Size in 2026 | $27.8 Billion |
| Market Size in 2035 | $63.44 Billion |
| CAGR (2026 – 2036) | 9.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Network Security, Endpoint Security, Application Security, Cloud Security, Identity & Access Management, Data Protection Deployment Model: On-Premises, Cloud-Based, Hybrid, Virtual Private Network, Air-Gapped Systems, Secure Enclaves Use Case: Threat Intelligence, Incident Response, Vulnerability Management, Risk Assessment, Cryptography, Security Compliance End User: Military Branches, Defense Contractors, Intelligence Agencies, National Security Operations, Cyber Defense Units, Space Command |
| Companies Covered | Lockheed Martin Corporation, BAE Systems plc, Northrop Grumman Corporation, General Dynamics Corporation, Thales Group, Raytheon Technologies Corporation, Booz Allen Hamilton, Leidos Holdings Inc., L3Harris Technologies Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Defence Cybersecurity Market Trends and Innovations
Defense cybersecurity is pivoting from reactive threat response to predictive resilience architecture, with artificial intelligence and quantum-safe protocols redefining operational requirements across classified and coalition networks.
Homomorphic encryption is digitizing secure computation on encrypted data without decryption, enabling intelligence agencies to share threat analytics across allied networks while preserving source protection. NATO's CCDCOE is piloting federated learning architectures that train models on distributed classified datasets without centralizing sensitive information. This capability is compressing the classification barrier that historically fragmented coalition cyber defense.
The EU NIS2 Directive is mandating 24-hour incident reporting timelines for defense-critical entities and imposing supply chain security obligations on contractors operating across European jurisdictions. Member states are transposing these requirements into national military procurement regulations, forcing non-EU vendors to establish EU-based security operations centers. French and German defense ministries are now requiring NIS2-equivalent certification as a gate for classified contract eligibility.
Military buyers are consolidating vendor relationships around platform-level cybersecurity subscriptions rather than point-product acquisitions, compressing the traditional multi-vendor security stack. United States Space Command and Cyber Command are leading this shift through enterprise licensing agreements that bundle endpoint detection, network monitoring, and identity management under single-contractor accountability. This concentration is visible across Five Eyes nations where sovereign capability requirements still mandate domestic prime contractors but subsystem integration increasingly flows through managed security service providers.
Defence Cybersecurity Market Segmentation
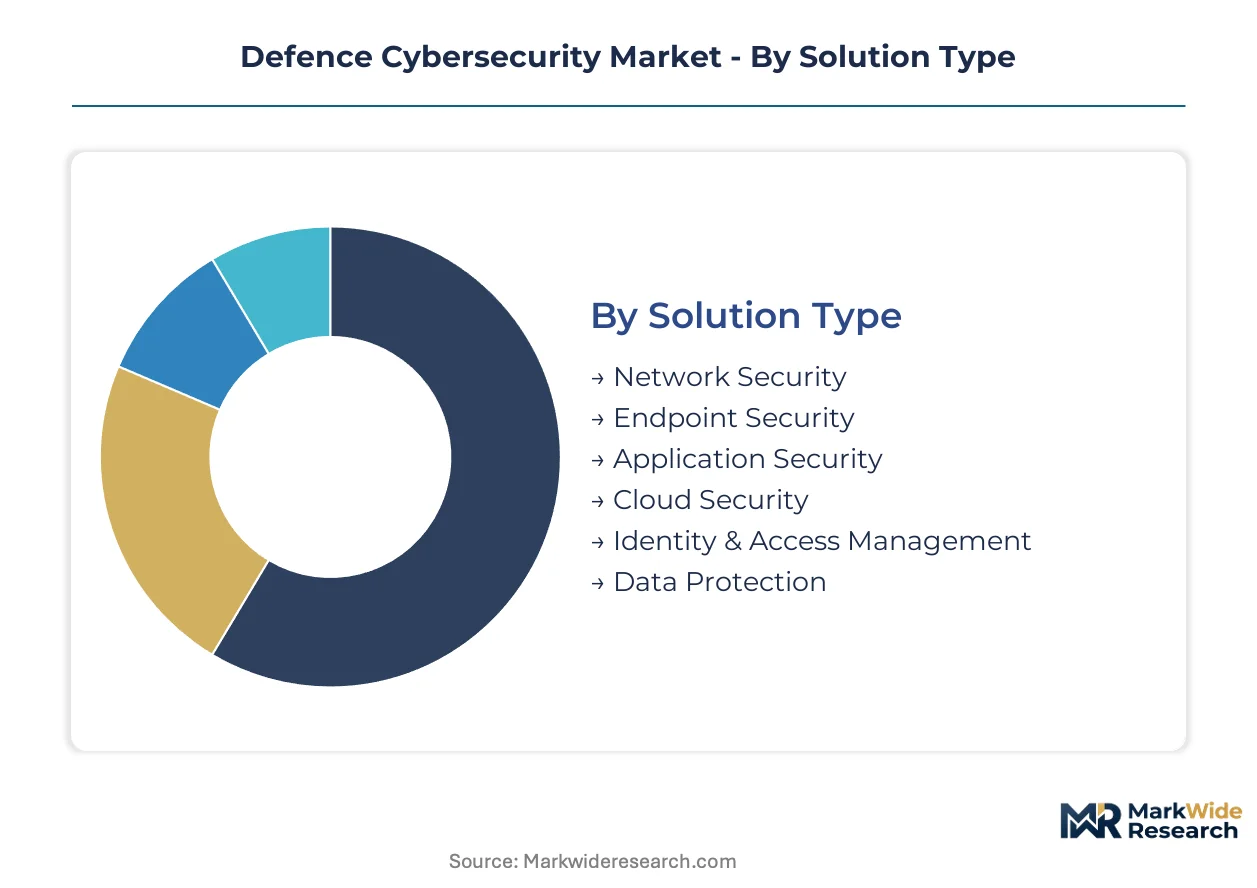
Defense cybersecurity procurement fragments across solution architectures, deployment topologies, operational missions, and classified user communities. Each segmentation axis reflects distinct compliance mandates, threat models, and sovereign capability requirements that reshape vendor positioning.
Solution Type:
Mature perimeter defenses coexist with emerging zero-trust platforms across military procurement budgets, creating tiered investment patterns.
- Network Security:Firewalls, intrusion detection systems, and cross-domain guards protect classified enclaves through hardware-enforced isolation. United States Space Command drives next-generation procurement for satellite-to-ground link hardening against jamming and spoofing attacks.
- Cloud Security:Hybrid architectures for non-sensitive workloads demand encryption key management, container security, and sovereign data residency controls. Five Eyes nations are building domestic classified cloud infrastructure, opening procurement channels for alliance-certified vendors.
- Endpoint Security:Hardened device protection for tactical field units employs hardware roots of trust and behavioral monitoring.
- Application Security:Secure software development pipelines and runtime protection for mission-critical weapons systems.
- Identity & Access Management:Biometric multi-factor authentication and privileged access management for cleared personnel.
- Data Protection:Encryption, data loss prevention, and secure destruction protocols for classified information handling.
Network Security retains volume leadership; Cloud Security holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates legacy infrastructure hardening from greenfield cloud-native investments across defense budgets.
- On-Premises:Traditional data center deployments maintain air-gapped environments for nuclear command and strategic weapons systems. Legacy perimeter-based infrastructure resists continuous verification without operational disruption.
- Air-Gapped Systems:Physically isolated networks for highest classification levels require specialized cross-domain guards and manual data transfer protocols. Semiconductor supply concentration for radiation-hardened components creates single-point-of-failure risk.
- Cloud-Based:Multi-tenant and dedicated cloud instances for non-sensitive military workloads with FedRAMP or equivalent certification.
- Hybrid:Integrated on-premises and cloud architectures enabling workload portability across classification levels.
- Virtual Private Network:Encrypted tunnels for remote access and coalition partner interoperability.
- Secure Enclaves:Hardware-isolated execution environments for sensitive computation on shared infrastructure.
On-Premises dominates current installed base; Air-Gapped Systems command premium pricing tiers.
Use Case:
Application maturity varies from established compliance workflows to experimental AI-driven threat hunting across defense operations.
- Threat Intelligence:Federated learning architectures train models on distributed classified datasets without centralizing sensitive information. NATO's CCDCOE pilots compress the classification barrier that historically fragmented coalition cyber defense.
- Incident Response:Automated containment and forensic preservation for advanced persistent threat campaigns. The EU NIS2 Directive mandates 24-hour reporting timelines for defense-critical entities.
- Vulnerability Management:Continuous attack surface monitoring and patch orchestration for weapons systems.
- Risk Assessment:Quantified cyber risk scoring for acquisition and operational decisions.
- Cryptography:NIST post-quantum standards accelerate hardware root-of-trust upgrades across strategic assets.
- Security Compliance:CMMC certification workflows and audit automation for Defense Industrial Base contractors.
Threat Intelligence captures R&D investment focus; Incident Response faces regulatory acceleration.
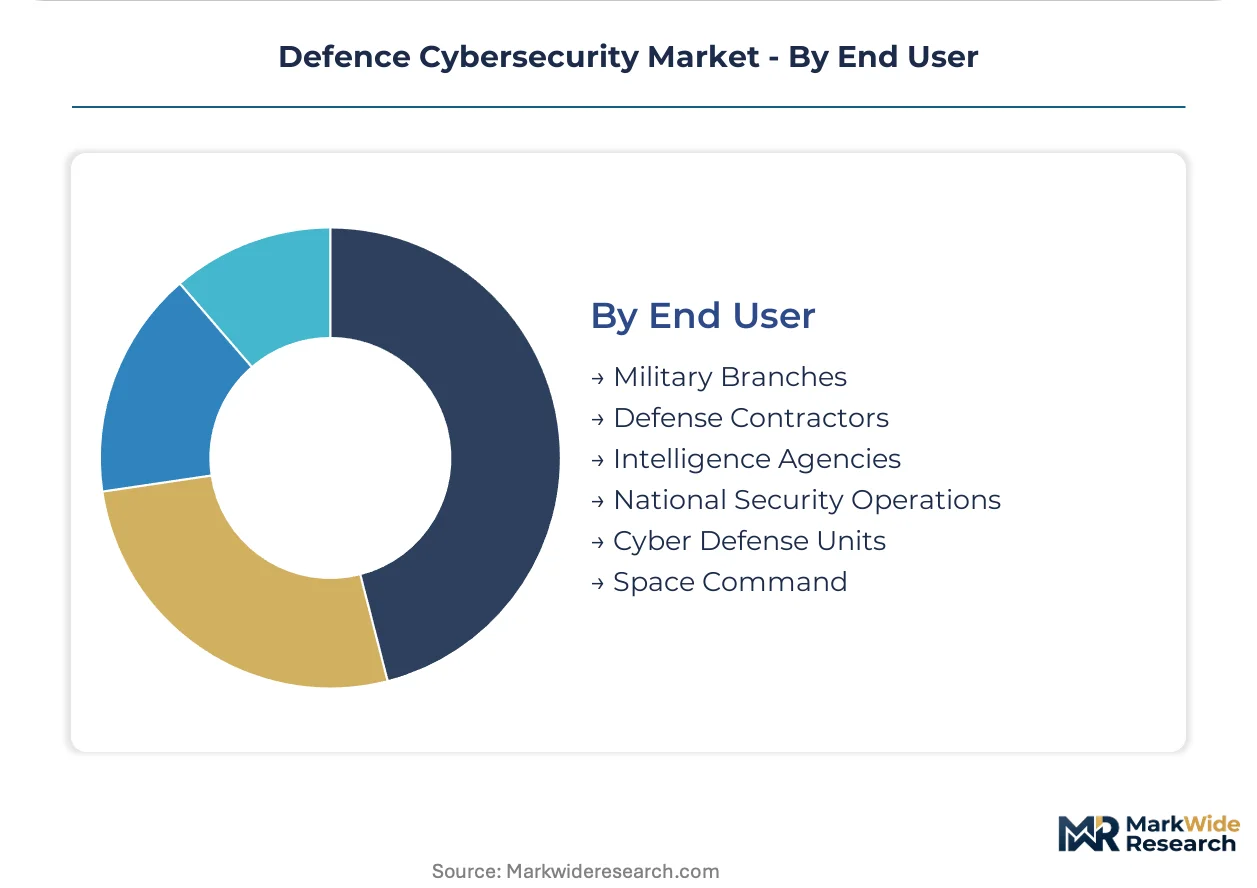
End User:
Customer type segmentation separates sovereign capability requirements from coalition interoperability demands.
- Military Branches:Service-specific cyber commands procure zero-trust architectures for tactical and strategic networks. United States Cyber Command consolidates vendor relationships around platform-level subscriptions.
- Defense Contractors:CMMC 2.0 mandates create immediate compliance-driven procurement across the supply chain. Third-party assessment organization capacity constraints delay contractor certification.
- Intelligence Agencies:Signals intelligence and counterintelligence operations demand specialized tools with enhanced source protection.
- National Security Operations:Cross-agency coordination centers for critical infrastructure protection.
- Cyber Defense Units:Specialized military formations for offensive and defensive cyber operations.
- Space Command:Orbital asset protection and ground segment resilience for satellite constellations.
Military Branches anchor procurement volume; Space Command generates the fastest capability investment.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States defense contractors export cyber resilience architectures to NATO allies and Five Eyes partners, establishing transatlantic procurement corridors for classified network infrastructure. This trade pattern concentrates advanced capability development in North American industrial clusters while European and Asia-Pacific nations build sovereign alternatives.
United States
Space Command and Cyber Command drive procurement for satellite-to-ground link hardening and zero-trust architectures for tactical networks. CMMC 2.0 mandates from the Department of Defense enforce tiered cybersecurity certification across the Defense Industrial Base supply chain. The National Capital Region anchors classified systems integration, with Virginia and Maryland hosting prime contractor facilities for multi-domain command contracts.
United Kingdom
Sovereign capability requirements mandate domestic prime contractors for sensitive military networks while permitting subsystem integration through managed security service providers. The National Cyber Security Centre shapes procurement standards for defense-critical entities alongside NATO CCDCOE alignment. London and the South East concentrate cyber defense R&D, with BAE Systems maintaining transatlantic market presence through UK-Australia capability partnerships.
Germany
The Federal Office for Information Security enforces supply chain security obligations on defense contractors operating across European jurisdictions. NIS2-equivalent certification now gates classified contract eligibility for non-EU vendors seeking Bundeswehr procurement channels. Munich and Bavaria host industrial cybersecurity clusters developing hardware roots of trust for strategic weapons systems.
Australia
Domestic classified cloud infrastructure construction opens procurement channels for alliance-certified vendors under Five Eyes sovereign cloud initiatives. The Australian Signals Directorate mandates enhanced incident reporting timelines for defense-critical entities mirroring EU NIS2 Directive structures. Canberra anchors cyber defense policy coordination while Sydney and Melbourne develop sovereign capability for tactical network protection.
France
The National Agency for Information Security imposes 24-hour incident reporting requirements on defense contractors operating across European jurisdictions. Direction Générale de l'Armement procurement regulations now require NIS2-equivalent certification as a gate for classified contract eligibility. Paris and the Île-de-France region concentrate aerospace-defense cybersecurity integration for satellite constellation protection.
Defence Cybersecurity Market Competitive Landscape
Channel-controlling players compete with product-specialist players across tiered procurement hierarchies shaped by sovereign capability mandates and coalition interoperability requirements. Prime contractors anchor multi-domain command contracts through classified systems integration heritage, while subsystem specialists capture margin pools in biometric authentication and hardware root-of-trust components. Two strategic archetypes dominate: vertically integrated defense primes with security clearance infrastructure, and boutique cyber specialists with AI-driven threat hunting capabilities. Competitive moves concentrate on strategic partnerships for cross-domain middleware development and portfolio diversification into quantum-resistant cryptography.
Among US-based defense primes, Lockheed Martin Corporation and Northrop Grumman Corporation exemplify the vertically integrated archetype, anchoring classified network infrastructure procurement through established security clearance ecosystems. BAE Systems plc represents the transatlantic positioning archetype, sustaining market presence through sovereign capability requirements in multiple Five Eyes jurisdictions. These three occupy positions where prime contractor accountability for platform-level cybersecurity subscriptions compresses traditional multi-vendor security stacks.
| Leading Market Players |
|---|
| Lockheed Martin Corporation |
| BAE Systems plc |
| Northrop Grumman Corporation |
| General Dynamics Corporation |
| Thales Group |
| Raytheon Technologies Corporation |
| Booz Allen Hamilton |
| Leidos Holdings Inc. |
| L3Harris Technologies Inc. |
| Others |
Pricing and Supply Chain Analysis
The Trans-Pacific fiber-optic cable corridor carries encrypted defense data flows between Five Eyes nations, with bandwidth cost dynamics amplifying pricing power for radiation-hardened semiconductor foundries while compressing margins for cloud-native security platform vendors serving coalition interoperability mandates.
Pricing Analysis
Perimeter-based security platforms command legacy premiums against zero-trust architectures and experimental quantum-resistant cryptography tiers. Subscription-based platform licensing dominates procurement, with price differentiation anchored in CMMC certification grade and sovereign data residency controls. Cost compression in unclassified cloud security tiers is intensifying because hyperscaler competition commoditizes baseline encryption services. Defense contractors with cleared personnel pipelines exhibit lowest price sensitivity; subsystem integrators without security clearance infrastructure face acute margin pressure.
Supply Chain Analysis
Extended payment terms from prime contractors to radiation-hardened chip suppliers stretch 90-120 days, with supply-chain finance facilities concentrated among TSMC, GlobalFoundries, and BAE Systems. Trusted foundry capacity for strategic-grade semiconductors rests on Taiwan, the United States, and the United Kingdom. Gallium nitride substrates, sapphire wafers, and hardware security modules constitute critical input dependencies. Single-source vulnerability for radiation-hardened ASICs creates chokepoint exposure. Distribution runs through Defense Logistics Agency-managed procurement channels and NATO CCDCOE-certified vendor pools.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Defense cybersecurity is entering a cyclical upswing driven by CMMC 2.0 compliance deadlines forcing accelerated procurement across the Defense Industrial Base supply chain.
For Market Incumbents: Harden classified systems integration franchises by accelerating cross-domain middleware development for air-gapped legacy infrastructure. Deepen backward integration into hardware root-of-trust components to capture margin pools from biometric authentication mandates. Lockheed Martin and Northrop Grumman must defend against boutique AI-driven threat hunting specialists encroaching on platform-level subscriptions. For New Entrants and Emerging Players: Build out sovereign cloud infrastructure partnerships in Australia, Canada, and the United Kingdom where Five Eyes certification requirements create procurement gates for non-alliance vendors. Target Space Command satellite-to-ground link hardening as the most penetrable segment, with federated learning architectures offering coalition interoperability without clearance infrastructure. Pursue managed security service provider positioning as the primary go-to-market angle. For Investors and Strategic Acquirers: Carve-out targets emerge from conglomerate defense primes seeking to divest non-core cyber units lacking platform-scale subscription revenue. Long-term viability favors vendors with clearance infrastructure and quantum-resistant cryptography roadmaps. Boutique specialists with NIST post-quantum certification progress represent prime acquisition archetypes. Watch CMMC third-party assessment organization capacity expansion as the inflection signal for supply chain compliance velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Migration | Continuous verification protocols displace perimeter-based security across NATO classified networks. |
| Quantum-Resistant Cryptography Certification | NIST post-quantum standards accelerate hardware upgrades for nuclear command systems. |
| Sovereign Cloud Infrastructure Buildout | Five Eyes nations construct domestic classified clouds, opening alliance-certified vendor channels. |
| CMMC Compliance Automation | Third-party assessment bottlenecks create procurement delays threatening contractor program eligibility. |
| Federated Learning Deployment | NATO CCDCOE pilots compress classification barriers fragmenting coalition cyber defense coordination. |
Research Methodology
The analysis maps network security, cloud security, endpoint protection, and identity management sub-sectors, each validated through cyber command procurement officers, Defense Industrial Base compliance directors, cleared systems integrators, and NATO CCDCOE policy specialists. Primary intelligence combines structured interviews with secondary validation against SEC 10-K filings, DoD budget justification documents, EU NIS2 transposition notices, and Five Eyes defense procurement databases. Bottom-up vendor revenue triangulation against top-down national defense cyber spending estimates anchors market sizing.
Fixed assumptions include sustained CMMC 2.0 enforcement intensity, continued NATO collective defense commitment, and stable Five Eyes intelligence sharing frameworks across the projection horizon. Segmentation models capture solution type, deployment topology, operational mission, and end-user classification level. CAGRs derive from weighted scenario analysis across compliance-driven, threat-driven, and technology-replacement demand vectors. Quantum computing threat timelines and satellite constellation deployment rates constitute defense-specific forecast inputs.
The forecast holds incumbent behavior within observed patterns; aggressive platform consolidation moves by hyperscale cloud providers or accelerated sovereign capability mandates from EU member states would shift outcomes. Macroeconomic defense budget contraction, CMMC enforcement relaxation, or breakthrough quantum decryption capabilities would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Maritime Cybersecurity Market
Defense Cybersecurity
Asia-Pacific Cyber Weapons Market
Defense Cybersecurity
Cyber Weapons Market
Defense Cybersecurity
Vehicle Cybersecurity Market
Defense Cybersecurity
Europe Cyber Weapons Market
Defense Cybersecurity
Ballistics Targeting Software Market
Defense Cybersecurity
Automotive Cyber Security Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Mine and IED Detection System Market
Defense Cybersecurity
Automotive Cybersecurity Service Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Military Cybersecurity Market
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Military Sensors Cybersecurity Solutions Market
Defense Cybersecurity
Aviation Cyber Security Market