
 Automotive Cyber Security Market | 2026-2036
Automotive Cyber Security Market Size, Share, and Industry Trends Forecast 2026-2036
Automotive Cyber Security Market Analysis
Silicon carbide is shifting into powertrain inverters, altering thermal and electromagnetic profiles that security architectures must protect. Robert Bosch GmbH leverages its Tier-1 scale to embed hardware security modules across multiple OEM platforms. NXP Semiconductors anchors its position through automotive-grade secure element portfolios purpose-built for ECU authentication. ESCRYPT specializes in embedded encryption stacks that harden vehicle-to-everything communication channels.
Automotive cyber security encompasses hardware, software, and service layers designed to protect vehicle electronic architectures from unauthorized access, data exfiltration, and remote manipulation across powertrain, infotainment, and advanced driver-assistance domains. The discipline relies on cryptographic protocols operating at sub-millisecond latencies, secure boot chains verified through hardware root-of-trust modules, and intrusion detection systems monitoring Controller Area Network and Ethernet backbones. Software and solutions segments command the dominant share as over-the-air update pipelines and remote diagnostics expand attack surfaces requiring continuous patching. Hardware security modules represent the fastest-growing category as OEMs integrate dedicated cryptographic processors directly into domain controllers rather than relying on general-purpose computing resources.
UNECE R155 and ISO/SAE 21434 establish mandatory cybersecurity management systems and risk assessment frameworks for vehicle type approval across European and aligned markets. NHTSA guidance in the United States shapes voluntary but influential security benchmarks that liability-conscious OEMs treat as de facto compliance thresholds. Stakeholders must monitor how regional divergence between binding European mandates and American guidance-based approaches reshapes supplier certification burdens and market access requirements.
Market Dynamics
Automotive cyber security dynamics pivot on UNECE R155's mandatory cybersecurity management system requirements, which force OEMs to re-architect vehicle development cycles and supplier qualification protocols across European and aligned export markets.
Growth Catalysts
- UNECE R155 Mandate:European vehicle type approval now requires demonstrable cybersecurity management systems, compelling OEMs to harden electronic architectures before market entry.
- Silicon Carbide Inverter Proliferation:Powertrain electrification through SiC-based inverters generates new electromagnetic attack surfaces requiring specialized shielding and cryptographic monitoring.
- Over-the-Air Update Pipelines:Remote software delivery infrastructure at connected vehicle fleets expands recurring security service contracts and continuous vulnerability management demand.
Market Restraints
- Hardware Security Module Cost Structure:Dedicated cryptographic processors add bill-of-materials burden that compresses margin at volume vehicle segments.
- Tier-1 Supplier Concentration:Bosch, Continental, and Denso control critical ECU integration channels, limiting security vendor direct access to OEM specification processes.
- Latency Constraints:Sub-millisecond cryptographic verification requirements in ADAS domains restrict algorithmic complexity and certification pathways.
Strategic Opportunities
- Indian Market Underpenetration:Domestic OEMs and joint ventures lag European cybersecurity maturity, creating first-mover advantage for compliance-ready solution providers.
- Vehicle-to-Grid Integration:Bidirectional charging infrastructure creates new authentication and encryption requirements at residential and commercial energy interfaces.
- ISO/SAE 21434 Alignment:Risk assessment framework standardization enables security vendors to productize assessment tools and recurring audit services.
Industry Challenges
- Functional Safety-Cybersecurity Integration:ISO 26262 and ISO/SAE 21434 parallel compliance demands engineers fluent in both hazard analysis and threat modeling disciplines.
- Legacy Fleet Retrofit Complexity:Pre-2024 vehicle architectures lack hardware root-of-trust modules, complicating aftermarket security upgrades and insurance liability.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Automotive Cyber Security Market |
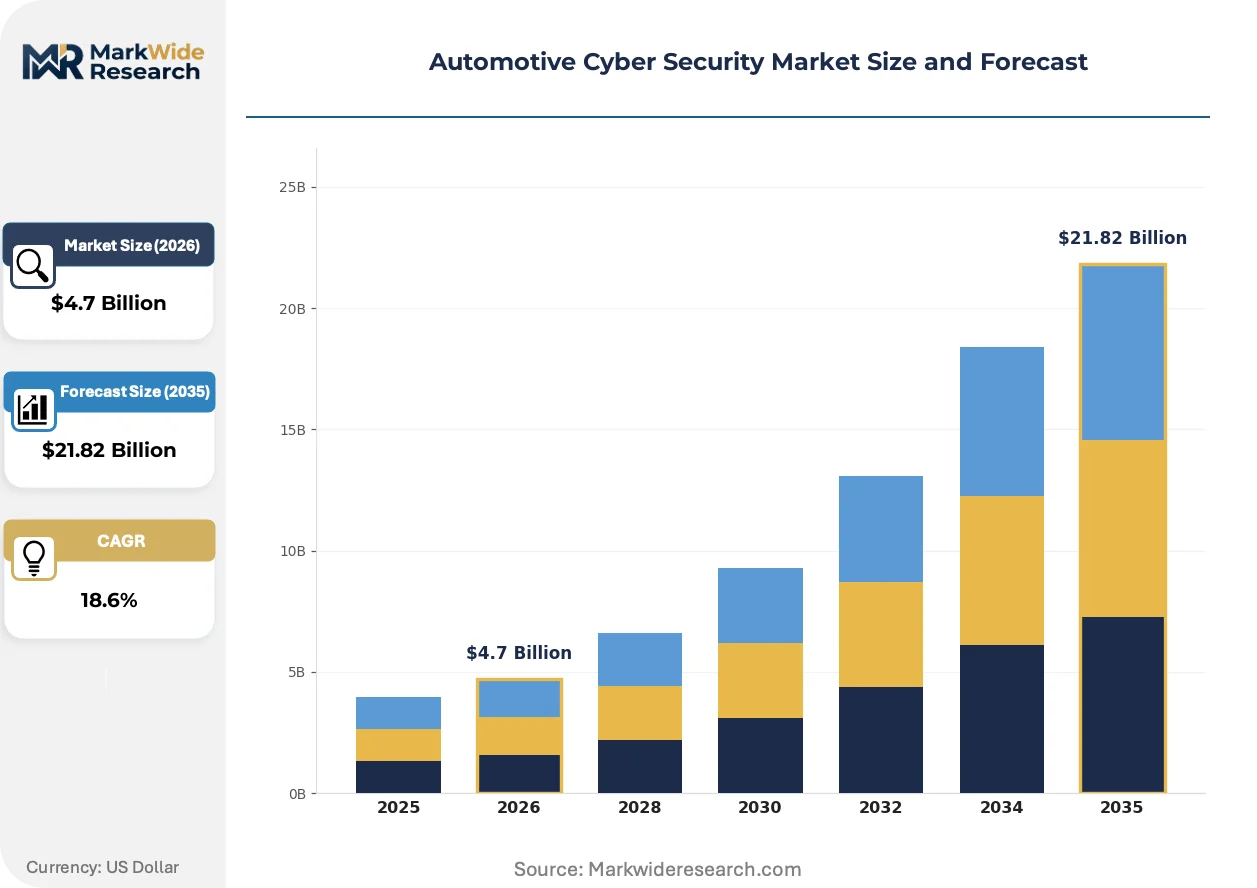
| Market Size in 2026 | $4.7 Billion |
| Market Size in 2035 | $21.82 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Hardware, Software, Services, Solutions Threat Type: Malware, Phishing, Denial of Service, Ransomware End User: OEMs, Tier-1 Suppliers, Aftermarket Providers, Fleet Operators Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Service |
| Companies Covered | Continental AG, Robert Bosch GmbH, Harman International, DENSO Corporation, Aptiv, NXP Semiconductors, Infineon Technologies AG, Argus Cyber Security, ESCRYPT, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Automotive Cyber Security Market Emerging Trajectories
Automotive cyber security innovation clusters around three vectors: hardware-rooted trust architectures displacing software-only protection, regulatory frameworks forcing cross-border compliance harmonization, and procurement models shifting from perpetual licenses toward continuous security service subscriptions.
Hardware security modules are converging with domain controller silicon to embed cryptographic acceleration directly adjacent to powertrain and ADAS compute. Tier-1 suppliers at Germany and Japan electronics clusters now specify HSM-integrated SoCs for new platform launches. This convergence compresses attack windows by eliminating bus-exposed key material.
UNECE R155 and ISO/SAE 21434 are tightening vehicle type approval requirements across European and aligned markets. OEMs must now submit cybersecurity management system documentation before regulatory approval. Powertrain and ADAS domain controllers face the steepest compliance burden as these systems carry highest safety integrity levels.
Fleet operators now contract security as a managed service rather than purchasing perpetual software licenses. Automotive OEMs and mobility providers in the United States and Germany are consolidating vendor relationships around continuous monitoring and incident response retainers. This shift concentrates procurement volume with vendors demonstrating 24/7 security operations center capabilities.
Automotive Cyber Security Market Segmentation
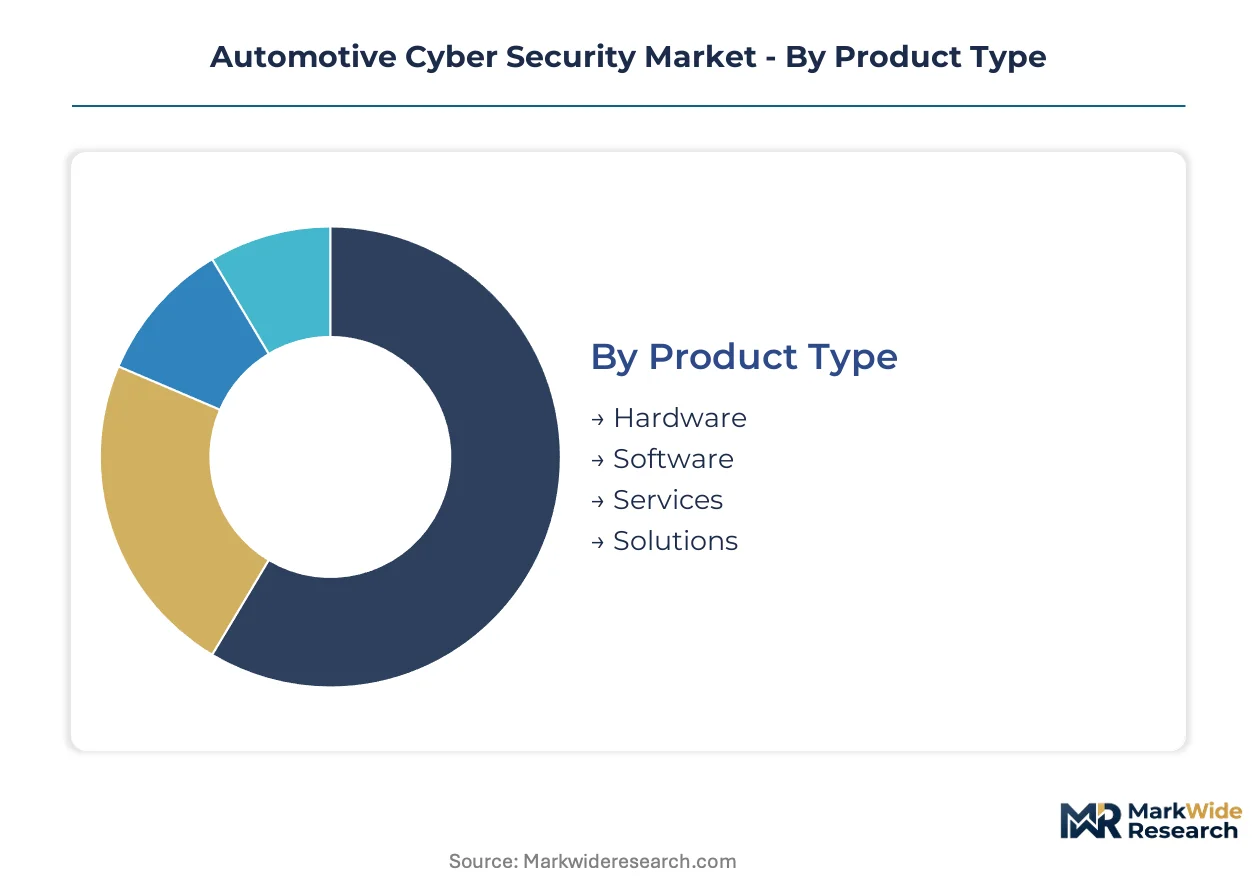
Automotive cyber security procurement patterns diverge sharply across product architectures, threat vectors, and deployment models. Suppliers must align offerings with UNECE R155 compliance timelines and the specific integration constraints of Tier-1 electronic clusters.
Product Type:
Supply concentration in hardware security modules and embedded software stacks determines how vendors capture value across OEM platform generations.
- Hardware:Dedicated cryptographic processors, secure elements, and hardware security modules provide tamper-resistant key storage and acceleration. Demand clusters at German and Japanese electronics manufacturing hubs where Bosch, Continental, and Denso specify HSM-integrated domain controllers for powertrain and ADAS platforms facing UNECE R155 certification deadlines.
- Software:Embedded encryption libraries, intrusion detection systems, and secure boot chain implementations operate across ECU fleets. Procurement concentrates among OEMs building over-the-air update pipelines requiring continuous vulnerability patching without hardware retrofits.
- Services:Penetration testing, threat intelligence feeds, and incident response retainers.
- Solutions:Integrated hardware-software bundles with managed security operations.
Software absorbs the bulk of installed capacity; hardware is expanding most quickly as OEMs embed dedicated cryptographic silicon into new domain controller architectures.
Threat Type:
Cost tier differentiation separates commodity signature-based detection from premium behavioral analytics targeting zero-day exploitation.
- Malware:Code injection and payload execution targeting infotainment and telematics units. Demand concentrates in connected vehicle fleets where USB and wireless vectors expose high-value data exfiltration opportunities at German and US OEMs.
- Ransomware:Encryption of critical vehicle systems or backend infrastructure for extortion. Procurement accelerates among fleet operators managing thousands of vehicles where operational downtime costs dwarf ransom payments.
- Phishing:Credential harvesting targeting OEM supplier networks and diagnostic tool access.
- Denial of Service:Network flooding attacks against vehicle-to-everything communication channels.
Malware defenses command the largest installed base; ransomware protection is climbing the fastest as fleet operators quantify operational risk exposure.
End User:
Application maturity varies from OEM captive development through aftermarket retrofit complexity.
- OEMs:Vehicle manufacturers integrating security from platform conception through UNECE R155 type approval. Procurement concentrates at Volkswagen Group, Toyota, and Ford where cybersecurity management system documentation precedes regulatory submission.
- Tier-1 Suppliers:Bosch, Continental, Denso, and Magna embedding security into domain controllers before OEM handoff. Demand clusters at electronics manufacturing clusters in Stuttgart, Tokyo, and Detroit where specification control limits direct vendor access.
- Fleet Operators:Mobility providers and logistics companies contracting managed security monitoring.
- Aftermarket Providers:Third-party retrofitters addressing pre-2024 vehicle architectures lacking hardware root-of-trust.
Tier-1 suppliers absorb the bulk of component-level procurement; fleet operators are gaining share fastest through subscription-based security service models.
Deployment Model:
Customer type segmentation separates perpetual license holders from continuous service subscribers.
- Cloud-Based:Centralized threat intelligence platforms and over-the-air update orchestration delivered via secure cloud infrastructure. Demand concentrates at US-based mobility providers and connected fleet operators requiring elastic compute for machine learning-powered anomaly detection.
- Managed Service:24/7 security operations center monitoring with guaranteed response times. Procurement accelerates among German OEMs consolidating vendor relationships around incident response retainers rather than point solution purchases.
- On-Premise:Air-gapped security infrastructure for sensitive development and testing environments.
- Hybrid:Split architectures combining edge-based detection with cloud analytics.
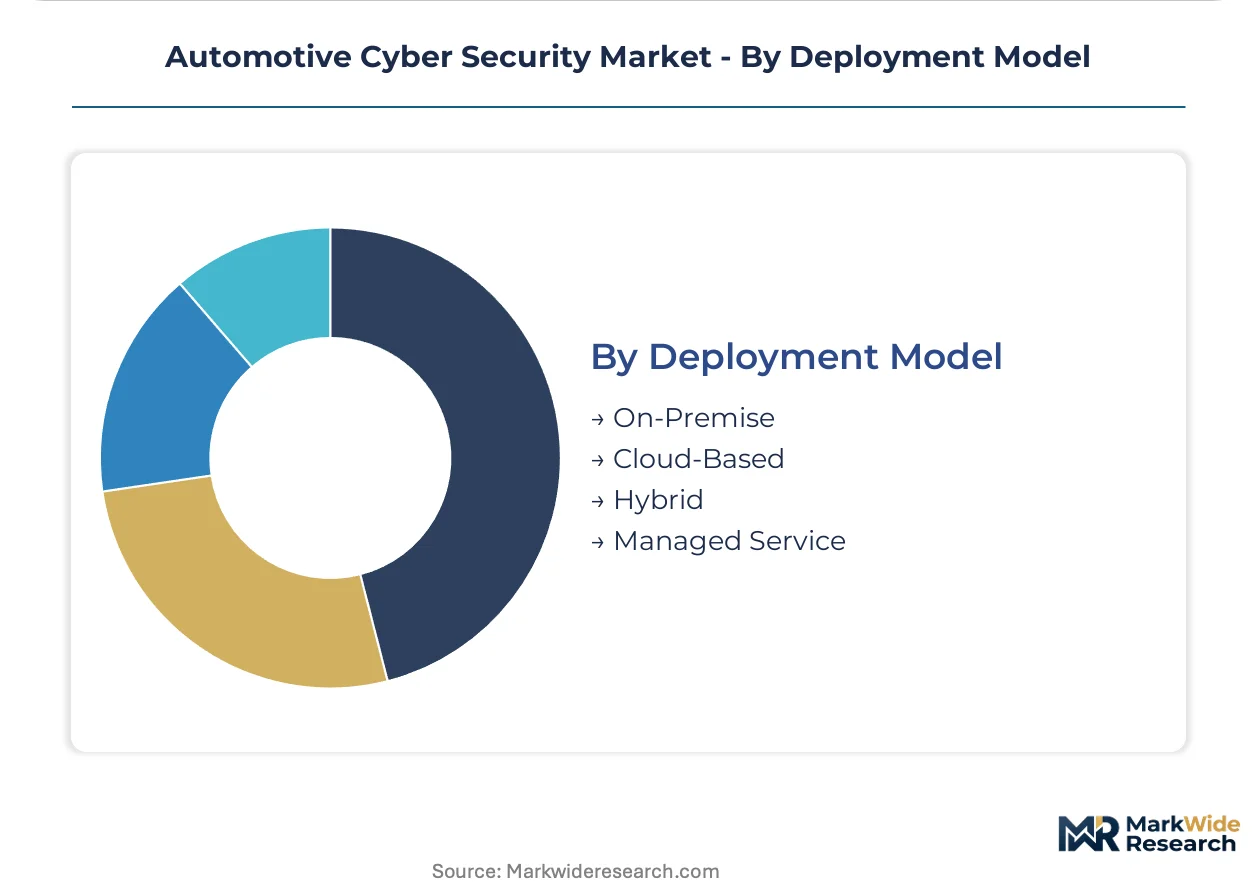
Cloud-based deployment holds the largest active footprint; managed services are expanding most quickly as procurement shifts from capital expenditure to operational expenditure models.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Germany, Japan, and the United States concentrate procurement volume where automotive electronics manufacturing clusters intersect with stringent regulatory mandates.
Germany
Stuttgart and Munich electronics corridors drive hardware security module integration into domain controllers. UNECE R155 mandates cybersecurity management system documentation before KBA type approval. Bosch and Continental specification control channels security procurement through Tier-1 supplier networks concentrated in Baden-Württemberg and Bavaria.
United States
Detroit OEM captive development and Silicon Valley mobility providers expand cloud-based security service contracts. NHTSA guidance shapes voluntary but liability-influential security benchmarks. Michigan and California clusters diverge: legacy automakers harden powertrain architectures while Bay Area fleet operators prioritize over-the-air update pipeline protection.
Japan
Toyota City and Nagoya electronics manufacturing anchor ECU authentication demand across keiretsu supplier hierarchies. METI alignment with UNECE R155 accelerates domestic cybersecurity management system adoption. Denso specification control limits direct vendor access to OEM platforms concentrated in Aichi Prefecture.
China
Shanghai and Shenzhen EV manufacturers embed hardware security modules into battery management and autonomous driving systems. MIIT cybersecurity standards for connected vehicles mandate cryptographic protocols at sub-millisecond latencies. Yangtze River Delta and Pearl River Delta electronics clusters concentrate domestic secure element foundry capacity.
India
Maharashtra and Tamil Nadu automotive joint ventures lag European cybersecurity maturity, creating compliance-ready solution gaps. BIS standards alignment with ISO/SAE 21434 remains partial. Chennai and Pune manufacturing corridors attract first-mover security vendors targeting pre-certification platform development.
Automotive Cyber Security Market Vendor Landscape
Strategic partnerships dominate the current landscape as Tier-1 suppliers consolidate security vendor relationships around continuous monitoring capabilities. The market structures into three tiers: semiconductor specialists providing hardware root-of-trust, embedded software vendors hardening communication channels, and managed service providers operating security operations centers. Competitive moves cluster on technology licensing for cryptographic acceleration and portfolio diversification into vehicle-to-everything protection.
Within the semiconductor archetype, NXP Semiconductors and Infineon Technologies AG occupy positions anchoring automotive-grade secure element supply. Among Tier-1 integrators, Robert Bosch GmbH exemplifies specification control that channels security procurement across multiple OEM platforms. ESCRYPT represents the embedded encryption specialist tier, sitting within portfolios focused on vehicle-to-everything communication hardening.
| Leading Market Players |
|---|
| Continental AG |
| Robert Bosch GmbH |
| Harman International |
| DENSO Corporation |
| Aptiv |
| NXP Semiconductors |
| Infineon Technologies AG |
| Argus Cyber Security |
| ESCRYPT |
| Others |
Supply Flow & Price Mechanics
Certification-grade divergence between UNECE R155-compliant hardware security modules and legacy software-only protection manifests in both procurement premiums and supplier qualification bottlenecks. OEMs face tiered cost structures where automotive-grade secure elements command substantial bill-of-materials premiums over general-purpose cryptographic implementations, compressing margins at volume vehicle segments while concentrating supply relationships with qualified Tier-1 integrators.
Pricing Analysis
Volume-scale fleet operators negotiate subscription-based security service contracts with SaaS-tiered pricing structures, while individual OEM platform development commands project-based licensing fees. Price differentiation rests on ISO/SAE 21434 certification tier and hardware root-of-trust integration depth. Cost compression in economy vehicle segments is intensifying because dedicated cryptographic processors add per-unit burden that Tier-1 suppliers struggle to absorb. Aftermarket retrofit providers exhibit highest price sensitivity due to legacy fleet hardware constraints; premium EV platforms show lowest sensitivity given safety-critical ADAS content requirements.
Supply Chain Analysis
UNECE R155 qualification gating restricts hardware security module supply to certified foundries concentrated in Germany, Japan, and Taiwan. Automotive-grade secure element production draws from silicon carbide substrate suppliers, AEC-Q100 qualified packaging facilities, and cryptographic IP licensors. Single-source vulnerability persists at advanced node semiconductor fabrication where automotive security silicon competes with consumer electronics capacity allocation. Distribution runs through Bosch, Continental, and Denso specification channels that limit direct vendor access to OEM platform engineering teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Automotive cyber security functions as a cost-of-compliance market where UNECE R155 vehicle type approval creates a regulatory moat favoring pre-certified solution providers. The mandatory cybersecurity management system documentation requirement erects barrier-to-entry thresholds that compliant vendors exploit for pricing power and procurement consolidation.
For Market Incumbents: Cement specification control at German and Japanese Tier-1 electronics clusters through deeper integration into domain controller silicon roadmaps. Prioritize cryptographic acceleration IP licensing to fend off emerging semiconductor specialists threatening hardware security module margin structures. Channel consolidation around continuous security service subscriptions reinforces recurring revenue streams against point-solution commoditization. For New Entrants and Emerging Players: The premium-to-economy pricing gap in Indian domestic OEM joint ventures offers white-space penetration before BIS standards achieve full ISO/SAE 21434 alignment. Target fleet operator managed service contracts in US mobility corridors where procurement is shifting from capital expenditure to operational expenditure models. Pursue vehicle-to-grid integration authentication as a specialist beachhead before incumbent energy-sector players extend automotive security capabilities. For Investors and Strategic Acquirers: Re-rating potential sits with embedded encryption software specialists given fleet operator subscription revenue inflection. Long-term viability over a five-to-ten year horizon favors vendors demonstrating 24/7 security operations center capabilities and cross-OEM platform portability. Acquisition target archetypes include ISO/SAE 21434 assessment tool providers with recurring audit service pipelines. The signal to watch is Tier-1 supplier consolidation of vendor relationships around continuous monitoring retainers rather than perpetual license purchases.| Strategic Initiative | Industry Significance |
|---|---|
| Hardware Security Module Integration | Embedding cryptographic processors into domain controllers eliminates bus-exposed key material at Bosch and Continental platforms. |
| Continuous Security Service Subscriptions | Fleet operators in Germany and the United States consolidate procurement around 24/7 security operations center retainers. |
| ISO/SAE 21434 Assessment Tool Productization | Standardized risk assessment frameworks enable recurring audit revenue streams from OEM compliance documentation requirements. |
| Vehicle-to-Grid Authentication Development | Bidirectional charging infrastructure at residential and commercial interfaces creates new cryptographic protocol demand. |
| Indian Market Pre-Certification Positioning | Domestic OEM joint ventures in Maharashtra and Tamil Nadu lag European cybersecurity maturity, creating first-mover advantage. |
Methodological Framework
Independent corroboration across OEM platform engineering directors, Tier-1 supplier procurement leads, automotive semiconductor product managers, and fleet operator cybersecurity officers underwrites the qualitative findings. Primary interviews with stakeholders at Stuttgart, Tokyo, and Detroit electronics manufacturing clusters combined with secondary validation from UNECE regulatory filings, NHTSA guidance documents, vehicle production databases, and IHS Markit registration data. Bottom-up segment sizing triangulates against top-down market value estimates.
Comparable-period anchoring to historical cybersecurity procurement patterns across connected vehicle fleet rollouts informs the projection horizon modeling. Segmentation dimensions include hardware-software-services product architecture, threat vector type, end-user category from OEM through aftermarket, and deployment model from cloud through managed service. CAGRs derive from installed base expansion rates and content-per-vehicle trajectory analysis. Forecast inputs incorporate UNECE R155 compliance timeline phasing and silicon carbide inverter proliferation electromagnetic shielding requirements.
Underlying measurement precision varies by segment; hardware security module procurement at German Tier-1 suppliers carries tighter precision than aftermarket retrofit demand estimation. Forecasts reflect documented assumptions regarding regulatory alignment timelines and OEM platform launch schedules. Specific risk factors that could revise projections include divergence between binding European mandates and American guidance-based approaches, plus legacy fleet retrofit complexity exceeding insurance liability modeling. A model refresh is warranted upon material change in UNECE R155 enforcement stringency or Tier-1 supplier consolidation patterns.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Blockchain Technology in Aerospace and Defense Market
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Anti-Drone Defense System Market
Defense Cybersecurity
Maritime Cybersecurity Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Electronic Countermeasures Market
Defense Cybersecurity
Electronic Warfare Market
Defense Cybersecurity
Global Defense Tactical Radio Market
Defense Cybersecurity
Ballistics Targeting Software Market
Defense Cybersecurity
Military Computers Market
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Asia-Pacific Cyber Weapons Market
Defense Cybersecurity
Military Cybersecurity Market
Defense Cybersecurity
Defensive Cyber Weapons Market
Defense Cybersecurity
Asia-Pacific Missiles and Missile Defense Systems Market
Defense Cybersecurity
Cyber Weapons Market