
 Railway Cyber Security Market | 2026-2036
Railway Cyber Security Market Size, Share, and Industry Trends Forecast 2026-2036
Railway Cyber Security Market Analysis
Buyer concentration among national rail operators is hardening as state-backed infrastructure providers consolidate procurement authority across trunk corridors. Thales Group leverages its signaling heritage to bundle cyber-physical security suites for European high-speed networks. Siemens AG anchors its position through embedded security modules in its Trainguard platform. Alstom competes by integrating rail-specific intrusion detection into its rolling stock and wayside systems.
Railway cyber security encompasses the hardware, software, and protocols that protect train control systems, passenger information networks, and critical infrastructure from unauthorized access, malware, and operational disruption. The discipline centers on safeguarding communication-based train control (CBTC) and European Train Control System (ETCS) installations where latency below 500 milliseconds defines safety-critical performance thresholds. Network security solutions dominate current spending as operators retrofit legacy signaling with IP-connected architectures. Cloud-based deployment is expanding fastest among mid-tier operators seeking to outsource security operations centers without capital-intensive on-premises builds. Endpoint security retains concentrated margin pools in freight and urban transit segments where distributed rolling stock creates persistent attack surfaces across thousands of mobile assets.
The EU NIS2 Directive imposes mandatory incident reporting and supply-chain risk management on rail operators, reshaping procurement specifications across member states. The European Union Agency for Cybersecurity (ENISA) publishes rail-specific threat landscapes that inform national regulator enforcement priorities. The U.S. Transportation Security Administration (TSA) mandates cyber security directives for freight and passenger railroads above defined revenue thresholds. Stakeholders must monitor how divergent transatlantic compliance architectures influence vendor certification requirements and cross-border contract eligibility.
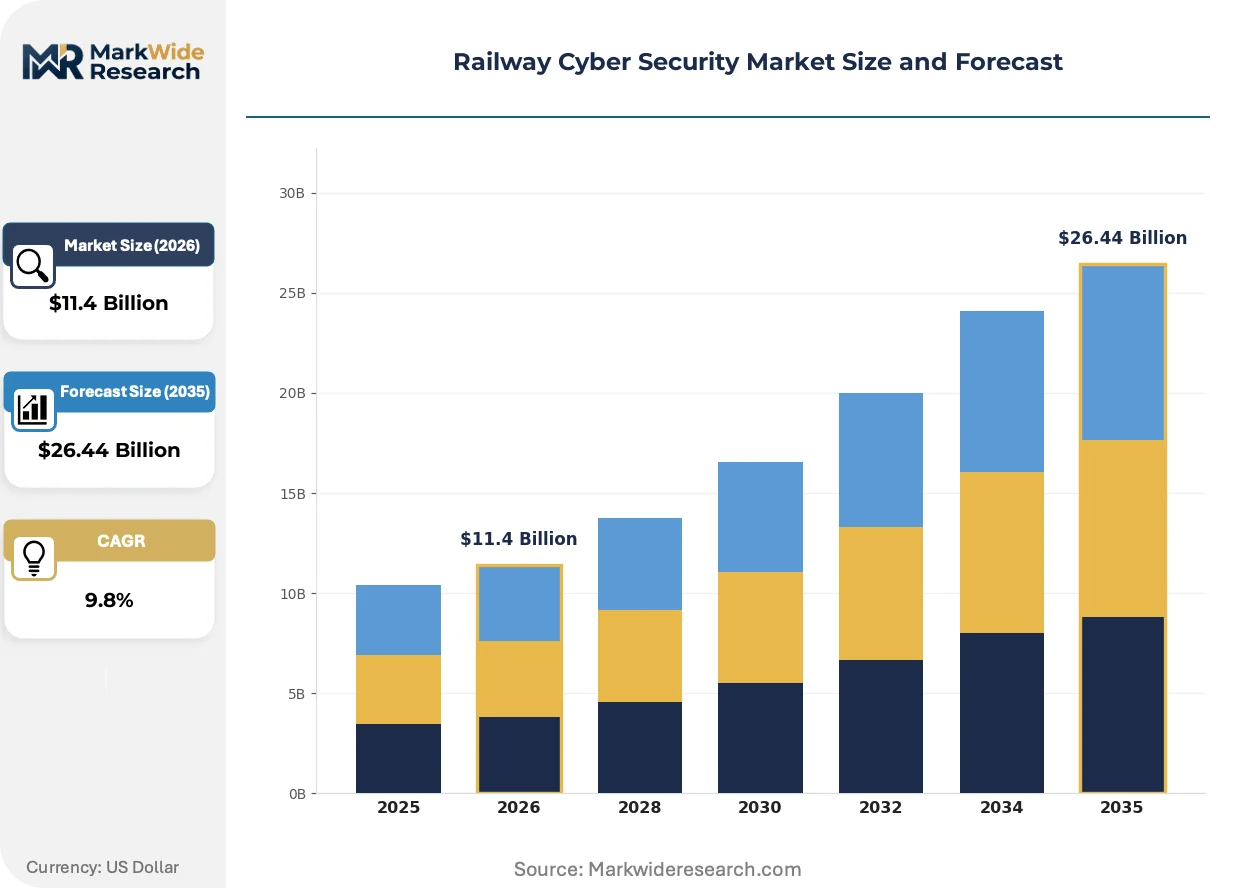
Market Dynamics
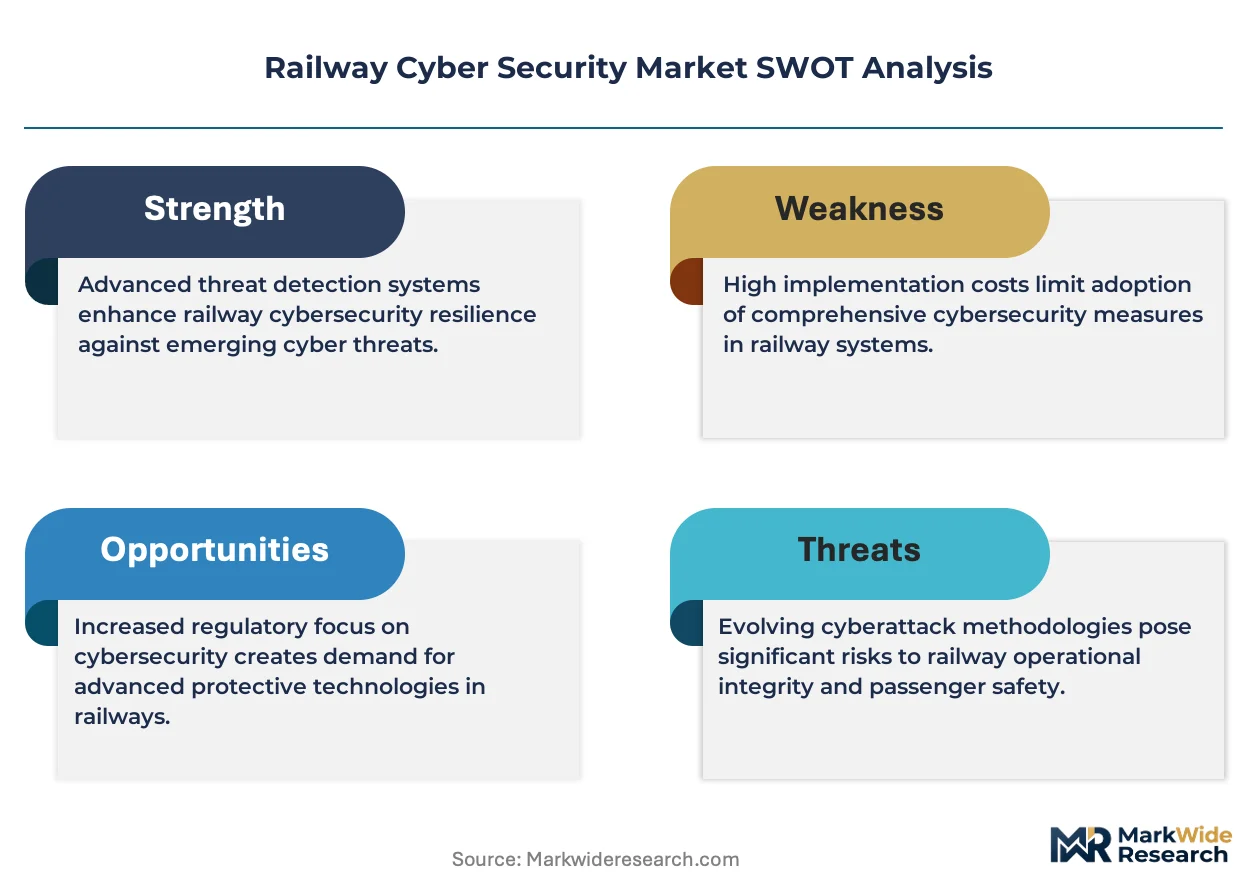
The EU NIS2 Directive's mandatory incident reporting and supply-chain risk management obligations are hardening procurement specifications across European rail networks. This regulatory compression is forcing operators to consolidate vendor relationships and embed cyber-physical security deeper into signaling modernization programs.
Growth Catalysts
- ETCS Level 3 Deployment:European rail operators are accelerating migration to the European Train Control System Level 3 architecture, which requires hardened IP-connected signaling networks with sub-500 millisecond latency guarantees.
- Germany's Digital Rail Initiative:Deutsche Bahn's trunk corridor modernization is creating concentrated demand for integrated cyber-physical security suites across high-speed and freight networks.
- Cloud-Based Security Operations:Mid-tier operators are outsourcing security operations centers to avoid capital-intensive on-premises infrastructure builds, expanding addressable market for managed security services.
Market Restraints
- Semiconductor Supply Concentration:Embedded security modules for train control systems depend on concentrated fabrication capacity in East Asia, exposing procurement timelines to geopolitical friction.
- Legacy System Interoperability:Analog signaling infrastructure predating IP connectivity requires expensive retrofit gateways, compressing margins on brownfield deployments.
- Specialized Talent Scarcity:The shallow pool of engineers trained in both rail safety systems and offensive cyber defense is extending implementation timelines for complex installations.
Strategic Opportunities
- Freight Operator Underpenetration:North American Class I railroads lag European passenger networks in cyber maturity, creating white space for intrusion detection systems across distributed rolling stock fleets.
- Zero Trust Architecture Mandates:The U.S. Transportation Security Administration's security directives are forcing freight and passenger operators above revenue thresholds to re-architect network segmentation.
- AI-Augmented Threat Detection:Machine learning models trained on rail-specific operational technology traffic patterns are converging with edge computing deployments for real-time anomaly detection in wayside systems.
Industry Challenges
- Cross-Domain Certification Complexity:Cyber-physical systems must satisfy both functional safety standards and information security frameworks, extending validation timelines for new product releases.
- Operational Technology Integration Friction:Security tools must coexist with legacy train control protocols designed without authentication layers, requiring custom protocol gateways that introduce latency risk.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Railway Cyber Security Market |
| Market Size in 2026 | $11.4 Billion |
| Market Size in 2035 | $26.44 Billion |
| CAGR (2026 – 2036) | 9.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, Antivirus, Intrusion Detection System, Encryption Deployment: On-premises, Cloud-based, Hybrid, Embedded End User: Rail Operators, Infrastructure Providers, Government Agencies, Service Certification Bodies Type: Network Security, Application Security, Endpoint Security, Data Security |
| Companies Covered | Thales Group, Siemens AG, Alstom, Cisco Systems, Inc., Hitachi Ltd., Huawei Technologies Co., Ltd., Nokia Corporation, Wabtec Corporation, IBM, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Railway Cyber Security Market Emerging Trajectories
Digital signaling architectures are dissolving the historical air-gap between operational technology and enterprise networks. This convergence is forcing security vendors to redesign products for deterministic performance environments where safety-critical latency thresholds are non-negotiable.
Edge-native intrusion detection systems are converging with deterministic Ethernet backbones to enable real-time threat response without violating train control latency budgets. European high-speed operators are piloting these integrated stacks on ETCS Level 2 corridors ahead of Level 3 migration. The technology is compressing the historical separation between safety engineering and cyber defense functions within operator organizations.
The EU NIS2 Directive's sector-specific obligations are reshaping procurement specifications across member states. Rail operators must now document supply-chain risk management for critical component vendors and report significant incidents within compressed timeframes. Germany, France, and the United Kingdom are seeing the most immediate specification changes as national regulators align enforcement with ENISA threat landscapes.
Buyer concentration is hardening as state-backed infrastructure providers consolidate procurement authority across trunk corridors. National rail operators are shifting from point-product acquisitions to multi-year framework agreements that bundle cyber security with signaling maintenance. This pattern is most visible in France and Germany where operator restructuring has centralized technology decision-making.
Railway Cyber Security Market Segmentation
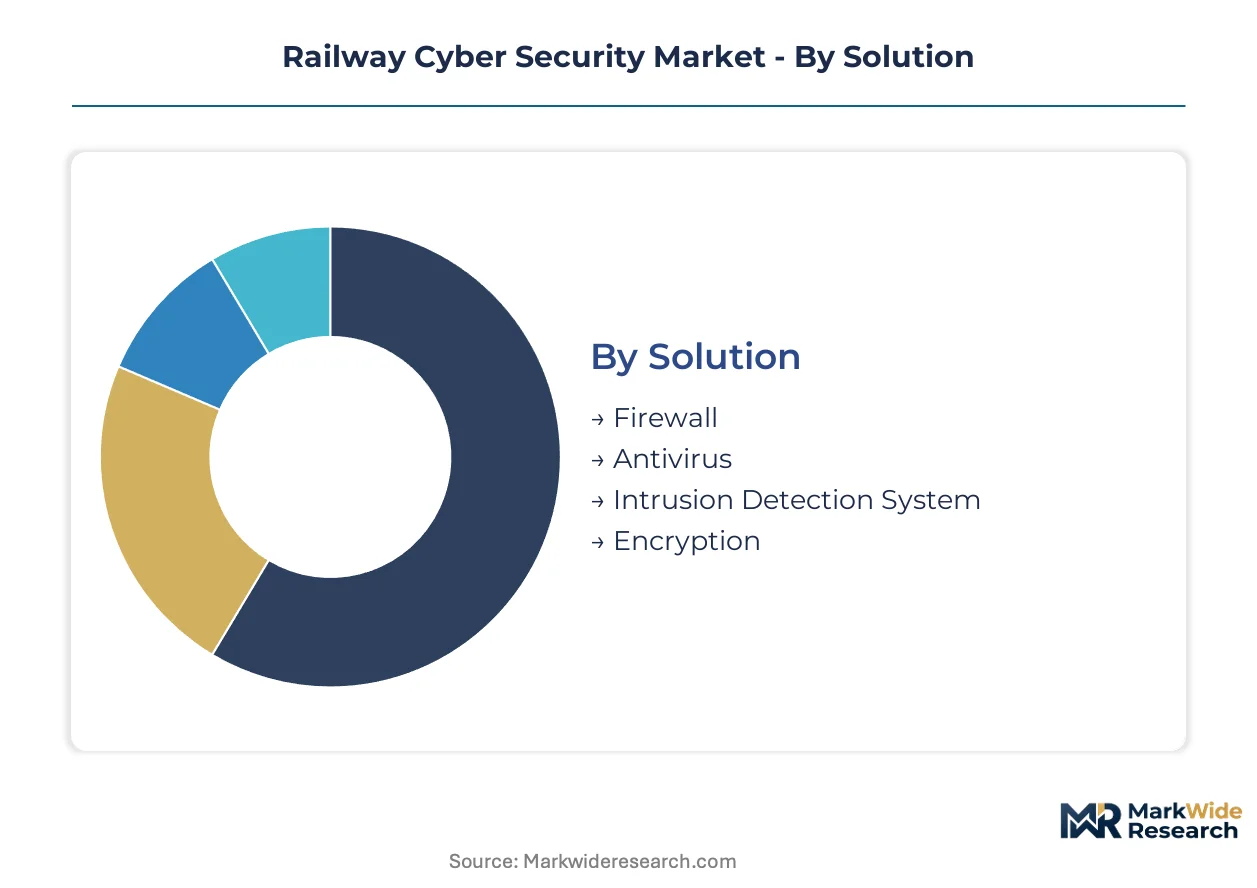
Railway cyber security procurement fragments across four structural dimensions that determine contract sizing, vendor qualification, and implementation complexity. Solution architecture and deployment mode together dictate capital commitment levels, while end-user type and security domain govern regulatory compliance obligations and technical specification depth.
Solution:
Capital intensity varies sharply across solution categories, with hardware-dependent offerings requiring substantially higher upfront investment than software-centric alternatives.
- Firewall:Deep packet inspection appliances engineered for deterministic Ethernet backbones in train control networks. Deutsche Bahn's digital corridor program is consolidating procurement around next-generation industrial firewalls with sub-millisecond latency guarantees for ETCS Level 3 migration.
- Intrusion Detection System:Rail-specific anomaly detection combining signature-based and behavioral analytics for operational technology protocols. Edge-native deployments on European high-speed lines are absorbing concentrated R&D investment ahead of NIS2 compliance deadlines.
- Antivirus:Endpoint protection suites adapted for rolling stock maintenance terminals and wayside computing nodes.
- Encryption:Hardware security modules and protocol-level cryptography for CBTC and ETCS communication links.
Firewall solutions absorb the bulk of installed capacity; intrusion detection systems are expanding most quickly.
Deployment:
Deployment architecture determines ongoing operational expenditure profiles and internal capability requirements, with substantial divergence between capital-heavy and outsourcing-oriented approaches.
- On-premises:Dedicated security operations centers with localized SIEM infrastructure and sovereign data retention. French and German national operators maintain these facilities for trunk corridor control systems subject to strict national cyber security frameworks.
- Cloud-based:Managed detection and response services delivered via multi-tenant platforms with rail-specific SLA guarantees. Mid-tier operators in the United Kingdom are adopting these arrangements to bypass security engineering talent scarcity.
- Hybrid:Segmented architectures preserving on-premises control for safety-critical networks while outsourcing enterprise IT security.
- Embedded:Security modules integrated directly into signaling hardware and rolling stock control systems at manufacturing stage.
On-premises deployments retain the largest installed base; cloud-based arrangements are climbing the fastest among operators below top-tier scale.
End User:
Procurement authority concentration varies dramatically across end-user categories, with implications for contract duration and solution bundling scope.
- Rail Operators:Integrated passenger and freight carriers with centralized technology decision-making. State-backed infrastructure providers in Germany, France, and the United Kingdom are consolidating multi-year framework agreements spanning signaling maintenance and cyber defense.
- Infrastructure Providers:Track and station asset managers with distributed operational technology footprints. These entities prioritize endpoint security for geographically dispersed wayside systems.
- Government Agencies:National regulators and transport ministries specifying certification requirements and incident reporting protocols.
- Service Certification Bodies:Independent assessors validating compliance with functional safety and information security standards for cross-border interoperability.
Rail operators command the dominant share of contract value; infrastructure providers are gaining procurement velocity as track-side digitalization accelerates.
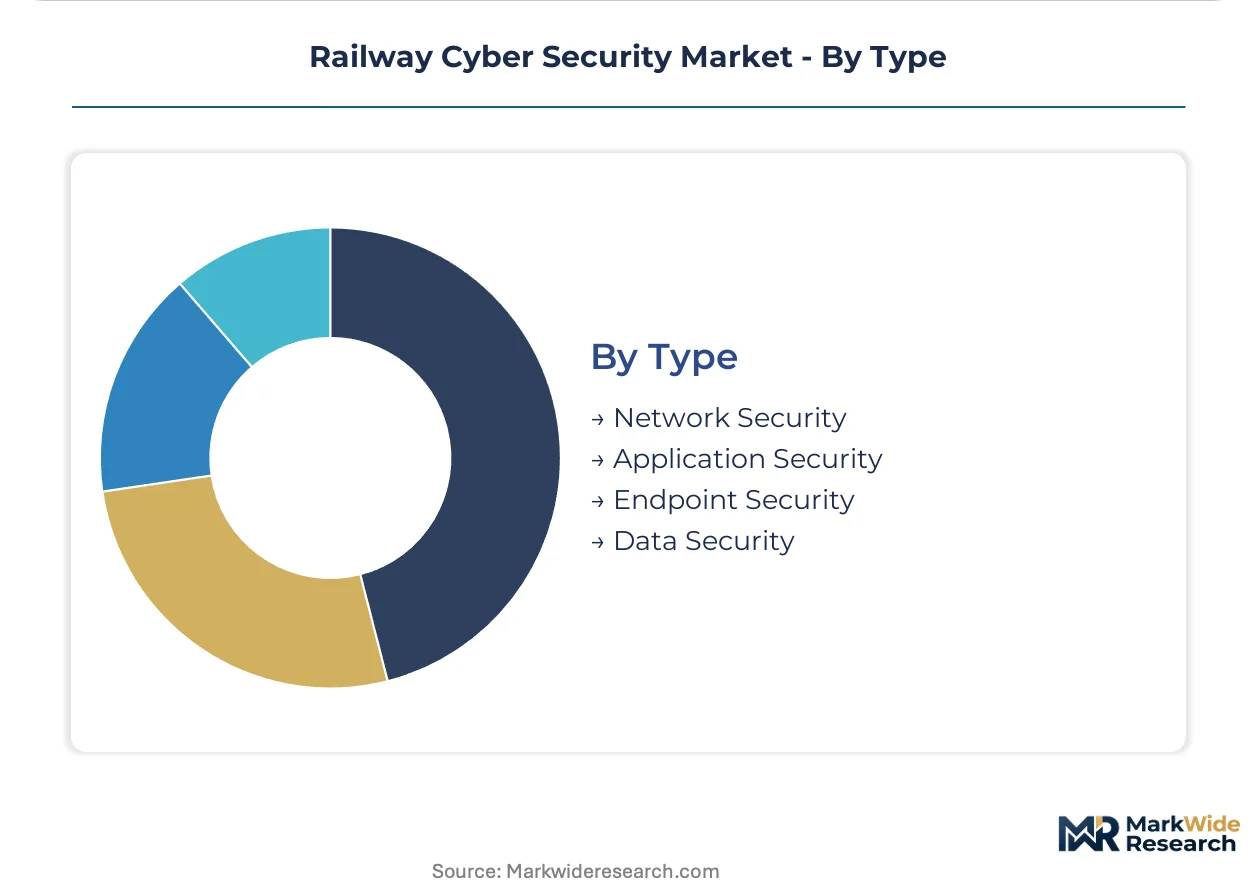
Type:
Security domain specialization governs vendor qualification pathways and the depth of rail-specific engineering required for deployment success.
- Network Security:Segmentation, access control, and traffic monitoring for converged operational technology and enterprise architectures. ETCS Level 2 and Level 3 corridors in France and Germany are driving concentrated demand for deterministic performance guarantees.
- Endpoint Security:Agent-based protection for maintenance laptops, driver cab terminals, and remote diagnostic equipment. Distributed rolling stock fleets across North American Class I railroads create persistent attack surfaces requiring fleet-wide coverage.
- Application Security:Code analysis and runtime protection for passenger information systems and mobile ticketing platforms.
- Data Security:Classification, encryption, and loss prevention for passenger records and operational telemetry.
Network security retains the steepest expansion trajectory as IP-connected signaling modernization proceeds; endpoint security maintains concentrated margin pools in freight segments.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
European state-backed rail operators concentrate procurement authority for cyber-physical security suites. German trunk corridor digitalization and French centralized framework agreements are compressing vendor relationships. United Kingdom mid-tier operators are accelerating cloud-based security operations outsourcing.
Germany
Deutsche Bahn's Digital Rail Initiative is modernizing high-speed and freight trunk corridors with hardened ETCS Level 3 signaling networks. The EU NIS2 Directive mandates supply-chain risk documentation and compressed incident reporting timelines for national operators. Engineering clusters in Munich and Berlin are embedding security modules directly into Trainguard platform deployments.
France
SNCF's centralized technology procurement is consolidating multi-year framework agreements spanning signaling maintenance and cyber defense. The national cyber security framework requires sovereign data retention for trunk corridor control systems. Industrial concentration around Paris and Lyon is driving integrated intrusion detection pilots on ETCS Level 2 corridors ahead of Level 3 migration.
United Kingdom
Network Rail's infrastructure digitalization is creating demand for deterministic Ethernet firewalls with sub-millisecond latency guarantees. The UK rail regulator aligns enforcement with ENISA threat landscapes and NIS2-derived obligations. Mid-tier operators in the Midlands and Northern England are outsourcing security operations centers to bypass specialized talent scarcity.
United States
North American Class I freight railroads lag European passenger networks in cyber maturity, creating white space for distributed rolling stock endpoint security. The Transportation Security Administration mandates network segmentation re-architecture for operators above revenue thresholds. Chicago and Los Angeles freight corridors are piloting zero trust architectures for converged operational technology and enterprise networks.
Japan
East Japan Railway and Central Japan Railway are retrofitting legacy Shinkansen signaling with IP-connected intrusion detection systems. METI guidelines on critical infrastructure protection inform procurement specifications for communication-based train control networks. Manufacturing clusters in Nagoya and Osaka are supplying embedded security modules for next-generation rolling stock platforms.
Railway Cyber Security Market Vendor Landscape
European producers anchor one tier; North American technology specialists hold adjacent positions in network infrastructure and managed services. The vendor base compresses around signaling heritage bundling and embedded module integration. Three archetypes dominate: legacy signaling conglomerates extending cyber-physical suites, industrial automation specialists retrofitting deterministic security, and telecommunications vendors supplying converged network backbones. Consolidation pressures favor multi-year framework agreements over point-product sales; strategic partnerships between rail operators and technology integrators are displacing transactional procurement.
Within the signaling-heritage tier, Thales Group, Siemens AG, and Alstom exemplify the bundling archetype where cyber security attaches to long-term maintenance contracts. Thales represents French state-backed consolidation across high-speed network programs. Siemens AG occupies a position anchored in German trunk corridor digitalization. Alstom sits within the rolling stock integration vector where intrusion detection embeds at manufacturing stage rather than retrofit.
| Leading Market Players |
|---|
| Thales Group |
| Siemens AG |
| Alstom |
| Cisco Systems, Inc. |
| Hitachi Ltd. |
| Huawei Technologies Co., Ltd. |
| Nokia Corporation |
| Wabtec Corporation |
| IBM |
| Others |
Supply Flow & Price Mechanics
Industrial semiconductor price indices cascade through railway cyber security supply chains, compressing margins on embedded security modules while amplifying pricing power for vendors with captive fabrication arrangements. ETCS Level 3 procurement deadlines concentrate buyer leverage, yet geopolitical friction in East Asian foundry access forces tiered pricing stratification across European national operators.
Pricing Analysis
Volume concentration among German, French, and British national rail operators splits the market between high-margin bundled framework agreements and commoditized point-product sales. Three-tier pricing structure across premium, standard, and economy levels tracks certification depth, with ENISA-aligned threat detection commanding substantial premiums over baseline firewall configurations. Pricing pressure stems from semiconductor input cost volatility and legacy retrofit gateway requirements. Mid-tier operators in the United Kingdom exhibit highest price sensitivity due to constrained capital budgets, while Deutsche Bahn's consolidated procurement maintains lowest sensitivity through multi-year maintenance bundling.
Supply Chain Analysis
Single-source vulnerability sits with concentrated advanced logic fabrication in Taiwan and South Korea, where security chip foundry capacity feeds directly into Trainguard platform and ETCS module production. Hardware security modules draw from German precision manufacturing and Japanese industrial electronics clusters, with raw silicon, rare earth magnets, and specialized laminates anchoring component costs. Tariff exposure on semiconductor imports from East Asia compounds procurement timeline risk. Distribution runs through signaling conglomerate direct sales organizations and rail-specific systems integrators, bypassing traditional IT channel structures.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The EU NIS2 Directive transforms railway cyber security into a cost-of-compliance arena where mandatory incident reporting and supply-chain documentation erect substantial barrier-to-entry moats for certified incumbents.
For Market Incumbents: To counter cloud-native security vendors encroaching on mid-tier operator segments, Siemens AG and Thales Group should deepen embedded module integration into manufacturing-stage rolling stock deployments, while expanding sovereign data retention capabilities for French and German national frameworks. Certification investment in dual functional safety and information security standards extends validation timelines that new entrants cannot absorb. For New Entrants and Emerging Players: The TSA security directives in the United States open a window for intrusion detection specialists to capture white space among North American Class I freight railroads lagging European cyber maturity. Target distributed endpoint security for mobile rolling stock fleets, where fleet-scale deployments exceed ten thousand assets and legacy vendor relationships remain underdeveloped. A managed detection and response service model bypasses capital-intensive on-premises builds that freight operators resist. For Investors and Strategic Acquirers: Distressed-cycle entries favor industrial automation specialists with deterministic Ethernet expertise in Germany and Japan, where rail-specific engineering talent scarcity extends implementation timelines for pure-play cyber vendors. Long-term viability hinges on signaling heritage bundling rather than point-product positioning. Watch for ETCS Level 3 corridor award announcements as inflection indicators for multi-year framework agreement velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Embedded Security Module Integration | Manufacturing-stage deployment in Alstom rolling stock platforms captures retrofit avoidance value. |
| Cloud-Based Security Operations Outsourcing | Mid-tier British operators bypass talent scarcity through managed detection and response services. |
| Zero Trust Architecture Re-architecture | TSA-mandated network segmentation creates replacement demand across converged operational technology backbones. |
| AI-Augmented Threat Detection Development | Machine learning models trained on rail-specific operational technology traffic patterns enable real-time anomaly response. |
| Multi-Year Framework Agreement Consolidation | SNCF and Deutsche Bahn centralized procurement favors bundled cyber-physical security over point-product sales. |
Methodological Framework
Trade association data, regulatory filings, and customs records anchored secondary inputs, combining primary interviews with rail operator technology directors, signaling system procurement leads, ENISA policy officers, and industrial cybersecurity engineering heads with bottom-up and top-down triangulation. ENISA rail threat landscape publications, EU NIS2 implementation guidance from member state regulators, U.S. TSA security directive compliance filings, and Deutsche Bahn supplier qualification databases supplied validation benchmarks.
Data-stream reconciliation across solution architecture, deployment mode, end-user category, and security domain segmentation dimensions shaped the analytical framework over the projection horizon. CAGRs derived from installed base migration curves for ETCS Level 2 to Level 3 corridors and cloud-based security operations adoption rates among mid-tier operators. Forecast inputs incorporated semiconductor supply lead time volatility and national rail operator restructuring timelines.
The model assumes a particular technology adoption path; alternative pathways for edge-native intrusion detection convergence with deterministic Ethernet would alter the outlook. Forecasts reflect assumptions around regulatory enforcement consistency and signaling modernization funding continuity. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Cyber Weapons Market
Defense Cybersecurity
Asia-Pacific Cyber Weapons Market
Defense Cybersecurity
Europe Automotive Cybersecurity Market
Defense Cybersecurity
Asia-Pacific Missiles and Missile Defense Systems Market
Defense Cybersecurity
Automotive Cybersecurity Service Market
Defense Cybersecurity
Mine and IED Detection System Market
Defense Cybersecurity
Military Cybersecurity Market
Defense Cybersecurity
Europe Cyber Weapons Market
Defense Cybersecurity
Electronic Warfare Market
Defense Cybersecurity
Automotive Cyber Security Market
Defense Cybersecurity
Anti-Drone Defense System Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Electronic Countermeasures Market
Defense Cybersecurity
Maritime Cybersecurity Market