
 Automotive Cybersecurity Service Market | 2026-2036
Automotive Cybersecurity Service Market Size, Share, and Industry Trends Forecast 2026-2036
Automotive Cybersecurity Service Market Insights
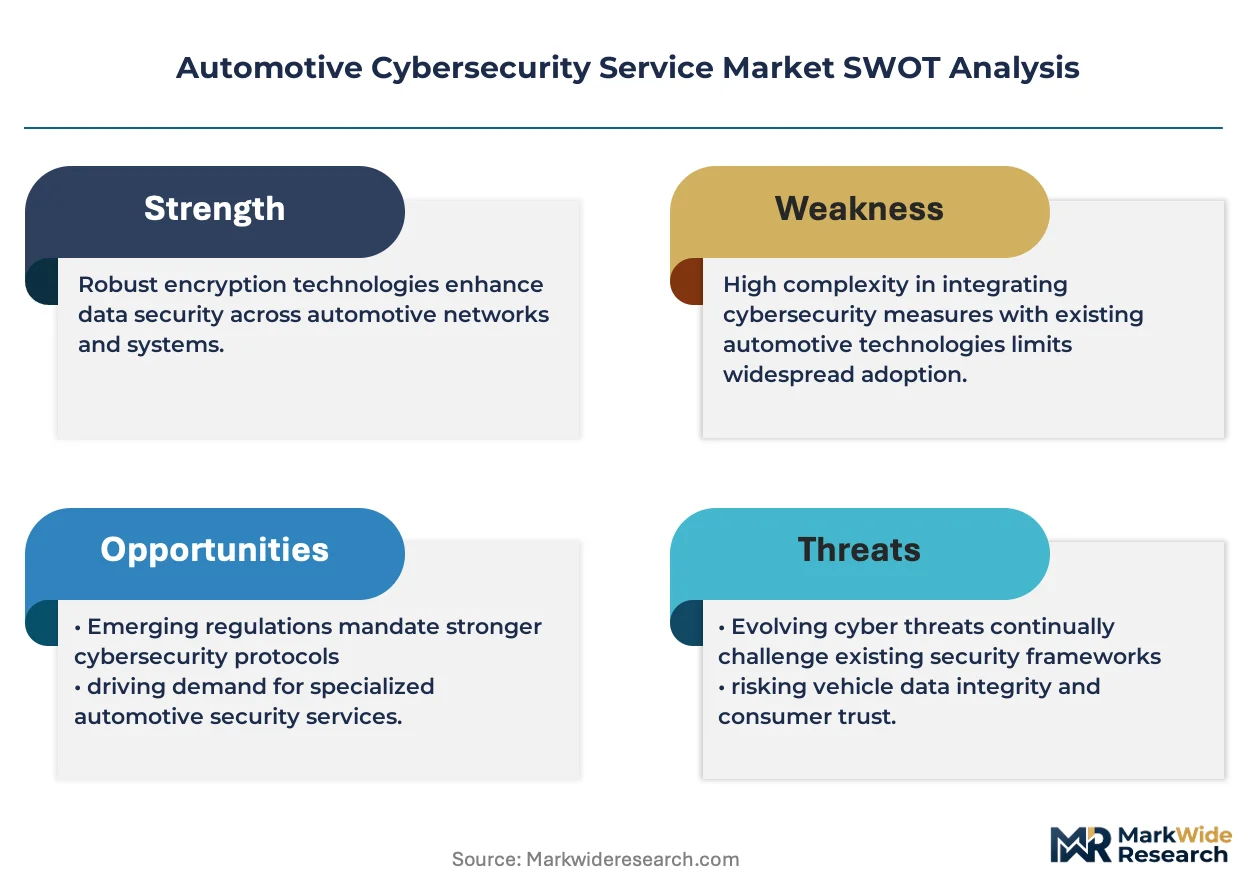
Automotive-grade security certification is rotating from optional to mandatory across supplier contracts. Robert Bosch GmbH leverages its tier-1 embedded systems footprint to anchor hardware-software integration services. ESCRYPT specializes in ECU-level encryption stacks for German OEM supply chains. Karamba Security differentiates through runtime threat detection tuned for CAN bus architectures.
Automotive cybersecurity service encompasses threat monitoring, penetration testing, and secure over-the-air update management for vehicle electronic architectures, typically operating across gateway controllers, telematics units, and ADAS compute platforms with sub-100-millisecond latency requirements for real-time intrusion response. Its primary commercial purpose is to preserve functional safety, data privacy, and brand liability exposure across connected vehicle fleets. Managed Security Service leads in revenue share as OEMs outsource 24/7 security operations centers rather than build in-house SOC capabilities. Cloud-Based deployment is expanding fastest as automakers adopt zonal E/E architectures requiring centralized, scalable threat intelligence platforms.
UNECE WP.29 Regulation No. 155, ISO/SAE 21434, and the EU Cyber Resilience Act collectively mandate cybersecurity management systems, risk assessment frameworks, and post-market monitoring obligations that reshape supplier qualification criteria and software update governance. The US NHTSA and FDA jointly influence standards where vehicle systems intersect with medical device transport or emergency response fleets. Stakeholders must monitor harmonization gaps between regional type-approval regimes and cloud sovereignty requirements before committing to multi-tenant security architectures.
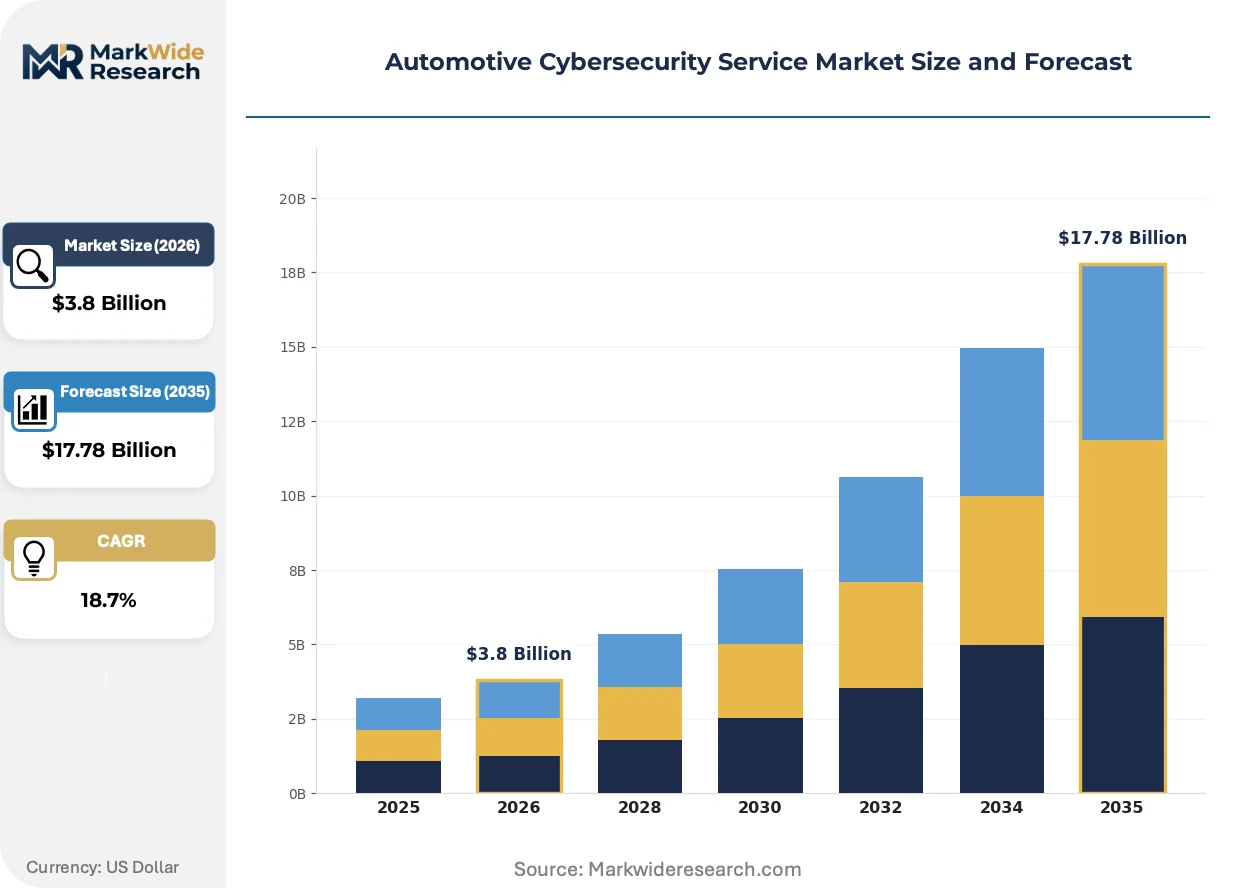
Market Dynamics
UNECE WP.29 Regulation No. 155 is compressing supplier qualification timelines as OEMs scramble to achieve type approval before enforcement deadlines, forcing cybersecurity services from peripheral consulting to core procurement categories.
Growth Catalysts
- UN Regulation No. 155:Mandates cybersecurity management systems for vehicle type approval across multiple jurisdictions, creating immediate compliance demand from tier-1 suppliers.
- Fleet operator digitization:Connected vehicle platform expansion among commercial fleets generates recurring revenue for managed security service providers.
- CAN bus architecture vulnerabilities:Legacy in-vehicle networks lack native encryption, driving retrofit demand for runtime threat detection solutions.
Market Restraints
- Embedded systems cost structure:Hardware-software integration for automotive-grade security adds 15-25% to ECU bill-of-materials, squeezing tier-2 supplier margins.
- Supplier ecosystem concentration:German OEM supply chains dominate premium vehicle cybersecurity procurement, limiting vendor diversification.
- ISO/SAE 21434 compliance friction:Risk assessment framework requirements extend development cycles by 8-14 months for new vehicle platforms.
Strategic Opportunities
- Zonal E/E architecture migration:Centralized compute platforms in next-generation vehicles enable cloud-native security service deployment at fleet scale.
- EU Cyber Resilience Act tailwind:Post-market monitoring obligations for connected devices expand recurring revenue potential for security operations centers.
- ADAS compute platform protection:Autonomous driving sensor fusion creates high-value attack surfaces requiring sub-100-millisecond intrusion response.
Industry Challenges
- Functional safety-cybersecurity integration:ISO 26262 and ISO/SAE 21434 skill sets rarely coexist in single engineering teams, creating hiring bottlenecks.
- Legacy gateway controller retrofit:Pre-2020 vehicle architectures lack hardware security modules, complicating over-the-air update authentication.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Automotive Cybersecurity Service Market |
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.78 Billion |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Security Service, Incident Response, Vulnerability Assessment, Compliance Management Technology: Intrusion Detection System, Firewall, Encryption, Endpoint Protection End User: OEMs, Aftermarket Providers, Fleet Operators, Insurance Companies Deployment Model: On-Premise, Cloud-Based, Hybrid, Network-Based |
| Companies Covered | Continental AG, Robert Bosch GmbH, Harman International, Aptiv PLC, DENSO Corporation, Argus Cyber Security, ESCRYPT, Karamba Security, Infineon Technologies AG, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Automotive Cybersecurity Service Market Trends and Innovations
Automotive cybersecurity is pivoting from perimeter defense to runtime integrity verification as software-defined vehicle architectures expose new attack surfaces across distributed compute nodes.
Hardware security modules integrated directly into ECU silicon are supplanting software-only encryption stacks for powertrain and chassis control systems. German and Japanese OEMs are mandating HSM inclusion in tier-1 RFQs issued since 2023. This migration is compressing pricing for pure-software security licensing while expanding addressable market for semiconductor-embedded trust anchors.
The EU Cyber Resilience Act imposes mandatory vulnerability disclosure and patch timelines for connected vehicle components sold in European markets. Suppliers must maintain software bills of materials and incident response capabilities across 10-year vehicle lifecycles. Aftermarket telematics providers face the steepest compliance burden, as many lack structured product security incident response teams.
Fleet operators are consolidating vendor relationships around full-stack security providers capable of spanning threat intelligence, penetration testing, and incident response. Single-point solution vendors face exclusion from multi-year service contracts. North American commercial vehicle fleets exhibit the fastest consolidation pace, driven by insurance carriers demanding demonstrated cybersecurity posture for premium coverage.
Automotive Cybersecurity Service Market Segmentation
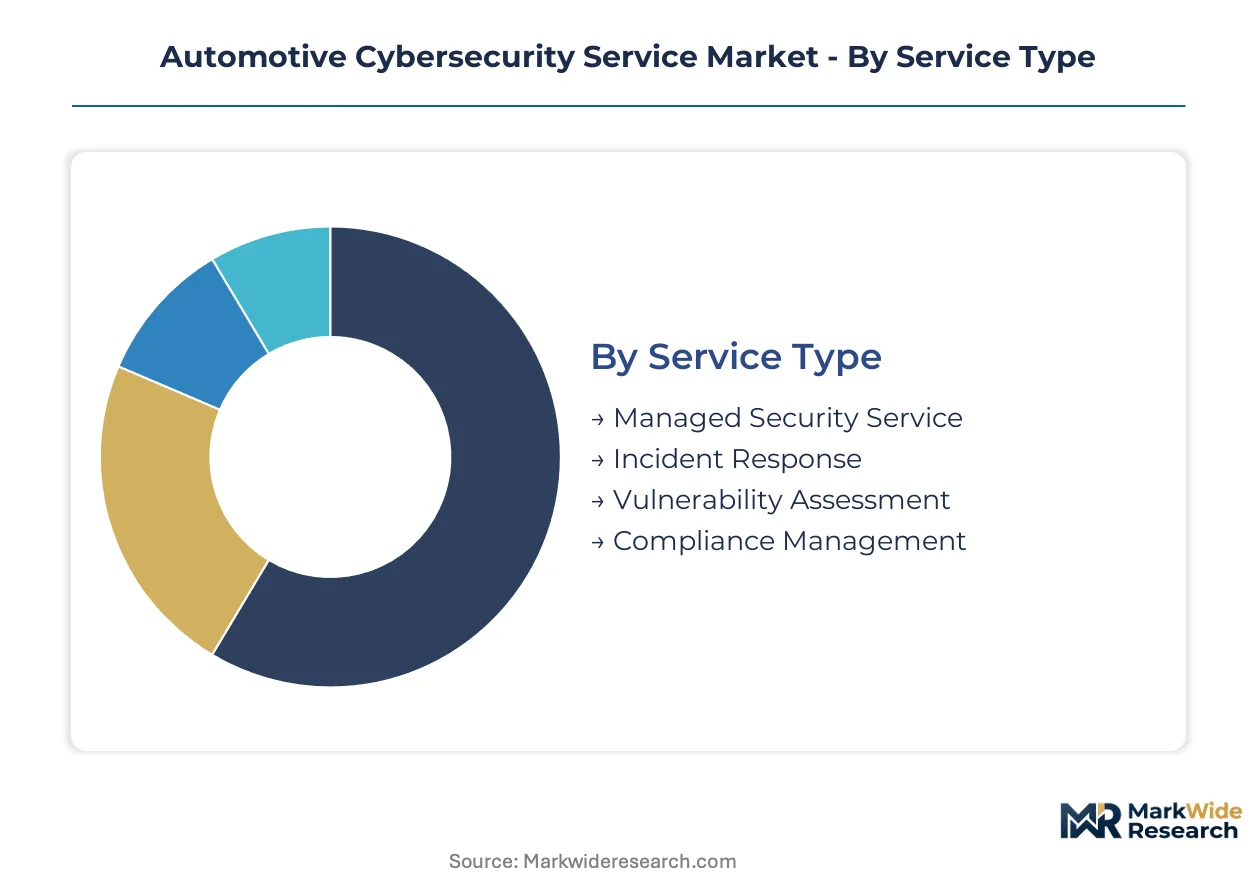
Automotive cybersecurity services fragment across four distinct category axes, each reflecting different procurement priorities and margin structures. Service type and deployment model capture the largest contract values, while technology and end-user segmentation determines integration complexity and recurring revenue durability.
Service Type:
Margin pools concentrate in recurring operational services rather than one-time consulting engagements, reflecting OEM preferences for outsourced security operations over in-house capability building.
- Managed Security Service:Continuous 24/7 monitoring of vehicle fleet security postures through dedicated security operations centers. German OEMs and North American commercial fleets drive procurement concentration, prioritizing outsourced SOC capabilities over capital-intensive internal builds. UN Regulation No. 155 compliance deadlines compress vendor selection timelines for this segment.
- Incident Response:Structured breach containment and forensic investigation protocols activated upon threat detection. Fleet operators in logistics and emergency services generate concentrated demand, motivated by insurance carrier requirements for demonstrated response capabilities. The segment commands premium pricing due to specialized automotive forensic expertise scarcity.
- Vulnerability Assessment:Systematic penetration testing and attack surface mapping across vehicle electronic architectures.
- Compliance Management:Documentation and audit support for ISO/SAE 21434 and type-approval cybersecurity management systems.
The dominant share belongs to Managed Security Service, while Incident Response is closing the gap fastest as breach severity escalates across connected vehicle fleets.
Technology:
Hardware-integrated protection mechanisms capture expanding budget allocation as software-only defenses prove inadequate for powertrain and chassis control system protection.
- Intrusion Detection System:Real-time anomaly detection across CAN bus and Ethernet vehicle networks with sub-100-millisecond response latency. ADAS compute platforms and zonal gateway controllers represent the highest-value deployment surfaces. Japanese and German OEMs mandate IDS inclusion in tier-1 RFQs for autonomous vehicle programs.
- Encryption:Cryptographic protection for over-the-air updates and inter-ECU communication channels. Hardware security module integration is displacing pure-software stacks in powertrain applications, compressing margins for legacy encryption licensing while expanding semiconductor-embedded trust anchor markets.
- Firewall:Network segmentation controls between vehicle domains and external connectivity interfaces.
- Endpoint Protection:Agent-based threat prevention deployed on telematics units and infotainment systems.
Encryption holds the dominant technology position, though Intrusion Detection System is expanding most quickly as runtime integrity verification supplants perimeter-focused defenses.
End User:
Procurement authority and contract scale vary sharply across buyer types, with fleet operators consolidating vendor relationships around full-stack providers while OEMs segment purchases by vehicle platform.
- OEMs:Original equipment manufacturers integrating cybersecurity across new vehicle development cycles and legacy platform retrofits. German premium OEMs concentrate procurement through established tier-1 supplier relationships, while volume manufacturers pursue multi-vendor strategies to reduce concentration risk.
- Fleet Operators:Commercial vehicle and logistics fleet managers securing connected vehicle platforms at enterprise scale. North American operators exhibit the fastest vendor consolidation pace, driven by insurance underwriting requirements for demonstrated cybersecurity posture.
- Aftermarket Providers:Third-party telematics and connectivity device suppliers retrofitting pre-2020 vehicle architectures.
- Insurance Companies:Cyber risk carriers procuring assessment services for policy pricing and claims validation.
OEMs retain the dominant procurement volume, yet Fleet Operators are gaining share fastest as commercial vehicle digitization accelerates recurring security service adoption.
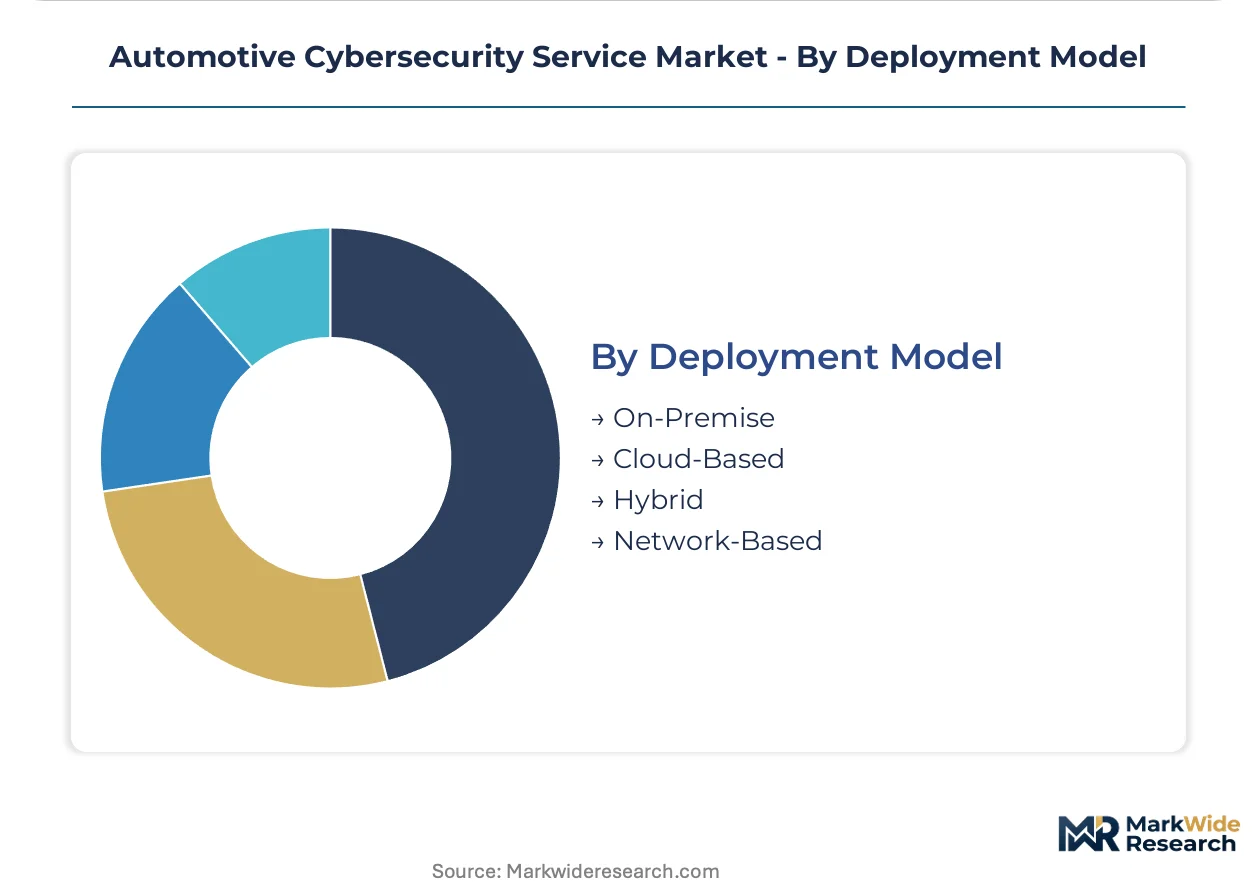
Deployment Model:
Cloud infrastructure economics are restructuring deployment economics as zonal E/E architectures enable centralized threat intelligence platforms serving fleet-scale vehicle populations.
- Cloud-Based:Scalable security service delivery through centralized threat intelligence platforms with fleet-wide policy orchestration. Next-generation zonal vehicle architectures enable this model by consolidating compute and reducing edge device complexity. German and US automakers lead migration toward cloud-native security operations.
- On-Premise:Dedicated security infrastructure deployed within OEM data centers or fleet operator facilities. Highly regulated buyers in defense and emergency response sectors sustain demand despite higher total cost of ownership.
- Hybrid:Split architectures combining edge detection with cloud analytics for latency-sensitive applications.
- Network-Based:Security functions embedded within vehicle network infrastructure and gateway controllers.
Cloud-Based deployment claims the dominant trajectory, while Hybrid models are climbing fastest as transitional architectures bridge legacy and next-generation vehicle platforms.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German tier-1 suppliers anchor the supply base for automotive cybersecurity services, with engineering talent clustering around Stuttgart, Munich, and Wolfsburg. Regulatory leadership from UNECE WP.29 and ISO/SAE 21434 standard-setting compresses procurement timelines across multiple jurisdictions.
United States
NHTSA cybersecurity guidance and commercial fleet digitization drive procurement concentration. The NHTSA-FDA joint oversight for emergency response vehicle systems creates specialized compliance requirements. Detroit automakers and Silicon Valley autonomous vehicle developers split demand between legacy platform retrofits and next-generation zonal architectures.
Germany
Dense OEM-supplier ecosystems in Baden-Württemberg and Bavaria generate concentrated service demand. UN Regulation No. 155 enforcement through KBA type-approval processes mandates cybersecurity management systems. Stuttgart and Munich host the dominant engineering centers for ECU-level encryption and hardware security module integration.
Japan
METI industrial cybersecurity frameworks and autonomous vehicle development programs expand service procurement. Japanese OEMs mandate intrusion detection systems in tier-1 RFQs for ADAS compute platforms. Nagoya and Tokyo metropolitan areas concentrate supplier engineering resources for CAN bus architecture protection.
China
MIIT connected vehicle security standards and domestic EV platform scaling create compliance-driven demand. GB standards for automotive cybersecurity reshape supplier qualification criteria. Shanghai and Shenzhen clusters concentrate threat intelligence platform development for fleet-scale deployments.
South Korea
MFDS automotive software safety oversight and Hyundai-Kia connected vehicle expansion drive service adoption. Korean OEMs pursue multi-vendor cybersecurity strategies to reduce supplier concentration risk. Seoul Capital Area hosts the dominant engineering centers for over-the-air update security infrastructure.
Automotive Cybersecurity Service Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes, with tier-1 embedded systems suppliers commanding hardware-software integration premiums while specialized cybersecurity vendors capture runtime detection niches. The market structure tiers across semiconductor-anchored trust providers, automotive-focused encryption specialists, and fleet-scale managed security operators. Two strategic archetypes dominate: integrated tier-1 suppliers leveraging ECU manufacturing footprints, and pure-play cybersecurity vendors with automotive-specific threat intelligence. Competitive moves concentrate on strategic partnerships for zonal architecture migration and portfolio diversification into adjacent functional safety domains.
Within the integrated tier-1 tier, Robert Bosch GmbH and Continental AG anchor hardware-software integration capabilities, while ESCRYPT exemplifies the specialized encryption stack archetype for German OEM supply chains. These three entities occupy positions spanning embedded systems manufacturing, tier-1 supplier relationships, and ECU-level cryptographic implementation respectively.
| Leading Market Players |
|---|
| Continental AG |
| Robert Bosch GmbH |
| Harman International |
| Aptiv PLC |
| DENSO Corporation |
| Argus Cyber Security |
| ESCRYPT |
| Karamba Security |
| Infineon Technologies AG |
| Others |
Pricing and Supply Chain Analysis
Eighteen-month qualification timelines for tier-1 cybersecurity suppliers compress procurement cycles and concentrate pricing power among German embedded systems manufacturers with pre-existing OEM relationships. This lead-time structure rewards incumbents who have already achieved UN Regulation No. 155 certification, while squeezing margins for tier-2 suppliers attempting late entry.
Pricing Analysis
UN Regulation No. 155 dictates the pricing tier structure across automotive cybersecurity services, separating certified managed security providers from uncertified consulting shops. Three-tier pricing stratifies across premium hardware-software integration, standard SaaS-tiered monitoring subscriptions, and economy vulnerability assessment bundles. Cost compression in the standard tier intensifies as cloud-native entrants displace legacy on-premise deployments. Fleet operators exhibit highest price sensitivity due to per-vehicle scaling economics, while German premium OEMs prioritize certification grade over unit cost.
Supply Chain Analysis
Hardware security module fabrication chokepoints in Taiwan and South Korea constrain upstream capacity for automotive-grade encryption silicon. The supply chain draws from German ECU manufacturing clusters, Japanese semiconductor packaging facilities, and Chinese telematics hardware assembly. Single-source vulnerability concentrates in automotive-grade HSM foundry access, where TSMC and Samsung anchor global supply. Distribution runs through tier-1 supplier integration contracts rather than open market procurement, locking aftermarket providers into secondary sourcing positions.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation opportunity emerges across automotive cybersecurity as fleet operator digitization splinters demand between OEM-anchored tier-1 relationships and direct commercial vehicle procurement. This demand-side shift creates serviceable niches for specialized runtime detection vendors outside traditional supply chain gatekeepers.
For Market Incumbents: Compound defensive positioning through hardware security module backward integration and captive SOC capacity expansion in Stuttgart and Munich engineering clusters. Threat from cloud-native security vendors with zonal architecture expertise demands preemptive certification investment ahead of EU Cyber Resilience Act enforcement. Vertical integration into semiconductor trust anchors represents the critical lever for margin defense against software-only commoditization. For New Entrants and Emerging Players: ISO/SAE 21434 fast-track certification opens procurement access to North American commercial fleet operators consolidating vendor relationships around full-stack providers. White-space targets concentrate in aftermarket telematics retrofit for pre-2020 vehicle architectures and runtime threat detection for CAN bus legacy networks. Go-to-market angle should lead with insurance carrier partnership channels, where demonstrated cybersecurity posture unlocks premium coverage eligibility. For Investors and Strategic Acquirers: Carve-out targets emerge from tier-1 automotive suppliers spinning non-core cybersecurity divisions ahead of zonal architecture migration. Long-term viability centers on recurring revenue durability from managed security services rather than one-time compliance consulting. Acquisition archetype prioritizes vendors with embedded OEM RFQ relationships and hardware-software integration capabilities. Signal to watch is NHTSA rulemaking momentum for mandatory cybersecurity management systems, which would replicate UN Regulation No. 155 demand compression in North American markets.| Strategic Initiative | Industry Significance |
|---|---|
| Hardware Security Module Integration | Semiconductor-embedded trust anchors displace software-only encryption in powertrain ECUs from German and Japanese OEMs. |
| Cloud-Native SOC Deployment | Centralized threat intelligence platforms enable fleet-scale monitoring for zonal E/E architectures adopted by US automakers. |
| ISO/SAE 21434 Certification Investment | Risk assessment framework compliance compresses vendor qualification timelines for UN Regulation No. 155 type approval. |
| Runtime Intrusion Detection Development | Sub-100-millisecond response latency meets ADAS compute platform protection requirements in autonomous vehicle programs. |
| Insurance Carrier Partnership Channel | Cybersecurity posture demonstration unlocks premium coverage eligibility for North American commercial fleet operators. |
Research Methodology
The analysis maps managed security services, incident response protocols, encryption technology stacks, and fleet operator procurement patterns, each validated through primary engagement with OEM platform engineers, tier-1 supplier procurement leads, commercial fleet operations managers, and automotive cybersecurity specialists. Secondary validation draws from UNECE WP.29 regulatory filings, ISO/SAE 21434 implementation guidelines, NHTSA cybersecurity guidance documents, and vehicle production registration databases. Bottom-up service provider revenue estimates triangulate against top-down OEM cybersecurity spending allocations.
Consistency checks against external benchmarks validate volume and value outputs across the projection horizon. The analytical framework models service type, deployment architecture, technology layer, and end-user procurement authority as core segmentation dimensions, with vehicle class and regional regulatory cluster as automotive-specific overlay variables. CAGRs derive from fitted growth curves applied to compliance-driven demand inflection points and fleet digitization adoption S-curves. Forecast inputs incorporate zonal E/E architecture migration timelines and hardware security module penetration assumptions.
Underlying assumptions cover regulatory enforcement adherence, OEM supplier relationship stability, and cloud infrastructure scaling economics, with deviation risk concentrated in harmonization gaps between regional type-approval regimes and legacy vehicle retrofit feasibility. Practitioners should keep alternative scenarios live as NHTSA rulemaking trajectory and EU Cyber Resilience Act implementation pace evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Vehicle Cybersecurity Market
Defense Cybersecurity
Cyber Weapons Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Defensive Cyber Weapons Market
Defense Cybersecurity
Ballistics Targeting Software Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Military Sensors Cybersecurity Solutions Market
Defense Cybersecurity
Maritime Cybersecurity Market
Defense Cybersecurity
Military Cybersecurity Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Global Defense Tactical Radio Market
Defense Cybersecurity
Anti-Drone Defense System Market
Defense Cybersecurity
Electronic Warfare Market
Defense Cybersecurity
Asia-Pacific Missiles and Missile Defense Systems Market
Defense Cybersecurity
Asia-Pacific Cyber Weapons Market
Defense Cybersecurity
Automotive Cyber Security Market