

Maritime Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Maritime Cybersecurity Market Insights
Channel partnerships between satellite communications providers and vessel IT integrators is tilting toward consolidated managed security offerings. Fortinet leverages its firewall appliance ecosystem to anchor shore-to-ship network protection contracts. Naval Dome specializes in OT-specific maritime defenses, differentiating its platform from generic enterprise tools. Thales Group dominates naval-grade encryption segments, extending sovereign defense capabilities into commercial shipping channels.
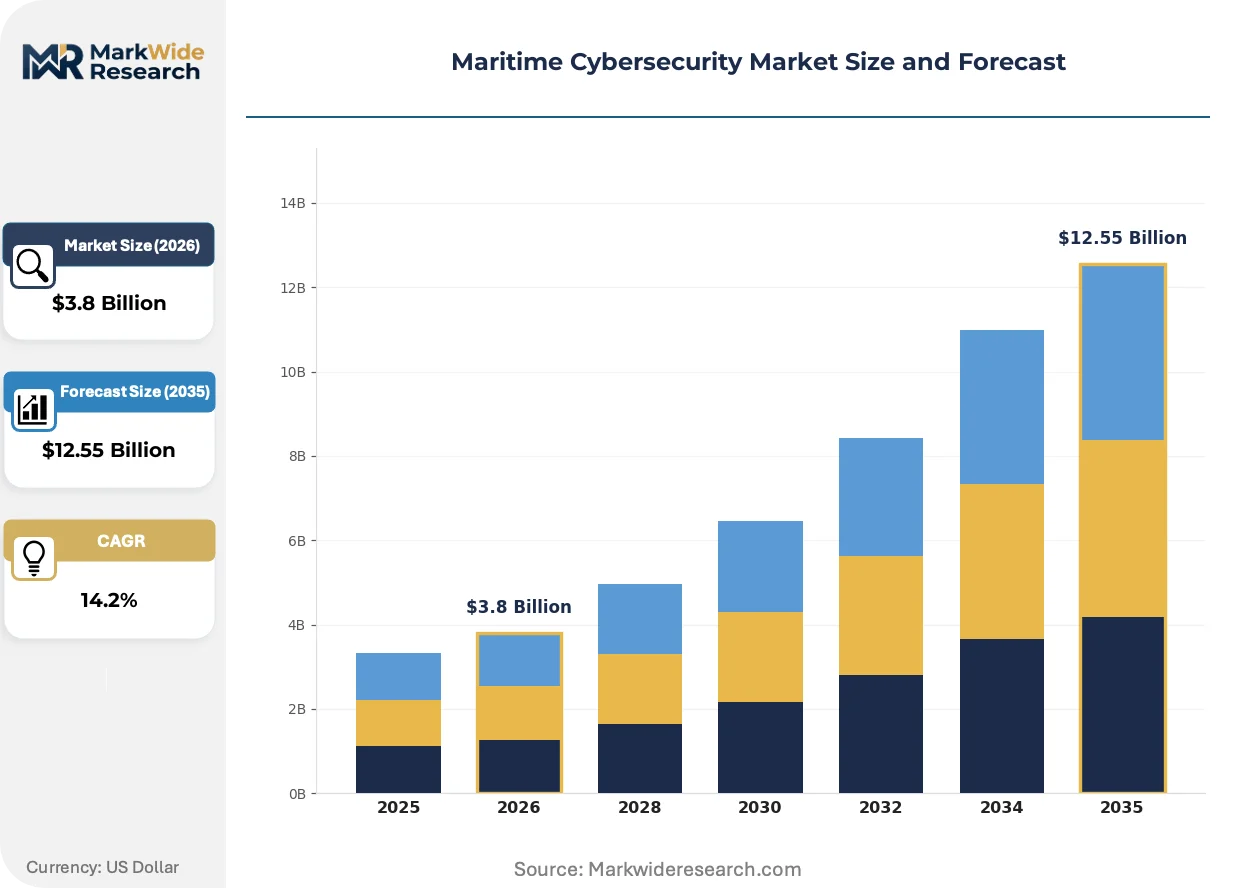
Maritime cybersecurity encompasses the protection of shipboard information technology, operational technology, and satellite communication systems from unauthorized access, data exfiltration, and navigational disruption through encryption protocols, network segmentation, and continuous anomaly detection. Its primary purpose is ensuring vessel safety, cargo integrity, and port operational continuity against escalating threat actor campaigns targeting global supply chains. Network Security solutions lead current procurement as fleet-wide connectivity expands, while Threat Intelligence segments capture expanding margin pools as operators seek predictive rather than reactive postures. Cloud-Based deployment modes are gaining share among mid-size operators seeking to avoid capital-intensive on-premises infrastructure.
The International Maritime Organization's 2021 cybersecurity guidelines, the EU NIS2 Directive extending to port operators, and the US Coast Guard's maritime security regulations collectively mandate systematic risk assessment and incident reporting, directly shaping vendor product roadmaps and customer procurement checklists. Classification societies including ABS Group of Companies now embed cyber resilience into vessel certification frameworks, conditioning market access on demonstrated compliance. Stakeholders must monitor the divergence between flag-state enforcement rigor and actual fleet implementation gaps, as this variance will determine which solution architectures achieve scalable adoption.
Market Dynamics
Classification societies now embed cyber resilience into vessel certification frameworks, conditioning market access on demonstrated compliance and forcing procurement checklists to prioritize integrated risk assessment platforms over point solutions.
Growth Catalysts
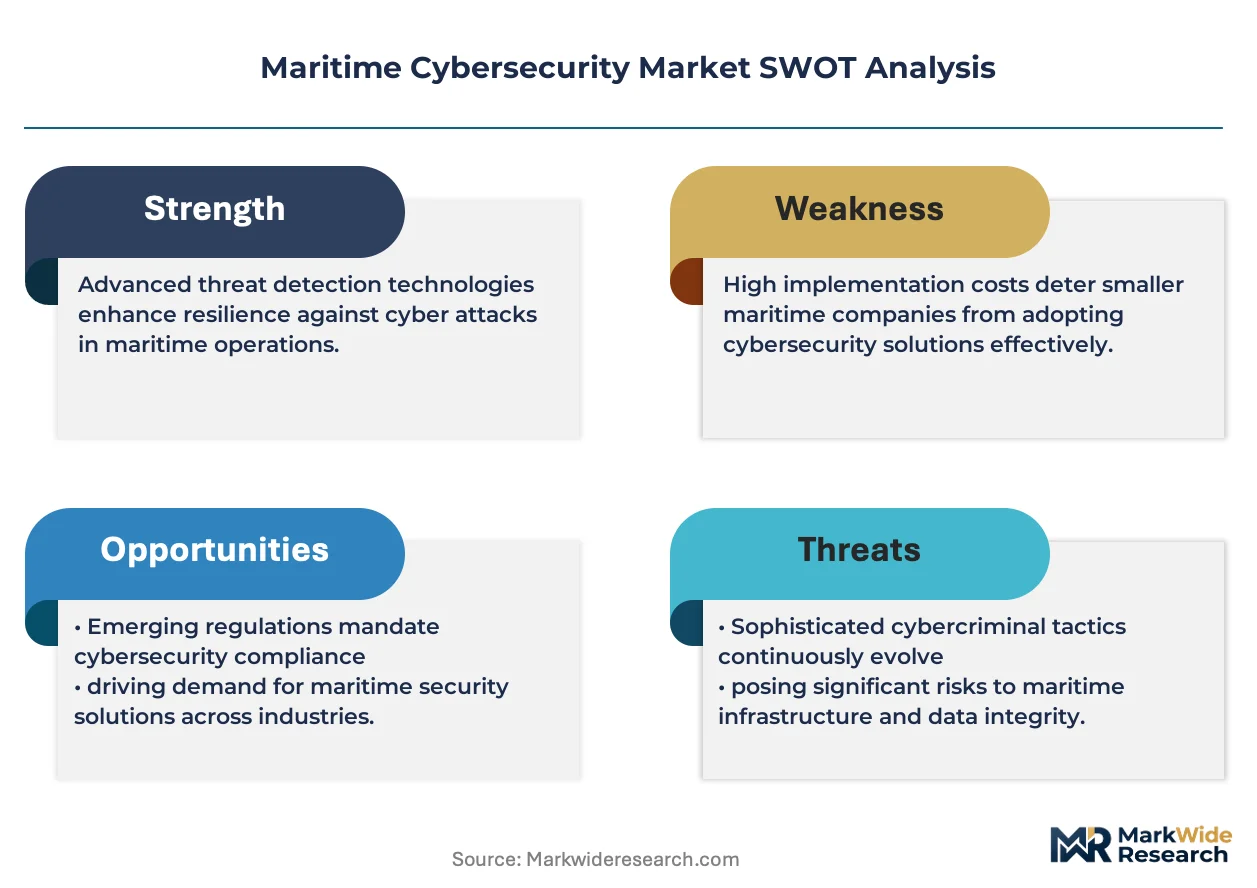
- IMO 2021 Guidelines:The International Maritime Organization's mandatory cybersecurity framework requires fleet-wide risk management systems, compelling container shipping lines to upgrade shore-to-ship network protection.
- EU NIS2 Directive:Port operators across European Union member states must implement systematic incident reporting and threat detection, expanding addressable market for managed security services.
- Satellite connectivity expansion:Low-earth orbit constellations are digitizing fleet communications infrastructure, multiplying attack surfaces and necessitating continuous monitoring solutions.
Market Restraints
- Legacy OT integration costs:Shipboard operational technology systems built on proprietary protocols require expensive retrofitting to achieve network segmentation compatible with modern cybersecurity architectures.
- Specialized talent scarcity:Maritime cybersecurity combines naval architecture, satellite communications, and threat intelligence expertise, creating recruitment bottlenecks in Norway's technology cluster and other concentrated hubs.
- Flag-state enforcement variance:Divergence between strict EU port state control and lax open-registry enforcement creates competitive disadvantages for compliant operators.
Strategic Opportunities
- Autonomous vessel preparation:Unmanned ship trials in Norwegian waters are generating demand for AI-driven anomaly detection that secures navigation systems without human intervention.
- Cloud-based deployment:Mid-size operators seeking to avoid capital-intensive infrastructure present expansion potential for subscription-managed security platforms.
- Threat intelligence services:Predictive posture adoption among major container lines opens margin pools beyond commodity firewall procurement.
Industry Challenges
- OT-IT convergence complexity:Integrating operational technology monitoring with enterprise information technology security without disrupting propulsion and cargo handling systems requires specialized engineering capabilities.
- Certification timeline compression:Classification society cyber resilience verification processes lag behind regulatory deadlines, creating compliance gaps for fleet renewal programs.
Report Scope
MarkWide ResearchGet the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Maritime Cybersecurity Market Trends and Innovations
Maritime cybersecurity is pivoting from perimeter defense toward continuous monitoring of operational technology networks, with artificial intelligence and sovereign encryption requirements redefining competitive differentiation.
Edge computing architectures deployed on vessels are digitizing threat detection capabilities by processing anomalies locally rather than transmitting raw data to shore-based security operations centers. Container shipping lines operating high-frequency Asia-Europe routes are adopting these systems fastest due to latency constraints in satellite backhaul. This distributed processing model is digitizing the traditional shore-centric security operations model and compressing response times from hours to seconds.
The EU NIS2 Directive's extension to port operators mandates systematic risk assessment and incident reporting with specific technical and organizational measures. Port authorities in Rotterdam, Hamburg, and Antwerp must now demonstrate supply chain resilience across terminal operating systems and cargo handling equipment interfaces. Container terminal operators are responding by procuring integrated platforms that unify IT and OT security governance under single-dashboard visibility.
Charterers and cargo owners now require cyber resilience documentation as a condition of contract, displacing price-only procurement for vessel operators. Major commodity traders and automotive manufacturers are inserting security audit clauses into freight agreements, particularly for routes transiting high-risk waters. This contractual pressure is most visible in Norwegian and Singapore-flagged fleets where classification society certification carries premium market access.
Maritime Cybersecurity Market Segmentation
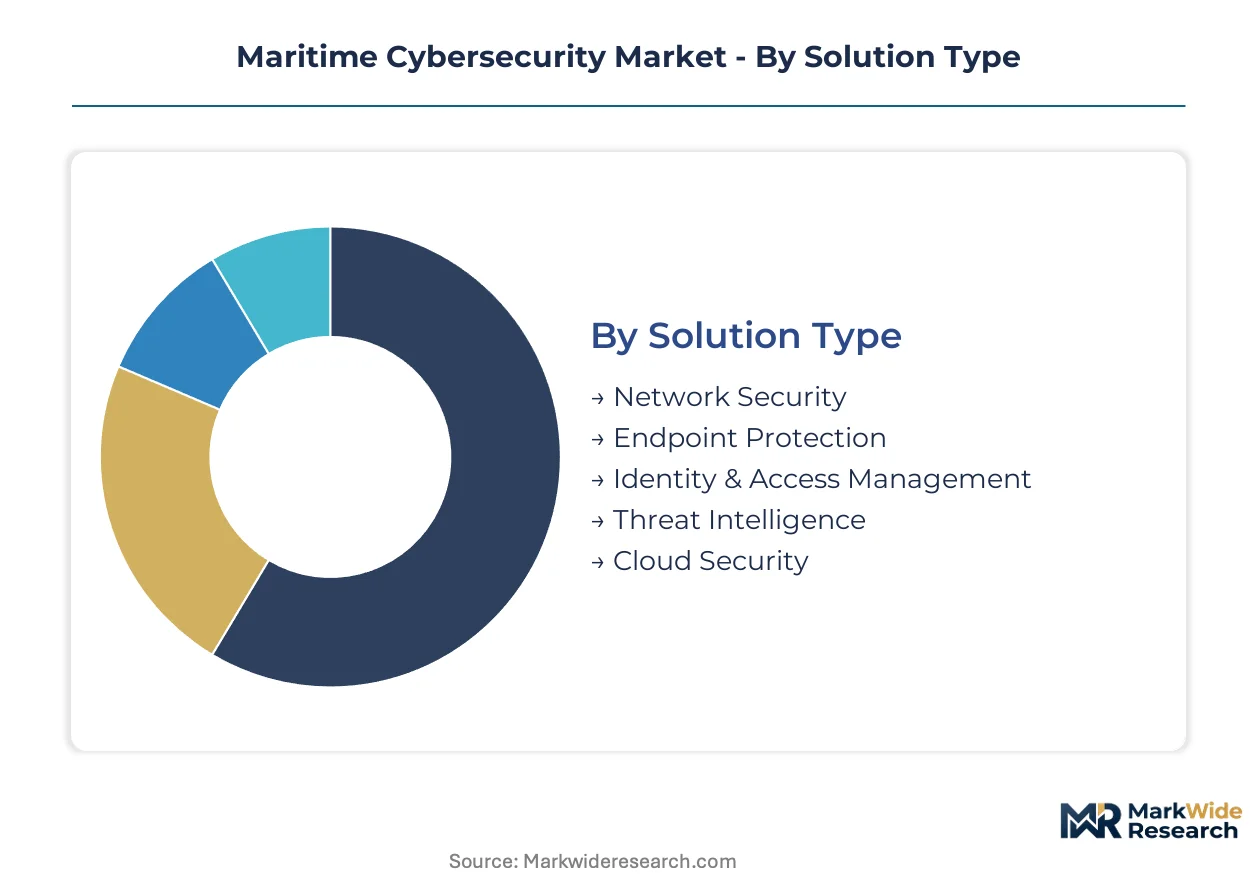
Maritime cybersecurity procurement varies sharply by operational context, with vessel operators prioritizing OT-compatible defenses while port authorities emphasize supply chain visibility platforms. Segmentation reveals how solution architectures must adapt to distinct threat surfaces across mobile fleet assets and fixed infrastructure.
Solution Type:
Network Security and Threat Intelligence concentrate procurement spending as fleet digitization expands attack surfaces requiring real-time monitoring and predictive analytics.
- Network Security:Firewalls, intrusion detection systems, and shore-to-ship VPNs segment fleet communications from unauthorized access. Container shipping lines operating Asia-Europe routes are deploying these solutions fastest due to satellite bandwidth constraints and IMO compliance deadlines.
- Threat Intelligence:Predictive analytics platforms aggregate attack signatures from maritime-specific sources including AIS spoofing incidents and port ransomware campaigns. Major commodity traders now require threat intelligence documentation as a contract condition, displacing price-only procurement for vessel operators.
- Endpoint Protection:Shipboard workstation and server hardening against malware and phishing vectors.
- Identity & Access Management:Multi-factor authentication and role-based access controls for crew and shore personnel.
- Cloud Security:Data encryption and access governance for cloud-hosted fleet management platforms.
The dominant share belongs to Network Security, while Threat Intelligence is closing the gap fastest.
Deployment Mode:
Cost tier differentiation separates capital-intensive on-premises installations from subscription-managed alternatives favored by mid-size operators avoiding infrastructure ownership.
- Managed Security Service:Third-party providers operate continuous monitoring and incident response through shore-based security operations centers. Norwegian-flagged fleets are adopting these services fastest due to classification society cyber resilience certification requirements and specialized talent scarcity in the country's maritime technology cluster.
- Cloud-Based:Software-defined security functions delivered via satellite connectivity eliminate hardware refresh cycles. Mid-size container operators in Singapore are migrating to these platforms to avoid capital expenditure while satisfying charterer audit demands.
- On-Premises:Hardware appliances installed directly on vessels or in port data centers.
- Hybrid:Combined cloud and local processing for latency-sensitive navigation system protection.
- Virtualized Security:Containerized security functions deployed on vessel edge computing infrastructure.
Managed Security Service commands the largest revenue pool, though Cloud-Based deployment is expanding most quickly among operators seeking operational flexibility.
Application:
Application segmentation tracks where cyber defenses interface with safety-critical maritime operations, from bridge navigation to terminal cargo handling.
- Navigation Systems Protection:ECDIS, GPS, and autopilot hardening against spoofing and jamming attacks. Autonomous vessel trials in Norwegian waters are generating specialized demand for AI-driven anomaly detection that secures navigation without human intervention.
- Port Facility Security:Terminal operating system and cargo handling equipment protection. Port authorities in Rotterdam, Hamburg, and Antwerp must demonstrate supply chain resilience under the EU NIS2 Directive, expanding procurement for integrated IT-OT governance platforms.
- Vessel Monitoring:Engine performance and fuel system telemetry protection.
- Cargo Management Security:Container tracking and documentation system integrity.
- Communication Systems Defense:Satellite link and VHF protection against interception.
Navigation Systems Protection leads investment as autonomous shipping approaches, while Port Facility Security is gaining share fastest under EU regulatory pressure.
End User:
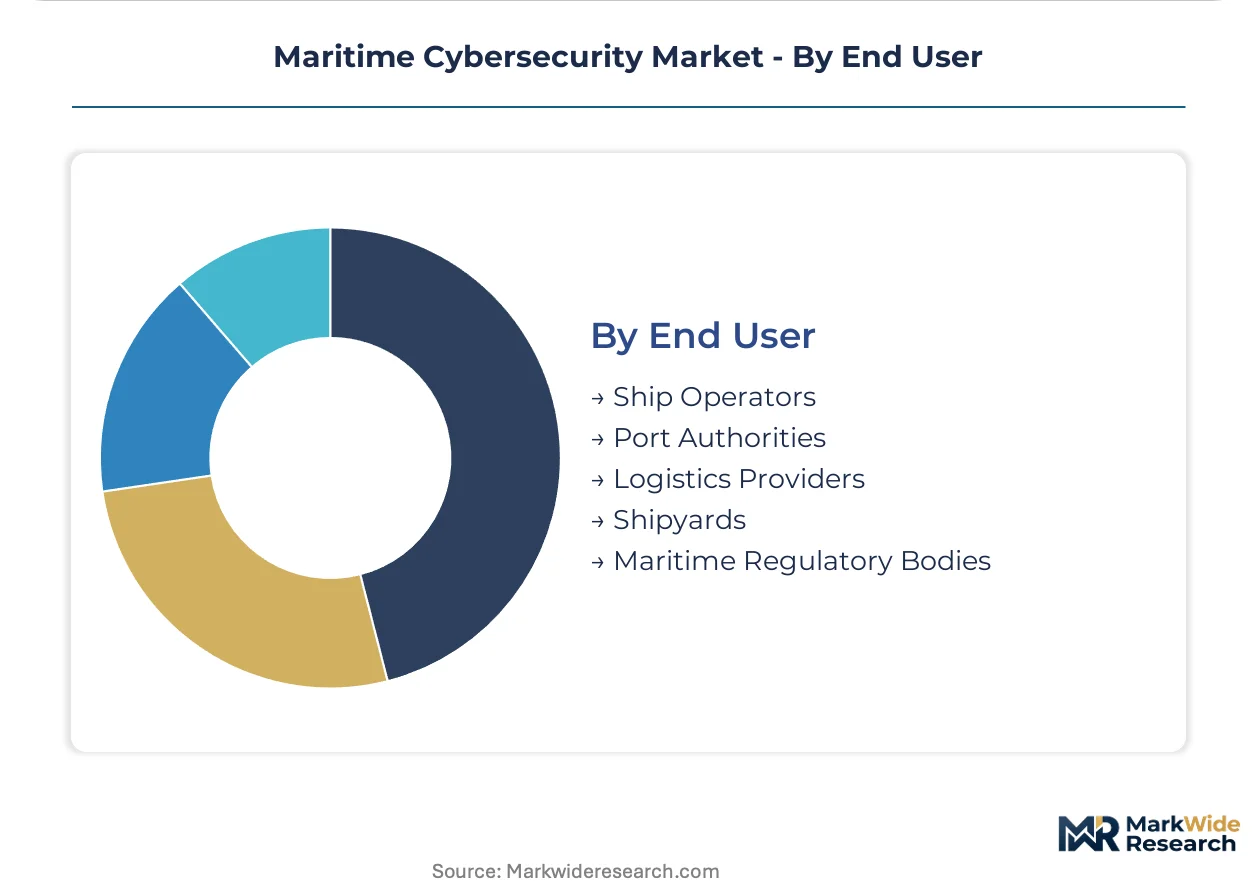
End user segmentation reflects divergent procurement authority across vessel ownership, port administration, and regulatory enforcement layers.
- Ship Operators:Container lines, tanker owners, and bulk carriers implementing fleet-wide cyber risk management. Classification societies including ABS Group now embed cyber resilience into vessel certification frameworks, forcing procurement checklists to prioritize integrated platforms over point solutions.
- Port Authorities:Terminal operators and harbor masters securing critical infrastructure. The US Coast Guard's maritime security regulations mandate systematic risk assessment, directly shaping vendor product roadmaps for this customer segment.
- Logistics Providers:Freight forwarders and third-party logistics firms securing cargo documentation chains.
- Shipyards:Newbuild construction and retrofit installation of cyber defense systems.
- Maritime Regulatory Bodies:Flag states and classification societies procuring audit and certification tools.
Ship Operators account for the dominant procurement volume, while Port Authorities are climbing the fastest as EU NIS2 and US Coast Guard mandates tighten compliance requirements.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Port of Rotterdam's terminal automation systems anchor Europe's maritime cybersecurity procurement intensity, while Singapore's transshipment dominance drives Asian fleet digitization investment. Classification society headquarters in Oslo and Hamburg shape regulatory technology adoption patterns across their respective flag-state networks.
Norway
Autonomous vessel trials in Norwegian waters generate specialized demand for AI-driven navigation security without human intervention. The Norwegian Maritime Authority enforces cyber resilience certification through DNV's classification framework. Kongsberg's maritime technology cluster in Kongsberg and Oslo concentrates OT-IT integration engineering talent for fleet-wide risk management platforms.
United States
The Port of Long Beach's cargo volume drives West Coast terminal operators toward integrated IT-OT governance dashboards. The US Coast Guard's maritime security regulations mandate systematic risk assessment and incident reporting for critical port infrastructure. Houston's energy shipping corridor concentrates demand for tanker fleet cyber defenses protecting cargo documentation and navigation systems.
Germany
Port authorities in Hamburg and Bremerhaven must demonstrate supply chain resilience under the EU NIS2 Directive's technical and organizational measures. The country's national cybersecurity regulator BSI extends critical infrastructure standards to terminal operating systems and cargo handling equipment interfaces. The maritime technology cluster in Hamburg anchors development of shore-to-ship network protection contracts for container lines.
Singapore
The Maritime and Port Authority's cybersecurity standards compel transshipment operators to adopt fleet-wide monitoring solutions across high-frequency Asia-Europe routes. Mid-size container operators migrate to cloud-based security platforms to satisfy charterer audit demands while avoiding capital expenditure. The city-state's position as a flag registry concentrates procurement for vessel certification compliance tools.
United Kingdom
Thames port automation and North Sea offshore vessel operations drive demand for satellite communication protection against spoofing and jamming attacks. The UK Maritime and Coastguard Agency implements cybersecurity guidelines aligned with IMO 2021 frameworks. London's maritime insurance market conditions coverage on demonstrated cyber resilience documentation from classification societies.
Maritime Cybersecurity Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream supplying encryption modules and anomaly detection engines. The vendor base organizes around three strategic archetypes: satellite communications providers bundling managed security services, classification societies embedding cyber resilience into certification workflows, and OT-specific defenders differentiating from generic enterprise tools. Consolidation pressure favors integrated platform vendors over point-solution providers as procurement checklists prioritize single-dashboard visibility. Partnership velocity between satellite operators and vessel IT integrators exceeds acquisition activity in this compliance-driven market.
Within the defense-grade encryption tier, Thales Group anchors sovereign capability extension into commercial shipping channels. Fortinet occupies a position exemplifying firewall appliance ecosystems anchoring shore-to-ship network protection contracts. Naval Dome represents the OT-specialist archetype differentiating maritime-specific defenses from generic enterprise security tools.
| Leading Market Players |
|---|
| Marlink SAS |
| Fortinet |
| Naval Dome |
| Cydome Security |
| CyberOwl |
| ABS Group of Companies |
| Waterfall Security Solutions |
| Kongsberg Gruppen |
| Thales Group |
| Others |
Pricing and Supply Chain Analysis
The Asia-Europe container corridor's satellite bandwidth economics concentrate procurement power among fleet operators above two thousand TEU capacity, compressing margins for cybersecurity vendors while forcing three-tier differentiation across managed service tiers.
Pricing Analysis
Volume-discount tiering structures dominate maritime cybersecurity procurement, with container lines negotiating fleet-wide subscriptions that stratify across IMO 2021 compliance grade, threat intelligence sophistication, and shore-based SOC response time. Price differentiation hinges on classification society certification level and satellite connectivity redundancy, with DNV-certified platforms commanding premium positioning. Cost compression in the mid-market tier is intensifying because mid-size operators are consolidating vendor relationships to satisfy charterer audit demands. Bulk carriers and tanker fleets exhibit highest price sensitivity due to thinner operating margins, while cruise operators and autonomous vessel developers demonstrate lowest sensitivity given safety-critical navigation requirements.
Supply Chain Analysis
Tariff exposure between the United States and China dominates component sourcing risk for maritime cybersecurity hardware, particularly affecting firewall appliance and encryption module procurement. Manufacturing concentrates in Taiwan, Israel, and the United States for specialized maritime OT security components. The supply chain draws from proprietary navigation system interfaces, sovereign-grade encryption chipsets, and low-earth orbit satellite transceivers. Single-source vulnerability persists in classification society certification workflows, where DNV, ABS, and Lloyd's Register control market access gating. Distribution runs through vessel IT integrators and satellite communications providers bundling managed security services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Maritime cybersecurity functions as a defensive-moat market where regulatory entrenchment creates durable competitive positions through classification society certification requirements that lock in vendor relationships across vessel renewal cycles.
For Market Incumbents: Entrench market position by embedding OT-specific anomaly detection deeper into Kongsberg and Wärtsilä navigation system architectures, creating switching costs that resist generic enterprise security vendors. Acquire specialized talent in Norway's maritime technology cluster to address the recruitment bottleneck threatening service expansion. Prioritize certification timeline acceleration with DNV and ABS to capture fleet renewal programs ahead of compliance deadlines. For New Entrants and Emerging Players: Mid-size container operators in Singapore and Southeast Asian transshipment hubs represent the most penetrable entry point, as these fleets seek cloud-based security platforms to avoid capital expenditure while satisfying EU NIS2-aligned charterer demands. Autonomous vessel trial participants in Norwegian waters offer a second white-space target requiring AI-driven navigation security without human intervention. A channel partnership strategy with regional satellite communications providers enables rapid market access without direct fleet sales infrastructure. For Investors and Strategic Acquirers: Carve-out targets emerge from defense contractors seeking to monetize non-core maritime encryption capabilities, particularly those with existing Thales Group or national sovereign security relationships. Long-term viability centers on platforms achieving classification society certification integration, as this regulatory entrenchment determines scalable adoption. Monitor divergence between EU port state control enforcement rigor and open-registry implementation gaps as the critical inflection signal for which solution architectures achieve dominant design status.| Strategic Initiative | Industry Significance |
|---|---|
| Classification Society Certification Integration | DNV and ABS cyber resilience frameworks condition market access on vendor platform compliance. |
| OT-Specific Threat Intelligence Development | Maritime-focused AIS spoofing and GPS jamming signatures differentiate from generic enterprise tools. |
| Satellite Communications Partnership | Low-earth orbit providers bundling managed security services capture shore-to-ship network contracts. |
| Autonomous Vessel Security Platform | AI-driven anomaly detection for unmanned navigation systems secures Norwegian trial program participation. |
| Cloud-Based Managed Security Service | Subscription models eliminate capital expenditure barriers for mid-size Singapore-flagged operators. |
Research Methodology
Two parallel data streams informed the analysis: primary interviews with fleet cybersecurity officers, port authority IT directors, classification society technical auditors, and satellite communications procurement leads; and secondary validation through IMO regulatory filings, EU NIS2 directive implementation guidance, US Coast Guard maritime security bulletins, and vessel classification database records. Bottom-up triangulation across fleet deployment estimates and top-down reconciliation against aggregate maritime technology expenditure patterns ensured cross-verified outputs.
Forecast inputs span solution type segmentation across network security and threat intelligence, deployment mode differentiation between managed services and cloud-based platforms, application coverage from navigation systems to port facility security, and end-user categorization across ship operators and port authorities. CAGRs were derived through regression analysis of historical procurement patterns against regulatory mandate timelines, incorporating satellite connectivity expansion curves and autonomous vessel trial progression as maritime-specific demand drivers.
Stress conditions across flag-state enforcement variance, legacy OT retrofit cost inflation, and specialized talent availability were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions regarding IMO 2021 guideline adoption rates and EU NIS2 directive harmonization timelines. Material shifts in classification society certification workflow standardization or sovereign encryption export control regimes would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.