
 Vehicle Cybersecurity Market | 2026-2036
Vehicle Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Vehicle Cybersecurity Market Insights
The automotive software supply chain is fragmenting as tier-1 suppliers, semiconductor vendors, and specialized cybersecurity firms compete for architecture control. Bosch Group anchors its position through deep integration of hardware security modules with braking and steering domains. Harman International differentiates via over-the-air update platforms that embed continuous threat monitoring. NXP Semiconductors dominates the secure element segment, supplying tamper-resistant chips to multiple OEM programs.
Vehicle cybersecurity encompasses the hardware, software, and protocols that protect electronic control units, in-vehicle networks, and external connectivity interfaces from unauthorized access, manipulation, or disruption. The discipline relies on cryptographic key lengths of 256 bits for symmetric encryption and hardware-backed root-of-trust implementations to ensure functional safety coexists with data protection. Intrusion Detection systems command the largest technology share as OEMs mandate real-time anomaly monitoring across CAN and Ethernet backbones. Cloud deployment architectures are expanding fastest among fleet management applications where centralized security operations centers monitor thousands of vehicles simultaneously.
The UNECE WP.29 R155 regulation and ISO/SAE 21434 standard together mandate formal cybersecurity management systems across vehicle lifecycles, compelling OEMs and suppliers to restructure development processes and procurement criteria. NHTSA guidance in the United States and type-approval requirements from Germany's KBA create parallel compliance obligations that shape regional product roadmaps. Stakeholders must monitor how edge computing architectures redistribute security processing loads between vehicle gateways and cloud infrastructure as autonomous driving functions mature.
Market Dynamics
The proliferation of software-defined vehicle architectures is compressing development cycles while expanding the attack surface across electronic control units, forcing automotive supply chains to embed security-by-design principles into hardware procurement specifications.
Growth Catalysts
- UNECE WP.29 R155:This regulation mandates cybersecurity management systems for new vehicle types, compelling OEMs and tier-1 suppliers to restructure development processes and procurement criteria across European markets.
- Over-the-air update infrastructure:Fleet operators and passenger vehicle OEMs are deploying continuous software delivery pipelines that require persistent threat monitoring and cryptographic verification at every update cycle.
- Centralized security operations centers:Large commercial fleet managers in Germany are consolidating real-time monitoring across thousands of vehicles, creating concentrated demand for cloud-native intrusion detection platforms.
Market Restraints
- Semiconductor supply concentration:Secure element manufacturing for hardware security modules clusters among a limited set of foundry capabilities, creating vulnerability to capacity constraints.
- Legacy CAN bus architectures:Older in-vehicle networks lack native encryption or authentication protocols, forcing expensive retrofitting or gateway-based mediation that increases bill-of-materials complexity.
- Skill scarcity in automotive cryptography:The intersection of functional safety engineering and cryptographic implementation requires specialized expertise that remains concentrated among a small pool of qualified practitioners.
Strategic Opportunities
- Edge computing redistribution:Autonomous driving functions are migrating security processing loads from cloud infrastructure to vehicle gateways, creating demand for high-performance onboard cryptographic accelerators.
- ISO/SAE 21434 certification services:Third-party assessment and audit capabilities for cybersecurity management systems represent an emerging services layer as OEMs seek external validation.
- India's automotive software ecosystem:Engineering centers in Bangalore and Pune are expanding their role in security architecture design for global platforms, offering cost-competitive development resources.
Industry Challenges
- Functional safety integration:Combining ISO 26262 safety requirements with cybersecurity controls creates verification complexity that extends development timelines and testing costs.
- Multi-stakeholder liability allocation:Tier-1 suppliers, semiconductor vendors, and software providers dispute responsibility boundaries for security incidents, complicating contract structuring and insurance placement.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Vehicle Cybersecurity Market |
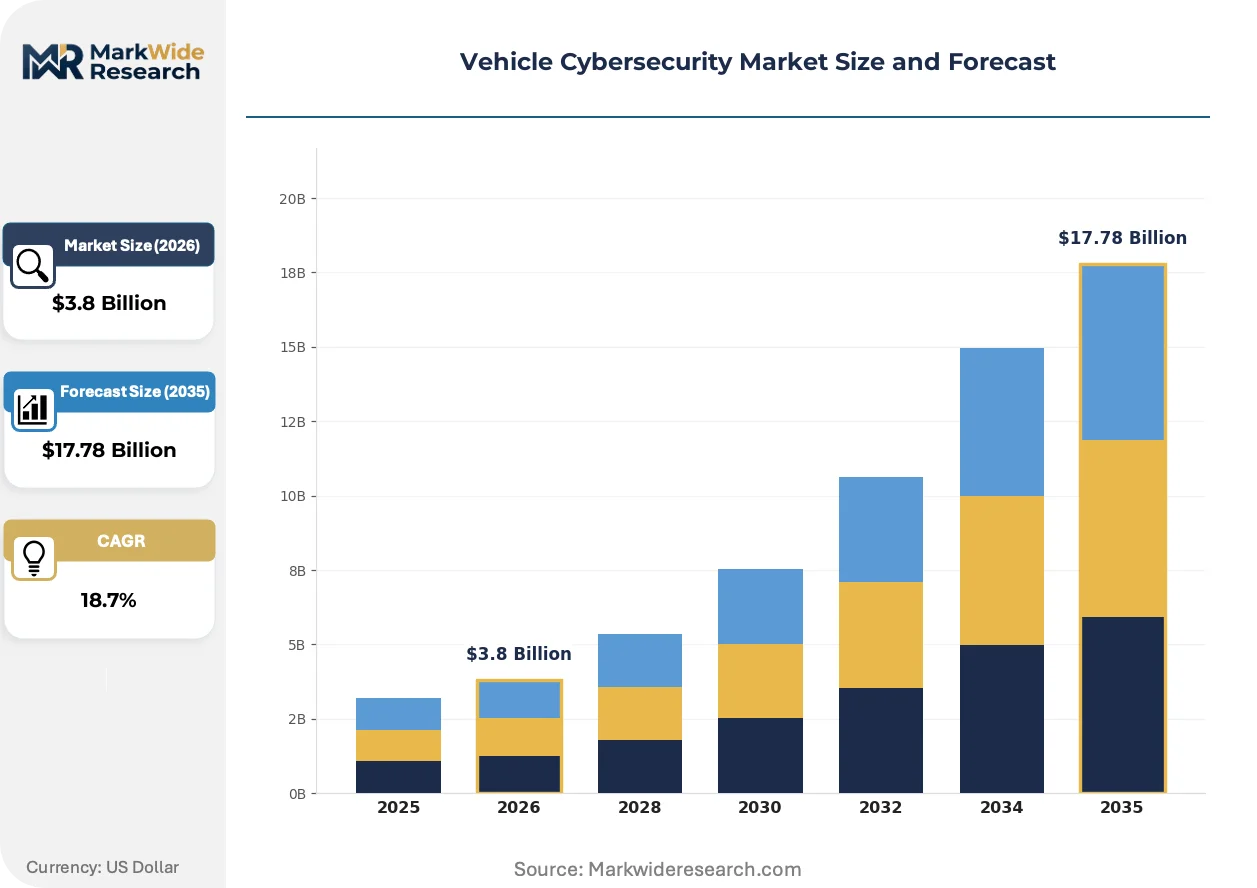
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.78 Billion |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Intrusion Detection, Firewall, Encryption, Authentication Application: Connected Cars, Autonomous Vehicles, Fleet Management, Electric Vehicles End User: OEMs, Tier-1 Suppliers, Aftermarket Providers, Regulatory Bodies Deployment: On-Premise, Cloud, Hybrid, Edge Computing |
| Companies Covered | Argus Cyber Security, Harman International, NXP Semiconductors, Continental AG, Bosch Group, GuardKnox, Infineon Technologies, Vector Informatik, Karamba Security, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Vehicle Cybersecurity Market Trends and Innovations
Automotive cybersecurity is pivoting from perimeter defense to distributed trust architectures as vehicle software stacks grow more complex and update frequencies accelerate from annual to weekly cycles.
Hardware security modules are virtualizing key storage and cryptographic operations that previously required dedicated silicon, enabling OEMs to consolidate security functions onto fewer specialized chips. Tier-1 suppliers are adopting software-based trusted execution environments to reduce dependency on discrete secure elements. This virtualization is compressing the secure element supplier base while expanding the addressable market for security software licensing.
Germany's KBA has aligned type-approval requirements with UNECE WP.29 R155 implementation timelines, creating compliance urgency that accelerates procurement of certified cybersecurity management systems. OEMs serving European markets must demonstrate formal risk assessment documentation before receiving vehicle approvals. The certification burden falls most heavily on mid-volume manufacturers lacking in-house regulatory affairs capabilities, driving demand for external consulting and tooling platforms.
Fleet procurement teams are consolidating vendor relationships and demanding unified security operations dashboards that span multiple vehicle platforms and model years. Traditional point-solution cybersecurity vendors face displacement by integrated platform providers offering end-to-end monitoring, incident response, and compliance reporting. This concentration is most visible in Germany, where centralized fleet management functions at commercial vehicle operators have standardized on single-vendor security operations center architectures.
Vehicle Cybersecurity Market Segmentation
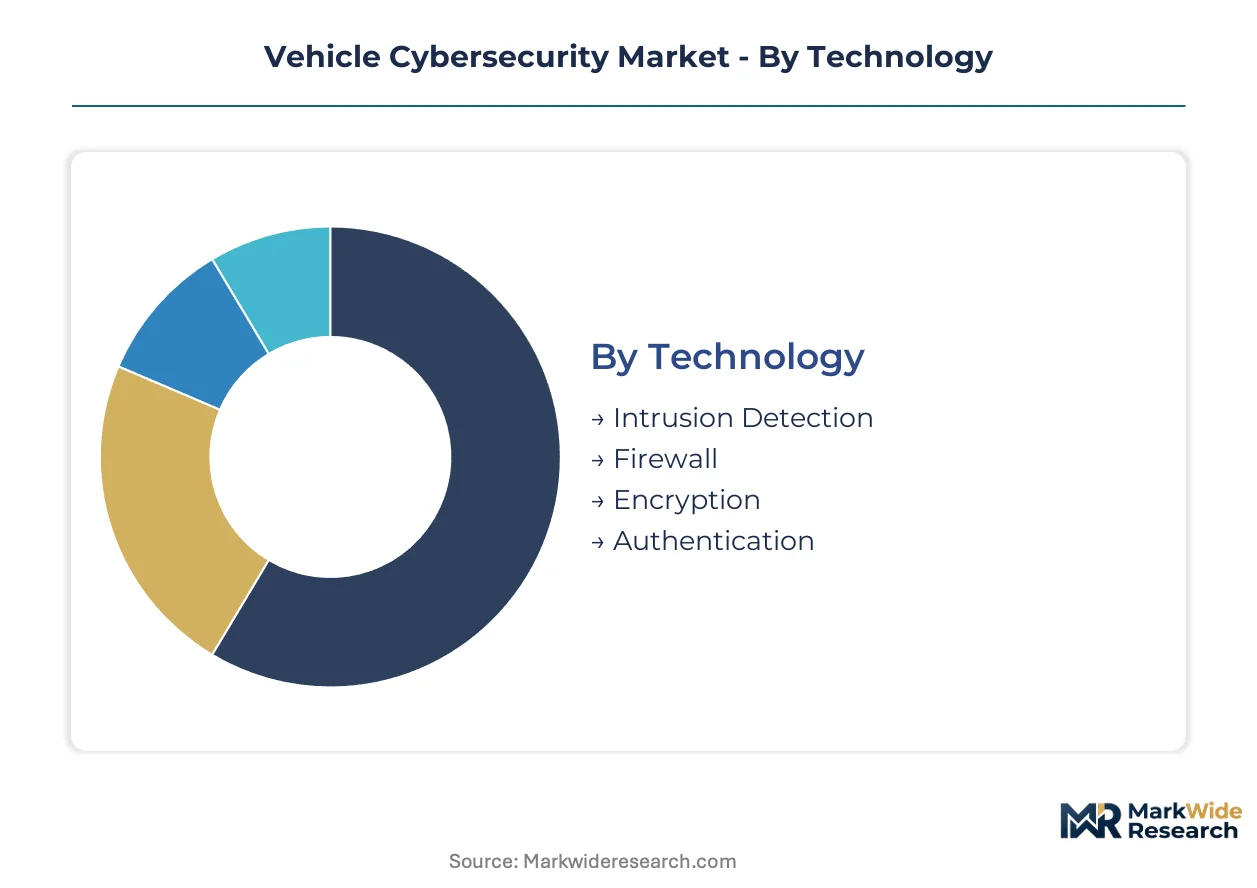
Vehicle cybersecurity architectures demand precise segmentation matching protection layers to threat surfaces across electronic control units, external interfaces, and fleet operations. Each dimension reveals distinct procurement patterns, technology requirements, and compliance obligations that reshape competitive positioning across the automotive supply chain.
Technology:
The use-case spectrum spans real-time threat detection through cryptographic protection, with each technology addressing specific vulnerability classes in connected vehicle architectures.
- Intrusion Detection:Real-time anomaly monitoring systems analyze CAN bus and Ethernet traffic patterns to identify unauthorized access attempts. OEMs in Germany mandate these systems for type-approval under KBA requirements, with fleet operators demanding centralized dashboards spanning thousands of vehicles.
- Firewall:Network segmentation gateways enforce policy-based traffic filtering between vehicle domains and external connectivity interfaces. Tier-1 suppliers integrate these into central gateway modules to satisfy UNECE WP.29 R155 boundary protection requirements.
- Encryption:Symmetric and asymmetric cryptographic protocols protect data transmission across V2X interfaces and over-the-air update channels.
- Authentication:Hardware-backed identity verification ensures only authorized entities access safety-critical vehicle functions.
Established volume favors Intrusion Detection; emerging adoption favors Encryption.
Application:
Cost tier differentiation separates premium integrated platforms from modular point solutions across vehicle categories.
- Connected Cars:Infotainment and telematics integration creates persistent external attack surfaces requiring continuous monitoring. European OEMs specify unified security architectures spanning multiple model generations to amortize certification costs.
- Fleet Management:Commercial vehicle operators consolidate security operations across heterogeneous fleets, demanding cloud-native platforms with centralized incident response capabilities.
- Autonomous Vehicles:Safety-critical perception and decision systems require deterministic security processing with minimal latency overhead.
- Electric Vehicles:Battery management and charging infrastructure interfaces introduce specialized protection requirements for high-voltage systems.
Deployment scale concentrates in Connected Cars; steepest expansion trajectory appears in Fleet Management.
End User:
Customer type determines procurement authority, with specification-setting power cascading from OEM headquarters through tiered supply chains.
- OEMs:Vehicle manufacturers define platform-wide security architectures and mandate compliance across supplier networks. German OEMs drive global specifications through engineering center influence.
- Tier-1 Suppliers:Integrated module providers embed security functions into braking, steering, and gateway domains, consolidating multiple protection layers.
- Aftermarket Providers:Retrofit solutions address legacy fleet vehicles lacking native cybersecurity capabilities.
- Regulatory Bodies:Type-approval authorities validate cybersecurity management system documentation before market entry.
Procurement authority concentrates with OEMs; implementation burden falls heaviest on Tier-1 Suppliers.
Deployment:
Supply concentration in semiconductor manufacturing shapes deployment architecture tradeoffs between onboard processing and cloud dependency.
- Cloud:Centralized security operations centers aggregate telemetry from thousands of vehicles for pattern analysis and threat intelligence. Fleet operators in Germany standardize on cloud-native architectures for multi-platform visibility.
- Edge Computing:Vehicle-side processing reduces latency for autonomous driving functions while limiting data exposure. NHTSA guidance encourages localized security decision-making for safety-critical systems.
- On-Premise:Dedicated infrastructure within OEM or fleet operator data centers addresses data sovereignty requirements.
- Hybrid:Tiered processing distributes routine monitoring to cloud infrastructure while reserving sensitive operations for onboard execution.
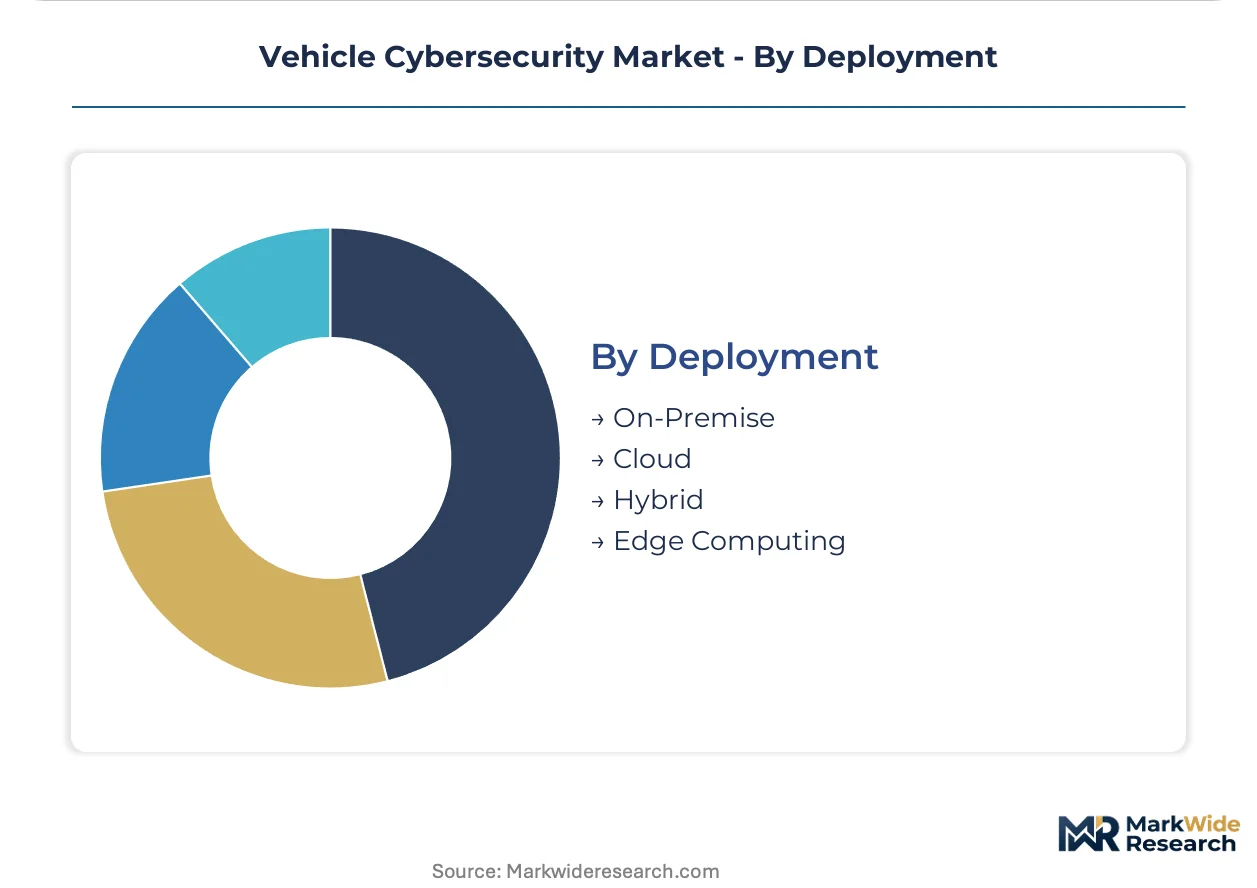
Current procurement favors Cloud; autonomous driving maturation is accelerating Edge Computing adoption.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Germany commands pricing power through OEM specification-setting authority, while India's engineering centers capture cost-advantaged development work without equivalent pricing leverage.
United States
NHTSA guidance on vehicle cybersecurity and autonomous driving safety creates compliance pressure across Detroit's engineering corridors. The regulator mandates localized security decision-making for safety-critical systems. Michigan's automotive cluster concentrates tier-1 supplier headquarters where procurement specifications for intrusion detection systems originate.
Germany
KBA type-approval requirements aligned with UNECE WP.29 R155 accelerate certified cybersecurity management system procurement. The country's national automotive regulator enforces formal risk assessment documentation before market entry. Stuttgart and Munich engineering centers drive global platform security architectures for multiple OEM programs.
China
MIIT standards for connected vehicle security and data localization reshape domestic cybersecurity requirements. The ministry's GB standards mandate cryptographic protocols for V2X interfaces and over-the-air update channels. Shanghai and Beijing automotive software clusters expand security architecture design capabilities for both domestic and export programs.
Japan
METI initiatives on automotive cybersecurity and software-defined vehicles redirect supplier investment toward secure element manufacturing. The ministry's policy frameworks encourage hardware-backed root-of-trust implementations. Nagoya's Chubu region concentrates tier-1 module production where braking and steering domain security integration occurs.
India
Automotive PLI scheme incentives attract cybersecurity software development for global vehicle platforms. The government's production-linked incentive program supports engineering services expansion. Bangalore and Pune technical centers deepen their role in security architecture specification for international OEM programs.
Vehicle Cybersecurity Market Competitive Landscape
Integrated module suppliers and specialized cybersecurity firms split the market between hardware-anchored and software-native protection approaches. Tier-1 automotive suppliers consolidate security functions into braking, steering, and gateway domains, while semiconductor vendors dominate secure element supply. Two archetypes predominate: diversified industrial conglomerates with captive automotive divisions, and pure-play cybersecurity specialists targeting fleet management applications. Competitive moves concentrate on strategic partnerships between chip vendors and tier-1 integrators, plus technology licensing agreements that embed security stacks into broader vehicle platforms.
Among diversified industrial groups, Bosch Group and Continental AG exemplify the integrated module supplier archetype, anchoring positions through deep hardware-software co-design capabilities. Harman International occupies a distinct tier as an audio and connectivity specialist that has extended into over-the-air update platforms with embedded threat monitoring. These three represent divergent strategic postures: captive vertical integration, tier-1 systems integration, and infotainment-centric security extension.
| Leading Market Players |
|---|
| Argus Cyber Security |
| Harman International |
| NXP Semiconductors |
| Continental AG |
| Bosch Group |
| GuardKnox |
| Infineon Technologies |
| Vector Informatik |
| Karamba Security |
| Others |
Pricing and Supply Chain Analysis
Rotterdam-Antwerp corridor freight costs compress margins for hardware security module shipments from European foundries, amplifying price differentiation between certified Tier-1 integrated platforms and modular point solutions while fleet procurement consolidation intensifies volume-based negotiation leverage.
Pricing Analysis
The customization-premium spread spans three-to-five-fold between configured-to-order cybersecurity management systems and standard intrusion detection modules. Subscription-based SaaS pricing dominates fleet management applications, while per-unit transactional models govern OEM hardware procurement. Price differentiation hinges on ISO/SAE 21434 certification grade and volume scale, with mid-volume manufacturers facing acute cost compression due to amortization disadvantages. Pricing pressure stems from semiconductor foundry capacity constraints, though tier-1 suppliers with captive integration maintain margin insulation. Fleet operators exhibit highest price sensitivity; autonomous vehicle programs demonstrate lowest sensitivity due to safety-critical requirements.
Supply Chain Analysis
Contract manufacturing concentration at TSMC, Samsung Foundry, and GlobalFoundries anchors secure element production for hardware security modules. Geographic supply concentrates in Taiwan, South Korea, and Germany, with advanced node fabrication drawing from concentrated foundry capacity. Raw material dependencies span silicon wafers, rare earth elements for tamper-resistant packaging, and specialized substrates for automotive-grade reliability. Single-source vulnerability pervades sub-7nm cryptographic accelerator production. Distribution runs through tier-1 supplier integration channels rather than direct OEM procurement, with Bosch and Continental consolidating security functions into braking and gateway domains.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fleet operator procurement consolidation into centralized security operations centers has shifted buyer power toward volume aggregators, fragmenting vendor pricing power across heterogeneous vehicle platforms.
For Market Incumbents: Entrench platform dominance through deeper hardware-software co-design in braking and steering domains, while accelerating ISO/SAE 21434 certification tooling to capture mid-volume manufacturer compliance demand. Threat from pure-play cybersecurity specialists with cloud-native architectures demands preemptive response. Vertical integration into secure element sourcing mitigates foundry capacity risk. For New Entrants and Emerging Players: India's automotive software ecosystem offers underpenetrated engineering services expansion, with Bangalore and Pune technical centers deepening security architecture roles for global platforms. Fleet management SaaS represents the most penetrable segment given procurement team demands for unified multi-platform dashboards. Go-to-market through OEM regulatory consulting partnerships accelerates credibility establishment. For Investors and Strategic Acquirers: UNECE WP.29 R155 full enforcement reshapes the acquisition landscape toward certified cybersecurity management system providers with documented KBA approval track records. Long-term viability centers on regulatory compliance automation capabilities rather than point-solution threat detection. Target acquisition archetype: mid-scale specialists with ISO/SAE 21434 audit tooling and existing tier-1 supplier relationships. Signal to watch: edge computing security processing load redistribution patterns as autonomous driving functions mature.| Strategic Initiative | Industry Significance |
|---|---|
| Hardware Security Module Virtualization | TSMC advanced packaging enables consolidation of discrete secure elements onto fewer specialized chips. |
| ISO/SAE 21434 Certification Tooling Investment | Mid-volume OEMs lacking in-house regulatory capabilities drive external audit platform demand. |
| Edge Computing Cryptographic Accelerator Development | NHTSA guidance encourages localized security decision-making for autonomous vehicle safety systems. |
| Centralized Security Operations Center Platform Launch | German fleet operators standardize on single-vendor architectures spanning multi-model-year fleets. |
| India Engineering Center Capability Expansion | Automotive PLI scheme incentives attract cost-competitive security architecture design for global programs. |
Research Methodology
Two parallel data streams informed the analysis: structured primary interviews with OEM platform engineers, tier-1 supplier procurement leads, fleet operations managers, and automotive regulatory affairs specialists; and secondary validation against UNECE WP.29 documentation, KBA type-approval filings, NHTSA guidance publications, and vehicle production databases from IHS Markit. Bottom-up triangulation across supplier revenue disclosures and top-down demand modeling from connected vehicle shipment forecasts ensured cross-verification.
Forecast inputs span technology adoption curves across intrusion detection, encryption, and authentication segments; application penetration in connected cars, fleet management, autonomous vehicles, and electric vehicles; and deployment architecture shifts between cloud, edge computing, and hybrid models. CAGRs derive from segment-level growth rate synthesis applied across the projection horizon. Industry-specific inputs include UNECE WP.29 R155 compliance timeline acceleration and semiconductor foundry capacity expansion trajectories.
The forecast holds incumbent behavior within observed patterns; aggressive moves by cloud-native cybersecurity specialists or foundry capacity expansions beyond projected timelines would shift outcomes. Quarterly review of KBA type-approval processing volumes, tier-1 supplier security module procurement announcements, and fleet operator security operations center vendor selections is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Global Counter IED Market
Defense Cybersecurity
Blockchain Technology in Aerospace and Defense Market
Defense Cybersecurity
Asia-Pacific Missiles and Missile Defense Systems Market
Defense Cybersecurity
Defence Cybersecurity Market
Defense Cybersecurity
Electronic Warfare Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Electronic Countermeasures Market
Defense Cybersecurity
Railway Cyber Security Market
Defense Cybersecurity
Maritime Cybersecurity Market
Defense Cybersecurity
Cyber Weapons Market
Defense Cybersecurity
High Energy Lasers Market
Defense Cybersecurity
Aviation Cyber Security Market
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Europe Automotive Cybersecurity Market
Defense Cybersecurity
Ballistics Targeting Software Market