
 Asia-Pacific Cyber Weapons Market | 2026-2036
Asia-Pacific Cyber Weapons Market Size, Share, and Industry Trends Forecast 2026-2036
Asia-Pacific Cyber Weapons Market Insights
Market Context
The gap between bespoke nation-state cyber arsenals and commercially available intrusion tools is recalibrating procurement strategies across the Asia-Pacific. Lockheed Martin leverages its classified R&D pipelines to sustain premium-tier contracts with sovereign buyers. BAE Systems anchors its regional position through deep integration with British Commonwealth defense networks. Cisco Systems competes on the commercial flank by extending enterprise security platforms that blur into dual-use cyber capability markets.
Technical Definition and Segment Structure
Asia-Pacific cyber weapons encompass software-based offensive systems engineered to exploit network vulnerabilities, disrupt adversary infrastructure, or exfiltrate intelligence through tailored payload delivery and command-and-control architectures. These tools incorporate zero-day exploit chains, polymorphic code structures, and stealth persistence mechanisms to evade detection during prolonged operations. Malware and ransomware segments under Threat Type dominate current procurement volumes, while AI-driven Solutions within the Technology dimension represents the fastest-expanding margin pool as autonomous targeting reduces operator attribution risk. Cloud-based and Hybrid deployment models are gaining share where militaries seek operational flexibility without fixed infrastructure exposure.
Regulatory Framework and Outlook
Japan's METI and Australia's Cyber Security Centre impose strict domestic controls on cyber weapon development and export, while China's MIIT and SAMR enforce data sovereignty rules that constrain cross-border capability sharing. India's CEA and defense procurement frameworks are formalizing indigenous cyber weapon standards under the PLI scheme for strategic electronics. Stakeholders must monitor how divergent national encryption backdoor mandates and critical infrastructure protection laws reshape vendor eligibility across bilateral defense agreements.
Market Dynamics
Zero-day exploit commodification is compressing development cycles across Asia-Pacific defense procurement, forcing sovereign buyers to accelerate refresh rates for offensive cyber arsenals while vendors scramble to differentiate through AI-augmented targeting systems.
Growth Catalysts
- India's PLI scheme for strategic electronics:Domestic manufacturing incentives are accelerating indigenous cyber weapon development under CEA and defense procurement frameworks, reducing import dependency for critical payload systems.
- Critical infrastructure protection mandates:Japan's METI guidelines and Australia's Cyber Security Centre are compelling energy and telecommunications operators to procure offensive counter-intrusion capabilities as defensive complements.
- Polymorphic code structures:Advancements in self-modifying malware architectures are enabling longer dwell times in adversary networks, driving procurement of next-generation persistence tools across regional military cyber commands.
Market Restraints
- Export control fragmentation:Divergent national encryption backdoor mandates between China's MIIT, Japan's METI, and Australia's domestic controls create compliance friction for cross-border capability transfers.
- Specialized talent scarcity:Shortage of operators proficient in both zero-day discovery and operational security protocols constrains deployment velocity for advanced persistent threat operations.
- Attribution technology costs:Stealth mechanism development requires sustained R&D expenditure in quantum-resistant communication layers, elevating total cost of ownership for sovereign buyers.
Strategic Opportunities
- Cloud-based deployment models:Hybrid infrastructure architectures are expanding operational flexibility for militaries seeking reduced fixed-asset exposure during contingency operations.
- AI-driven autonomous targeting:Machine learning inference at the edge is expanding into real-time vulnerability assessment, compressing decision cycles for time-sensitive offensive operations.
- Thailand and Vietnam defense modernization:Emerging procurement programs in Southeast Asian militaries present first-mover advantages for vendors establishing localized integration partnerships.
Industry Challenges
- Legacy system interoperability:Integration of modern exploit chains with decades-old command-and-control infrastructure in regional militaries demands costly middleware development.
- Operator certification timelines:Extended security clearance processes and specialized training pipelines delay operational deployment of procured capabilities by 18-24 months.
- Attribution risk management:Forensic countermeasures must continuously evolve against advancing behavioral analysis techniques employed by adversary threat intelligence units.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Asia-Pacific Cyber Weapons Market |
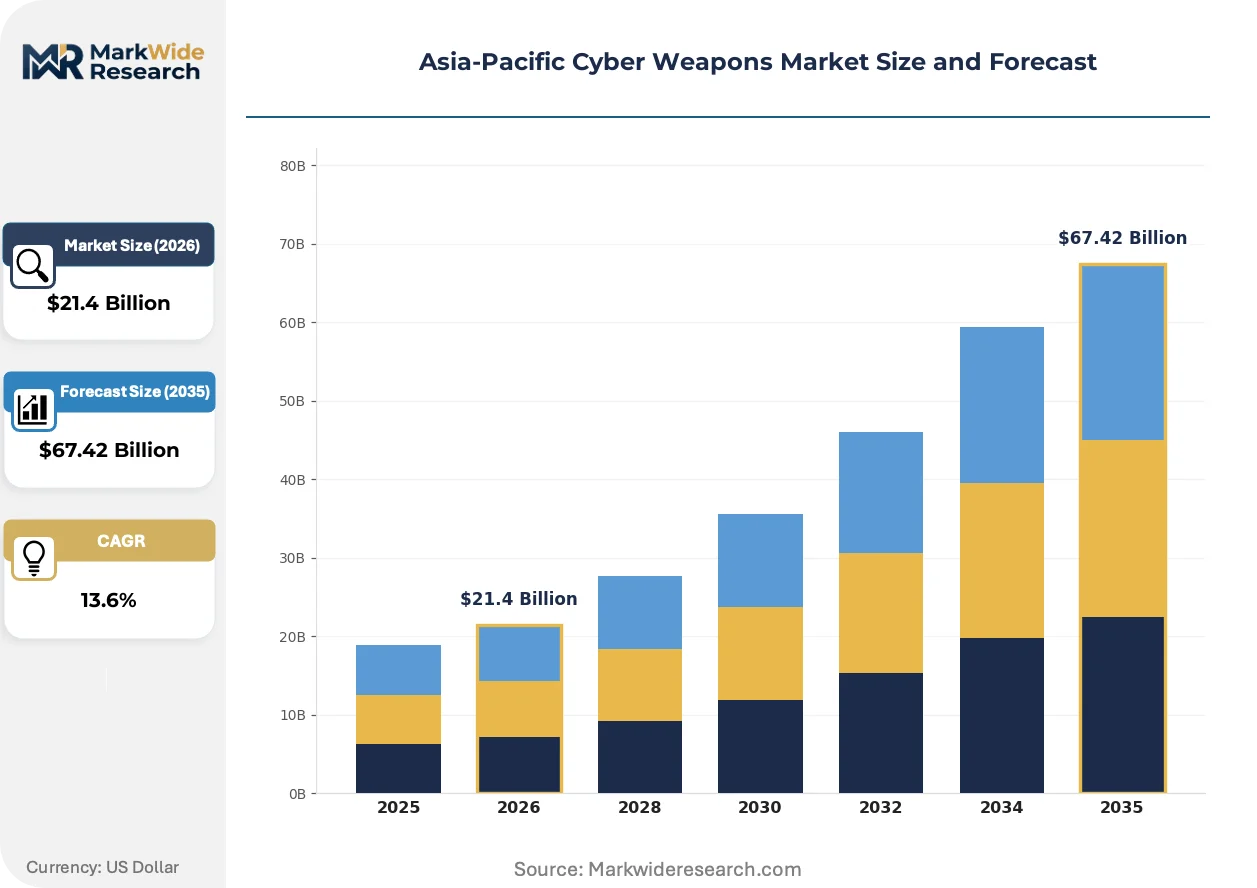
| Market Size in 2026 | $21.4 Billion |
| Market Size in 2035 | $67.42 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Threat Type: Malware, Ransomware, Phishing, DDoS Deployment Model: On-premises, Cloud-based, Hybrid, Managed Services End User: Government, Military, Private Sector, Critical Infrastructure Technology: AI-driven Solutions, Encryption Tools, Network Analysis, Threat Intelligence |
| Companies Covered | Lockheed Martin Corporation, BAE Systems, Raytheon Technologies Corporation, Northrop Grumman Corporation, General Dynamics Corporation, The Boeing Company, Cisco Systems, Booz Allen Hamilton Inc., FireEye Inc., Others |
| Regions Covered | Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Asia-Pacific Cyber Weapons Market Trends and Innovations
Autonomous targeting systems are recalibrating procurement specifications across Asia-Pacific defense agencies, shifting operator requirements from technical execution toward strategic oversight and legal compliance frameworks.
Large language model integration into malware generation pipelines is expanding into automated payload customization, enabling threat actors with limited technical expertise to produce tailored exploits. Regional military cyber commands are adopting these tools at accelerated procurement cycles, compressing the traditional vendor-customer development relationship. This capability diffusion is expanding into new market entrants previously excluded by technical barriers.
China's MIIT cybersecurity standards and SAMR data sovereignty rules are tightening cross-border data flow restrictions, forcing foreign vendors to establish localized development facilities. Industrial consequence includes segmented supply chains where code provenance must demonstrate domestic processing. Australian and Japanese defense procurement frameworks are responding with enhanced vendor nationality screening for critical payload components.
Subscription-based capability licensing is displacing perpetual ownership models in Australian and Indian defense procurement, aligning cyber weapon refresh cycles with operational technology upgrade timelines. Systems integrators are capturing margin through bundled training and attribution-risk insurance. This pattern is most visible in Australia's defense modernization programs, where multi-year enterprise agreements now dominate offensive cyber capability acquisition.
Asia-Pacific Cyber Weapons Market Segmentation
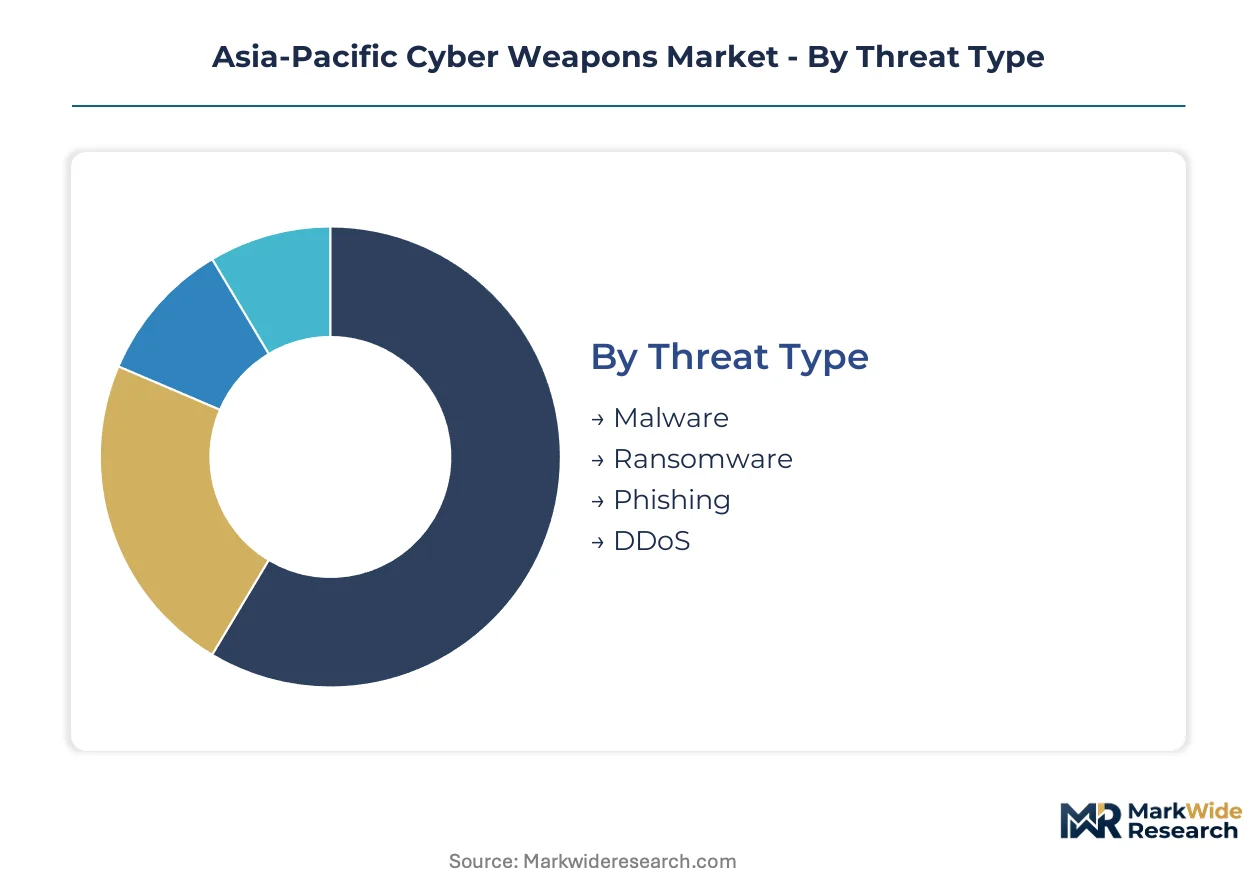
Segmentation in the Asia-Pacific cyber weapons market reveals how procurement priorities diverge across sovereign buyers, commercial operators, and defense integrators. Each dimension exposes distinct compliance burdens, deployment constraints, and capability thresholds that reshape vendor positioning.
Threat Type:
Malware and ransomware segments face Australia's Cyber Security Centre certification requirements for offensive deployment, while phishing and DDoS tools navigate lighter Japan METI disclosure thresholds.
- Malware:Polymorphic payload architectures with self-modifying code structures enable extended dwell times in adversary networks. Australia's defense modernization programs and India's military cyber command buildout are concentrating procurement for advanced persistent threat operations, driven by zero-day exploit commodification compressing development cycles.
- Ransomware:Encryption-based disruption tools with asymmetric key distribution mechanisms target critical infrastructure degradation. India's PLI scheme for strategic electronics is accelerating indigenous development under CEA oversight, reducing import dependency for payload delivery systems.
- Phishing:Social engineering platforms with credential harvesting modules.
- DDoS:Distributed denial-of-service tools leveraging botnet amplification.
Leading the category by volume: Malware. Growing fastest: Ransomware.
Deployment Model:
Cost tiers stratify sharply between capital-intensive on-premises installations and operational-expense-driven cloud subscriptions reshaping Australian and Indian procurement.
- On-premises:Fixed infrastructure deployment with dedicated hardware stacks and air-gapped command-and-control architectures. Japan's METI critical infrastructure guidelines impose strict physical security audits, elevating total cost of ownership for energy and telecommunications operators.
- Cloud-based:Elastic compute resources with distributed payload hosting and API-driven orchestration. Australia's defense modernization programs are expanding multi-year enterprise agreements, aligning refresh cycles with operational technology upgrades.
- Hybrid:Mixed architectures combining local processing with remote analytics.
- Managed Services:Vendor-operated platforms with bundled training and attribution-risk insurance.
Cloud-based deployment is climbing the fastest as militaries seek reduced fixed-asset exposure during contingency operations. On-premises retains dominance in classified environments.
End User:
Application intensity varies across sovereign defense networks, where government and military buyers demand sovereign code provenance, versus commercial operators prioritizing speed-to-deployment.
- Government:National intelligence agencies and civilian cyber commands procuring strategic offensive capabilities. China's MIIT cybersecurity standards enforce data sovereignty rules constraining cross-border capability sharing, forcing localized development facilities.
- Military:Unified combatant commands and service-specific cyber units requiring battlefield-integrated tools. India's defense procurement frameworks under the CEA are formalizing indigenous standards, accelerating domestic manufacturing incentives.
- Private Sector:Defense contractors and security firms with dual-use licensing.
- Critical Infrastructure:Energy, telecommunications, and financial operators under Japan's METI and Australia's Cyber Security Centre protection mandates.
Military end users command the steepest expansion trajectory. Government procurement maintains the largest committed volume.
Technology:
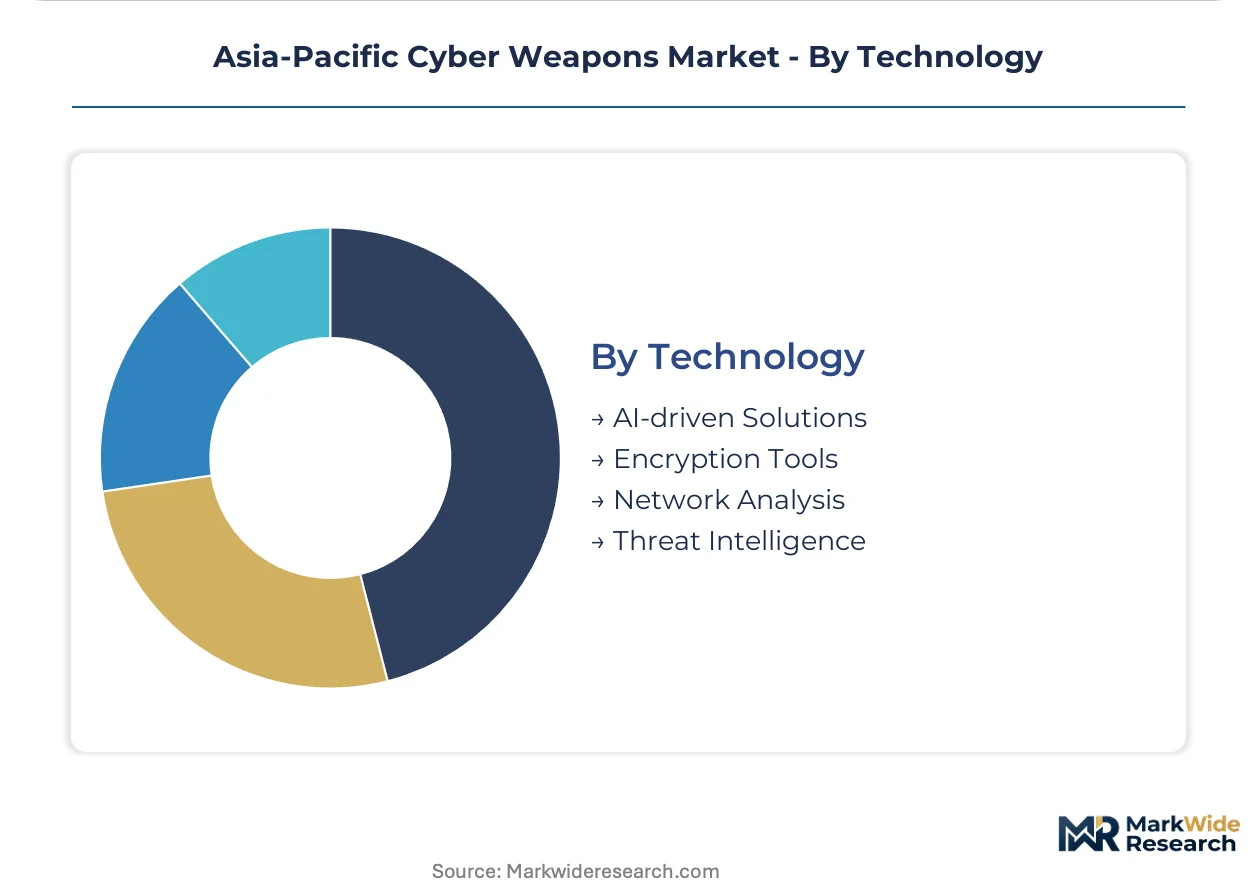
Margin concentration shifts toward autonomous systems as AI-augmented targeting reduces operator attribution risk and compresses decision cycles for time-sensitive operations.
- AI-driven Solutions:Machine learning inference engines for real-time vulnerability assessment and autonomous payload customization. Large language model integration is expanding automated exploit generation, enabling threat actors with limited technical expertise to produce tailored tools.
- Encryption Tools:Quantum-resistant communication layers and asymmetric key management systems. Sustained R&D expenditure in stealth mechanism development elevates total cost of ownership for sovereign buyers managing attribution technology costs.
- Network Analysis:Traffic inspection and behavioral profiling platforms.
- Threat Intelligence:Adversary tracking and indicator-of-compromise databases.
AI-driven Solutions is gaining share fastest. Encryption Tools retains the deepest incumbent footprint.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Singapore's Jurong Innovation District anchors Asia-Pacific cyber weapons R&D concentration, hosting classified development facilities for regional defense procurement networks.
China
Beijing-Tianjin-Hebei's defense technology corridor drives sovereign cyber arsenal expansion through MIIT cybersecurity standards enforcement. SAMR data sovereignty rules mandate localized code processing for foreign vendors. Shanghai's Zhangjiang Hi-Tech Park concentrates domestic payload engineering for military cyber commands.
Japan
Tokyo's defense industrial base accelerates offensive capability procurement under METI critical infrastructure guidelines. The country's national cybersecurity regulator imposes strict domestic controls on cyber weapon export and development licensing. Osaka-Kobe manufacturing clusters integrate dual-use cyber tools into maritime defense systems.
India
Bengaluru's technology corridor hosts indigenous cyber weapon development under CEA oversight and PLI scheme incentives for strategic electronics. Defense procurement frameworks formalize sovereign standards for military cyber command buildout. Hyderabad's defense research complex concentrates payload engineering talent for indigenous capability programs.
Australia
Canberra's defense establishment drives multi-year enterprise agreements for offensive cyber capability acquisition through the Cyber Security Centre certification regime. Critical infrastructure protection mandates compel energy and telecommunications operators toward counter-intrusion procurement. Melbourne's defense technology precinct integrates cloud-based deployment models for operational flexibility.
South Korea
Seoul Capital Area defense contractors expand AI-driven autonomous targeting procurement for military cyber units. The country's national cybersecurity framework tightens vendor eligibility screening for critical payload components. Busan-Ulsan industrial zones concentrate maritime cyber defense system integration.
Asia-Pacific Cyber Weapons Market Competitive Landscape
Capital-heavy producers compete with asset-light designers across tiered procurement channels. Sovereign defense agencies concentrate contracts among integrated systems houses with classified R&D pipelines, while commercial security platforms fragment across dual-use capability markets. Three archetypes dominate: classified defense primes with national security clearances, enterprise security vendors extending into offensive tooling, and specialized cyber consultancies bundling training with attribution-risk management. Competitive dynamics center on strategic partnerships with regional defense procurement frameworks and geographic expansion through localized development facilities.
Within the classified prime tier, Lockheed Martin Corporation and BAE Systems occupy positions shaped by deep integration with Commonwealth and allied defense networks. Raytheon Technologies Corporation represents the scale-driven archetype competing on multi-domain cyber capability portfolios. Cisco Systems sits within the commercial flank, exemplifying enterprise security platforms that blur into dual-use markets through operational technology upgrade alignment.
| Leading Market Players |
|---|
| Lockheed Martin Corporation |
| BAE Systems |
| Raytheon Technologies Corporation |
| Northrop Grumman Corporation |
| General Dynamics Corporation |
| The Boeing Company |
| Cisco Systems |
| Booz Allen Hamilton Inc. |
| FireEye Inc. |
| Others |
Pricing and Supply Chain Analysis
Sovereign-backed defense primes with classified R&D pipelines dominate supply-side ownership structures, compressing procurement timelines for zero-day exploit chains while elevating pricing discipline through sole-source contracting authority. Subscription licensing models now displace perpetual ownership across Australian and Indian defense modernization programs, tightening vendor cash conversion cycles.
Pricing Analysis
Outcome-linked pricing tied to operational uptime and mission success rates anchors contract structures for AI-driven autonomous targeting systems. Three-tier pricing structure across premium, standard, and economy levels separates bespoke nation-state arsenals from commercially adapted intrusion tools and training-only packages. Price differentiation rests on certification grade under Australia's Cyber Security Centre regime and sovereign code provenance requirements. Cost compression in commercial-flank segments intensifies as Cisco Systems and enterprise security vendors encroach on dual-use markets. Government and military buyers exhibit lowest price sensitivity, prioritizing attribution-risk reduction over procurement cost.
Supply Chain Analysis
Dual-sourcing mandates from Japan's METI and Australia's Cyber Security Centre compel vendors to qualify redundant payload engineering facilities across Singapore's Jurong Innovation District and Bengaluru's technology corridor. Geographic supply concentration centers on China for zero-day discovery talent, India for PLI-scheme manufacturing incentives, and Australia for cloud-based deployment infrastructure. Raw material dependencies include specialized semiconductor fabrication for quantum-resistant encryption layers, polymorphic code generation frameworks, and edge-computing hardware for autonomous targeting. Single-source vulnerability in classified R&D pipelines poses structural risk as sovereign buyers restrict cross-border capability sharing. Distribution runs through defense procurement frameworks with multi-year enterprise agreements dominating Australian and Indian channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical-integration races now define competitive positioning as vendors pursue backward control over zero-day discovery pipelines and forward integration into operator training ecosystems. Sovereign code provenance requirements accelerate captive development facility investments.
For Market Incumbents: To counter LLM-enabled malware generation commodifying exploit development, Lockheed Martin and BAE Systems must deepen classified R&D pipeline investments while securing exclusive operator certification partnerships with Australia's Cyber Security Centre. Capacity addition in Singapore's Jurong Innovation District preserves regional integration advantages against emerging cloud-native competitors. For New Entrants and Emerging Players: Begin with Thailand and Vietnam defense modernization programs where procurement frameworks remain underdeveloped and localized partnership requirements create entry barriers for established primes. Target cloud-based deployment models in Southeast Asian militaries seeking reduced fixed-asset exposure. Pursue bundled training and attribution-risk insurance offerings to differentiate from hardware-centric incumbents. For Investors and Strategic Acquirers: Distressed-cycle entries favor specialized cyber consultancies with sovereign security clearances in India and Australia where PLI scheme acceleration and Cyber Security Centre certification backlogs constrain organic growth. Long-term viability hinges on 5-10 year subscription licensing penetration replacing perpetual ownership models. Monitor India's CEA indigenous standard formalization as inflection indicator for import-dependent vendor displacement.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Day Pipeline Acquisition | Backward integration into exploit discovery reduces dependency on external researchers and accelerates refresh cycles. |
| Localized Development Facility | Establishing code engineering presence in Singapore or Bengaluru satisfies MIIT and CEA data sovereignty mandates. |
| Autonomous Targeting Platform Launch | Machine learning inference at the edge compresses decision cycles for time-sensitive offensive operations. |
| Multi-Year Enterprise Agreement | Subscription licensing with Australia's defense establishment aligns refresh cycles with operational technology upgrades. |
| Operator Certification Partnership | Bundled training programs with India's military cyber command accelerate deployment velocity and reduce clearance delays. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs for this analysis, cross-referenced with primary interviews involving defense procurement officers, cyber command technical directors, platform engineers, and systems integration specialists. Secondary sources included MIIT cybersecurity standard disclosures, CEA strategic electronics notifications, Australia's Cyber Security Centre certification registries, and defense ministry budget appropriations documents. Bottom-up segment sizing triangulated against top-down macroeconomic indicators ensured methodological consistency.
Granularity-level modeling deployed threat-type, deployment model, end-user, and technology dimensions at country-level resolution across the Asia-Pacific region. AI-driven Solutions and ransomware segments received discrete growth trajectory treatment given their divergent regulatory exposure. CAGRs derived from weighted average of historical procurement velocity and policy-mandated modernization timelines. Forecast inputs incorporated PLI scheme incentive trajectories, METI critical infrastructure protection mandate expansion, and cloud adoption curves in defense establishments.
Underlying measurement precision varies by segment; malware and on-premises deployment carry tighter precision given established procurement reporting, while AI-driven Solutions and cloud-based models face wider confidence intervals due to classification barriers. Forecasts reflect assumptions regarding sustained sovereign defense spending prioritization and stable bilateral technology transfer frameworks. Deviation in China's MIIT data sovereignty enforcement intensity or India's CEA standard formalization pace would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Defense Cybersecurity
Defence Cybersecurity Market
Defense Cybersecurity
Ballistics Targeting Software Market
Defense Cybersecurity
Asia-Pacific Defense Market
Defense Cybersecurity
Global C4I Systems Market
Defense Cybersecurity
Anti-Drone Defense System Market
Defense Cybersecurity
Maritime Cybersecurity Market
Defense Cybersecurity
Military Computers Market
Defense Cybersecurity
Military Sensors Cybersecurity Solutions Market
Defense Cybersecurity
Europe Cyber Weapons Market
Defense Cybersecurity
Europe Automotive Cybersecurity Market
Defense Cybersecurity
Global Handheld Counter IED Market
Defense Cybersecurity
Vehicle Cybersecurity Market
Defense Cybersecurity
Railway Cyber Security Market
Defense Cybersecurity
Asia-Pacific Missiles and Missile Defense Systems Market
Defense Cybersecurity
Electronic Countermeasures Market
Defense Cybersecurity
High Energy Lasers Market