
 Cloud Security Market | 2026-2036
Cloud Security Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Security Market Intelligence
Enterprise-grade zero-trust certification is redrawing competitive boundaries in cloud security procurement. Microsoft Corporation leverages its hybrid cloud footprint to anchor large government contracts. Palo Alto Networks specializes in network-centric security stacks that differentiate its platform in financial services verticals.
Cloud security encompasses the policies, controls, and technologies protecting data, applications, and infrastructure across distributed computing environments, with encryption standards typically requiring AES-256 or equivalent key management. Its primary purpose is ensuring confidentiality, integrity, and availability of resources hosted outside traditional perimeter defenses. Identity and access management solutions command the deepest margin pools as workforce decentralization strains credential governance. Hybrid cloud deployments represent the fastest-expanding segment as organizations straddle on-premises legacy systems with elastic public resources.
FDA guidelines for cloud-hosted healthcare data, EU GDPR cross-border transfer rules, and NIST cybersecurity frameworks collectively shape product roadmaps and market access requirements for vendors serving regulated industries. Compliance-driven procurement now filters vendor selection before technical evaluation begins. Stakeholders must weigh sovereign cloud mandates against the interoperability costs of region-fragmented security architectures.
Market Dynamics
Zero-trust architecture mandates from regulators across multiple jurisdictions are forcing infrastructure redesigns that reshape vendor selection criteria and procurement timelines.
Growth Catalysts
- GDPR Cross-Border Transfer Rules:EU data sovereignty requirements compel financial institutions to deploy region-locked encryption and key management systems.
- Industrial Cloud Adoption:German manufacturing compliance requirements intersect with operational technology security needs, accelerating specialized procurement cycles.
- Hybrid Cloud Deployments:Organizations straddling on-premises legacy systems with elastic public resources drive demand for unified security orchestration platforms.
Market Restraints
- Encryption Key Management Complexity:AES-256 equivalent standards require specialized hardware security modules that inflate deployment costs.
- Regulatory Fragmentation:Divergent FDA guidelines for healthcare data and NIST frameworks create compliance overhead that slows vendor certification.
- Skill Concentration:Identity and access management expertise clusters in specific metropolitan technology hubs, creating hiring bottlenecks.
Strategic Opportunities
- Sovereign Cloud Mandates:Japan's METI guidelines for data localization create openings for domestic-anchored security service providers.
- Healthcare Vertical Expansion:FDA cloud-hosted data guidelines are opening procurement channels for HIPAA-compliant encryption specialists.
- Convergence of SIEM and SOAR:Security information platforms merging with automated response tools are creating new platform categories.
Industry Challenges
- Zero-Trust Certification Timelines:Enterprise-grade validation processes extend sales cycles and strain vendor engineering resources.
- Legacy Perimeter Integration:Organizations with entrenched firewall architectures face technical debt when migrating to distributed security models.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Security Market |
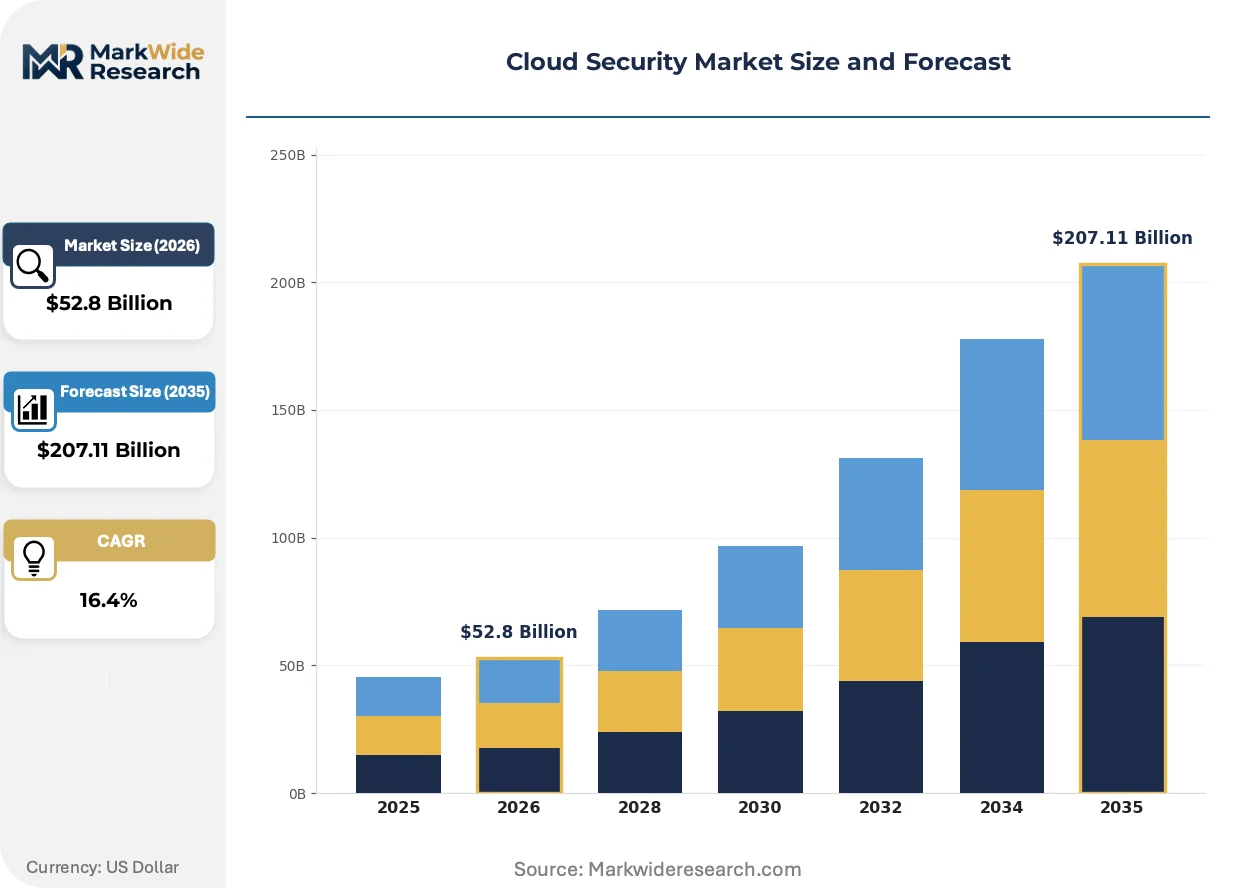
| Market Size in 2026 | $52.8 Billion |
| Market Size in 2035 | $207.11 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Community Cloud Solution Type: Identity & Access Management, Data Loss Prevention, Intrusion Detection System, Encryption, Security Information & Event Management Use Case: Threat Intelligence, Compliance Management, Application Security, Insider Threat Detection, Network Security End User: BFSI, Telecommunications, Government, IT & Telecom, Manufacturing |
| Companies Covered | Microsoft Corporation, Amazon Web Services, Google Cloud Platform, Broadcom, Cisco Systems, Palo Alto Networks, IBM Corporation, Trend Micro, Check Point Software Technologies, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Security Market Strategic Shifts & Innovations
Cloud security architecture is actively splitting between centralized governance platforms and edge-distributed enforcement nodes, with regulatory pressure accelerating both paths simultaneously.
Confidential computing hardware is bifurcating the encryption market. Trusted execution environments protect data during processing, not merely at rest or in transit. Financial services firms in Frankfurt and Singapore are deploying these enclaves for high-frequency trading analytics. The technology is bifurcating vendor roadmaps between hardware-dependent and software-only encryption paths.
EU AI Act risk classification rules are reshaping cloud security procurement for machine learning workloads. High-risk AI systems must demonstrate auditability and data lineage controls that exceed standard encryption requirements. Healthcare and financial services verticals in France and Germany are pre-emptively deploying governance tooling to meet these mandates before enforcement deadlines.
Consumption-based security licensing is displacing perpetual enterprise agreements. Mid-market buyers in manufacturing and retail verticals prefer metered identity verification and threat detection services. This shift is most pronounced in US and UK markets where CFOs prioritize operational expenditure classification over capital deployment.
Cloud Security Market Segmentation
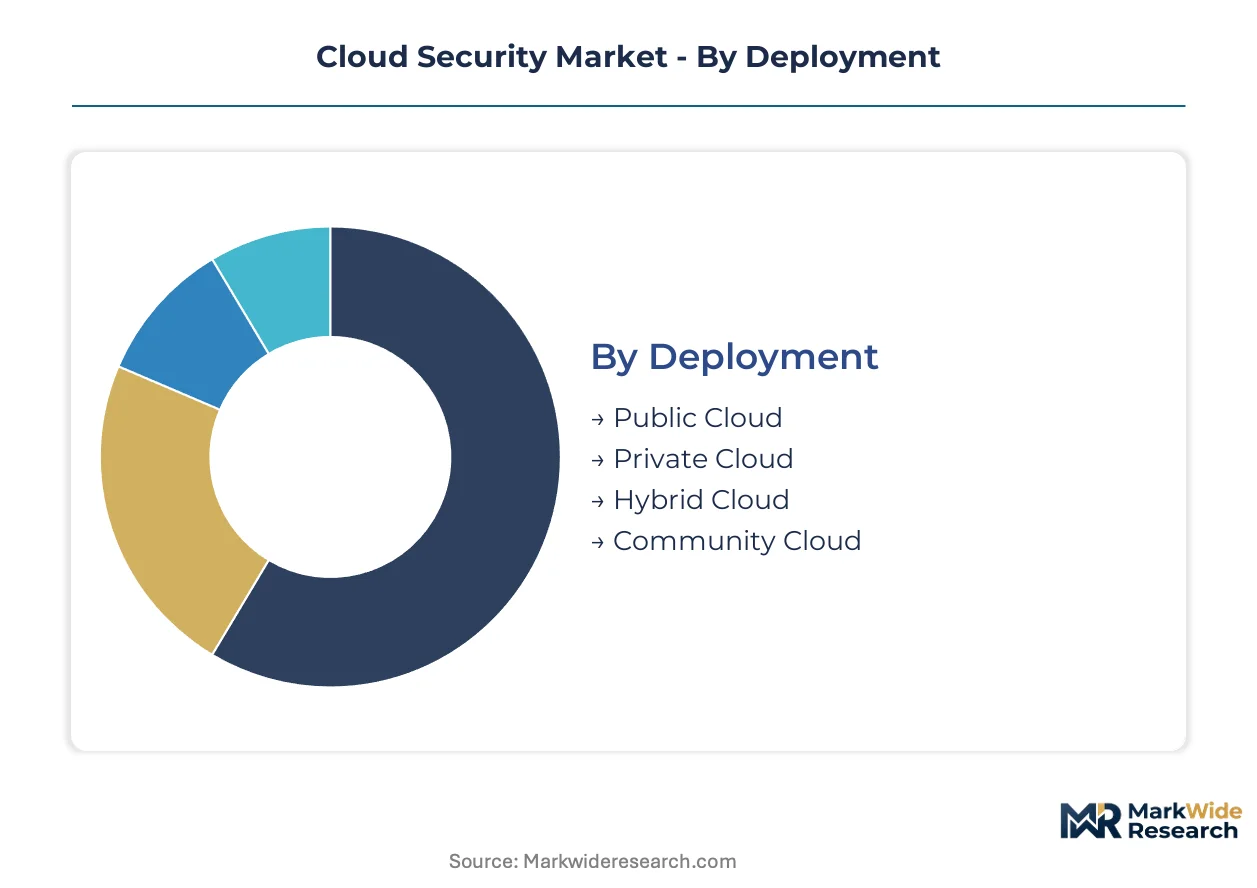
Cloud security procurement patterns diverge sharply across deployment models and regulatory contexts. Solution architecture, compliance mandates, and end-user risk profiles collectively determine vendor selection and pricing structures.
Deployment:
German industrial data sovereignty rules and Japanese METI localization guidelines are fragmenting deployment strategies across jurisdictions.
- Public Cloud:Multi-tenant infrastructure delivers elastic compute with shared security controls. Financial services firms in Singapore and retail operators in the United Kingdom favor this model for cost predictability, though GDPR cross-border restrictions limit European adoption for sensitive workloads.
- Hybrid Cloud:Unified orchestration layers bridge on-premises hardware with public resource pools. Manufacturing conglomerates in Germany deploy this architecture to satisfy operational technology isolation requirements while accessing cloud analytics.
- Private Cloud:Single-tenant environments with dedicated physical infrastructure. Healthcare systems subject to FDA cloud-hosted data guidelines select this deployment for direct control over encryption key management.
- Community Cloud:Shared infrastructure serving specific industry verticals or regulatory cohorts. Defense contractors and government agencies in classified procurement frameworks utilize these segmented environments.
Hybrid Cloud handles the majority of throughput; Hybrid Cloud is also the fastest mover on share.
Solution Type:
Margin concentration follows credential governance complexity rather than threat detection volume.
- Identity & Access Management:Centralized credential lifecycle management with multi-factor authentication and privileged access controls. Workforce decentralization strains governance frameworks, concentrating demand in metropolitan technology hubs where specialized talent clusters.
- Encryption:AES-256 equivalent key management with hardware security module integration. Frankfurt and Singapore financial services deploy confidential computing enclaves for high-frequency trading analytics, bifurcating vendor roadmaps between hardware-dependent and software-only paths.
- Data Loss Prevention:Content inspection and egress monitoring for sensitive information classification.
- Intrusion Detection System:Network traffic analysis and anomaly detection for perimeter breach identification.
- Security Information & Event Management:Log aggregation and correlation platforms merging with automated response tooling.
Identity & Access Management commands the deepest margin pools; Encryption is expanding most quickly as confidential computing hardware penetrates regulated verticals.
Use Case:
Procurement priority shifts from perimeter defense to auditability and lineage verification.
- Compliance Management:Automated control mapping and evidence collection for regulatory attestation. EU AI Act risk classification rules are reshaping procurement for machine learning workloads, with French and German healthcare and financial services verticals pre-emptively deploying governance tooling.
- Threat Intelligence:External indicator feeds and adversary behavior analysis for proactive defense posture.
- Application Security:Code scanning and runtime protection for cloud-native software development.
- Insider Threat Detection:Behavioral analytics and access pattern monitoring for credential misuse identification.
- Network Security:Microsegmentation and zero-trust access enforcement for distributed architectures.
Compliance Management absorbs the largest share of enterprise security budgets; Compliance Management is climbing the fastest as AI governance mandates approach enforcement deadlines.
End User:
Vertical specialization determines certification requirements and sales cycle duration.
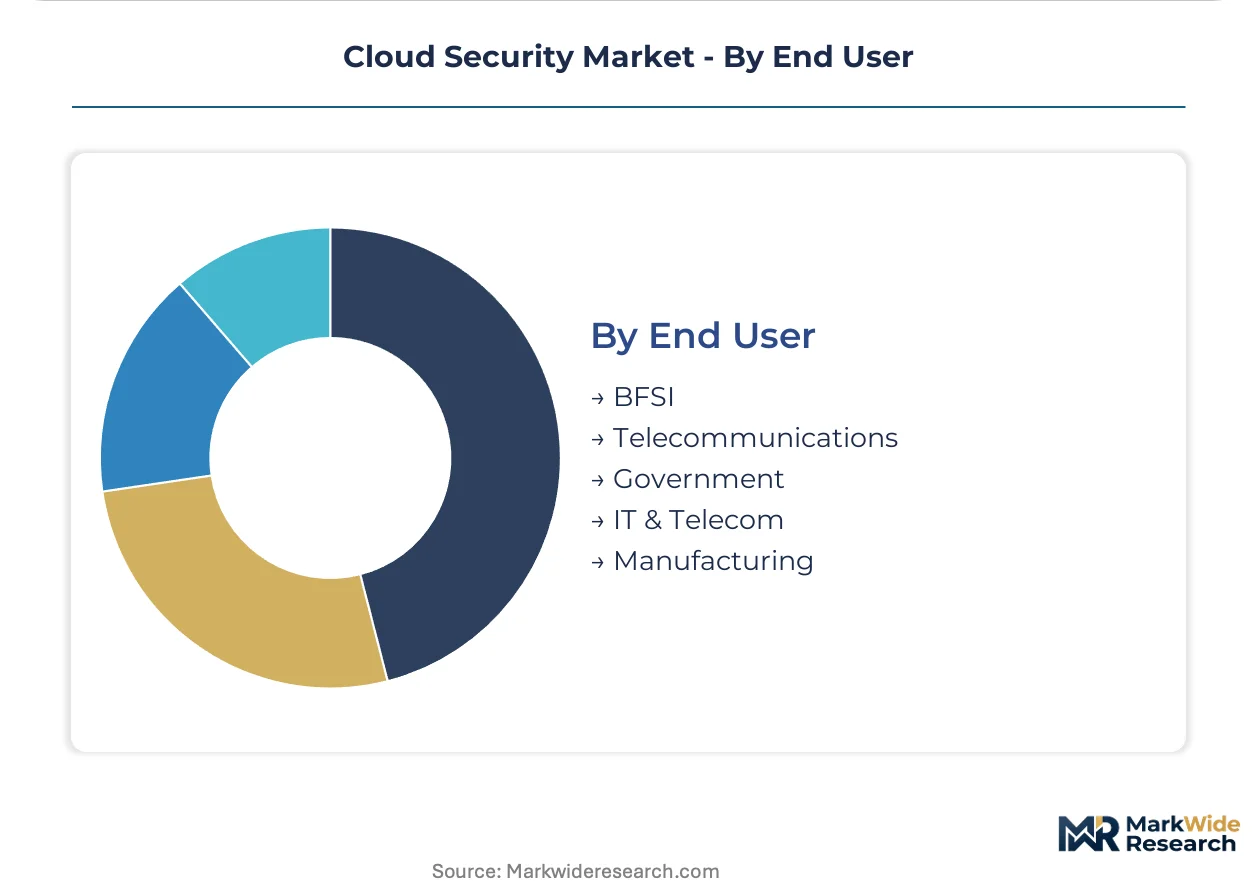
- BFSI:Banking, financial services, and insurance institutions with stringent data sovereignty and audit trail mandates. German manufacturing compliance requirements intersect with operational technology security needs, accelerating specialized procurement cycles for industrial banking clients.
- Government:Federal, state, and municipal agencies with classified and unclassified workload separation. Zero-trust architecture mandates from regulators across the European Union, the United States, and Japan are forcing infrastructure redesigns.
- Telecommunications:Carrier infrastructure and subscriber data protection for 5G core networks.
- IT & Telecom:Service provider internal security and managed security service delivery.
- Manufacturing:Operational technology integration and industrial control system protection.
BFSI dominates absolute expenditure; Government is gaining share fastest as sovereign cloud mandates proliferate across jurisdictions.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Vendor engineering resources concentrate in metropolitan technology hubs across three continents, with regulatory certification requirements fragmenting procurement patterns by jurisdiction. Cloud security procurement cycles vary dramatically based on local data sovereignty mandates and industrial specialization.
United States
Financial services firms and federal agencies drive enterprise-grade zero-trust deployments. NIST cybersecurity frameworks shape product roadmaps for vendors serving regulated industries. The Washington DC metropolitan area anchors government contract procurement, while New York and San Francisco clusters concentrate fintech security engineering talent.
Germany
Industrial cloud adoption intersects with heavy manufacturing compliance requirements, accelerating specialized procurement cycles. GDPR cross-border transfer rules compel region-locked encryption and key management systems. Frankfurt financial services deploy confidential computing enclaves for high-frequency trading analytics, bifurcating vendor roadmaps.
Japan
Zero-trust architecture mandates from regulators force infrastructure redesigns across banking and telecommunications verticals. METI guidelines for data localization create openings for domestic-anchored security service providers. Tokyo and Osaka metropolitan areas concentrate identity and access management expertise.
Singapore
Financial services firms favor multi-tenant public cloud infrastructure for cost predictability. The Monetary Authority of Singapore's technology risk management guidelines shape vendor certification requirements. Singapore's technology corridor serves as regional headquarters for security orchestration platform providers.
United Kingdom
Mid-market buyers in manufacturing and retail verticals prefer metered identity verification and threat detection services. Consumption-based security licensing displaces perpetual enterprise agreements. London's financial district drives demand for unified security orchestration platforms bridging on-premises legacy systems.
Cloud Security Market Key Industry Players
Technology leadership and cost leadership are held by different player archetypes, with the market consolidating around three distinct tiers. Tier-one providers anchor large government contracts through hybrid cloud footprints. Tier-two specialists differentiate through network-centric security stacks targeting financial services verticals. Tier-three regional players compete on sovereign cloud compliance and localized key management. Dominant competitive moves include strategic partnerships with hardware security module manufacturers and geographic expansion through compliance-first market entry.
Within the hyperscaler tier, Microsoft Corporation, Amazon Web Services, and Google Cloud Platform occupy positions defined by infrastructure scale and integrated security orchestration. These entities exemplify the platform archetype where cloud compute and security services converge. Palo Alto Networks represents the specialist archetype, anchoring network-centric procurement in regulated verticals. The competitive dynamic situates integrated platform breadth against vertical-specific depth, with procurement decisions filtering through compliance certification timelines before technical evaluation proceeds.
| Leading Market Players |
|---|
| Microsoft Corporation |
| Amazon Web Services |
| Google Cloud Platform |
| Broadcom |
| Cisco Systems |
| Palo Alto Networks |
| IBM Corporation |
| Trend Micro |
| Check Point Software Technologies |
| Others |
Cost & Logistics Intelligence
Hardware security module substitution for software-only encryption key management simultaneously shifts supply geography toward Taiwan and South Korea semiconductor foundries and compresses pricing economics for mid-market identity verification services.
Pricing Analysis
NIST cybersecurity framework certification dictates the pricing tier structure across the cloud security market. Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized platforms from SOC 2-compliant mid-market offerings and uncertified point solutions. Cost compression in the standard tier is intensifying because consumption-based licensing displaces perpetual agreements. Mid-market manufacturing buyers exhibit highest price sensitivity; federal agencies demonstrate lowest sensitivity due to mandate-driven procurement.
Supply Chain Analysis
Inventory lead times for hardware security modules extend procurement cycles for encryption-dependent deployments. Supply concentrates in Taiwan, South Korea, and the United States for confidential computing chipsets and trusted execution environment components. Vendor engineering draws from specialized cryptographic hardware, sovereign cloud infrastructure, and certified integration labor pools. Single-source vulnerability around Taiwan semiconductor fabrication creates structural risk. Distribution runs through hyperscaler marketplaces and direct enterprise sales teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Zero-trust architecture mandates across the European Union, United States, and Japan constitute a high-growth disruption, forcing infrastructure redesigns that expand addressable market scope for compliance-certified vendors.
For Market Incumbents: Secure FedRAMP and EU sovereign cloud certifications ahead of enforcement deadlines to anchor government procurement channels. Deepen backward integration into hardware security module supply chains to mitigate Taiwan concentration risk. Consolidate around unified security orchestration platforms that bridge hybrid deployments.
For New Entrants and Emerging Players: Managed detection and response service gaps in mid-market manufacturing verticals offer white-space entry points where Palo Alto Networks and Microsoft Corporation under-serve. Target German industrial cloud adoption intersecting with operational technology security needs. Pursue channel partnerships with regional system integrators possessing existing manufacturing relationships.
For Investors and Strategic Acquirers: EU AI Act enforcement reshapes the acquisition landscape toward governance tooling providers with pre-deployed auditability and data lineage controls. Long-term viability centers on platforms serving high-risk AI system compliance in healthcare and financial services verticals. Acquire confidential computing specialists with hardware-dependent encryption roadmaps. Watch FDA cloud-hosted healthcare data guideline expansion as inflection indicator.
| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Certification Investment | FedRAMP authorization opens federal procurement channels worth billions in contract value. |
| Confidential Computing Hardware Partnership | Trusted execution environment integration differentiates encryption offerings in Frankfurt financial services. |
| Sovereign Cloud Geographic Expansion | Japan METI-compliant data localization captures domestic-anchored security service provider openings. |
| SIEM-SOAR Platform Convergence | Automated response tooling merger creates new platform category with premium pricing power. |
| Healthcare Vertical Specialization | HIPAA-compliant encryption expertise accesses FDA-guided cloud-hosted data procurement channels. |
Research Approach
Desk research of regulatory filing databases, hyperscaler capex disclosures, and security vendor SEC filings preceded structured interviews with CISOs, cloud architects, identity and access management specialists, and federal procurement officers. Primary fieldwork combined with secondary validation across NIST framework documentation, GDPR enforcement records, and EU AI Act draft provisions. Bottom-up segment sizing triangulated against top-down market boundary analysis.
Variance decomposition across deployment models, solution types, use cases, and end-user verticals shaped the analytical framework throughout the forecast period. Modeled segmentation dimensions encompassed public-hybrid-private-community cloud architectures, identity-encryption-DLP-IDS-SIEM solution categories, and BFSI-government-telecommunications-manufacturing end-user splits. CAGRs derived from regression against IT security spending intensity and regulatory mandate adoption curves, with confidential computing penetration and consumption-based licensing shift as key industry-specific inputs.
Forecasts assume regulatory continuity in EU GDPR enforcement, US NIST framework evolution, and Japan METI localization guidelines; material policy shifts would require re-modeling. Revision becomes warranted when sovereign cloud mandate proliferation crosses thresholds that fragment interoperability standards.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Server Security Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
Digital Security Market
Cybersecurity
Global Network Security Firewall Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
DNS Security Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
M2M Network Security Market