
 Spear Phishing Solution Market | 2026-2036
Spear Phishing Solution Market Size, Share, and Industry Trends Forecast 2026-2036
Spear Phishing Solution Market Analytics
The divergence between premium AI-native detection tiers and commodity signature-based offerings is realigning vendor strategies across the sector. Proofpoint, Inc. leverages deep email telemetry to sustain enterprise retention rates. Microsoft Corporation anchors cloud-integrated deployment through native Office 365 security modules. Cisco Systems, Inc. competes on network-edge convergence with email gateway appliances.
Spear phishing solutions are software and service-based detection systems that analyze email headers, content metadata, and behavioral sender patterns to intercept targeted social engineering attacks before credential compromise occurs. These systems apply natural language processing and identity graph analysis to distinguish spoofed executive communications from legitimate correspondence. Cloud deployment options are capturing the fastest expansion as organizations abandon on-premises email security appliances. Enterprise end users dominate current spending, though educational institutions represent an emerging segment with specialized compliance needs.
The U.S. SEC enforces cyber disclosure rules that mandate public companies report material email-borne breaches within four business days. The EU AI Act classifies certain autonomous phishing detection algorithms as high-risk, requiring conformity assessments before market deployment. Japan's METI issues sector-specific cybersecurity guidelines that elevate procurement standards for critical infrastructure operators. Stakeholders must monitor how divergent regulatory timelines for AI transparency reshape product roadmaps and geographic rollout priorities.
Market Dynamics
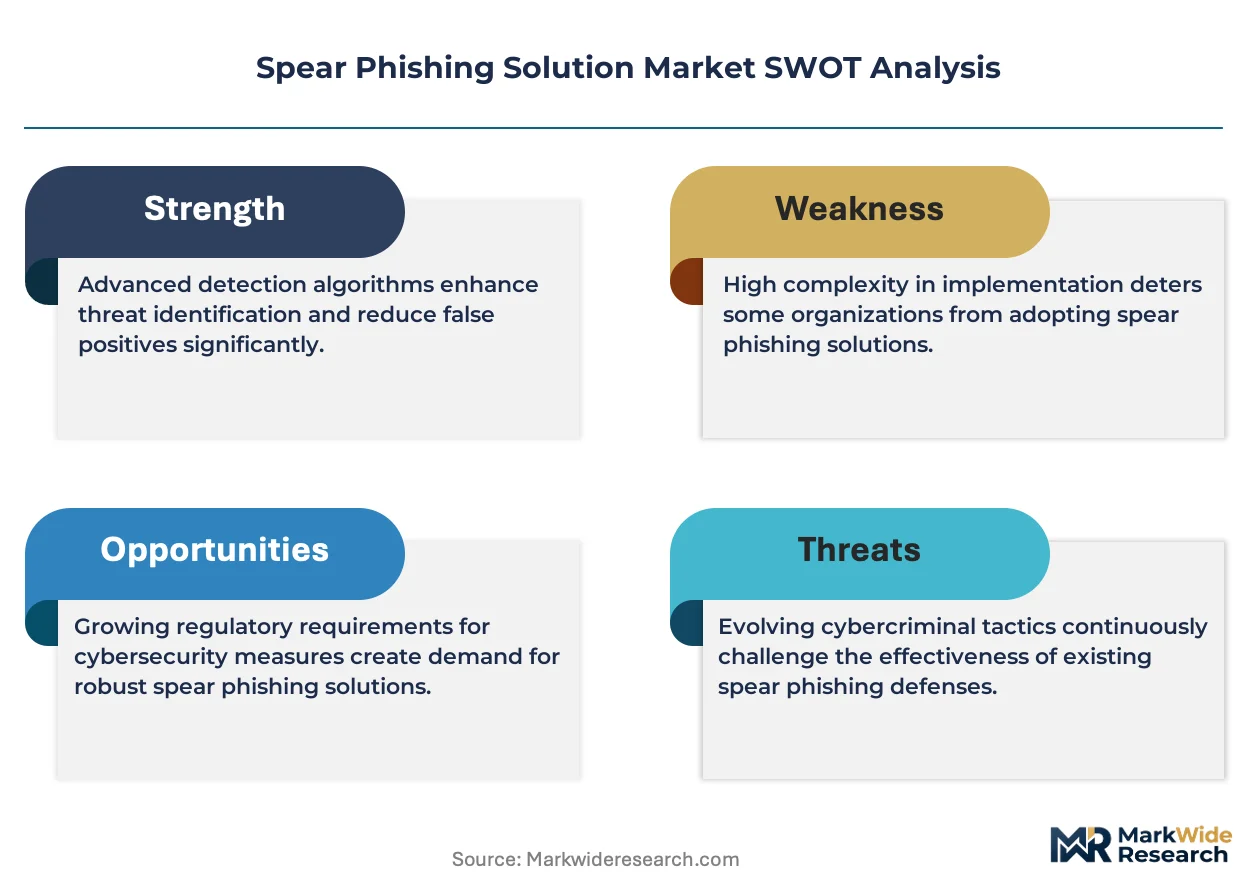
Deep learning architectures are compressing detection latency windows, forcing legacy signature-based vendors to reengineer core engines or cede enterprise accounts to AI-native platforms.
Growth Catalysts
- EU AI Act high-risk classification:Mandatory conformity assessments for autonomous detection algorithms are filtering out undercapitalized vendors and concentrating procurement among certified suppliers across German and French financial institutions.
- Cloud email migration:Organizations abandoning on-premises Exchange servers are simultaneously replacing gateway appliances with API-integrated cloud-native detection, creating bundled purchasing momentum.
- Executive impersonation volume:BEC attack frequency against C-suite targets is compelling mid-market enterprises to upgrade from basic spam filtering to behavioral analysis platforms.
Market Restraints
- False positive calibration costs:Overly aggressive detection thresholds disrupt legitimate business workflows, requiring dedicated security operations center staffing that smaller enterprises cannot sustain.
- Threat actor adaptation cycles:Adversaries now weaponize generative text models to evade linguistic pattern recognition, compressing the effective lifespan of trained detection models.
- API rate limiting:Cloud email providers impose query throttling that constrains real-time header analysis depth for third-party security vendors.
Strategic Opportunities
- Educational institution compliance:FERPA-adjacent data protection mandates at US universities are creating specialized procurement requirements for student and faculty email protection.
- Identity graph convergence:Integration between email detection and zero-trust network access platforms is unifying security budgets under single-vendor relationships.
- Japan METI critical infrastructure guidelines:Sector-specific cybersecurity standards for energy and transportation operators are elevating procurement specifications above commodity thresholds.
Industry Challenges
- ML engineer scarcity:Recruitment competition from hyperscale technology firms constrains vendor ability to staff adversarial research teams.
- Multi-tenant architecture isolation:Cloud-native platforms must demonstrate data segregation between competing enterprise clients during procurement security reviews.
- Legacy SIEM integration:Custom correlation rule development for on-premises security information platforms extends deployment timelines and strains professional services capacity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Spear Phishing Solution Market |
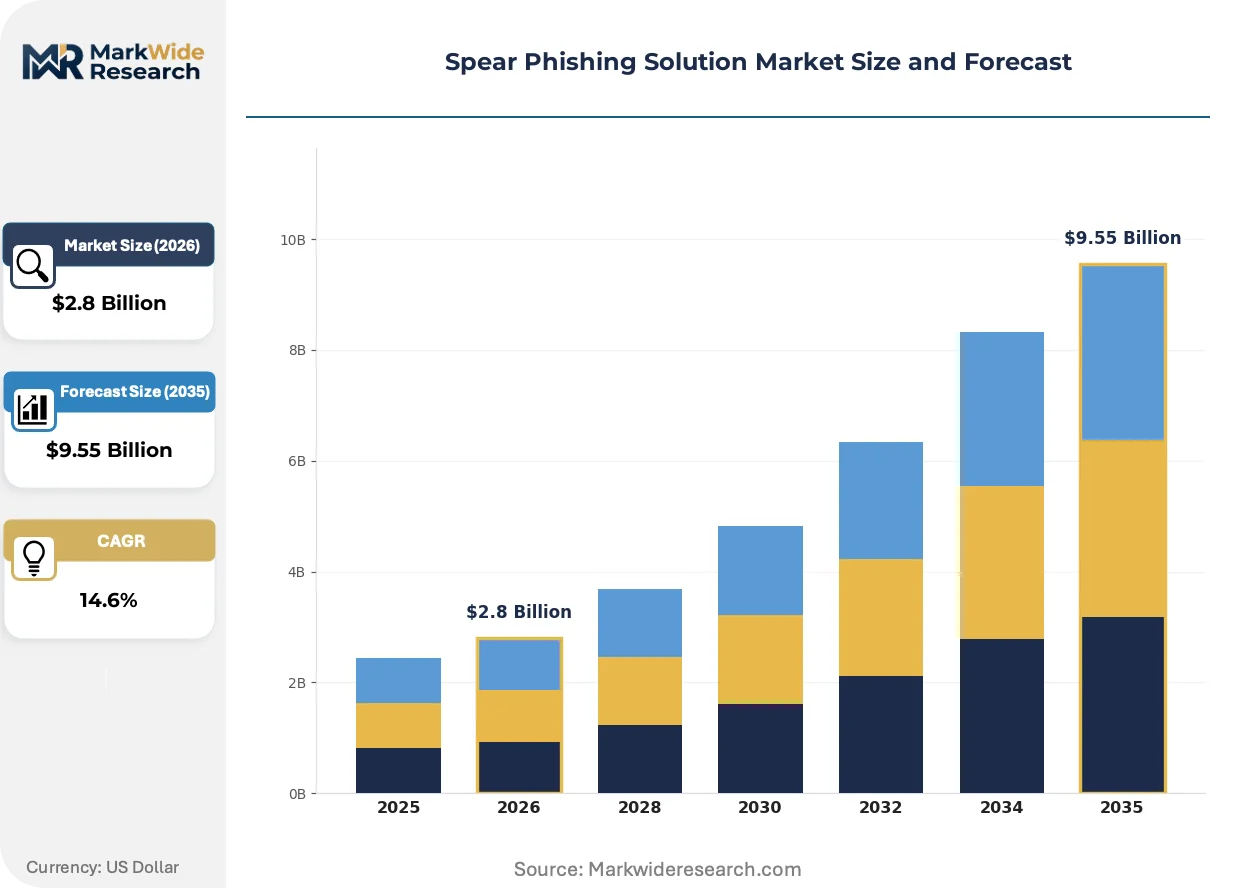
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $9.55 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Software, Service, Platform, Tool Deployment: Cloud, On-Premises, Hybrid, Managed End User: Enterprise, Government, SMB, Educational Institution Channel: Direct Sales, Reseller, Online, Affiliate |
| Companies Covered | Microsoft Corporation, Proofpoint, Inc., BAE Systems, Cisco Systems, Inc., FireEye Inc., Mimecast Ltd., Barracuda Networks Inc., GreatHorn, Inc., Check Point Software Technologies Ltd., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Spear Phishing Solution Market Evolving Landscape
Natural language understanding engines are replacing static pattern libraries as the primary detection substrate, compressing the competitive relevance of vendors lacking proprietary training data pipelines.
Large language model-based semantic analysis is unifying sender intent classification with content risk scoring into single inference passes. Financial services security teams in New York and London are piloting these architectures for real-time executive communication verification. This convergence is collapsing the traditional separation between email security and identity protection budgets.
The EU AI Act's high-risk system designation is mandating algorithmic transparency documentation for autonomous phishing detection tools deployed across member states. Vendors must now submit conformity assessments to notified bodies before commercial release. German automotive and French aerospace supply chains are experiencing the most acute compliance timeline pressure.
Security procurement committees are consolidating vendor relationships through platform consolidation rather than point-solution accumulation. Mid-market enterprises in the United States are specifically rejecting best-of-breed email gateways in favor of Microsoft or Google native security modules bundled with existing licensing. This preference shift is compressing standalone vendor addressable market expansion in the sub-5,000 employee segment.
Spear Phishing Solution Market Segmentation
Spear phishing solution procurement patterns diverge sharply across deployment architectures and buyer sophistication levels. Organizations replacing legacy gateway appliances evaluate segments through fundamentally different technical and economic lenses than first-time adopters.
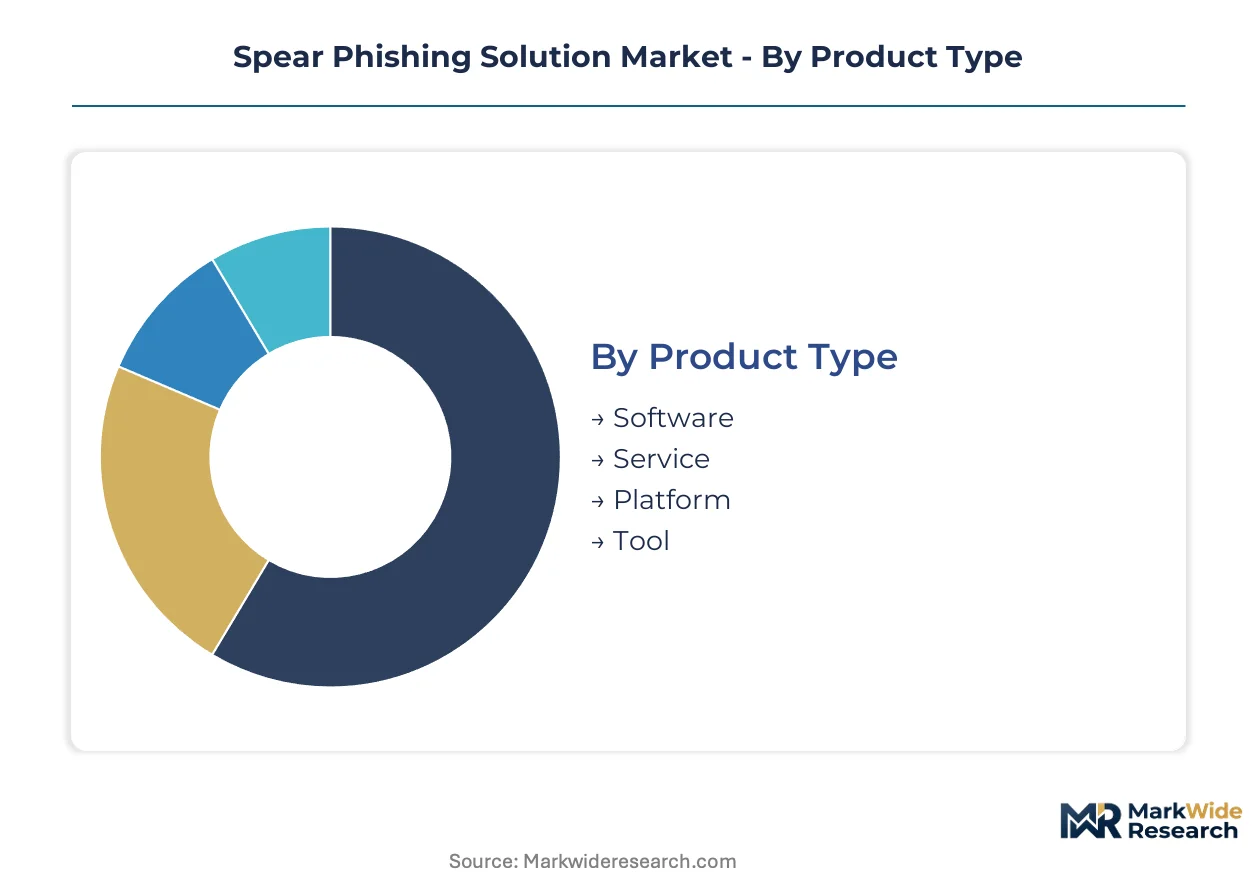
Product Type:
Upgrade cycles from signature-based detection to behavioral analysis engines are compressing replacement timelines across financial services and critical infrastructure operators.
- Software:Deployable detection modules integrate via API into existing email infrastructure without hardware replacement. Demand concentrates among mid-market enterprises in Germany and Japan seeking modular augmentation of Microsoft 365 environments without full platform displacement.
- Service:Managed detection and response offerings combine automated scanning with analyst-verified threat intelligence. European banks under EU AI Act compliance pressure favor externally validated service tiers to satisfy conformity assessment documentation requirements.
- Platform:Unified consoles consolidating email security with identity protection and zero-trust network access.
- Tool:Point-solution utilities for specific verification tasks like header analysis or link sandboxing.
Volume placements concentrate in Software; the faster expansion belongs to Service.
Deployment:
Cost tier differentiation separates capital-intensive perpetual licensing from operational expenditure models favored by budget-constrained security teams.
- Cloud:Native SaaS architectures with continuous model updates and elastic compute scaling. United States enterprises abandoning on-premises Exchange servers are driving bundled procurement alongside Microsoft and Google workspace licensing.
- On-Premises:Air-gapped appliances for classified or regulated environments requiring data sovereignty. Japanese energy operators under METI guidelines maintain these deployments for critical infrastructure isolation.
- Hybrid:Split architectures routing executive communications through cloud analysis while retaining sensitive departmental traffic on-premises.
- Managed:Fully outsourced security operations center functions with vendor-assumed detection liability.
Cloud deployments dominate current procurement volumes; hybrid configurations are climbing the fastest as regulated industries navigate compliance fragmentation.
End User:
Customer type maturity determines feature depth requirements and acceptable false-positive thresholds.
- Enterprise:Global organizations with dedicated security operations centers and custom SIEM correlation requirements. Financial services firms in London and New York are expanding procurement of AI-native detection tiers with executive impersonation-specific training pipelines.
- Government:National and sub-national agencies with classified communication mandates and domestic data residency requirements.
- SMB:Resource-constrained organizations prioritizing turnkey deployment and minimal ongoing administration overhead.
- Educational Institution:Universities and school districts with FERPA-adjacent student data protection obligations and distributed faculty governance structures.
Enterprise accounts generate the largest contract values; educational institutions are gaining share fastest as specialized compliance procurement frameworks mature.
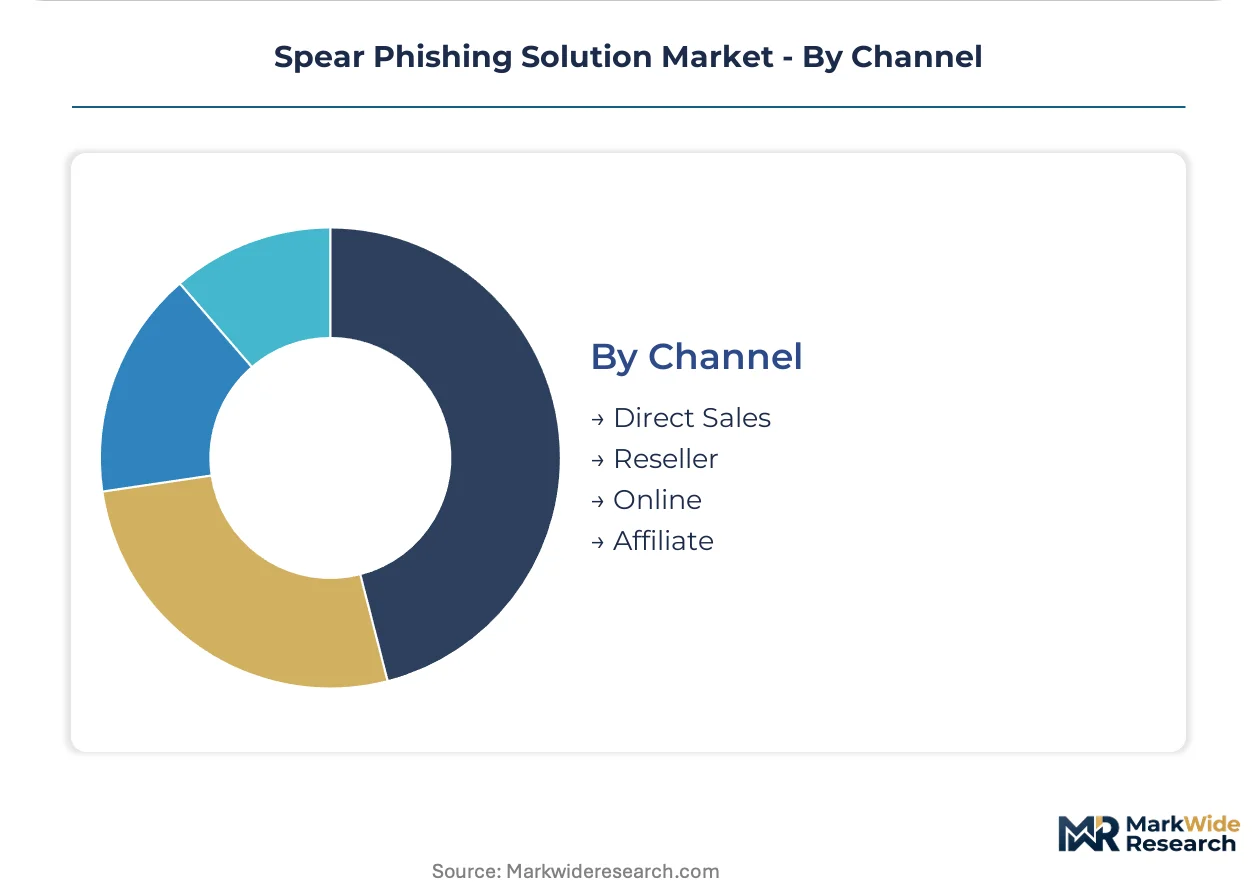
Channel:
Supply concentration among dominant platforms is reshaping how independent vendors reach end buyers.
- Direct Sales:Vendor field teams engaging CISO-level stakeholders for complex multi-year enterprise agreements. Large financial institutions in Frankfurt and Singapore prefer direct relationships for security-critical procurement.
- Reseller:Value-added distributors bundling email security with broader cybersecurity portfolios. Regional specialists in France and Italy leverage existing SIEM relationships to attach spear phishing modules.
- Online:Self-service provisioning through vendor marketplaces with credit-card subscription activation.
- Affiliate:Commission-based referral arrangements with cybersecurity consultancies and incident response firms.
Direct sales capture the highest-value placements; reseller channels are expanding most quickly as platform consolidation drives attach-rate opportunities.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
San Francisco anchors enterprise security procurement intensity as financial services and technology firms headquartered there drive early adoption of AI-native detection platforms. The United States, Germany, and Japan concentrate solution deployment as breach disclosure mandates tighten across their regulatory jurisdictions.
United States
Financial services firms in New York and Chicago are expanding procurement of behavioral analysis engines with executive impersonation-specific training. The SEC enforces cyber disclosure rules mandating public companies report material email-borne breaches within four business days. Silicon Valley security teams pilot large language model-based semantic analysis for real-time C-suite communication verification.
Germany
Automotive and aerospace supply chains in Stuttgart and Munich experience acute compliance timeline pressure under EU AI Act high-risk system designations. The EU AI Act mandates algorithmic transparency documentation and conformity assessments before commercial release. Frankfurt-based financial institutions favor externally validated managed detection services to satisfy documentation requirements.
Japan
Energy and transportation operators under METI sector-specific cybersecurity guidelines maintain elevated procurement specifications above commodity thresholds. METI guidelines for critical infrastructure operators mandate data sovereignty and isolation standards. Tokyo and Osaka security procurement committees consolidate vendor relationships through platform consolidation rather than point-solution accumulation.
United Kingdom
London financial services security teams pilot converged email detection and zero-trust network access platforms to unify security budgets. The UK Information Commissioner's Office enforces data protection standards that elevate vendor security review rigor. The City of London and Canary Wharf clusters drive demand for managed detection offerings combining automated scanning with analyst-verified threat intelligence.
France
Aerospace supply chains in Toulouse and Paris face EU AI Act conformity assessment pressure for autonomous phishing detection algorithms. ANSM and CNIL oversight frameworks extend to cybersecurity procurement in regulated industries. Regional specialists in Lyon leverage existing SIEM relationships to attach spear phishing modules to broader cybersecurity portfolios.
Spear Phishing Solution Market Competitive Landscape
Premium-margin players sit above commodity-margin players across AI-native detection capability and proprietary training data access. The vendor base stratifies into three tiers: cloud-native platforms with continuous model updates, legacy gateway appliance providers reengineering core engines, and managed security service operators assuming detection liability. Consolidation pressure concentrates procurement among certified suppliers as regulatory conformity assessments filter undercapitalized vendors. Dominant competitive moves include strategic partnerships with cloud email providers and portfolio diversification into identity protection convergence.
Within the cloud-native platform tier, Microsoft Corporation and Proofpoint, Inc. occupy positions reflecting divergent deployment philosophies. Microsoft anchors cloud-integrated deployment through native Office 365 security modules bundled with existing enterprise licensing. Proofpoint leverages deep email telemetry to sustain enterprise retention rates among financial services and critical infrastructure operators. Cisco Systems, Inc. sits within the network-edge convergence archetype, competing through email gateway appliances that integrate with broader security infrastructure. These three entities exemplify how vendor strategies realign around the divergence between premium AI-native detection tiers and commodity signature-based offerings.
| Leading Market Players |
|---|
| Microsoft Corporation |
| Proofpoint, Inc. |
| BAE Systems |
| Cisco Systems, Inc. |
| FireEye Inc. |
| Mimecast Ltd. |
| Barracuda Networks Inc. |
| GreatHorn, Inc. |
| Check Point Software Technologies Ltd. |
| Others |
Value Network & Pricing Analysis
Horizontal integration into cloud email platforms anchors both supply positioning and pricing power for spear phishing solution vendors. Microsoft and Google bundle native security modules with workspace licensing, compressing standalone vendor margins and forcing point-solution providers toward API-integrated deployment models.
Pricing Analysis
Outcome-based pricing tied to breach prevention rates anchors enterprise tier structures. Three-tier pricing structure across premium AI-native detection, standard behavioral analysis, and economy signature-based levels separates vendors by model sophistication. Cost compression in the mid-market tier is intensifying because bundled Microsoft 365 security displaces standalone procurement. SMB buyers exhibit highest price sensitivity, while financial services firms in New York and London accept premium tiers for executive impersonation protection.
Supply Chain Analysis
Single-source vulnerability sits with Taiwan-based semiconductor fabrication for AI inference accelerators powering detection engines. Cloud infrastructure draws from United States, Ireland, and Singapore data center clusters. GPU supply constraints and EU AI Act conformity assessment bottlenecks create procurement delays. Distribution runs through direct enterprise sales teams and hyperscaler marketplaces with native integration pathways.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The spear phishing solution market sits in a technology-transition phase as deep learning architectures displace signature-based detection engines. Natural language understanding models are compressing the competitive relevance of vendors lacking proprietary training data pipelines.
For Market Incumbents: Deploy continuous model retraining pipelines to defend against generative AI-powered adversarial adaptation. Acquire specialized threat intelligence feeds from financial services and critical infrastructure operators to maintain detection edge. Consolidate procurement relationships through zero-trust platform convergence before Microsoft and Google capture bundled security budgets.
For New Entrants and Emerging Players: Capture educational institution procurement frameworks by building FERPA-adjacent compliance documentation and student data protection features. Target mid-market German and Japanese enterprises seeking modular API augmentation of existing Microsoft 365 environments. Pursue managed detection service positioning to bypass capital-intensive model development requirements.
For Investors and Strategic Acquirers: Exit pathways concentrate in platform consolidation plays by hyperscale cloud providers seeking native security differentiation. Long-term viability favors vendors with proprietary email telemetry archives and EU AI Act conformity assessment completion. Watch for inflection when API rate limiting from cloud email providers constrains third-party vendor scalability.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies email security with zero-trust network access under single-vendor relationships. |
| Acquisition of Specialist Firm | Captures proprietary training data pipelines and adversarial research capabilities. |
| Product Launch | Deploys large language model-based semantic analysis for real-time executive verification. |
| Strategic Partnership | Secures API integration priority with Microsoft or Google cloud email platforms. |
| Geographic Expansion | Establishes conformity assessment pathways for EU AI Act high-risk system deployment. |
Research Methodology
Multi-period observation of detection engine replacement cycles and cloud migration patterns anchored the trend analysis, supplemented by interviews with CISOs at financial services firms, security operations center directors, IT procurement officers, and channel partners. Secondary validation drew from SEC cyber disclosure filings, EU AI Act regulatory documentation, METI cybersecurity guidelines, and hyperscaler security module revenue disclosures. Bottom-up vendor revenue triangulation against top-down enterprise security spending estimates calibrated market sizing.
Segment-weighting across deployment architecture, buyer sophistication tier, and regional regulatory cluster shaped the analytical framework. Modeled dimensions included product type, cloud versus on-premises deployment, end-user category, and channel structure. CAGRs were derived from fitted growth curves against historical replacement cycle data and procurement intention surveys. AI-native detection adoption rates and executive impersonation attack frequency served as industry-specific forecast inputs across the projection horizon.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to adversarial adaptation cycles and cloud provider API policy changes. Forecasts reflect documented assumptions about regulatory enforcement timelines and enterprise cloud migration completion rates. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Global Internet Security Market
Cybersecurity
CDN Security Market
Cybersecurity
North America Extended Detection and Response Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Germany Cybersecurity Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market