
 Digital Security Market | 2026-2036
Digital Security Market Size, Share, and Industry Trends Forecast 2026-2036
Digital Security Market Analysis
GDPR enforcement is decoupling data residency from legacy infrastructure assumptions. Microsoft leverages its cloud-native security stack to anchor enterprise contracts across regulated industries. Palo Alto Networks specializes in zero-trust network segmentation, competing directly with Fortinet's integrated hardware-software platform. CrowdStrike Holdings extends its endpoint detection footprint through native AI-driven threat hunting capabilities.
Digital security encompasses hardware, software, and service-based systems engineered to protect data integrity, confidentiality, and availability across networked environments, typically operating through cryptographic protocols, real-time traffic inspection, and behavioral anomaly detection at sub-millisecond latency thresholds. Its primary commercial purpose is to neutralize unauthorized access, data exfiltration, and operational disruption across enterprise IT and operational technology stacks. Firewall and encryption deployments command the largest installed base, while artificial intelligence and machine learning technologies represent the fastest-expanding capability layer as vendors automate threat response. Banking and government end users concentrate procurement around certified, high-assurance products, whereas retail and healthcare buyers are shifting toward cloud and hybrid deployment models to reduce capital intensity.
The EU AI Act, GDPR, and the US SEC cybersecurity disclosure rules are collectively elevating product certification requirements and mandating board-level accountability for breach reporting timelines. Japan's METI guidelines and China's GB standards add further compliance layers for vendors selling into Asia-Pacific jurisdictions. Stakeholders must monitor regulatory divergence between jurisdictions to anticipate where certification costs will fragment go-to-market economics.
Market Dynamics
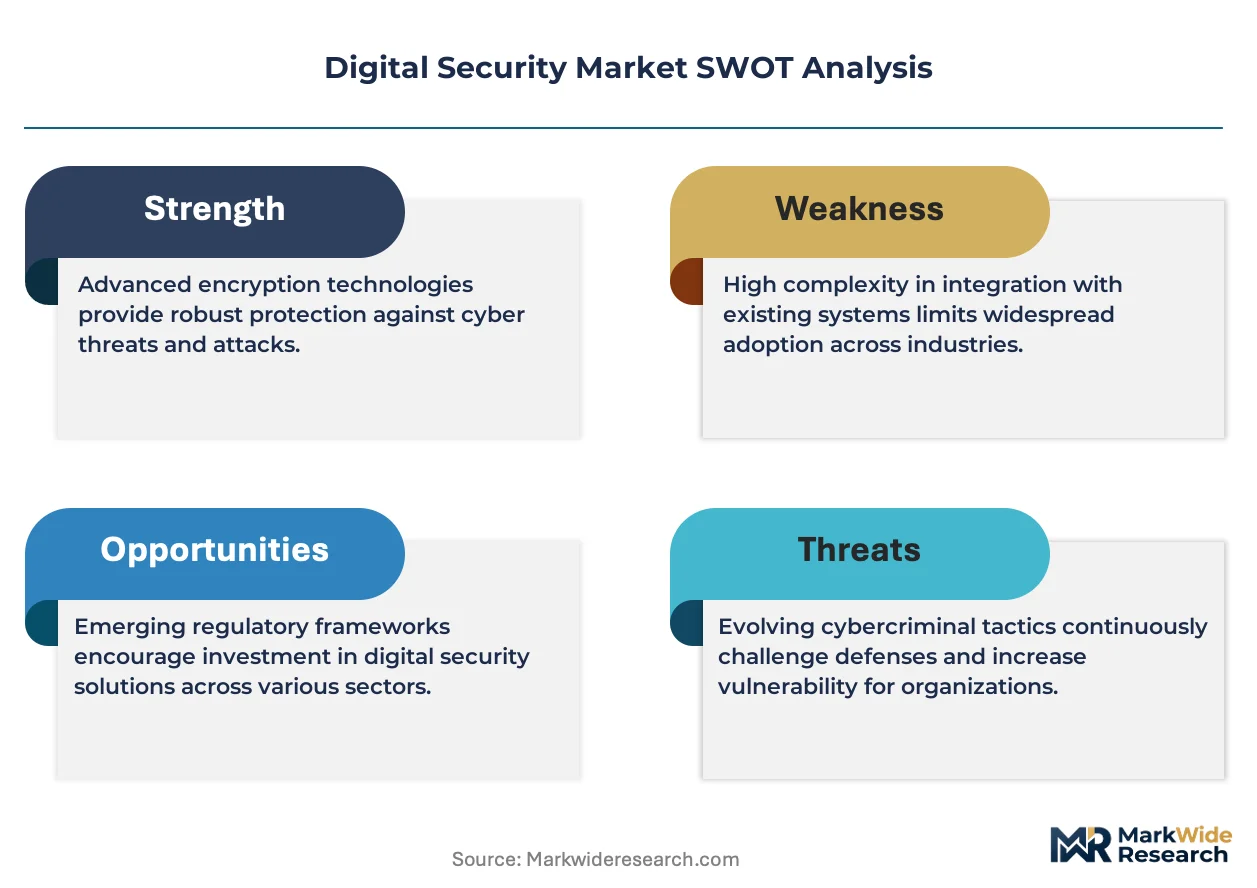
Regulatory fragmentation between the EU AI Act, GDPR, and US SEC disclosure rules is forcing vendors to maintain parallel certification tracks, elevating compliance costs while creating competitive moats for scaled providers with dedicated regulatory affairs functions.
Growth Catalysts
- Healthcare digitization:Hospital networks in the United States are expanding cybersecurity procurement to protect electronic health records under HIPAA breach notification mandates.
- EU AI Act enforcement:The European Union's risk-based classification system for AI systems is compelling enterprises to invest in audit-ready security infrastructure.
- Zero-trust architecture mandates:Federal agencies and defense contractors are replacing perimeter-based models with microsegmentation protocols.
Market Restraints
- Specialized talent scarcity:The shortage of certified security architects and threat intelligence analysts limits deployment velocity for mid-market buyers.
- Input cost volatility:Semiconductor supply constraints for specialized encryption hardware create procurement bottlenecks and price instability.
- Regulatory friction:Divergent breach notification timelines between EU GDPR and US state laws complicate incident response automation.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy facilities are integrating IT security stacks with industrial control systems.
- Cloud-native security services:Managed detection and response offerings are displacing on-premise security operations centers.
- Japan METI guidelines:The Ministry of Economy, Trade and Industry's cybersecurity framework for critical infrastructure creates certified product demand.
Industry Challenges
- Legacy system integration:Mainframe and proprietary operational technology environments resist API-based security orchestration.
- Certification timeline compression:Accelerated product release cycles conflict with Common Criteria evaluation periods.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Digital Security Market |
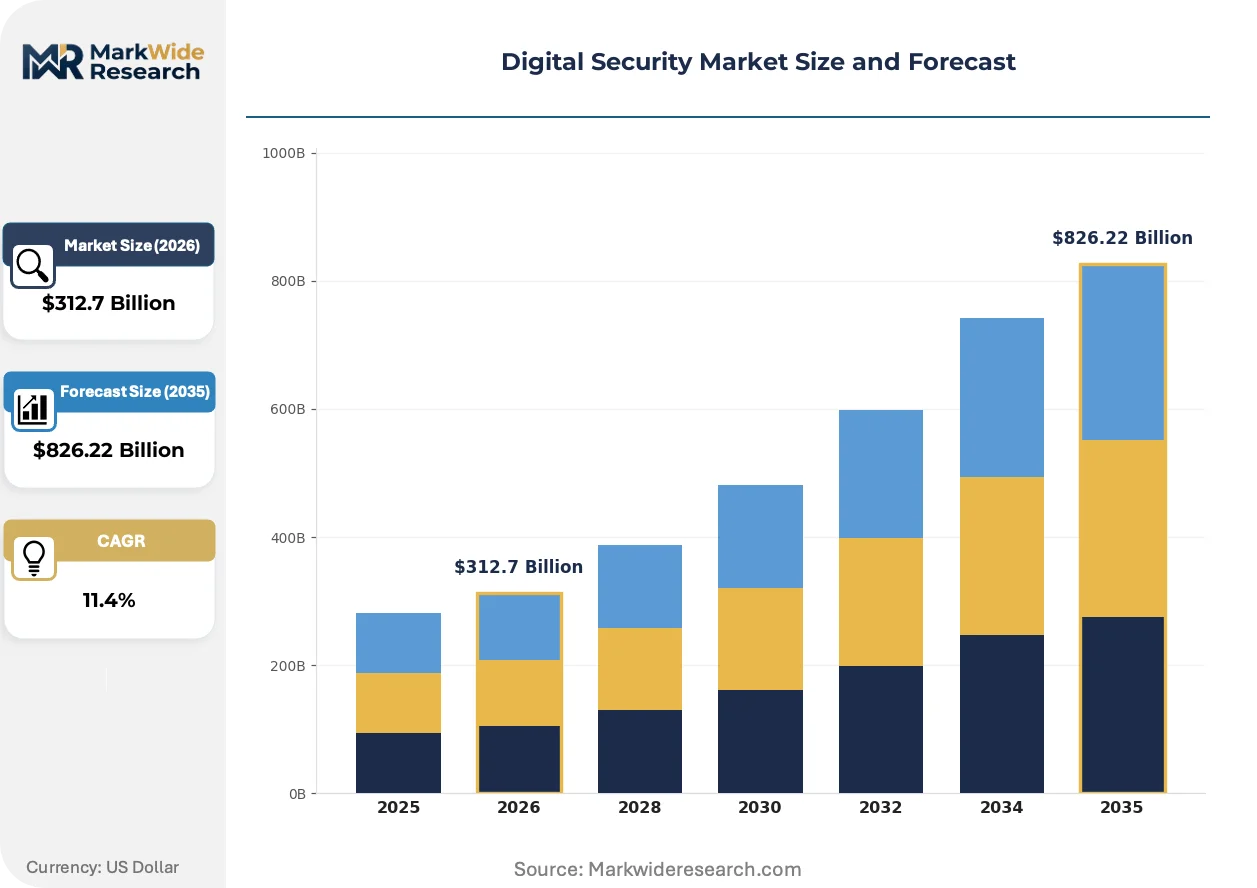
| Market Size in 2026 | $312.7 Billion |
| Market Size in 2035 | $826.22 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Anti-Virus, Intrusion Detection, Encryption Technology: Blockchain, Artificial Intelligence, Machine Learning, Biometric End User: Banking, Healthcare, Retail, Government Deployment: Cloud, On-Premises, Hybrid, Managed Service |
| Companies Covered | Cisco Systems, Inc., Microsoft, Palo Alto Networks, Fortinet, Inc., IBM Corporation, Check Point Software Technologies Ltd., CrowdStrike Holdings, Inc., Trend Micro, Inc., Broadcom, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Digital Security Market Emerging Trajectories
Artificial intelligence is expanding from threat detection into autonomous response workflows, compressing mean-time-to-remediation metrics while redrawing competitive boundaries between platform vendors and point solution providers.
Extended detection and response platforms aggregate telemetry across endpoints, networks, and cloud workloads into unified data lakes. Large financial institutions and healthcare systems are adopting these consolidated architectures fastest. The technology is expanding into mid-market accounts through managed service wrappers that abstract deployment complexity.
The EU AI Act's high-risk system obligations require security vendors to maintain technical documentation and human oversight mechanisms for automated decision systems. This elevates product development costs but creates differentiation for vendors with established governance frameworks. Banking and government procurement teams in France and Germany now prioritize suppliers with pre-submitted conformity assessments.
Consumption-based licensing models are displacing perpetual software licenses in enterprise security procurement. Chief information security officers favor annual recurring revenue structures that align spending with actual deployment scale. This shift is most visible in United States technology and retail verticals where cloud migration has already normalized utility pricing for compute infrastructure.
Digital Security Market Segmentation
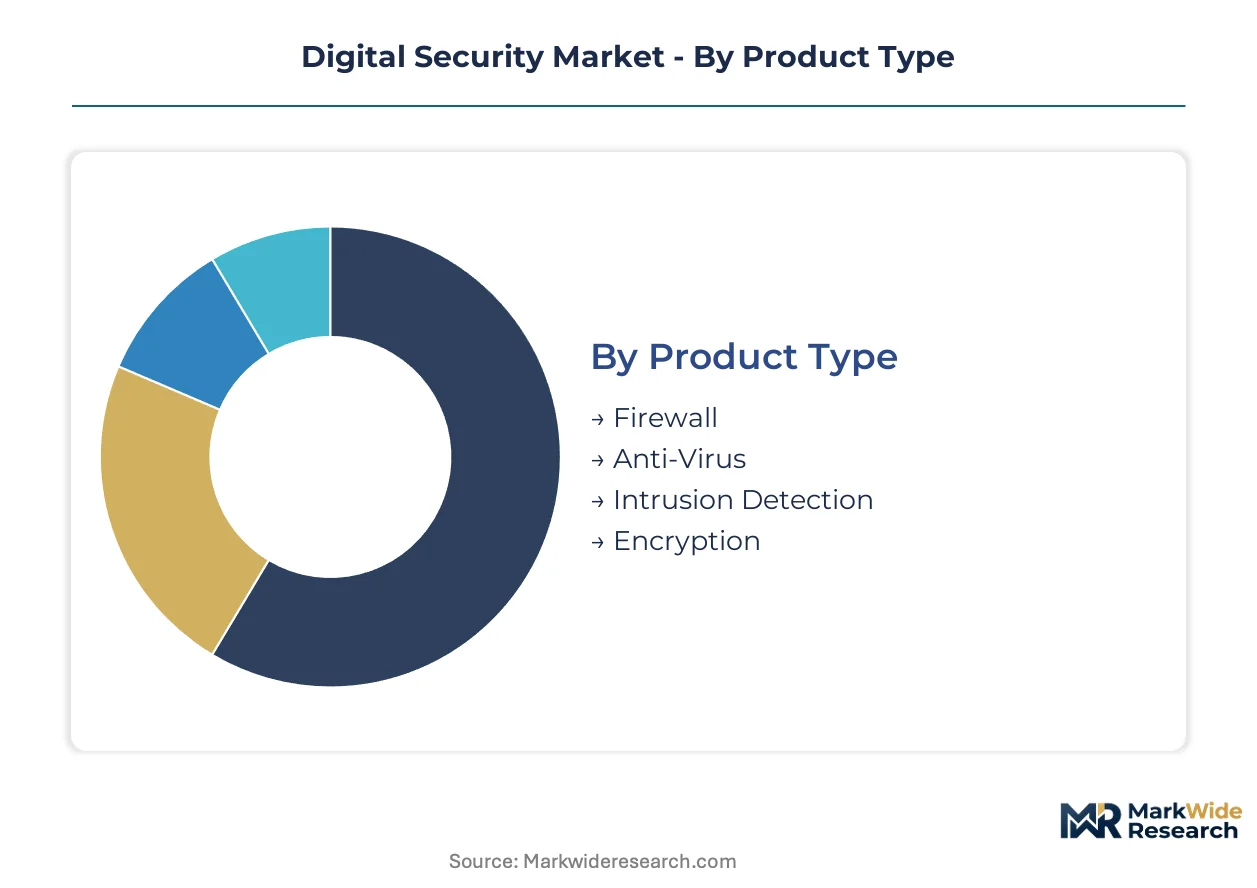
Digital security procurement splits across four fundamental axes that determine integration architecture, pricing models, and compliance requirements. Product type dictates capital intensity and refresh cycles. Technology selection governs automation depth and threat response velocity. End user verticals impose sector-specific certification mandates. Deployment mode shapes operational control and recurring cost structures.
Product Type:
Standalone perimeter products dominate legacy infrastructure, while embedded cryptographic modules integrate directly into application stacks and hardware roots of trust.
- Firewall:Network traffic inspection appliances and software-defined perimeter controllers enforce policy at protocol boundaries. United States federal agencies and defense contractors concentrate procurement here under zero-trust architecture mandates, with FIPS 140-2 certification now table stakes for new awards.
- Encryption:Data-at-rest and data-in-transit cryptographic implementations span symmetric algorithms, public-key infrastructure, and quantum-resistant protocols. Banking networks in Germany and France prioritize end-to-end encryption for SWIFT connectivity and GDPR-aligned data residency requirements.
- Anti-Virus:Signature-based and heuristic malware detection systems operate across endpoints and email gateways.
- Intrusion Detection:Network and host-based anomaly detection systems monitor traffic patterns for policy violations and threat indicators.
Firewall deployments lead volumes today; encryption solutions are gaining share fastest as regulatory data protection mandates harden.
Technology:
Foundation technologies determine automation autonomy, with inference engines operating at sub-millisecond latency while distributed ledgers anchor immutable audit trails.
- Artificial Intelligence:Neural network architectures for behavioral anomaly detection and autonomous threat response compress mean-time-to-remediation metrics. Healthcare systems in the United States deploy AI-driven security operations centers to manage HIPAA breach notification compliance with limited analyst headcount.
- Machine Learning:Supervised and unsupervised learning pipelines for threat intelligence correlation and predictive vulnerability scoring. Retail payment processors favor ML-powered fraud detection that adapts to transaction pattern shifts without rule-base rewrites.
- Blockchain:Distributed ledger implementations for identity verification and supply chain integrity attestation.
- Biometric:Fingerprint, facial recognition, and behavioral biometric authentication systems for identity assurance.
Artificial Intelligence anchors the largest R&D allocations currently; Machine Learning is climbing the fastest as managed service wrappers democratize access.
End User:
Vertical concentration varies sharply by assurance requirements, with certified high-assurance procurement in regulated sectors and utility-priced consumption in commercial segments.
- Banking:Tier-1 financial institutions mandate Common Criteria EAL4+ certification for cryptographic modules and maintain dedicated security operations centers. German and French banking regulators enforce stringent technical documentation requirements under the EU AI Act for automated fraud detection systems.
- Government:National security and civilian agencies specify supply chain provenance and domestic encryption standards. United States federal procurement requires NIST SP 800-53 controls and CMMC certification for defense industrial base contractors.
- Healthcare:Hospital networks and payer organizations balance HIPAA compliance with cloud migration imperatives.
- Retail:E-commerce platforms and point-of-sale networks prioritize PCI-DSS compliance and payment fraud mitigation.
Banking commands premium pricing tiers today; Healthcare is expanding procurement most quickly as electronic health record digitization accelerates.
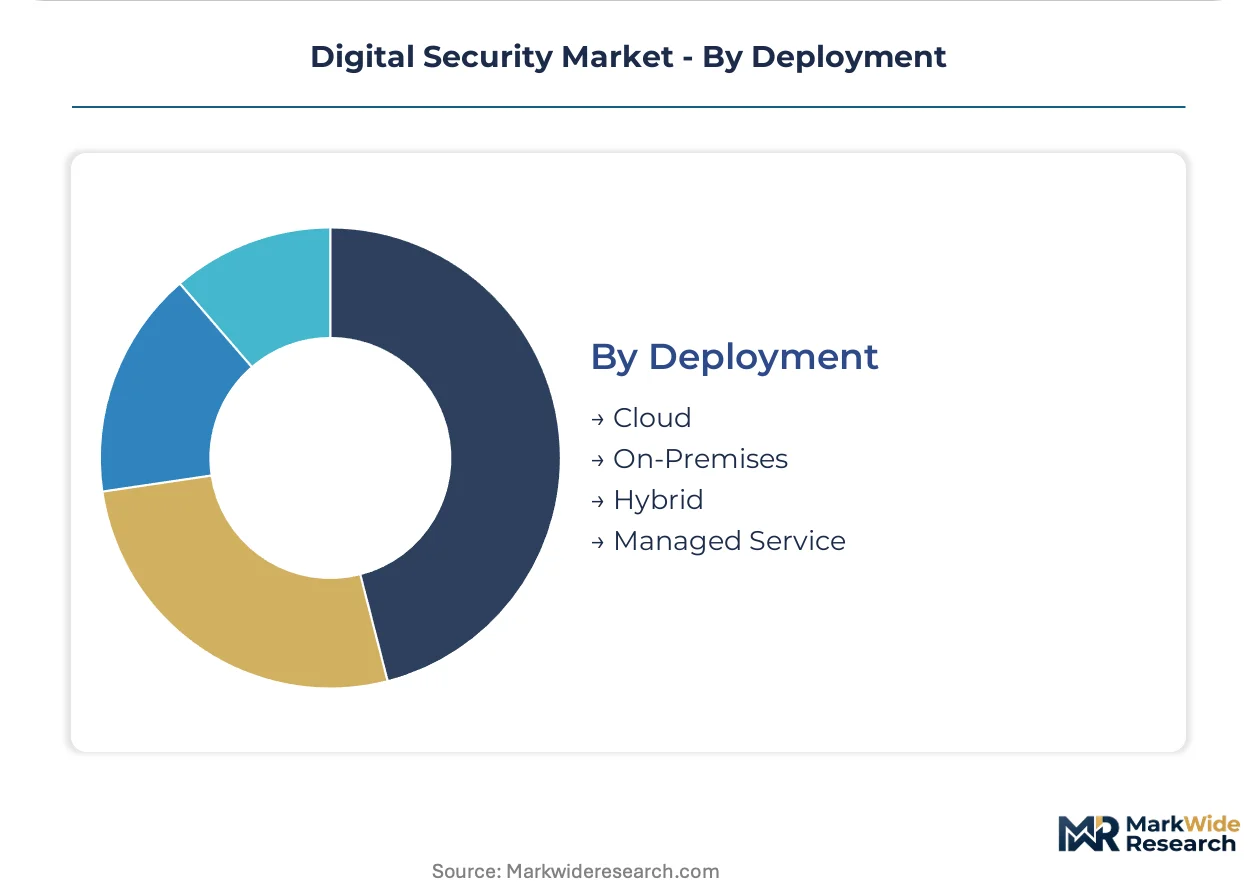
Deployment:
Delivery models segment by operational control retention, with self-managed stacks preserving customization latitude and outsourced functions transferring accountability.
- Cloud:Native security services delivered through hyperscaler marketplaces and independent software vendor SaaS platforms. United States technology enterprises favor cloud-native deployment to align security spending with actual consumption and eliminate data center overhead.
- Managed Service:Outsourced security operations, threat hunting, and incident response delivered through subscription contracts. Mid-market manufacturers in Japan adopt METI-aligned managed detection and response to address certified security architect scarcity without internal hiring.
- On-Premises:Customer-operated hardware and software installations within owned or colocated facilities.
- Hybrid:Orchestrated security stacks spanning cloud and on-premises environments with unified policy management.
Cloud delivery leads new contract value today; Managed Service is expanding most quickly as mid-market buyers prioritize operational simplicity over control retention.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Certified security architects cluster in the United States, Germany, and Japan, anchoring procurement sophistication and compliance infrastructure across three distinct regulatory spheres.
United States
Federal agencies and defense contractors drive zero-trust architecture mandates under NIST SP 800-53 and CMMC certification requirements. The SEC's cybersecurity disclosure rules impose board-level accountability for breach reporting timelines. Silicon Valley and the Washington DC metro area concentrate cloud-native security R&D and federal procurement headquarters respectively.
Germany
Automotive and banking verticals demand Common Criteria EAL4+ certification for cryptographic modules under BSI technical guidelines. The EU AI Act's risk-based classification system compels enterprises to maintain audit-ready security infrastructure. Munich and Frankfurt host the densest concentrations of industrial cybersecurity operations and financial services security procurement.
Japan
Critical infrastructure operators adopt METI-aligned managed detection and response services to address certified security architect scarcity. The Ministry of Economy, Trade and Industry's cybersecurity framework creates certified product demand for manufacturing and energy facilities. Tokyo and Osaka anchor domestic vendor headquarters and enterprise security operations center deployment.
France
Banking regulators under ACPR and CNIL enforce stringent technical documentation requirements for automated fraud detection systems. The EU AI Act mandates human oversight mechanisms for high-risk AI security applications. Paris concentrates fintech security procurement and regulatory affairs functions for continental European operations.
United Kingdom
Financial services firms align cybersecurity procurement with Bank of England operational resilience requirements and FCA guidelines. Post-Brexit regulatory divergence creates parallel certification tracks for vendors serving EU and UK markets. London's City and Canary Wharf clusters dominate European financial services security spending and threat intelligence operations.
Digital Security Market Vendor Landscape
The competitive structure tilts toward platform consolidation. Scaled providers with dedicated regulatory affairs functions capture disproportionate share as compliance complexity fragments mid-tier vendor economics. Three archetypes dominate: hyperscale cloud platforms with native security stacks, network-focused hardware-software integrators, and endpoint-centric AI-native specialists. M&A activity concentrates around cloud-native security services and managed detection response capabilities.
Within the platform tier, Microsoft anchors enterprise contracts across regulated industries through cloud-native integration. Palo Alto Networks and CrowdStrike Holdings occupy positions at opposite ends of the network-to-endpoint spectrum, representing the segmentation-specialist and AI-native archetypes respectively. These three exemplify how scale and architectural focus determine competitive positioning under escalating certification requirements.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Microsoft |
| Palo Alto Networks |
| Fortinet, Inc. |
| IBM Corporation |
| Check Point Software Technologies Ltd. |
| CrowdStrike Holdings, Inc. |
| Trend Micro, Inc. |
| Broadcom, Inc. |
| Others |
Supply Flow & Price Mechanics
Certification-grade divergence between Common Criteria EAL4+ products and uncertified commercial alternatives manifests in both pricing power and supply chain configuration. Premium-tier vendors source specialized cryptographic hardware from certified fabs while commodity players draw from standard semiconductor channels, creating parallel procurement ecosystems with divergent margin structures.
Pricing Analysis
Bundled managed detection and response services command annual recurring revenue premiums over unbundled point-product licensing. Pricing stratifies across certified high-assurance, enterprise-grade, and mid-market tiers, with Common Criteria certification and FedRAMP authorization driving the widest spreads. Pricing pressure stems from hyperscaler-native security bundles absorbing standalone vendor volumes. Mid-market healthcare buyers exhibit highest price sensitivity due to HIPAA compliance cost burdens, while federal defense contractors show lowest sensitivity under zero-trust architecture mandates.
Supply Chain Analysis
Specialized encryption processor supply rests on Taiwanese foundry capacity and South Korean memory fabrication. Raw material dependencies span silicon wafers, hardware security modules, and quantum-resistant cryptographic IP cores. Single-source vulnerability concentrates in FIPS 140-2 certified chip packaging facilities. Distribution runs through value-added resellers with federal contracting clearances, hyperscaler marketplaces, and direct enterprise field sales.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Geographic-arbitrage opportunities emerge from compliance cost differentials between EU AI Act jurisdictions and US SEC disclosure regimes, with certification investment requirements running higher in European markets.
For Market Incumbents: Deploy regulatory affairs scale as a competitive moat. Accelerate Common Criteria pre-certification for next-generation AI-driven threat detection modules before EU AI Act enforcement hardens. Acquire managed detection and response specialists to displace mid-market point-product vendors facing certification cost fragmentation. For New Entrants and Emerging Players: Cloud-native channel partners with hyperscaler marketplace presence offer the fastest path to revenue. Target Japanese manufacturing mid-market accounts where METI-aligned managed services address certified security architect scarcity. Lead with consumption-based pricing that eliminates upfront capital intensity for hospital networks migrating electronic health records. For Investors and Strategic Acquirers: Consolidation pressure builds where compliance cost escalation fragments mid-tier vendor economics. Frame long-term viability around platform consolidation winners with dedicated regulatory affairs functions and hyperscaler co-sell relationships. Watch hyperscaler security bundle attach rates as the critical inflection signal for standalone vendor displacement risk.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and cloud telemetry under single policy orchestration for federal zero-trust mandates. |
| Acquisition of Specialist Firm | Adds managed detection and response capabilities to address mid-market buyer preference for outsourced security operations. |
| Geographic Expansion | Establishes EU AI Act compliance infrastructure ahead of high-risk system documentation requirements in France and Germany. |
| Strategic Partnership | Secures hyperscaler marketplace placement to counter native security bundle absorption of standalone procurement. |
| Product Launch | Introduces quantum-resistant encryption modules aligned with NIST post-quantum cryptographic standards for banking networks. |
Methodological Framework
Quantitative tracking and qualitative interviews ran in parallel throughout the study window. Primary fieldwork engaged chief information security officers, federal procurement officers, healthcare IT directors, cloud platform engineers, and regulatory affairs leads at security vendors. Secondary validation drew from SEC cybersecurity disclosure filings, NIST SP 800-53 control baselines, EU AI Act technical documentation requirements, and CMMC certification databases. Bottom-up contract value aggregation and top-down market sizing triangulated volume estimates.
Segment-weighting approaches distributed value across product type, technology layer, end-user vertical, and deployment mode dimensions. The analytical framework modeled adoption curves across the projection horizon, with CAGRs derived from regression against historical procurement velocity and regulatory enforcement timelines. Forecast inputs incorporated HIPAA breach notification incident rates, federal zero-trust architecture spending directives, and hyperscaler security revenue disclosures.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to EU AI Act enforcement calibration and quantum computing threat timeline acceleration. Forecasts reflect documented assumptions about regulatory implementation pace and semiconductor supply normalization. A small set of triggers—hyperscaler bundle attach rate inflection, Common Criteria evaluation backlog expansion, and federal CMMC deadline acceleration—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Global Container and Kubernetes Security Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
Global Patch Management Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
United States Cybersecurity Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Global Internet Security Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Endpoint Security Market