
 M2M Network Security Market | 2026-2036
M2M Network Security Market Size, Share, and Industry Trends Forecast 2026-2036
M2M Network Security Market Analysis
The gap between premium hardware-anchored security stacks and commodity software-only layers is rebalancing as enterprise buyers demand deterministic latency guarantees in industrial settings. Cisco Systems leverages its router-to-cloud architecture to sustain integrated threat visibility across cellular and fixed-line M2M backbones. Thales Digital Identity & Security anchors its position through embedded SIM and hardware security module specialization in automotive and aerospace supply chains. Sierra Wireless competes by extending its module-level security firmware into managed connectivity services for logistics and utility meters.
M2M network security encompasses cryptographic protocols, access control mechanisms, and traffic monitoring systems engineered to protect machine-to-machine communications across cellular, satellite, and fixed networks, typically operating with sub-100-millisecond latency thresholds for time-critical industrial control loops. Its primary purpose is to prevent unauthorized device provisioning, data exfiltration, and command injection in unattended endpoints operating at massive scale. The solution dimension shows firewall and encryption categories absorbing the majority of procurement budgets as enterprises retrofit legacy SCADA and telemetry networks. Cloud-based and hybrid deployment models are expanding fastest among mid-market industrial automation buyers seeking to avoid capital-intensive on-premises security appliances. Authentication solutions represent a concentrated margin pool where hardware token and certificate lifecycle management capabilities command pricing premiums over baseline password or API-key approaches.
The Federal Communications Commission in the United States, the European Union Agency for Cybersecurity under the Cybersecurity Act, and the EU's NIS2 Directive collectively shape device certification timelines, incident reporting obligations, and baseline encryption standards for cross-border M2M traffic. These frameworks compel module manufacturers and network operators to embed security-by-design principles rather than retrofit protections after deployment. Stakeholders must monitor evolving national implementation timelines for NIS2 across EU member states and assess whether fragmented compliance requirements will favor regional security specialists over global platform vendors.
Market Dynamics
Embedded hardware security modules are displacing software-only encryption stacks as industrial automation buyers in Germany and Japan demand deterministic sub-50-millisecond latency guarantees for unattended machine control loops. This hardware pivot is compressing procurement timelines and fragmenting vendor qualification standards across automotive supply chains.
Growth Catalysts
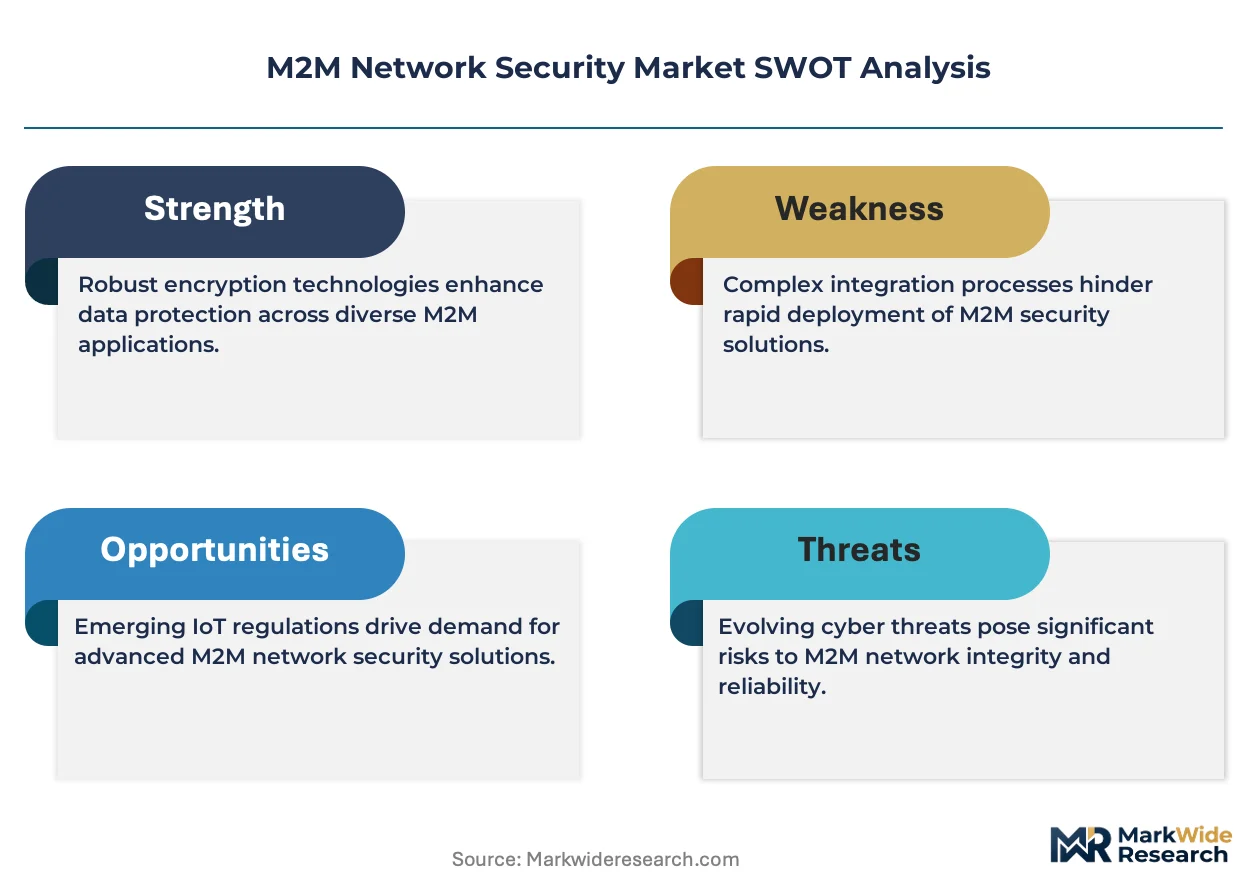
- EU Cybersecurity Act certification mandates:Device manufacturers must achieve Common Criteria EAL4+ ratings before connecting to critical infrastructure networks, accelerating replacement cycles for legacy telemetry hardware.
- Automotive fleet telematics:Connected vehicle platforms in Germany and the United States are embedding over-the-air firmware update capabilities that require hardware-anchored root-of-trust architectures.
- Industrial control loop latency requirements:Manufacturing clusters in Japan and South Korea are specifying sub-100-millisecond encrypted command-response thresholds that software-only stacks cannot guarantee.
Market Restraints
- Semiconductor foundry concentration:Advanced security chip fabrication concentrates in Taiwan, exposing module vendors to single-source supply disruptions and extended qualification timelines.
- EU NIS2 Directive implementation fragmentation:Member states are interpreting incident reporting obligations inconsistently, creating compliance cost duplication for cross-border M2M service providers.
- Commodity microcontroller substitution:Low-cost general-purpose processors without dedicated cryptographic accelerators threaten pricing floors for hardware-anchored security stacks in price-sensitive utility meter deployments.
Strategic Opportunities
- Satellite-terrestrial convergence:Low-earth-orbit backhaul is converging with cellular M2M in remote mining and maritime applications, opening greenfield deployments beyond terrestrial coverage limits.
- India industrial automation corridor:The country's Production Linked Incentive scheme for electronics manufacturing is attracting module vendors to establish local certification and assembly capabilities.
- Post-quantum cryptographic migration:NIST-standardized lattice-based algorithms create upgrade revenue streams for enterprises holding decade-long infrastructure depreciation schedules.
Industry Challenges
- Embedded systems security engineering talent:Shortages of firmware developers with hardware security module integration experience are extending product development cycles by six to twelve months.
- Legacy SCADA protocol retrofit complexity:Brownfield industrial sites running Modbus and DNP3 require protocol gateway architectures that introduce new attack surfaces and certification scope expansion.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | M2M Network Security Market |
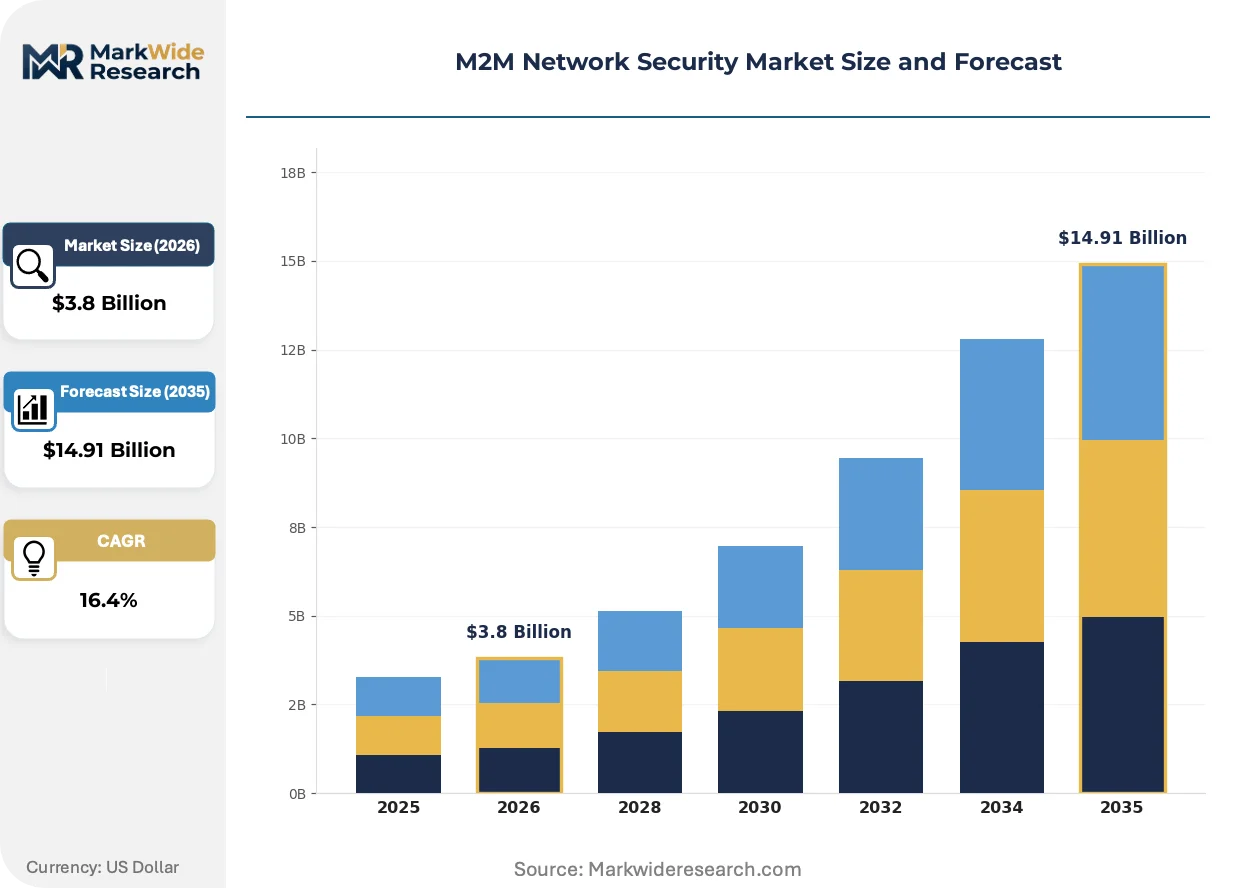
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $14.91 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, Intrusion Detection System, Encryption, Authentication Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Application: Healthcare, Automotive, Industrial Automation, Smart Home End User: Enterprises, Government, Telecom Operators, Others |
| Companies Covered | Sierra Wireless, NetComm Wireless, Cisco Systems, Telit, Digi International, Thales Digital Identity & Security, Eurotech, Verizon, KORE Wireless, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
M2M Network Security Market Emerging Trajectories
Hardware-anchored trust architectures are converging with cloud-native security orchestration platforms, compressing the traditional boundary between edge device protection and centralized threat intelligence. This fusion is redrawing competitive boundaries among module manufacturers, network operators, and cybersecurity software vendors.
Post-quantum cryptographic algorithms are converging with existing ECC and RSA implementations through hybrid certificate chains that maintain backward compatibility while enabling future-proofing. Automotive OEMs in Germany and aerospace suppliers in France are piloting these dual-signature schemes for long-lifecycle vehicle platforms. The structural consequence is converging with hardware security module refresh cycles, as existing HSMs lack the throughput to handle larger lattice-based key sizes at industrial latency thresholds.
The European Union Agency for Cybersecurity is mandating Common Criteria EAL4+ evaluations for all M2M devices connecting to critical infrastructure under the Cybersecurity Act framework. This certification requirement is forcing module vendors to maintain parallel product lines: one for regulated European markets and another for less stringent geographies. Industrial automation buyers in Germany are responding by consolidating procurement around vendors with established EU-notified body relationships, compressing qualification timelines for second-tier suppliers.
Buyer procurement patterns are compressing from capital-intensive appliance purchases toward subscription-based managed security service contracts. Mid-market logistics operators in the United States and utility cooperatives in rural Germany are displacing on-premises firewall deployments with cellular-operator-provided security stacks embedded in connectivity tariffs. This shift is most visible in fleet telematics, where transportation managers prioritize operational expenditure predictability over hardware ownership flexibility.
M2M Network Security Market Segmentation
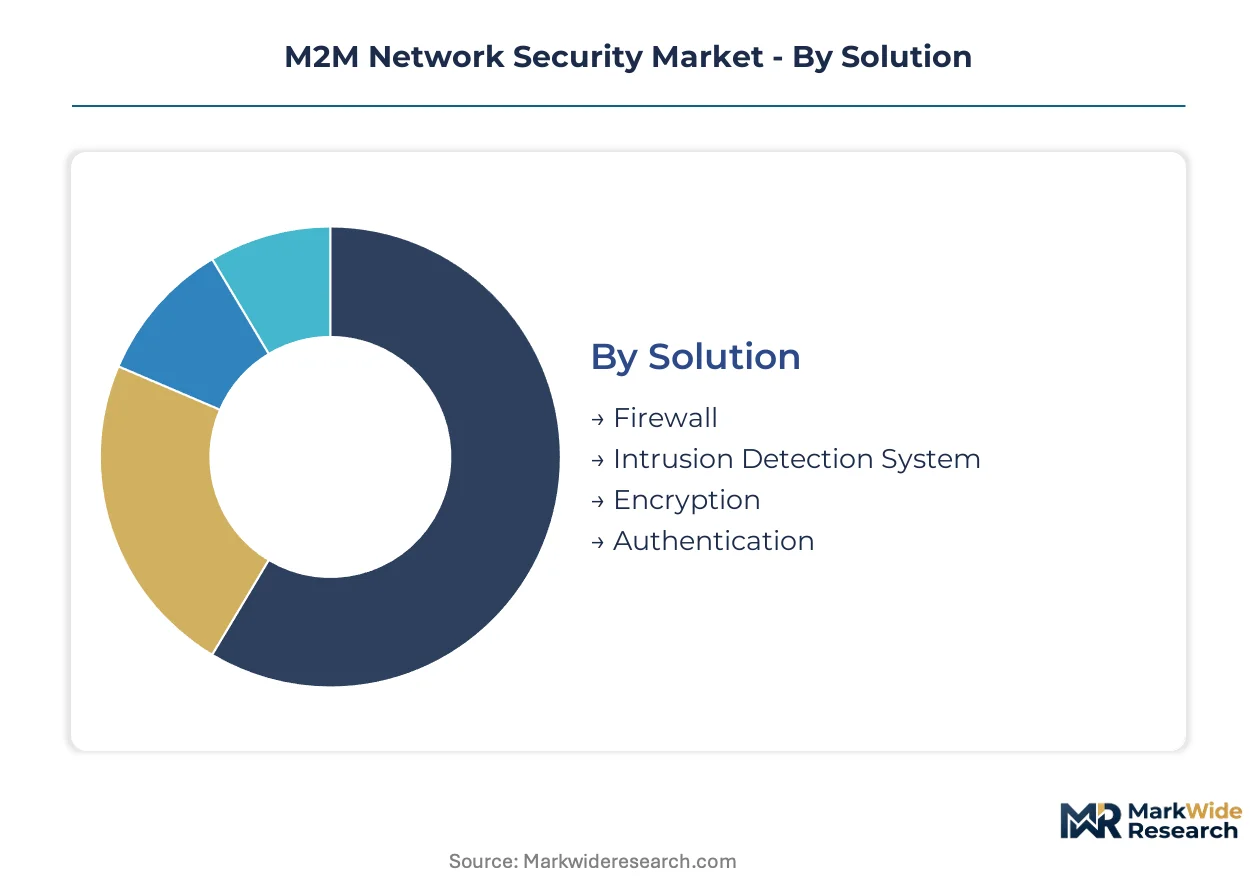
M2M network security procurement patterns diverge sharply across solution architectures and operational contexts. Buyers segment investments based on latency tolerance, regulatory exposure, and legacy infrastructure constraints rather than uniform threat models.
Solution:
Firewall and encryption layers dominate capital allocation as industrial buyers retrofit brownfield telemetry networks with deterministic latency guarantees.
- Firewall:Deep packet inspection engines filter command traffic in SCADA backbones. German automotive clusters specify sub-50-millisecond throughput thresholds that compress vendor qualification timelines.
- Encryption:Hardware-anchored cryptographic stacks displace software-only implementations in Japan and South Korea. Manufacturing control loops demand AES-256 acceleration without latency penalty.
- Intrusion Detection System:Behavioral analytics monitor anomalous M2M traffic patterns across cellular backbones.
- Authentication:Certificate lifecycle management commands pricing premiums over API-key approaches in regulated healthcare deployments.
Mature deployment sits with firewall appliances. Newer deployment is concentrated in hardware-anchored encryption modules.
Deployment Model:
Cost tier differentiation separates capital-intensive appliance buyers from subscription-oriented mid-market operators.
- Cloud-Based:Security orchestration platforms deliver centralized threat intelligence without on-premises hardware. Mid-market logistics operators in the United States prioritize operational expenditure predictability.
- Hybrid:Edge-cloud architectures balance local latency requirements with centralized analytics. Industrial automation buyers in Germany straddle legacy SCADA and modern connectivity stacks.
- On-Premises:Dedicated appliances serve critical infrastructure with air-gapped compliance requirements.
- Managed:Cellular operators embed security stacks into connectivity tariffs for rural utility cooperatives.
Volume concentration rests with cloud-based subscriptions. Steepest expansion trajectory belongs to hybrid architectures bridging operational technology and information technology domains.
Application:
End-use context dictates certification grade and procurement channel more than technical specification alone.
- Industrial Automation:Control loop security demands sub-100-millisecond encrypted command-response. Japan and South Korea specify hardware security module integration for unattended machine endpoints.
- Automotive:Connected vehicle platforms require over-the-air firmware update capabilities with hardware-anchored root-of-trust. Germany's OEM supply chains enforce Common Criteria EAL4+ certification.
- Healthcare:Patient data telemetry triggers HIPAA compliance obligations for device manufacturers.
- Smart Home:Consumer-grade M2M devices face price pressure from commodity microcontroller substitution.
Margin pool depth tracks industrial automation. Regulatory velocity is highest in automotive applications.
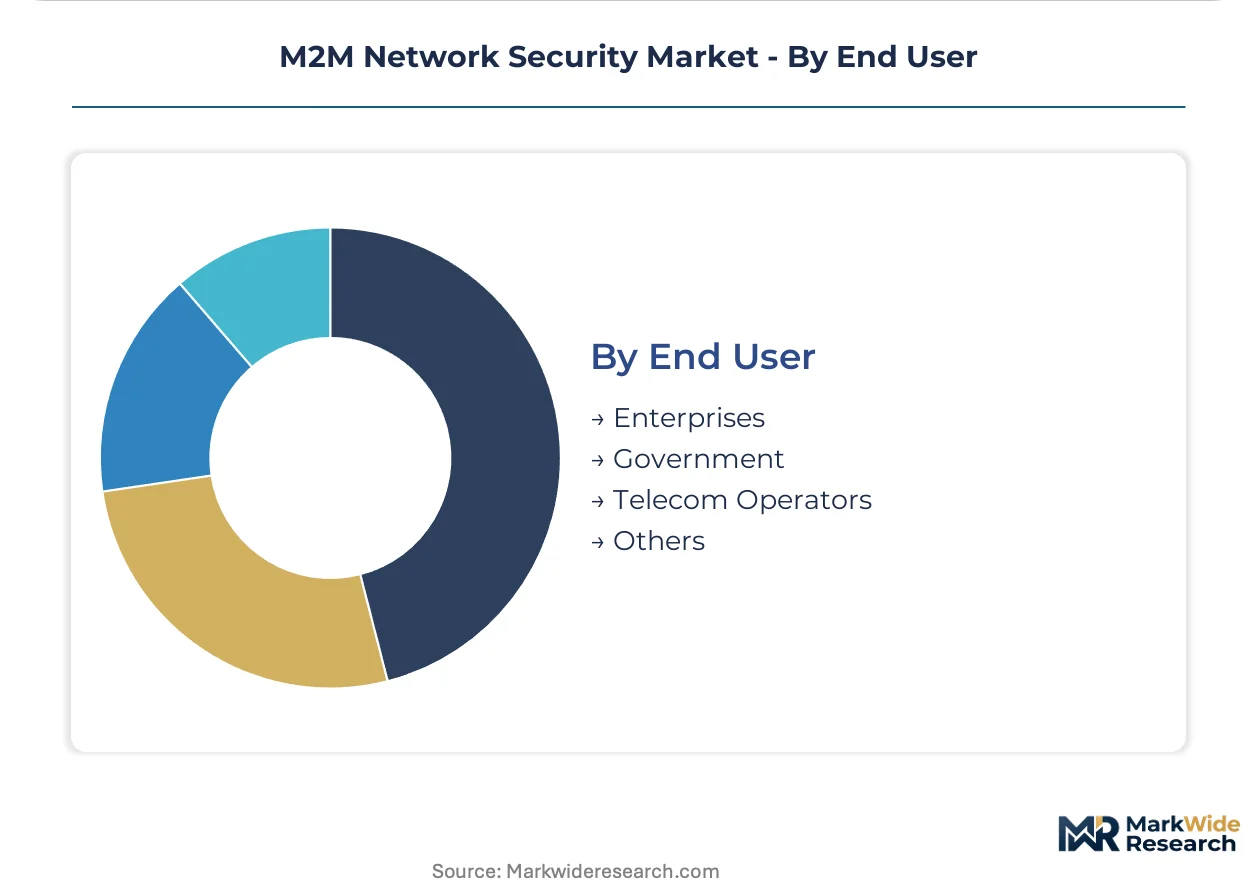
End User:
Customer type determines contract structure, incident response obligations, and vendor liability exposure.
- Telecom Operators:Managed security services bundle cellular connectivity with embedded threat monitoring. German and United States carriers monetize security as a tariff tier differentiator.
- Enterprises:Industrial conglomerates consolidate procurement around vendors with established EU-notified body relationships.
- Government:Critical infrastructure mandates under EU Cybersecurity Act accelerate replacement cycles for legacy telemetry hardware.
- Others:Utility cooperatives and agricultural consortiums represent fragmented, price-sensitive demand.
Procurement standardization is most advanced among telecom operators. Compliance cost duplication burdens government buyers navigating NIS2 implementation fragmentation.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Stuttgart anchors automotive M2M security deployment, where OEM supply chains enforce hardware-anchored root-of-trust architectures for connected vehicle platforms. The city's industrial automation clusters demand sub-50-millisecond latency guarantees that reshape procurement patterns across European markets.
United States
Fleet telematics operators and utility cooperatives drive managed security service adoption. The FCC shapes device certification timelines and baseline encryption standards for cross-border M2M traffic. Detroit's automotive corridors embed over-the-air firmware capabilities with hardware security module integration.
Germany
Industrial automation buyers in Baden-Württemberg and Bavaria consolidate procurement around vendors with EU-notified body relationships. The Cybersecurity Act mandates Common Criteria EAL4+ ratings for critical infrastructure connectivity. Munich's automotive OEMs enforce deterministic latency thresholds that compress vendor qualification timelines.
Japan
Manufacturing control loops in Nagoya and Osaka specify hardware security module integration for unattended machine endpoints. METI guidelines accelerate replacement cycles for legacy telemetry hardware. Toyota's supplier ecosystem demands AES-256 acceleration without latency penalty in embedded frameworks.
South Korea
Semiconductor and electronics manufacturers in Seoul and Gyeonggi-do specify sub-100-millisecond encrypted command-response thresholds. The Korea Internet and Security Agency certifies M2M devices for critical infrastructure networks. Samsung's industrial automation partners embed post-quantum cryptographic readiness in long-lifecycle platforms.
India
The Production Linked Incentive scheme for electronics manufacturing attracts module vendors to establish local certification capabilities. TRAI regulations shape baseline security requirements for IoT and M2M device deployment. Bangalore's technology corridors host pilot programs for industrial automation security frameworks.
M2M Network Security Market Vendor Landscape
Capital-heavy producers compete with asset-light designers across the M2M security stack, creating tiered competitive dynamics. The market fragments across module manufacturers, network operators, and cybersecurity software vendors rather than consolidating around unified platforms. Three archetypes dominate: integrated router-to-cloud architects, embedded hardware security specialists, and managed connectivity service providers. Competitive moves concentrate on strategic partnerships bridging cellular infrastructure with cloud-native orchestration, plus portfolio diversification into satellite-terrestrial convergence.
Within the integrated platform tier, Cisco Systems and Thales Digital Identity & Security exemplify contrasting approaches to hardware-anchored trust architectures. Sierra Wireless occupies a position among module-level specialists extending firmware capabilities into managed services. These three anchors represent the spectrum from enterprise networking heritage through aerospace supply chain specialization to cellular module origination.
| Leading Market Players |
|---|
| Sierra Wireless |
| NetComm Wireless |
| Cisco Systems |
| Telit |
| Digi International |
| Thales Digital Identity & Security |
| Eurotech |
| Verizon |
| KORE Wireless |
| Others |
Supply Flow & Price Mechanics
EU Cybersecurity Act certification mandates for Common Criteria EAL4+ ratings are compressing procurement timelines and forcing module vendors to absorb upfront qualification costs before revenue recognition, shifting pricing power toward buyers with established EU-notified body relationships.
Pricing Analysis
Throughput-based subscription tiers anchor pricing for managed security services, with cellular operators monetizing embedded threat monitoring as connectivity tariff differentiators. Price differentiation separates Common Criteria EAL4+ certified stacks from uncertified alternatives, with German automotive OEMs paying premiums for deterministic sub-50-millisecond latency guarantees. Cost compression in commodity microcontroller tiers is intensifying because low-cost general-purpose processors without cryptographic accelerators threaten hardware-anchored security pricing floors. Rural utility cooperatives exhibit highest price sensitivity, while aerospace suppliers in France demonstrate lowest sensitivity due to decade-long platform lifecycles.
Supply Chain Analysis
Dual-sourcing requirements from German automotive OEMs and Japanese industrial automation buyers mandate parallel qualification of security chip suppliers across Taiwan, South Korea, and the United States. Advanced security module fabrication draws from silicon wafers, cryptographic IP cores, and embedded firmware stacks. Single-source vulnerability concentrates in Taiwan foundry capacity for hardware security modules. Distribution runs through cellular operator channel partnerships and direct OEM supply agreements.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market reads as a cost-of-compliance story where EU NIS2 Directive implementation creates a barrier-to-entry moat for vendors with established EU-notified body relationships and pre-qualified hardware security module supply chains.
For Market Incumbents: Acquire post-quantum cryptographic IP portfolios to preempt NIST-standardized lattice-based algorithm migration cycles. Deepen backward integration into hardware security module design to defend against semiconductor foundry concentration risks in Taiwan. Consolidate EU certification capabilities to compress second-tier supplier qualification timelines. For New Entrants and Emerging Players: The mid-market pricing gap between premium hardware-anchored stacks and economy software-only layers opens white-space in Indian industrial automation corridors under Production Linked Incentive schemes. Satellite-terrestrial convergence applications in remote mining and maritime represent the most penetrable deployment context. Pursue cellular operator white-label partnerships to bypass direct OEM procurement barriers. For Investors and Strategic Acquirers: Re-rating potential sits with embedded hardware security specialists given post-quantum cryptographic refresh cycle catalysts. Long-term viability favors vendors with automotive and aerospace supply chain anchoring. Target acquisition archetypes include module-level firmware developers with managed services extensions. Watch NIS2 implementation fragmentation across EU member states as inflection indicator for compliance cost duplication winners.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptographic Migration | NIST lattice-based algorithms create upgrade revenue streams for enterprises with decade-long depreciation schedules. |
| EU-Notified Body Certification Investment | Common Criteria EAL4+ pre-qualification compresses procurement timelines for German automotive OEM supply chains. |
| Satellite-Terrestrial Convergence Partnership | Low-earth-orbit backhaul integration opens greenfield deployments beyond terrestrial cellular coverage limits. |
| Hardware Security Module Backward Integration | In-house cryptographic accelerator design mitigates Taiwan foundry concentration and single-source supply risk. |
| Managed Security Service Subscription Launch | Cellular operator tariff embedding captures mid-market logistics operators seeking operational expenditure predictability. |
Methodological Framework
Regulatory filings from ENISA, FCC dockets, and EU Cybersecurity Act implementation guidance formed the secondary backbone, cross-referenced with primary interviews involving cellular operator security architects, automotive OEM procurement leads, industrial automation system integrators, and hardware security module firmware developers. Bottom-up module shipment analysis triangulated against top-down enterprise security spending surveys.
Historical trendline analysis of embedded security module deployments informed projection modeling across solution architecture, deployment model, application context, and end-user type dimensions throughout the forecast period. CAGRs derived from segment-level growth rate reconciliation against macroeconomic indicators and regulatory implementation timelines. Industry-specific inputs included Common Criteria certification pipeline tracking and semiconductor foundry capacity allocation disclosures.
Underlying measurement precision varies by segment; firewall and encryption categories carry tighter precision than emerging intrusion detection system deployments due to established procurement reporting channels. Forecasts reflect documented assumptions regarding NIS2 implementation uniformity and post-quantum cryptographic standardization velocity. Deviation in EU member state NIS2 transposition timelines or Taiwan foundry supply disruptions would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Thailand IT and Security Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Digital Security Market
Cybersecurity
Cloud Security Gateway Market
Cybersecurity
South Korea Ransomware Protection Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Application-Level Encryption Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Benelux Cybersecurity Market