
 Singapore Cybersecurity Market | 2026-2036
Singapore Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Singapore Cybersecurity Market Analytics
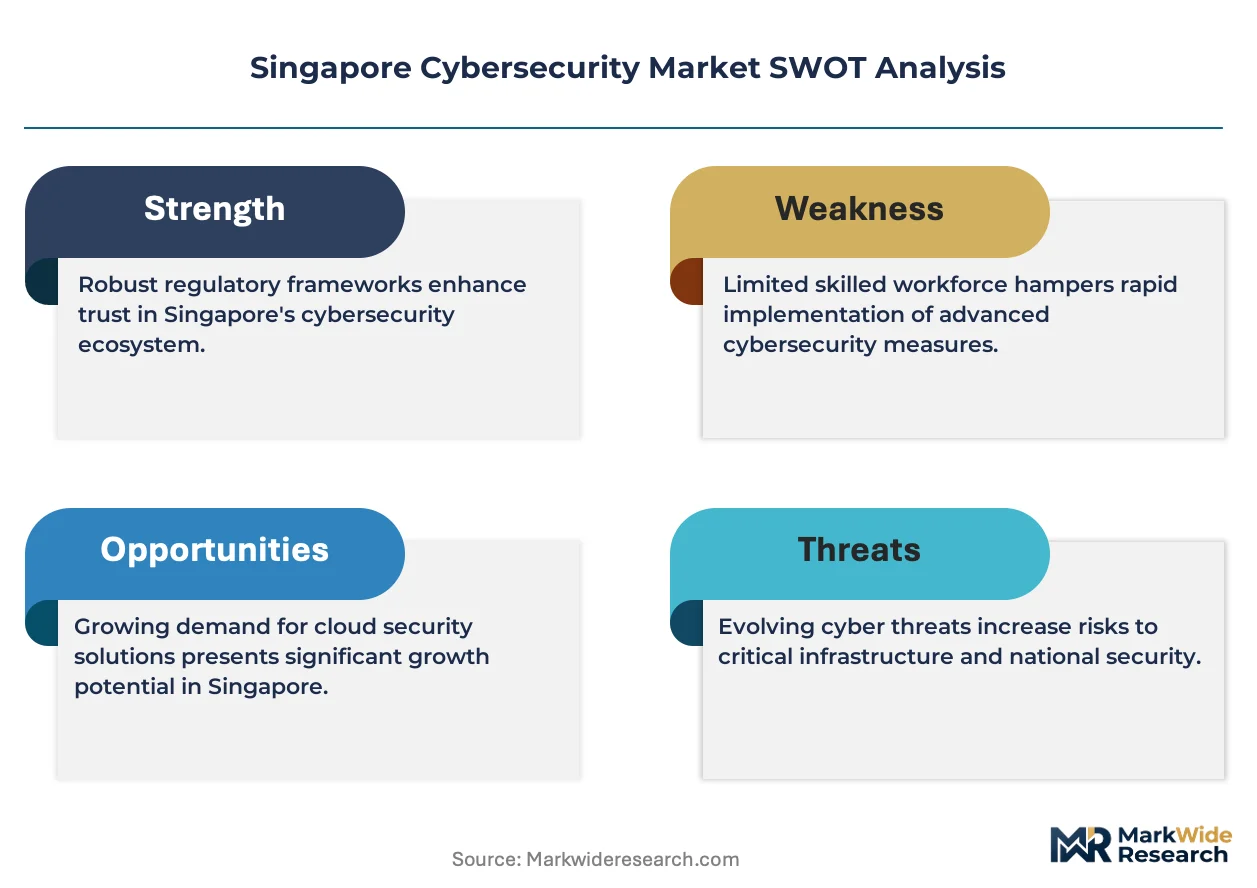
Managed security service provider channels in Singapore is fragmenting as specialized boutiques challenge incumbent telecom-linked operators. Ensign InfoSecurity leverages deep local threat intelligence capabilities to anchor high-stakes government contracts. ST Engineering Cyber competes through dual-use technology transfer from defense-grade systems into civilian infrastructure protection. Singtel Cyber Security sustains enterprise reach by bundling connectivity with monitored detection services across ASEAN regional footprints.
Singapore cybersecurity encompasses defensive technologies, operational processes, and governance frameworks designed to protect digital assets from unauthorized access, disruption, or exfiltration across enterprise and government networks. Solutions integrate encryption protocols, behavioral analytics engines, and zero-trust architecture principles to maintain confidentiality, integrity, and availability of critical information systems. Cloud deployment models now attract disproportionate investment as financial services and healthcare end users seek elastic capacity without capital-intensive infrastructure buildouts. Network security and IAM solutions command premium positioning due to complexity in securing hybrid workforce access patterns and API-driven service interconnects.
Singapore's Cyber Security Agency coordinates national strategy while the Personal Data Protection Commission enforces data breach notification and accountability requirements that directly shape procurement specifications. Monetary Authority of Singapore technology risk management guidelines impose baseline controls on financial institutions, creating compliance-driven demand for audited security services. Stakeholders must weigh sovereign data residency requirements against cloud-native agility when architecting multi-layered defense postures.
Market Dynamics
Cloud-native security architectures are compressing procurement cycles as Singapore's financial institutions abandon multi-year appliance refresh programs in favor of elastic, consumption-based protection models aligned to MAS technology risk management guidelines.
Growth Catalysts
- Personal Data Protection Act enforcement:The Commission's mandatory breach notification rules compel enterprises to maintain continuous monitoring capabilities, expanding demand for managed detection and response services across healthcare and retail sectors.
- API security investments:Open banking protocols under MAS guidelines require granular access controls, driving specialized identity and access management deployments at digital-native financial institutions.
- Smart Nation infrastructure:Government sensor networks and municipal IoT systems generate sustained procurement for operational technology security vendors with sovereign data handling clearances.
Market Restraints
- Specialized talent scarcity:Certified cloud security architects and threat intelligence analysts command compensation premiums that inflate service delivery costs beyond budget-constrained mid-market enterprises.
- Vendor concentration risk:Critical threat intelligence feeds and signature databases originate from a narrow base of US and Israeli sources, exposing domestic operators to geopolitical supply disruptions.
- Legacy system technical debt:Mainframe-dependent financial institutions face integration friction when overlaying zero-trust principles onto decades-old core banking infrastructure.
Strategic Opportunities
- Operational technology convergence:Maritime port automation and energy grid modernization create demand for industrial control system security that bridges IT-OT boundaries.
- ASEAN regional service extension:Singapore-based operators with MAS audit credentials can export compliance-aligned security operations to emerging financial centers in Vietnam and Indonesia.
- Quantum-resistant cryptography:National quantum-safe roadmap timelines are accelerating procurement for post-quantum encryption migration services among defense-adjacent contractors.
Industry Challenges
- Cross-domain certification complexity:Vendors must simultaneously satisfy MAS technology risk guidelines, CSA cybersecurity certification, and sector-specific health or defense accreditation, extending sales cycles.
- Alert fatigue remediation:Security operations centers struggle to operationalize high-volume telemetry from cloud-native detection tools, degrading mean-time-to-response metrics.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Singapore Cybersecurity Market |
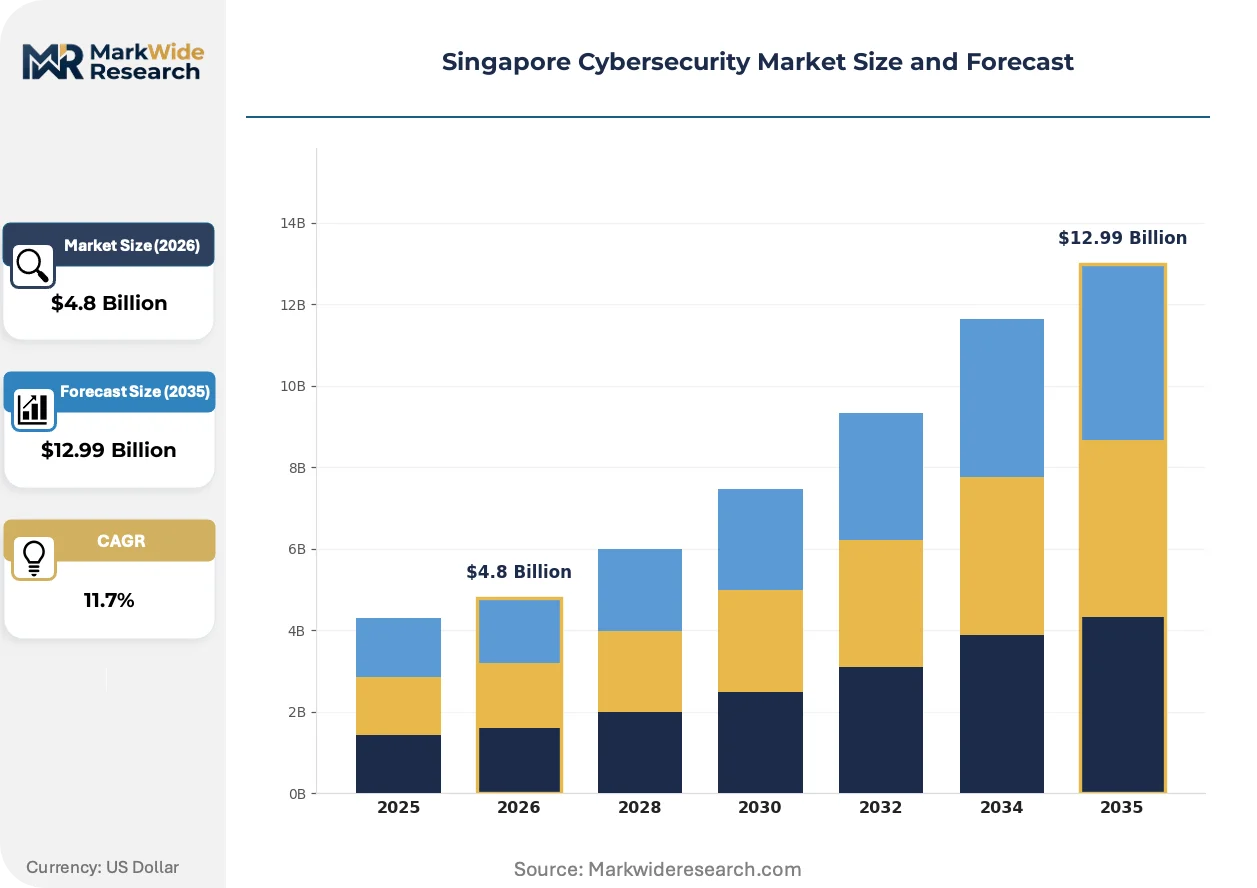
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $12.99 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Software, Hardware, Services, Solutions Deployment Model: On-premises, Cloud, Hybrid, Managed End User: Government, Financial Services, Healthcare, Retail Solution: Network Security, Endpoint Security, Data Protection, IAM |
| Companies Covered | ST Engineering Cyber, Wizlynx Group Singapore, Ensign InfoSecurity, Group-IB Singapore, Quann, Singtel Cyber Security, Horangi Cyber Security, SecureAge Technology, NCS Cybersecurity, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Singapore Cybersecurity Market Evolving Landscape
Security service delivery models are fragmenting as buyers reject monolithic annual contracts in favor of modular, API-integrated capabilities that align spending to actual threat exposure and business risk quantification.
Extended detection and response platforms are collapsing the traditional distinction between endpoint, network, and cloud security silos by unifying telemetry ingestion and automated response orchestration across hybrid environments. Large domestic banks and government agencies are adopting these consolidated stacks within eighteen-month procurement windows. This convergence is collapsing standalone point-product markets as buyers prioritize integration depth over best-of-breed functional breadth.
Monetary Authority of Singapore technology risk management guidelines now mandate independent validation of cloud control frameworks before financial institutions deploy sensitive workloads to distributed infrastructure. This regulatory pressure has spawned specialized audit and attestation services that pre-qualify vendors for accelerated procurement. Tier-one banks and digital payment operators are most affected, embedding these compliance checkpoints into vendor onboarding workflows.
Outcome-based service level agreements are displacing traditional input-based contracts across enterprise security procurement, with buyers insisting on guaranteed mean-time-to-detect and mean-time-to-respond metrics tied to penalty clauses. Managed security service providers are restructuring pricing models to absorb this performance risk. This shift is most visible among Singapore-based regional headquarters of multinational financial services firms seeking to transfer operational liability.
Singapore Cybersecurity Market Segmentation
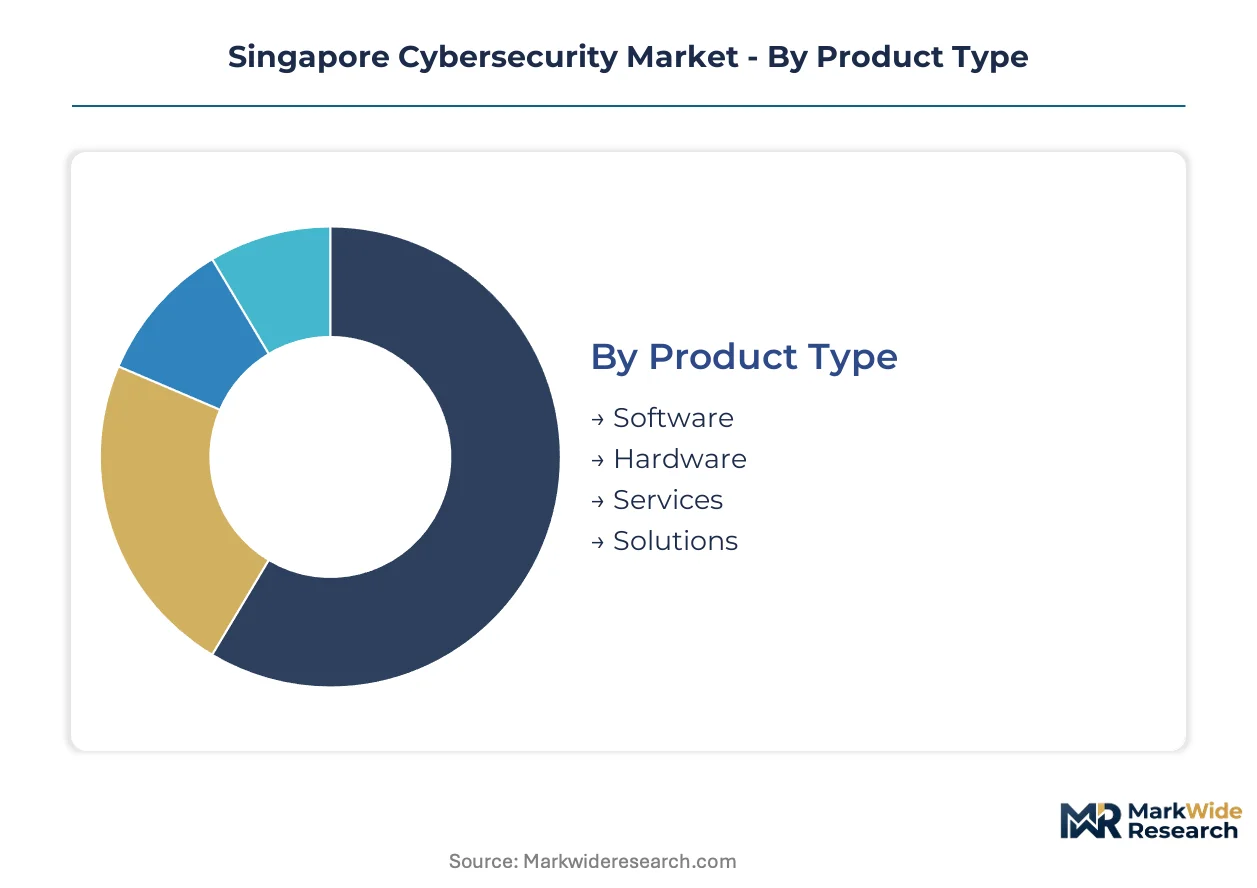
Singapore's cybersecurity procurement patterns fragment across four intersecting dimensions. Each axis reveals distinct purchasing rhythms, compliance pressures, and vendor competitive dynamics that shape how security budgets flow through enterprise and government channels.
Product Type:
Services turn over fastest with annual contract renewals, while hardware refresh cycles stretch across three to five years. Software occupies the middle ground with subscription-based velocity.
- Software:Cloud-native security platforms deliver encryption, behavioral analytics, and policy orchestration through API-integrated modules. Financial services institutions under MAS technology risk guidelines drive disproportionate procurement here, seeking elastic capacity without capital-intensive infrastructure buildouts.
- Services:Managed detection and response, security operations center outsourcing, and incident response retainers constitute the fastest-expanding revenue pool. Healthcare and retail sectors concentrate demand as Personal Data Protection Act enforcement compels continuous monitoring capabilities beyond in-house staffing limits.
- Hardware:Dedicated appliances for network segmentation, hardware security modules, and on-premise encryption gateways serve defense-adjacent contractors with sovereign data residency requirements.
- Solutions:Integrated bundles combining software, hardware, and managed services appeal to mid-market enterprises seeking single-accountability vendor relationships.
Services dominate installed base expansion. Software is where margin compression concentrates as platform consolidation accelerates.
Deployment Model:
Cloud deployments compress procurement cycles to quarterly scaling decisions, while on-premises installations require twelve-to-eighteen-month capital approval workflows. Hybrid architectures impose the longest integration timelines due to cross-environment orchestration complexity.
- Cloud:Elastic, consumption-based protection models align spending to actual threat exposure and business risk quantification. Tier-one banks and digital payment operators under MAS cloud control framework mandates drive validation-heavy procurement processes.
- Hybrid:Distributed architectures spanning private data centers and public cloud partitions serve mainframe-dependent financial institutions overlaying zero-trust principles onto legacy core banking infrastructure.
- On-premises:Air-gapped deployments persist in defense, critical infrastructure, and government sensor networks where sovereign data handling clearances override cloud agility preferences.
- Managed:Fully outsourced security operations transfer operational liability to Singapore-based regional headquarters of multinational financial services firms seeking guaranteed mean-time-to-detect metrics.
Cloud deployments dominate new budget allocation. Hybrid architectures capture the steepest expansion trajectory as regulated industries navigate technical debt constraints.
End User:
Government procurement cycles align to fiscal year appropriations with multi-year security operations contracts. Financial services refresh security stacks continuously in response to MAS guideline updates.
- Government:Cyber Security Agency-coordinated national strategy drives sustained procurement for operational technology security vendors with sovereign data handling clearances across Smart Nation infrastructure.
- Financial Services:Open banking protocols under MAS guidelines require granular access controls, driving specialized identity and access management deployments at digital-native institutions alongside incumbent banks.
- Healthcare:Personal Data Protection Commission breach notification rules compel patient data protection investments across public hospital clusters and private specialist networks.
- Retail:E-commerce payment security and customer data protection attract mid-market security spending as digital transaction volumes expand.
Financial Services dominates absolute spending volume. Healthcare is where compliance-driven expansion concentrates following enforcement intensification.
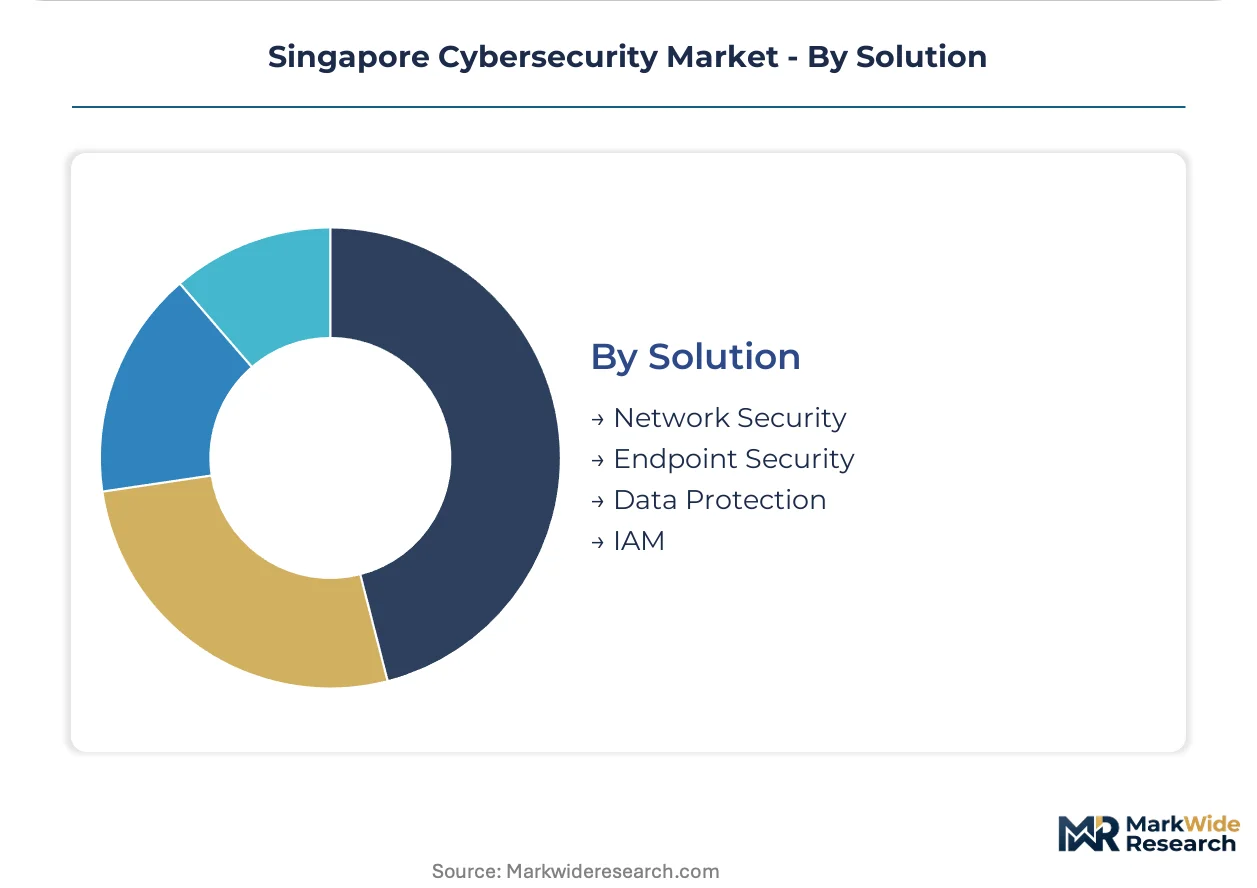
Solution:
Network security and IAM solutions command premium positioning due to complexity in securing hybrid workforce access patterns. Endpoint security refreshes most frequently as device proliferation accelerates.
- IAM:Identity and access management platforms unify workforce, customer, and machine identity governance across API-driven service interconnects. Large domestic banks adopt these consolidated stacks within compressed procurement windows.
- Network Security:Zero-trust segmentation, micro-perimeters, and software-defined perimeters protect distributed infrastructure as enterprises abandon traditional perimeter defenses.
- Endpoint Security:Extended detection and response platforms collapse the distinction between endpoint, network, and cloud security silos through unified telemetry ingestion.
- Data Protection:Encryption, data loss prevention, and privacy-enhancing technologies address Personal Data Protection Act accountability requirements across regulated sectors.
IAM dominates enterprise deal value. Endpoint security is where platform consolidation concentrates as buyers prioritize integration depth over best-of-breed functional breadth.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power concentrates in Singapore's financial district while procurement costs escalate in Jakarta and Bangkok. ASEAN neighbors import compliance-aligned security operations from Singapore-based operators holding Monetary Authority of Singapore audit credentials. This asymmetry shapes cross-border service extension strategies across Southeast Asian emerging financial centers.
Malaysia
Iskandar Malaysia's digital free zone attracts data center investments from Singapore-headquartered operators seeking lower-cost delivery nodes. Bank Negara Malaysia's technology risk management guidelines mirror MAS frameworks, easing cross-border service standardization. Kuala Lumpur's financial district sources managed detection capabilities from Singapore-based providers with sovereign data handling clearances.
Indonesia
Jakarta's digital banking expansion generates demand for identity and access management deployments at neobanks lacking mature security operations. Otoritas Jasa Keuangan regulations on electronic banking security create compliance-driven procurement for foreign operators with regional headquarters in Singapore. Surabaya's port automation projects attract industrial control system security vendors from Singapore's maritime technology cluster.
Thailand
Bangkok's open banking initiative under Bank of Thailand guidelines requires granular API access controls at commercial banks. Thai financial institutions source cloud security validation services from Singapore-based operators with pre-qualified vendor status under MAS cloud control frameworks. Eastern Economic Corridor smart city deployments generate procurement for operational technology security bridging IT-OT boundaries.
Vietnam
Ho Chi Minh City's fintech sector concentrates demand for endpoint security as digital payment operators scale transaction volumes. State Bank of Vietnam cybersecurity regulations on payment intermediaries compel continuous monitoring investments beyond local staffing capacity. Hanoi government data center modernization attracts Singapore-based operators with Cyber Security Agency certification credentials.
Philippines
Bangko Sentral ng Pilipinas digital bank licensing requirements mandate baseline security controls that exceed domestic provider capabilities. Manila-based neobanks contract Singapore-based managed security service providers for 24/7 security operations center coverage. Cebu business process outsourcing clusters generate sustained procurement for data protection services aligned to Personal Data Protection Act-equivalent local standards.
Singapore Cybersecurity Market Competitive Landscape
Telco-affiliated operators and independent specialists split the market along customer scale and compliance complexity vectors. Incumbents leverage bundled connectivity relationships to anchor enterprise accounts, while boutiques compete through deep vertical expertise and threat intelligence specialization. Three archetypes dominate: defense-technology spinoffs with sovereign clearance advantages, telecom-cybersecurity hybrids with regional network footprints, and pure-play boutiques with sector-specific compliance credentials. Competitive moves center on M&A for threat intelligence capabilities and strategic partnerships for cloud-native platform integration.
Among Singapore-based operators, Ensign InfoSecurity and ST Engineering Cyber exemplify contrasting archetypes. Ensign anchors high-stakes government contracts through local threat intelligence depth. ST Engineering Cyber occupies a position bridging defense-grade systems into civilian infrastructure protection. Singtel Cyber Security sits within the telecom-hybrid tier, sustaining enterprise reach across ASEAN regional footprints through connectivity bundling. These three patterns illustrate how vendor selection tracks customer priorities between sovereign clearance requirements, dual-use technology access, and regional service scalability.
| Leading Market Players |
|---|
| ST Engineering Cyber |
| Wizlynx Group Singapore |
| Ensign InfoSecurity |
| Group-IB Singapore |
| Quann |
| Singtel Cyber Security |
| Horangi Cyber Security |
| SecureAge Technology |
| NCS Cybersecurity |
| Others |
Value Network & Pricing Analysis
Israeli and US threat intelligence feed providers anchor the upstream layer where signature databases and adversary tracking capabilities concentrate, directing margin pools toward vendors with direct licensing relationships to these sources and squeezing Singapore-based operators lacking proprietary collection infrastructure.
Pricing Analysis
The customization-premium spread between configured-to-order managed detection services and standard SaaS-tiered endpoint protection runs wide across Singapore's procurement landscape. Subscription-based cloud security platforms dominate, with price differentiation driven by MAS audit certification tier and vertical integration depth into threat intelligence sources. Pricing pressure stems from mid-market buyers consolidating spend onto consolidated XDR stacks, compressing standalone point-product margins. Government and defense-adjacent contractors show least price sensitivity due to sovereign clearance requirements, while retail and healthcare segments negotiate aggressively on annual contract values.
Supply Chain Analysis
Tariff exposure between the United States and China dominates supply chain risk planning as hardware security modules and specialized network appliances draw from manufacturing footprints across both jurisdictions. Critical components including silicon-based encryption processors, FPGA-based packet inspection engines, and quantum-resistant cryptographic modules rest on concentrated sources in Taiwan, South Korea, and the United States. Single-source vulnerability around US-origin threat intelligence feeds creates geopolitical exposure for Singapore operators. Distribution runs through direct vendor relationships with tier-one financial institutions and government agencies, supplemented by systems integrator channels for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Singapore's cybersecurity market sits at a platform-economics inflection where API-integrated security service orchestration is displacing monolithic annual contracts, with interoperability across cloud-native detection stacks becoming the primary buyer selection criterion.
For Market Incumbents: Insulate government contract positions through accelerated Cyber Security Agency certification investments before boutique competitors achieve sovereign clearance parity. Deepen proprietary threat intelligence collection capabilities to reduce licensing exposure to US and Israeli feed providers. Vertical integration into managed security service delivery absorbs margin pressure from outcome-based SLA pricing.
For New Entrants and Emerging Players: Build out operational technology security capabilities targeting maritime port automation and energy grid modernization projects where IT-OT convergence creates specialist demand gaps. Vietnam and Indonesia offer the most penetrable geographies for compliance-aligned security operations export. Partner with Singapore-based systems integrators holding pre-existing MAS audit credentials to accelerate enterprise access.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with private equity-backed managed security service providers pursuing regional ASEAN expansion through acquisition. The five-to-ten year viability window favors platforms with demonstrated cloud-native architecture and API-first integration capabilities. Watch for MAS cloud control framework validation backlogs as an inflection signal indicating procurement acceleration among tier-one banks.
| Strategic Initiative | Industry Significance |
|---|---|
| Threat Intelligence Acquisition | Proprietary feed development reduces licensing costs and differentiates against Singtel Cyber Security's bundled offerings. |
| Cloud-Native Platform Integration | API-first architecture satisfies MAS cloud control framework mandates at digital-native financial institutions. |
| Operational Technology Security Buildout | Industrial control system capabilities capture Smart Nation infrastructure procurement from Cyber Security Agency-coordinated projects. |
| ASEAN Regional Service Extension | Export of compliance-aligned operations to Vietnam and Indonesia leverages Singapore's regulatory credibility advantage. |
| Quantum-Resistant Cryptography Migration | Post-quantum encryption services align with national quantum-safe roadmap timelines among defense-adjacent contractors. |
Research Methodology
Cross-validation between primary interviews with CISOs at domestic banks and secondary analysis of Monetary Authority of Singapore technology risk guideline enforcement patterns anchors the qualitative findings. Chief information security officers, security operations center directors, cloud procurement officers, and Cyber Security Agency certification leads provided operational perspective. Secondary sources include MAS regulatory filings, CSA cybersecurity certification databases, cloud provider capex disclosures, and enterprise security spending surveys. Bottom-up vendor revenue aggregation and top-down addressable market sizing were reconciled through iterative triangulation.
Calibration against historical procurement cycle data and regulatory implementation timelines shaped the analytical framework across the projection horizon. Segmentation dimensions modeled include deployment model, end-user vertical, solution category, and compliance complexity tier. CAGRs were derived from trend extrapolation of annual contract value growth rates and platform adoption curves. Forecast inputs incorporated MAS guideline update frequency, cloud migration velocity at financial institutions, and sovereign clearance processing backlogs.
Practitioners should monitor regulatory enforcement intensification, geopolitical disruption to threat intelligence supply, and quantum-safe migration acceleration for early signals requiring forecast revision. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
India Cybersecurity Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
SSL VPN Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Enterprise Firewall Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Sweden Cybersecurity Market