
 Server Security Market | 2026-2036
Server Security Market Size, Share, and Industry Trends Forecast 2026-2036
Server Security Market Analytics
Cloud-native workload protection is reshaping how server security architectures are engineered and deployed across enterprise environments. CrowdStrike leverages endpoint detection and response telemetry to anchor its cloud workload platform in hybrid infrastructure. Palo Alto Networks competes through Prisma Cloud's unified policy engine spanning containers and virtual machines. Microsoft extends its security graph across Azure, Windows Server, and third-party Linux distributions to dominate enterprise license consolidation.
Server security encompasses hardware and software safeguards engineered to protect physical and virtual servers from unauthorized access, malware injection, and data exfiltration through mechanisms including kernel-level integrity verification, memory encryption, and runtime application self-protection. Its primary commercial purpose is ensuring continuous availability of business-critical applications while preserving data confidentiality against evolving threat vectors. Firewall and intrusion detection system deployments represent mature segments with established procurement cycles, while cloud-based deployment models capture the fastest expansion as organizations retire legacy on-premise appliances. Encryption software commands premium margins in regulated verticals where data-at-rest mandates from HIPAA and GDPR create non-negotiable compliance spend.
FDA cybersecurity guidance for medical device servers, EU NIS2 requirements for essential entity hardening, and China's GB standards for critical information infrastructure collectively elevate baseline security specifications and compress vendor qualification timelines. The SEC's incident disclosure rules for publicly traded firms further accelerate board-level accountability for server breach response. Stakeholders must evaluate whether their current vendor portfolios deliver sovereign data residency alongside cross-platform workload coverage.
Market Dynamics
Ransomware campaigns targeting core banking infrastructure are forcing financial services firms to reallocate capital toward sovereign-compliant server hardening stacks. The EU AI Act and NIS2 Directive are compressing vendor qualification timelines while mandating kernel-level integrity verification for critical digital service providers.
Growth Catalysts
- EU NIS2 Directive:Essential entities across Germany, France, and Italy must deploy runtime application self-protection by Q3 2025, creating immediate procurement pull for hardened server stacks.
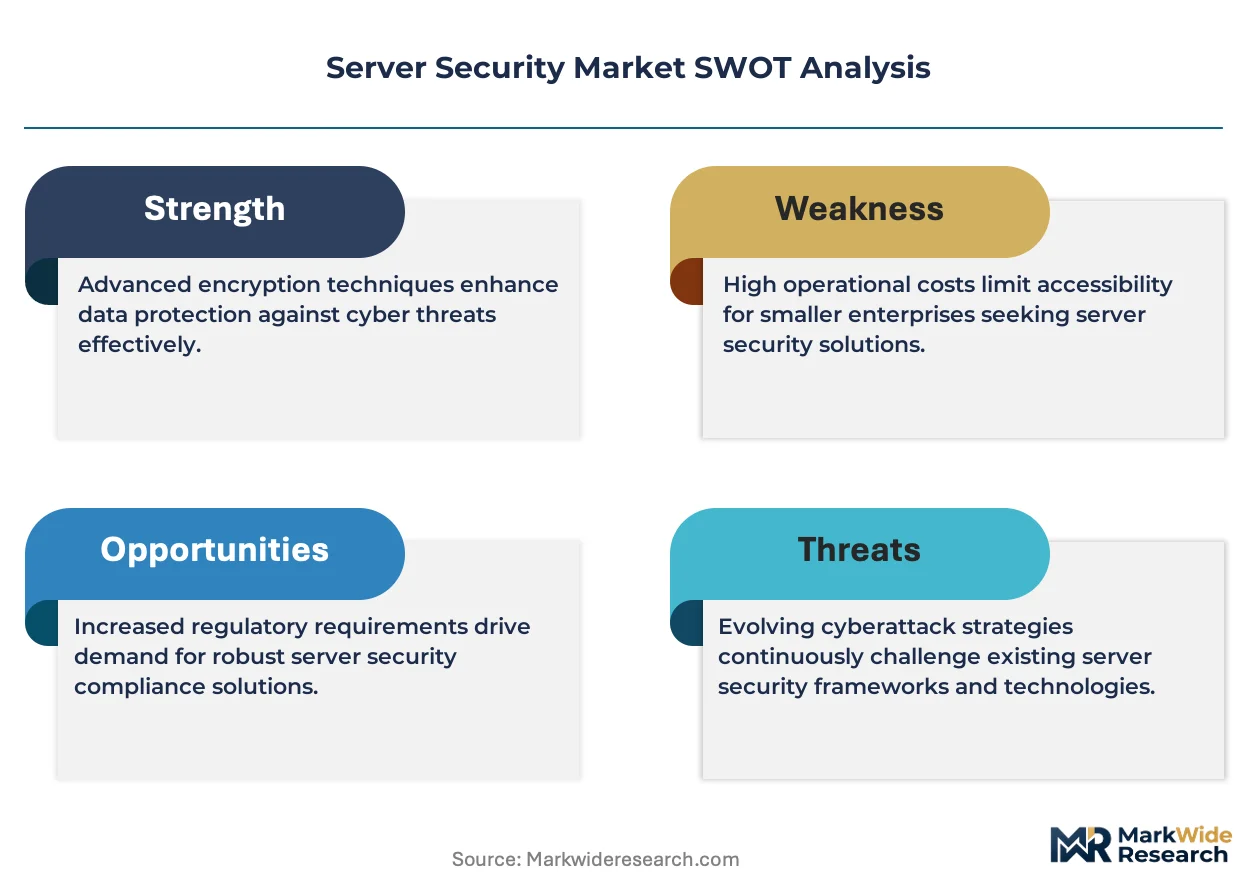
- Medical device servers:FDA cybersecurity guidance mandates encryption-at-rest for hospital imaging systems, accelerating compliance-driven replacement cycles in US healthcare networks.
- Confidential computing:Memory encryption modules are anchoring new procurement specifications for industrial data centers in Stuttgart and Munich requiring sovereign data residency.
Market Restraints
- Semiconductor supply concentration:Trusted Platform Module fabrication concentrates in Taiwan and South Korea, exposing server OEMs to single-source vulnerability during geopolitical friction.
- Specialized firmware engineering talent:Kernel-level security development requires scarce expertise in UEFI secure boot implementation, inflating R&D costs for mid-tier vendors.
- Legacy Windows Server estates:Extended support contracts for end-of-life operating systems drain security budgets that would otherwise fund cloud-native workload migration.
Strategic Opportunities
- India's critical information infrastructure:RBI and SEBI are mandating server hardening for payment system operators, opening white space for sovereign-compliant security stacks in Mumbai and Bangalore data centers.
- Post-quantum cryptography:NIST standardization of lattice-based algorithms is converging with existing TLS implementations to create premium upgrade cycles for encryption software vendors.
- Managed security service channels:Industrial manufacturers in Japan are outsourcing server hardening to METI-certified providers, displacing direct appliance procurement with subscription-based workload protection.
Industry Challenges
- FIPS 140-3 certification timelines:Cryptographic module validation currently spans 18-24 months, delaying product launches for encryption vendors targeting federal procurement.
- Hybrid cloud integration complexity:Organizations running VMware on-premises alongside Azure Stack face policy engine fragmentation that extends deployment cycles and inflates professional services costs.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Server Security Market |
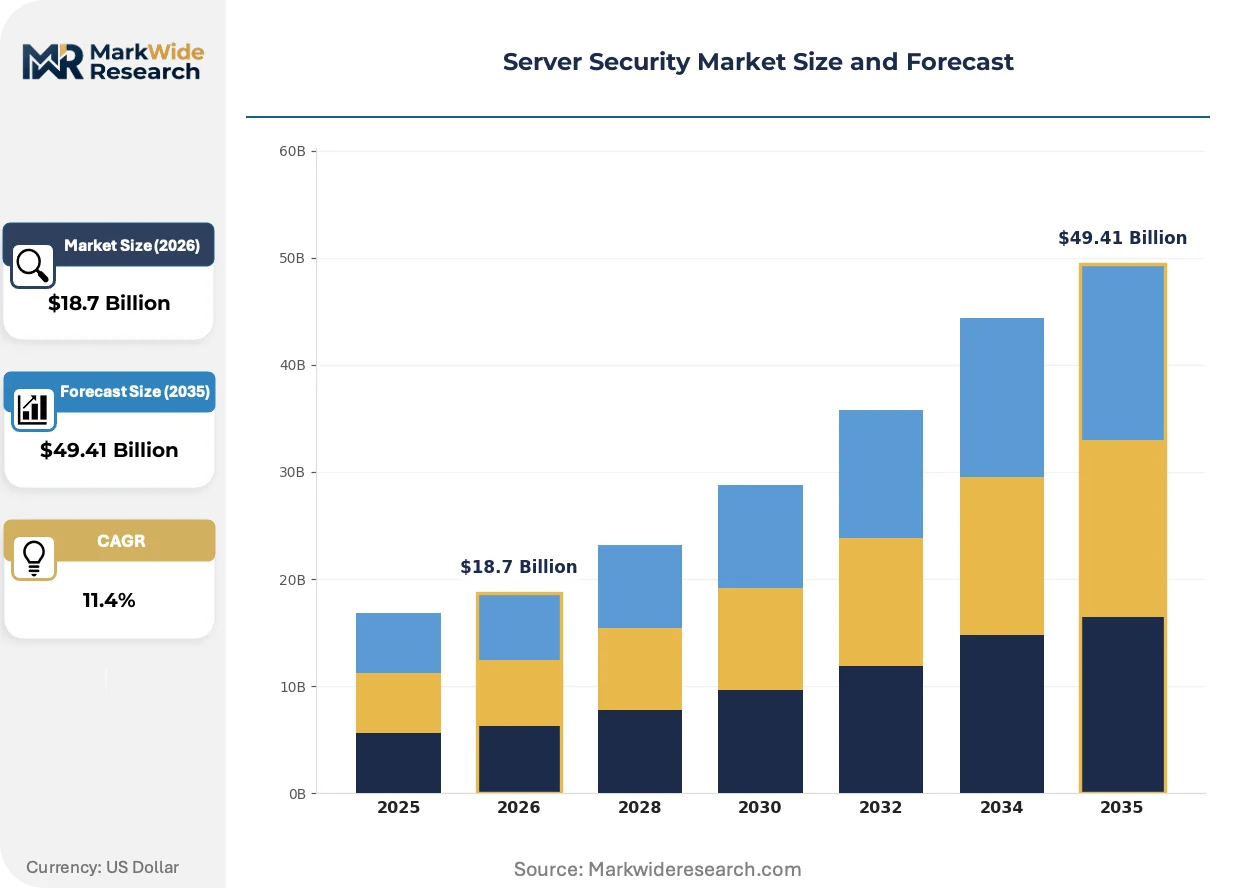
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $49.41 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Antivirus, Intrusion Detection System, Encryption Software Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Services End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Agencies Application: Data Protection, Network Security, Compliance Management, Threat Management |
| Companies Covered | Cisco, Commvault, IBM, CrowdStrike, Varonis, Microsoft, Fortinet, Check Point Software Technologies, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Server Security Market Evolving Landscape
Confidential computing architectures are redrawing the boundary between hardware-rooted trust and software-defined security. Three developments are compressing traditional server protection paradigms.
Trusted execution environments using hardware-based memory encryption are rendering obsolete software-only approaches to workload isolation in financial services data centers. German automotive manufacturers are adopting Intel TDX and AMD SEV-SNP for supplier collaboration platforms. This hardware-rooted model is compressing liability exposure for multi-tenant cloud deployments handling proprietary design files.
The EU AI Act's risk-classification framework is mandating server audit trails for high-risk AI systems deployed in healthcare and transportation. France's CNIL is enforcing data localization requirements that preclude cross-border processing without sovereign infrastructure. Medical device manufacturers are responding by deploying EU-only server instances with hardened hypervisors.
Consumption-based licensing for security software is displacing perpetual appliance purchases in mid-market enterprises. Value-added distributors in the Netherlands and Belgium are bundling CrowdStrike Falcon with Dell PowerEdge deployments, capturing margin that previously flowed to direct OEM channels. This shift is most pronounced among manufacturing SMEs in the Eindhoven technology cluster seeking to outsource security operations.
Server Security Market Segmentation
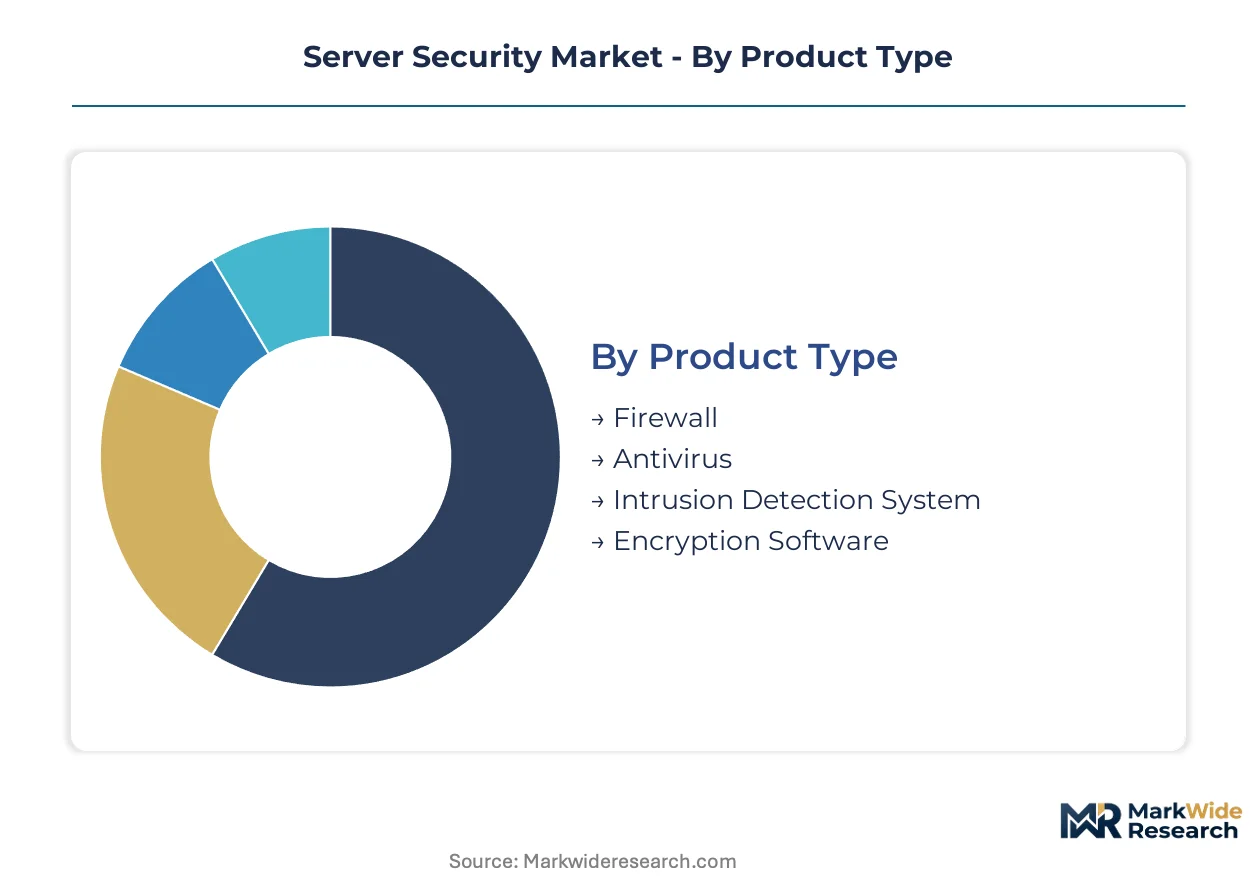
Server security procurement diverges sharply across deployment architectures, organizational scale, and regulatory exposure. Vendors must align product roadmaps with these fracture lines to capture premium pricing and recurring revenue streams.
Product Type:
Firewalls anchor perimeter defense for legacy data centers while encryption software commands compliance-driven premiums in regulated verticals.
- Firewall:Stateful packet inspection and next-generation application control dominate hardware appliance sales. German automotive suppliers deploy clustered firewall arrays to segment supplier collaboration platforms from core engineering networks.
- Encryption Software:AES-256 and emerging post-quantum lattice implementations protect data-at-rest for HIPAA and GDPR mandates. US hospital networks are replacing legacy disk encryption following FDA cybersecurity guidance for medical device servers.
- Antivirus:Signature-based detection converges with behavioral heuristics in hybrid cloud workloads.
- Intrusion Detection System:Network and host-based variants feed SIEM correlation engines for financial services SOCs.
The dominant share belongs to Firewall, while Encryption Software is closing the gap fastest.
Deployment Model:
Cost-to-scale ratios favor cloud-native architectures for mid-market enterprises, though sovereign data residency requirements sustain on-premise demand in European industrial clusters.
- Cloud-Based:Agentless workload protection and API-driven policy orchestration reduce operational overhead. French healthcare providers are migrating imaging system security to EU-sovereign cloud instances under CNIL data localization enforcement.
- Hybrid:Unified policy engines span VMware on-premises and Azure Stack, though integration complexity inflates professional services costs. Japanese manufacturers favor hybrid deployments to maintain METI-certified control over critical production data.
- On-Premise:Dedicated appliance stacks persist in air-gapped government and defense environments.
- Managed Services:Subscription-based hardening displaces direct procurement among manufacturing SMEs in the Netherlands and Belgium.
Cloud-Based deployments claim the largest addressable base, with Hybrid architectures gaining share fastest among multi-cloud enterprises.
End User:
Procurement sophistication scales with IT headcount and regulatory scrutiny, creating distinct vendor engagement models.
- Large Enterprises:Consolidated security graphs across Windows Server, Linux distributions, and container platforms drive enterprise license agreements. Financial services firms in Mumbai and Bangalore data centers mandate sovereign-compliant stacks under RBI and SEBI critical infrastructure rules.
- Government Agencies:FIPS 140-3 certification and FedRAMP authorization filter vendor eligibility, extending sales cycles. US federal procurement requires hardware-rooted trust modules for classified workload isolation.
- Medium Enterprises:Value-added distributor bundles compress direct sales economics.
- Small Enterprises:Consumption-based SaaS licensing reduces upfront capital requirements.
Large Enterprises dominate current spending, while Government Agencies are expanding procurement fastest under mandatory hardening directives.
Application:
Use-case prioritization reflects industry-specific threat models and audit requirements.
- Data Protection:Memory encryption and confidential computing architectures render software-only isolation obsolete. Intel TDX and AMD SEV-SNP deployments concentrate in Stuttgart and Munich industrial data centers requiring sovereign data residency.
- Compliance Management:Automated audit trails and kernel-level integrity verification satisfy EU AI Act risk-classification mandates for high-risk healthcare and transportation AI systems.
- Network Security:East-west traffic segmentation dominates microservices architecture protection.
- Threat Management:EDR telemetry integration with cloud workload platforms enables runtime application self-protection.
Data Protection holds the leading position, with Compliance Management expanding most quickly under NIS2 and AI Act enforcement timelines.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial institutions and critical infrastructure operators across Germany, the United States, Japan, India, and France are expanding server security procurement to satisfy sovereign data residency mandates and sector-specific hardening requirements.
United States
Healthcare networks and federal agencies drive encryption-at-rest deployments for HIPAA-covered imaging systems and FedRAMP-authorized cloud workloads. The FDA's cybersecurity guidance for medical device servers compresses vendor qualification timelines for hospital procurement teams. Hospital networks in the Greater Boston and Pacific Northwest corridors are replacing legacy disk encryption following federal mandates.
Germany
Industrial data centers in Stuttgart and Munich require sovereign-compliant security stacks with hardware-rooted trust modules for supplier collaboration platforms. The EU NIS2 Directive and AI Act mandate kernel-level integrity verification for essential entities by Q3 2025. Automotive manufacturers in Baden-Württemberg are adopting Intel TDX and AMD SEV-SNP for confidential computing architectures.
Japan
Industrial manufacturers are outsourcing server hardening to METI-certified managed security providers, displacing direct appliance procurement with subscription-based workload protection. The country's national cybersecurity framework elevates baseline specifications for critical production data. Manufacturing clusters in the Nagoya and Osaka corridors favor hybrid deployments to maintain sovereign control over operational technology networks.
India
RBI and SEBI regulations mandate server hardening for payment system operators and capital market infrastructure, opening procurement white space in Mumbai and Bangalore data centers. Financial services firms in these cities require sovereign-compliant stacks under critical information infrastructure rules. The central bank's directives are accelerating replacement cycles for legacy perimeter defenses in tier-one financial institutions.
France
CNIL data localization enforcement drives healthcare providers to migrate imaging system security to EU-sovereign cloud instances with hardened hypervisors. The EU AI Act's risk-classification framework mandates server audit trails for high-risk healthcare AI systems. Medical device manufacturers in the Île-de-France and Auvergne-Rhône-Alpes regions are deploying EU-only server instances to satisfy cross-border processing restrictions.
Server Security Market Competitive Landscape
Channel-controlling players compete with product-specialist players for enterprise security budgets across hybrid cloud and on-premise deployments. The vendor base clusters around three strategic archetypes: endpoint telemetry platforms extending into workload protection, network security incumbents with unified policy engines, and cloud-native specialists with API-driven orchestration. Dominant competitive moves include portfolio diversification through adjacent security category expansion and strategic partnerships with server OEMs to capture distributor margin.
Within the endpoint-native tier, CrowdStrike and Microsoft exemplify platform consolidation strategies that leverage existing telemetry relationships to anchor cloud workload offerings. Palo Alto Networks occupies a position among network-centric players that have extended into container and virtual machine protection through unified policy engines. Cisco represents the infrastructure-anchored archetype, leveraging hardware distribution channels to bundle security software with server and networking equipment deployments.
| Leading Market Players |
|---|
| Cisco |
| Commvault |
| IBM |
| CrowdStrike |
| Varonis |
| Microsoft |
| Fortinet |
| Check Point Software Technologies |
| Palo Alto Networks |
| Others |
Value Network & Pricing Analysis
Single-source dependency for Trusted Platform Module fabrication in Taiwan and South Korea compresses pricing power for server OEMs while simultaneously dictating supply chain redundancy investments. This concentration dynamic widens spreads between premium FIPS-certified stacks and standard-tier offerings as buyers absorb geopolitical risk premiums.
Pricing Analysis
Cost-plus contracts with semiconductor indexation dominate procurement for hardware-rooted security modules. Pricing stratifies across FIPS 140-3 certified, Common Criteria evaluated, and uncertified tiers based on validation depth and sovereign compliance scope. Cost compression in standard-tier firewall appliances intensifies as value-added distributors bundle subscription workloads, displacing direct OEM margin. Small enterprises exhibit highest price sensitivity through consumption-based SaaS preference, while government agencies accept premium positioning for FedRAMP-authorized deployments.
Supply Chain Analysis
Tariff exposure between the United States and China dominates supply chain risk calculus for server security hardware. Trusted Platform Module production concentrates in Taiwan and South Korea, with UEFI firmware development anchored in the United States and Israel. Raw material dependencies span silicon wafers, cryptographic accelerators, and specialized ASICs. Single-source vulnerability for TPM fabrication threatens continuity during geopolitical friction. Distribution runs through value-added distributors in the Netherlands and Belgium, displacing direct OEM channels for mid-market manufacturing clusters.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Server security functions as a defensive-moat market where regulatory entrenchment creates sticky procurement relationships. Compliance mandates compress vendor qualification timelines, elevating switching costs for established players.
For Market Incumbents: Insulate market position through backward integration into sovereign-compliant cloud infrastructure and exclusive certification partnerships with national regulators. Kernel-level security engineering talent scarcity threatens mid-tier vendor R&D economics. Capacity addition in Germany and India captures NIS2 and RBI-mandated procurement windows. Channel control through server OEM bundling defends margin against distributor disintermediation. For New Entrants and Emerging Players: India's critical information infrastructure white space offers the most penetrable entry corridor for sovereign-compliant security stacks. Mumbai and Bangalore data centers require hardened deployments under RBI and SEBI directives with limited incumbent saturation. Post-quantum cryptography integration presents a technical differentiation angle against legacy encryption vendors. Managed security service channels in Japan's manufacturing clusters provide a subscription-based go-to-market path that bypasses direct appliance competition. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors platform-consolidation archetypes with cross-workload telemetry integration. Long-term viability rests on cloud-native architecture dominance and regulatory certification moats. Acquisition targets should display FIPS 140-3 progress, EU sovereign cloud partnerships, or confidential computing hardware alliances. The signal to watch is NIS2 enforcement velocity across German and French essential entities as a demand inflection indicator.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | Intel TDX and AMD SEV-SNP alliances capture German automotive supplier procurement specifications. |
| Sovereign Cloud Certification | EU-only instance deployments satisfy CNIL data localization for French healthcare imaging systems. |
| Managed Security Service Launch | METI-certified outsourcing channels displace direct appliance sales in Japan's manufacturing clusters. |
| Post-Quantum Cryptography Integration | NIST lattice-based algorithm convergence creates premium upgrade cycles for regulated verticals. |
| Value-Added Distributor Alliance | CrowdStrike-Dell bundling in the Netherlands captures margin from traditional OEM channels. |
Research Methodology
Cross-validation between primary fieldwork and regulatory filing analysis anchors the qualitative findings. Interviews with CISOs, data center operations directors, channel sales heads at value-added distributors, and procurement leads at financial services firms combined with secondary validation from SEC filings, hyperscaler security capex disclosures, and EU NIS2 implementation guidance. Bottom-up sizing across deployment models and top-down constraint analysis from semiconductor supply data completed the triangulation.
Calibration against historical adoption curves for encryption software and firewall appliances informed the analytical framework across the projection horizon. Segmentation dimensions modeled include deployment architecture, organization scale, regulatory exposure tier, and sovereign compliance scope. CAGRs derived from elasticity-adjusted replacement cycles and compliance-driven procurement acceleration. Confidential computing hardware penetration and managed security service displacement rates served as industry-specific forecast inputs.
Practitioners should monitor NIS2 enforcement timelines, TPM supply continuity indicators, and post-quantum standardization progress for early signals of forecast revision. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Mexico Cybersecurity Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Information Security Products and Services Market
Cybersecurity
Enterprise Mobility Security Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Cybersecure Vehicle Control Unit Gateway Systems Market
Cybersecurity
Post-Quantum Cryptography Market
Cybersecurity
Threat Intelligence Market
Cybersecurity
Ddos Protection and Mitigation Security Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
Deception Technology Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Cyber Warfare Market