
 V2X Cybersecurity Market | 2026-2036
V2X Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
V2X Cybersecurity Market Analysis
Aftermarket service revenue is narrowing toward embedded security lifecycle management as OEMs internalize V2X protection from chip to cloud. Qualcomm Technologies leverages its Snapdragon Automotive platform to anchor end-to-end cryptographic processing for C-V2X modems. ETAS (ESCRYPT) specializes in automotive embedded security software, sustaining long-term partnerships with German Tier-1 suppliers for secure boot and key management. Karamba Security differentiates through runtime integrity enforcement, competing directly on deterministic threat blocking for ECU-level V2X interfaces.
V2X cybersecurity encompasses hardware-backed encryption, secure boot protocols, and real-time intrusion detection systems that protect vehicle-to-everything communication links against spoofing, replay, and man-in-the-middle attacks. The technology stack relies on HSM-protected asymmetric cryptography meeting FIPS 140-2 Level 3 or equivalent tamper resistance, with sub-10 millisecond latency budgets for safety-critical V2V message verification. Encryption and intrusion detection technologies command the deepest margin pools due to silicon-level IP concentration and recurring threat-signature update revenue. Vehicle-to-infrastructure and vehicle-to-cloud applications are expanding fastest as smart city deployments and OTA software management scale, while vehicle-to-pedestrian remains nascent pending smartphone ecosystem standardization.
The US NHTSA and FCC jointly shape V2X security demand through spectrum allocation rules and crash-avoidance communication mandates, while the EU's ETSI standards and GDPR-derived data governance constrain cross-border vehicular data flows. China's MIIT enforces domestic GB standards for connected vehicle security, creating parallel certification pathways that fragment vendor compliance scope. Stakeholders must monitor regulatory divergence between DSRC and C-V2X mandates as governments finalize spectrum and interoperability decisions that will lock in regional technology winners.
Market Dynamics
Automotive OEMs are internalizing V2X security stacks from silicon to cloud, compressing the addressable market for standalone cybersecurity vendors while elevating procurement standards for hardware-backed encryption and runtime integrity enforcement.
Growth Catalysts
- C-V2X protocol proliferation:Cellular vehicle-to-everything standards are displacing DSRC in major deployment corridors, creating fresh demand for modem-integrated security processors and certificate management systems.
- EU Cyber Resilience Act:Mandatory cybersecurity certification for connected devices is forcing automotive suppliers to embed tamper-resistant hardware security modules across production lines.
- German automotive cluster:OEM headquarters in Stuttgart and Munich are anchoring global testing protocols, drawing Tier-1 suppliers into concentrated R&D partnerships for secure vehicular communication.
Market Restraints
- Silicon supply concentration:Hardware security module fabrication depends on a limited foundry base in Taiwan and South Korea, exposing procurement timelines to geopolitical disruption.
- Regulatory fragmentation:Divergent DSRC and C-V2X mandates between US FCC spectrum rules and EU ETSI standards are forcing vendors to maintain parallel certification tracks.
- Integration cost barriers:Sub-10 millisecond latency requirements for safety-critical V2V message verification demand specialized cryptographic accelerators that inflate bill-of-materials costs.
Strategic Opportunities
- Vehicle-to-cloud lifecycle management:OTA software update infrastructure is creating recurring revenue pools for security stack vendors managing cryptographic key rotation and threat signature distribution.
- Smart city V2I deployments:Municipal traffic management authorities in Singapore and Dubai are piloting secure roadside unit networks, opening public-sector procurement channels distinct from automotive supply chains.
- Post-quantum cryptography transition:NIST standardization of quantum-resistant algorithms is positioning early movers to capture retrofit demand as governments mandate cryptographic agility in vehicular systems.
Industry Challenges
- Embedded systems security talent scarcity:Shortage of engineers combining automotive ECU architecture expertise with cryptographic implementation experience is elongating product development cycles.
- Multi-stakeholder certificate governance:Root-of-trust management spanning OEMs, infrastructure operators, and regional transport authorities is creating complex liability allocation disputes.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | V2X Cybersecurity Market |
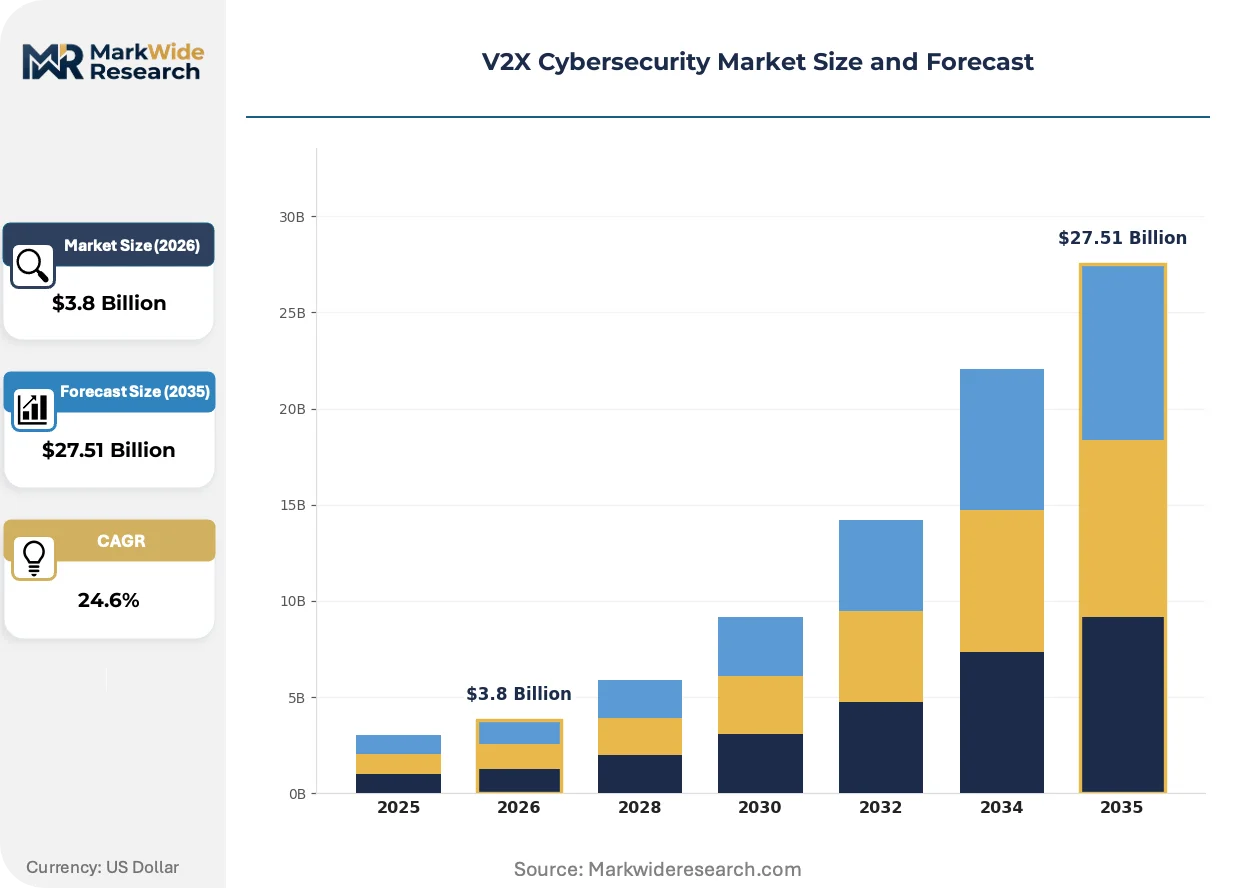
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $27.51 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Encryption, Firewall, Intrusion Detection, Identity Management Application: Vehicle-to-Vehicle, Vehicle-to-Infrastructure, Vehicle-to-Pedestrian, Vehicle-to-Cloud End User: OEMs, Fleet Operators, Transportation Agencies, Cybersecurity Firms Deployment: On-Premises, Cloud-Based, Hybrid, Edge Computing |
| Companies Covered | Qualcomm Technologies, Inc., AUTOCRYPT Co., Ltd., Continental AG, ETAS (ESCRYPT), Green Hills Software LLC, Infineon Technologies AG, Aptiv PLC, Karamba Security Ltd., NXP Semiconductors, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
V2X Cybersecurity Market Emerging Trajectories
Deterministic runtime protection is displacing signature-based detection in safety-critical vehicular networks. Three developments are compressing vendor positioning windows and reshaping procurement criteria.
Hardware-enforced control-flow integrity is rendering obsolete software-only intrusion detection for ECU-level V2X interfaces. German Tier-1 suppliers are mandating deterministic threat blocking that operates within hard real-time constraints. This technology is compressing competitive differentiation around latency guarantees rather than detection accuracy metrics.
The EU's Cyber Resilience Act is mandating vulnerability disclosure timelines and automatic update capabilities for all connected vehicle components sold in member states. Automotive suppliers are restructuring development workflows to embed continuous security monitoring from design phase through end-of-life. Powertrain and chassis ECU categories face the steepest compliance deadlines given their safety-critical classification.
Fleet operators are consolidating vendor relationships around end-to-end security stack providers capable of spanning chip-to-cloud architectures. Long-term service contracts bundling hardware, software, and threat intelligence are displacing point-product procurement at major commercial vehicle operators. This consolidation is most visible in North American long-haul trucking segments where telematics providers are absorbing cybersecurity functions into platform offerings.
V2X Cybersecurity Market Segmentation
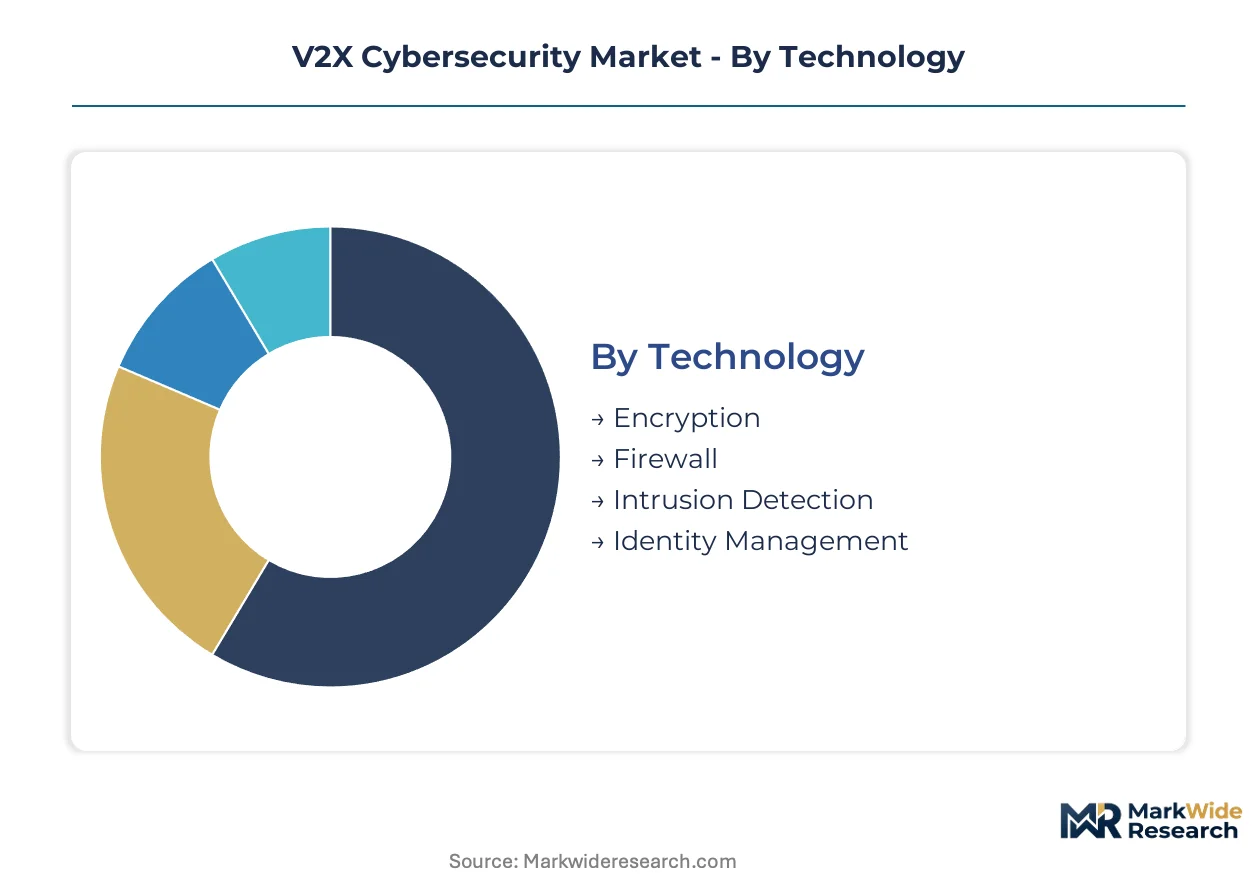
V2X cybersecurity procurement patterns diverge sharply across technology layers and deployment architectures. OEMs prioritize hardware-backed encryption for safety-critical V2V messaging, while fleet operators favor cloud-native certificate management for distributed vehicle populations.
Technology:
Cost tier stratification in V2X security procurement separates silicon-integrated capabilities from software-overlay solutions.
- Encryption:Hardware security modules executing AES-256 and ECC operations meet sub-10 millisecond latency budgets for safety-critical V2V authentication. German Tier-1 suppliers anchor demand for FIPS 140-2 Level 3 certified implementations in Stuttgart and Munich development centers.
- Intrusion Detection:Deterministic runtime integrity enforcement operates within hard real-time constraints on automotive ECUs. North American long-haul trucking fleets are consolidating procurement around telematics-integrated threat blocking that eliminates signature-based scanning overhead.
- Firewall:Perimeter defense for V2X protocol gateways filters malformed DSRC and C-V2X packets before ECU processing.
- Identity Management:Certificate lifecycle systems automate pseudonym rotation for privacy-preserving vehicular authentication.
Encryption holds installed capacity. Intrusion Detection is rotating up the share rankings.
Application:
Volume concentration varies by deployment maturity and infrastructure dependency.
- Vehicle-to-Infrastructure:Secure roadside unit networks in Singapore and Dubai municipal deployments create public-sector procurement channels distinct from automotive supply chains. Smart city traffic management authorities specify hardware-backed encryption for traffic signal preemption and emergency vehicle priority systems.
- Vehicle-to-Cloud:OTA software update infrastructure generates recurring revenue for cryptographic key rotation and threat signature distribution. Fleet operators bundle lifecycle management into long-term service contracts spanning chip-to-cloud architectures.
- Vehicle-to-Vehicle:Direct peer-to-peer safety messaging requires deterministic latency guarantees for crash-avoidance scenarios.
- Vehicle-to-Pedestrian:Smartphone ecosystem standardization gaps delay commercial deployment despite technical protocol readiness.
Vehicle-to-Cloud commands the steepest expansion trajectory. Vehicle-to-Infrastructure is climbing the fastest in absolute deployment count.
End User:
Customer type determines procurement authority and contract structure across the value chain.
- OEMs:Internalization of security stacks from silicon to cloud compresses addressable market for standalone vendors while elevating hardware-backed encryption standards. Powertrain and chassis ECU categories face the steepest EU Cyber Resilience Act compliance deadlines given safety-critical classification.
- Fleet Operators:Commercial vehicle aggregators consolidate vendor relationships around end-to-end providers capable of unified telematics and cybersecurity platforms. This consolidation is most visible in North American long-haul segments where procurement bundles hardware, software, and threat intelligence.
- Transportation Agencies:Municipal and national road authorities specify secure roadside unit procurement for smart corridor deployments.
- Cybersecurity Firms:Specialized vendors supply cryptographic IP and certification support to automotive Tier-1 suppliers.
OEMs hold installed capacity. Fleet Operators are rotating up the share rankings.
Deployment:
Architecture choice reflects latency requirements and data sovereignty constraints.
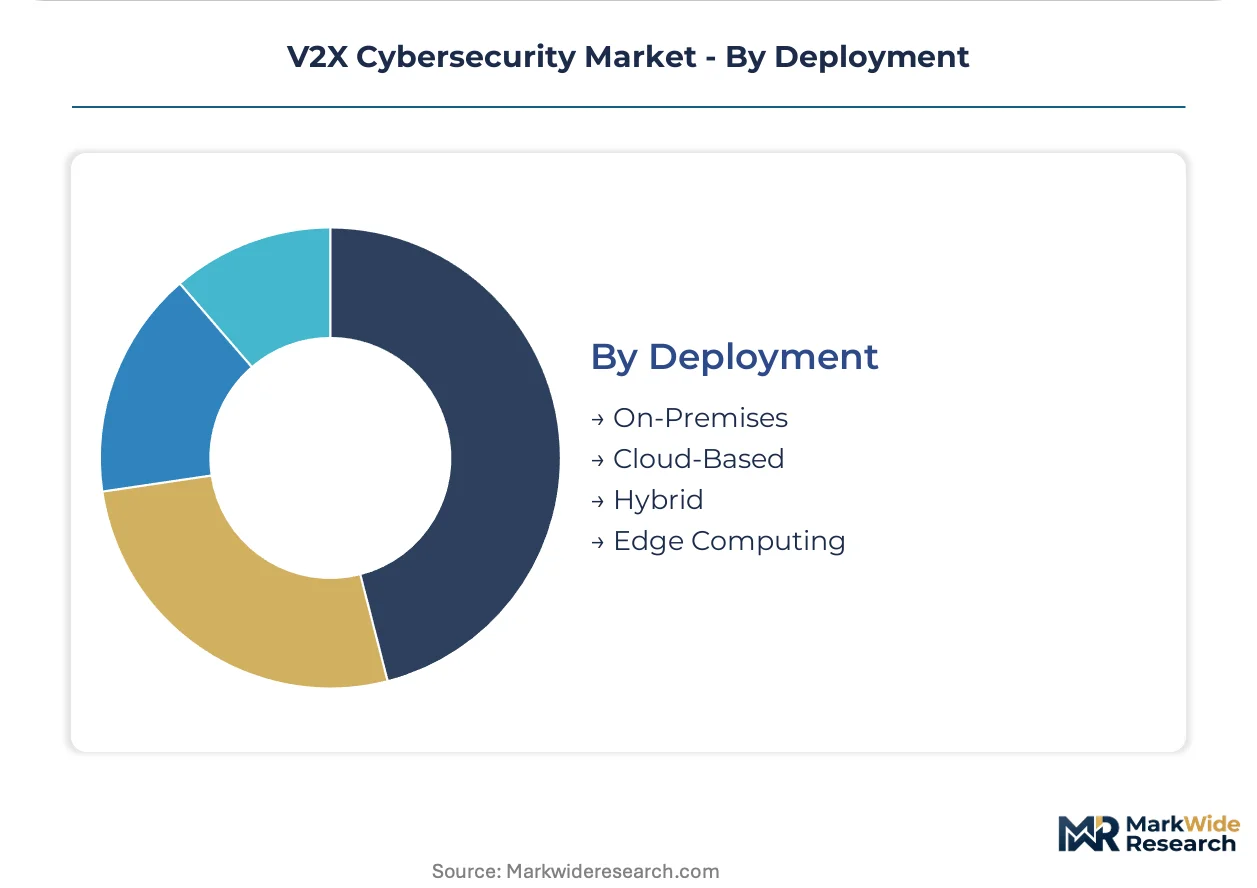
- Edge Computing:Distributed cryptographic processing at roadside units and vehicle gateways minimizes round-trip latency for safety-critical message verification. German automotive clusters prioritize edge-resident HSMs to satisfy GDPR-derived data governance constraints on cross-border vehicular data flows.
- Hybrid:Partitioned architectures route safety-critical V2V authentication through on-vehicle edge nodes while delegating certificate management and threat intelligence to cloud infrastructure.
- On-Premises:Captive data center deployments serve defense and government fleet applications with air-gapped security requirements.
- Cloud-Based:Fully centralized certificate authorities and OTA update distribution suit light-commercial vehicle segments with relaxed latency budgets.
Edge Computing holds installed capacity. Hybrid is rotating up the share rankings.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Fleet operators in Germany demonstrate the lowest price elasticity, absorbing premium hardware security modules without procurement delays. Buyers in India and Southeast Asia exhibit acute sensitivity to bill-of-materials inflation, forcing vendors to strip non-essential cryptographic features from entry-tier offerings.
United States
Commercial trucking fleets in Texas and California are consolidating procurement around telematics-integrated security stacks. The NHTSA and FCC jointly enforce spectrum allocation rules that mandate crash-avoidance communication hardware. Detroit's automotive engineering corridor anchors testing protocols for DSRC-to-C-V2X migration pathways.
Germany
OEM headquarters in Stuttgart and Munich command the world's densest concentration of V2X security R&D expenditure. The EU Cyber Resilience Act imposes mandatory certification timelines that compress supplier qualification windows. Baden-Württemberg's Tier-1 supplier ecosystem coordinates global standardization for secure boot and key management implementations.
China
Domestic EV manufacturers in Shanghai and Shenzhen are integrating MIIT-mandated GB standards for connected vehicle security. The Ministry of Industry and Information Technology enforces parallel certification pathways that fragment vendor compliance scope. Yangtze River Delta production clusters source cryptographic processors from captive semiconductor foundries to bypass import dependency.
Japan
Keiretsu-affiliated suppliers in Nagoya and Tokyo resist cloud-native certificate management in favor of edge-resident hardware security modules. METI guidelines emphasize deterministic latency guarantees for safety-critical V2V messaging. Kansai region automotive electronics specialists collaborate with domestic semiconductor fabricators on tamper-resistant module designs.
Singapore
Smart city infrastructure authorities specify hardware-backed encryption for municipal traffic signal preemption networks. The Land Transport Authority pilots secure roadside unit deployments that diverge from automotive supply chain procurement patterns. Jurong innovation district hosts validation laboratories for tropical climate resilience testing of vehicular communication hardware.
V2X Cybersecurity Market Vendor Landscape
Semiconductor platform providers and automotive embedded security specialists split the market along the silicon-to-software boundary. Tier-1 automotive suppliers internalize cryptographic IP while maintaining external procurement for certification support and threat intelligence feeds. Three archetypes dominate: chip-integrated security module vendors, runtime integrity enforcement specialists, and end-to-end lifecycle management platforms. Competitive dynamics center on strategic partnerships with German OEM headquarters and M&A targeting cryptographic acceleration IP.
Within the semiconductor platform tier, Qualcomm Technologies, Inc. and NXP Semiconductors occupy positions anchoring modem-integrated cryptographic processing for C-V2X deployments. ETAS (ESCRYPT) exemplifies the embedded software specialist archetype, sustaining development partnerships concentrated in Stuttgart and Munich. Karamba Security Ltd. represents the deterministic runtime enforcement segment, competing on hard real-time threat blocking capabilities for ECU-level interfaces. AUTOCRYPT Co., Ltd. sits within the certificate lifecycle management specialization, serving Korean and Asia-Pacific fleet operators with pseudonym rotation systems.
| Leading Market Players |
|---|
| Qualcomm Technologies, Inc. |
| AUTOCRYPT Co., Ltd. |
| Continental AG |
| ETAS (ESCRYPT) |
| Green Hills Software LLC |
| Infineon Technologies AG |
| Aptiv PLC |
| Karamba Security Ltd. |
| NXP Semiconductors |
| Others |
Supply Flow & Price Mechanics
Taiwan's foundry concentration in Hsinchu and Tainan anchors global hardware security module fabrication, translating wafer allocation tightness into pricing leverage for cryptographic processor vendors serving automotive OEMs. This geographic lock-in compresses margin negotiation windows for downstream security stack providers while elevating premium tiers for FIPS 140-2 Level 3 certified implementations.
Pricing Analysis
After-sales service contracts bundling cryptographic key rotation and threat signature distribution drive lifetime value capture for V2X security vendors. Three-tier pricing structure across premium, standard, and economy levels separates FIPS-certified automotive-grade modules from commercial telematics overlays and stripped-down fleet management tiers. Cost compression in entry-tier offerings intensifies because Indian and Southeast Asian buyers demand bill-of-materials reductions. Fleet operators in North American long-haul trucking segments exhibit the lowest price sensitivity, absorbing end-to-end platform premiums without procurement delays.
Supply Chain Analysis
Silicon wafer supply draws from captive foundry capacity in Taiwan, South Korea, and domestic Yangtze River Delta facilities serving China's MIIT-mandated GB standards. Raw material dependencies span EUV lithography equipment, advanced packaging substrates, and tamper-resistant module casings. Single-source vulnerability concentrates in TSMC's automotive-qualified process nodes. Distribution runs through Tier-1 supplier engineering centers in Stuttgart, Munich, and Detroit before final OEM integration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
V2X cybersecurity functions as a defensive-moat market where regulatory entrenchment creates sticky procurement relationships. Certification timelines under the EU Cyber Resilience Act and US NHTSA mandates erect switching costs that protect incumbent positions.
For Market Incumbents: Build switching-cost moats through embedded lifecycle management contracts that span vehicle production through end-of-life decommissioning. Deepen certification investment ahead of EU Cyber Resilience Act enforcement deadlines to compress supplier qualification windows for challengers. Counter runtime integrity specialists by acquiring deterministic threat-blocking IP or forming exclusive R&D partnerships with German Tier-1 engineering clusters. For New Entrants and Emerging Players: Municipal smart city deployments in Singapore and Dubai represent the most penetrable entry point, diverging from automotive supply chain procurement patterns dominated by entrenched semiconductor platforms. Post-quantum cryptography retrofit services for existing fleet populations offer a second white-space target ahead of NIST standardization completion. Pursue channel partnerships with telematics providers serving North American commercial trucking segments rather than direct OEM sales cycles. For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-capture play because certification entrenchment and standard-setting participation determine vendor survival across multi-decade automotive platform lifecycles. Target acquisition candidates combining cryptographic acceleration IP with existing German OEM development partnerships. Monitor NIST post-quantum algorithm finalization as the inflection signal for retrofit demand acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptography Transition | NIST algorithm standardization positions early movers for government-mandated vehicular retrofit procurement cycles. |
| Smart City V2I Partnership | Singapore Land Transport Authority pilots create public-sector revenue channels outside automotive supply chain concentration. |
| Runtime Integrity Acquisition | Deterministic threat-blocking IP addresses German Tier-1 mandates for hard real-time ECU protection. |
| Certificate Lifecycle Platform | Pseudonym rotation automation serves Korean and Asia-Pacific fleet operator consolidation trends. |
| Edge-Resident HSM Deployment | GDPR-derived data governance constraints in Germany favor localized cryptographic processing over cloud-native alternatives. |
Methodological Framework
A standing panel of Tier-1 supplier procurement directors, OEM platform security architects, municipal traffic authority technology officers, and fleet telematics operations managers provided ongoing calibration throughout the study. Primary interview findings triangulated against secondary validation from NHTSA rulemaking dockets, ETSI technical specifications, MIIT GB standard publications, and automotive production registration databases. Bottom-up segment sizing and top-down macro constraint checks converged on final market estimates.
Scenario-bracketing around C-V2X versus DSRC protocol dominance, EU Cyber Resilience Act enforcement timing, and semiconductor foundry capacity allocation generated projection bounds across the analysis window. Segmentation modeling spanned technology layer, application architecture, end-user procurement authority, and regional regulatory cluster. CAGRs derived from installed base penetration curves, replacement cycle assumptions, and content-per-vehicle escalation for safety-critical versus convenience-tier V2X deployments.
Macroeconomic conditions sit as an overlay; deviation in automotive production volumes, semiconductor capital expenditure cycles, or cross-border data governance enforcement would shift the trajectory. Forecasts reflect documented assumptions regarding protocol migration timelines and certification harmonization progress. Material shifts in NIST post-quantum standardization schedules or major spectrum reallocation decisions would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Canada Cybersecurity Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Global Network Security Firewall Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Cyber Security As a Service Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
Application Security Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Global Content Disarm and Reconstruction Market