
 Sweden Cybersecurity Market | 2026-2036
Sweden Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Sweden Cybersecurity Market Analytics
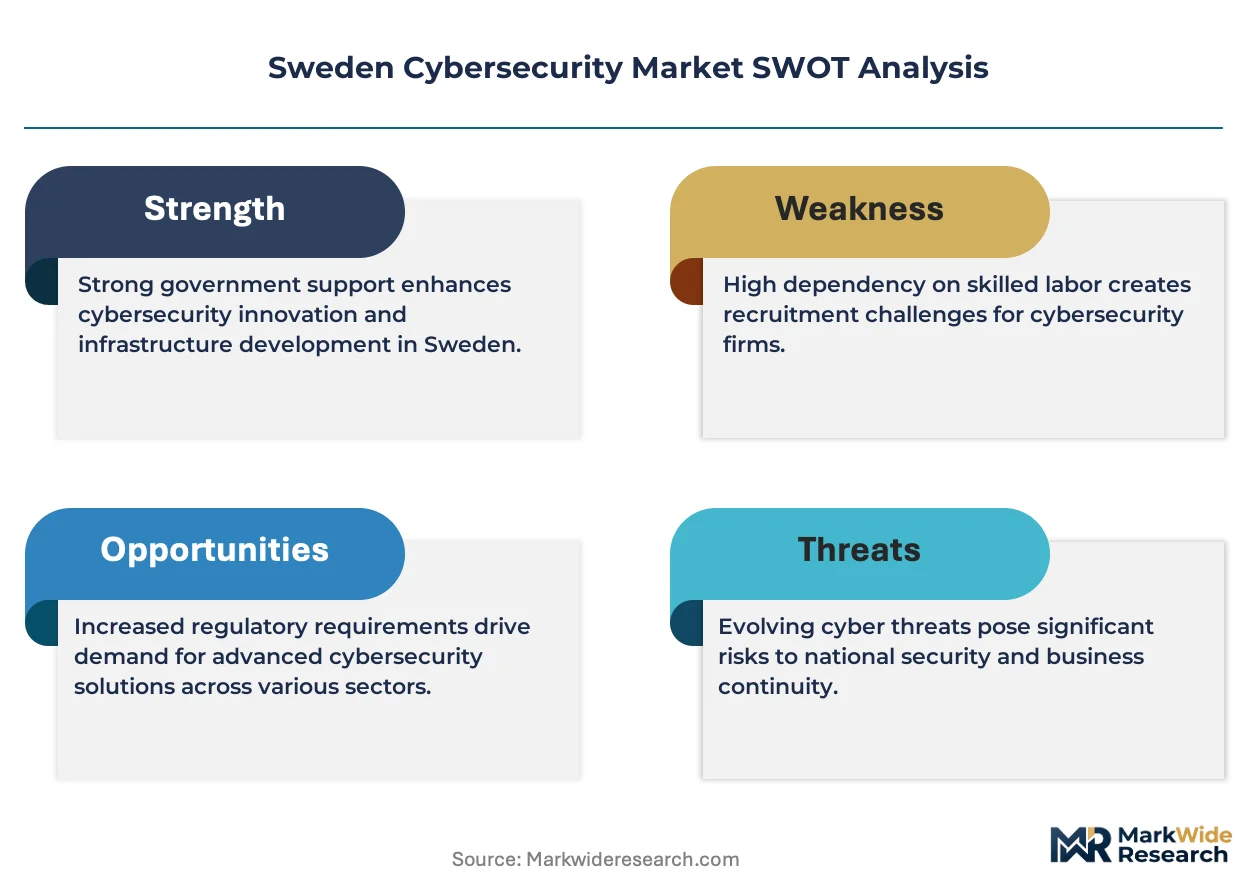
Project finance for sovereign-critical infrastructure is narrowing the field of qualified cybersecurity vendors in Sweden. Clavister AB leverages its domestic clearance credentials to anchor government and defense contracts. Truesec AB specializes in incident response retainers that sustain recurring revenue depth. Palo Alto Networks Inc. competes through cloud-native platform breadth across hybrid Swedish enterprise estates.
Sweden cybersecurity encompasses technical systems, processes, and controls designed to protect networks, endpoints, and data assets from unauthorized access, disruption, or exfiltration, typically incorporating encryption protocols, firewall rule sets, and behavioral anomaly detection operating at millisecond latency thresholds. Its primary commercial purpose is to preserve operational continuity, regulatory compliance, and stakeholder trust across digitized value chains. Managed Security Services commands disproportionate margin pools as Swedish mid-market firms outsource 24/7 security operations center functions rather than building in-house capability. Cloud-Based deployment is expanding fastest as Stockholm-region enterprises migrate workloads to distributed infrastructure. Threat Intelligence represents an emerging premium tier where contextualized adversary data commands pricing power.
Swedish cybersecurity demand is shaped by the Swedish Civil Contingencies Agency (MSB) enforcement of NIS2 transposition requirements, the Swedish Post and Telecom Authority (PTS) resilience mandates for electronic communications providers, and EU GDPR data breach notification standards that compress response timelines. These frameworks compel organizations to maintain demonstrable detection capability and documented incident response playbooks as conditions of market access. Stakeholders must weigh whether to build proprietary security operations or embed third-party managed services into core infrastructure strategy.
Market Dynamics
Swedish cybersecurity procurement is pivoting toward sovereign-cleared vendors as the MSB enforces NIS2 incident-response mandates that disqualify non-domestic suppliers from critical infrastructure contracts.
Growth Catalysts
- EU NIS2 Directive:The Swedish transposition compels operators of essential services to deploy continuous monitoring and 72-hour breach notification, forcing procurement cycles.
- Stockholm fintech density:The urban corridor concentrates payment processors and digital banks that require specialized fraud detection and API security layers.
- Cloud workload migration:Distributed infrastructure adoption creates demand for cloud-native security posture management across hybrid estates.
Market Restraints
- Domestic vendor scarcity:Only three Swedish firms hold MSB Tier-3 clearance for defense and energy contracts, limiting competitive supply.
- Specialized labor costs:Certified incident responders command 40% wage premiums over general IT security roles, inflating MSSP delivery costs.
- Legacy OT integration:Industrial control systems in manufacturing and utilities run proprietary protocols that resist standard endpoint detection.
Strategic Opportunities
- Gothenburg maritime cluster:Port operators and shipping logistics firms remain underpenetrated for OT security and vessel-to-shore communication protection.
- AI-augmented threat hunting:Machine learning behavioral analytics converging with human-led investigation creates premium service tiers.
- PTS 5G security mandates:Electronic communications providers must implement network slicing isolation and edge security by regulatory deadline.
Industry Challenges
- Clearance backlog:MSB personnel vetting timelines stretch 8-14 months, delaying vendor onboarding for classified contracts.
- OT-IT convergence complexity:Manufacturing CISOs struggle to unify governance across Purdue Model Level 0-3 systems with cloud-native security tools.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Sweden Cybersecurity Market |
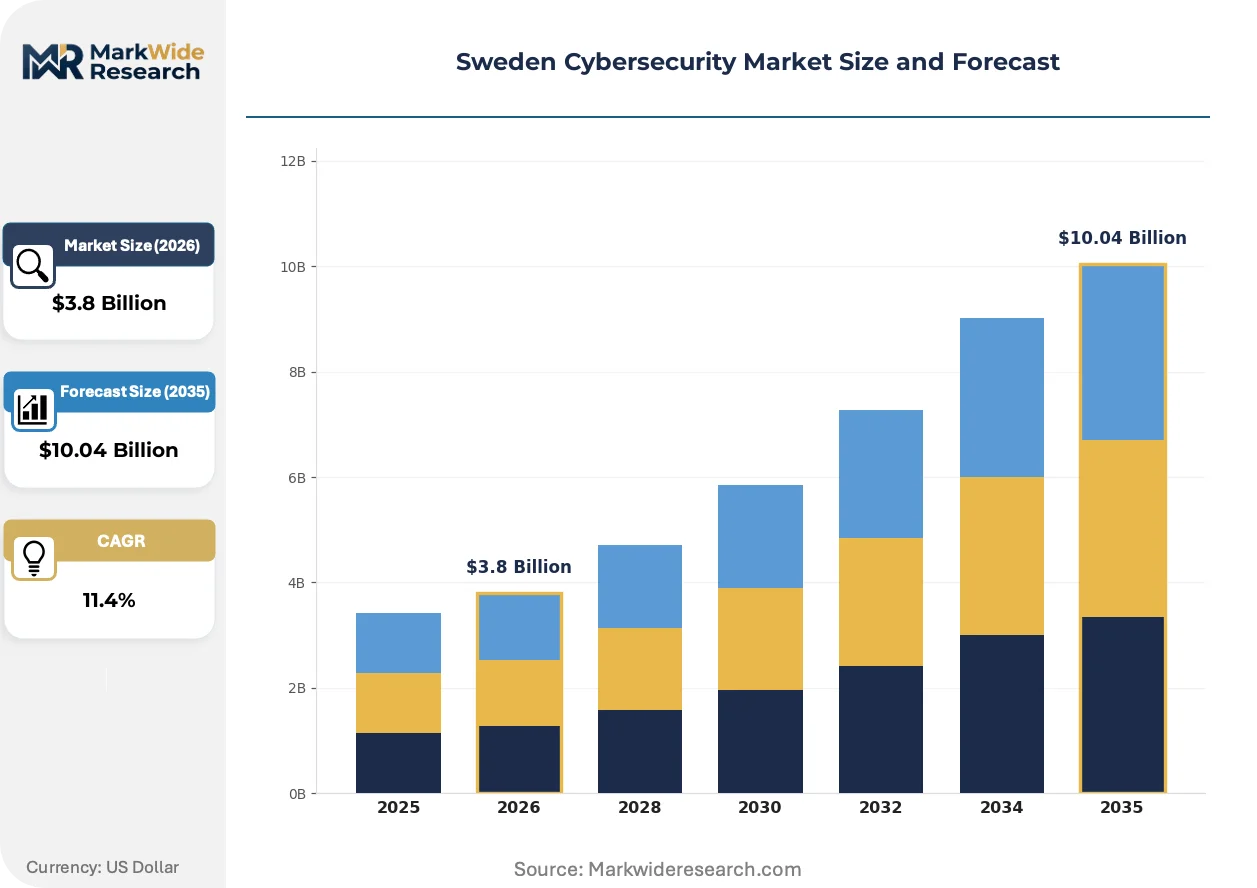
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $10.04 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Firewall, Intrusion Detection System, Antivirus Software, Encryption Service Type: Consulting, Managed Security Services, Incident Response, Threat Intelligence End User: Government, BFSI, Healthcare, Retail Deployment: On-Premises, Cloud-Based, Hybrid Solution, Managed Services |
| Companies Covered | Clavister AB, Truesec AB, Advenica AB, Palo Alto Networks Inc., Fortinet Inc., Cisco Systems Inc., Check Point Software Technologies Ltd., Trend Micro Incorporated, F5 Inc., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Sweden Cybersecurity Market Evolving Landscape
Swedish cybersecurity architecture is fragmenting into modular, API-first components that displace monolithic platform consolidation. Vendors and buyers alike are prioritizing interoperability over single-vendor coverage.
Extended detection and response platforms are hybridizing endpoint telemetry with identity threat detection and cloud workload monitoring into unified data lakes. Swedish financial institutions and critical infrastructure operators are adopting these converged stacks to satisfy MSB visibility requirements. The technology is hybridizing previously siloed security functions into correlated detection pipelines that reduce mean time to respond.
The Swedish Civil Contingencies Agency's NIS2 enforcement guidelines mandate documented incident response playbooks and tabletop exercises for essential service operators. Industrial consequence includes forced restructuring of security operations center staffing and retainer relationships. Energy and transport sectors are most affected, with state-owned utilities accelerating sovereign-cleared MSSP procurement.
Security service purchasing is consolidating around outcome-based retainers that tie vendor compensation to measurable mean-time-to-containment metrics. Traditional hourly consulting and hardware resale models are losing share to performance-guaranteed contracts. This shift is most visible in Stockholm's fintech cluster, where venture-backed firms demand contractual risk transfer from security providers.
Sweden Cybersecurity Market Segmentation
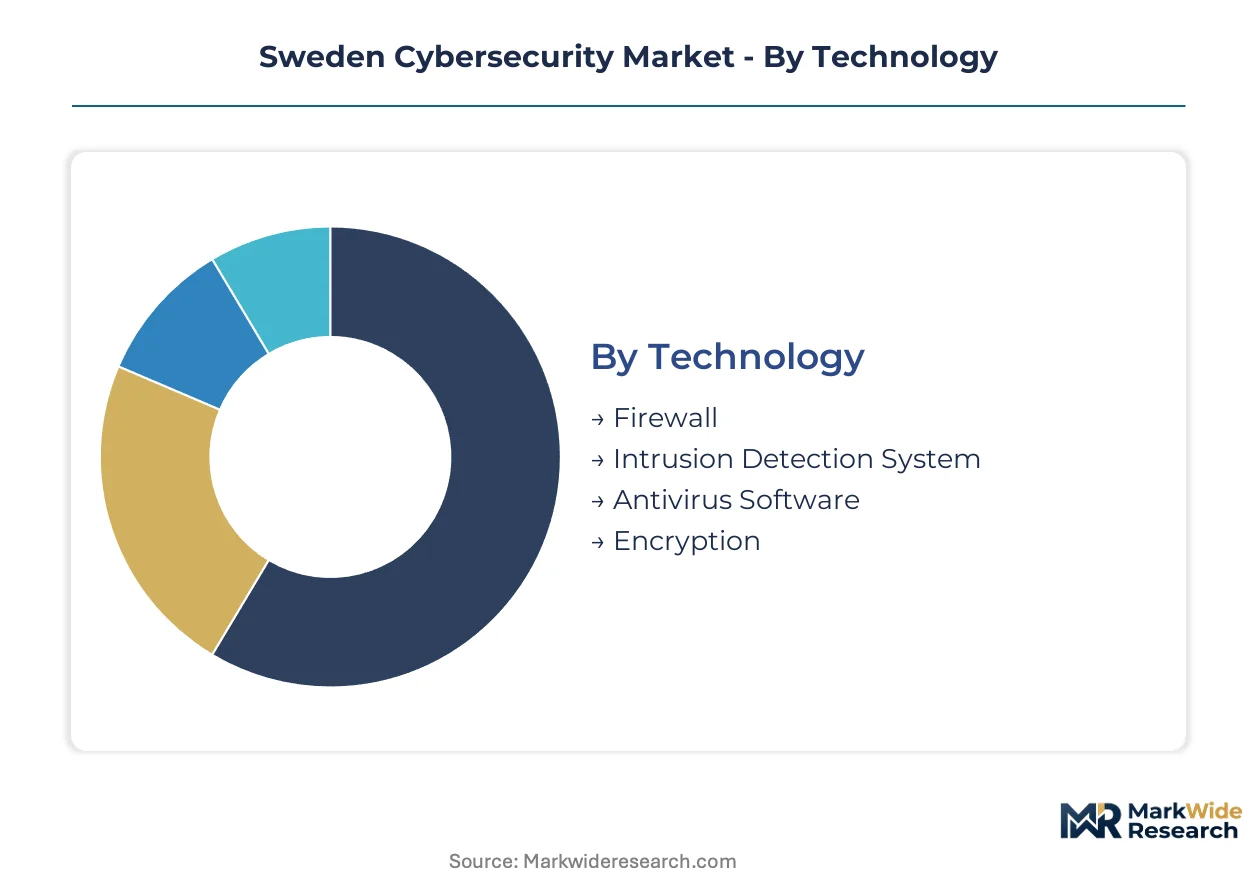
Swedish cybersecurity procurement fragments across technology stacks, service delivery models, and deployment architectures. Each segment carries distinct margin profiles and vendor qualification requirements under MSB oversight.
Technology:
After-sales service intensity varies sharply across technology categories, with managed detection platforms requiring continuous signature updates and 24/7 analyst support while perimeter appliances demand periodic hardware refresh cycles.
- Firewall:Next-generation firewalls integrate deep packet inspection with application-layer visibility for encrypted traffic. Swedish energy operators and Stockholm fintech clusters deploy these at network perimeters to satisfy NIS2 segmentation mandates, though legacy OT protocol support remains patchy.
- Intrusion Detection System:Network-based and host-based variants analyze traffic patterns against behavioral baselines. Demand concentrates in Gothenburg maritime logistics and defense-adjacent manufacturing where OT-IT convergence creates novel attack surfaces requiring specialized sensor deployment.
- Antivirus Software:Endpoint protection platforms with EDR capabilities dominate Swedish enterprise procurement.
- Encryption:Data-at-rest and data-in-transit solutions address GDPR Article 32 compliance requirements.
Firewall holds the largest share; momentum sits with Intrusion Detection System.
Service Type:
Cost tier stratification separates advisory consulting from retained operational support, with incident response commanding premium pricing during active breach engagements.
- Managed Security Services:24/7 security operations center functions delivered through sovereign-cleared facilities. Swedish mid-market firms outsource these capabilities rather than building in-house teams, with MSB Tier-3 clearance becoming a mandatory filter for critical infrastructure contracts.
- Incident Response:Retainer-based breach containment and forensic investigation services. Stockholm financial institutions sustain recurring revenue relationships with specialized providers, tying compensation to mean-time-to-containment metrics rather than hourly billing.
- Consulting:Advisory services spanning security architecture design and compliance gap assessments.
- Threat Intelligence:Contextualized adversary data feeds and indicator-of-compromise sharing.
Managed Security Services dominates procurement volume; Threat Intelligence is climbing the fastest as contextualized adversary data commands pricing power.
End User:
Application-specific requirements drive divergent technology stacks, with government and BFSI segments imposing the most stringent sovereign-cleared vendor mandates.
- Government:Defense, civilian agencies, and state-owned utilities requiring MSB Tier-3 clearance. Swedish Civil Contingencies Agency procurement rules disqualify non-domestic suppliers from classified contracts, narrowing the qualified vendor pool to three cleared domestic firms.
- BFSI:Banking, financial services, and insurance encompassing Stockholm's dense fintech corridor. Payment processors and digital banks require specialized fraud detection layers and API security postures that differ from traditional retail banking infrastructure.
- Healthcare:Regional health authorities and private hospital networks managing patient data.
- Retail:E-commerce platforms and physical point-of-sale networks.
Government holds the largest share; BFSI is gaining share fastest on fintech cluster expansion.
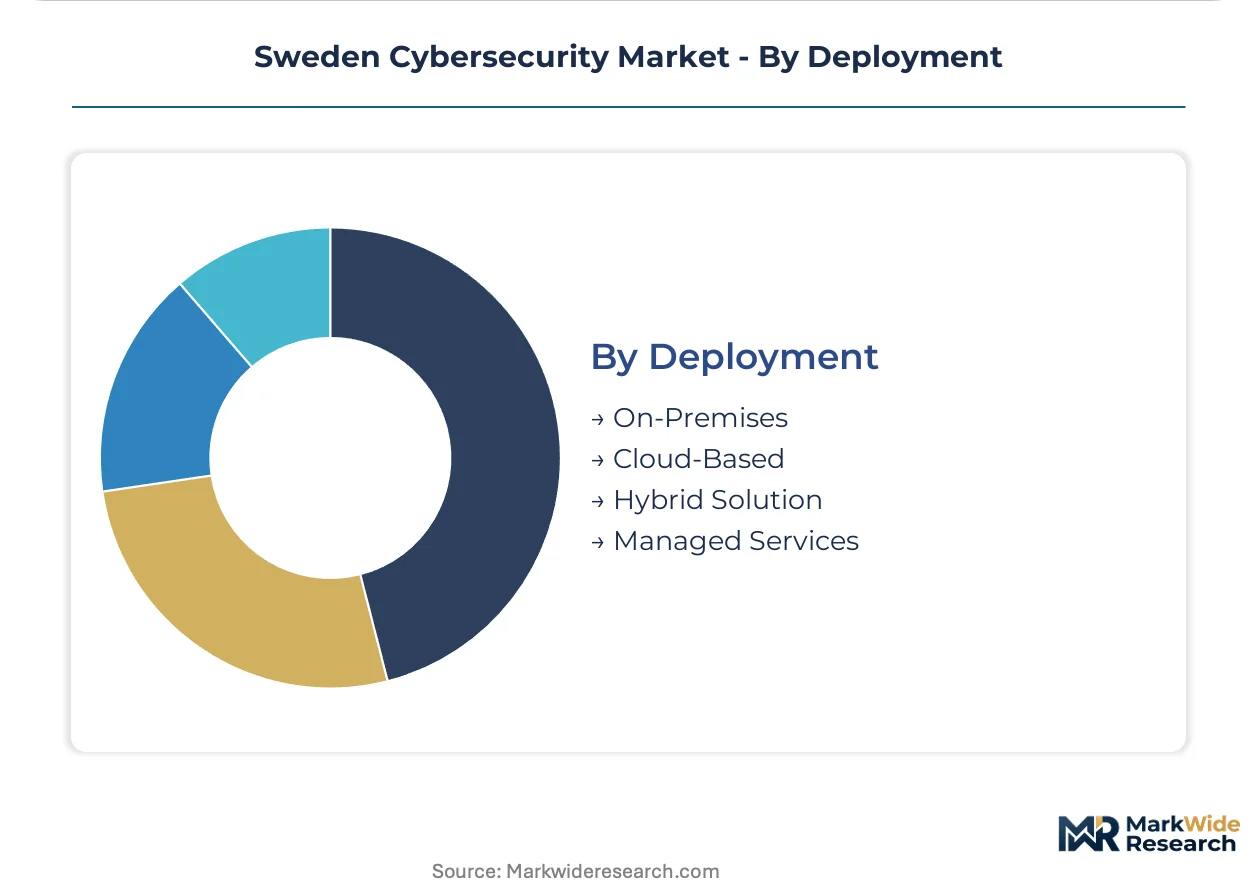
Deployment:
Customer type and internal capability maturity determine deployment architecture selection, with hybrid models accommodating staged cloud migration timelines.
- Cloud-Based:Native security controls and cloud workload protection platforms. Stockholm-region enterprises migrating distributed infrastructure drive steepest expansion trajectory, though data residency requirements limit multi-tenant SaaS adoption for defense-adjacent workloads.
- Hybrid Solution:Orchestrated controls spanning on-premises and cloud-native environments. Manufacturing CISOs favor this architecture to unify governance across Purdue Model Level 0-3 systems with modern detection capabilities.
- On-Premises:Air-gapped or self-managed infrastructure for classified environments.
- Managed Services:Fully outsourced security operations delivered as utility consumption.
Hybrid Solution holds the largest share; Cloud-Based is expanding most quickly on workload migration velocity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Swedish Civil Contingencies Agency's enforcement of NIS2 transposition requirements is redistributing cybersecurity procurement across domestic sub-regions. Stockholm's fintech density and Gothenburg's maritime infrastructure create divergent demand profiles that shape vendor qualification requirements.
Stockholm Metropolitan Region
Payment processors and digital banks in Stockholm's urban tech corridor drive specialized fraud detection procurement. The Swedish Post and Telecom Authority mandates resilience standards for electronic communications providers headquartered in the capital. Kista Science City concentrates cloud-native security posture management adoption as enterprises migrate distributed workloads.
Gothenburg and Västra Götaland
Port operators and shipping logistics firms in Gothenburg's maritime cluster generate underpenetrated demand for OT security solutions. The Swedish Transport Agency enforces vessel-to-shore communication protection standards for critical infrastructure operators. Lindholmen Science Park anchors industrial cybersecurity research partnerships between maritime firms and domestic vendors.
Malmö and Skåne County
Cross-border data flows through the Öresund Bridge corridor intensify GDPR Article 32 compliance investments among logistics firms. The Swedish Data Protection Authority audits breach notification timelines for healthcare networks operating across the Danish border. Medicon Valley's life sciences cluster implements encryption protocols for patient data transfers between Lund and Copenhagen facilities.
Linköping and Östergötland
Defense-adjacent manufacturing in Linköping requires MSB Tier-3 cleared vendors for classified aerospace contracts. The Swedish Defence Materiel Administration imposes personnel vetting timelines stretching 8-14 months for supplier onboarding. Saab AB's presence drives sovereign-cleared managed security services procurement from domestic providers with facility clearances.
Luleå and Norrbotten
Hyperscale data centers in Luleå's arctic region create demand for air-gapped security architectures and data residency controls. The Swedish Energy Agency enforces critical infrastructure protection standards for state-owned utilities operating hydroelectric facilities. Facebook's server farms anchor cloud workload protection platform deployment among facility operators.
Sweden Cybersecurity Market Competitive Landscape
On the supply side, the industry is bifurcating between sovereign-cleared domestic specialists and global platform vendors competing for hybrid enterprise estates. Swedish procurement rules disqualify non-domestic suppliers from classified government contracts, creating a protected tier for cleared vendors. Two strategic archetypes dominate: domestically headquartered firms with MSB Tier-3 clearance credentials, and multinational platform providers with cloud-native breadth. Competitive moves center on clearance acquisition partnerships and outcome-based retainer restructuring that ties vendor compensation to containment metrics.
Within the sovereign-cleared tier, Clavister AB and Truesec AB occupy positions that exemplify divergent specialization strategies. Clavister anchors government and defense contract procurement through its domestic facility clearances. Truesec sustains recurring revenue relationships with Stockholm financial institutions through incident response retainers tied to mean-time-to-containment performance. Palo Alto Networks Inc. represents the multinational platform archetype competing across hybrid Swedish enterprise estates without clearance-dependent contract access.
| Leading Market Players |
|---|
| Clavister AB |
| Truesec AB |
| Advenica AB |
| Palo Alto Networks Inc. |
| Fortinet Inc. |
| Cisco Systems Inc. |
| Check Point Software Technologies Ltd. |
| Trend Micro Incorporated |
| F5 Inc. |
| Others |
Value Network & Pricing Analysis
MSB Tier-3 clearance vetting timelines stretching 8-14 months compress vendor availability and inflate pricing spreads between sovereign-cleared domestic specialists and non-cleared multinational platforms. This regulatory chokepoint forces Swedish critical infrastructure operators to pay substantial premiums for cleared incident response retainers while channeling procurement toward the three qualified domestic firms.
Pricing Analysis
Certification level creates the primary spread across the Swedish cybersecurity market. Three-tier pricing structure across premium, standard, and economy levels reflects MSB clearance tier, with Tier-3 cleared vendors commanding substantial premiums for defense and energy contracts. Subscription-based SaaS models dominate cloud-native security posture management, while outcome-based retainers tie incident response compensation to mean-time-to-containment metrics. Pricing pressure stems from certified incident responder wage premiums inflating MSSP delivery costs. Mid-market firms exhibit highest price sensitivity, driving demand for fully outsourced managed services over in-house capability builds.
Supply Chain Analysis
Contract manufacturing concentration for security hardware components rests on facilities in Taiwan, China, and South Korea. Semiconductor supply for next-generation firewalls and encryption modules draws from these Asian manufacturing hubs, with specialized sensor production for OT-IT convergence applications anchored in Germany and Japan. Single-source vulnerability around advanced packet inspection chipsets creates exposure to export control restrictions. Distribution runs through Stockholm-region systems integrators and sovereign-cleared MSSP facilities for classified contracts, with direct vendor relationships dominating cloud-native software procurement.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Swedish cybersecurity architecture is fragmenting into modular, API-first components that displace monolithic platform consolidation, creating platform-economics inflection where interoperability standards reshape competitive positioning.
For Market Incumbents: Pre-empt sovereign-cleared competitor expansion by accelerating MSB Tier-3 certification partnerships and embedding outcome-based performance guarantees into retainer structures. Defensive consolidation around cloud-native platform breadth protects against modular specialist disaggregation, while backward integration into threat intelligence data lakes secures differentiated adversary context. For New Entrants and Emerging Players: Gothenburg's maritime logistics cluster offers underpenetrated white-space for OT security and vessel-to-shore communication protection solutions. AI-augmented threat hunting services targeting manufacturing CISOs struggling with Purdue Model governance unification provide a second penetrable entry point. Go-to-market should anchor on Lindholmen Science Park research partnerships to establish domestic credibility. For Investors and Strategic Acquirers: NIS2 transposition enforcement reshapes the acquisition landscape by privileging vendors with demonstrable MSB clearance credentials and documented incident response playbook maturity. Long-term viability centers on firms capable of bridging OT-IT convergence complexity for industrial clients. Watch for PTS 5G security mandate deadlines as inflection indicators accelerating network slicing isolation procurement.| Strategic Initiative | Industry Significance |
|---|---|
| MSB Tier-3 Clearance Acquisition | Unlocks classified defense and energy contracts previously restricted to three domestic vendors. |
| Outcome-Based Retainer Restructuring | Ties vendor compensation to mean-time-to-containment metrics demanded by Stockholm fintech clusters. |
| API-First Platform Modularization | Addresses interoperability priorities displacing monolithic consolidation in Swedish enterprise procurement. |
| OT-IT Convergence Capability Build | Captures manufacturing demand for unified governance across Purdue Model Level 0-3 systems. |
| Gothenburg Maritime Cluster Expansion | Penetrates underdeveloped port operator and shipping logistics security demand in Västra Götaland. |
Research Methodology
A standing panel of CISOs at critical infrastructure operators, MSSP delivery directors, MSB procurement officers, and PTS compliance leads provided ongoing calibration across primary interview rounds. Secondary validation drew from MSB enforcement guidelines, PTS resilience mandates, EU NIS2 transposition documents, and Swedish Civil Contingencies Agency incident response protocols. Bottom-up segment sizing triangulated against top-down market envelope estimates from trade association disclosures and government procurement databases.
Scenario-bracketing framed the analytical approach across the analysis window, modeling technology segmentation by deployment architecture and service delivery model alongside end-user vertical and geographic sub-region dimensions. CAGRs derived from historical trajectory analysis adjusted for regulatory enforcement timelines and cloud workload migration velocity. Forecast inputs incorporated MSB clearance backlog duration estimates and certified incident responder labor market tightness.
Practitioners should monitor MSB personnel vetting timeline compression, PTS 5G security mandate compliance deadlines, and sovereign-cleared vendor pool expansion for early signals requiring forecast revision. Cross-checking against Swedish Energy Agency critical infrastructure protection standards and Swedish Post and Telecom Authority resilience audit results is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Hungary Cybersecurity Market
Cybersecurity
Global Mobile Application Security Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Data Center Security Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market