
 Network Edge Security Solutions Market | 2026-2036
Network Edge Security Solutions Market Size, Share, and Industry Trends Forecast 2026-2036
Network Edge Security Solutions Market Foresight
Zero-trust architecture certification is redrawing procurement standards across enterprise edge deployments. Cisco Systems leverages its integrated hardware-software stack to dominate campus and branch edge installations. Fortinet sustains R&D intensity in converged networking-security appliances, while Palo Alto Networks specializes in cloud-native edge orchestration for distributed workforces.
Network edge security solutions encompass firewalls, intrusion detection systems, VPNs, and secure web gateways that enforce policy inspection within 50 milliseconds of traffic ingress at distributed network perimeters. These systems protect IoT endpoints, remote branches, and cloud interconnection points from lateral threat movement. Firewalls and secure web gateways anchor current revenue pools due to universal deployment mandates, though behavioral analysis and zero-trust technology segments are capturing fastest expansion as organizations retire implicit-trust network models. Small enterprises and service providers represent contrasting demand profiles, with the former prioritizing managed services deployment to offset skills scarcity.
FCC guidelines on communications infrastructure resilience, the EU NIS2 Directive's expanded critical entity coverage, and ISO 27001 certification requirements collectively elevate baseline product specifications and vendor qualification barriers. The EPA's cybersecurity evaluations for water sector operational technology further fragment market access by utility vertical. Stakeholders must weigh sovereign data residency rules against cloud-native architecture investments when configuring multi-country edge footprints.
Market Dynamics
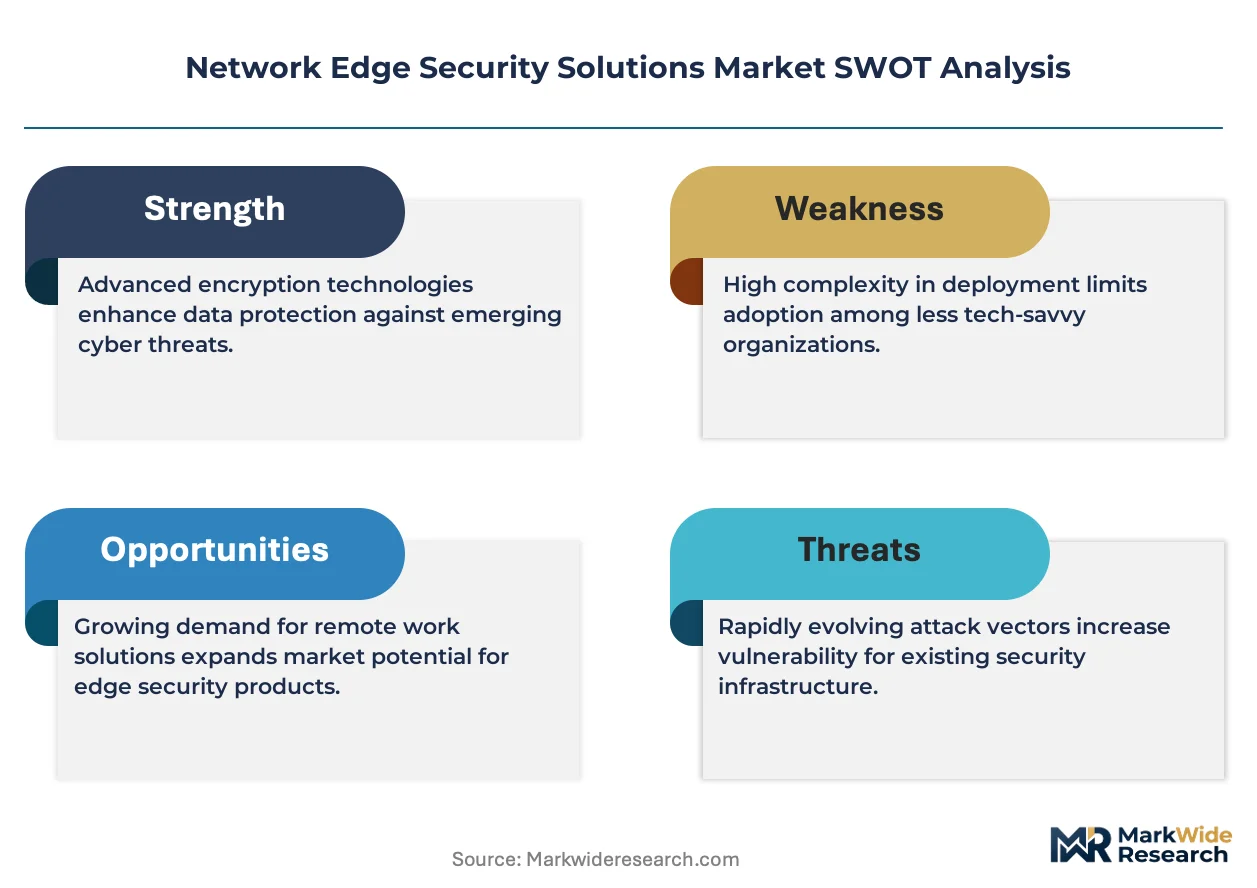
Zero-trust architecture mandates are dismantling perimeter-centric security procurement, forcing buyers to evaluate vendors on continuous verification capabilities rather than hardware throughput metrics alone.
Growth Catalysts
- EU NIS2 Directive:The directive's expanded critical entity coverage compels healthcare delivery networks and energy operators to upgrade edge inspection capabilities ahead of enforcement deadlines.
- Industrial IoT densification:Manufacturing corridors in Germany deploy hardened perimeter defenses as machine-to-machine traffic volumes overwhelm legacy firewall architectures.
- Behavioral analytics:Healthcare providers adopt real-time endpoint monitoring to detect anomalous access patterns across decentralized patient data repositories.
Market Restraints
- Specialized engineering talent scarcity:Zero-trust implementation requires scarce network security architects, inflating deployment timelines for mid-market enterprises.
- Silicon supply concentration:Custom ASIC production for converged security appliances clusters with Taiwanese foundries, exposing lead time volatility.
- Legacy infrastructure lock-in:Implicit-trust network architectures in established enterprises resist forklift replacement due to embedded operational dependencies.
Strategic Opportunities
- Managed security services:Small enterprises lacking in-house security operations centers represent an underpenetrated channel for subscription-based edge monitoring.
- ISO 27001 certification bundling:Vendors can package automated compliance documentation tools with hardware sales to accelerate procurement cycles.
- AI-powered threat detection:Convergence of machine learning inference engines with edge hardware enables sub-50-millisecond response without cloud round-trips.
Industry Challenges
- Multi-vendor integration complexity:Enterprises struggle to orchestrate policy consistency across firewalls, secure web gateways, and zero-trust brokers from different suppliers.
- Skills gap in cloud-native orchestration:Security teams trained on box-centric administration lack expertise in Kubernetes-native policy enforcement.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Network Edge Security Solutions Market |
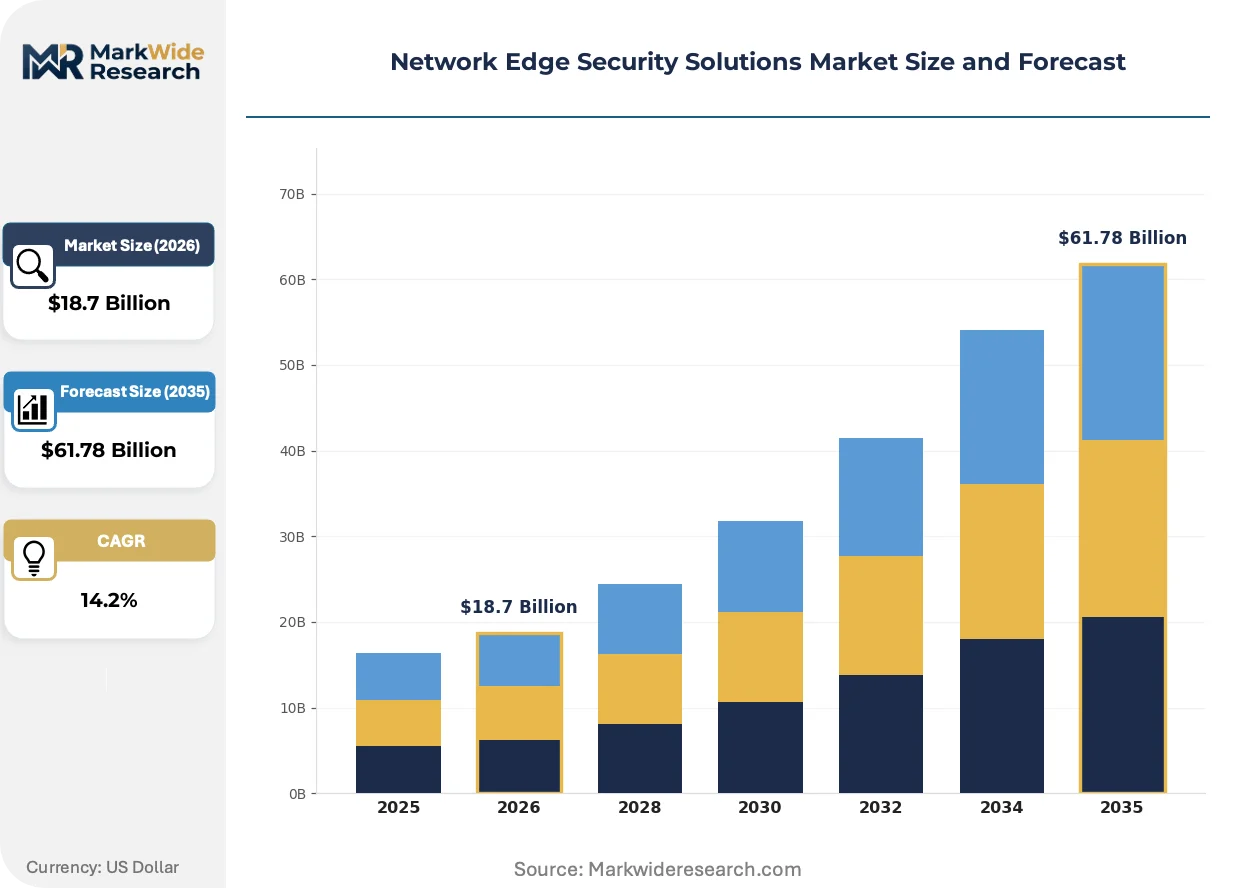
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $61.78 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewalls, Intrusion Detection Systems, VPNs, Secure Web Gateways End User: Small Enterprises, Large Enterprises, Service Providers, Government Agencies Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Technology: Artificial Intelligence, Machine Learning, Zero Trust, Behavioral Analysis |
| Companies Covered | Cisco Systems, Fortinet, Palo Alto Networks, Check Point Software Technologies, Zscaler, Cloudflare, Broadcom, Akamai Technologies, F5 Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Network Edge Security Solutions Market Shifts & Advancements
Edge security architectures are fragmenting into disaggregated software layers, separating control plane intelligence from data plane execution. This decomposition is rewriting vendor competitive moats.
Secure access service edge (SASE) frameworks are decomposing traditional perimeter security into cloud-delivered policy enforcement points. Financial services firms and distributed healthcare networks adopt these architectures fastest, replacing branch firewall appliances with software-defined edges. The technology is decomposing hardware-centric vendor margins into recurring software subscriptions.
The EU AI Act's risk classification system imposes mandatory cybersecurity documentation requirements on high-risk AI systems deployed at network edges. Critical infrastructure operators must now maintain audit trails for automated threat response decisions. Water utilities under EPA cybersecurity evaluations face the steepest compliance burden as operational technology networks converge with IT security stacks.
Consolidated platform procurement is displacing best-of-breed point solutions as CISOs reduce vendor sprawl. Mid-market enterprises favor integrated networking-security appliances over separate firewall and VPN purchases. German manufacturing clusters exhibit this preference most acutely, where standardization on single-vendor stacks simplifies cross-factory policy management.
Network Edge Security Solutions Market Segmentation
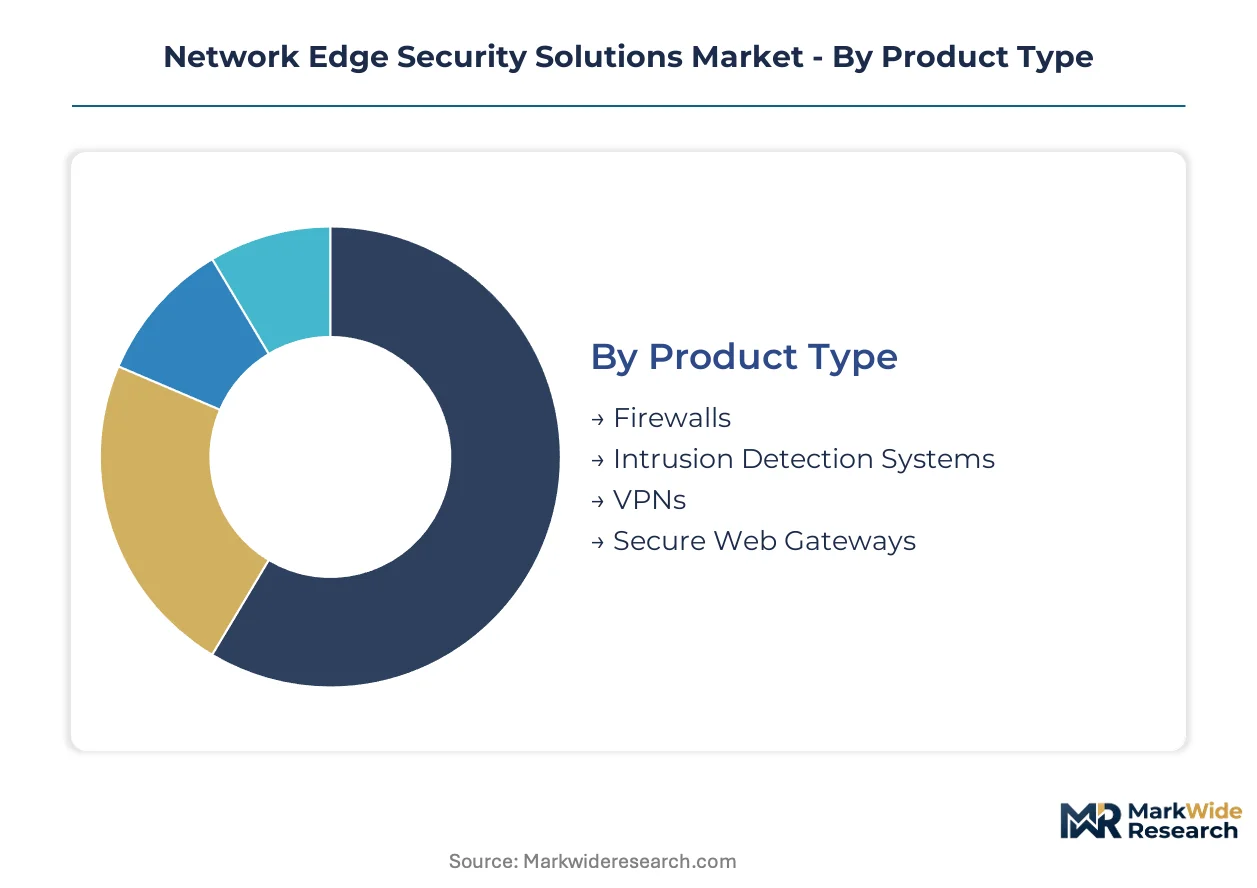
Edge security procurement fragments across four dimensions that reshape vendor go-to-market strategies. Product type determines hardware versus software revenue mix, while deployment mode separates capital expenditure buyers from subscription-oriented service providers.
Product Type:
Firewalls and secure web gateways anchor current margin pools due to universal deployment mandates, though behavioral analysis and zero-trust technology segments are capturing fastest expansion as organizations retire implicit-trust network models.
- Firewalls:Stateful packet inspection appliances enforce policy at 50-millisecond latency thresholds for manufacturing IoT corridors in Germany. Healthcare delivery networks upgrade next-generation firewall capacity as patient data decentralizes across endpoints.
- Intrusion Detection Systems:Signature and anomaly-based monitors scan east-west traffic for lateral movement patterns. Water utilities under EPA cybersecurity evaluations deploy these systems most aggressively as operational technology networks converge with IT stacks.
- VPNs:Encrypted tunnel termination for distributed workforces remains standard in financial services branch architectures.
- Secure Web Gateways:URL filtering and SSL inspection appliances protect egress traffic from cloud-connected endpoints.
The dominant share belongs to Firewalls, while Intrusion Detection Systems is closing the gap fastest.
End User:
Small enterprises and service providers represent contrasting demand profiles, with the former prioritizing managed services deployment to offset skills scarcity while the latter build multi-tenant infrastructure at scale.
- Small Enterprises:Organizations under 500 employees lack security operations centers and favor subscription-based edge monitoring. EU NIS2 Directive compliance deadlines compress procurement cycles for this segment.
- Large Enterprises:Multinational manufacturers standardize on single-vendor stacks to simplify cross-factory policy management across German industrial corridors.
- Service Providers:Telecommunications and MSSP entities aggregate edge security capacity for downstream resale to mid-market clients.
- Government Agencies:Critical infrastructure operators face mandatory cybersecurity baselines under FCC resilience guidelines and EPA sector-specific evaluations.
Large Enterprises command the deepest procurement budgets, yet Small Enterprises are expanding most quickly as managed security services penetrate underpenetrated channels.
Deployment:
Cloud-native architectures are displacing box-centric administration as security teams retrain on Kubernetes-native policy enforcement, fragmenting traditional hardware vendor margins into recurring software subscriptions.
- On-Premises:Appliance-based deployment persists in regulated verticals requiring sovereign data residency. German manufacturing clusters favor this model for air-gapped operational technology environments.
- Cloud-Based:Secure access service edge frameworks deliver policy enforcement through distributed cloud points of presence. Financial services firms adopt these architectures fastest to replace branch firewall appliances.
- Hybrid:Split-tunnel configurations maintain sensitive traffic on-premises while directing general internet egress to cloud inspection nodes.
- Managed Services:Third-party security operations centers monitor edge infrastructure for organizations lacking in-house expertise. Small enterprises drive demand concentration here.
On-Premises retains the largest installed base, though Cloud-Based deployment is gaining share fastest as SASE architectures mature.
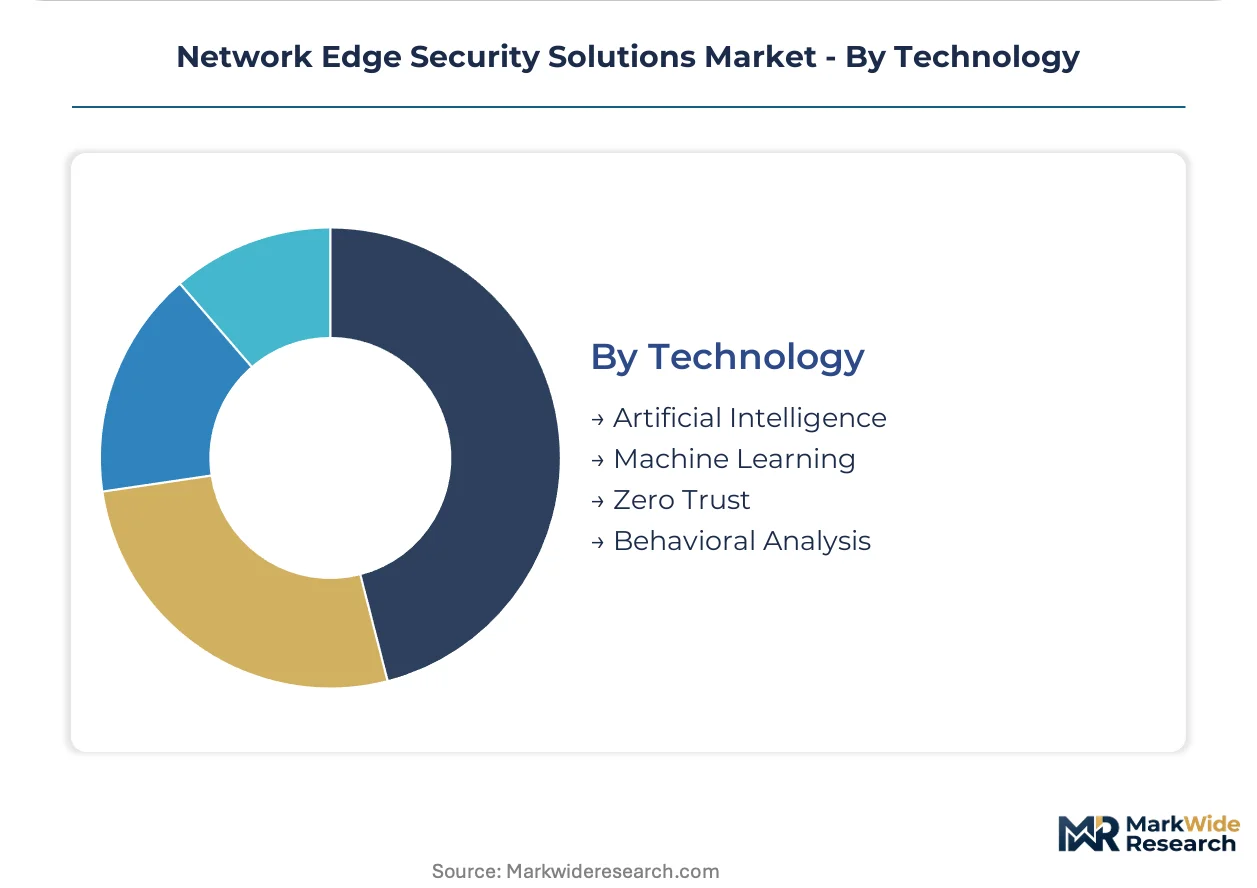
Technology:
Zero-trust mandates are dismantling perimeter-centric procurement standards, forcing buyers to evaluate vendors on continuous verification capabilities rather than hardware throughput metrics alone.
- Artificial Intelligence:Inference engines embedded in edge hardware enable sub-50-millisecond threat response without cloud round-trips. The EU AI Act imposes mandatory cybersecurity documentation requirements on these high-risk systems.
- Machine Learning:Behavioral models trained on endpoint telemetry detect anomalous access patterns across decentralized patient data repositories in healthcare networks.
- Zero Trust:Continuous verification architectures replace implicit-trust network models. Implementation requires scarce network security architects, inflating deployment timelines for mid-market enterprises.
- Behavioral Analysis:Real-time monitoring of user and entity behavior identifies compromised credentials through deviation from established baselines.
Zero Trust claims the steepest expansion trajectory, while Artificial Intelligence is climbing fastest as silicon vendors integrate inference accelerators into security appliances.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Specialized ASIC production for converged security appliances clusters with Taiwanese foundries, exposing lead time volatility that ripples through procurement cycles across end markets. German industrial IoT deployments and US healthcare networks absorb disproportionate supply allocations as compliance deadlines compress.
United States
Financial services firms and distributed healthcare networks adopt cloud-delivered policy enforcement fastest, replacing branch firewall appliances with software-defined edges. The FCC's communications infrastructure resilience guidelines elevate baseline product specifications for critical operators. Water utilities under EPA cybersecurity evaluations deploy intrusion detection systems most aggressively as operational technology networks converge with IT stacks.
Germany
Manufacturing corridors deploy hardened perimeter defenses as machine-to-machine traffic volumes overwhelm legacy firewall architectures. The EU NIS2 Directive's expanded critical entity coverage compels energy operators to upgrade edge inspection capabilities ahead of enforcement deadlines. Bavarian industrial clusters standardize on single-vendor stacks to simplify cross-factory policy management.
China
Domestic cloud providers build multi-tenant infrastructure at scale for downstream resale to mid-market clients. MIIT cybersecurity standards for critical information infrastructure impose mandatory compliance documentation on high-risk systems. Yangtze River Delta manufacturing hubs integrate inference accelerators into security appliances for sub-50-millisecond threat response.
Japan
Automotive supply chains densify edge monitoring across connected vehicle ecosystems and smart factory deployments. METI's industrial security guidelines mandate continuous verification architectures for critical manufacturing assets. Nagoya-area automotive clusters exemplify consolidated platform procurement displacing best-of-breed point solutions.
United Kingdom
Managed security services penetrate underpenetrated channels among small enterprises lacking in-house security operations centers. GDPR and post-Brexit data residency rules complicate multi-country edge footprint configurations. London financial services firms drive SASE architecture adoption to replace legacy branch firewall estates.
Network Edge Security Solutions Market Competitive Landscape
Concentration sits with integrated networking-security stack providers and cloud-native orchestration specialists. The vendor base stratifies across three tiers: converged appliance manufacturers with captive silicon programs, software-defined edge platforms delivering policy-as-a-service, and managed security service providers aggregating capacity for downstream resale. Strategic moves center on zero-trust certification bundling and AI-powered threat detection integration to accelerate procurement cycles.
Within the converged appliance tier, Cisco Systems and Fortinet exemplify hardware-software integration strategies, while Palo Alto Networks occupies a position representing cloud-native edge orchestration for distributed workforce architectures. These three anchors demonstrate how procurement standards now prioritize continuous verification capabilities over hardware throughput metrics alone.
| Leading Market Players |
|---|
| Cisco Systems |
| Fortinet |
| Palo Alto Networks |
| Check Point Software Technologies |
| Zscaler |
| Cloudflare |
| Broadcom |
| Akamai Technologies |
| F5 Networks |
| Others |
Supply & Pricing Matrix
EU NIS2 Directive compliance deadlines simultaneously gate vendor qualification and stratify price tiers across critical infrastructure procurement, forcing security appliance manufacturers to absorb certification costs into premium positioning while mid-market buyers face compressed upgrade cycles.
Pricing Analysis
FCC resilience guidelines dictate the pricing tier structure for communications infrastructure operators, separating certified premium appliances from standard enterprise offerings. Three-tier pricing structure across premium, standard, and economy levels tracks ISO 27001 documentation depth and AI-powered inference capability bundling. Cost compression in the standard tier is intensifying because managed security service providers aggregate volume procurement for downstream resale. Small enterprises exhibit highest price sensitivity due to skills-scarcity-driven reliance on subscription models, while German manufacturing clusters prioritize single-vendor standardization over unit cost minimization.
Supply Chain Analysis
Trans-Pacific container availability fluctuations and Kaohsiung port congestion ripple through lead times for custom ASIC-dependent appliances. Taiwan, South Korea, and the United States anchor silicon wafer and advanced packaging supply for converged security hardware. Production draws from Taiwanese foundries for firewall ASICs, South Korean memory components, and US-designed inference accelerators. Single-source vulnerability concentrates at the 7nm and 5nm process nodes where alternative qualified capacity remains scarce. Distribution runs through direct OEM channels for large enterprise accounts and telecommunications distributors for service provider aggregation.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Open-source zero-trust software stacks threaten incumbent hardware margins by enabling commodity white-box deployments, compelling established vendors to defend through integrated certification bundling and captive silicon differentiation.
For Market Incumbents: Compound zero-trust architecture certification into hardware-software bundles to accelerate procurement cycles and lock out best-of-breed point solution competitors. Deepen backward integration into custom ASIC design to escape Taiwanese foundry queue volatility and defend appliance margins against cloud-native SASE erosion. Prioritize ISO 27001 automated documentation tools as a channel control mechanism for mid-market accounts lacking security operations expertise.
For New Entrants and Emerging Players: Managed security services for small enterprises under 500 employees represents an under-penetrated channel where incumbent appliance vendors lack subscription-native delivery capabilities. Target healthcare delivery networks facing EU NIS2 Directive enforcement deadlines with compliance-accelerated deployment packages that front-load documentation automation. Pursue telecommunications partnerships for multi-tenant infrastructure resale rather than direct enterprise sales force buildout.
For Investors and Strategic Acquirers: EPA cybersecurity evaluations for water sector operational technology reshape the acquisition landscape by fragmenting market access and elevating vertical-specific compliance expertise as a scarce asset. Position for consolidation plays around managed security service providers with established small enterprise channels and ISO 27001 audit automation capabilities. Monitor EPA sector-specific evaluation rollout timelines as the inflection signal for utility vertical demand compression.
| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Certification Bundling | Accelerates procurement cycles for EU NIS2 Directive compliance deadlines in critical infrastructure. |
| Custom ASIC Vertical Integration | Reduces exposure to Taiwanese foundry lead time volatility for converged appliance production. |
| Managed Security Service Expansion | Captures small enterprise demand from organizations lacking in-house security operations centers. |
| AI Inference Engine Integration | Enables sub-50-millisecond threat response without cloud round-trips for manufacturing IoT corridors. |
| ISO 27001 Automation Tools | Reduces vendor sprawl evaluation friction for mid-market CISOs consolidating platform procurement. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at healthcare delivery networks, telecommunications procurement officers, manufacturing IT directors in German industrial corridors, and managed security service provider executives. Secondary validation drew from FCC infrastructure resilience filings, EPA cybersecurity evaluation documentation, EU NIS2 Directive implementation guidance, and ISO 27001 certification registry data. Bottom-up segment sizing triangulated against top-down macroeconomic indicators across the analysis window.
Across the modeling period, forecasts deployed a structured analytical framework spanning product type, deployment mode, end-user scale tier, and technology architecture segmentation. CAGRs were derived from fitted growth curves calibrated to regulatory enforcement timelines and silicon supply availability assumptions. Inputs included EU AI Act risk classification rollout schedules, German industrial IoT deployment trajectories, and healthcare endpoint densification patterns.
Material uncertainties — tariff exposure on Taiwanese semiconductor imports, EPA evaluation timeline acceleration, and open-source zero-trust stack maturity — sit outside the modeled envelope. Forecasts reflect documented assumptions regarding regulatory enforcement adherence and foundry capacity allocation prioritization. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Digital Forensics Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Post-Quantum Cryptography Market
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Enterprise Firewall Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
South Korea Ransomware Protection Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
Wireless Network Security Market