
 Cloud File Security Software Market | 2026-2036
Cloud File Security Software Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud File Security Software Market Insights
Enterprise buyer concentration in cloud file security is consolidating around large financial services and healthcare organizations with multi-cloud footprints. Microsoft leverages its Azure ecosystem to anchor integrated security suites across hybrid deployments. Palo Alto Networks competes through specialized threat detection capabilities for distributed file workloads. IBM Corporation sustains enterprise trust with encryption key management and regulatory consulting bundled into platform offerings.
Cloud file security software encompasses encryption, access governance, and real-time threat monitoring systems designed to protect data at rest and in motion across distributed cloud storage architectures, typically operating through API-native integrations with object storage services and identity providers. The primary commercial purpose centers on preventing unauthorized exfiltration, ensuring data residency compliance, and maintaining audit trails for regulated industries. Hybrid Cloud deployments now lead in revenue contribution as organizations retain sensitive files on-premises while bursting archival workloads to public infrastructure. Encryption services command the deepest margin pools due to key management complexity and compliance-driven non-discretionary spending. Threat Detection represents the fastest-expanding service type as AI-powered anomaly scanning replaces periodic manual audits.
GDPR enforcement by European data protection authorities and HIPAA oversight from the US Department of Health and Human Services are reshaping product requirements toward automated data classification and breach notification capabilities. PCI DSS standards further constrain how payment processors architect file access controls, creating procurement urgency among retail and fintech end users. ISO 27001 certification has become a baseline vendor qualification, filtering out smaller providers lacking documented security management systems. Stakeholders must weigh whether to consolidate around platform-native security modules or maintain best-of-breed point solutions as cloud provider ecosystems deepen their native capabilities.
Market Dynamics
The EU AI Act enforcement timeline is compressing procurement cycles for automated compliance tools across financial services and healthcare organizations with multi-cloud footprints.
Growth Catalysts
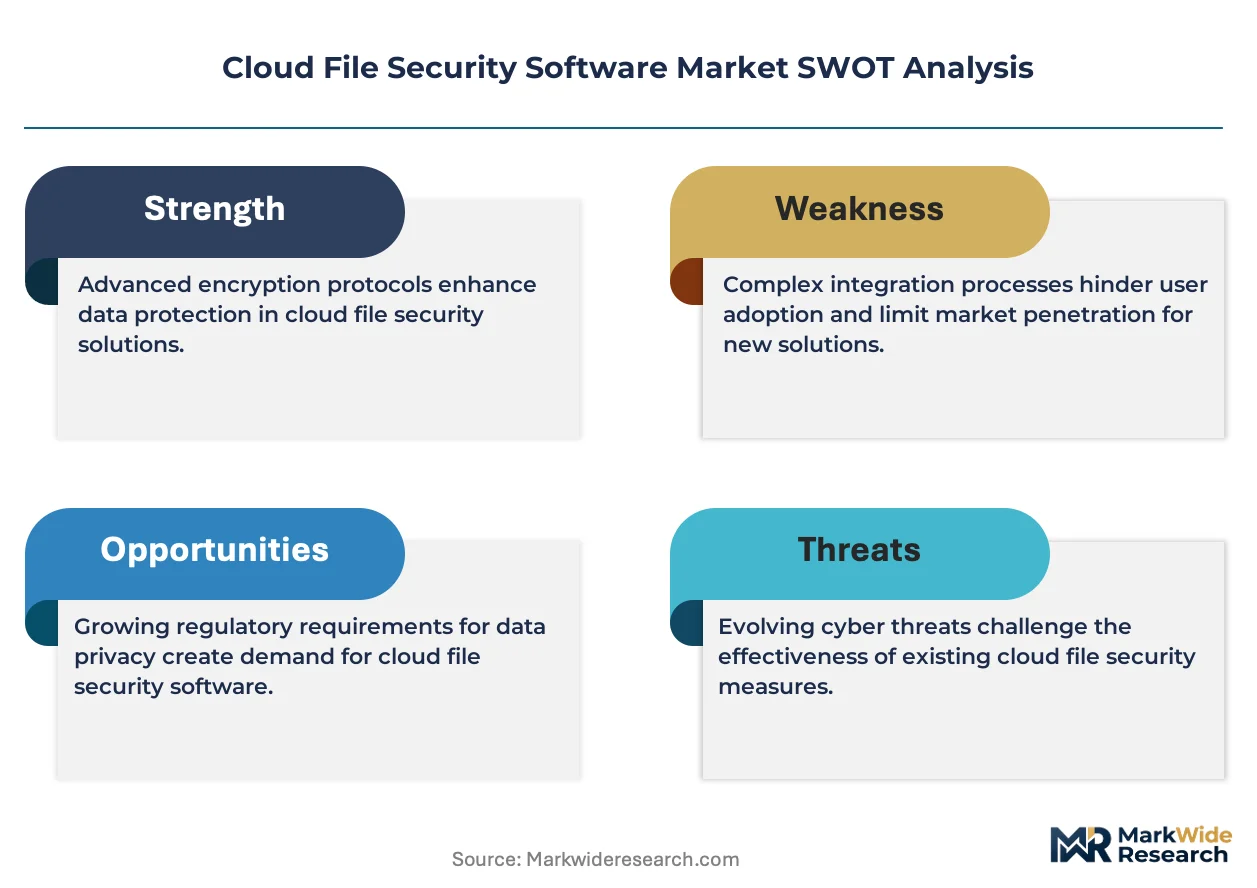
- GDPR enforcement actions:European data protection authorities impose fines that exceed cost of preventive software, accelerating replacement of manual audit processes with automated data classification systems.
- Hybrid cloud architectures:Financial services firms retain sensitive files on-premises while bursting archival workloads, creating dual-environment security requirements that API-native platforms address.
- PCI DSS 4.0 mandates:Payment processors face stricter file access control requirements, generating procurement urgency among retail and fintech end users before the March 2025 deadline.
Market Restraints
- Encryption key management complexity:FIPS 140-2 Level 3 hardware security module procurement adds 40-60% cost overhead to baseline software licenses, constraining mid-market adoption.
- Cloud provider ecosystem lock-in:Native Azure, AWS, and Google Cloud security modules deepen integration dependencies, raising switching costs for enterprises seeking best-of-breed alternatives.
- Cross-border data transfer friction:Schrems II rulings invalidate Privacy Shield mechanisms, forcing vendors to architect region-specific instances that fragment development resources.
Strategic Opportunities
- Japan's data sovereignty requirements:METI guidelines on financial data localization create demand for in-country encryption key custody services that foreign vendors currently under-serve.
- AI-powered anomaly detection:Convergence of large language models with behavioral analytics enables real-time insider threat identification that replaces periodic manual audits.
- Healthcare IoT file streams:Connected medical devices generate unstructured imaging and telemetry data requiring edge-to-cloud encryption pipelines that existing tools inadequately address.
Industry Challenges
- Zero-trust architecture implementation:Micro-segmentation of file access requires identity provider reconfiguration that strains enterprise IT teams lacking cloud-native security expertise.
- ISO 27001 certification timelines:Vendor qualification processes extend 12-18 months, filtering smaller providers and compressing competitive windows for emerging entrants.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud File Security Software Market |
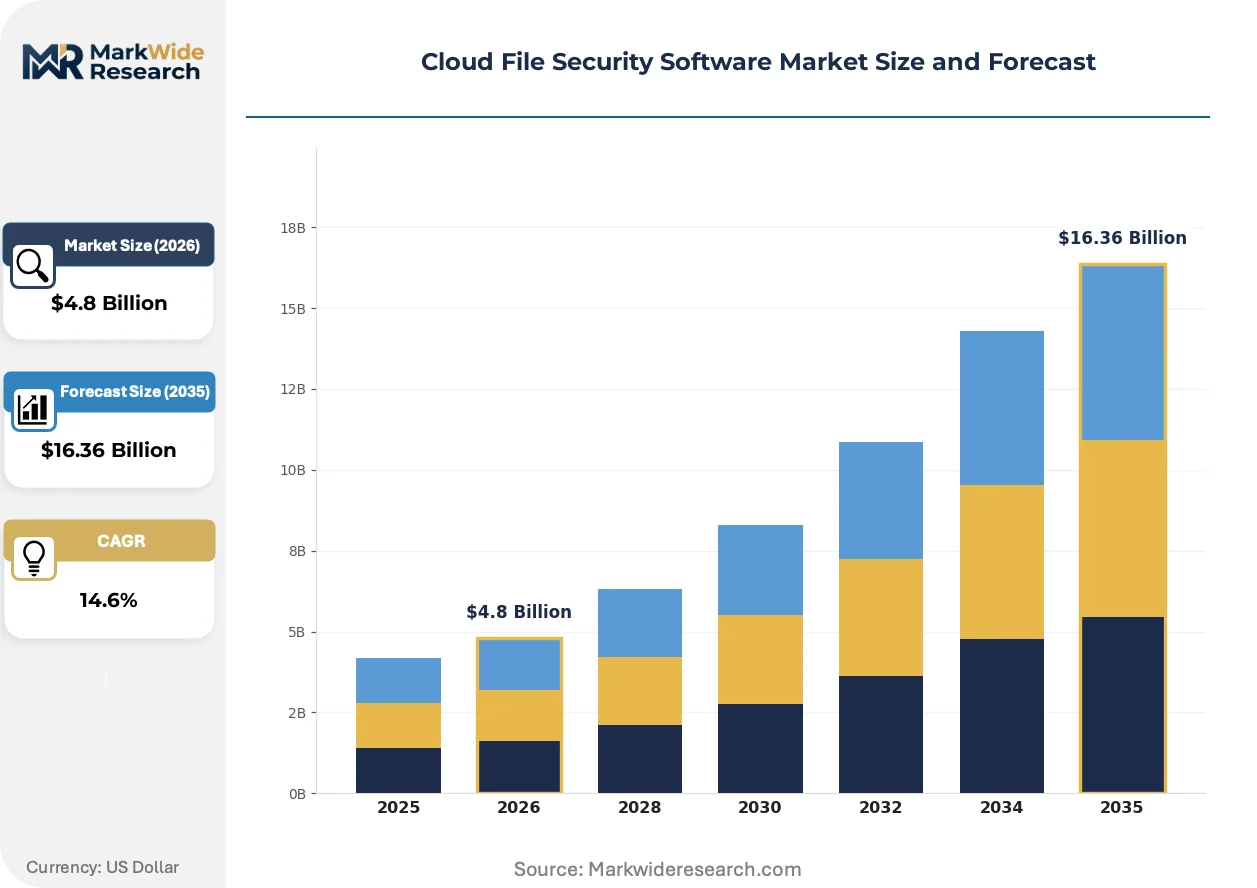
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $16.36 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Service Type: Encryption, Access Control, Threat Detection, Compliance Monitoring End User: Enterprise, SMBs, Government, Non-Profit Compliance Standard: GDPR, HIPAA, PCI DSS, CCPA |
| Companies Covered | Microsoft, Amazon Web Services, Broadcom, Check Point Software Technologies, Palo Alto Networks, IBM Corporation, Cisco Systems, Fortinet, Virtru, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud File Security Software Market Trends and Innovations
Artificial intelligence is rewriting threat detection economics by replacing signature-based scanning with behavioral models that reduce false-positive rates and operational overhead.
Confidential computing hardware is consolidating encryption processing into trusted execution environments at the CPU level. Financial services institutions in Germany and Switzerland deploy these enclaves for high-frequency trading data and patient records. The technology is consolidating competitive differentiation around hardware-backed attestation rather than software-only claims.
The EU AI Act risk classification framework imposes documentation burdens on security vendors deploying automated decision systems. High-risk applications require conformity assessments that extend sales cycles by 4-6 months. Healthcare providers in France and the Netherlands delay procurement of AI-enabled access governance tools pending clarity from national regulators on classification boundaries.
Enterprise buyers now unbundle security software from cloud storage contracts to avoid provider lock-in. Procurement teams in United States manufacturing and energy verticals issue separate RFPs for encryption, access governance, and threat monitoring. This fragmentation favors specialized vendors with API flexibility over integrated suites in sectors with complex compliance requirements.
Cloud File Security Software Market Segmentation
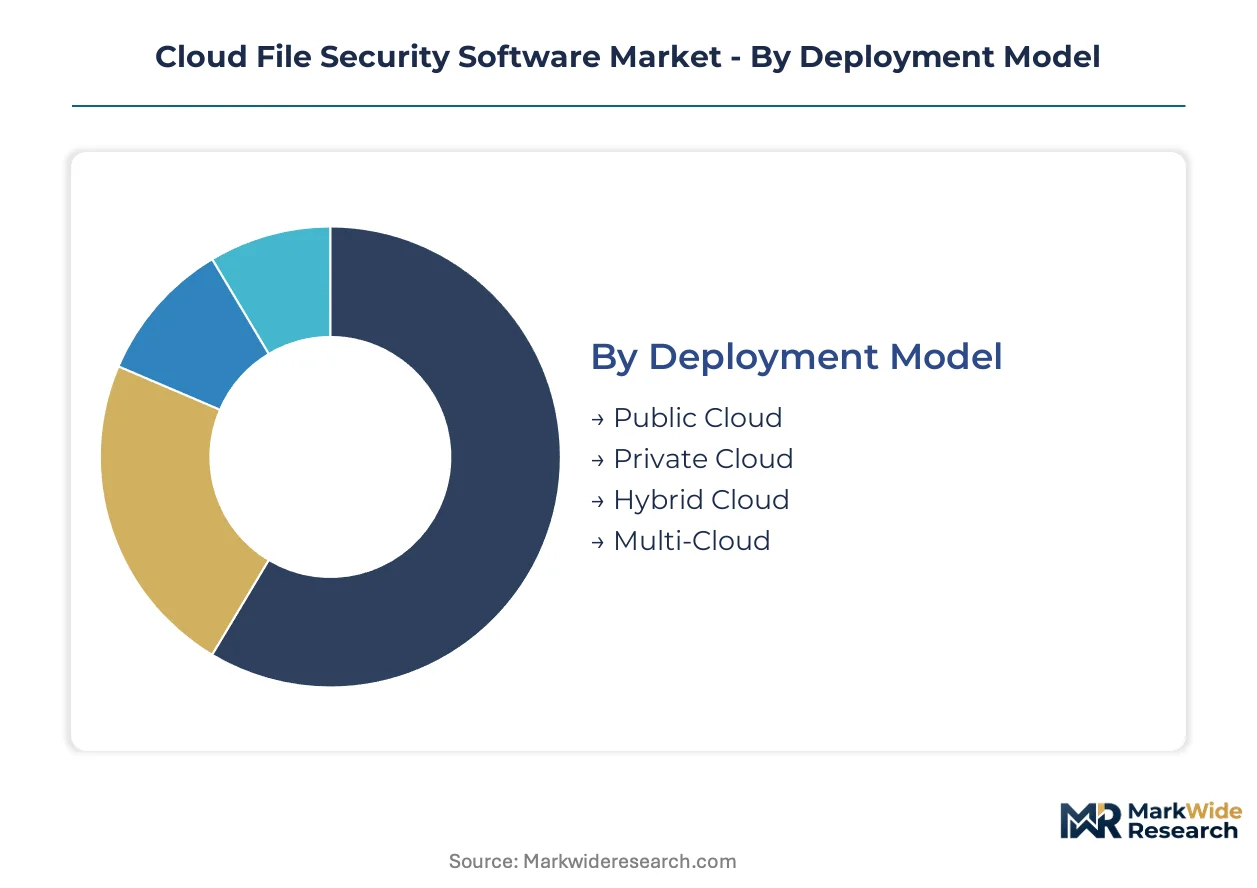
Cloud file security procurement patterns diverge sharply across deployment architectures and regulatory exposure levels. Buyers segment investments by data sensitivity tiers, with financial services and healthcare organizations driving premium service adoption.
Deployment Model:
Supply concentration in hybrid infrastructure tooling has consolidated around vendors with dual-environment orchestration capabilities.
- Hybrid Cloud:Organizations retain sensitive files on-premises while bursting archival workloads to public infrastructure, creating dual-environment security requirements that API-native platforms address. Financial services firms in Germany and the United States dominate procurement, driven by GDPR and state-level data residency mandates.
- Multi-Cloud:Distributed architectures spanning AWS, Azure, and Google Cloud demand vendor-agnostic encryption key management. Enterprise buyers unbundle security from storage contracts to avoid provider lock-in, favoring specialized vendors with cross-platform API flexibility.
- Public Cloud:Native security modules from hyperscalers serve cost-sensitive workloads with baseline encryption.
- Private Cloud:On-premises deployments concentrate in defense and critical infrastructure sectors with air-gapped requirements.
Hybrid Cloud absorbs the bulk of installed capacity; Multi-Cloud is expanding most quickly.
Service Type:
Cost tier differentiation separates compliance-mandated non-discretionary spending from discretionary threat intelligence investments.
- Encryption:Services command the deepest margin pools due to key management complexity and FIPS 140-2 Level 3 hardware security module requirements. Demand concentrates among payment processors facing PCI DSS 4.0 deadlines, with fintech procurement urgency peaking ahead of regulatory enforcement.
- Threat Detection:AI-powered anomaly scanning replaces periodic manual audits, reducing false-positive rates and operational overhead. Healthcare organizations in France and the Netherlands delay procurement pending EU AI Act classification clarity from national regulators.
- Access Control:Identity provider integrations govern file permissions across distributed repositories.
- Compliance Monitoring:Automated data classification systems accelerate replacement of manual audit processes under GDPR enforcement pressure.
Encryption captures the largest revenue share; Threat Detection exhibits the steepest expansion trajectory.
End User:
Customer type determines procurement sophistication, with enterprise buyers unbundling security components while smaller organizations accept integrated suites.
- Enterprise:Multi-cloud footprints with dedicated procurement teams issue separate RFPs for encryption, access governance, and threat monitoring. Manufacturing and energy verticals in the United States lead this fragmentation trend, favoring API flexibility over integrated suites.
- Government:Sovereign data requirements drive in-country encryption key custody demand that foreign vendors currently under-serve.
- SMBs:Limited IT security expertise constrains adoption to cloud-native bundled offerings with minimal configuration.
- Non-Profit:Budget constraints prioritize open-source or donor-subsidized security tools over commercial platforms.
Enterprise accounts dominate absolute spending; Government procurement is gaining share fastest.
Compliance Standard:
Regulatory maturity shapes product requirements, with established frameworks commanding stable investment and emerging mandates creating procurement spikes.
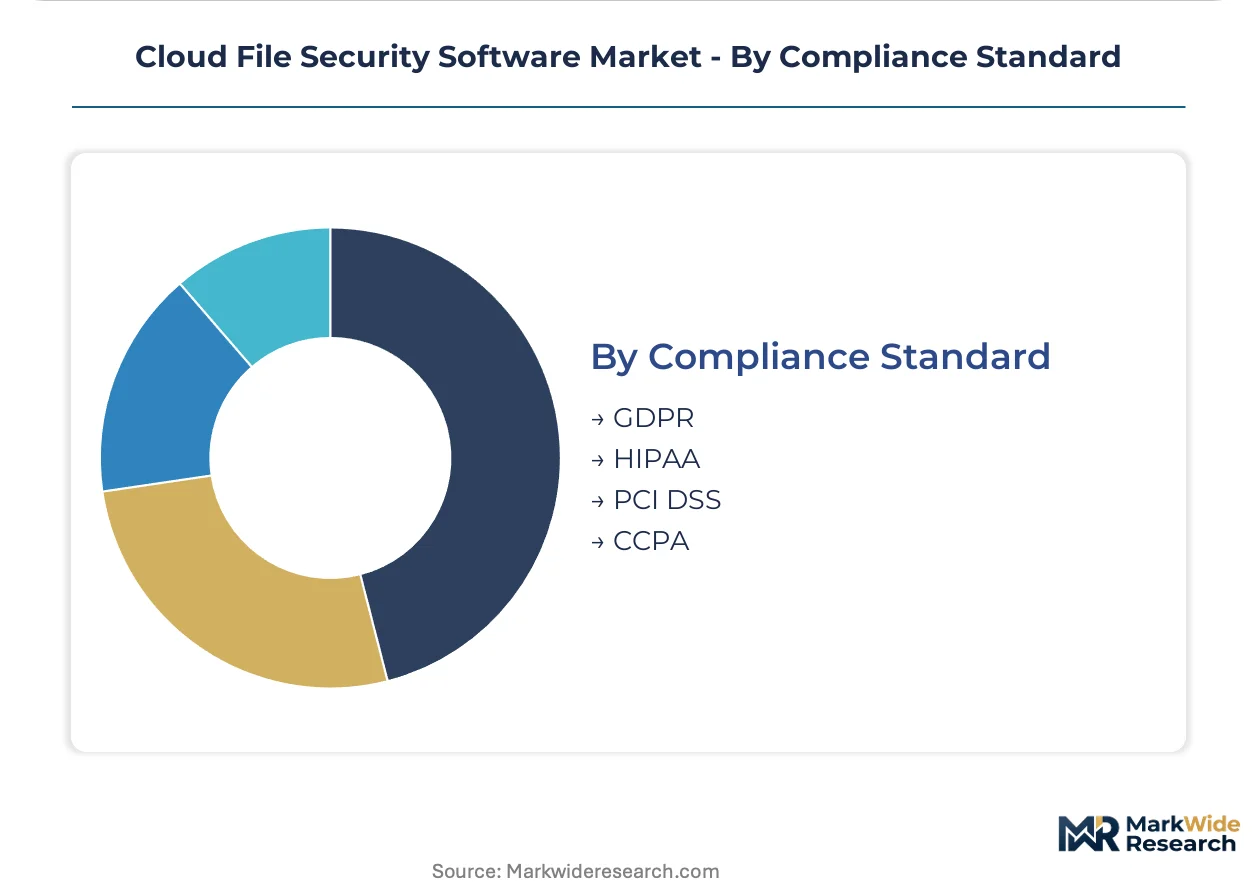
- GDPR:European data protection authorities impose fines that exceed preventive software costs, accelerating automated data classification and breach notification capabilities. Enforcement actions in Germany and France reshape vendor qualification toward documented security management systems.
- HIPAA:US Department of Health and Human Services oversight drives encryption for patient records and connected medical device telemetry streams.
- PCI DSS:Payment processors face stricter file access control requirements under version 4.0, generating urgency among retail and fintech end users.
- CCPA:California's privacy framework extends consumer data rights, prompting data inventory and deletion tooling investments.
GDPR-aligned solutions anchor the installed base; HIPAA-driven procurement is climbing the fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cloud file security procurement concentrates in jurisdictions with stringent data sovereignty mandates and active regulatory enforcement. Financial services and healthcare organizations in Germany, the United States, and Japan drive premium solution adoption.
United States
Enterprise buyers in manufacturing and energy verticals unbundle security components to avoid cloud provider lock-in. HIPAA oversight from the Department of Health and Human Services mandates encryption for patient records and connected medical device telemetry. The Greater Boston cluster hosts procurement teams issuing separate RFPs for encryption, access governance, and threat monitoring.
Germany
Financial institutions deploy confidential computing enclaves for high-frequency trading data under GDPR enforcement pressure. The country's national data protection authority imposes fines that exceed preventive software costs. Frankfurt's banking sector anchors demand for FIPS 140-2 Level 3 hardware security modules.
Japan
METI guidelines on financial data localization create demand for in-country encryption key custody services. Healthcare providers delay AI-enabled access governance procurement pending regulatory clarity. Tokyo's enterprise IT market leads hybrid cloud adoption with dual-environment security requirements.
France
CNIL enforcement actions reshape vendor qualification toward documented security management systems. Healthcare organizations in Paris and the Netherlands border region await EU AI Act classification boundaries for automated decision systems. The Île-de-France cluster drives compliance monitoring tool procurement ahead of regulatory deadlines.
United Kingdom
Post-Brexit data transfer arrangements force vendors to architect region-specific instances. London's fintech sector faces PCI DSS 4.0 file access control mandates with March 2025 enforcement. The capital's payment processors generate urgency for automated data classification systems.
Cloud File Security Software Market Competitive Landscape
United States producers anchor the platform-integrated tier; European specialists hold the compliance consulting segment. The vendor base organizes around three strategic archetypes: hyperscaler ecosystems, best-of-breed threat detection vendors, and legacy enterprise consultancies bundling encryption with regulatory advisory. Competitive moves concentrate on API-native integration partnerships and vertical-specific certification acceleration.
Within the platform-integrated tier, Microsoft and Amazon Web Services exemplify ecosystem lock-in strategies through native security modules. Palo Alto Networks occupies a position among specialized threat detection vendors competing for distributed file workloads. IBM Corporation sits within the legacy consultancy archetype, bundling encryption key management with regulatory advisory services.
| Leading Market Players |
|---|
| Microsoft |
| Amazon Web Services |
| Broadcom |
| Check Point Software Technologies |
| Palo Alto Networks |
| IBM Corporation |
| Cisco Systems |
| Fortinet |
| Virtru |
| Others |
Pricing and Supply Chain Analysis
FIPS 140-2 Level 3 hardware security module procurement costs cascade through SaaS subscription tiers, with compliance-mandated encryption services commanding premium pricing while baseline threat detection modules face downward pressure from hyperscaler native alternatives. Financial services firms in Germany and payment processors under PCI DSS 4.0 deadlines absorb these hardware cost premiums, whereas mid-market buyers in the United States and Japan consolidate around bundled offerings to minimize procurement complexity.
Pricing Analysis
Volume concentrates in standardized SaaS tiers while margins pool in customized encryption deployments with dedicated key custody infrastructure. Pricing stratifies across enterprise-grade FIPS-certified modules, mid-market API-native platforms, and economy-tier bundled security from cloud providers. Cost compression in the mid-market tier is intensifying because Microsoft Azure and AWS deepen native security integration at no incremental license cost. Enterprise buyers in healthcare and financial services exhibit the lowest price sensitivity due to non-discretionary compliance spending, while SMBs in manufacturing verticals prioritize cost minimization over feature depth.
Supply Chain Analysis
Dual-sourcing requirements for encryption hardware compel buyers to qualify both Thales and Entrust HSM vendors alongside software-layer alternatives, fragmenting procurement leverage across the stack. Supply concentrates in the United States for FIPS-certified hardware, Israel for behavioral analytics engines, and India for API development and integration services. The software layer draws from open-source cryptographic libraries, proprietary AI training pipelines, and hyperscaler infrastructure-as-a-service. Single-source vulnerability in hardware security module fabrication creates procurement risk for European buyers facing Schrems II data localization mandates. Distribution runs through direct enterprise sales teams for large accounts and cloud marketplaces for mid-market self-service procurement.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud file security vendors are racing to deepen vertical integration into encryption hardware and managed key custody services, with control over the cryptographic trust anchor emerging as the decisive margin lever. This upstream integration imperative reshapes competitive positioning across all three archetypes: hyperscaler ecosystems, best-of-breed specialists, and legacy consultancies.
For Market Incumbents: Deepen API-native integration partnerships with identity providers and object storage platforms to defend against hyperscaler ecosystem lock-in. Invest in ISO 27001 certification acceleration to compress vendor qualification timelines that currently filter emerging competitors. The threat of AI-powered anomaly detection commoditization demands proprietary training data accumulation and vertical-specific model tuning to sustain differentiation. For New Entrants and Emerging Players: AI-powered confidential computing orchestration offers a technology-first wedge into financial services deployments in Germany and Switzerland where hardware-backed attestation requirements exceed current vendor capabilities. Japan's METI data localization guidelines create the most penetrable geography for foreign entrants offering in-country encryption key custody. A channel partnership strategy with systems integrators in Tokyo and Frankfurt accelerates enterprise access without direct sales infrastructure. For Investors and Strategic Acquirers: EU AI Act conformity assessment delays are the leading indicator that regulatory clarity will trigger a 4-6 month procurement surge for automated compliance tools. The 5-10 year viability window favors acquisition targets with documented security management systems and existing healthcare or financial services customer concentration. The signal to watch is national regulator guidance on high-risk system classification boundaries in France and the Netherlands.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | Hardware-backed enclaves from Intel and AMD differentiate German banking sector offerings from software-only competitors. |
| Regulatory Certification Acceleration | ISO 27001 and EU AI Act pre-certification compresses 12-18 month vendor qualification cycles for healthcare buyers. |
| Geographic Data Sovereignty Expansion | In-country encryption key custody services capture Japanese financial institutions under METI localization mandates. |
| AI Threat Detection Platform Launch | Behavioral models trained on healthcare IoT telemetry streams address edge-to-cloud security gaps in connected medical devices. |
| API-Native Integration Acquisition | Specialized vendors with cross-platform flexibility counter hyperscaler ecosystem lock-in for multi-cloud enterprise buyers. |
Research Methodology
Document review covered regulatory filings from the SEC and EU data protection authorities, complemented by interviews with chief information security officers, cloud procurement leads, and encryption key management specialists. Secondary validation drew from GDPR enforcement action databases, PCI DSS compliance audit reports, and hyperscaler security service disclosures. Bottom-up triangulation across deployment model adoption rates and top-down validation through compliance-spending estimates anchored the market sizing framework.
Segmentation outputs reflect modeled dimensions spanning deployment architecture, service type, organization size tier, and regional regulatory cluster intensity. Growth trajectory derivation incorporated encryption key management complexity premiums, AI-powered threat detection adoption curves, and cross-border data transfer friction coefficients. Inputs feeding the projection framework included HIPAA audit frequency data, EU AI Act implementation timelines, and confidential computing hardware availability roadmaps from Intel and AMD.
Several conditions sit outside the modeled scope, including unannounced regulatory enforcement actions, hyperscaler pricing restructuring, and breakthrough cryptographic algorithm standardization. Forecasts reflect assumptions regarding sustained GDPR fine severity, PCI DSS 4.0 deadline adherence, and continued Schrems II data localization pressure. Deviation in EU AI Act classification boundary clarity or confidential computing hardware cost curves would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Secure Access Service Edge Market
Security Software
Wi-Fi Based Home Camera Market
Security Software
Personal Data Recovery Software Market
Security Software
Identity Verification Software Market
Security Software
AD-Blocking Software Market
Security Software
Battery-Powered Doorbell Camera Market
Security Software
Global Background Check Software Market
Security Software
Secure Email Gateway Market
Security Software
AI in Security Market
Security Software
Global Anti-Spam Software Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Patch and Remediation Software Market
Security Software
Global Privileged Access Management (PAM) Solutions Market
Security Software
Embedded Security Market
Security Software
Global SMS Firewall Market
Security Software
Network Security Appliance Market