
 Cloud Security in Banking Market | 2026-2036
Cloud Security in Banking Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Security in Banking Market Outlook
Quantum-resistant encryption is repositioning cloud security economics for financial institutions facing long-term data protection horizons. Palo Alto Networks leverages AI-driven threat detection to sustain technology leadership in cloud-native banking environments. Microsoft Azure anchors enterprise trust through extensive compliance certifications across financial services verticals. Fortinet competes on integrated networking-security convergence, reducing operational complexity for mid-tier banks migrating core systems to cloud infrastructure.
Cloud security in banking encompasses the policies, technologies, and controls protecting financial data, applications, and infrastructure hosted across distributed computing environments, typically employing zero-trust architectures with continuous authentication protocols and end-to-end encryption standards. Its primary purpose is to maintain confidentiality, integrity, and availability of sensitive financial records while enabling scalable digital service delivery. Hybrid cloud deployment models attract the largest security investment as banks balance regulatory data sovereignty requirements against elasticity needs. Identity management services command premium pricing due to escalating credential-based attack volumes targeting financial institutions. Security information and event management solutions represent the fastest-expanding segment as real-time threat correlation becomes essential for regulatory reporting and incident response.
The Federal Financial Institutions Examination Council in the United States, the European Banking Authority under EU jurisdiction, and the Monetary Authority of Singapore shape cloud security demand through mandatory risk assessment frameworks and third-party vendor oversight requirements. These regulators enforce baseline encryption standards, incident notification timelines, and audit trail preservation that directly determine product design priorities and market access eligibility for cloud security vendors. Stakeholders must monitor evolving cross-border data localization mandates that could fragment cloud architecture strategies and compliance tooling requirements across jurisdictions.
Market Dynamics
Zero-trust architecture mandates from US federal banking regulators and the EU AI Act are forcing financial institutions to rebuild cloud governance frameworks from authentication protocols upward, compressing procurement cycles and elevating identity management vendors to strategic supplier status.
Growth Catalysts
- GDPR Article 32 Enforcement:European banking supervisors now mandate encryption-at-rest for all customer transaction data processed in cloud environments, compelling infrastructure upgrades across retail and commercial banking segments.
- Real-time payment rails:FedNow and similar instant settlement systems in the United States, India, and Singapore generate continuous data flows that require cloud-native security architectures with sub-second threat detection capabilities.
- Quantum computing threat horizons:Long-dated financial instruments held by insurers and pension funds face decryption vulnerabilities that accelerate migration to post-quantum cryptographic standards.
Market Restraints
- Hyperscaler concentration:Cloud infrastructure supply concentrates among three US-based providers, creating systemic operational risk for European and Asian banks subject to data sovereignty requirements.
- Specialized talent scarcity:Certified cloud security architects with financial services compliance experience command compensation premiums exceeding 40% above generalist cybersecurity roles, inflating implementation costs.
- Cross-border data friction:China's Cybersecurity Law and data localization mandates fragment cloud architectures for multinational banks operating across Asia-Pacific jurisdictions.
Strategic Opportunities
- Southeast Asia expansion:Vietnam, Indonesia, and Philippines retail banking sectors show minimal cloud security penetration relative to transaction volume growth, creating first-mover advantages for compliance-automated platforms.
- AI-driven threat hunting:Convergence of machine learning inference at the network edge with centralized SIEM correlation enables predictive incident response previously unavailable to mid-tier institutions.
- Open banking API security:PSD2-mandated data sharing across European financial services creates specialized demand for API gateway protection and consent management tooling.
Industry Challenges
- Mainframe integration complexity:Core banking systems running COBOL on-premises require custom API middleware to interface with cloud-native security monitoring, extending deployment timelines.
- Multi-jurisdiction audit fatigue:Institutions operating across US, EU, and Singapore regulatory domains face overlapping but non-identical penetration testing and documentation requirements.
- Third-party vendor verification:Supply chain security assessments for cloud security vendors themselves lack standardized frameworks, complicating due diligence.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Security in Banking Market |
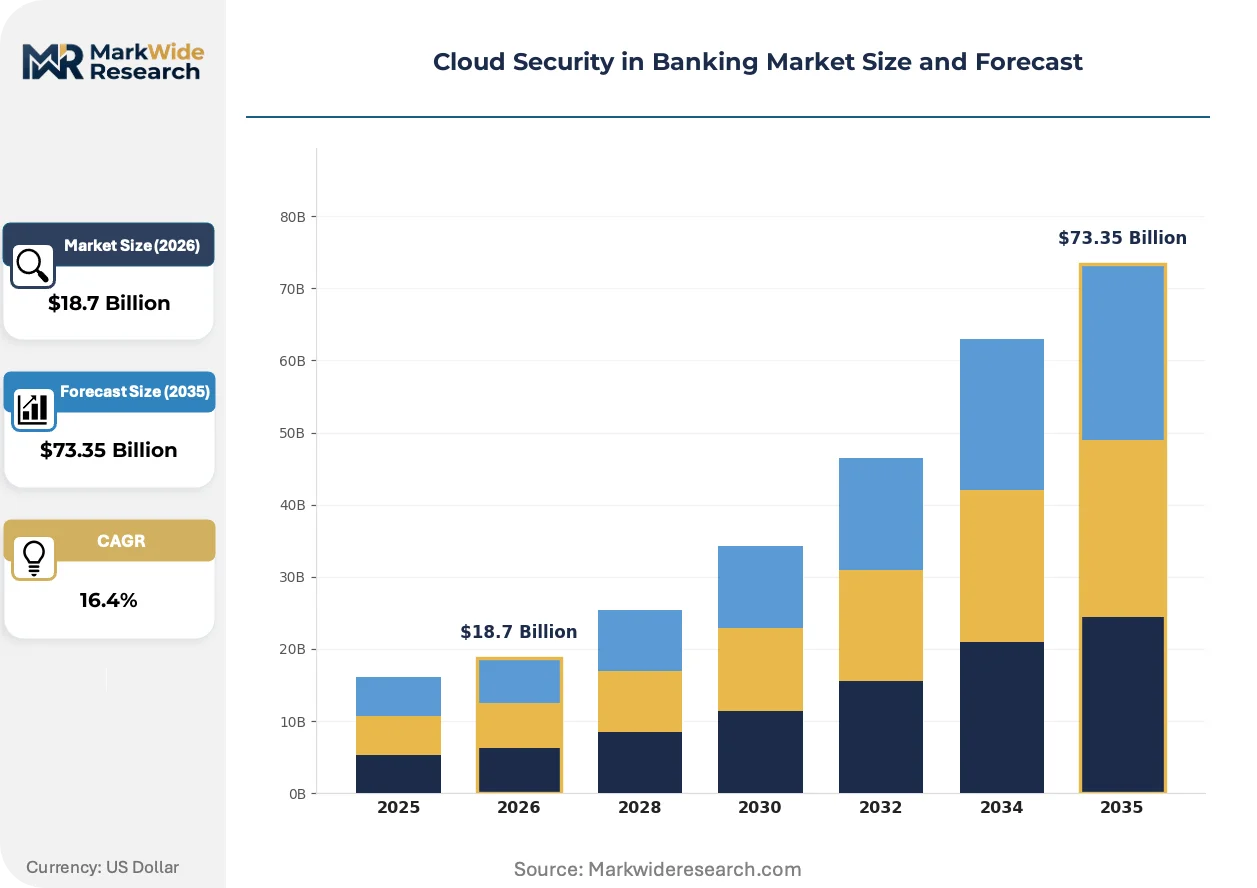
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $73.35 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Service Type: Identity Management, Data Encryption, Threat Intelligence, Compliance Management End User: Retail Banks, Investment Banks, Credit Unions, Insurance Firms Solution: Access Controls, Security Information & Event Management, Multi-Factor Authentication, Intrusion Detection Systems |
| Companies Covered | Amazon Web Services, Microsoft Azure, Google Cloud Platform, IBM Cloud Security, Oracle Cloud, Palo Alto Networks, Fortinet, Cisco, Check Point Software Technologies, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Security in Banking Market Strategic Shifts
Cloud security in banking is pivoting from perimeter defense to continuous runtime protection as containerized workloads and serverless functions displace monolithic applications, embedding security controls directly into development pipelines.
Confidential computing using hardware-based trusted execution environments is unifying data protection with processing integrity for sensitive financial analytics. Large US and European banks are deploying Intel SGX and AMD SEV technologies for anti-money laundering model training. This unifying capability eliminates the historical trade-off between computational utility and cryptographic isolation, enabling multi-party fraud detection across institutional boundaries without raw data exposure.
The EU AI Act's risk classification system for credit scoring and insurance underwriting algorithms imposes mandatory documentation, human oversight, and accuracy testing requirements. Cloud security vendors must now embed model explainability and version control into their platforms. European retail banks with automated lending decisions face the most immediate compliance deadlines and are pre-qualifying vendors based on AI governance tooling integration.
Security service edge architectures are displacing traditional hub-and-spoke network designs as distributed workforces and branchless banking models fragment access patterns. Financial institutions in the United States and United Kingdom are consolidating multiple point solutions into unified cloud-delivered platforms. This consolidation compresses vendor management overhead while improving latency for mobile banking applications serving geographically dispersed customer bases.
Cloud Security in Banking Market Segmentation
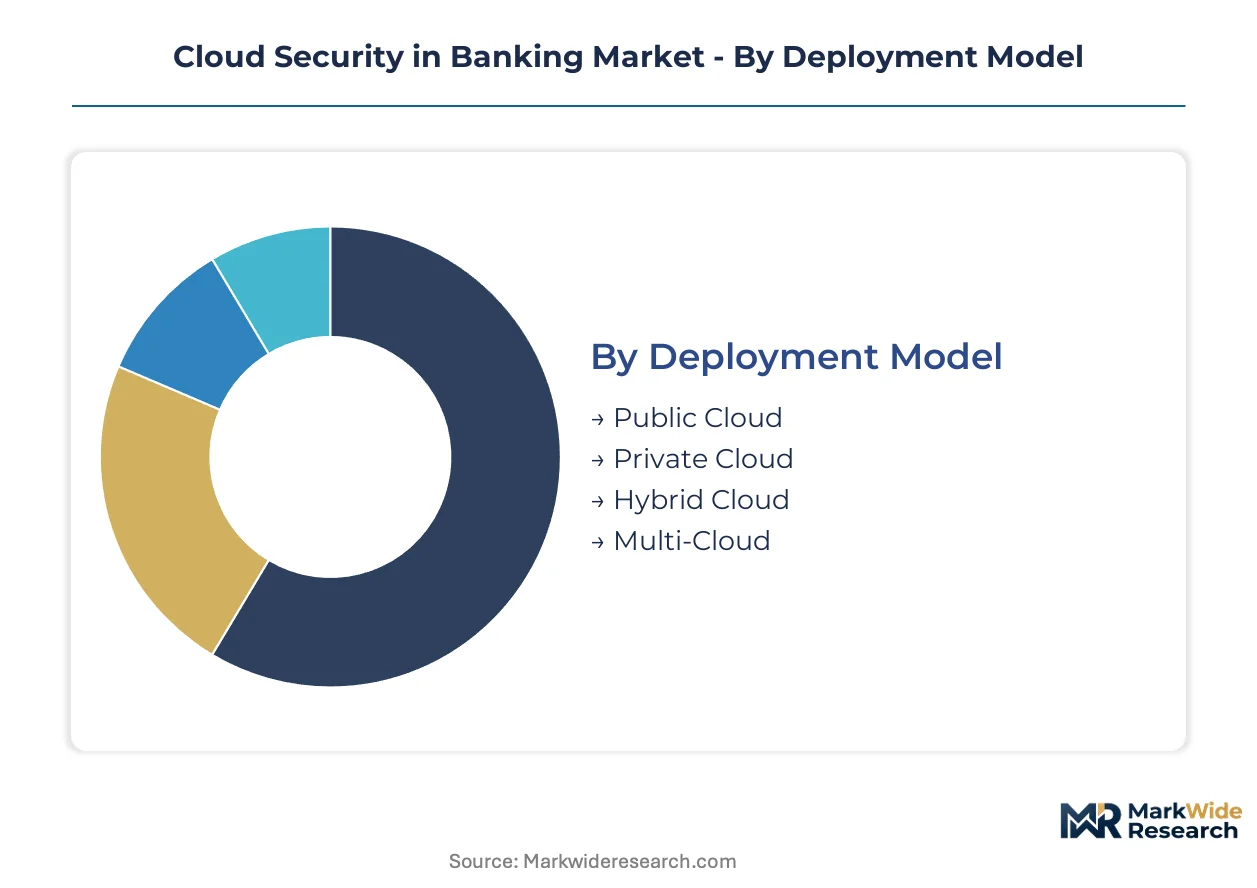
Cloud security procurement in banking diverges sharply by institutional risk tolerance, regulatory exposure, and legacy system complexity. Deployment architecture and service prioritization reflect these underlying buyer characteristics rather than uniform technology adoption curves.
Deployment Model:
Banks select cloud architectures based on data sovereignty mandates, core system age, and regulatory audit intensity rather than cost optimization alone.
- Public Cloud:Shared infrastructure delivers elastic compute for non-sensitive workloads like customer-facing mobile applications and marketing analytics. Tier-2 retail banks in the United States and United Kingdom dominate uptake here, driven by FedNow integration timelines and FCA operational resilience requirements.
- Private Cloud:Dedicated environments host core banking ledgers and payment settlement systems requiring hardware-level isolation. European institutions facing GDPR Article 32 enforcement and EBA outsourcing guidelines concentrate investment in sovereign private cloud deployments.
- Hybrid Cloud:Split architectures balance regulatory data residency with scalability demands for digital lending platforms and real-time fraud detection. This configuration attracts the largest security capital allocation as banks modernize incrementally without full core migration.
- Multi-Cloud:Distributing workloads across AWS, Azure, and Google Cloud mitigates vendor lock-in risks flagged by US federal banking regulators and Singapore's MAS. Complexity premiums for unified security orchestration limit adoption to top-tier institutions with dedicated cloud centers of excellence.
Hybrid Cloud leads volumes today; Multi-Cloud is gaining share fastest.
Service Type:
Service selection priorities track the attack surface evolution from perimeter breaches toward credential compromise and insider threats.
- Identity Management:Centralized authentication, privileged access governance, and lifecycle management for distributed workforces and third-party developers. Escalating credential-based attacks against SWIFT endpoints and banking APIs drive replacement cycles for legacy directory services.
- Data Encryption:At-rest, in-transit, and in-use cryptographic protection aligned to quantum-resistant standards. Long-duration financial instruments held by insurers and pension funds accelerate post-quantum migration timelines beyond typical IT refresh cycles.
- Threat Intelligence:External indicator feeds, dark web monitoring, and adversary attribution services tailored to financial sector threat actors.
- Compliance Management:Automated evidence collection, control mapping, and audit trail generation for multi-jurisdiction regulatory reporting.
Identity Management commands premium pricing; Compliance Management shows steepest expansion trajectory.
End User:
Institutional type determines budget scale, procurement speed, and vendor relationship depth in cloud security engagements.
- Retail Banks:High-volume transaction processing and mass-market digital channels create the broadest attack surface. Branch network consolidation and mobile-first customer acquisition in Vietnam, Indonesia, and Philippines generate outsized security investment relative to IT budget share.
- Investment Banks:Proprietary trading algorithms, M&A data rooms, and cross-border settlement systems demand confidential computing for algorithm protection. EU AI Act risk classification for automated trading decisions imposes documentation and human oversight requirements.
- Credit Unions:Member-owned structures with constrained IT staffing favor managed security service consumption over in-house platform deployment.
- Insurance Firms:Long-dated liabilities and actuarial model sensitivity drive quantum-resistant encryption priorities distinct from banking peers.
Retail Banks anchor category volumes; Investment Banks are expanding security spend most rapidly.
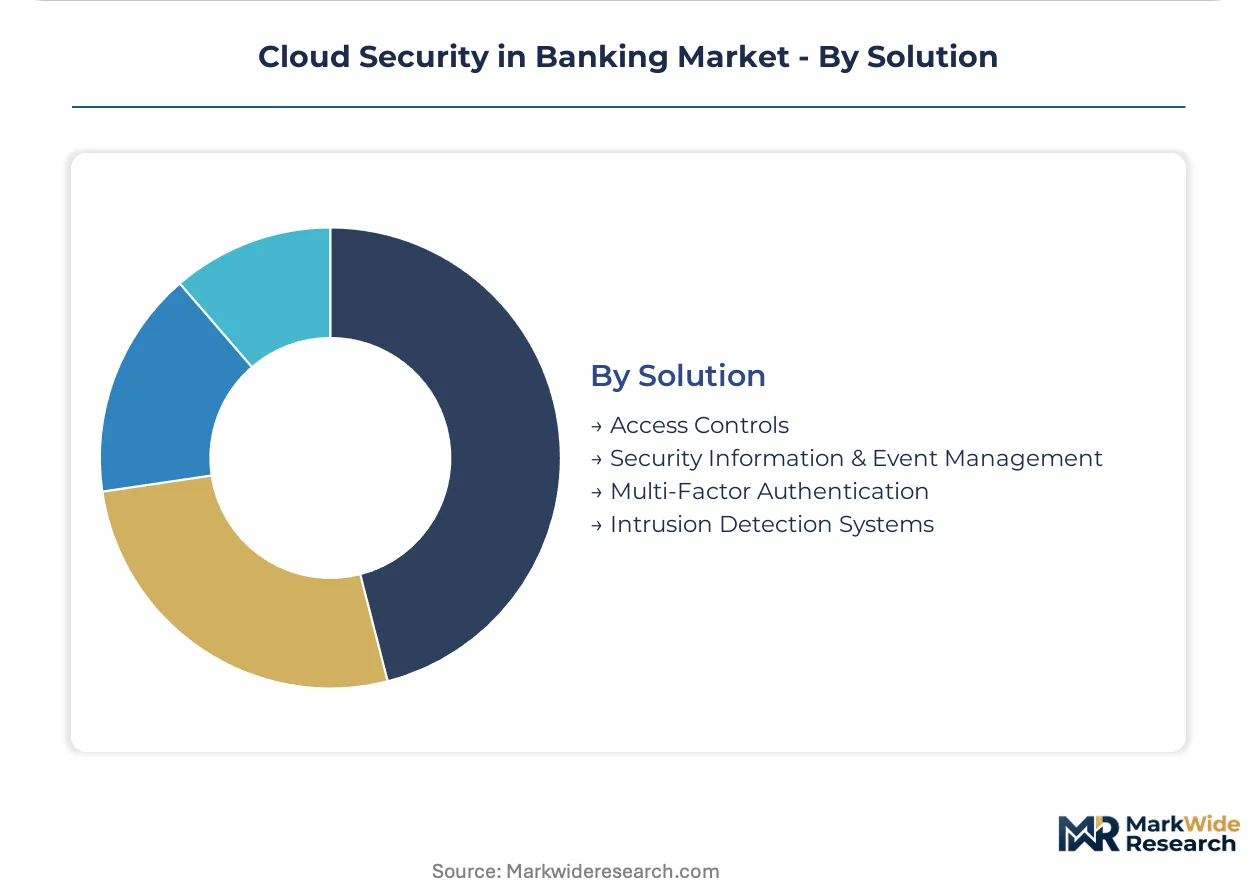
Solution:
Control deployment patterns follow the shift from perimeter defense toward runtime protection embedded in development pipelines.
- Access Controls:Role-based and attribute-based authorization frameworks enforcing least-privilege principles across cloud-native and legacy systems. Zero-trust mandates from US federal banking regulators and the EU AI Act compress procurement cycles for modernized access architectures.
- Security Information & Event Management:Real-time log aggregation, correlation, and incident response orchestration. FedNow and instant payment rails in India and Singapore generate continuous data flows requiring sub-second threat detection capabilities.
- Multi-Factor Authentication:Biometric, hardware token, and behavioral verification layers for high-risk transaction authorization.
- Intrusion Detection Systems:Network and host-based monitoring with machine learning-enhanced anomaly detection for containerized workloads.
SIEM solutions lead current deployment; Access Controls are climbing the fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial centers in New York, London, and Singapore generate concentrated demand for banking cloud security infrastructure as regulatory complexity intensifies across major jurisdictions. Sovereign data requirements and instant payment system rollouts reshape procurement priorities. Regional differentiation reflects varying maturity in digital banking adoption and enforcement stringency.
United States
FedNow integration timelines and branch network digitization drive cloud security procurement at tier-2 retail banks. The Federal Financial Institutions Examination Council mandates specific risk assessment frameworks for third-party cloud outsourcing. New York-based money center banks anchor investment in confidential computing for anti-money laundering model training.
Germany
Automated lending decisions and algorithmic trading systems face immediate EU AI Act compliance deadlines. BaFin enforcement of EBA outsourcing guidelines compels hardware-level isolation for core banking ledgers. Frankfurt's concentration of systemically important banks sustains premium demand for sovereign private cloud deployments.
Singapore
Cross-border wealth management platforms and real-time payment corridors generate continuous data flows requiring sub-second threat detection. The Monetary Authority of Singapore's Technology Risk Management Guidelines prescribe mandatory penetration testing and audit trail preservation. Marina Bay financial district institutions lead multi-cloud adoption to mitigate vendor concentration risks.
United Kingdom
Open banking API proliferation under PSD2 creates specialized demand for gateway protection and consent management tooling. The Financial Conduct Authority's operational resilience requirements compress procurement cycles for zero-trust architectures. London fintech clusters drive managed security service consumption among credit unions with constrained IT staffing.
India
UPI transaction volume expansion and digital lending platform growth outpace existing security infrastructure capacity. The Reserve Bank of India's cloud outsourcing guidelines mandate data localization and incident notification timelines. Mumbai and Bangalore financial technology corridors attract compliance-automated platform vendors targeting retail banking modernization.
Cloud Security in Banking Market Competitive Environment
Global majors compete with regional champions across compliance certification depth and sovereign cloud deployment capabilities. The vendor base organizes around three tiers: hyperscale infrastructure providers with embedded security stacks, standalone cybersecurity specialists with financial services verticalization, and managed security service providers serving mid-tier institutions. Consolidation pressures intensify as banks reduce vendor management overhead through unified platform procurement. Strategic partnerships between cloud infrastructure and security specialists displace point solution deployments.
Within the hyperscale infrastructure tier, Amazon Web Services, Microsoft Azure, and Google Cloud Platform occupy positions as default compute substrates where security functions embed natively. Palo Alto Networks and Fortinet exemplify the standalone cybersecurity specialist archetype, competing on AI-driven threat detection and networking-security convergence respectively. These five entities collectively anchor competitive dynamics as banks evaluate build-versus-partner decisions for zero-trust architecture implementation.
| Leading Market Players |
|---|
| Amazon Web Services |
| Microsoft Azure |
| Google Cloud Platform |
| IBM Cloud Security |
| Oracle Cloud |
| Palo Alto Networks |
| Fortinet |
| Cisco |
| Check Point Software Technologies |
| Others |
Value Chain & Pricing Dynamics
Private-equity-rolled-up cybersecurity specialists have consolidated fragmented cloud security tooling vendors across the United States and Israel, compressing vendor management overhead for retail banks while hardening pricing discipline through bundled platform offerings. This ownership concentration feeds directly into supply behavior as PE-backed platforms prioritize recurring revenue predictability over project-based customization, reshaping how tier-2 institutions procure zero-trust architectures.
Pricing Analysis
Input-cost pass-through from certified cloud security architects with financial services compliance experience drives pricing stratification across deployment tiers. Premium-mid-economy pricing differentiation separates FedNow-integrated retail banks requiring sub-second threat detection from credit unions consuming managed security services. Pricing pressure stems from hyperscaler embedded security stacks bundling baseline controls at marginal cost, compressing standalone vendor margins. Credit unions exhibit highest price sensitivity due to constrained IT staffing budgets, while investment banks absorb premium pricing for confidential computing deployments.
Supply Chain Analysis
Workforce availability constraints in Israel, the United States, and Ireland shape delivery capacity for AI-driven threat detection engineering and zero-trust architecture implementation. Semiconductor fabrication for trusted execution environments draws from Taiwan and South Korea, while cryptographic hardware modules source from Switzerland and Germany. Single-source vulnerability concentrates in Intel SGX and AMD SEV supply for confidential computing deployments. Distribution runs through hyperscaler marketplaces and direct enterprise sales teams serving money center banks in New York and London.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a regulatory compounder where compliance deadlines generate replacement-cycle demand. The EU AI Act's risk classification system for automated lending decisions imposes immediate vendor pre-qualification requirements across European retail banking.
For Market Incumbents: Anchor platform consolidation strategies around FedNow integration timelines and EBA outsourcing guideline enforcement. Defensive moves require embedding AI governance tooling directly into SIEM platforms to pre-empt standalone compliance vendors. Threat substitution emerges from hyperscalers bundling security controls at marginal cost, compressing pricing power for point solutions. Certification investment in quantum-resistant cryptographic standards preserves long-dated contract viability with insurers and pension funds. For New Entrants and Emerging Players: Capture white-space opportunity in Vietnam, Indonesia, and Philippines retail banking sectors where cloud security penetration lags transaction volume growth. The most penetrable segment comprises compliance-automated platforms serving mid-tier banks without dedicated cloud centers of excellence. Go-to-market angle targets managed security service consumption models that eliminate upfront capital expenditure barriers for member-owned credit unions. For Investors and Strategic Acquirers: Valuations sit cheapest among regional champions with sovereign cloud deployment capabilities and BaFin or MAS certification depth. Long-term viability across the projection horizon hinges on quantum-resistant encryption roadmap execution and AI governance tooling integration. Acquisition target archetype includes confidential computing specialists with hardware-based trusted execution environment deployments at tier-1 institutions. Signal to watch: EBA enforcement actions against banks lacking hardware-level isolation for core ledgers.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidates point solutions into unified cloud-delivered architectures for FedNow-integrated retail banks. |
| Regulatory Certification Investment | Secures BaFin and MAS pre-qualification for EU AI Act and Technology Risk Management Guidelines compliance. |
| Confidential Computing Deployment | Enables multi-party fraud detection across institutional boundaries without raw data exposure. |
| Geographic Expansion | Captures first-mover positioning in Vietnam, Indonesia, and Philippines retail banking modernization. |
| Strategic Partnership | Aligns standalone cybersecurity vendors with hyperscaler marketplaces to reduce customer acquisition friction. |
Study Parameters
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary conversations with CISOs at tier-1 retail banks, cloud security procurement officers at credit unions, FedNow integration specialists, and EBA compliance leads with secondary validation. Primary sources included CTOs at mid-tier institutions, SIEM platform engineers, and regulatory affairs directors navigating multi-jurisdiction audit requirements. Secondary data drew from FFIEC outsourcing guidance documentation, EBA outsourcing guidelines, MAS Technology Risk Management Guidelines, SEC 10-K disclosures from listed cybersecurity vendors, and hyperscaler capex allocation reports. Bottom-up deployment model sizing triangulated against top-down regulatory-driven budget estimates.
Comparable-period anchoring aligned the projection horizon against historical FedNow rollout phases, GDPR Article 32 enforcement waves, and instant payment system adoption curves across India, Singapore, and the United States. Segmentation dimensions modeled encompassed deployment architecture, service type prioritization, institutional tier, and regulatory jurisdiction cluster. CAGRs derived from vendor booking data, public sector procurement disclosures, and replacement-cycle timing across compliance mandate deadlines. Industry-specific inputs included quantum computing threat horizon assessments for long-dated financial instruments and confidential computing adoption rates at money center banks.
Underlying measurement precision varies by segment; public cloud security deployments carry tighter precision than multi-cloud orchestration due to standardized hyperscaler reporting. Forecasts reflect assumptions around regulatory enforcement intensity, talent availability for certified cloud security architects, and hyperscaler bundling strategies. Material deviation in EU AI Act implementation timelines, FedNow transaction volume trajectories, or cross-border data localization mandate expansion warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Brazil Cybersecurity Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Retail Cybersecurity Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Corporate Web Security Market