
 Patch and Remediation Software Market | 2026-2036
Patch and Remediation Software Market Size, Share, and Industry Trends Forecast 2026-2036
Patch and Remediation Software Market Outlook
Mid-sized enterprises with lean IT security teams is collapsing as the dominant buyer archetype, while government organizations with zero-trust mandates are gaining procurement share. Microsoft Corporation leverages its endpoint management ecosystem to anchor federal compliance contracts. Tanium competes through real-time vulnerability telemetry at enterprise scale. Automox specializes in cloud-native patching for distributed workforces without VPN dependency.
Patch and remediation software comprises automated systems that identify, prioritize, and deploy security updates across operating systems, applications, and network infrastructure, typically integrating with configuration management databases and vulnerability scanners to maintain asset inventories and track remediation SLAs. Its primary purpose is to compress the window between vulnerability disclosure and patch application, thereby reducing mean time to remediate. Cloud-based solutions are capturing the fastest expansion as organizations retire on-premises management servers, while vulnerability scanning commands the deepest margin pools due to continuous assessment requirements. Threat intelligence integration represents an emerging premium tier as buyers demand contextual prioritization beyond CVSS scores.
SEC cybersecurity disclosure rules, NIST SP 800-40 guidance, and FedRAMP authorization requirements collectively reshape product roadmaps by mandating auditable remediation timelines and encrypted patch distribution. The EU NIS2 Directive and Japan's METI cybersecurity framework extend these obligations across multi-jurisdictional deployments. Stakeholders must evaluate whether their vendor's compliance automation satisfies divergent regional audit standards before committing to platform consolidation strategies.
Market Dynamics
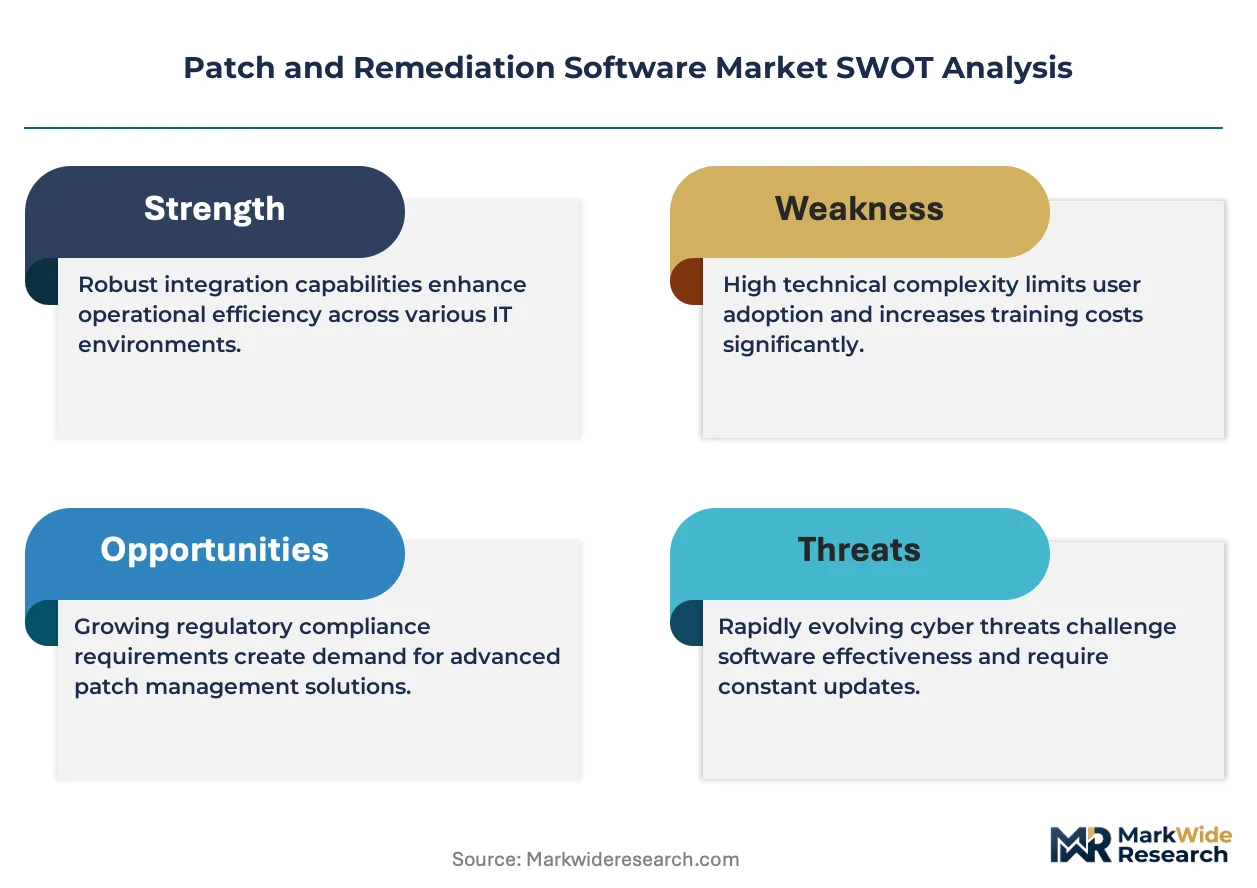
Zero-trust security mandates are compressing procurement cycles for automated patch management systems, forcing vendors to embed continuous compliance validation into core architectures rather than bolt-on modules.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Financial services institutions must document vulnerability remediation timelines, accelerating replacement of manual patching workflows with automated platforms that generate audit-ready evidence trails.
- Cloud-Native Deployment Models:Organizations retiring on-premises management servers are driving demand for agentless patching architectures that eliminate VPN dependencies for distributed workforces.
- Industrial Control Systems:Critical infrastructure operators face NERC CIP compliance deadlines, expanding the addressable market beyond traditional IT endpoints into operational technology environments.
Market Restraints
- Legacy System Inertia:Mainframe and specialized manufacturing equipment running unsupported operating systems cannot accommodate modern patching agents, creating persistent vulnerability blind spots.
- Skills Concentration:Certified vulnerability management specialists cluster in major metropolitan technology hubs, leaving secondary markets dependent on remote support with higher incident response latency.
- Input Cost Volatility:Cloud infrastructure pricing fluctuations directly impact SaaS-delivered patch management margins, compressing vendor profitability during compute cost spikes.
Strategic Opportunities
- Japan's METI Cybersecurity Framework:Mandatory security management standards for critical infrastructure operators create a regulatory tailwind for vendors with localized compliance automation.
- Threat Intelligence Convergence:Integration of exploit prediction scoring with CVSS-based prioritization enables premium pricing tiers for contextual risk assessment beyond basic vulnerability scanning.
- Healthcare IoT Expansion:Connected medical devices lacking built-in update mechanisms represent an underpenetrated segment requiring specialized firmware-over-the-air patching solutions.
Industry Challenges
- Multi-Jurisdictional Compliance Mapping:Vendors must simultaneously satisfy FedRAMP authorization requirements, EU NIS2 Directive timelines, and Japan's METI audit standards without fragmenting product roadmaps.
- Mean Time to Remediate Compression:Enterprise security teams face SLA pressure to deploy critical patches within 72 hours of disclosure, straining change management processes and testing bandwidth.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Patch and Remediation Software Market |
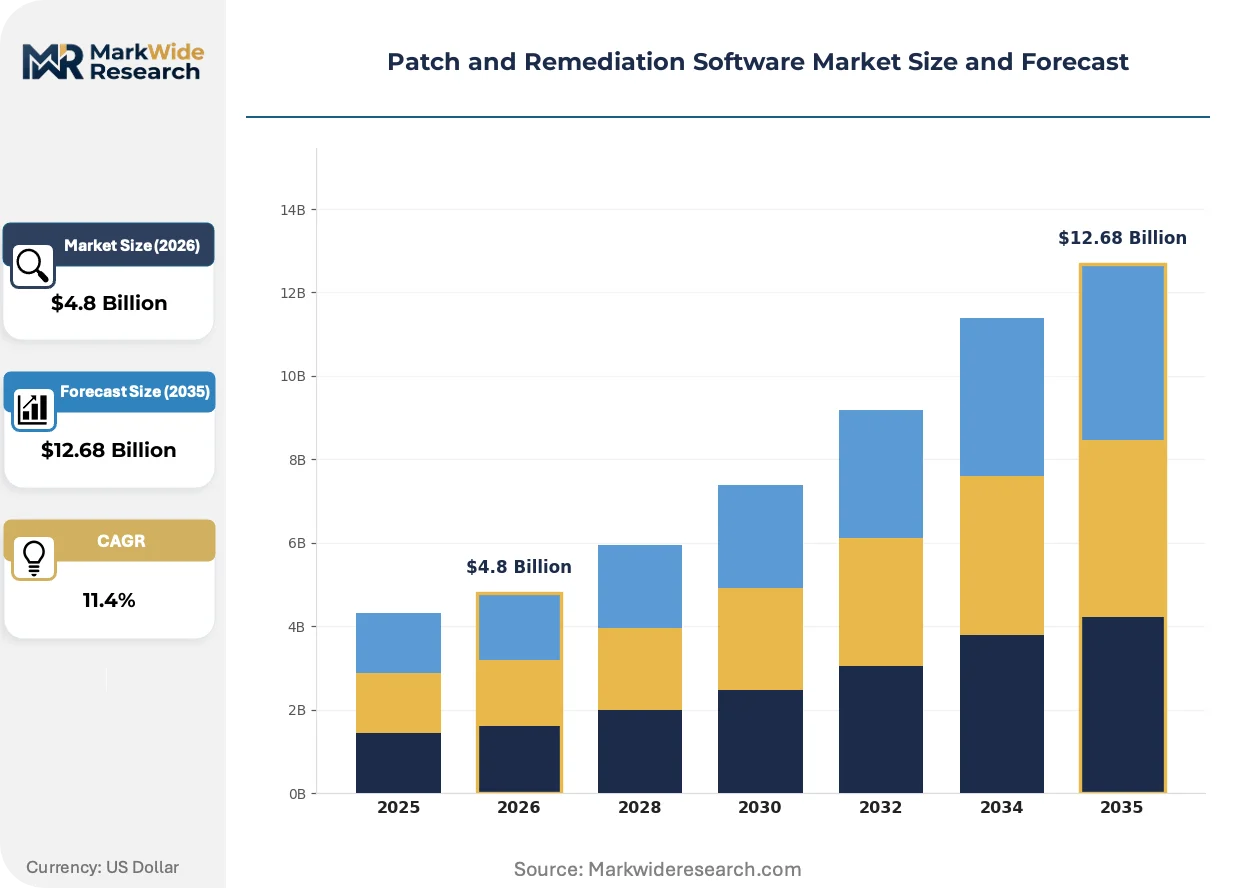
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $12.68 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: On-Premises Solutions, Cloud-Based Solutions, Hybrid Solutions, Infrastructure Management Tools End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Organizations Deployment Model: Public Cloud, Private Cloud, Managed Services, Hybrid Cloud Solution: Vulnerability Scanning, Compliance Management, Patch Management, Threat Intelligence |
| Companies Covered | Microsoft Corporation, IBM Corporation, Broadcom Inc., Ivanti, ManageEngine, Automox, NinjaOne, SolarWinds, Tanium, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Patch and Remediation Software Market Strategic Shifts
Agentless patching architectures are supplanting traditional endpoint agent models, eliminating deployment friction while enabling coverage of ephemeral cloud workloads and contractor devices.
Artificial intelligence-driven risk prioritization is supplanting static CVSS scoring in enterprise procurement evaluations. Security teams at financial institutions and healthcare systems now demand exploit prediction algorithms that incorporate threat actor activity feeds. This capability compression is forcing incumbent vendors to acquire or partner with threat intelligence providers.
The EU NIS2 Directive mandates incident reporting timelines and supply chain security obligations for essential and important entities. Managed security service providers are embedding automated patch compliance into bundled offerings to satisfy these requirements. German critical infrastructure operators represent the most affected segment, with procurement specifications now requiring encrypted patch distribution and immutable audit logs.
Consumption patterns are shifting from perpetual licensing toward usage-based pricing tied to endpoint count and scan frequency. Mid-sized enterprises with variable workforce sizes prefer this model over fixed annual commitments. This transition is most visible in North American technology and professional services verticals where headcount fluctuates seasonally.
Patch and Remediation Software Market Segmentation
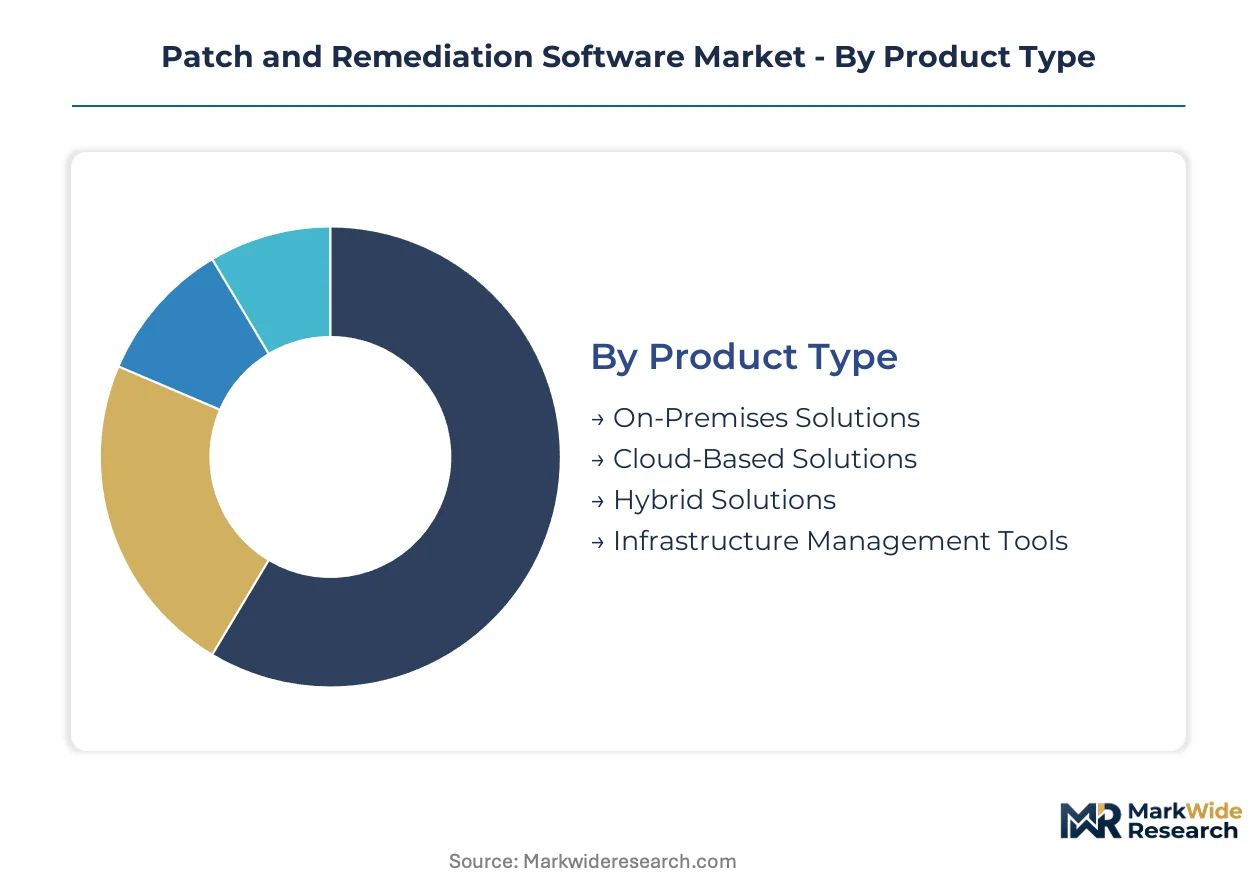
Patch and remediation software vendors configure product architectures around deployment constraints, buyer scale, and compliance complexity. Segmentation reveals where cloud-native delivery outpaces legacy on-premises installations and which buyer categories drive premium pricing for integrated threat intelligence.
Product Type:
Cloud-based solutions dominate cross-border deployments, while on-premises installations cluster in regulated domestic markets with data sovereignty requirements.
- On-Premises Solutions:Deployed within customer data centers with direct control over patch distribution infrastructure. German critical infrastructure operators and Japanese financial institutions favor these configurations to satisfy METI and domestic banking regulator audit requirements for data localization.
- Cloud-Based Solutions:Delivered through SaaS architectures with agentless endpoint coverage. US technology firms and distributed workforces across North America drive demand for VPN-independent patching that scales across ephemeral cloud workloads without persistent infrastructure.
- Hybrid Solutions:Blend on-premises control planes with cloud-delivered intelligence feeds. Organizations with mixed legacy-modern infrastructure in France and the UK deploy these to bridge operational technology and IT environments.
- Infrastructure Management Tools:Embed patching within broader configuration management platforms. Italian and Spanish mid-market enterprises adopt these for consolidated vendor relationships and unified asset visibility.
On-premises solutions command the established base. The steepest expansion runs through cloud-based delivery models.
End User:
Buyer scale determines pricing tier access and solution complexity, with government procurement introducing specialized compliance automation requirements.
- Small Enterprises:Deploy lightweight SaaS patching with minimal customization. US professional services firms and German Mittelstand manufacturers select these for rapid deployment without dedicated security operations centers.
- Medium Enterprises:Balance cost constraints with multi-platform coverage needs. Healthcare systems across France, Italy, and Japan represent concentrated demand as these organizations face HIPAA, GDPR, and METI framework obligations simultaneously.
- Large Enterprises:Require enterprise-wide orchestration across tens of thousands of endpoints. US financial institutions under SEC cybersecurity disclosure rules and EU banks subject to NIS2 Directive timelines drive the deepest investment in automated remediation workflows.
- Government Organizations:Mandate FedRAMP authorization, encrypted distribution, and immutable audit trails. Federal agencies in the US, German critical infrastructure operators, and Japanese government entities represent procurement pools with extended sales cycles but substantial contract values.
Large enterprises anchor current revenue concentration. Government organizations are gaining share fastest as zero-trust mandates accelerate replacement cycles.
Deployment Model:
Architecture choice reflects data sensitivity, workforce distribution, and existing cloud provider relationships.
- Public Cloud:Leverages hyperscaler infrastructure for elastic compute during patch campaigns. US and Canadian technology companies with seasonal workforce fluctuations prefer usage-based scaling over fixed capacity commitments.
- Private Cloud:Maintains isolated environments for regulated workloads. Swiss banking consortiums and German automotive suppliers deploy these to satisfy national financial regulator and industry-specific cybersecurity standards.
- Managed Services:Outsources patch operations to specialized security providers. UK and Australian organizations with lean internal IT teams contract these to satisfy insurer requirements for documented remediation SLAs.
- Hybrid Cloud:Distributes workloads across public and private boundaries based on asset classification. French and Italian enterprises with legacy mainframe dependencies use these to modernize gradually without full infrastructure replacement.
Public cloud deployments hold the volume base. Managed services are climbing the fastest as skills shortages persist in secondary markets.
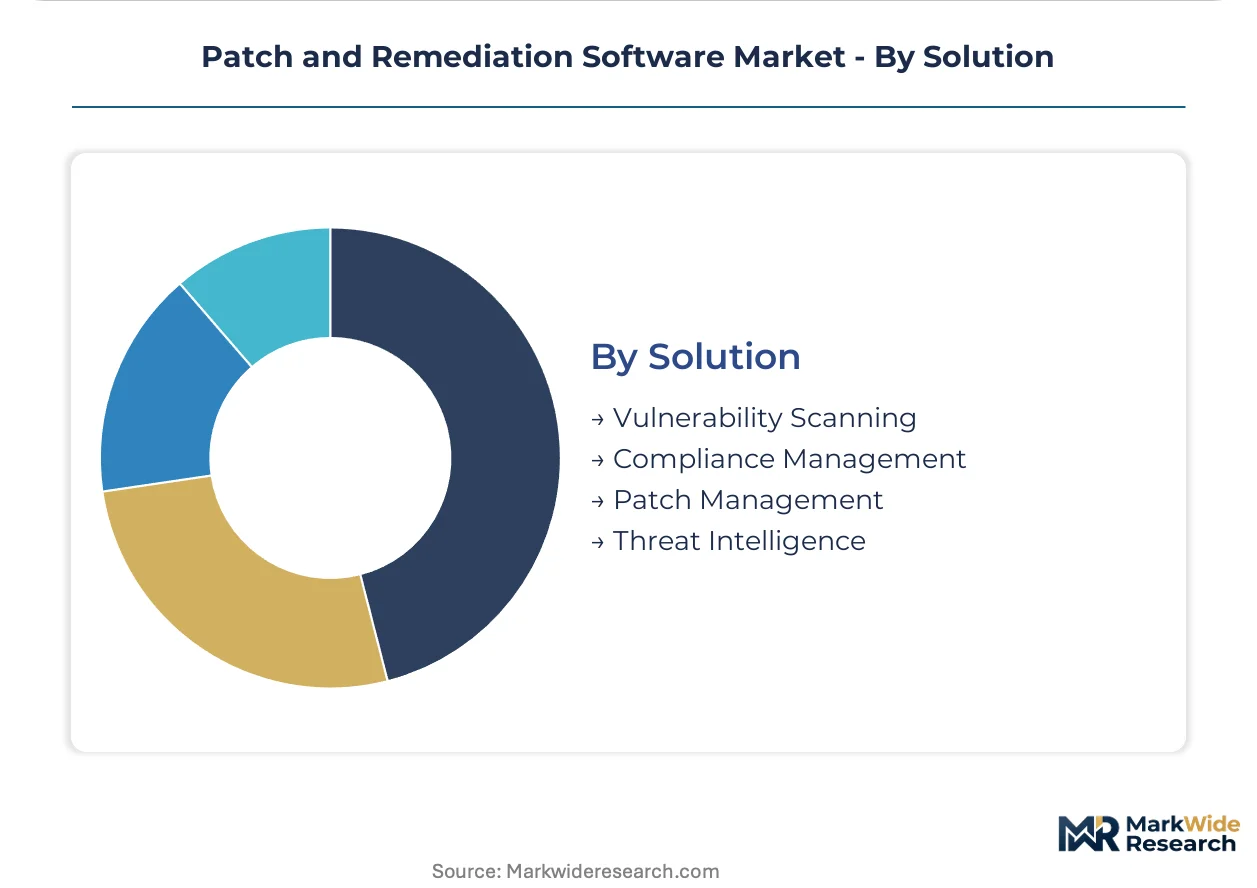
Solution:
Functional modules differentiate on integration depth, with buyers increasingly demanding unified platforms over point tools.
- Vulnerability Scanning:Continuous asset discovery and CVSS-based risk scoring form the foundational layer. US healthcare systems and German manufacturing operations deploy these for baseline visibility before patch prioritization.
- Compliance Management:Automates evidence collection for regulatory audits across multiple frameworks. Financial services institutions in the US, UK, and Japan integrate these to satisfy SEC, FCA, and FSA disclosure requirements with reduced manual documentation.
- Patch Management:Orchestrates deployment workflows with rollback capabilities and change management integration. Mid-sized enterprises across Spain, Italy, and Canada select these as core modules before expanding to adjacent capabilities.
- Threat Intelligence:Contextualizes vulnerability severity with exploit prediction and actor attribution. Premium buyers at US defense contractors and Japanese critical infrastructure operators pay elevated pricing for contextual prioritization beyond static scoring.
Patch management retains the installed base. Threat intelligence is gaining share fastest as exploit prediction algorithms displace CVSS-only approaches.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Patch and remediation software development concentrates in the United States, with hyperscaler infrastructure and venture capital flows sustaining innovation velocity. Vendor headquarters cluster in Seattle, Boston, and Silicon Valley corridors. Regulatory divergence across jurisdictions forces multi-framework engineering investments.
United States
Financial services institutions and federal agencies drive procurement volume. SEC cybersecurity disclosure rules mandate auditable remediation timelines, compressing sales cycles for automated platforms. The Washington DC-Baltimore corridor anchors federal compliance contracting, while New York-based banks prioritize threat intelligence integration.
Germany
Critical infrastructure operators and automotive suppliers constitute the core demand base. The EU NIS2 Directive and national banking regulator standards require encrypted patch distribution with immutable audit trails. Munich and Stuttgart industrial clusters deploy hybrid architectures bridging operational technology and IT environments.
Japan
Government entities and manufacturing conglomerates lead adoption. METI cybersecurity framework mandates for critical infrastructure create procurement specifications favoring localized compliance automation. Tokyo and Osaka metropolitan areas concentrate enterprise security operations centers with zero-trust transformation mandates.
United Kingdom
Managed security service providers and mid-market enterprises represent growth segments. FCA disclosure requirements for financial institutions parallel SEC rules, driving automated evidence collection demand. London's technology corridor and Manchester's professional services cluster favor usage-based pricing models for variable workforce sizes.
Canada
Healthcare systems and energy operators anchor public sector procurement. Health Canada and provincial privacy commissioners enforce breach notification timelines, accelerating vulnerability scanning investments. Toronto and Calgary technology corridors concentrate SaaS-native vendor relationships for cross-border workforce coverage.
Patch and Remediation Software Market Competitive Environment
Concentration sits with diversified technology conglomerates and specialized endpoint security vendors. The market structure reflects tiered competition between platform ecosystems and best-of-breed automation specialists. Three archetypes dominate: hyperscaler-integrated suites, real-time telemetry specialists, and cloud-native disruptors. Competitive moves center on threat intelligence partnerships and FedRAMP authorization acquisitions.
Within the hyperscaler-integrated tier, Microsoft Corporation exemplifies platform leverage through endpoint management ecosystem anchoring. Tanium occupies a position among real-time telemetry specialists serving enterprise-scale federal contracts. Automox represents the cloud-native disruptor archetype, targeting distributed workforces without VPN dependencies. These three companies illustrate divergent architectural bets on agent versus agentless deployment models.
| Leading Market Players |
|---|
| Microsoft Corporation |
| IBM Corporation |
| Broadcom Inc. |
| Ivanti |
| ManageEngine |
| Automox |
| NinjaOne |
| SolarWinds |
| Tanium |
| Others |
Value Chain & Pricing Dynamics
Agentless architectures displacing legacy endpoint agents simultaneously redistribute development talent toward Seattle and Boston corridors while compressing SaaS delivery costs below on-premises maintenance thresholds. This substitution dynamic concentrates pricing power with cloud-native vendors and fragments margin pools for traditional perpetual-license providers.
Pricing Analysis
Volume-discount tiering structures dominate procurement negotiations, with enterprise buyers securing per-endpoint rates below mid-market thresholds by committing to multi-year SaaS contracts. Pricing stratifies across premium threat-intelligence tiers, standard automated patching modules, and economy vulnerability-scanning baselines. Cost compression in the economy tier is intensifying because hyperscaler infrastructure pricing directly impacts SaaS margins. Government organizations exhibit the lowest price sensitivity due to FedRAMP authorization requirements, while small professional services firms drive hardest bargain hunting.
Supply Chain Analysis
Just-in-time feature deployment preferences among agile development teams contrast with strategic stockpiling of compliance documentation by federal contractors preparing for audit cycles. Development talent concentrates in the United States, Ireland, and Israel. Cloud infrastructure provisioning rests on hyperscaler data center networks, open-source vulnerability databases, and threat intelligence feed partnerships. Single-source vulnerability in NVD (National Vulnerability Database) latency creates systemic exposure windows. Distribution runs through direct enterprise sales teams and managed security service provider channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Patch and remediation software sits in early-cycle expansion as SEC disclosure rules and EU NIS2 mandates convert manual workflows into automated platform procurement across financial services and critical infrastructure.
For Market Incumbents: Secure FedRAMP authorization expansions to anchor federal compliance contracts against emerging cloud-native challengers. Deepen threat intelligence partnerships to embed exploit prediction scoring before CVSS-only approaches commoditize baseline scanning modules. Prioritize encrypted patch distribution capabilities for German critical infrastructure and Japanese METI framework compliance. For New Entrants and Emerging Players: FedRAMP authorization fast-tracks open procurement pathways into US federal agencies with extended sales cycles but substantial contract values. Healthcare IoT firmware-over-the-air patching represents the most penetrable white space, with connected medical devices lacking built-in update mechanisms. Position through managed service provider partnerships to bypass direct enterprise sales infrastructure requirements. For Investors and Strategic Acquirers: The market sits at a regulatory-acceleration phase that favors specialized compliance automation over generic endpoint management. Long-term viability hinges on multi-jurisdictional framework coverage spanning SEC, NIS2, and METI requirements. Acquisition targets should demonstrate threat intelligence integration depth. Watch cloud infrastructure pricing volatility as the signal indicating SaaS margin compression thresholds.| Strategic Initiative | Industry Significance |
|---|---|
| Threat Intelligence Partnership | Exploit prediction scoring enables premium pricing tiers beyond CVSS-only vulnerability assessment. |
| FedRAMP Authorization Acquisition | Federal compliance contracting anchors multi-year revenue streams with immutable audit trail requirements. |
| Agentless Architecture Launch | VPN-independent patching captures distributed workforce demand across North American technology verticals. |
| Healthcare IoT Module Development | Firmware-over-the-air patching addresses underpenetrated medical device segment lacking built-in update mechanisms. |
| METI Framework Localization | Japanese critical infrastructure operators mandate localized compliance automation with encrypted distribution standards. |
Study Parameters
Operator-level perspectives from CISOs, IT procurement officers, vulnerability management specialists, and managed security service provider architects anchored the qualitative base. Primary interviews combined with secondary validation against SEC disclosure filings, FedRAMP authorization databases, EU NIS2 implementation guidance, and Japanese METI framework documentation. Bottom-up endpoint count modeling and top-down security software spending analysis provided triangulation across the analysis window.
Sensitivity analysis tested deployment model adoption curves, cloud infrastructure pricing scenarios, and regulatory timeline compressions across the projection horizon. Segmentation dimensions modeled include deployment architecture, organization scale, vertical industry, compliance complexity tier, and regional regulatory cluster. CAGRs derived from endpoint growth trajectories and pricing tier mix shifts. Threat intelligence integration penetration and agentless architecture adoption served as industry-specific forecast inputs.
Decision-makers should treat outputs as directional under assumptions of sustained regulatory enforcement intensity and hyperscaler infrastructure availability; material deviation would warrant model refresh. Revision becomes warranted when cloud infrastructure pricing volatility or multi-jurisdictional compliance fragmentation crosses thresholds that alter vendor margin structures or procurement cycle lengths.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market
Security Software
Decentralized Identity Software Market
Security Software
Mobile Security Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
Global Digital Identity Solutions Market
Security Software
Asia Pacific Anti Money Laundering Solutions Market
Security Software
Secure Digital Card Market
Security Software
Global Secure Mobile Communications Software Market
Security Software
E Passport Market
Security Software
Security Software Market
Security Software
Global Security Operation Center As a Service Market
Security Software
Quantum Key Distribution System Market
Security Software
IAM Security Services Market
Security Software
Door Phone Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Japan Mobile Biometrics Market