
 Global Privileged Access Management (PAM) Solutions Market | 2026-2036
Global Privileged Access Management (PAM) Solutions Market Size, Share, and Industry Trends Forecast 2026-2036
Global Privileged Access Management (PAM) Solutions Market Foresight
Modular bundling of vaulting with session management and threat analytics is restructuring how enterprises evaluate PAM procurement, shifting purchasing from point solutions toward integrated platforms. CyberArk leverages its technology leadership in credential vaulting to anchor premium deployments across financial and energy sectors. BeyondTrust competes through specialized remote access controls that dominate industrial operational technology environments. Wallix extends its footprint with streamlined virtual appliance configurations designed for mid-market European manufacturing and public sector buyers.
Privileged Access Management (PAM) Solutions encompass software systems that discover, secure, manage, and monitor accounts with elevated permissions across IT infrastructure, typically enforcing session recording, credential rotation, and least-privilege access through policy engines integrated with directory services. These systems serve the primary commercial purpose of preventing credential theft, insider threats, and lateral movement by attackers who exploit standing administrative access. Deployment mode segmentation shows cloud and SaaS configurations capturing accelerated growth as organizations retire on-premises identity stacks, while hybrid architectures sustain substantial share among regulated entities requiring data residency controls. End-user concentration tilts toward financial institutions and energy operators, where compromise of privileged credentials carries systemic risk and regulatory penalties.
ISO 27001, NIST SP 800-207 zero-trust architecture guidelines, and the EU NIS2 Directive collectively shape product standards and procurement specifications across the addressable market, with HIPAA and SEC cybersecurity disclosure rules adding sector-specific compliance pressure in the United States. SAMR and GB standards in China, alongside Japan's METI cybersecurity framework, create additional certification requirements for vendors seeking access across Asia-Pacific public sector tenders. Stakeholders must monitor how convergence between PAM and identity governance platforms reshapes competitive boundaries and whether just-in-time access automation displaces traditional vaulting-centric architectures.
Market Dynamics
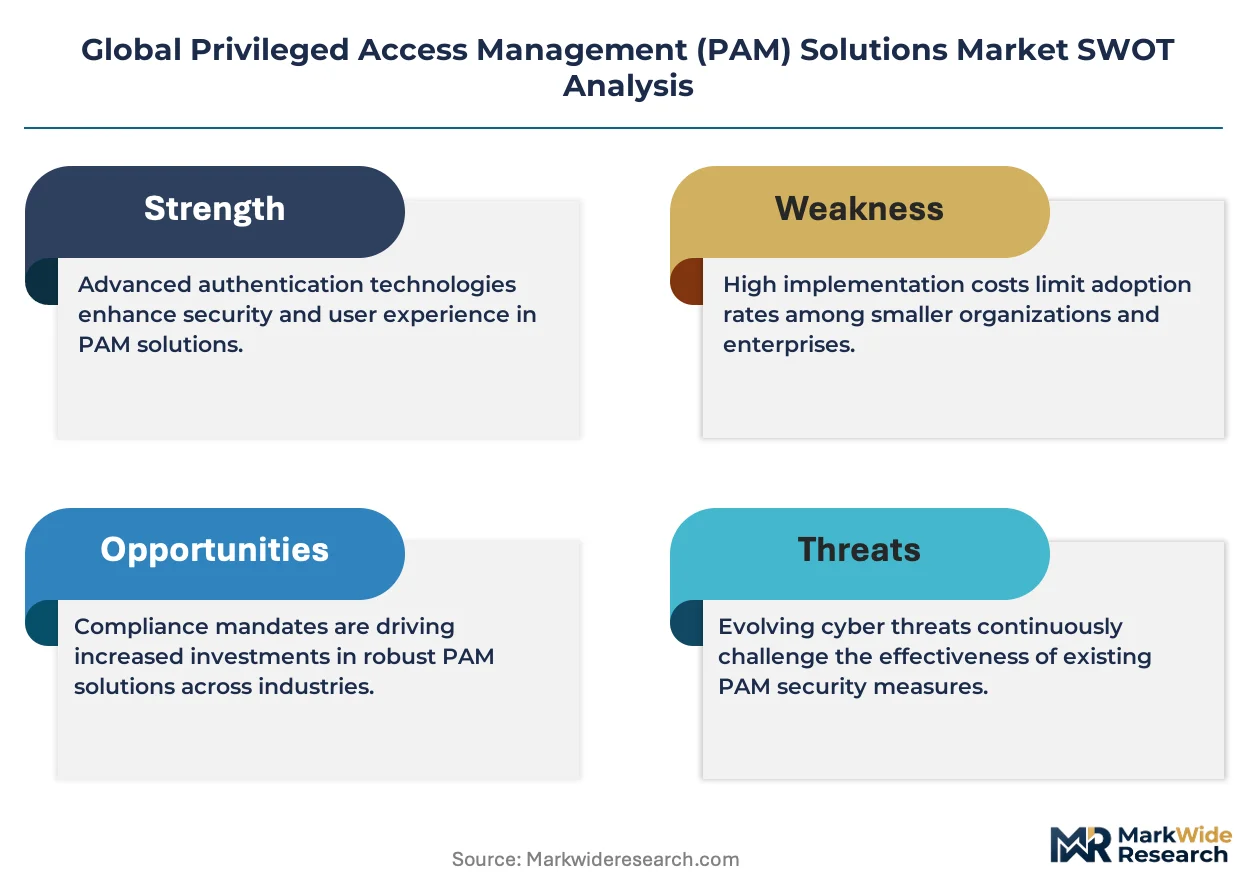
Zero-trust architecture mandates from federal agencies and the EU NIS2 Directive are compressing deployment timelines, forcing organizations to retire legacy vaulting systems in favor of just-in-time access automation with continuous session monitoring.
Growth Catalysts
- EU NIS2 Directive:Mandatory privileged session monitoring and just-in-time access controls are compelling European financial institutions and energy operators to accelerate PAM procurement cycles.
- Cloud migration:Organizations retiring on-premises identity stacks are adopting SaaS-configured PAM platforms to reduce operational overhead and enable elastic scaling.
- Credential-based attacks:Rising sophistication of lateral movement techniques is driving demand for credential vaulting with automated rotation across critical infrastructure sectors.
Market Restraints
- Implementation complexity:Integration with legacy directory services and custom authentication protocols extends deployment timelines by 6-18 months for regulated enterprises.
- Skill scarcity:Shortage of identity security architects with PAM-specific expertise inflates professional services costs and constrains vendor delivery capacity.
- Data residency requirements:Hybrid architectures persist among financial institutions in Germany and Switzerland due to strict national data localization laws.
Strategic Opportunities
- Operational technology convergence:Industrial control systems in manufacturing and energy present underpenetrated attack surfaces requiring specialized remote access controls.
- Mid-market expansion:Streamlined virtual appliance configurations are opening procurement pathways for European manufacturing and public sector buyers with limited security budgets.
- Identity governance integration:Convergence between PAM and IGA platforms creates white space for unified policy engines that span privileged and standard identity lifecycle management.
Industry Challenges
- Legacy system interoperability:Mainframe environments and proprietary industrial protocols resist standard API-based integration, forcing custom connector development.
- Insider threat detection:Behavioral analytics engines generate false positive rates exceeding 40% in high-velocity trading environments, eroding security team trust.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Privileged Access Management (PAM) Solutions Market |
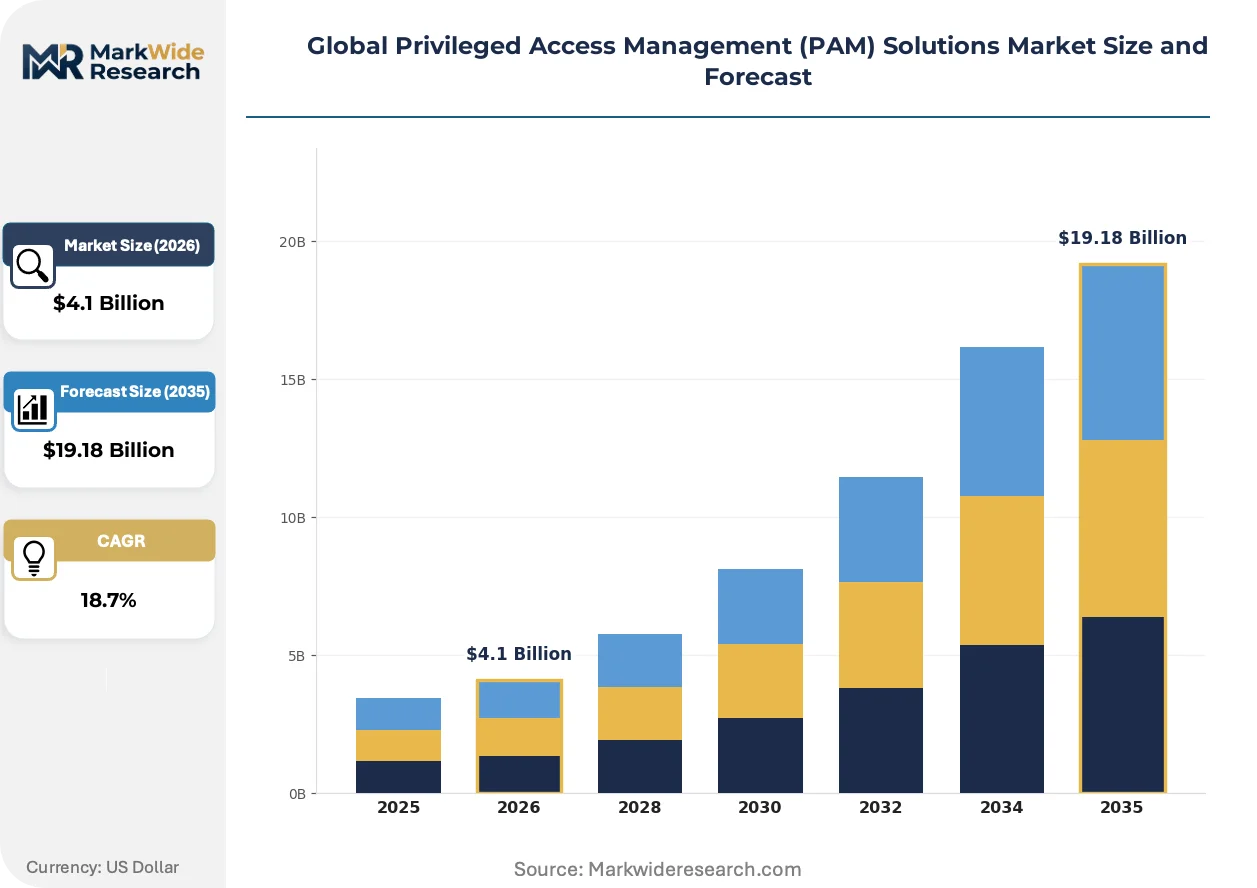
| Market Size in 2026 | $4.1 Billion |
| Market Size in 2035 | $19.18 Billion |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Vaulting, Session Management, Password Management, Access Control, Analytics Deployment Mode: Cloud, On-Premises, Hybrid, Virtual Appliance, SaaS End User: Government Agencies, Financial Institutions, Telecommunication Providers, Energy Operators, Education Institutions Application: Identity Governance, Threat Detection, Regulatory Compliance, Operational Efficiency, Risk Mitigation |
| Companies Covered | CyberArk, Fortinet, Broadcom, BeyondTrust, Delinea, ManageEngine, ARCON, Wallix, One Identity, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Privileged Access Management (PAM) Solutions Market Shifts & Advancements
Artificial intelligence and machine learning capabilities are absorbing privileged access workflows, while regulatory fragmentation across jurisdictions accelerates product roadmap complexity for multinational vendors.
Just-in-time access automation is absorbing traditional vaulting-centric architectures by provisioning ephemeral credentials that expire after single sessions. Financial services firms in the United States are deploying these capabilities at the fastest pace, compressing standing administrative access from permanent assignments to time-bound, approval-gated permissions. This shift is absorbing legacy privileged account inventory management by eliminating persistent credentials that attackers target for lateral movement.
The EU NIS2 Directive mandates privileged session monitoring with automated anomaly detection for critical infrastructure operators. Industrial consequence includes mandatory breach notification timelines of 24-72 hours and supply chain security audits extending to third-party privileged access. Energy operators in Germany and France are responding by consolidating fragmented point solutions into integrated platforms with unified audit trails.
Security procurement teams are compressing vendor evaluation cycles from 12-18 months to 90-120 days through pre-certified solution shortlists aligned with ISO 27001 and NIST SP 800-207. Managed security service providers are displacing direct enterprise licensing in mid-market segments. This pattern is most visible in United Kingdom healthcare and United States municipal government verticals where internal security engineering capacity remains constrained.
Global Privileged Access Management (PAM) Solutions Market Segmentation
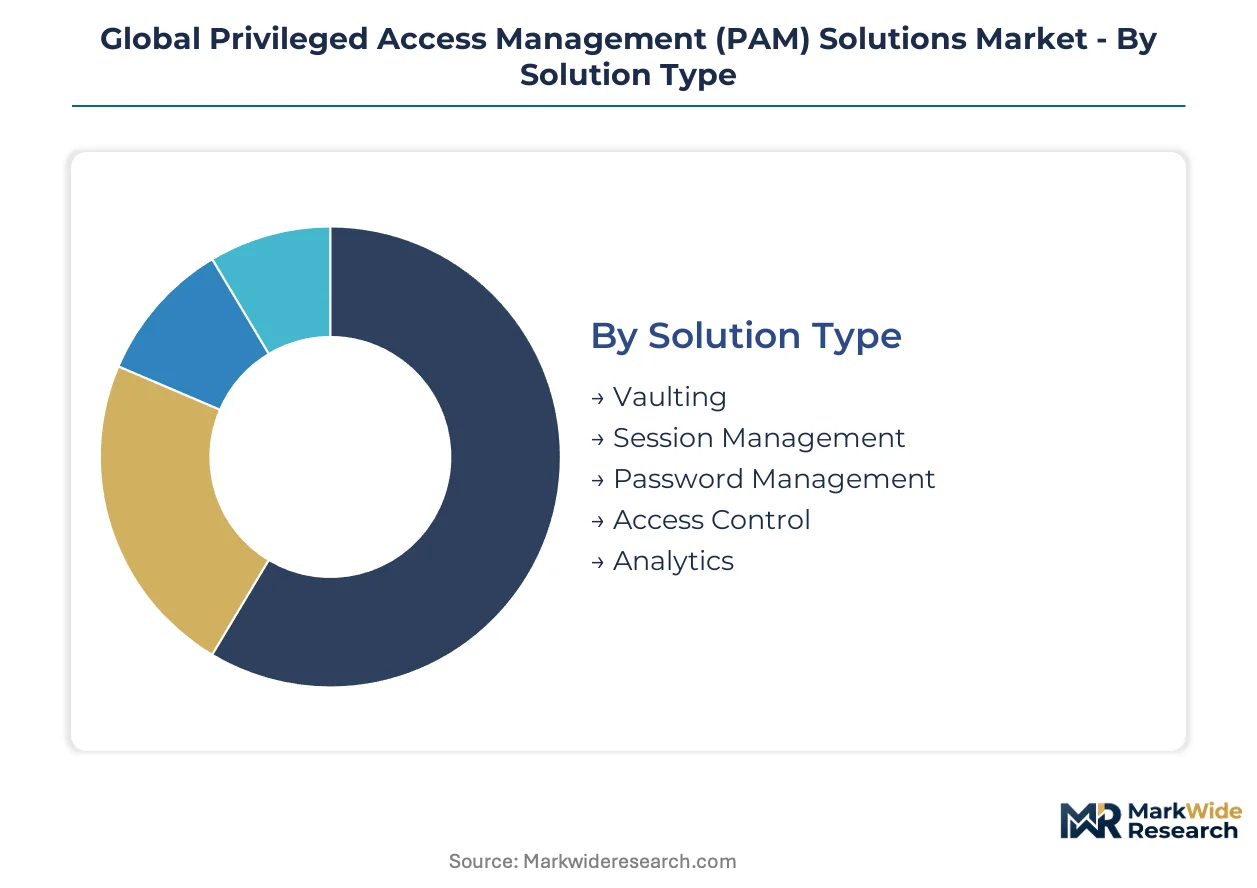
Privileged Access Management procurement patterns diverge sharply between organizations seeking standalone security tools and those embedding controls within broader identity architectures. Understanding these integration pathways reveals where vendors capture premium pricing versus commodity volume.
Solution Type:
Standalone vaulting platforms dominate enterprise deployments, while embedded analytics modules gain traction within converged security stacks.
- Vaulting:Centralized credential repositories with automated rotation and encryption-at-rest protect against credential theft in financial trading environments. Demand concentrates among United States federal agencies implementing zero-trust mandates, where FERC and SEC cybersecurity disclosure rules compel hardened secret management.
- Session Management:Real-time monitoring and recording of privileged sessions enables forensic reconstruction of insider actions or lateral movement attempts. German energy operators under EU NIS2 Directive pressure deploy these capabilities to satisfy mandatory breach notification timelines of 24-72 hours.
- Password Management:Enterprise password vaults with policy enforcement reduce credential sprawl across mid-market organizations.
- Access Control:Policy engines governing elevation requests and time-bound permissions enforce least-privilege principles.
- Analytics:Behavioral analysis engines detecting anomalous privilege usage patterns increasingly ship as embedded modules within broader platforms.
Volume placements concentrate in Vaulting; the faster expansion belongs to Session Management.
Deployment Mode:
Cost tiering separates premium managed services from self-operated infrastructure, with compliance requirements dictating hybrid persistence.
- Cloud:Elastic PAM infrastructure delivered through hyperscaler marketplaces eliminates capital expenditure for mid-market buyers. United Kingdom healthcare trusts and United States municipal governments favor this model where internal security engineering capacity remains constrained.
- SaaS:Fully managed tenant architectures with vendor-operated patching and scaling absorb fastest growth as organizations retire on-premises identity stacks. Japanese financial institutions under METI cybersecurity framework guidelines adopt these configurations to reduce operational overhead.
- On-Premises:Air-gapped deployments persist in defense and intelligence environments with classified data handling requirements.
- Hybrid:Split architectures maintaining sensitive credentials on-premises while pushing session brokers to cloud satisfy German and Swiss data localization laws.
- Virtual Appliance:Pre-configured software images streamline deployment for European manufacturing buyers with limited security budgets.
On-Premises retains the largest installed base; SaaS configurations are climbing the fastest.
End User:
Application context determines whether PAM investments target insider threat prevention or external attack surface reduction.
- Financial Institutions:Trading platforms and core banking systems require sub-second credential injection with comprehensive audit trails. United States banks face dual pressure from SEC cybersecurity disclosure rules and HIPAA enforcement for healthcare payment processing arms.
- Energy Operators:Industrial control systems and SCADA environments demand specialized remote access controls isolating OT from IT networks. French and German operators consolidate fragmented point solutions into integrated platforms with unified audit trails under EU NIS2 Directive mandates.
- Government Agencies:Federal zero-trust architecture mandates accelerate vaulting and analytics procurement across civilian and defense departments.
- Telecommunication Providers:Network infrastructure management requires privileged access controls spanning multi-vendor equipment stacks.
- Education Institutions:Research computing environments with federated identity needs drive demand for scalable session management.
Financial Institutions anchor current spending; Energy Operators show the steepest expansion trajectory.
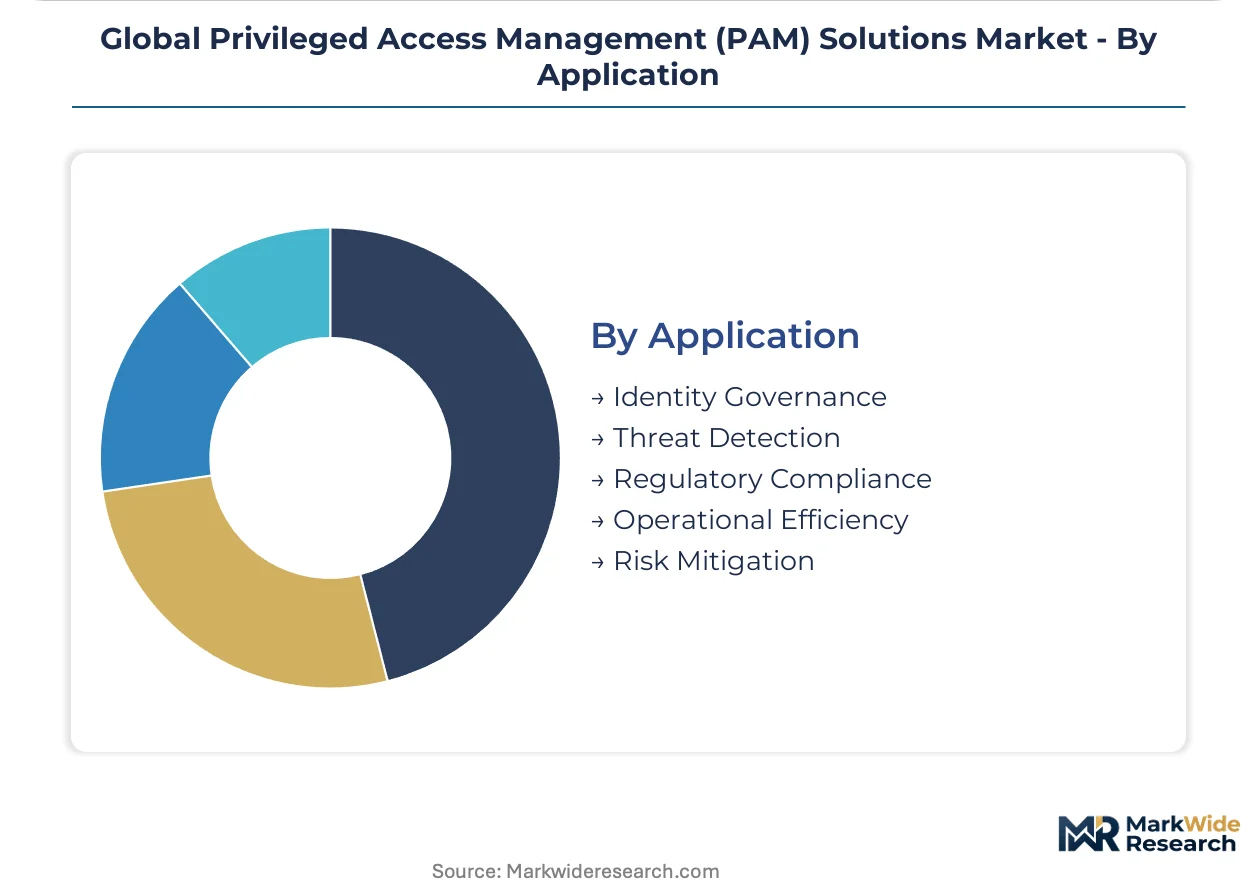
Application:
Maturity stages separate compliance-driven baseline deployments from advanced automation use cases.
- Regulatory Compliance:Audit logging, policy enforcement, and attestation workflows satisfy ISO 27001, NIST SP 800-207, and sector-specific mandates. This application category captures foundational spending across all regulated verticals.
- Threat Detection:Behavioral analytics and anomaly identification represent advanced deployments requiring mature security operations capabilities.
- Identity Governance:Lifecycle management integration with HR systems and directory services automates provisioning and deprovisioning workflows.
- Risk Mitigation:Quantitative risk scoring of privileged access exposure supports board-level cybersecurity reporting.
- Operational Efficiency:Automated credential rotation and session brokering reduce helpdesk burden and manual administrative overhead.
Regulatory Compliance drives baseline adoption; Threat Detection is gaining share fastest among mature security programs.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Production of PAM solutions concentrates in the United States and Israel, while consumption spreads across financial centers and critical infrastructure hubs in Europe and Asia-Pacific. The regulatory fragmentation across jurisdictions forces vendors to maintain multiple compliance certifications. Enterprise procurement cycles vary dramatically by region, with federal mandates compressing timelines in North America.
United States
Financial institutions in New York and Chicago drive vaulting demand for trading platforms, while federal agencies accelerate zero-trust deployments. SEC cybersecurity disclosure rules and HIPAA enforcement create dual compliance pressure for healthcare payment processors. Silicon Valley vendors anchor the SaaS configuration segment, serving mid-market buyers retiring on-premises stacks.
Germany
Energy operators in the Ruhr industrial corridor consolidate fragmented point solutions under EU NIS2 Directive mandates. The country's national data localization laws sustain hybrid architectures despite cloud migration trends. Bavarian manufacturing clusters adopt streamlined virtual appliances to satisfy privileged session monitoring requirements with limited security budgets.
United Kingdom
Healthcare trusts favor cloud-delivered PAM where internal security engineering capacity remains constrained. NHS procurement frameworks compress vendor evaluation cycles through pre-certified solution shortlists. London financial services firms deploy just-in-time access automation at the fastest pace in Europe, eliminating standing administrative credentials.
Japan
Financial institutions under METI cybersecurity framework guidelines adopt SaaS configurations to reduce operational overhead. Tokyo-based trading houses require sub-second credential injection with comprehensive audit trails. Osaka manufacturing networks present underpenetrated attack surfaces for specialized remote access controls isolating OT from IT.
France
Energy operators in Île-de-France respond to mandatory breach notification timelines by consolidating fragmented solutions into integrated platforms. ANSM and CNIL oversight extends to third-party privileged access in pharmaceutical supply chains. Lyon industrial automation clusters demand specialized connectors for proprietary protocols resisting standard API integration.
Global Privileged Access Management (PAM) Solutions Market Competitive Landscape
The competitive structure tilts toward integrated platform providers over point solution specialists. Consolidation pressure intensifies as procurement teams favor unified vaulting, session management, and analytics bundles. Three archetypes dominate: legacy vaulting incumbents extending through acquisition, cloud-native challengers capturing mid-market SaaS transitions, and OT-security hybrids penetrating industrial environments. Dominant competitive moves include portfolio diversification into identity governance convergence and strategic partnerships with hyperscaler marketplaces.
Within the integrated platform tier, CyberArk anchors premium deployments across financial and energy sectors. BeyondTrust occupies a position specializing in remote access controls for industrial operational technology environments. Wallix represents the streamlined virtual appliance archetype designed for mid-market European manufacturing and public sector buyers. These three exemplify how vendor positioning diverges between vaulting-centric heritage, OT-specialized functionality, and deployment simplicity for constrained budgets.
| Leading Market Players |
|---|
| CyberArk |
| Fortinet |
| Broadcom |
| BeyondTrust |
| Delinea |
| ManageEngine |
| ARCON |
| Wallix |
| One Identity |
| Others |
Supply & Pricing Matrix
Federal zero-trust architecture mandates and EU NIS2 Directive procurement specifications are compressing vendor evaluation cycles to 90-120 days, forcing PAM providers to pre-certify solutions against ISO 27001 and NIST SP 800-207 while absorbing compliance costs into subscription pricing tiers.
Pricing Analysis
Cost-down pressure on SaaS configurations accelerates as managed security service providers displace direct enterprise licensing in United Kingdom healthcare and United States municipal government verticals. Three-tier pricing structure across premium, standard, and economy levels separates full-platform vaulting-session-analytics bundles from modular point solutions and entry-level virtual appliances. Price differentiation rests on FIPS 140-2 certification tier and deployment complexity rather than core feature parity. Mid-market buyers in European manufacturing show highest price sensitivity; United States federal agencies demonstrate lowest sensitivity due to zero-trust mandate urgency.
Supply Chain Analysis
Freight and data sovereignty compliance costs sustain hybrid architecture premiums in Germany and Switzerland despite cloud migration trends. Software development concentrates in the United States, Israel, and India, with hyperscaler marketplace distribution running through AWS, Azure, and Google Cloud partner channels. Component dependencies include cryptographic hardware security modules, AI/ML inference engines, and legacy directory service connectors. Single-source vulnerability persists in specialized OT protocol connectors for industrial control environments. Distribution runs through direct enterprise sales, MSSP intermediaries, and hyperscaler marketplaces with regional fulfillment centers in Virginia, Frankfurt, and Singapore.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Identity security architect scarcity constrains vendor delivery capacity across all deployment modes, propping professional services pricing and extending backlog visibility for certified implementation partners.
For Market Incumbents: Deploy just-in-time access automation R&D to anchor premium positioning against cloud-native challengers absorbing mid-market SaaS transitions. Acquire specialized OT-security connector firms to defend against BeyondTrust's industrial remote access dominance. Consolidate fragmented point solution vendors before procurement teams complete platform standardization cycles. For New Entrants and Emerging Players: Hyperscaler marketplace listings offer the fastest route to procurement visibility without direct enterprise sales infrastructure. Target European manufacturing mid-market buyers with streamlined virtual appliances satisfying EU NIS2 session monitoring mandates at sub-incumbent price points. Lead with managed service packaging to bypass internal security engineering capacity constraints in United Kingdom healthcare and United States municipal government segments. For Investors and Strategic Acquirers: The window for entry favors OT-security hybrid specialists with proprietary industrial protocol connectors. Long-term viability hinges on convergence positioning between PAM and identity governance platforms as unified policy engines reshape competitive boundaries. Watch for just-in-time access automation displacement rates exceeding traditional vaulting renewal volumes as inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies vaulting, session management, and analytics to satisfy EU NIS2 consolidated audit trail mandates. |
| Acquisition of Specialist Firm | Captures proprietary OT protocol connectors for industrial control environments in German energy sector. |
| Strategic Partnership | Accelerates hyperscaler marketplace placement to reach United Kingdom healthcare trusts with constrained security engineering. |
| Product Launch | Introduces just-in-time access automation to displace standing administrative credentials in United States federal deployments. |
| Geographic Expansion | Establishes Swiss data residency operations to capture German and Swiss financial institution hybrid architecture demand. |
Research Methodology
Document review covered SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, and NIST SP 800-207 zero-trust architecture guidelines, complemented by interviews with CISOs at financial institutions, identity security architects at energy operators, procurement officers at United Kingdom NHS trusts, and channel partners at hyperscaler marketplaces. Secondary validation drew from ISO certification databases, FERC infrastructure security reports, and METI cybersecurity framework documentation. Bottom-up deployment mode sizing and top-down regulatory mandate impact assessment were triangulated against vendor revenue disclosures.
Segment-level value projections across the analysis window reflect modeled adoption curves for vaulting, session management, and analytics modules by deployment mode, organization size tier, vertical regulatory pressure, and regional compliance maturity. CAGRs were derived from regression against historical procurement cycle compression and mandate implementation timelines. Industry-specific inputs included zero-trust architecture mandate penetration rates and EU NIS2 critical infrastructure operator coverage thresholds.
The model holds under sustained regulatory enforcement and cloud migration continuity; deviation in hyperscaler data sovereignty policy or federal procurement freeze would shift trajectory. Stakeholders should weight assumptions against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Ultra-Secure Smartphone Market
Security Software
Global Security Orchestration Automation and Response (SOAR) Market
Security Software
Vsaas Market
Security Software
Global Error Monitoring Software Market
Security Software
Devsecops Market
Security Software
Web Content Filtering Market
Security Software
US and Latin America Identity and Access Management (IAM) Market
Security Software
Secure Flash Drive Market
Security Software
Application Control Software Market
Security Software
Global Anti-Spam Software Market
Security Software
Global Digital Vehicle Forensics Market
Security Software
Japan Mobile Biometrics Market
Security Software
Software Defined Perimeter (SDP) Market
Security Software
Disk Encryption Software Market
Security Software
Global Data Breach Notification Software Market
Security Software
Smartphone Security Market