
 Source Code Escrow Market | 2026-2036
Source Code Escrow Market Size, Share, and Industry Trends Forecast 2026-2036
Source Code Escrow Market Insights
ISO 27001 certification is bifurcating the competitive landscape into qualified and non-qualified escrow providers. NCC Group leverages its broad geographic footprint to sustain multi-jurisdictional verification capabilities. Iron Mountain anchors physical custody infrastructure across key financial corridors. Codekeeper specializes in automated SaaS escrow workflows for cloud-native deployments.
Source code escrow is a tripartite contractual mechanism whereby a software application's source code, build instructions, and associated intellectual property are deposited with an independent third party for conditional release to a licensee upon predefined trigger events, typically including vendor bankruptcy, acquisition, or material breach. The primary commercial purpose is to protect licensee continuity by ensuring operational access to mission-critical software assets when direct vendor support becomes unavailable. Managed escrow services command premium positioning due to ongoing verification obligations and dynamic update protocols, while cloud-based deployment models are gaining structural share as SaaS providers seek frictionless integration with CI/CD pipelines. On-premise deployments retain dominance in healthcare and finance where data sovereignty requirements override cloud convenience.
FDA scrutiny of software supply chain integrity in medical devices, HIPAA requirements for business associate agreements, and EU GDPR mandates for data processor accountability are collectively elevating escrow from contractual option to regulatory expectation in regulated verticals. The SEC's cybersecurity disclosure rules for public companies further reinforce source code continuity as a material governance concern. Stakeholders must evaluate whether their current escrow arrangements encompass executable verification environments rather than static code deposits.
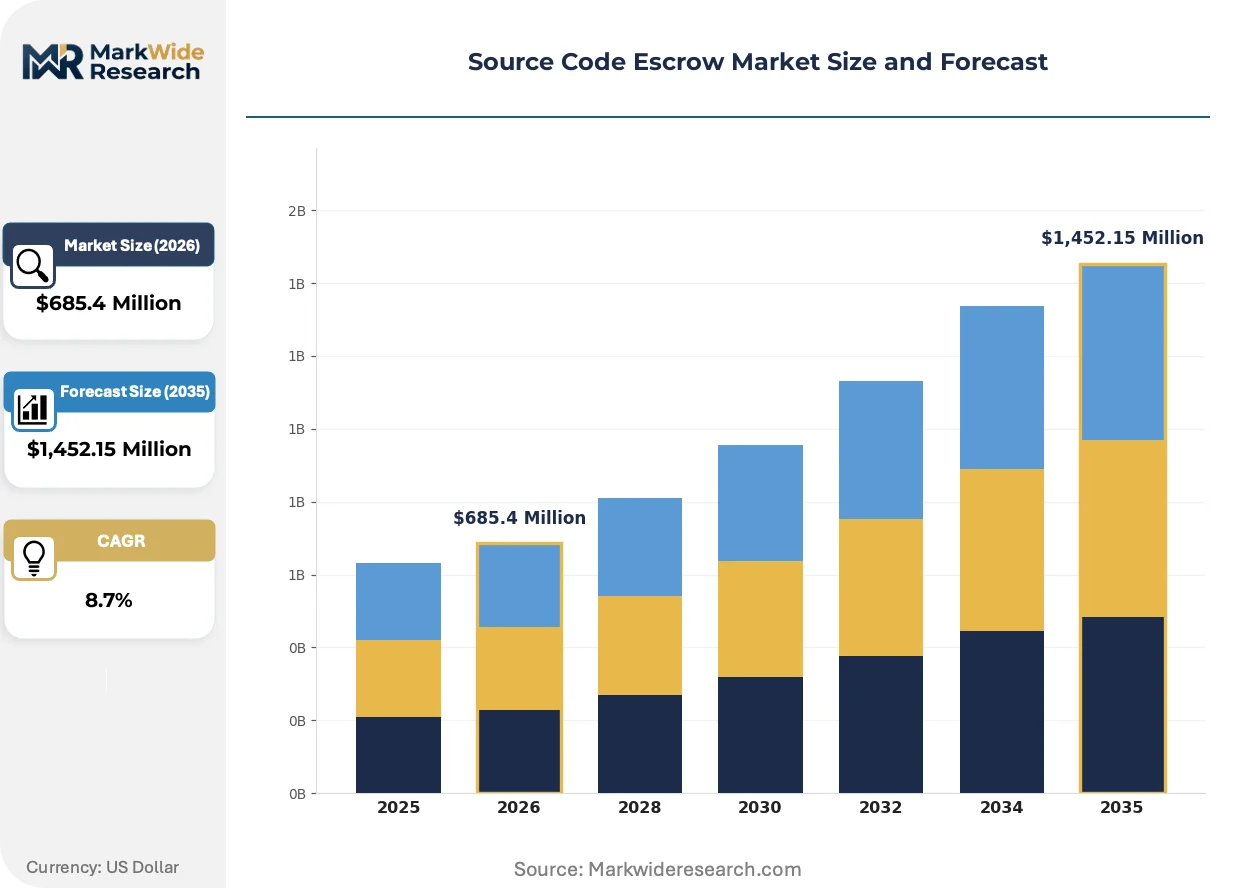
Market Dynamics
Cloud-native CI/CD pipelines are forcing escrow providers to abandon static code deposits in favor of executable verification environments that mirror production runtime conditions. This architectural shift compresses update cycles from quarterly to continuous, redefining operational obligations across the vendor base.
Growth Catalysts
- EU AI Act compliance mandates:SaaS providers deploying machine learning modules in the European Union must demonstrate algorithmic transparency and continuity safeguards, elevating escrow from optional to mandatory contractual infrastructure.
- Financial institution risk frameworks:Basel III operational resilience guidelines and SEC cybersecurity disclosure rules for public companies classify source code access as a material governance control, driving institutional procurement.
- Medical device software integrity:FDA premarket submission requirements for interconnected devices now explicitly reference supply chain verification, creating escrow demand among diagnostic and therapeutic equipment manufacturers.
Market Restraints
- Qualified escrow provider scarcity:ISO 27001 certification requirements bifurcate the vendor landscape, limiting viable supplier options to a narrow tier of audit-capable firms with multi-jurisdictional physical custody infrastructure.
- Static deposit technical obsolescence:Traditional source code escrow without build environment replication delivers limited operational value, degrading licensee willingness to pay premium fees for outdated service models.
- Cross-border data localization friction:India's data protection authority and China's MIIT impose divergent custody location requirements, complicating unified escrow architecture for multinational software deployments.
Strategic Opportunities
- Underpenetrated Indian SaaS ecosystem:Bangalore and Hyderabad cloud infrastructure providers lack formalized escrow adoption despite rapid international customer acquisition, presenting first-mover positioning for verification-capable entrants.
- Automated CI/CD escrow integration:DevOps toolchain convergence with escrow workflows enables subscription-based recurring revenue models that supplant transactional deposit arrangements.
- GDPR Article 28 processor accountability:Data controller liability for subprocessor continuity creates regulatory tailwind for escrow services encompassing not merely code but runtime configuration and encryption key custody.
Industry Challenges
- Executable environment replication complexity:Container orchestration and serverless architectures demand escrow providers maintain current expertise across Kubernetes, AWS Lambda, and Azure Functions deployment patterns.
- Multi-jurisdictional legal harmonization:Trigger event definitions and release protocols vary across German civil code, English common law, and Delaware corporate law, complicating standardized contract templates.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Source Code Escrow Market |
| Market Size in 2026 | $685.4 Million |
| Market Size in 2035 | $1,452.15 Million |
| CAGR (2026 – 2036) | 8.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Standard Escrow, Managed Escrow, On-Demand Escrow, Custom Escrow End User: Software Developers, Enterprises, SaaS Providers, IT Service Firms Deployment Model: Cloud-Based, On-Premise, Hybrid, Multi-Tenant Industry Vertical: Healthcare, Finance, Education, Telecommunications |
| Companies Covered | EscrowTech, NCC Group, Iron Mountain, PRAXIS Technology Escrow, National Software Escrow, Codekeeper, Escrow London, SES-Escrow, TUV SUD, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Source Code Escrow Market Trends and Innovations
Verification automation is compressing escrow service delivery from manual quarterly audits to continuous compliance monitoring, restructuring cost economics and competitive differentiation across provider tiers.
Immutable ledger-based deposit attestation is supplanting traditional notarization and physical vault documentation for code provenance verification. Financial services procurement teams in Frankfurt and Singapore are mandating blockchain-anchored custody records for critical trading infrastructure. This technology is enabling real-time audit trails that compress dispute resolution timelines from months to days.
REACH chemical substance tracking obligations and EU AI Act risk classification rules are converging to impose algorithmic ingredient disclosure requirements on software vendors. Industrial consequence includes mandatory documentation of training data lineage and model architecture for high-risk AI applications. German automotive suppliers and French healthcare AI developers are most affected, responding by embedding escrow clauses into standard procurement templates.
Buyer procurement committees are consolidating vendor risk assessment functions that previously fragmented across legal, IT security, and procurement departments. Enterprise software selection in United States healthcare and United Kingdom financial services now routes through dedicated third-party risk management offices. This concentration is most visible in London and New York, where dedicated escrow specialists have displaced generalist contract negotiators in high-value SaaS transactions.
Source Code Escrow Market Segmentation

Escrow procurement patterns diverge sharply across service tiers and deployment architectures. Segment boundaries determine pricing power, verification obligations, and compliance exposure for both providers and licensees.
Service Type:
Substitution pressure intensifies as automated CI/CD pipelines erode the value proposition of static deposit models.
- Standard Escrow:Static source code deposits with periodic manual verification cycles. German automotive suppliers and French healthcare AI developers still specify this tier for legacy procurement templates despite technical limitations.
- Managed Escrow:Continuous verification environments with dynamic update protocols and build replication services. United States financial institutions in New York and Chicago pay premium fees for ISO 27001-certified providers offering executable runtime mirroring.
- On-Demand Escrow:Trigger-activated release services without ongoing verification obligations. Indian SaaS providers in Bangalore favor this model for cost-sensitive international customer contracts.
- Custom Escrow:Bespoke arrangements covering encryption key custody, runtime configuration, and specialized trigger conditions. Singapore trading infrastructure operators mandate blockchain-anchored custody records under this tier.
Managed Escrow retains volume leadership; Custom Escrow holds the steepest expansion curve.
End User:
Procurement sophistication varies dramatically by organizational scale and regulatory exposure.
- Software Developers:Individual vendors and small development shops seeking basic bankruptcy protection for licensees. United States and German independent software vendors dominate this segment's transaction volume.
- Enterprises:Large organizations with dedicated third-party risk management offices. London and New York headquarters drive consolidated vendor assessment functions across multinational deployments.
- SaaS Providers:Cloud-native vendors requiring frictionless CI/CD integration. Hyderabad infrastructure providers are accelerating adoption to satisfy EU AI Act compliance demands from European customers.
- IT Service Firms:Systems integrators and managed service providers embedding escrow into client solution architectures. Frankfurt procurement committees specify executable verification for critical trading infrastructure.
Enterprises dominate current procurement volume; SaaS Providers are expanding most quickly.
Deployment Model:
Data sovereignty requirements and runtime complexity reshape architectural preferences across verticals.
- Cloud-Based:Native SaaS escrow platforms with API-driven deposit workflows. Automated integration with Kubernetes and serverless environments commands premium positioning.
- On-Premise:Physical custody infrastructure with localized hardware security modules. Healthcare and finance sectors in the United States and Germany retain this model for HIPAA and GDPR data sovereignty compliance.
- Hybrid:Split architectures combining cloud accessibility with on-premise critical asset storage. Multi-jurisdictional deployments favor this approach to satisfy divergent custody location mandates.
- Multi-Tenant:Shared escrow infrastructure serving multiple licensees under standardized terms. Cost efficiency attracts mid-market software vendors with distributed customer bases.
On-Premise maintains share in regulated verticals; Cloud-Based is gaining share fastest.
Industry Vertical:
Regulatory intensity elevates escrow from contractual option to mandatory governance control.
- Healthcare:FDA medical device software integrity requirements and HIPAA business associate agreements drive escrow adoption. Diagnostic and therapeutic equipment manufacturers face explicit supply chain verification mandates.
- Finance:Basel III operational resilience guidelines and SEC cybersecurity disclosure rules classify source code access as material governance. United States and United Kingdom financial institutions anchor premium service demand.
- Education:University technology transfer offices and research institutions protecting licensed intellectual property. Lower regulatory pressure limits verification service penetration.
- Telecommunications:Critical infrastructure protection requirements and national security considerations. Network equipment vendors face procurement specifications from government and carrier customers.
Finance commands the highest service fees; Healthcare is climbing the fastest.

Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States financial institutions and German automotive suppliers anchor premium escrow procurement, while Indian SaaS providers and Singapore trading infrastructure operators are accelerating adoption to satisfy international compliance mandates.
United States
New York and Chicago financial institutions drive demand for ISO 27001-certified managed escrow services with executable runtime mirroring. SEC cybersecurity disclosure rules classify source code access as material governance control. Silicon Valley SaaS providers are integrating automated CI/CD escrow workflows to satisfy enterprise customer procurement committees.
Germany
Frankfurt procurement committees specify executable verification environments for critical trading infrastructure under Basel III operational resilience guidelines. EU AI Act compliance mandates elevate escrow from optional to mandatory contractual infrastructure for machine learning deployments. Stuttgart automotive suppliers embed escrow clauses into standard procurement templates for diagnostic software.
India
Bangalore and Hyderabad cloud infrastructure providers lack formalized escrow adoption despite rapid international customer acquisition. The country's data protection authority imposes divergent custody location requirements complicating unified escrow architecture. Telangana-based SaaS vendors are accelerating adoption to satisfy EU AI Act demands from European customers.
United Kingdom
London headquarters drive consolidated vendor assessment functions across multinational deployments through dedicated third-party risk management offices. UK financial services procurement teams mandate blockchain-anchored custody records for critical infrastructure. Edinburgh and Manchester technology transfer offices are formalizing escrow arrangements for licensed intellectual property.
Singapore
Trading infrastructure operators mandate blockchain-anchored custody records under custom escrow tiers for algorithmic transparency requirements. The Monetary Authority of Singapore's operational resilience guidelines reinforce source code continuity as material governance concern. Marina Bay financial district procurement teams are consolidating previously fragmented legal, IT security, and vendor risk assessment functions.
Source Code Escrow Market Competitive Landscape
Player mix skews toward verification-capable specialists with multi-jurisdictional physical custody infrastructure. The vendor base concentrates around three strategic tiers: ISO 27001-certified providers commanding premium positioning, cloud-native platforms offering API-driven deposit workflows, and traditional custodians anchoring physical infrastructure. Competitive differentiation centers on automated CI/CD integration capabilities and executable environment replication expertise rather than static code storage.
Among verification-capable specialists, NCC Group exemplifies the geographic footprint archetype with multi-jurisdictional capabilities, Iron Mountain occupies the physical custody infrastructure position across key financial corridors, and Codekeeper represents the cloud-native automation tier for SaaS escrow workflows. These three anchors illustrate the competitive spectrum from traditional custody to continuous compliance monitoring.
| Leading Market Players |
|---|
| EscrowTech |
| NCC Group |
| Iron Mountain |
| PRAXIS Technology Escrow |
| National Software Escrow |
| Codekeeper |
| Escrow London |
| SES-Escrow |
| TUV SUD |
| Others |
Pricing and Supply Chain Analysis
Automated CI/CD pipeline substitution for static deposit workflows simultaneously reshapes supply geography toward cloud-native verification hubs and compresses pricing economics across traditional custody tiers. Cloud-based escrow platforms in Bangalore and Singapore draw procurement share from physical vault providers, forcing price realignment across service archetypes.
Pricing Analysis
Cost-plus contracts with ISO 27001 certification indexation dominate managed escrow procurement, particularly among United States financial institutions. Pricing stratifies across ISO-certified premium tiers, executable verification mid-market tiers, and static deposit economy tiers, with certification level and build environment complexity as primary differentiation drivers. Cost compression in standard escrow is intensifying because automated SaaS-native alternatives erode perceived value. SaaS providers in Hyderabad exhibit highest price sensitivity; Frankfurt trading infrastructure operators show least.
Supply Chain Analysis
Just-in-time inventory strategy governs cloud-native escrow deposits, while strategic stockpile logic persists for on-premise hardware security module custody. Supply concentrates in the United States, Germany, and Singapore for verification-capable infrastructure, with India emerging for cost-sensitive on-demand services. Raw material dependencies center on cryptographic hardware, data center real estate, and blockchain attestation infrastructure. Single-source vulnerability runs through ISO 27001-certified provider scarcity. Distribution runs through direct enterprise sales and hyperscaler marketplace integrations.

Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Self-serve SaaS escrow platforms threaten incumbent verification specialists, forcing substitution defense through continuous compliance automation and CI/CD toolchain embedding.
For Market Incumbents: Compound defensive positioning by deepening executable environment replication expertise across Kubernetes and serverless architectures, and by acquiring cloud-native workflow automation capabilities to neutralize SaaS-native entrants. ISO 27001 certification investment remains essential as regulatory gatekeeping tightens.
For New Entrants and Emerging Players: Lead with automated CI/CD escrow integration targeting Bangalore and Hyderabad SaaS vendors seeking EU AI Act compliance without legacy infrastructure burden. White-space concentration sits in Indian cloud infrastructure providers lacking formalized escrow adoption; embed into DevOps toolchain marketplaces as primary go-to-market angle.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed escrow providers holding physical custody infrastructure but lacking cloud automation capabilities. Long-term viability hinges on verification environment replication expertise rather than vault real estate. Acquisition target archetype: ISO 27001-certified regional specialists with executable build environment capabilities. Watch for EU AI Act enforcement thresholds as inflection signal.
| Strategic Initiative | Industry Significance |
|---|---|
| CI/CD Pipeline Integration | Automated escrow workflows compress update cycles from quarterly to continuous, satisfying SEC disclosure requirements. |
| ISO 27001 Certification Investment | Regulatory gatekeeping bifurcates competitive landscape into qualified and non-qualified provider tiers. |
| Executable Verification Environment Deployment | Runtime mirroring capabilities command premium positioning among Basel III-compliant financial institutions. |
| Blockchain-Anchored Custody Records | Immutable ledger attestation compresses dispute resolution timelines for Singapore trading infrastructure. |
| Geographic Expansion into India | Telangana and Karnataka SaaS acceleration creates first-mover positioning for verification-capable entrants. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of SEC cybersecurity disclosure filings, EU regulatory guidance documents, and escrow provider certification databases. Interviews with CTOs at SaaS providers, IT procurement officers at financial institutions, platform engineers, and escrow operations specialists informed demand-side dynamics. Secondary validation drew from ISO certification registries, GDPR enforcement actions, and FDA medical device software guidance. Bottom-up transaction analysis and top-down regulatory sizing were triangulated.
Segmentation dimensions modeled span service type, end user organization scale, deployment architecture, and regional regulatory cluster across the analysis window. CAGRs were derived from verified transaction flows and regulatory mandate implementation timelines. Industry-specific forecast inputs include EU AI Act compliance deadline acceleration and Basel III operational resilience guideline adoption curves.
Forecasts assume regulatory continuity in United States SEC disclosure regimes and EU AI Act enforcement; material policy shifts would require re-modeling. Specific risks that could revise projections include cross-border data localization mandate divergence and qualified provider certification bottleneck intensification. Revision becomes warranted when automated CI/CD escrow penetration crosses threshold dominance in enterprise procurement.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Internet Filter Software Market
Security Software
Video Intercom Devices Market
Security Software
Parental Monitoring Software Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
North America Video Management System Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Remote Access Management Market
Security Software
Global Mobile Security Software Market
Security Software
Cybersecurity Software Market
Security Software
Global Wireless Intrusion Prevention System Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Digital Risk Protection Software Market
Security Software
DNS Protection Software Market
Security Software
Public Cloud Management and Security Services Market
Security Software
Mobile Antivirus Software Market
Security Software
Antivirus Software Package Market