
 Next-Generation Intrusion Prevention System (NGIPS) Market | 2026-2036
Next-Generation Intrusion Prevention System (NGIPS) Market Size, Share, and Industry Trends Forecast 2026-2036
Next-Generation Intrusion Prevention System (NGIPS) Market Foresight
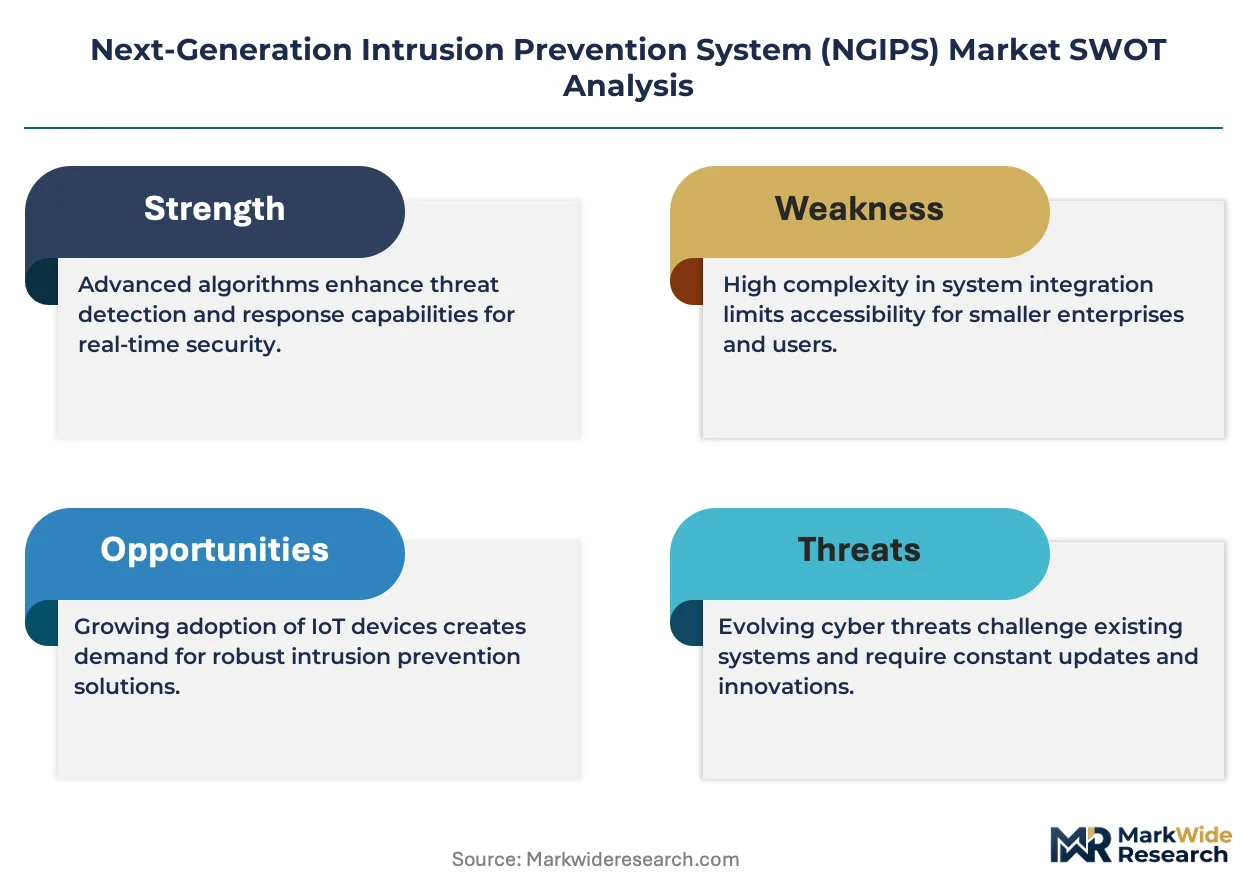
GDPR enforcement is realigning the cost-of-entry calculus for European NGIPS deployments, forcing vendors to embed privacy-preserving inspection protocols. Check Point Software Technologies Ltd. anchors its position through deep packet inspection specialization across hybrid environments. Cisco Systems, Inc. dominates enterprise hardware deployments with integrated threat intelligence fabrics. Palo Alto Networks, Inc. differentiates via cloud-native NGIPS architectures that extend into virtualized workloads.
Next-Generation Intrusion Prevention Systems combine deep packet inspection, behavioral analytics, and automated threat response at line speeds exceeding 100 Gbps to block malicious traffic before network penetration. The technology serves critical infrastructure operators, financial institutions, and government agencies requiring sub-millisecond latency in attack mitigation. Hardware deployments retain the largest installed base among product types due to performance requirements in high-throughput data centers, though managed services are expanding fastest as mid-market enterprises outsource security operations. Cloud deployment models are capturing margin pools from organizations migrating away from capital-intensive on-premises appliances toward consumption-based security delivery.
FCC guidelines on communications infrastructure security, EU NIS2 Directive requirements for critical entity protection, and HIPAA technical safeguards collectively shape product certification pathways and procurement eligibility. ISO 27001 alignment has become a de facto threshold for vendor qualification in regulated sectors. Stakeholders must evaluate whether their current NGIPS architectures can absorb forthcoming quantum-resistant encryption standards without forklift infrastructure replacement.
Market Dynamics
Zero-trust architecture mandates from federal agencies are compressing procurement cycles and forcing NGIPS vendors to pre-certify products against FedRAMP and DISA STIGs before contract eligibility.
Growth Catalysts
- FCC infrastructure security guidelines:Communications carriers must deploy deep packet inspection for 5G core networks, creating mandatory replacement cycles for legacy intrusion detection systems.
- Real-time payment infrastructure expansion:Financial services firms in the United States require sub-millisecond threat response to protect instant settlement rails without transaction latency.
- EU NIS2 Directive enforcement:Critical entities across energy, transport, and healthcare must implement automated response capabilities by 2024, triggering compliance-driven procurement waves.
Market Restraints
- Specialized silicon supply concentration:High-throughput deep packet inspection ASICs depend on TSMC and Samsung foundry capacity in Taiwan and South Korea, creating single-source vulnerability for 100 Gbps+ appliances.
- GDPR inspection protocol friction:European privacy regulators constrain payload analysis depth, forcing vendors to architect privacy-preserving inspection that degrades threat detection fidelity.
- Quantum-resistant encryption transition:NIST post-quantum cryptography standards will obsolete current TLS inspection architectures, threatening premature hardware obsolescence for deployed appliances.
Strategic Opportunities
- Managed detection and response services:Mid-market enterprises in Germany and France are outsourcing NGIPS operations to MSSPs, shifting revenue from appliance sales to recurring subscription models.
- Virtualized workload protection:Cloud-native NGIPS architectures are expanding into Kubernetes container environments, capturing margin from organizations migrating off physical data centers.
- HIPAA technical safeguard alignment:Healthcare delivery organizations in the United States face audit pressure, creating procurement urgency for NGIPS with pre-mapped HIPAA control documentation.
Industry Challenges
- Threat intelligence analyst scarcity:SOC teams lack personnel capable of tuning behavioral analytics engines, forcing vendors to embed automated policy optimization or risk customer churn.
- Multi-vendor integration complexity:Enterprises operate hybrid NGIPS estates across Cisco, Palo Alto Networks, and Check Point platforms, creating alert correlation nightmares and delayed incident response.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Next-Generation Intrusion Prevention System (NGIPS) Market |
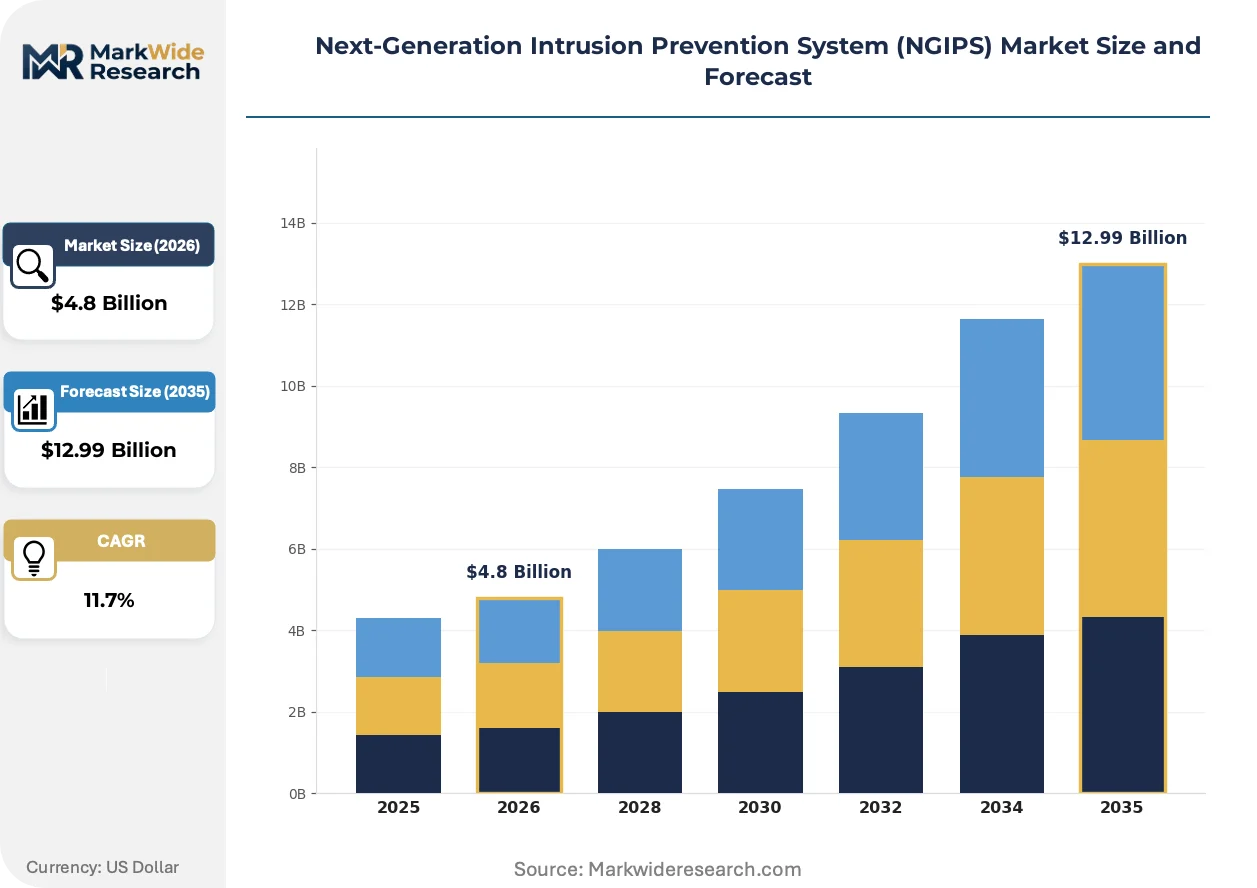
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $12.99 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Hardware, Software, Hybrid, Managed Service Deployment Model: On-Premises, Cloud, Hybrid Cloud, Virtualized End User: Enterprises, Government, Educational Institutions, Service Providers Application: Network Security, Data Security, Threat Management, Compliance |
| Companies Covered | Check Point Software Technologies Ltd., International Business Machines Corporation, Cisco Systems, Inc., Trend Micro Incorporated, Huawei Technologies Co., Ltd., Fortinet, Inc., Juniper Networks, Inc., SonicWall Inc., Palo Alto Networks, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Next-Generation Intrusion Prevention System (NGIPS) Market Shifts & Advancements
Artificial intelligence inference at the network edge is compressing detection latency from seconds to milliseconds while forcing architectural trade-offs between model accuracy and hardware cost.
Machine learning-based behavioral analytics is expanding into encrypted traffic inspection without decryption. Financial institutions in New York and London are piloting these systems for SWIFT network protection. The technology is expanding into use cases previously blocked by privacy regulations, opening European markets previously closed to deep packet inspection vendors.
The EU AI Act classifies certain NGIPS autonomous response functions as high-risk AI systems, requiring conformity assessments and human oversight protocols. Vendors must now document training data provenance and model drift monitoring for European deployments. Healthcare and critical infrastructure operators in France and Germany are demanding pre-certified AI Act compliance before contract signature.
Consumption-based security delivery is displacing capital-intensive appliance procurement among mid-market enterprises. Managed service providers in the United States are bundling NGIPS with SOC-as-a-service offerings, capturing customers that previously deferred security investments. Manufacturing firms across Michigan and Ohio industrial corridors represent the fastest-adopting segment for this procurement model.
Next-Generation Intrusion Prevention System (NGIPS) Market Segmentation
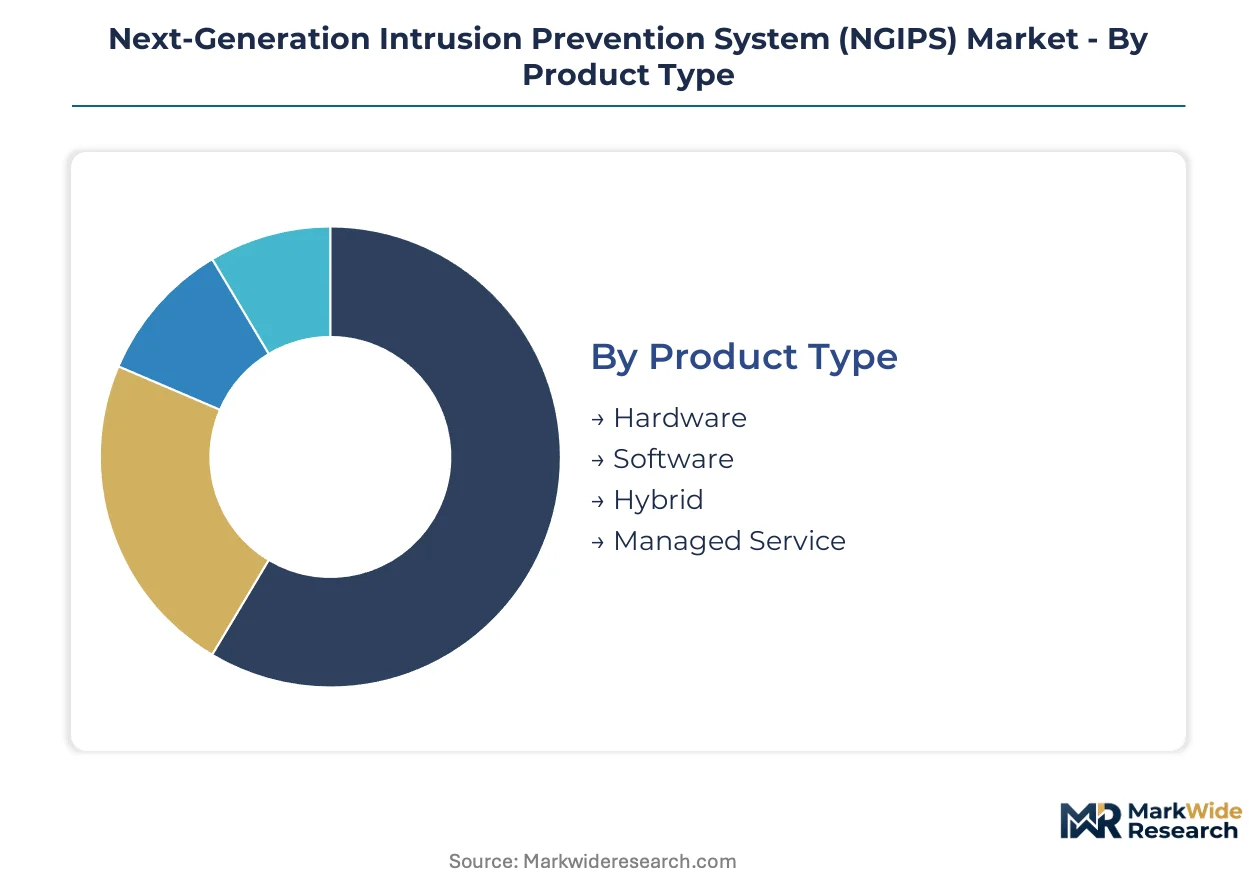
NGIPS procurement patterns diverge sharply across deployment architectures and buyer sophistication. Hardware appliances dominate high-throughput environments, while consumption-based models reshape mid-market economics.
Product Type:
Supply concentration in specialized ASIC fabrication tilts commercial leverage toward vendors with captive foundry relationships or long-term capacity agreements.
- Hardware:Purpose-built appliances integrate deep packet inspection silicon achieving 100 Gbps+ throughput with sub-millisecond latency. Data center operators in the United States and Germany specify these for payment infrastructure protection where performance guarantees are non-negotiable.
- Managed Service:MSSPs bundle NGIPS operations with 24/7 SOC coverage, shifting capital expenditure to recurring operational budgets. Mid-market manufacturers across Michigan and Ohio industrial corridors favor this model to bypass security staffing constraints.
- Software:Virtualized NGIPS instances deploy on commodity servers for branch office protection.
- Hybrid:Combined hardware-software architectures synchronize on-premises appliances with cloud analytics layers.
Hardware absorbs the bulk of installed capacity; managed service is expanding most quickly.
Deployment Model:
Migration patterns from capital-intensive appliances toward consumption-based delivery reshape margin capture across vendor portfolios.
- Cloud:Native NGIPS architectures auto-scale inspection capacity across multi-tenant infrastructure without physical appliance procurement. Financial services firms migrating SWIFT protection to London and Frankfurt cloud regions drive procurement urgency here.
- On-Premises:Appliance-based deployment retains dominance where data sovereignty requirements or air-gapped networks prohibit external connectivity. Critical infrastructure operators under EU NIS2 Directive and FCC infrastructure guidelines specify these for audit traceability.
- Hybrid Cloud:Split architectures route sensitive traffic through on-premises inspection while offloading bulk analysis to cloud analytics.
- Virtualized:Container-native NGIPS protects Kubernetes workloads without host-level appliance deployment.
On-premises retains the largest revenue base; cloud deployment is climbing the fastest as regulated sectors cautiously migrate.
End User:
Procurement sophistication varies dramatically across buyer categories, with federal mandates compressing sales cycles for government segments while enterprises negotiate multi-year enterprise licensing.
- Government:Federal agencies mandate FedRAMP and DISA STIG pre-certification before contract eligibility, favoring established vendors with existing authorization pathways. Zero-trust architecture directives from United States civilian and defense agencies accelerate replacement of legacy intrusion detection systems.
- Enterprises:Fortune 500 firms operate hybrid NGIPS estates across multiple vendor platforms, creating integration complexity that favors single-source consolidation plays.
- Service Providers:Telecommunications carriers deploy NGIPS at 5G network edges under FCC infrastructure security guidelines.
- Educational Institutions:Universities with research hospital affiliations face HIPAA technical safeguard audits alongside standard network protection requirements.
Government absorbs concentrated procurement volume; service providers are gaining share fastest as 5G security mandates propagate.
Application:
Regulatory compliance deadlines create synchronized procurement waves that override standard budget cycles in specific verticals.
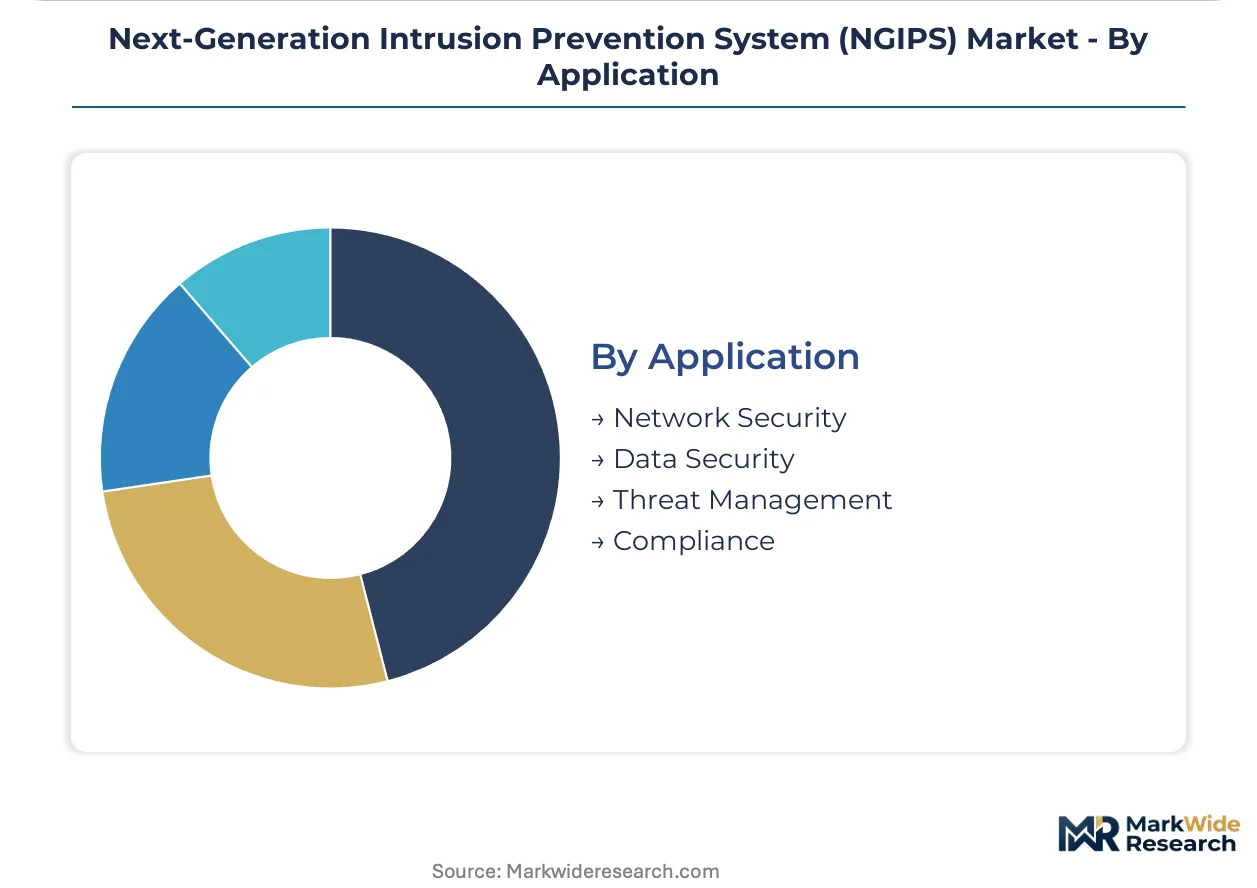
- Compliance:Pre-mapped control documentation for HIPAA, ISO 27001, and EU NIS2 Directive shortens security audit preparation for healthcare delivery organizations and critical infrastructure operators. Vendors with pre-certified documentation capture procurement preference in United States and German markets.
- Network Security:Core NGIPS functionality protecting perimeter and east-west traffic remains the foundational deployment pattern across all buyer categories.
- Data Security:Deep packet inspection for data loss prevention extends NGIPS into content-aware protection.
- Threat Management:Integrated threat intelligence fabrics correlate NGIPS alerts with broader security operations center workflows.
Network security retains foundational deployment share; compliance applications are expanding most steeply as regulatory deadlines approach.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal agencies are compressing NGIPS procurement cycles through zero-trust mandates, while EU NIS2 Directive deadlines trigger synchronized compliance waves across critical infrastructure operators.
United States
FCC infrastructure security guidelines mandate deep packet inspection for 5G core networks, forcing communications carriers into mandatory replacement cycles. Federal agencies require FedRAMP and DISA STIG pre-certification before contract eligibility, favoring established vendors with existing authorization pathways. Financial services firms in New York require sub-millisecond threat response to protect instant settlement rails.
Germany
Critical infrastructure operators under EU NIS2 Directive must implement automated response capabilities, triggering compliance-driven procurement waves. The country's national cybersecurity regulator enforces deeper packet inspection standards for energy and transport sectors. Manufacturing firms across Bavaria and Baden-Württemberg industrial corridors favor managed detection and response services to bypass security staffing constraints.
France
Healthcare and critical infrastructure operators demand pre-certified EU AI Act compliance before contract signature for autonomous NGIPS response functions. CNIL privacy regulators constrain payload analysis depth, forcing vendors to architect privacy-preserving inspection protocols. Paris-based financial institutions pilot machine learning-based behavioral analytics for encrypted traffic inspection without decryption.
United Kingdom
Financial services firms migrating SWIFT protection to London cloud regions drive procurement urgency for cloud-native NGIPS architectures. The country's national cybersecurity center mandates alignment with ISO 27001 as a threshold for vendor qualification in regulated sectors. Mid-market enterprises in London and Southeast England outsource NGIPS operations to managed security service providers.
Japan
METI industrial security guidelines accelerate NGIPS deployment for manufacturing firms protecting intellectual property in connected factory environments. The country's national cybersecurity regulator emphasizes supply chain security for semiconductor and automotive sectors. Tokyo and Osaka metropolitan clusters concentrate demand for hardware appliances achieving 100 Gbps+ throughput with sub-millisecond latency.
Next-Generation Intrusion Prevention System (NGIPS) Market Competitive Landscape
United States vendors anchor the premium tier; Israeli and Chinese specialists hold differentiated positions in behavioral analytics and telecommunications infrastructure respectively. The market structures around three tiers: established platform providers with FedRAMP authorization, cloud-native specialists capturing virtualized workload protection, and telecommunications-focused vendors securing 5G edge deployments. Strategic moves concentrate on portfolio diversification into managed detection and response services and technology licensing for quantum-resistant encryption readiness.
Within the established platform tier, Check Point Software Technologies Ltd. and Cisco Systems, Inc. exemplify vendors with deep specialization in hybrid environment inspection and integrated threat intelligence fabrics respectively. Palo Alto Networks, Inc. occupies a position representing cloud-native NGIPS architectures that extend into virtualized workloads. These three companies illustrate the competitive spectrum from hardware-centric enterprise deployments to consumption-based security delivery models.
| Leading Market Players |
|---|
| Check Point Software Technologies Ltd. |
| International Business Machines Corporation |
| Cisco Systems, Inc. |
| Trend Micro Incorporated |
| Huawei Technologies Co., Ltd. |
| Fortinet, Inc. |
| Juniper Networks, Inc. |
| SonicWall Inc. |
| Palo Alto Networks, Inc. |
| Others |
Supply & Pricing Matrix
Specialized silicon wafer pricing indices from Taiwan and South Korea cascade through NGIPS manufacturing tiers, compressing margins for hardware appliances while elevating subscription premiums for cloud-native alternatives that bypass foundry bottlenecks.
Pricing Analysis
Volume concentrates in hardware appliances where TSMC-fabricated ASICs command premium positioning, while cloud-native deployments capture margin through consumption-based SaaS tiers that decouple from silicon supply cycles. Price differentiation separates FedRAMP-authorized platforms from uncertified alternatives, with DISA STIG compliance adding substantial certification premiums. Cost compression in high-throughput hardware segments is intensifying as foundry capacity constraints persist. Mid-market enterprises exhibit highest price sensitivity, driving procurement toward managed service bundles that convert capital expenditure into predictable operational budgets.
Supply Chain Analysis
High-throughput deep packet inspection ASICs rest on Taiwanese and South Korean foundry capacity, with specialized packaging and testing concentrated in Malaysia and Vietnam. Raw material dependencies span silicon wafers, advanced substrates, and precision thermal management components. Single-source vulnerability around TSMC's leading-edge nodes creates procurement risk for 100 Gbps+ appliance vendors. Distribution runs through authorized channel partners serving federal integrators, telecommunications carriers, and enterprise security procurement teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The NGIPS market functions as a cost-of-compliance arena where EU NIS2 Directive mandates erect regulatory moats favoring vendors with pre-certified automated response capabilities and documented conformity pathways.
For Market Incumbents: To counter quantum-resistant encryption obsolescence threatening TLS inspection architectures, anchor defensive positioning through backward integration into post-quantum cryptography R&D partnerships and capacity expansion in FedRAMP-authorized cloud regions. Certification investment represents the critical lever for maintaining government contract eligibility against emerging cloud-native challengers. For New Entrants and Emerging Players: Cloud-native delivery models unlock white-space penetration among mid-market manufacturers across Michigan and Ohio industrial corridors, where security staffing constraints drive managed detection and response outsourcing. Kubernetes-native workload protection offers the most penetrable application layer, with HIPAA pre-mapped control documentation serving as the decisive go-to-market wedge for healthcare delivery organizations. For Investors and Strategic Acquirers: Distressed-cycle entries favor managed security service providers with established SOC operations in Germany and France, where EU AI Act compliance requirements are consolidating vendor landscapes. The inflection signal to monitor is NIST post-quantum cryptography standard finalization, which will trigger replacement waves obsoleting current hardware estates.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Pathway | Pre-certification against DISA STIGs unlocks federal agency procurement eligibility before contract competition. |
| Post-Quantum Cryptography R&D Partnership | Early alignment with NIST standards future-proofs TLS inspection architectures against encryption obsolescence. |
| Managed Detection and Response Service Launch | Recurring revenue capture from mid-market enterprises bypasses capital-intensive appliance sales cycles. |
| EU AI Act Conformity Assessment | Documented training data provenance satisfies French and German healthcare operator contract prerequisites. |
| Kubernetes-Native Platform Integration | Container workload protection captures margin from organizations migrating physical data center estates. |
Research Methodology
Independent corroboration across CISO interviews, federal procurement officer consultations, and MSSP operations directors underwrites the qualitative findings, with secondary validation drawing from DISA STIG documentation, FedRAMP authorization repositories, and EU NIS2 Directive implementation guidance. Bottom-up demand modeling from enterprise security budgets triangulates against top-down market sizing from vendor revenue disclosures and telecommunications carrier capex patterns.
Rate-of-change decomposition across the projection horizon segments NGIPS adoption by deployment architecture, end-user sophistication tier, and regulatory compliance urgency. The analytical framework models product type transitions, cloud migration velocity, and managed service penetration as independent variables. CAGRs derive from elasticity estimates around compliance deadline clustering and zero-trust mandate propagation through federal procurement channels.
The model holds under stable regulatory enforcement timelines and foundry capacity allocation; deviation in NIST post-quantum cryptography standard acceleration or Taiwan supply chain disruption would shift replacement cycle assumptions. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Identity and Access Management (IAM) Market
Security Software
Global Network Encryption Market
Security Software
Data Leakage Prevention Product Market
Security Software
Robocall Mitigation Market
Security Software
Software Protection Dongle Market
Security Software
Disk Encryption Software Market
Security Software
US Hardware OTP Token Authentication Market
Security Software
Personal Data Recovery Software Market
Security Software
Cyber Attack Simulation Software Market
Security Software
Global Secure Access Service Edge Market
Security Software
Privacy Management Software Market
Security Software
Security Information and Event Management (SIEM) Market
Security Software
Global Security Software in Telecom Market
Security Software
Software Assurance Market
Security Software
ATM Security Market