
 DC and PKI Market | 2026-2036
DC and PKI Market Size, Share, and Industry Trends Forecast 2026-2036
DC and PKI Market Outlook
Post-quantum cryptography is expanding its footprint across certificate lifecycle management, displacing classical RSA and ECC algorithms in high-assurance environments. Thales leverages dedicated hardware security module manufacturing to anchor its position in government and defense procurement channels. DigiCert competes through cloud-native certificate provisioning platforms that reduce enterprise deployment friction. Entrust Corporation specializes in hybrid on-premises and cloud credentialing systems for regulated financial workflows.
DC and PKI encompasses the infrastructure, protocols, and services that bind public key certificates to digital identities, typically operating through certificate authorities, registration authorities, and directory services using X.509 standards with key lengths ranging from 2048-bit RSA to 256-bit elliptic curves. The primary commercial purpose is to enable trusted authentication, encrypted communications, and non-repudiation across networked systems. Cloud-based deployment is capturing the fastest growth trajectory as enterprises abandon capital-intensive on-premises hardware for elastic, API-driven certificate services. Public Key Infrastructure retains the largest revenue pool due to its foundational role in root-of-trust architectures, though certificate management tools are extracting disproportionate margin from automation and policy enforcement workflows.
The EU AI Act, GDPR, and NIS2 Directive collectively mandate auditable identity verification and encrypted data flows for critical service operators across Europe. In the United States, NIST post-quantum migration standards and SEC cybersecurity disclosure rules are compressing enterprise timelines for certificate infrastructure modernization. Stakeholders must monitor regulatory divergence between jurisdictions and pre-position compliant architectures before enforcement windows crystallize into procurement mandates.
Market Dynamics
Post-quantum cryptographic migration is compressing enterprise certificate refresh cycles as NIST standards crystallize into procurement mandates. This technology transition is forcing infrastructure operators to rebuild root-of-trust architectures before existing algorithms face cryptanalytic compromise.
Growth Catalysts
- NIS2 Directive:European critical infrastructure operators must deploy auditable identity verification systems by enforcement deadlines, accelerating hardware security module procurement across energy and transport sectors.
- Automotive sector:Connected vehicle manufacturers in Germany are integrating quantum-resistant certificate architectures into V2X communication stacks to satisfy type-approval requirements.
- Hardware security modules:Financial institutions are mandating FIPS 140-3 Level 3 certified transaction signing devices to satisfy SEC cybersecurity disclosure obligations.
Market Restraints
- Semiconductor supply concentration:Dedicated cryptographic processor fabrication depends on Taiwan-based foundry capacity, creating single-source vulnerability for high-assurance module production.
- Legacy RSA/ECC lock-in:Embedded systems with decade-long depreciation cycles cannot accommodate algorithm agility without complete hardware replacement.
- EU AI Act compliance costs:Biometric identity verification systems require re-certification under new conformity assessment procedures, extending sales cycles by 8-14 months.
Strategic Opportunities
- Cloud-native certificate services:API-driven lifecycle management platforms are capturing mid-market enterprises abandoning on-premises hardware maintenance burdens.
- India's digital public infrastructure:The country's central identity regulator is expanding PKI coverage to agricultural commodity exchanges and pharmaceutical supply chains.
- Hybrid credentialing convergence:Physical smart card issuance systems are integrating with mobile device identity wallets to serve regulated financial workflows.
Industry Challenges
- Post-quantum cryptographic expertise scarcity:Lattice-based algorithm implementation requires specialized mathematical training unavailable in standard cybersecurity curricula.
- Cross-jurisdiction certificate recognition:Divergent national trust frameworks prevent seamless interoperability of qualified electronic signatures across borders.
- Legacy directory service integration:X.500-based identity repositories resist migration to lightweight directory access protocol standards without extensive schema reengineering.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | DC and PKI Market |
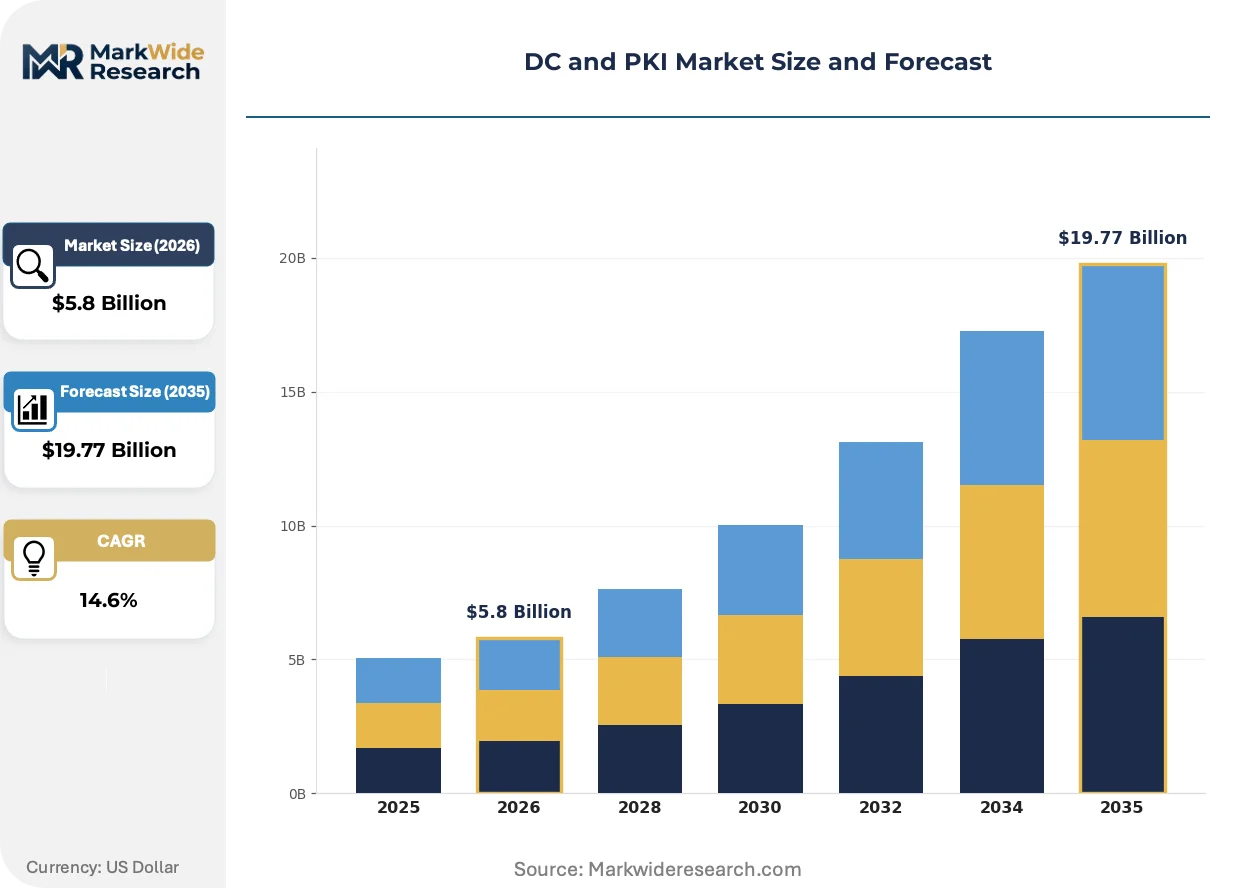
| Market Size in 2026 | $5.8 Billion |
| Market Size in 2035 | $19.77 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Public Key Infrastructure, Multi-Factor Authentication, Digital Signing, Certificate Management Application: Secure Email, Data Encryption, User Authentication, Document Integrity Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government Agencies, Financial Institutions, Healthcare Providers, Enterprises |
| Companies Covered | Thales, Google LLC, DigiCert, Keyfactor, HID Global Corporation, Amazon Web Services, Entrust Corporation, Venafi, Microsoft Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
DC and PKI Market Strategic Shifts
Distributed ledger technologies are reconfiguring certificate transparency and revocation workflows. These architectural shifts are displacing centralized trust models with cryptographic verification mechanisms that reduce single points of failure.
Blockchain-based certificate transparency logging is decentralizing the audit trail for TLS and code-signing credentials. Browser manufacturers and operating system vendors are mandating inclusion in public append-only logs before trust anchor acceptance. This architecture eliminates the opacity that enabled fraudulent certificate issuance by compromised authorities.
The EU AI Act's biometric identification provisions are forcing re-engineering of facial recognition and fingerprint matching systems. High-risk AI applications must satisfy conformity assessment procedures that extend to underlying PKI credentialing infrastructure. German automotive suppliers are pre-positioning qualified electronic signature modules to satisfy upcoming type-approval requirements for driver monitoring systems.
Enterprise buyers are consolidating certificate procurement under managed security service providers rather than maintaining direct authority relationships. This channel migration concentrates negotiation leverage with intermediaries who aggregate volume across multiple organizational tenants. Financial services firms in London and Singapore are driving this pattern through centralized procurement functions that mandate API-first delivery models.
DC and PKI Market Segmentation
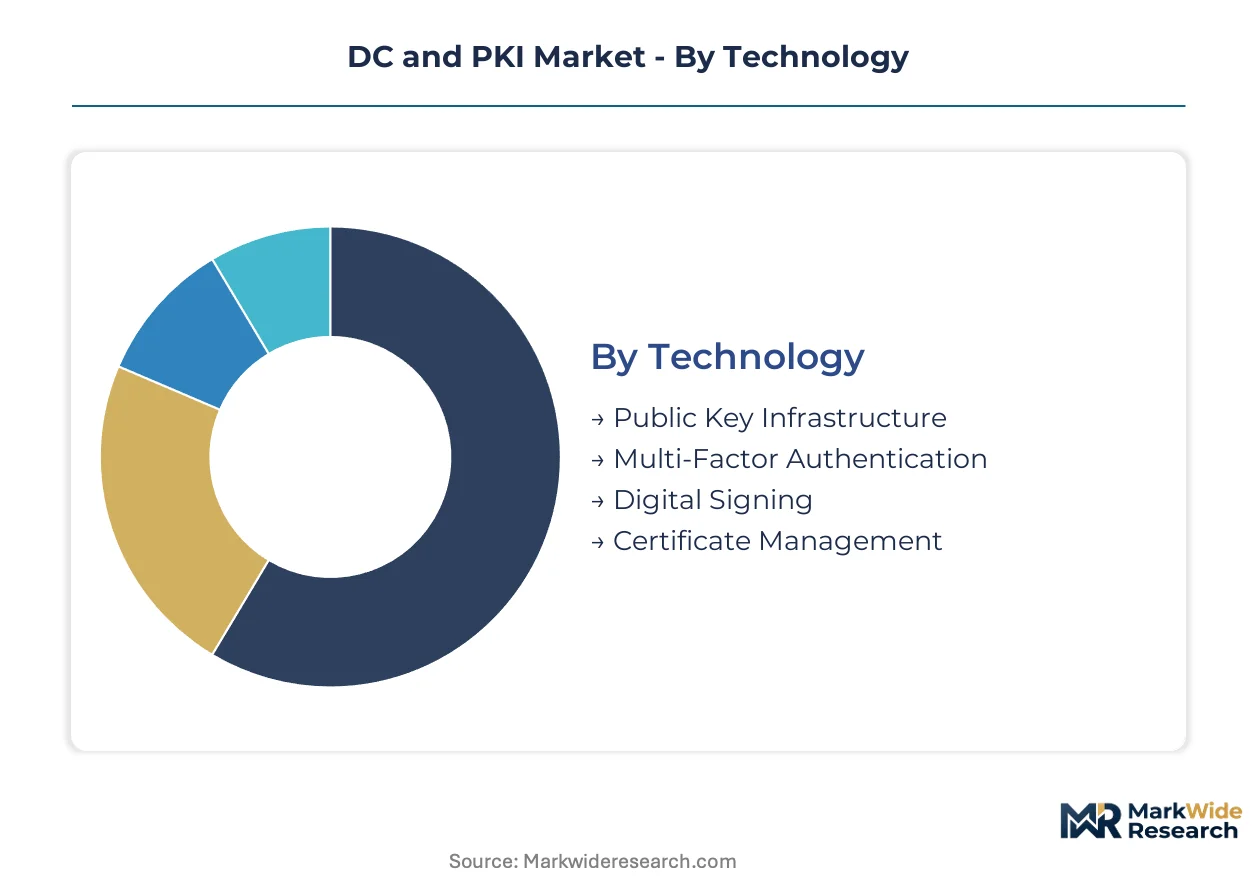
DC and PKI market segmentation reveals how cryptographic infrastructure fragments across deployment paradigms, end-user risk profiles, and application criticality. Supply-side specialization concentrates among hardware security module manufacturers, cloud-native platform vendors, and hybrid integration specialists serving distinct procurement workflows.
Technology:
Hardware security module fabrication concentrates among Taiwan-based foundries and European defense contractors, creating tiered availability by certification level.
- Public Key Infrastructure:Root-of-trust architectures anchor certificate hierarchies through certificate authorities and registration authorities operating X.509 standards. German automotive and industrial enterprises deploy quantum-resistant PKI at scale to satisfy type-approval requirements under evolving regulatory frameworks.
- Certificate Management:Automation platforms enforce policy workflows across certificate lifecycle events including provisioning, renewal, and revocation. Financial institutions in London and Singapore consolidate procurement under API-first managed security service providers to reduce operational overhead.
- Multi-Factor Authentication:Combines possession, knowledge, and inherence factors through hardware tokens, biometrics, and push notifications.
- Digital Signing:Cryptographic non-repudiation mechanisms bind identity to document integrity using qualified electronic signatures.
Today's leader: Public Key Infrastructure. Tomorrow's challenger: Certificate Management.
Application:
End-use concentration varies by regulatory exposure, with financial transaction integrity commanding premium pricing over internal enterprise workflows.
- User Authentication:Identity verification systems gate network access through credential validation against directory services. Healthcare providers deploy FIPS 140-3 certified modules to satisfy HIPAA obligations for workforce access control.
- Data Encryption:Cryptographic protection of data at rest and in transit using symmetric and asymmetric algorithms. Energy and transport sectors under NIS2 Directive mandates accelerate procurement of auditable encryption infrastructure.
- Secure Email:S/MIME and PGP protocols protect message confidentiality and sender authenticity.
- Document Integrity:Hash-based verification ensures contractual and regulatory submissions remain tamper-evident.
User Authentication commands current revenue concentration. Data Encryption exhibits the steepest expansion trajectory under compliance pressure.
Deployment:
Capital intensity thresholds separate segments, with cloud-native delivery capturing mid-market enterprises lacking dedicated security operations centers.
- Cloud-Based:Elastic, API-driven certificate services eliminate hardware maintenance burdens through subscription consumption models. Mid-market enterprises abandon on-premises capital expenditure for operational expenditure flexibility.
- Hybrid:Combines on-premises root-of-trust with cloud-delivered edge services for regulated financial workflows. Hybrid architectures satisfy data residency requirements while enabling centralized policy enforcement.
- On-Premises:Dedicated hardware security modules and certificate authorities maintained within organizational boundaries.
- Managed Services:Outsourced operation of PKI infrastructure by specialized security providers.
Cloud-Based deployment is gaining share fastest among new implementations. Hybrid architectures defend position in regulated sectors.
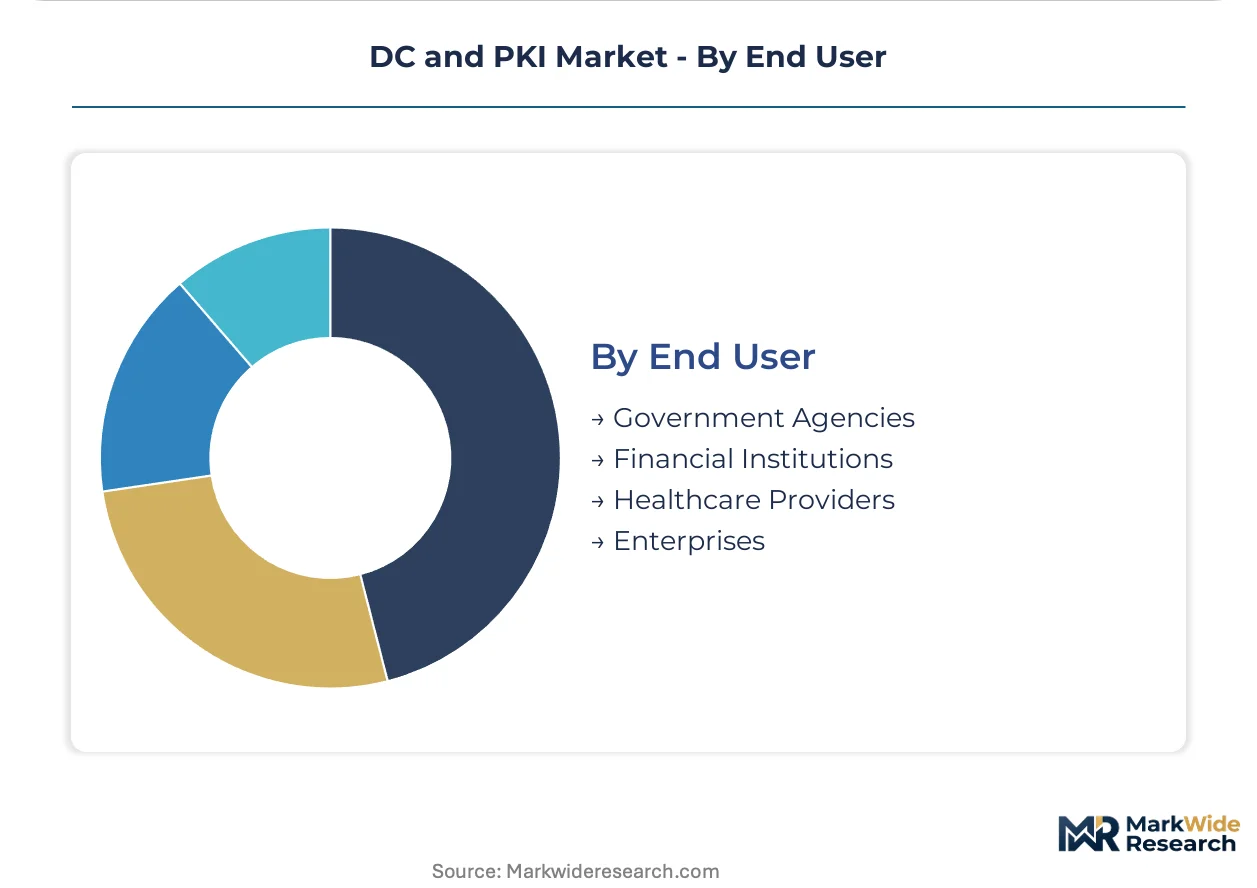
End User:
Procurement authority centralization varies, with financial services consolidating under chief information security officers while government agencies maintain distributed acquisition.
- Financial Institutions:Mandate FIPS 140-3 Level 3 certified transaction signing devices to satisfy SEC cybersecurity disclosure obligations. Hardware security module procurement accelerates as institutions modernize certificate infrastructure ahead of post-quantum migration deadlines.
- Government Agencies:Require sovereign cryptographic control through national certificate authorities and qualified trust service providers. Defense and intelligence procurement channels favor domestic hardware security module manufacturing.
- Healthcare Providers:Balance HIPAA compliance with interoperability requirements for health information exchange.
- Enterprises:Span verticals with heterogeneous risk profiles and certificate volume requirements.
Financial Institutions anchor premium segment revenue. Government Agencies present longest sales cycles but highest contract values.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German automotive and industrial enterprises anchor demand concentration for quantum-resistant certificate architectures as regulatory enforcement windows compress procurement timelines across critical infrastructure sectors.
United States
Financial institutions in New York and Chicago accelerate hardware security module procurement for transaction signing under SEC cybersecurity disclosure rules. NIST post-quantum migration standards compress enterprise certificate refresh cycles. Silicon Valley cloud providers dominate API-driven certificate service delivery to mid-market enterprises.
Germany
Automotive manufacturers in Munich and Stuttgart integrate quantum-resistant PKI into V2X communication stacks for type-approval compliance. The EU AI Act and NIS2 Directive mandate auditable identity verification across energy and transport infrastructure. Industrial enterprises in the Ruhr region deploy FIPS 140-3 Level 3 certified modules at scale.
United Kingdom
London-based financial services firms consolidate certificate procurement under managed security service providers demanding API-first delivery models. The country's national cybersecurity center publishes guidance on post-quantum cryptographic migration timelines. Fintech clusters in Manchester and Edinburgh drive cloud-native adoption for operational expenditure flexibility.
India
The central identity regulator expands PKI coverage to agricultural commodity exchanges and pharmaceutical supply chains through digital public infrastructure initiatives. Mumbai financial institutions mandate hybrid credentialing systems for regulated workflows. Bangalore technology enterprises consume elastic certificate services for cloud-native application deployment.
Japan
Automotive suppliers in Nagoya and Tokyo pre-position qualified electronic signature modules for driver monitoring system type-approvals under evolving biometric identification frameworks. METI standards guide post-quantum cryptographic transition timelines for critical infrastructure operators. Osaka-based industrial conglomerates maintain on-premises root-of-trust architectures for data residency compliance.
DC and PKI Market Competitive Environment
Strategic partnerships dominate the current landscape as vendors bridge hardware fabrication constraints with cloud-native delivery capabilities. The vendor base concentrates among three tiers: defense contractors with sovereign manufacturing capabilities, hyperscale cloud operators with API infrastructure, and specialized certificate lifecycle management platforms. Competitive positioning crystallizes around post-quantum cryptographic readiness and FIPS certification depth. M&A activity targets boutique algorithm specialists while geographic expansion concentrates on India's digital public infrastructure and European NIS2 compliance markets.
Among defense-oriented hardware security module fabricators, Thales occupies a position exemplifying sovereign cryptographic control through European manufacturing footprints. DigiCert and Entrust Corporation represent the hybrid-deployment archetype, anchoring credentialing systems that span on-premises root-of-trust with cloud-delivered edge services for regulated financial workflows. These three entities illustrate the competitive tension between hardware-centric assurance and software-defined agility that defines procurement decision frameworks across financial institutions and government agencies.
| Leading Market Players |
|---|
| Thales |
| Google LLC |
| DigiCert |
| Keyfactor |
| HID Global Corporation |
| Amazon Web Services |
| Entrust Corporation |
| Venafi |
| Microsoft Corporation |
| Others |
Value Chain & Pricing Dynamics
Post-quantum cryptographic migration simultaneously escalates R&D cost burdens for hardware security module manufacturers and concentrates procurement leverage among FIPS 140-3 certified foundries. Taiwan-based semiconductor fabrication and European defense contractors now capture disproportionate margin from algorithm-transition anxiety across financial and automotive certificate buyers.
Pricing Analysis
Input-cost pass-through from dedicated cryptographic processor wafer fabrication dominates pricing dynamics for high-assurance modules. Three-tier pricing structure across FIPS 140-3 Level 4, Level 3, and Level 2 certification grades separates defense procurement from financial services and mid-market enterprise segments. Cost compression in cloud-native certificate services is intensifying because API-driven platforms displace capital-intensive on-premises hardware. Mid-market enterprises exhibit highest price sensitivity; government agencies under sovereign cryptographic mandates demonstrate lowest elasticity.
Supply Chain Analysis
Freight cost escalation for tamper-evident hardware shipment from Taiwan and Germany to global certificate authority integration points adds 8-12% landed cost variance. Manufacturing concentration in Taiwan, Germany, and the United States draws from silicon wafer substrates, cryptographic co-processor IP cores, and tamper-responsive mesh enclosures. Single-source vulnerability at Taiwan-based foundries creates supply chain risk for FIPS 140-3 Level 3 and above module production. Distribution runs through managed security service providers who aggregate volume across multiple organizational tenants.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The DC and PKI market functions as a regulatory compounder where NIS2 Directive enforcement deadlines crystallize procurement mandates into predictable hardware security module demand waves.
For Market Incumbents: Hedge against post-quantum cryptographic expertise scarcity by acquiring lattice-based algorithm specialists before NIST migration standards compress enterprise refresh cycles. Anchor manufacturing capacity in European sovereign facilities to satisfy defense and intelligence procurement channels that reject Taiwan-dependent supply chains. Certification depth in FIPS 140-3 Level 4 represents the critical defensive lever against cloud-native platform erosion. For New Entrants and Emerging Players: The mid-tier pricing gap between Thales-grade sovereign hardware and commodity cloud certificates creates white-space opportunity for hybrid credentialing systems. India's digital public infrastructure expansion presents the most penetrable geography for API-first certificate lifecycle management platforms. Target agricultural commodity exchanges and pharmaceutical supply chains through regulator-aligned compliance automation as the primary go-to-market angle. For Investors and Strategic Acquirers: Valuations sit cheapest among boutique post-quantum cryptographic algorithm specialists lacking distribution scale but holding NIST-standard implementation expertise. Long-term viability across the projection horizon hinges on regulatory pre-positioning before enforcement windows crystallize into procurement mandates. Watch for EU AI Act biometric identification conformity assessment completion rates as the inflection signal for qualified electronic signature module demand acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Algorithm Patent Acquisition | Lattice-based cryptographic IP from NIST-standard contributors locks in government procurement channel access. |
| European Sovereign Manufacturing Footprint | Domestic HSM fabrication satisfies defense and intelligence procurement requirements under NIS2 Directive. |
| API-First Cloud Certificate Platform Launch | Elastic subscription models capture mid-market enterprises abandoning on-premises hardware maintenance burdens. |
| India Digital Public Infrastructure Partnership | Central identity regulator alignment opens agricultural and pharmaceutical PKI coverage expansion. |
| Hybrid Credentialing System Integration | Physical smart card issuance converged with mobile wallets serves regulated financial workflows in London and Singapore. |
Study Parameters
Multiple input streams — primary interviews with hardware security module procurement officers, certificate authority operations directors, and regulatory compliance leads; secondary validation through NIST post-quantum cryptographic standard filings, EU NIS2 Directive implementation guidance, and SEC cybersecurity disclosure rule interpretations; plus customs data on cryptographic processor trade flows — were reconciled through bottom-up certificate volume modeling and top-down infrastructure spend estimation.
Data-stream reconciliation across deployment model, certification level, end-user vertical, and regional regulatory cluster dimensions produced volume and value outputs throughout the forecast period. CAGRs were derived from algorithm migration timeline compression under NIST standards and NIS2 Directive enforcement windows. Post-quantum cryptographic patent filing velocity and FIPS 140-3 certification queue depth served as industry-specific forecast inputs.
Caveats apply where Taiwan semiconductor foundry capacity constraints, EU AI Act biometric re-certification delays, or legacy RSA/ECC embedded system depreciation cycles could materially shift the outlook. Stakeholders should weight assumptions against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Global User Provisioning Market
Security Software
Security Information and Event Management (SIEM) Market
Security Software
Next-Generation Intrusion Prevention System (NGIPS) Market
Security Software
Confidential Computing Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Encryption Software Market
Security Software
Software Assurance Market
Security Software
Cloud Identity and Access Management Software Market
Security Software
Video Intercom Devices Market
Security Software
Home Webcam Market
Security Software
Global Consumer Identity and Access Management Market
Security Software
Mobile Identity Management Market
Security Software
US and Latin America Identity and Access Management (IAM) Market
Security Software
Identity Governance and Administration Market