
 Network Sandboxing Market | 2026-2036
Network Sandboxing Market Size, Share, and Industry Trends Forecast 2026-2036
Network Sandboxing Market Foresight
Threat intelligence licensing revenue is reshaping competitive economics in network security. Palo Alto Networks leverages integrated platform architectures to sustain recurring revenue streams. Fortinet anchors its position through hardware-software bundling across distributed enterprise networks. Check Point Software Technologies specializes in unified threat management consoles that control channel pricing power.
Network sandboxing isolates suspicious files and executables within controlled virtual environments, executing code at CPU speeds up to native hardware performance while monitoring behavioral artifacts including registry modifications, network callbacks, and memory injection patterns to preemptively neutralize zero-day malware before production system contact. Cloud-based deployment models are capturing fastest growth as elastic compute resources reduce capital barriers for mid-market adopters, while on-premise installations retain margin concentration in regulated sectors requiring air-gapped data sovereignty. Behavioral analysis technology leads solution differentiation through dynamic execution tracing, though machine learning integration is accelerating automated verdict accuracy improvements.
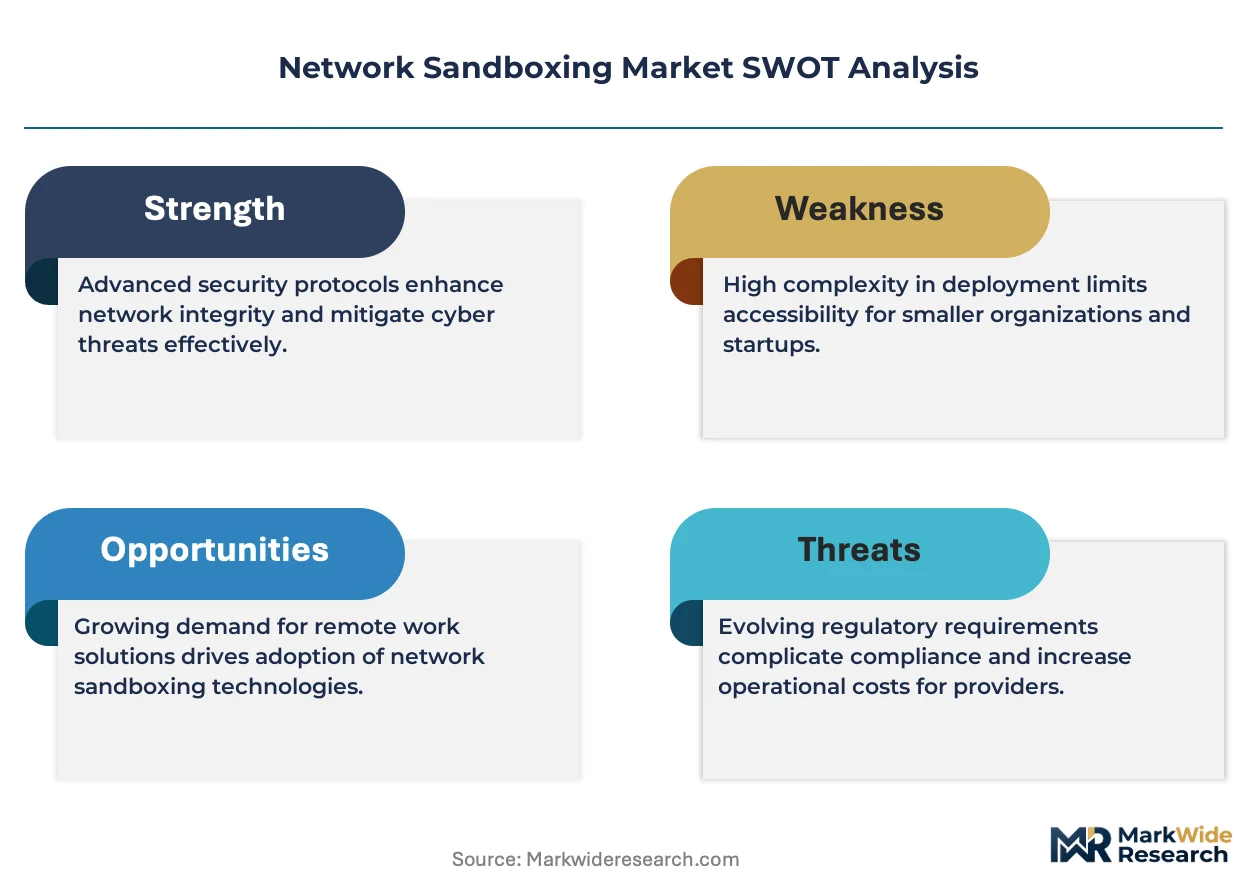
The EU AI Act and NIS2 Directive mandate algorithmic transparency and incident reporting timelines that reshape product development roadmaps for European deployments. The US NIST Cybersecurity Framework and SEC disclosure rules elevate board-level accountability for breach detection latency, directly influencing procurement specifications. Stakeholders must weigh sovereign cloud requirements against AI-enhanced detection velocity when architecting multi-tenant security stacks.
Market Dynamics
Cloud-native sandbox architectures are compressing deployment timelines from months to days, forcing incumbent vendors to restructure pricing models and channel economics around consumption-based metering rather than perpetual licensing.
Growth Catalysts
- EU AI Act enforcement:Financial institutions across member states must deploy algorithmic transparency tools for automated threat detection, mandating sandbox validation for AI-driven security decisions before production deployment.
- Behavioral analysis integration:Dynamic execution tracing now operates at native CPU speeds, enabling real-time malware verdicts without latency penalties that previously drove false-negative tolerance.
- Frankfurt banking cluster:Germany's concentration of systemically important financial institutions generates concentrated procurement for sovereign cloud sandbox deployments with air-gapped data residency requirements.
Market Restraints
- Elastic compute cost volatility:Cloud-based sandbox operations expose mid-market adopters to unpredictable egress and processing fees that erode budget predictability versus fixed-capital on-premise alternatives.
- Threat actor countermeasures:Evasive malware employing environmental awareness and anti-virtualization techniques reduces sandbox detection efficacy, forcing continuous engine redevelopment cycles.
- NIS2 Directive compliance timelines:Accelerated incident reporting mandates compress vendor certification windows, creating bottlenecks for product roadmap execution across European deployments.
Strategic Opportunities
- Operational technology convergence:Industrial control system networks in manufacturing verticals present underpenetrated attack surfaces where IT-OT sandbox bridging enables unified threat visibility.
- API-first distribution:Security service edge platforms now embed sandbox verdicts as microservices, opening channel partnerships with zero-trust network access vendors previously outside traditional cybersecurity procurement.
- SEC disclosure rule acceleration:US public company boards face personal liability for breach detection latency, elevating sandbox procurement from operational IT spend to board-level risk governance priority.
Industry Challenges
- Malware reverse engineering talent scarcity:The specialized skill set combining assembly-level analysis with behavioral pattern recognition commands premium compensation that mid-tier security vendors struggle to match.
- Legacy SIEM integration friction:Enterprise security operations centers demand seamless telemetry flow from sandbox appliances into decades-old correlation engines, requiring costly custom connector development.
- Cross-border data sovereignty conflicts:Multi-tenant cloud architectures face jurisdictional fragmentation when threat samples contain personally identifiable information subject to divergent national privacy regimes.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Network Sandboxing Market |
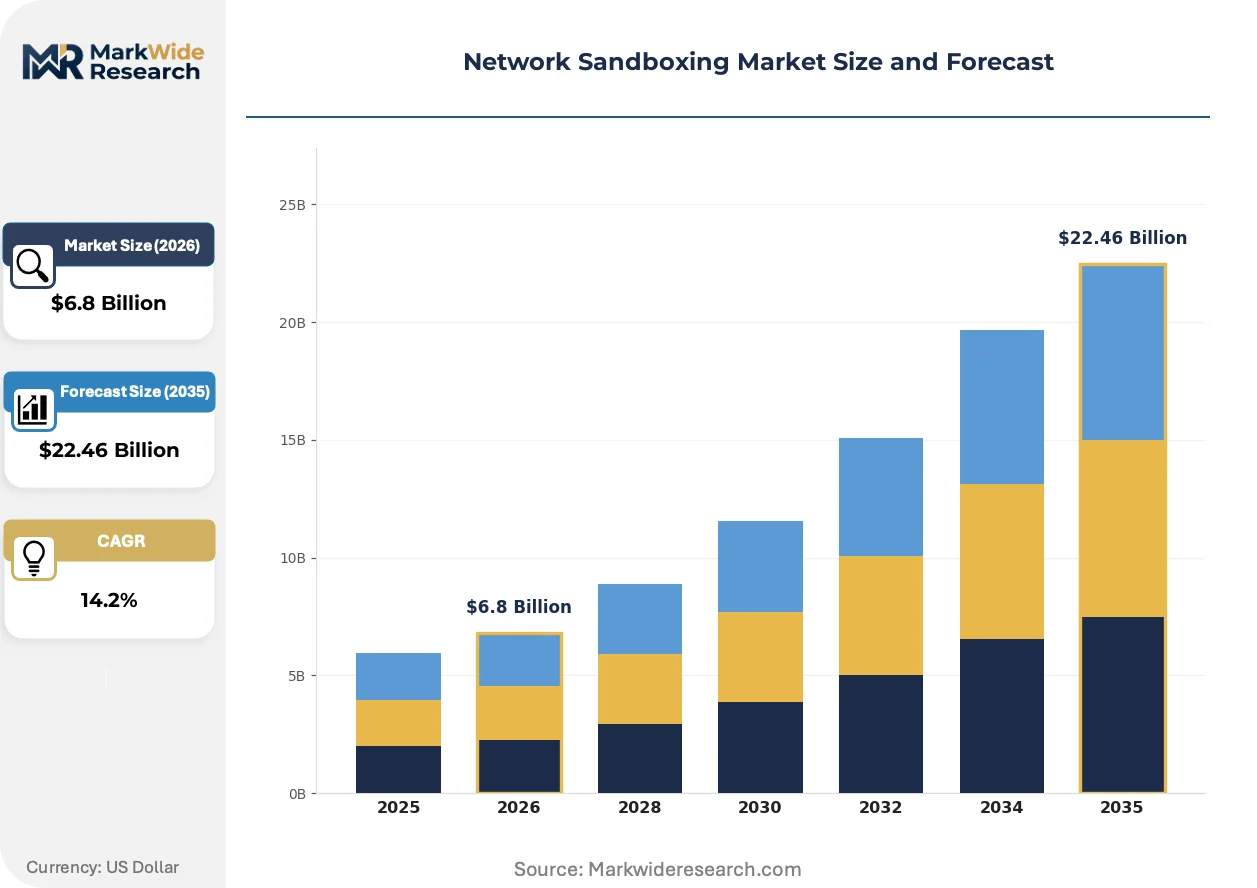
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $22.46 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premise, Cloud-Based, Hybrid, Virtual End User Type: Enterprises, Government Agencies, Managed Service Providers, Educational Institutions Solution Type: Endpoint Protection, Threat Intelligence, Security Analytics, Incident Response Technology: Behavioral Analysis, Machine Learning, Sandbox Environment, Malware Simulation |
| Companies Covered | Cisco Systems, Fortinet, Palo Alto Networks, Check Point Software Technologies, Symantec, Trend Micro, McAfee, Juniper Networks, Sophos, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Network Sandboxing Market Shifts & Advancements
Automated verdict generation is displacing human analyst review across enterprise security operations, compressing mean-time-to-response while elevating the strategic importance of false-positive rate optimization in vendor selection criteria.
Hardware-assisted virtualization extensions in modern server processors are digitizing sandbox execution environments, eliminating the performance gap between isolated analysis and native execution. Large financial institutions in London and Singapore now deploy these capabilities at scale for high-frequency transaction validation. The technology is digitizing threat detection economics by collapsing the cost per analyzed sample below manual review thresholds.
The EU AI Act's algorithmic transparency requirements are mandating explainable verdict logging for all automated security decisions affecting personal data. German and French regulators have issued supplementary guidance on sandbox logging retention periods. Financial services institutions in these jurisdictions now prioritize vendors with built-in audit trail generation over detection velocity alone.
Security procurement committees are consolidating vendor relationships around integrated platform architectures rather than best-of-breed point solutions. Enterprise buyers in the US and UK now demand sandbox capabilities embedded within broader secure access service edge contracts. This concentration favors vendors with existing zero-trust network presence over standalone specialists lacking distribution scale.
Network Sandboxing Market Segmentation
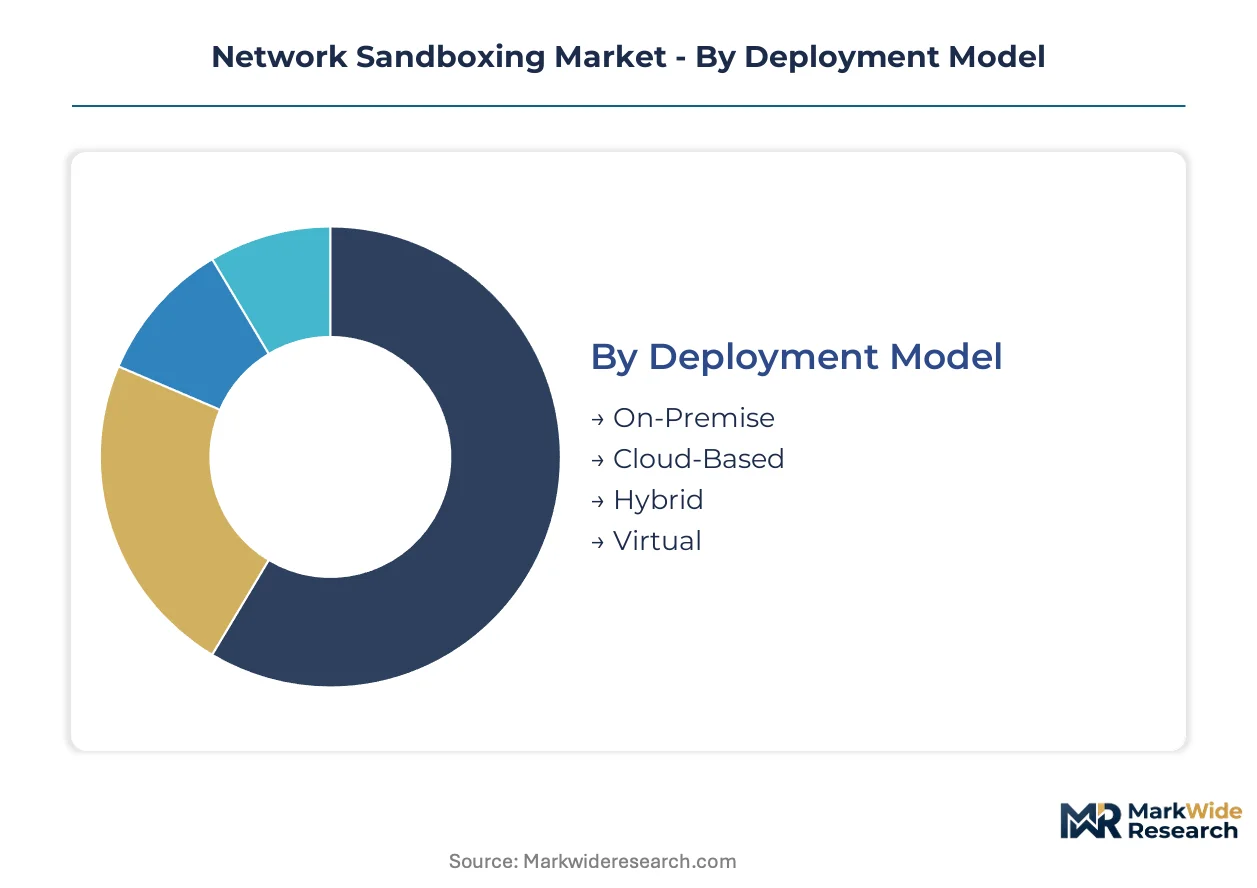
Network sandboxing procurement cycles vary dramatically across deployment architectures and user profiles. Solution providers structure R&D roadmaps around these divergent refresh timelines, with cloud-native offerings compressing sales cycles while regulated verticals extend evaluation periods.
Deployment Model:
Cloud-based deployments turn over fastest as elastic consumption models enable rapid scaling decisions; on-premise installations exhibit the longest replacement cycles due to capital amortization schedules.
- On-Premise:Dedicated hardware appliances execute malware analysis within air-gapped data centers, preserving complete telemetry control. Financial institutions in Frankfurt and Singapore maintain these installations for transaction validation workflows subject to sovereign data mandates.
- Cloud-Based:Elastic compute pools spin isolated execution environments on demand, eliminating upfront infrastructure commitments. Mid-market enterprises across Germany and France adopt these configurations to bypass capital expenditure approvals.
- Hybrid:Split architectures route routine analysis to cloud resources while reserving sensitive samples for on-premise inspection. Manufacturing conglomerates with OT-IT convergence requirements favor this model for operational continuity.
- Virtual:Software-defined sandboxes deploy atop existing hypervisor infrastructure without dedicated appliances. Educational institutions leverage campus virtualization licenses to extend security coverage.
On-premise configurations dominate installed base. Cloud-based deployment is where expansion concentrates.
End User Type:
Procurement sophistication stratifies sharply across buyer categories, with government agencies imposing the most stringent certification requirements and managed service providers optimizing for multi-tenant economics.
- Enterprises:Fortune 500 security operations centers integrate sandbox verdicts into SOAR platforms for automated response orchestration. German automotive manufacturers embed these capabilities within supplier risk management programs.
- Government Agencies:National security and civilian departments mandate FedRAMP or equivalent sovereign certifications before contract award. French defense procurement channels specify sandbox isolation for classified network segments.
- Managed Service Providers:Multi-tenant architectures enable per-customer sandbox instances with segregated verdict databases. UK-based MSSPs bundle these services into GDPR-compliant security packages for SME clients.
- Educational Institutions:University research networks face targeted academic espionage campaigns requiring malware analysis for intellectual property protection. US R1 institutions prioritize integration with existing identity federation systems.
Enterprise buyers anchor current revenue. Managed service providers are climbing the fastest.
Solution Type:
Margin profiles diverge substantially across functional modules, with threat intelligence commanding premium pricing while incident response solutions compete on automation depth.
- Endpoint Protection:Integrated agents extend sandbox verdicts to laptop and server fleets without separate analysis infrastructure. Healthcare delivery organizations deploy these for medical device security.
- Threat Intelligence:Curated indicator feeds and attribution analysis supplement raw sandbox outputs with contextual risk scoring. London-based financial exchanges subscribe to these services for preemptive blocking.
- Security Analytics:Correlation engines aggregate sandbox telemetry with network flow data for attack chain reconstruction. Singaporean sovereign wealth funds employ these for insider threat detection.
- Incident Response:Automated containment playbooks trigger from sandbox verdicts to isolate compromised endpoints. US critical infrastructure operators mandate these capabilities under SEC disclosure preparedness programs.
Endpoint protection commands largest installed base. Threat intelligence is where expansion concentrates.
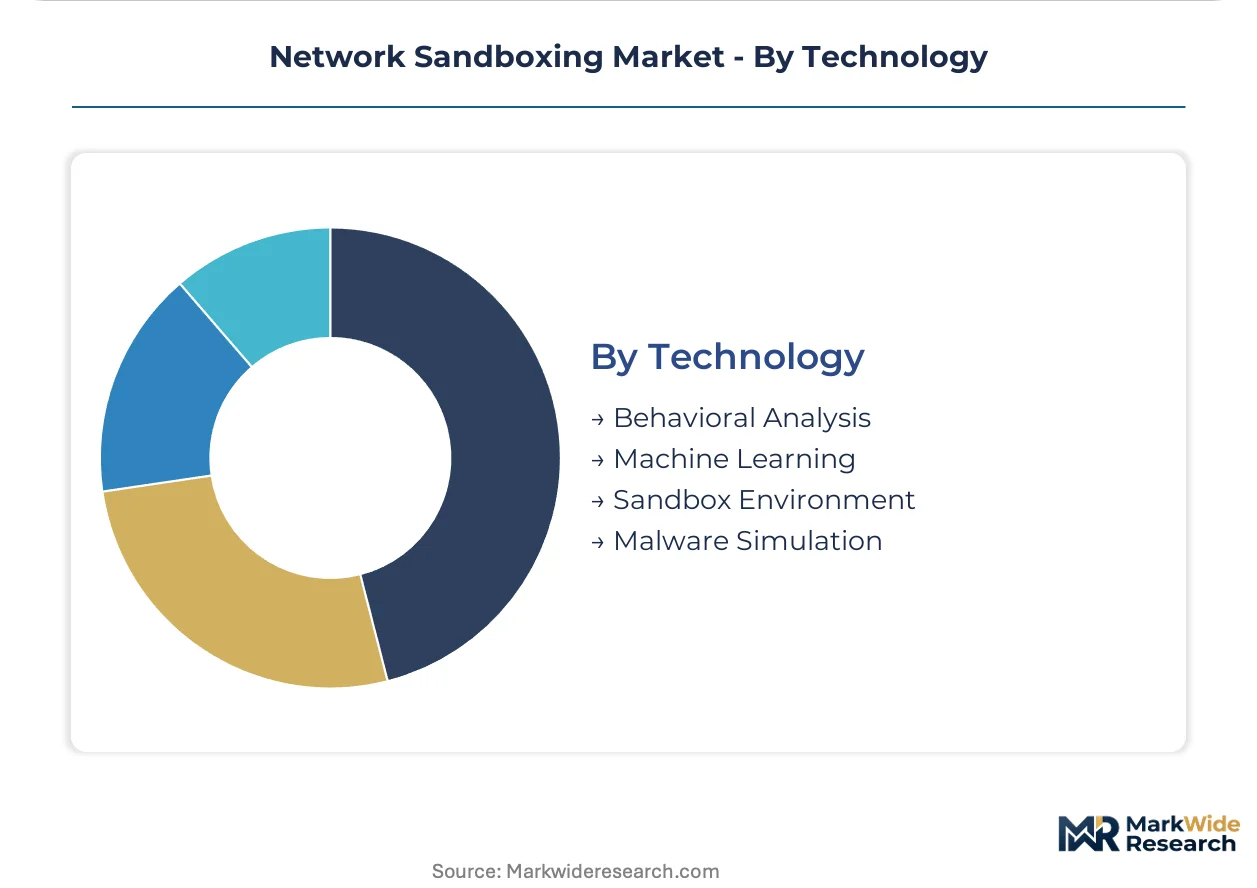
Technology:
Development velocity varies across detection methodologies, with machine learning models requiring continuous retraining while behavioral signatures stabilize over longer horizons.
- Behavioral Analysis:Dynamic execution tracing monitors API calls, registry modifications, and network callbacks during sample detonation. German banking regulators require these logs for algorithmic transparency compliance.
- Machine Learning:Neural classifiers score static and dynamic features for verdict acceleration without full execution. French cloud security vendors integrate these for EU AI Act explainability requirements.
- Sandbox Environment:Hardware-assisted virtualization extensions eliminate performance penalties between isolated and native execution. Singaporean high-frequency trading firms deploy these for sub-millisecond transaction validation.
- Malware Simulation:Synthetic attack generation tests sandbox detection efficacy against evasive techniques. US defense contractors employ these for red team exercises and control validation.
Behavioral analysis anchors installed base. Machine learning is gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Mid-market buyers in France and Germany exhibit the sharpest price elasticity for cloud-based deployments, while Singaporean sovereign wealth funds and Frankfurt banking consortia absorb premium pricing for air-gapped sovereignty.
United States
SEC disclosure rules and NIST Cybersecurity Framework mandates drive board-level procurement urgency for breach detection latency reduction. The SEC's personal liability provisions for directors accelerate sandbox adoption beyond operational IT budgets. New York financial exchanges and Silicon Valley cloud security vendors anchor the largest enterprise deployment base.
Germany
The EU AI Act and NIS2 Directive impose algorithmic transparency requirements that reshape product roadmaps for automated threat detection. Frankfurt's banking cluster concentrates systemically important financial institutions demanding sovereign cloud deployments with strict data residency. Baden-Württemberg automotive manufacturers embed sandbox capabilities within supplier risk management frameworks.
United Kingdom
GDPR-compliant security packages from London-based managed service providers bundle sandbox verdicts for mid-market SME clients. The Financial Conduct Authority's operational resilience requirements tighten incident response timelines for City trading firms. Manchester and Edinburgh technology corridors host emerging cybersecurity vendors targeting financial services verticals.
Singapore
Monetary Authority of Singapore guidelines for financial sector cyber resilience mandate sub-millisecond transaction validation capabilities. Hardware-assisted virtualization extensions deploy at scale among Marina Bay high-frequency trading operations. Sovereign wealth funds in the central business district employ advanced behavioral analytics for insider threat detection programs.
France
ANSM and CNIL supplementary guidance on sandbox logging retention periods prioritizes vendors with built-in audit trail generation. French defense procurement channels specify isolated sandbox deployments for classified network segments. Parisian cloud security vendors integrate machine learning classifiers to satisfy EU AI Act explainability mandates.
Network Sandboxing Market Competitive Landscape
Integrated platform vendors and standalone specialists split the market between consolidation-resistant enterprise accounts and best-of-breed procurement channels. The vendor base clusters around three strategic archetypes: hardware-software bundlers leveraging distributed network presence, unified threat management console providers controlling channel pricing power, and API-first microservice embedders penetrating zero-trust network access partnerships. Dominant competitive moves include M&A for behavioral analysis engine acquisition and strategic partnerships with security service edge platforms.
Among North American platform vendors, Palo Alto Networks and Cisco Systems exemplify the integrated architecture archetype, while Fortinet occupies a distinct position anchoring hardware-software bundling strategies. Check Point Software Technologies represents the unified console specialization that commands pricing leverage through channel control. These three entities collectively illustrate how distribution scale and platform breadth determine competitive viability against standalone specialists lacking embedded zero-trust network presence.
| Leading Market Players |
|---|
| Cisco Systems |
| Fortinet |
| Palo Alto Networks |
| Check Point Software Technologies |
| Symantec |
| Trend Micro |
| McAfee |
| Juniper Networks |
| Sophos |
| Others |
Supply & Pricing Matrix
Taiwan's semiconductor foundry cluster anchors hardware-assisted virtualization extension supply, concentrating cost leverage among sandbox appliance manufacturers who pass through component premiums to Frankfurt banking consortia and Singaporean sovereign wealth funds with limited price elasticity. This geographic concentration of processor supply creates asymmetric bargaining power that elevates capital expenditure thresholds for on-premise deployments while compressing margins for mid-market cloud-native alternatives.
Pricing Analysis
Extended threat intelligence licensing and managed detection response contracts drive lifetime value capture beyond initial appliance or subscription outlays. Three-tier pricing structure across premium sovereign-cloud, standard multi-tenant, and economy virtualized tiers segments buyer archetypes by data residency requirements and latency sensitivity. Cost compression in mid-market cloud tiers intensifies because hyperscaler compute commoditization erodes vendor differentiation. Government agencies and Frankfurt banking clusters exhibit least price sensitivity, while French and German mid-market enterprises show sharpest elasticity.
Supply Chain Analysis
US export controls on advanced GPU and AI accelerator technologies constrain hardware-assisted virtualization component flows to certain jurisdictions, forcing architectural workarounds. Taiwan, South Korea, and the United States concentrate high-performance processor fabrication that feeds sandbox engine development. Supply chains draw from specialized memory modules, cryptographic security processors, and behavioral analysis engine IP. Single-source vulnerability in advanced node semiconductor access threatens European deployment timelines. Distribution runs through OEM direct sales for enterprise accounts and security service edge platform embeds for cloud-native consumption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Network sandboxing is approaching a platform-economics inflection where API-first embeds into zero-trust architectures displace standalone procurement, driven by Palo Alto Networks and Cisco Systems consolidating security service edge ecosystems.
For Market Incumbents: Build switching-cost moats through SOAR platform pre-integration and FedRAMP certification depth. Fortify position by acquiring behavioral analysis engine specialists to counter evasive malware countermeasures. Anchor channel control through managed service provider co-development programs that embed sandbox verdicts as non-extractable microservices. For New Entrants and Emerging Players: Mid-market manufacturing conglomerates in Baden-Württemberg with OT-IT convergence requirements represent the most penetrable entry point for hybrid deployment architectures. Cloud-native API-first distribution through security service edge partnerships offers the lowest friction go-to-market angle against entrenched platform vendors. For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-compliance infrastructure play because EU AI Act and NIS2 Directive enforcement creates captive demand with limited substitution risk. Target acquisition candidates with pre-built algorithmic transparency logging and French ANSM audit trail certifications. Monitor SEC disclosure rule enforcement velocity as the signal indicating board-level procurement urgency inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedding sandbox verdicts into secure access service edge contracts captures zero-trust procurement consolidation. |
| Acquisition of Specialist Firm | Behavioral analysis engine purchases address evasive malware countermeasures compressing detection efficacy. |
| Geographic Expansion | Frankfurt sovereign cloud deployments satisfy EU AI Act data residency mandates for systemically important banks. |
| Strategic Partnership | API-first alliances with security service edge vendors open channels outside traditional cybersecurity procurement. |
| Product Launch | Hardware-assisted virtualization extensions eliminate latency penalties for Singaporean high-frequency trading validation. |
Research Methodology
Two parallel data streams informed the analysis: primary interviews with CISOs, security operations center directors, channel partners, and regulatory compliance officers; and secondary validation through SEC disclosure filings, EU NIS2 implementation guidance, hyperscaler capex disclosures, and behavioral analysis engine patent databases. Bottom-up deployment model sizing triangulated against top-down security software market allocations.
Forecast inputs considered deployment architecture elasticity, end-user procurement sophistication stratification, and technology development velocity across the projection horizon. Segmentation dimensions modeled include deployment model, end-user type, solution module, and detection methodology. CAGRs derived from regression analysis against historical security infrastructure spending patterns and regulatory compliance deadline clustering.
Practitioners should monitor EU AI Act enforcement timeline acceleration and evasive malware technique proliferation for early signals of demand inflection or detection efficacy degradation. Forecasts reflect assumptions about sovereign cloud certification velocity and hyperscaler compute pricing stability. Material shifts in export control regime stringency or NIS2 incident reporting mandate timelines would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
North America IoT Security Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Industrial Cybersecurity Market