
 Micro-Segmentation Solutions Market | 2026-2036
Micro-Segmentation Solutions Market Size, Share, and Industry Trends Forecast 2026-2036
Micro-Segmentation Solutions Market Foresight
Platform licensing revenue is narrowing as vendors bundle micro-segmentation into broader zero-trust suites. Illumio Inc. specializes in host-based segmentation for hybrid cloud environments. VMware Inc. leverages its hypervisor footprint to embed workload isolation natively. Cisco Systems Inc. anchors its position through network-layer enforcement integrated with existing switching infrastructure.
Micro-segmentation solutions partition network traffic into granular, policy-controlled zones using software-defined perimeters and identity-aware proxies. These systems enforce least-privilege access between workloads, containers, and endpoints through distributed firewalls and east-west traffic inspection. Cloud-based deployment is capturing the fastest expansion as organizations retire perimeter-centric architectures. Managed services within the solution-type dimension are accumulating margin pools as staffing shortages persist in enterprise security operations. Financial services dominates end-user adoption due to PCI DSS mandates and SWIFT customer security program requirements.
NIST, HIPAA, and PCI DSS collectively shape product roadmaps by mandating demonstrable network segregation for regulated data environments. The EU NIS2 Directive and GDPR cross-border processing rules are forcing European enterprises to adopt identity-aware segmentation with auditable policy trails. Stakeholders must weigh build-versus-buy decisions for policy orchestration engines as vendor consolidation accelerates.
Market Dynamics
The migration from perimeter-based firewalls to identity-aware micro-segmentation is compressing procurement cycles as federal mandates in the United States force rapid zero-trust adoption across critical infrastructure sectors.
Growth Catalysts
- NIST Zero-Trust Framework:Federal agencies and contractors face binding compliance deadlines that accelerate segmentation platform deployment across civilian and defense networks.
- Financial Services PCI DSS Mandates:Payment card networks require demonstrable network isolation for cardholder data environments, pushing banks and processors toward granular workload segmentation.
- Containerized Workload Proliferation:Kubernetes-native security policies now demand east-west traffic inspection between microservices that traditional perimeter controls cannot address.
Market Restraints
- Specialized Cybersecurity Talent Scarcity:Enterprise security operations centers lack sufficient staff fluent in policy orchestration engines and distributed firewall management.
- Legacy Network Infrastructure Inertia:Organizations with extensive Cisco and Juniper switching deployments face forklift upgrade costs to enable software-defined segmentation.
- Vendor Suite Consolidation Pressure:Buyers increasingly demand bundled zero-trust suites, squeezing standalone micro-segmentation licensing margins and forcing niche vendors toward acquisition.
Strategic Opportunities
- Operational Technology Convergence:Manufacturing and energy sectors are merging IT segmentation policies with industrial control system networks, creating demand for protocol-aware enforcement.
- EU NIS2 Directive Expansion:European critical infrastructure operators must implement auditable network segregation by late 2024, opening procurement windows across energy, transport, and healthcare.
- Managed Detection and Response Bundling:Security service providers are wrapping segmentation policy management into outsourced SOC offerings, capturing recurring revenue from staffing-constrained enterprises.
Industry Challenges
- Policy Sprawl Management:Organizations deploying segmentation across hybrid cloud environments struggle to maintain consistent least-privilege rules without creating operational bottlenecks.
- East-West Traffic Visibility Gaps:Encrypted internal communications between workloads complicate threat detection and policy verification for security operations teams.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Micro-Segmentation Solutions Market |
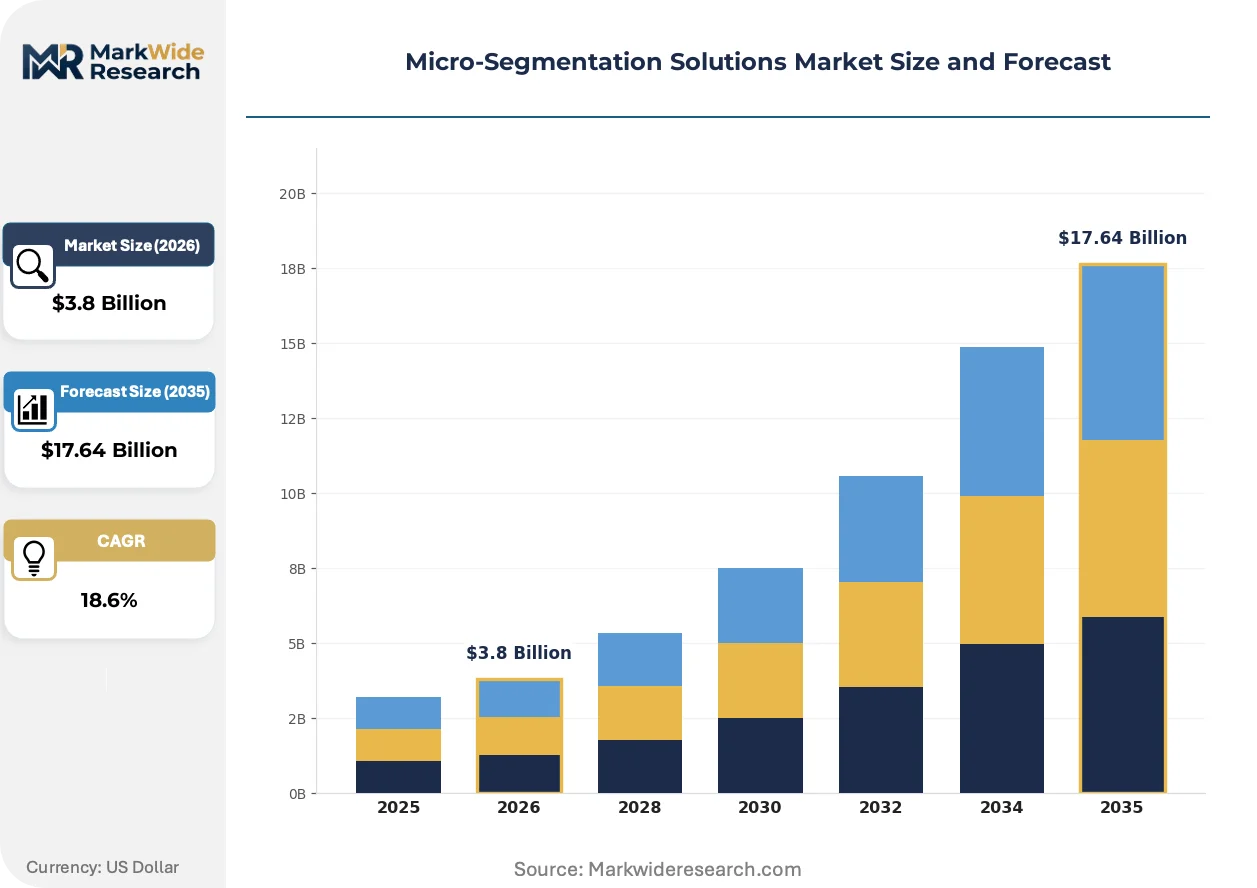
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.64 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-premises, Cloud-based, Hybrid, Multi-cloud Solution Type: Software, Subscription, Hardware, Managed Services End User: Financial Services, Healthcare, Retail, Manufacturing Compliance Standard: GDPR, HIPAA, PCI DSS, ISO 27001 |
| Companies Covered | Illumio Inc., VMware Inc., Cisco Systems Inc., Akamai Technologies Inc., Palo Alto Networks Inc., Fortinet Inc., Juniper Networks Inc., Dell Technologies Inc., ColorTokens Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Micro-Segmentation Solutions Market Shifts & Advancements
Artificial intelligence is transforming how segmentation policies are generated, tested, and enforced, reducing the manual overhead that has historically constrained deployment scale.
Agentless traffic inspection using cloud-native packet mirroring and virtual tap aggregation is rendering obsolete the requirement to install endpoint software on every protected workload. Large financial institutions in New York and London are piloting these techniques to accelerate cloud migration timelines without compromising compliance postures. The shift is compressing vendor evaluation cycles as buyers prioritize deployment velocity over feature depth.
The EU NIS2 Directive mandates network segmentation with auditable policy trails for operators of essential services across member states. Covered entities must demonstrate continuous compliance to national regulators or face operational penalties. German energy utilities and French healthcare networks are consolidating procurement authority at the CISO level to meet these obligations.
Security-conscious buyers now demand consumption-based licensing tied to protected workload counts rather than perpetual enterprise agreements. Channel partners and managed security providers are capturing this preference shift through utility-priced segmentation-as-a-service offerings. This pattern is most pronounced among mid-market healthcare providers in the United States seeking to align security spending with patient volume fluctuations.
Micro-Segmentation Solutions Market Segmentation
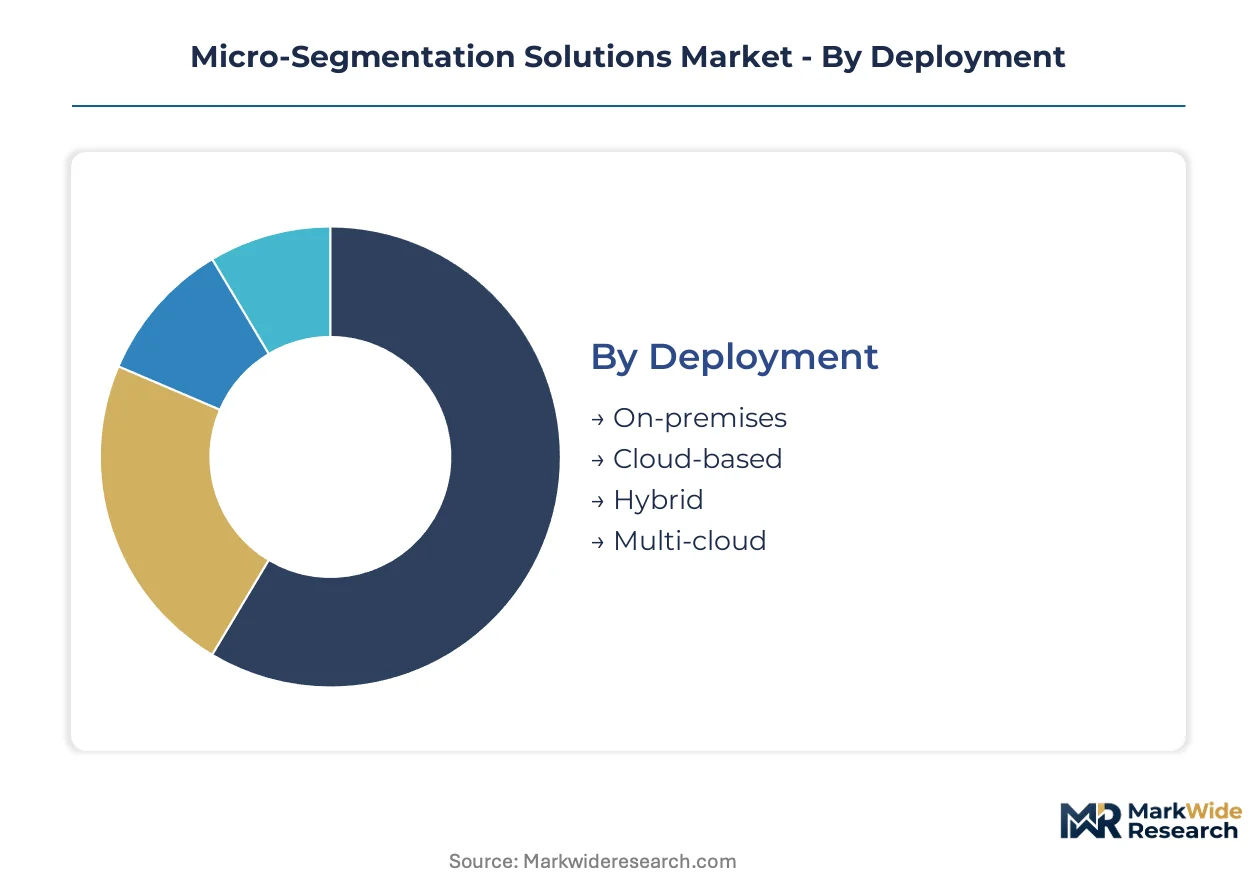
Micro-segmentation solutions serve divergent infrastructure maturity levels and regulatory exposure profiles across enterprise buyers. Deployment patterns, licensing models, and compliance mandates each reshape vendor product architecture and go-to-market economics in distinct ways.
Deployment:
Organizations span a use-case spectrum from air-gapped legacy data centers to fully ephemeral cloud-native environments, with segmentation architectures adapting to each operational reality.
- Cloud-based:Software-defined perimeters enforce identity-aware policies across AWS, Azure, and GCP workloads without hardware dependencies. Financial services firms in New York and London favor this model to compress cloud migration timelines while maintaining PCI DSS audit trails.
- Hybrid:Unified policy orchestration bridges on-premises VMware estates with public cloud instances through centralized control planes. Manufacturing conglomerates with legacy SCADA investments and nascent cloud strategies gravitate toward this architecture to avoid forklift infrastructure replacements.
- On-premises:Hardware-anchored enforcement remains prevalent in defense contractor networks and classified government facilities where data sovereignty requirements preclude cloud egress.
- Multi-cloud:Cross-platform consistency engines abstract policy definitions across heterogeneous cloud providers, appealing to enterprises hedging vendor lock-in risks.
The dominant share belongs to Cloud-based deployments, while Hybrid architectures are closing the gap fastest as enterprises pursue incremental modernization without abandoning sunk infrastructure investments.
Solution Type:
Cost tier differentiation separates perpetual license buyers from consumption-oriented adopters, with staffing constraints pushing mid-market buyers toward outsourced operational models.
- Managed Services:Third-party SOC teams assume policy lifecycle management, threat hunting, and compliance reporting burdens. Healthcare providers in the United States facing cybersecurity talent scarcity increasingly outsource segmentation operations to align spending with patient volume fluctuations.
- Subscription:Recurring revenue models tie pricing to protected workload counts, enabling budget predictability for seasonal businesses and growth-stage enterprises.
- Software:Perpetual licenses with annual maintenance contracts persist in regulated industries requiring demonstrable capital expenditure for audit purposes.
- Hardware:Purpose-built appliances survive in high-throughput financial trading environments where software packet inspection introduces unacceptable latency.
Managed Services command expanding margin pools as staffing shortages persist, though Subscription licensing is climbing fastest among cloud-native adopters prioritizing OpEx alignment.
End User:
Application-specific risk profiles and regulatory exposure dictate segmentation sophistication requirements across vertical markets.
- Financial Services:PCI DSS and SWIFT customer security program mandates drive granular cardholder data environment isolation. Tier-one banks deploy east-west traffic inspection between trading applications and settlement systems to contain lateral movement risks.
- Healthcare:HIPAA technical safeguards require auditable access controls for electronic protected health information. Hospital networks segment medical devices from administrative systems to prevent ransomware propagation.
- Retail:Point-of-sale network isolation and e-commerce payment gateway segmentation dominate procurement priorities.
- Manufacturing:Converged IT-OT segmentation policies protect industrial control systems from enterprise network-borne threats.
Financial Services retains the dominant share through compliance-driven refresh cycles, while Healthcare is gaining share fastest as medical device connectivity proliferates and ransomware targeting intensifies.
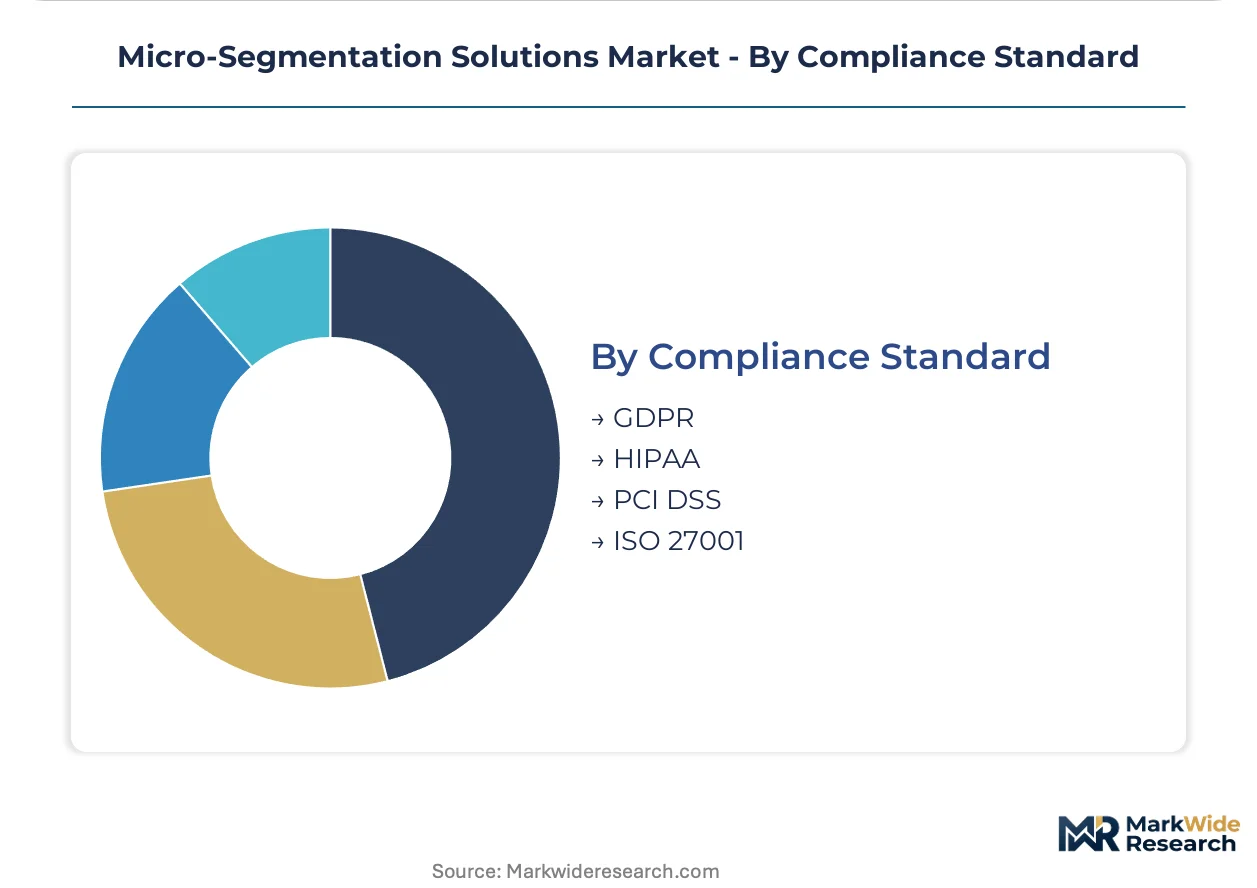
Compliance Standard:
Geographic jurisdiction and data sensitivity determine which certification frameworks shape segmentation policy design.
- PCI DSS:Payment card network mandates enforce network segmentation as a compensating control for cardholder data environments, with quarterly vulnerability scanning requirements driving continuous policy validation.
- GDPR:Cross-border processing rules and data localization requirements compel European enterprises to implement identity-aware segmentation with immutable audit trails for supervisory authority review.
- HIPAA:Technical safeguard specifications mandate access controls and audit logging for healthcare data environments.
- ISO 27001:Risk-based information security management systems incorporate network segmentation as a core control for asset protection.
PCI DSS anchors the largest addressable market through payment ecosystem ubiquity, while GDPR is expanding most quickly as NIS2 Directive implementation accelerates across European critical infrastructure operators.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Buyers in the United States show the least price elasticity due to federal compliance deadlines, while European procurement teams negotiate harder on licensing terms amid budget consolidation pressures.
United States
Federal zero-trust mandates and compressed cloud migration timelines drive urgent segmentation platform procurement across civilian agencies and defense contractors. NIST's cybersecurity framework imposes binding compliance deadlines that eliminate traditional vendor evaluation cycles. New York and Washington D.C. financial centers deploy east-west traffic inspection between trading applications to satisfy PCI DSS and SWIFT requirements.
Germany
Industrial conglomerates merge IT segmentation policies with operational technology networks to protect legacy SCADA investments from enterprise-borne threats. The EU NIS2 Directive compels critical infrastructure operators to implement auditable network segregation with immutable policy trails by late 2024. Frankfurt's financial district and Bavarian manufacturing clusters consolidate procurement authority at the CISO level to meet these obligations.
United Kingdom
London-based investment banks and insurance underwriters prioritize deployment velocity over feature depth to accelerate cloud migration without compromising GDPR cross-border processing compliance. The Financial Conduct Authority's operational resilience rules mandate demonstrable network isolation for critical business services. The City of London and Canary Wharf financial clusters pilot agentless traffic inspection techniques to reduce endpoint software overhead.
Japan
Manufacturing exporters and automotive suppliers adopt hybrid segmentation architectures to bridge on-premises VMware estates with nascent public cloud strategies. METI's cybersecurity guidelines for critical infrastructure operators emphasize identity-aware policy enforcement with centralized audit capabilities. Tokyo and Osaka industrial corridors concentrate demand for protocol-aware enforcement that spans IT and converged OT networks.
Australia
Healthcare networks and mining operators face ransomware targeting intensification that drives medical device isolation and remote site segmentation priorities. The country's critical infrastructure security obligations impose network segregation requirements for energy and transport operators with supervisory authority review provisions. Sydney and Melbourne enterprise clusters gravitate toward managed services models to address persistent cybersecurity staffing shortages.
Micro-Segmentation Solutions Market Competitive Landscape
Capability concentration sits with specialized segmentation vendors; scale advantage sits with infrastructure incumbents embedding workload isolation into broader platform suites. The market structure reflects a tiered dynamic where standalone micro-segmentation specialists compete against network hardware giants and cloud infrastructure providers. Three archetypes dominate: host-based segmentation specialists, hypervisor-native enforcement providers, and network-layer integration platforms. Consolidation pressure and bundled zero-trust suite expansion represent the dominant competitive vectors reshaping vendor positioning.
Within the specialization tier, Illumio Inc. and ColorTokens Inc. exemplify vendors anchoring their positions through host-based policy orchestration rather than infrastructure dependencies. VMware Inc. occupies a distinct position by leveraging hypervisor footprint to embed segmentation natively into workload virtualization layers. Cisco Systems Inc. represents the network-centric archetype, integrating enforcement capabilities with existing switching infrastructure to reduce forklift upgrade requirements for enterprise buyers.
| Leading Market Players |
|---|
| Illumio Inc. |
| VMware Inc. |
| Cisco Systems Inc. |
| Akamai Technologies Inc. |
| Palo Alto Networks Inc. |
| Fortinet Inc. |
| Juniper Networks Inc. |
| Dell Technologies Inc. |
| ColorTokens Inc. |
| Others |
Supply & Pricing Matrix
Silicon Valley's cybersecurity vendor concentration shapes downstream pricing power for micro-segmentation platforms, as hyperscaler partnerships and federal certification pipelines in the San Francisco Bay Area create tiered access to enterprise buyers. Subscription licensing dominates the market, with three-tier pricing structure across premium, standard, and economy levels differentiating by workload scale and compliance certification depth. Cost compression in the mid-market tier is intensifying because managed security providers bundle segmentation into broader SOC offerings. Healthcare networks in the United States show highest price sensitivity due to patient-volume-linked budgets, while defense contractors demonstrate lowest elasticity given binding NIST compliance deadlines.
Pricing Analysis
Long-term enterprise agreements anchor revenue for established vendors, though project-based deployment pricing gains traction among cloud-native adopters seeking consumption alignment. Price differentiation rests on ISO 27001 certification tier and geographic delivery cost for on-premises hardware components. Margins are tightening due to vendor suite consolidation pressure as buyers demand bundled zero-trust suites over standalone licenses. Financial services institutions in New York and London exhibit least price sensitivity given PCI DSS mandate urgency, while mid-market retailers face acute budget constraints.
Supply Chain Analysis
United States export-control regimes on cryptographic technologies constrain component flows to certain international markets, creating licensing friction for vendors with foreign national cloud footprints. Manufacturing concentrates in the United States, Israel, and Ireland for policy orchestration engine development, with hardware appliance fabrication anchored in Taiwan and Mexico. Raw material dependencies span specialized ASICs for packet inspection, encryption accelerators, and cloud compute capacity from hyperscaler partners. Single-source vulnerability in semiconductor supply chains for custom silicon poses structural risk. Distribution runs through channel partners and managed security service providers rather than direct enterprise sales.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Micro-segmentation solutions function as a defensive-moat market where switching costs and regulatory entrenchment protect incumbent positions. Network effects from policy template libraries and compliance certification accumulation create compounding advantages for established vendors.
For Market Incumbents: Entrench position through backward integration into managed detection and response services, capturing recurring revenue from staffing-constrained healthcare and financial services buyers. Deepen certification investment for EU NIS2 Directive compliance to lock out challengers in European critical infrastructure procurement windows. Counter emerging cloud-native entrants by embedding workload isolation natively into existing virtualization footprints, raising switching costs for hybrid cloud adopters.
For New Entrants and Emerging Players: Australian healthcare networks and mining operators present underpenetration white space where ransomware targeting intensification outpaces incumbent coverage. Target operational technology convergence in German manufacturing and Japanese automotive corridors where protocol-aware enforcement demands exceed current vendor specialization. Pursue segmentation-as-a-service positioning through utility-priced offerings to align with mid-market budget predictability preferences.
For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-entrenchment play because compliance mandate proliferation across NIST, PCI DSS, and EU NIS2 creates durable demand tailwinds independent of economic cycles. Acquisition targets should display host-based policy orchestration capabilities and existing federal certification pipelines. Monitor vendor consolidation velocity as standalone micro-segmentation specialists face margin compression from bundled suite competition.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedding workload isolation into VMware hypervisor layers reduces forklift upgrade friction for hybrid cloud adopters. |
| Acquisition of Specialist Firm | Consolidating host-based segmentation capabilities addresses talent scarcity in policy orchestration engine management. |
| Regulatory Certification Program | NIST zero-trust framework compliance opens federal agency procurement pipelines with compressed evaluation cycles. |
| Strategic Partnership | Hyperscaler alliances with AWS and Azure accelerate cloud-native deployment velocity for financial services migrations. |
| Geographic Expansion | EU NIS2 Directive readiness in Frankfurt and Paris captures critical infrastructure operator procurement windows. |
Research Methodology
A standing panel of CISOs, cloud architects, compliance officers, and managed security service provider executives provided ongoing calibration throughout the study period. Primary fieldwork combined structured interviews with secondary validation across SEC filings, NIST framework documentation, EU regulatory registers, and hyperscaler partner program disclosures. Bottom-up triangulation from workload deployment counts and top-down cross-check against enterprise IT security spending estimates anchored volume and value outputs.
Scenario-bracketing around federal compliance deadline acceleration and cloud migration timeline compression bounded the projection range across the analysis window. Segmentation dimensions modeled include deployment architecture, solution type, end-user vertical, and geographic regulatory cluster. CAGRs derived from policy engine installation trajectories and subscription renewal rate analysis, with inputs from Kubernetes-native security policy adoption curves and east-west traffic inspection penetration in financial trading environments.
Practitioners should monitor vendor consolidation announcements and hyperscaler native segmentation feature launches for early signals of pricing pressure inflection. Forecasts reflect assumptions regarding sustained regulatory mandate enforcement and cloud migration continuity. Material shifts in federal zero-trust implementation timelines or export-control regime expansion would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Container-based Firewall Market
Cybersecurity
Global API Security Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Home Wi-Fi Security Solutions Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Domain Name System (DNS) Firewall Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Threat Hunting Market