
 North America IoT Security Market | 2026-2036
North America IoT Security Market Size, Share, and Industry Trends Forecast 2026-2036
North America IoT Security Market Intelligence
Shortage of embedded security engineers is rotating talent premiums toward firms with dedicated firmware cryptography labs. Cisco Systems leverages its network hardware heritage to dominate cloud-native IoT segmentation. Palo Alto Networks anchors its position through zero-trust architecture specialization for operational technology environments. Claroty competes narrowly in industrial automation protocol inspection, sustaining differentiation where generalist platforms lack deep packet visibility into Modbus and DNP3 traffic.
North America IoT Security encompasses cryptographic protection, anomaly detection, and access governance for internet-connected sensors, actuators, and edge gateways operating across IP and non-IP industrial protocols, typically requiring sub-100-millisecond threat response latency to prevent physical system compromise. Its primary purpose is preserving data integrity and operational continuity in environments where device proliferation outpaces traditional perimeter defense. Network Security solutions occupy the largest installed base as enterprises retrofit legacy SCADA and building automation systems, while Edge Computing deployment models represent the fastest-expanding segment as manufacturers push inference closer to plant floors to reduce backhaul exposure. Identity Management tools command premium pricing in financial services and energy provider environments where device certificate lifecycle governance determines regulatory audit outcomes.
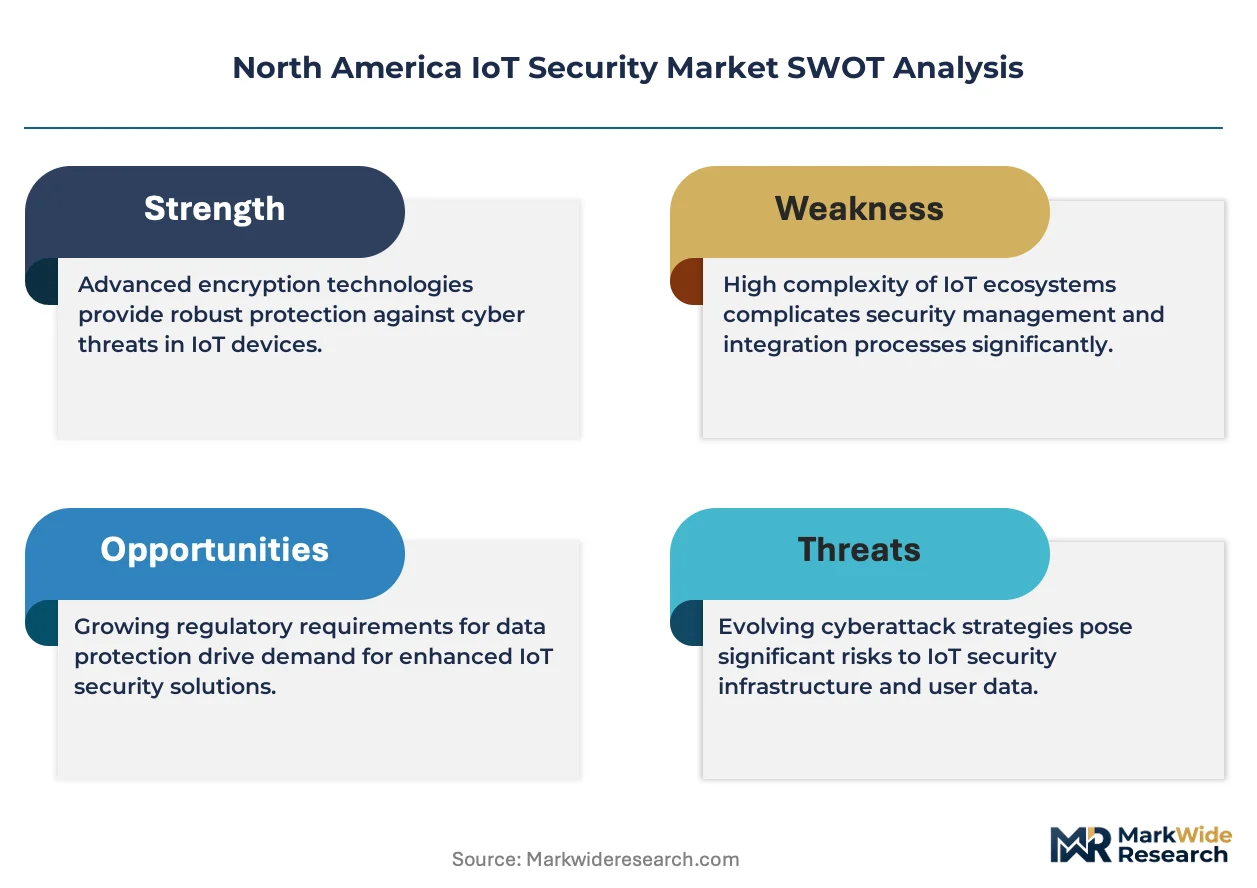
NIST, the FCC, and state attorneys general under California's SB-327 and similar statutes are mandating baseline password hygiene, vulnerability disclosure timelines, and encryption standards that reshape vendor product roadmaps and buyer procurement scorecards. The FDA's premarket guidance for connected medical devices adds parallel compliance layers for healthcare IoT deployments. Stakeholders must weigh cloud versus edge architectural bets against evolving federal procurement standards and sector-specific breach liability precedents.
Market Dynamics
Healthcare delivery networks across the United States are hardening procurement scorecards around NIST cybersecurity framework compliance, forcing vendors to embed firmware cryptography capabilities upstream or exit consideration cycles entirely.
Growth Catalysts
- SB-327 mandates:California's baseline password hygiene and encryption standards are disqualifying non-compliant devices from state agency and municipal procurement pipelines.
- Medical device connectivity:FDA premarket guidance for connected healthcare equipment is requiring vulnerability disclosure timelines that accelerate security-by-design investments.
- Silicon Valley corridor concentration:Venture deployment into firmware cryptography labs is creating talent pipelines that rotate toward IoT-native security architectures.
Market Restraints
- Embedded security engineer scarcity:Talent premiums concentrate among firms with dedicated firmware cryptography capabilities, compressing margins for generalist security vendors.
- Legacy SCADA retrofit costs:Industrial operators face capital intensity burdens when retrofitting decades-old Modbus and DNP3 systems with sub-100-millisecond threat response requirements.
- State-level regulatory fragmentation:Divergent breach notification timelines across Texas, California, and New York create compliance overhead for multi-state deployments.
Strategic Opportunities
- Texas medical device cluster expansion:Manufacturers near Houston and Dallas-Fort Worth are consolidating supply chains that demand localized security validation services.
- Edge inference convergence:Manufacturers pushing machine learning closer to plant floors require security architectures that reduce backhaul exposure without cloud dependency.
- Zero-trust architecture mandates:Federal procurement standards for operational technology environments are creating specification advantages for vendors with pre-certified segmentation capabilities.
Industry Challenges
- Certificate lifecycle governance complexity:Financial services and energy providers face audit failures when device identity management spans thousands of distributed endpoints with varying renewal cycles.
- Deep packet inspection skill scarcity:Industrial automation protocol expertise in Modbus and DNP3 traffic analysis remains concentrated among narrow specialists, limiting generalist platform expansion.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | North America IoT Security Market |
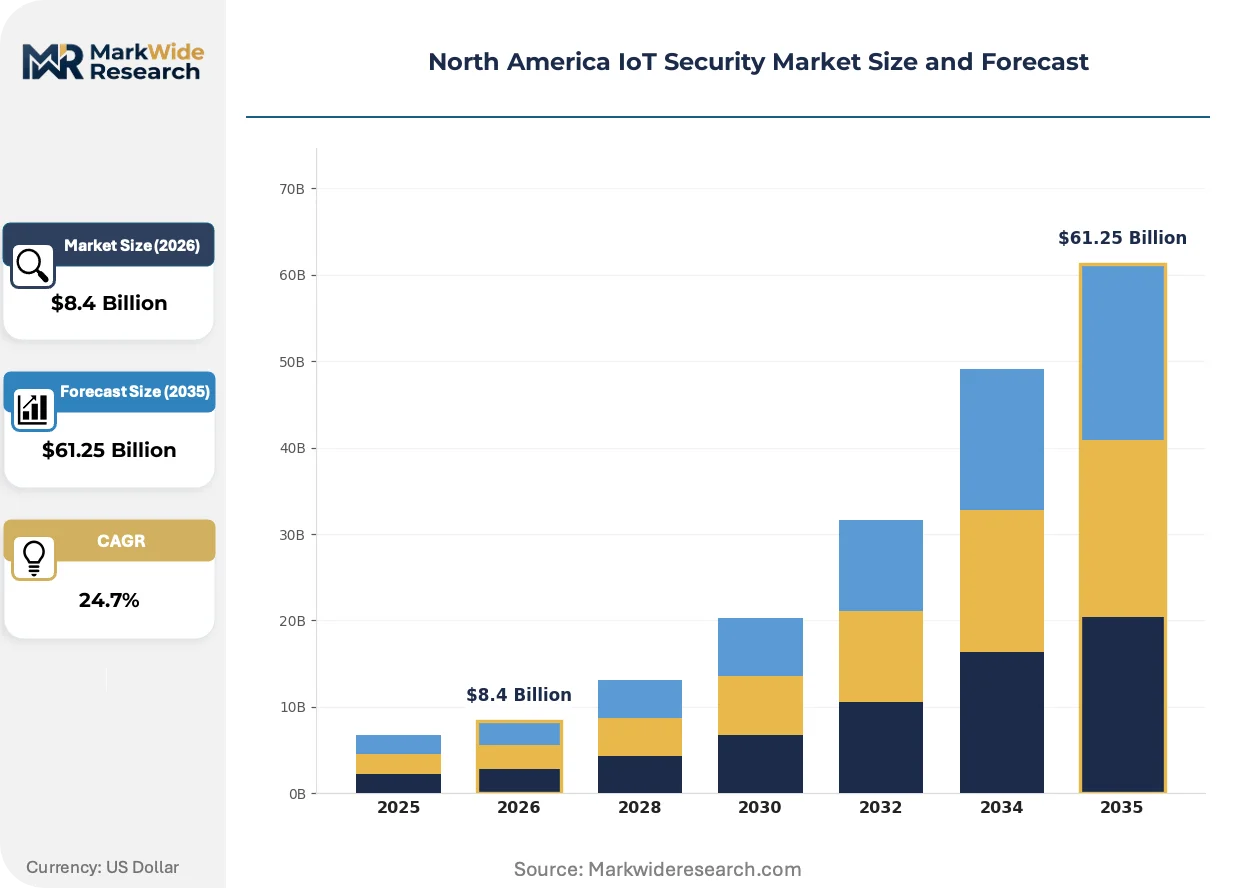
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $61.25 Billion |
| CAGR (2026 – 2036) | 24.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Network Security, Endpoint Protection, Identity Management, Data Encryption, Threat Intelligence, Access Control Application: Smart Homes, Connected Vehicles, Wearable Devices, Smart Grid, Industrial Automation, Retail Analytics Deployment Model: Cloud-Based, On-Premises, Hybrid, Edge Computing End User: Manufacturing Companies, Energy Providers, Financial Institutions, Government Agencies, Telecommunications Firms |
| Companies Covered | Cisco Systems, Palo Alto Networks, IBM Corporation, Symantec Corporation, Microsoft, Fortinet, Intel Corporation, Armis, Claroty, Others |
| Regions Covered | North America: US, Canada, Mexico |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
North America IoT Security Market Strategic Shifts & Innovations
Security architectures are compressing response latencies through hardware-rooted trust mechanisms, displacing software-only detection layers that cannot meet operational technology physical safety requirements.
Hardware security modules with embedded cryptographic accelerators are displacing pure software encryption stacks in medical device and energy grid deployments. Texas and California healthcare networks are adopting these modules at accelerated procurement cycles. The displacement is compressing vendor margins on traditional software licensing models while rewarding semiconductor-integrated security stacks.
NIST's post-quantum cryptography migration timelines are forcing firmware roadmap revisions across device manufacturers supplying federal healthcare and energy infrastructure. The industrial consequence is mandatory algorithm upgrades in field-deployed sensors with decade-long operational lifespans. Medical device vendors with FDA premarket submissions are most affected, responding by locking cryptographic agility into hardware abstraction layers.
Buyers are unbundling security validation from device procurement, creating standalone certification services that displace vendor-provided attestations. Industrial operators in the Texas medical device cluster are contracting third-party firmware penetration testing before accepting delivery. This pattern is most visible in Class II and Class III medical device supply chains where FDA audit documentation requirements exceed vendor standard disclosures.
North America IoT Security Market Segmentation
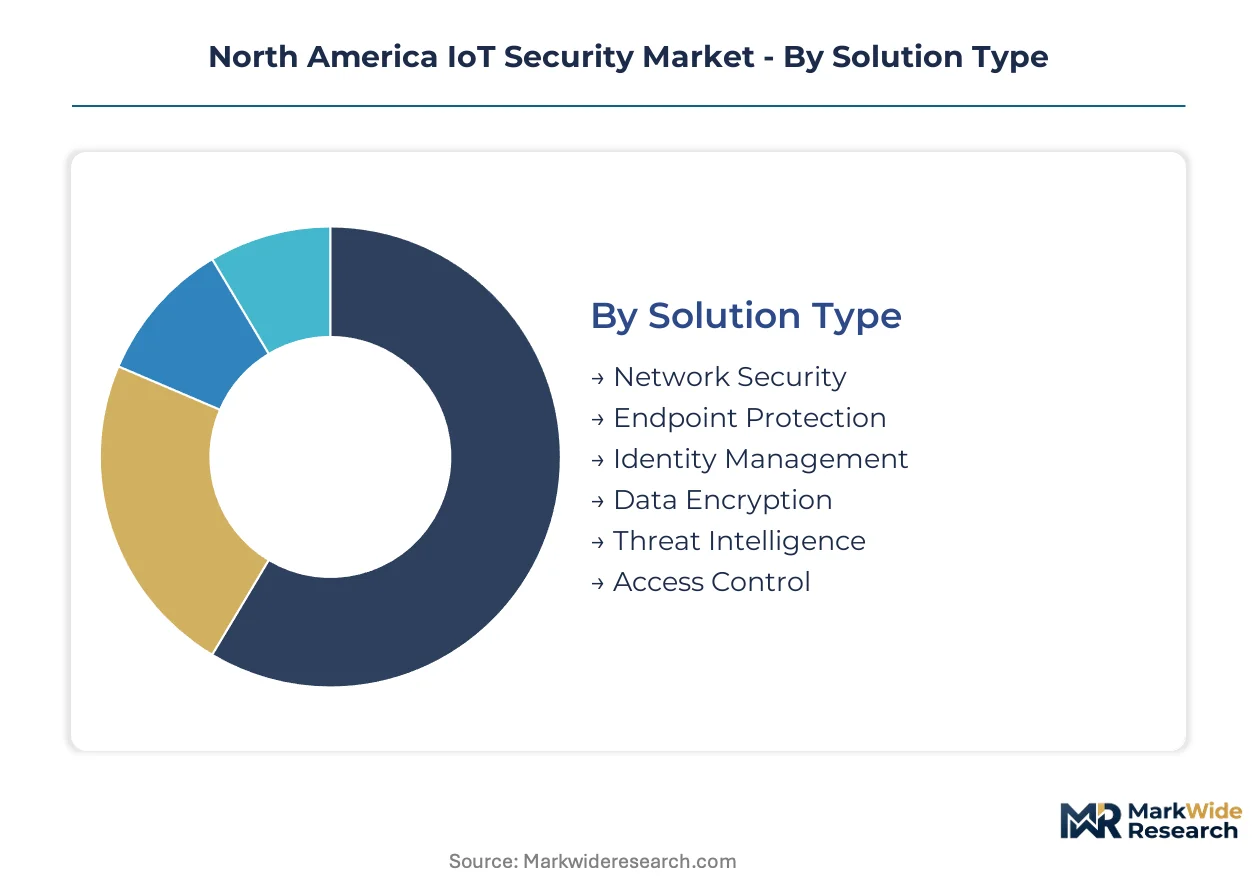
IoT security procurement patterns diverge sharply across deployment contexts, with regulatory mandates from NIST, FDA, and California's SB-327 forcing buyers to prioritize specific solution architectures over others. Understanding these segment boundaries reveals where vendor specialization creates sustainable pricing power versus commoditized competition.
Solution Type:
NIST cybersecurity framework compliance requirements and FDA premarket guidance create divergent procurement specifications across solution categories, with federal healthcare and energy infrastructure contracts demanding firmware-integrated capabilities that generalist platforms cannot satisfy.
- Network Security:Encompasses firewall segmentation, intrusion detection, and traffic monitoring for IP and non-IP industrial protocols including Modbus and DNP3. Demand concentrates in manufacturing and energy provider environments where retrofitting legacy SCADA systems with sub-100-millisecond threat response latency remains capital-intensive. California's Silicon Valley corridor and Texas medical device cluster drive premium procurement for hardware-accelerated deep packet inspection.
- Identity Management:Governs device certificate lifecycle, PKI infrastructure, and credential governance across distributed endpoint fleets. Financial institutions and energy providers face audit failures when renewal cycles span thousands of heterogeneous devices, commanding premium pricing for automated certificate orchestration.
- Endpoint Protection:Secures resource-constrained sensors and actuators through lightweight agents and behavioral monitoring.
- Data Encryption:Protects data at rest and in transit across edge-to-cloud pipelines, increasingly hardware-rooted.
- Threat Intelligence:Aggregates indicator feeds and anomaly signatures for proactive defense posture adjustment.
- Access Control:Enforces least-privilege policies for device-to-device and human-to-machine interactions.
Network Security handles the majority of throughput; Identity Management is gaining share fastest as certificate governance complexity escalates in multi-state deployments.
Application:
Physical safety requirements and breach liability exposure vary dramatically across application contexts, with FDA-regulated medical environments and FERC-overseen energy infrastructure demanding distinct security architectures from consumer-facing deployments.
- Industrial Automation:Secures operational technology environments where device proliferation outpaces perimeter defense and physical system compromise carries catastrophic liability. Texas and California manufacturing corridors prioritize sub-100-millisecond response latency and deep protocol visibility into Modbus and DNP3 traffic.
- Smart Grid:Protects distributed energy resources and advanced metering infrastructure against cascading failure scenarios. NERC CIP compliance mandates and FERC oversight create procurement specifications favoring vendors with pre-certified segmentation capabilities.
- Smart Homes:Addresses consumer IoT device security with baseline password hygiene and encryption standards.
- Connected Vehicles:Secures V2X communication and over-the-air update integrity against remote exploitation.
- Wearable Devices:Protects health data streams and biometric authentication channels in FDA-regulated and consumer contexts.
- Retail Analytics:Safeguards customer behavioral data and point-of-sale integration across distributed storefront networks.
Industrial Automation commands the largest security budgets; Smart Grid is expanding most quickly as NERC enforcement intensifies and distributed energy deployment accelerates.
Deployment Model:
Architectural bets between cloud dependency and edge autonomy are hardening around federal procurement standards and backhaul cost constraints, with manufacturers pushing inference closer to plant floors to reduce exposure windows.
- Edge Computing:Deploys security processing and inference capabilities proximal to device fleets, eliminating cloud backhaul latency and reducing attack surface. Texas medical device manufacturers and California industrial operators are consolidating supply chains around localized validation services that demand edge-resident security stacks.
- Cloud-Based:Centralizes security analytics and policy management through hyperscaler infrastructure, favored where capital constraints outweigh latency sensitivity.
- On-Premises:Maintains security infrastructure within organizational data centers for air-gapped or classified environments.
- Hybrid:Orchestrates policy across cloud and on-premises infrastructure with unified visibility.
Cloud-Based retains the largest installed base; Edge Computing shows the steepest expansion trajectory as manufacturers prioritize physical safety response requirements.
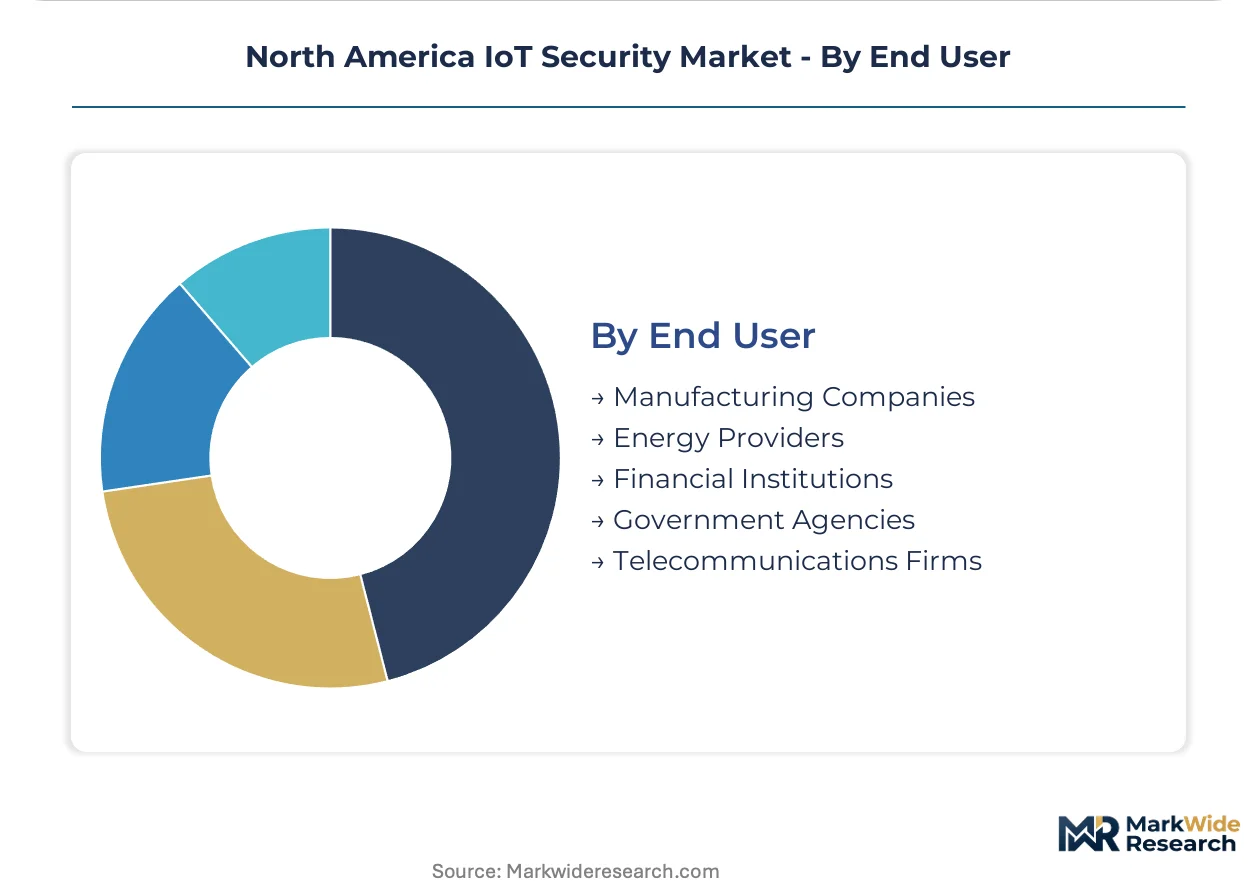
End User:
Sector-specific breach liability precedents and regulatory audit regimes create divergent willingness-to-pay profiles, with financial services and energy providers accepting premium pricing for identity governance while manufacturing prioritizes capital-efficient retrofit solutions.
- Energy Providers:Face NERC CIP compliance mandates and FERC oversight that disqualify non-certified vendors from critical infrastructure procurement. Certificate lifecycle governance across geographically distributed generation, transmission, and distribution systems commands specialized identity management investments.
- Financial Institutions:Navigate stringent audit requirements for device identity governance where renewal cycle failures trigger regulatory enforcement. Premium pricing concentrates in automated PKI orchestration and hardware security module integration.
- Manufacturing Companies:Balance legacy SCADA retrofit costs against operational continuity requirements.
- Government Agencies:Mandate NIST framework compliance and zero-trust architecture specifications in federal procurement.
- Telecommunications Firms:Secure massive IoT device fleets and edge infrastructure at scale.
Energy Providers deploy the most capital-intensive security architectures; Financial Institutions are climbing fastest on identity management spend as audit scrutiny intensifies.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
NIST cybersecurity frameworks and FDA premarket guidance anchor United States procurement specifications, while state-level breach notification laws in California, Texas, and New York fragment compliance architectures across the continent.
United States
Healthcare delivery networks are expanding connected device footprints under FDA premarket guidance requiring vulnerability disclosure timelines. NIST cybersecurity framework compliance has become mandatory in federal procurement pipelines. California's Silicon Valley corridor concentrates venture deployment into firmware cryptography labs that feed talent pipelines toward IoT-native security architectures.
California
SB-327 mandates on baseline password hygiene and encryption standards are disqualifying non-compliant devices from state agency and municipal procurement. The state's attorney general enforces breach notification timelines that exceed federal baselines. Medical device manufacturers in San Diego and San Jose are consolidating supply chains around localized security validation services.
Texas
The medical device cluster near Houston and Dallas-Fort Worth is demanding edge-resident security stacks for manufacturing floors. State-level breach notification laws create compliance overhead distinct from California and New York requirements. Industrial operators are contracting third-party firmware penetration testing before accepting Class II and Class III device deliveries.
New York
Financial institutions face stringent audit requirements for device identity governance where renewal cycle failures trigger regulatory enforcement. The state's Department of Financial Services imposes cybersecurity regulations that extend to IoT device procurement in banking infrastructure. Manhattan-based energy trading floors command premium pricing for automated PKI orchestration.
Canada
Health Canada and the Canadian Centre for Cyber Security are aligning federal procurement with NIST framework baselines for critical infrastructure. Provincial healthcare authorities in Ontario and Quebec are retrofitting legacy building automation systems with sub-100-millisecond threat response requirements. Toronto's financial district is adopting hardware security modules for device certificate lifecycle governance.
North America IoT Security Market Key Industry Players
Technology leadership and cost leadership are held by different player archetypes across the North America IoT Security landscape. Network hardware heritage and cloud-native segmentation capabilities define one strategic cluster, while zero-trust architecture specialization for operational technology environments defines another. Deep packet inspection expertise in industrial automation protocols represents a third narrow specialist tier. Dominant competitive moves include strategic partnerships with semiconductor vendors for hardware-rooted trust mechanisms and geographic expansion into Texas and California medical device clusters.
Within the network heritage tier, Cisco Systems exemplifies scale-driven platform consolidation. Palo Alto Networks occupies a position anchoring zero-trust specialization for federal operational technology procurement. Claroty sits within the narrow specialist archetype, representing differentiation where generalist platforms lack deep protocol visibility into Modbus and DNP3 traffic.
| Leading Market Players |
|---|
| Cisco Systems |
| Palo Alto Networks |
| IBM Corporation |
| Symantec Corporation |
| Microsoft |
| Fortinet |
| Intel Corporation |
| Armis |
| Claroty |
| Others |
Cost & Logistics Intelligence
NIST cybersecurity framework compliance and FDA premarket certification tiers simultaneously gate vendor qualification and stratify price levels across the North America IoT Security landscape. Hardware security module integration and firmware cryptography capabilities create procurement scorecards that separate premium-validated suppliers from commodity software vendors.
Pricing Analysis
California's SB-327 enforcement and Texas medical device cluster procurement create a 40-60% price spread between coast-validated and non-certified security stacks. Three-tier pricing structure across premium, standard, and economy levels dominates, with differentiation driven by NIST framework certification tier and hardware-rooted trust integration. Cost compression in the standard tier intensifies as generalist platforms compete for retrofit SCADA contracts. Manufacturing companies exhibit highest price sensitivity due to legacy system capital burdens, while energy providers accept premium positioning for NERC CIP pre-certified segmentation.
Supply Chain Analysis
Port congestion along the Los Angeles-Long Beach corridor and container availability constraints on Asia-Pacific trade lanes elevate inbound logistics costs for cryptographic semiconductor components. Taiwan, South Korea, and the United States anchor hardware security module and embedded accelerator supply. Raw material dependencies center on silicon wafers, rare earth elements for magnetic components, and specialized epoxy resins. Single-source vulnerability concentrates in advanced node semiconductor fabrication. Distribution runs through authorized cybersecurity distributors and direct OEM contracts with medical device and energy infrastructure manufacturers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The North America IoT Security market is recovering from a cyclical trough as federal procurement standardization and post-quantum cryptography migration timelines force replacement demand across decade-old device fleets.
For Market Incumbents: Compound firmware cryptography capabilities through dedicated lab acquisitions or semiconductor partnerships to defend against narrow specialists like Claroty. Prioritize NIST post-quantum algorithm certification investments to lock in federal healthcare and energy infrastructure contracts before roadmap deadlines harden. For New Entrants and Emerging Players: Lead with edge-resident security architectures targeting Texas medical device manufacturers consolidating localized validation services. The industrial automation retrofit segment offers lowest penetration barriers due to deep packet inspection skill scarcity among incumbent generalists. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across hardware-integrated security stacks as semiconductor co-design becomes mandatory for sub-100-millisecond threat response. Target acquisition archetypes include narrow industrial protocol specialists with Modbus and DNP3 expertise and firmware penetration testing services unbundled from device procurement. Watch NERC CIP enforcement intensity as the signal for energy provider security spend inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Semiconductor Partnership for Hardware Security Modules | Integrates cryptographic accelerators directly into medical device and energy grid deployments, displacing pure software encryption stacks. |
| Firmware Cryptography Lab Acquisition | Captures embedded security engineering talent premiums and accelerates NIST post-quantum algorithm certification timelines. |
| Third-Party Validation Service Launch | Addresses unbundling trend where Texas and California industrial operators contract standalone firmware penetration testing before device acceptance. |
| Zero-Trust Architecture Pre-Certification | Creates federal procurement specification advantages as operational technology environments mandate segmentation capabilities. |
| Edge Computing Security Stack Development | Supports manufacturers pushing machine learning inference closer to plant floors without cloud backhaul dependency. |
Research Approach
A standing panel of embedded security engineers, federal procurement officers, healthcare delivery network CIOs, and industrial automation protocol specialists provided ongoing calibration throughout the research process. Primary fieldwork combined structured interviews with these stakeholders and secondary validation against NIST framework documentation, FDA premarket guidance filings, state attorney general enforcement actions, and semiconductor vendor product roadmaps. Bottom-up device shipment estimates and top-down security spend allocations were triangulated against federal procurement databases and healthcare system capital expenditure disclosures.
Consistency checks validated volume and value outputs against external benchmarks including hyperscaler IoT platform revenue disclosures, industrial cybersecurity vendor SEC filings, and energy sector infrastructure investment surveys. The analytical framework modeled demand across solution type, deployment model, application context, and end-user sector throughout the projection horizon. CAGRs were derived from segment-level growth trajectory analysis incorporating regulatory mandate timelines, device fleet replacement cycles, and technology substitution patterns. Post-quantum cryptography migration schedules and NERC CIP enforcement intensity served as key forecast inputs.
The analysis sits within stated boundaries; outcomes outside sustained federal procurement standardization, stable semiconductor supply availability, or consistent state-level enforcement would require recalibration. Forecasts reflect documented assumptions regarding NIST framework adoption rates, FDA premarket guidance adherence, and embedded security engineering labor market dynamics. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Global Data Exfiltration Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Malaysia Cybersecurity Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Hungary Cybersecurity Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Global Database Encryption Market