
 Global Cyber Data Security Market | 2026-2036
Global Cyber Data Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Cyber Data Security Market Foresight
Multi-source procurement of security tooling is decoupling from legacy single-vendor enterprise suites. Microsoft leverages its cloud-native architecture to anchor identity and access management workloads across hybrid deployments. Palo Alto Networks competes through platform consolidation, while CrowdStrike specializes in endpoint detection and response with lightweight agent design.
Cyber data security encompasses technologies and practices that protect digital information from unauthorized access, exfiltration, or corruption through cryptographic protocols, access controls, and continuous monitoring systems operating at network speeds exceeding 100 Gbps. Its primary purpose is to preserve confidentiality, integrity, and availability of data assets across distributed computing environments. Cloud-based deployment leads solution delivery as enterprises migrate workloads away from capital-intensive on-premises infrastructure. Encryption and identity and access management capture concentrated margin pools due to regulatory mandates for data-at-rest protection and zero-trust architecture adoption.
The U.S. SEC enforces cyber disclosure rules requiring material incident reporting within four business days, while the EU NIS2 Directive expands security obligations to more critical sectors with heavier penalties. Japan's METI publishes cybersecurity management guidelines that shape procurement standards for domestic enterprises. Stakeholders must monitor divergence between U.S. sector-specific mandates and EU horizontal frameworks when architecting compliance-ready security stacks.
Market Dynamics
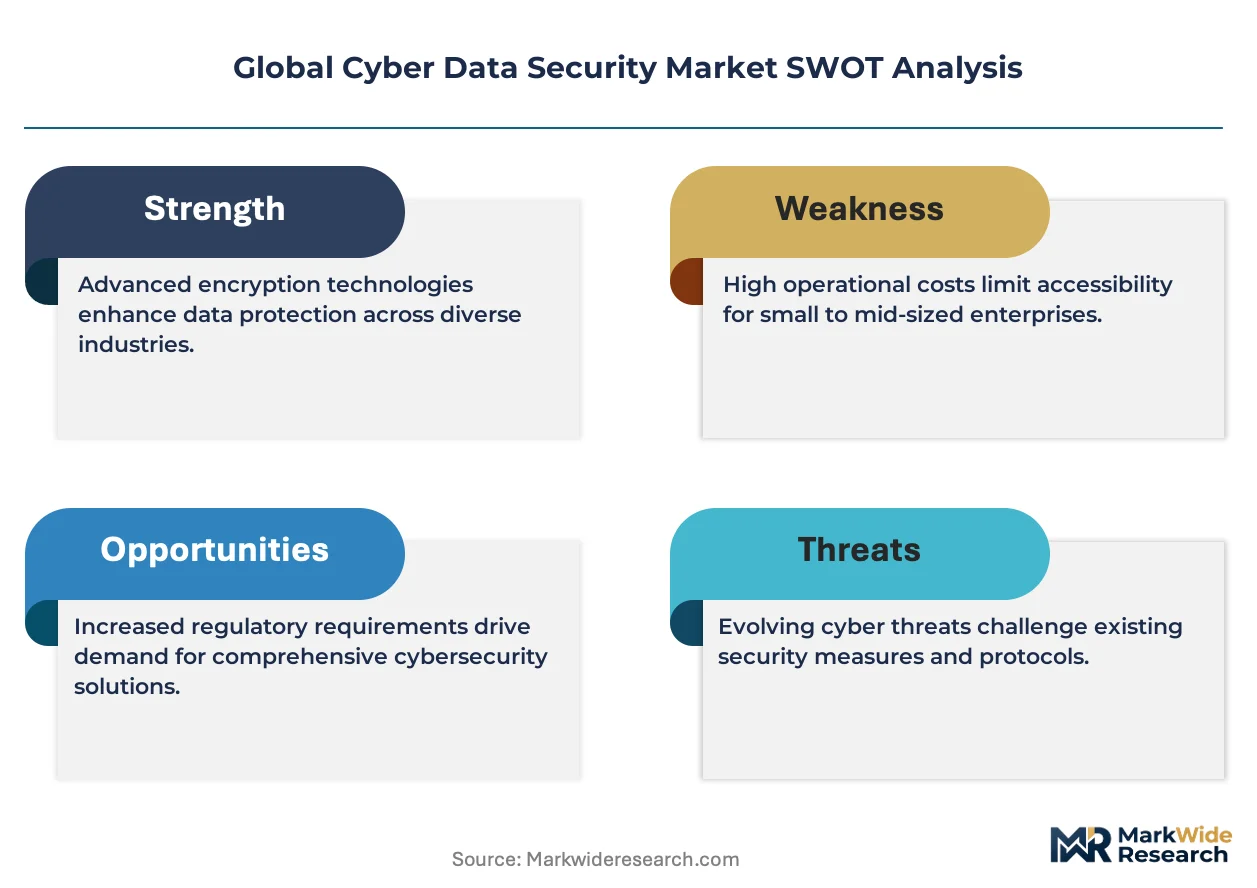
Zero-trust architecture mandates are fragmenting security procurement patterns as enterprises abandon perimeter-based models. Financial services and critical infrastructure operators now demand continuous verification protocols that legacy firewall-centric suites cannot deliver.
Growth Catalysts
- Ransomware proliferation:Attack frequency against healthcare and energy systems drives replacement cycles for endpoint detection tools. The U.S. SEC's four-day disclosure rule accelerates board-level security investment approvals.
- EU NIS2 Directive:Expanded coverage to digital infrastructure providers and public administration entities creates compliance-driven procurement across 27 member states. Penalty thresholds reaching 10 million euros concentrate vendor selection authority at C-suite level.
- Quantum-resistant cryptography:NIST's post-quantum algorithm standards prompt federal contractor migration timelines. Early adopters in defense and telecommunications supply chains are pre-positioning against harvest-now-decrypt-later threats.
Market Restraints
- Semiconductor supply concentration:Hardware security module fabrication depends on TSMC's advanced node capacity in Taiwan. Geopolitical friction risks create procurement lead time volatility exceeding 26 weeks for FIPS 140-3 Level 4 devices.
- Skilled practitioner scarcity:Global shortage of cloud security architects and threat intelligence analysts exceeds 3.4 million unfilled positions. Salary inflation above 15% annually compresses managed security service provider margins.
- Interoperability friction:Proprietary API architectures from dominant cloud hyperscalers lock data formats and complicate multi-vendor orchestration. Customer switching costs escalate with identity provider consolidation depth.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy facilities merge IT and OT security stacks as IEC 62443 adoption spreads. Converged platforms address protocol translation between Modbus and TCP/IP environments.
- Japan's METI guidelines:Supply chain security certification requirements for critical infrastructure create vendor qualification pathways. Domestic system integrators seek foreign technology partnerships to meet 2025 compliance deadlines.
- Confidential computing:Hardware-based trusted execution environments from Intel SGX and AMD SEV enable processing of encrypted data without decryption. Financial services and healthcare pilot projects validate regulatory-compliant analytics on sensitive datasets.
Industry Challenges
- Alert fatigue remediation:Security operations centers face false positive rates exceeding 80% from disconnected point solutions. Analyst burnout drives automation investment that itself requires extensive tuning and validation cycles.
- Legacy mainframe integration:Banking and government agencies maintain COBOL-based systems with incompatible authentication protocols. Modern identity federation requires custom middleware development with limited vendor support.
- Cross-border data sovereignty:Conflicting localization requirements between China's Cybersecurity Law and EU GDPR complicate unified security architecture design. Multinational enterprises fragment infrastructure deployment to satisfy jurisdictional constraints.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Cyber Data Security Market |
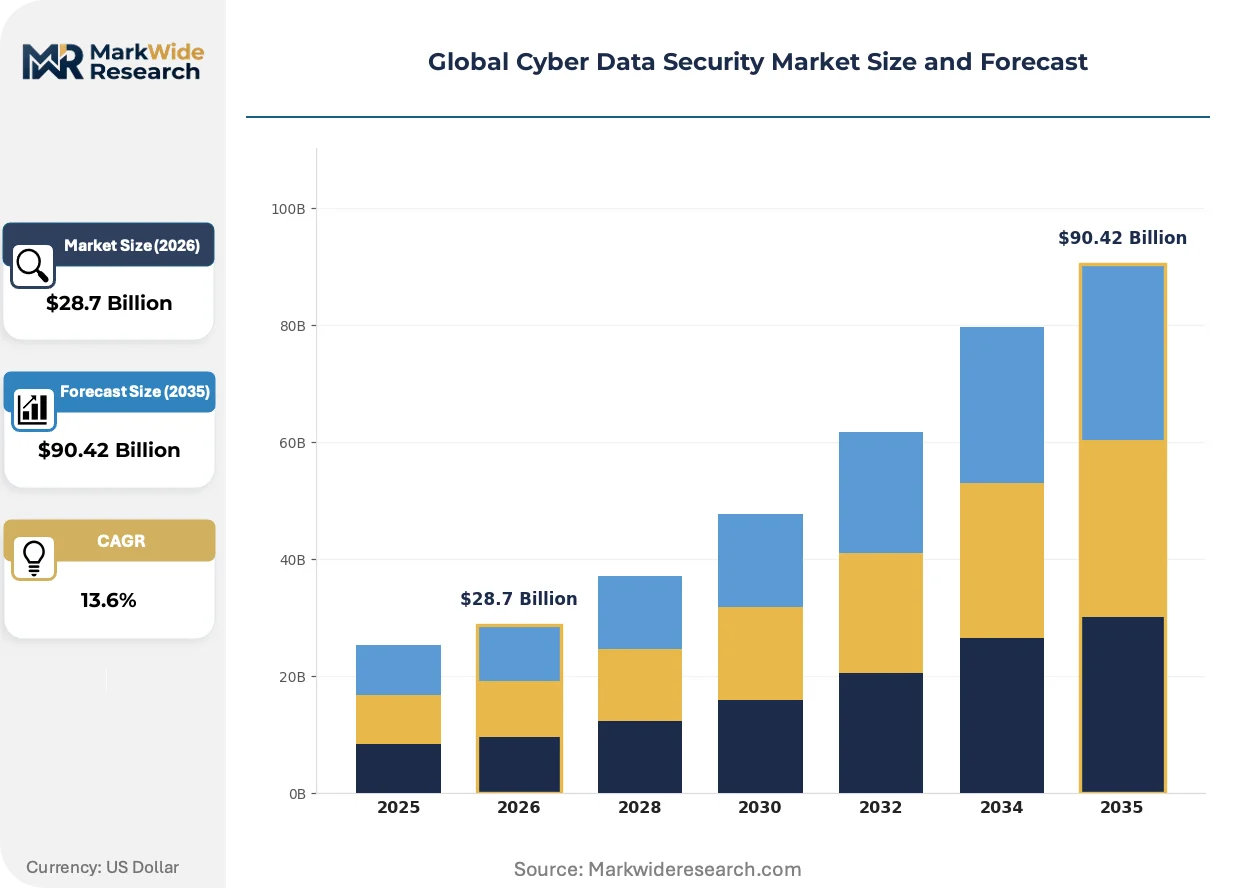
| Market Size in 2026 | $28.7 Billion |
| Market Size in 2035 | $90.42 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Multi-Cloud Solution Type: Encryption, Data Loss Prevention, Identity & Access Management, Endpoint Security, Security Information & Event Management Application: Financial Services, Government Agencies, Telecommunications, Manufacturing, Education End User: Enterprises, Small & Medium Businesses, Managed Security Service Providers, Cloud Service Providers |
| Companies Covered | IBM, Microsoft, Cisco Systems, Palo Alto Networks, Fortinet, Check Point Software Technologies, Trend Micro, CrowdStrike, Broadcom, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Cyber Data Security Market Shifts & Advancements
Security tool consolidation and autonomous response capabilities are compressing the window between threat detection and containment. Vendors race to embed machine learning inference directly at network edge points.
Homomorphic encryption is rewriting how regulated industries perform analytics on protected health and financial records. Pharmaceutical companies and insurance carriers pilot privacy-preserving computation for multi-party data collaboration. The technology eliminates data decryption requirements during processing, collapsing compliance review cycles from months to days.
The EU AI Act's risk-based classification system imposes mandatory security requirements on high-risk AI applications including biometric identification and critical infrastructure management. Providers must implement logging, human oversight, and robustness testing before market placement. German automotive and French healthcare AI developers are restructuring DevSecOps pipelines to satisfy conformity assessment obligations.
Enterprise buyers now unbundle managed detection and response services from underlying platform licenses, selecting specialist providers for 24/7 threat hunting. This disintermediation pressures bundled pricing models from incumbent security vendors. The pattern is most pronounced among mid-market financial services firms in the United States seeking SOC 2 Type II attestation without capital-intensive security operations center buildouts.
Global Cyber Data Security Market Segmentation
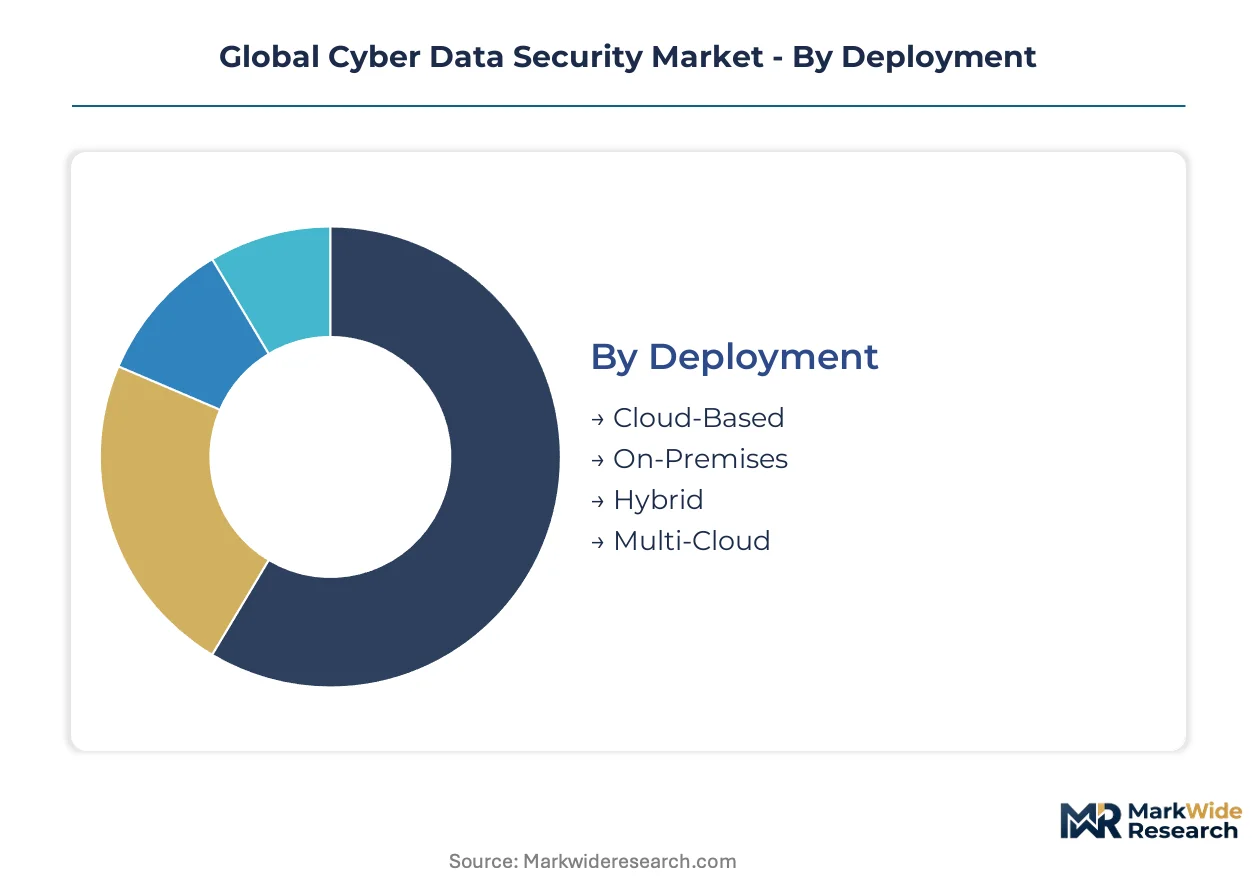
Cyber data security procurement patterns diverge sharply by infrastructure maturity and regulatory exposure. Deployment mode, solution architecture, and buyer scale each create distinct margin profiles and vendor selection criteria across the market.
Deployment:
Cloud-based architectures dominate transaction volume while hybrid configurations command premium pricing for regulated workloads.
- Cloud-Based:Scalable infrastructure delivered via SaaS models eliminates capital expenditure for endpoint detection and encryption key management. Financial services firms in the United States and Germany concentrate procurement here to satisfy SEC and EU NIS2 audit requirements without on-premises hardware refresh cycles.
- On-Premises:Dedicated hardware security modules and air-gapped networks serve defense contractors and classified government facilities with FIPS 140-3 compliance mandates. Japanese critical infrastructure operators under METI guidelines retain these deployments for operational technology environments where cloud connectivity introduces unacceptable risk.
- Hybrid:Split architectures process sensitive data locally while leveraging cloud analytics for threat intelligence correlation.
- Multi-Cloud:Workload portability across AWS, Azure, and Google Cloud environments avoids vendor lock-in for multinational enterprises.
Mature deployment sits with On-Premises. Newer deployment is concentrated in Multi-Cloud.
Solution Type:
Regulatory mandates concentrate spending on encryption and identity infrastructure, while endpoint tools face commoditization pressure.
- Encryption:Cryptographic protocols protecting data-at-rest and data-in-transit span symmetric, asymmetric, and emerging post-quantum algorithms. Healthcare systems across Germany and France prioritize this segment to satisfy GDPR Article 32 security requirements and EU AI Act data governance obligations for high-risk AI applications.
- Identity & Access Management:Zero-trust verification frameworks replace perimeter-based authentication with continuous user and device validation. United States federal agencies accelerate procurement here to meet OMB zero-trust architecture deadlines, displacing legacy VPN and firewall-centric approaches.
- Data Loss Prevention:Content inspection and egress monitoring tools classify sensitive information and block unauthorized exfiltration channels.
- Endpoint Security:Lightweight agents detect malware and anomalous behavior on laptops, servers, and mobile devices.
- Security Information & Event Management:Log aggregation and correlation platforms centralize visibility across disparate security tools.
Encryption captures the steepest expansion trajectory as NIST post-quantum standards drive replacement cycles. SIEM growth lags as buyers unbundle managed detection services from platform licenses.
Application:
Financial services and government sectors anchor procurement volume, while manufacturing presents underpenetrated expansion opportunity.
- Financial Services:Banks, insurers, and payment processors deploy layered defenses against ransomware and insider threats with regulatory capital implications. United States institutions face SEC four-day disclosure mandates that accelerate board-level security investment approvals and consolidate vendor relationships.
- Government Agencies:National security and civilian departments require FedRAMP-authorized or equivalent certified solutions with supply chain integrity verification. German federal and state administrations expand procurement under EU NIS2 Directive coverage of public administration entities.
- Telecommunications:Network operators protect subscriber data and signaling infrastructure from nation-state espionage.
- Manufacturing:Industrial facilities merge IT and OT security stacks as IEC 62443 adoption spreads across production environments.
- Education:Universities and K-12 districts balance open research collaboration with student data privacy requirements.
Financial Services maintains the deepest vendor relationships. Manufacturing represents the fastest-climbing application segment as operational technology convergence accelerates.
End User:
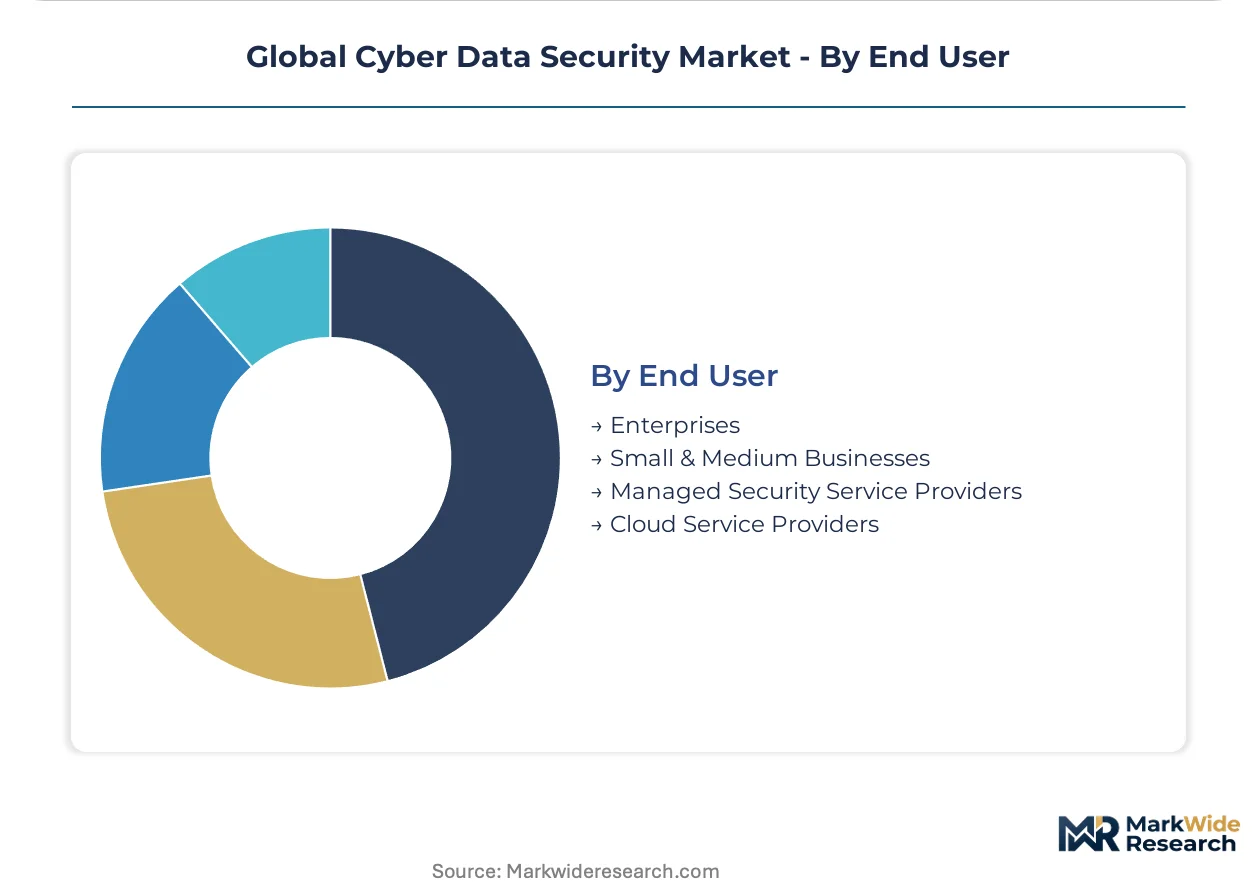
Enterprise buyers drive solution complexity while managed security service providers reshape channel economics.
- Enterprises:Fortune 500 and equivalent large organizations operate dedicated security operations centers with 24/7 staffing. Japanese conglomerates and United States healthcare systems concentrate spending here, seeking unified platforms that reduce interoperability friction across hybrid cloud environments.
- Managed Security Service Providers:Outsourced threat hunting and incident response vendors aggregate demand from mid-market clients lacking internal expertise. United States mid-market financial services firms disaggregate MDR services from platform licenses to obtain SOC 2 Type II attestation without capital-intensive SOC buildouts.
- Small & Medium Businesses:Resource-constrained organizations rely on bundled security offerings from productivity software vendors.
- Cloud Service Providers:Hyperscalers embed security capabilities into infrastructure-as-a-service offerings.
Enterprises anchor absolute spending. Managed Security Service Providers are gaining share fastest as buyer unbundling pressures incumbent bundled pricing models.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's venture concentration and Washington's procurement gravity anchor North American demand architecture for cyber data security solutions. Regulatory divergence between Washington and Brussels reshapes vendor compliance roadmaps across transatlantic deployments.
United States
Financial institutions and federal agencies drive concentrated procurement volume. The SEC's four-day disclosure mandate accelerates board-level security investment approvals. Washington D.C. and Northern Virginia house the densest cluster of FedRAMP-authorized vendors serving civilian and intelligence community contracts.
Germany
Automotive OEMs and industrial conglomerates anchor enterprise demand for operational technology security. The EU NIS2 Directive expands coverage to digital infrastructure providers with penalty thresholds reaching 10 million euros. Munich and Stuttgart concentrate vendor development centers addressing IEC 62443 convergence requirements.
Japan
Critical infrastructure operators and domestic system integrators reshape procurement patterns under METI cybersecurity guidelines. Supply chain security certification requirements for critical infrastructure create vendor qualification pathways. Tokyo and Osaka metropolitan areas concentrate pilot deployments of confidential computing for financial analytics.
United Kingdom
Financial services and defense contractors sustain premium-tier security spending. The National Cyber Security Centre shapes procurement standards through Cyber Essentials and NCSC-certified practitioner programs. London's fintech corridor drives demand for cloud-native identity and access management solutions.
France
Healthcare AI developers and aerospace suppliers navigate EU AI Act conformity assessment obligations. The ANSSI certification framework governs critical infrastructure security procurement. Paris-Saclay and Toulouse clusters concentrate DevSecOps restructuring for high-risk AI application compliance.
Global Cyber Data Security Market Competitive Landscape
Platform consolidation dominates the current landscape as enterprises abandon fragmented point solutions for unified security architectures. The vendor base organizes around three strategic tiers: cloud-native hyperscalers with identity anchoring capabilities, platform consolidators spanning network and endpoint domains, and specialists in lightweight agent design for endpoint detection. M&A activity and strategic technology licensing represent the dominant competitive moves as incumbents acquire niche capabilities to fill portfolio gaps.
Among cloud-native architects, Microsoft anchors hybrid identity workloads across government and enterprise deployments. Palo Alto Networks exemplifies the platform consolidation archetype through integrated network and cloud security positioning. CrowdStrike occupies a specialist position in endpoint detection with emphasis on agent efficiency and threat intelligence velocity.
| Leading Market Players |
|---|
| IBM |
| Microsoft |
| Cisco Systems |
| Palo Alto Networks |
| Fortinet |
| Check Point Software Technologies |
| Trend Micro |
| CrowdStrike |
| Broadcom |
| Others |
Supply & Pricing Matrix
Cloud security architect concentration in the United States and Germany creates labor-cost differentials that widen pricing-tier spreads between premium managed detection services and economy endpoint protection bundles. Buyers in Japan and France absorb steeper premiums for zero-trust architecture deployments as local certification requirements and METI guidelines extend implementation timelines.
Pricing Analysis
Warranty and service bundling separates premium-tier security vendors from commodity endpoint providers. Three-tier pricing structure across premium, standard, and economy levels reflects differentiation by FedRAMP authorization status and SOC 2 Type II attestation inclusion. Pricing pressure stems from mid-market financial services firms unbundling managed detection services from platform licenses. Small and medium businesses exhibit highest price sensitivity, while United States federal agencies demonstrate lowest elasticity due to OMB zero-trust deadlines.
Supply Chain Analysis
Dual-sourcing requirements for hardware security modules mandate multi-supplier qualification across Taiwan, South Korea, and United States fabrication facilities. FIPS 140-3 Level 4 device production draws from TSMC advanced node capacity, Intel foundry services, and domestic Japanese semiconductor suppliers. Single-source vulnerability concentrates in Taiwanese advanced packaging for cryptographic processors. Distribution runs through authorized FedRAMP resellers and domestic system integrators in Germany and Japan.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market consolidates around platform vendors with sufficient R&D scale to absorb quantum-resistant cryptography migration costs. Smaller point-solution providers face displacement as enterprise buyers demand unified security architectures.
For Market Incumbents: Cement platform consolidation advantages by acquiring confidential computing specialists and OT security vendors addressing IEC 62443 convergence. CrowdStrike's lightweight agent design and Palo Alto Networks' network-cloud integration demonstrate defensible positioning against Microsoft identity anchoring. Invest in post-quantum algorithm certification ahead of NIST contractor migration timelines.
For New Entrants and Emerging Players: Begin with operational technology security gaps in German automotive and Japanese manufacturing facilities where legacy firewall vendors lack protocol translation capabilities. Target managed security service provider channel partnerships in United States mid-market financial services seeking SOC 2 Type II attestation without capital-intensive security operations center buildouts.
For Investors and Strategic Acquirers: Re-rating potential sits with confidential computing specialists given EU AI Act high-risk application mandates and pharmaceutical privacy-preserving analytics pilots. Long-term viability favors vendors with hardware-software co-design capabilities spanning Intel SGX and AMD SEV implementations. Watch NIST post-quantum standard adoption velocity as inflection indicator for federal contractor replacement cycle timing.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and identity workloads to reduce interoperability friction for hybrid cloud enterprises. |
| Acquisition of Specialist Firm | Fills confidential computing or OT security gaps as IEC 62443 adoption spreads across manufacturing environments. |
| Strategic Partnership | Enables domestic system integrators in Japan to meet METI supply chain certification requirements through foreign technology licensing. |
| Product Launch | Addresses post-quantum cryptographic protocols as NIST standards prompt federal contractor migration timelines. |
| Geographic Expansion | Establishes FedRAMP-authorized delivery centers in Washington D.C. corridor for civilian and intelligence community contracts. |
Research Methodology
Independent corroboration across CISO interviews, managed security service provider operational data, and hyperscaler capex disclosures underwrites the qualitative findings. Primary fieldwork engaged chief information security officers at United States financial institutions, German automotive OEMs, and Japanese critical infrastructure operators alongside channel partners and federal procurement specialists. Secondary validation incorporated SEC cyber disclosure filings, EU NIS2 implementation guidance, METI cybersecurity guideline updates, and FedRAMP authorization databases. Bottom-up deployment modeling and top-down regulatory impact assessment were triangulated to establish market sizing.
Rate-of-change decomposition across the analysis window segmented growth by deployment mode, solution architecture, buyer scale, and regional regulatory enforcement intensity. Modeled dimensions included cloud-native versus hybrid infrastructure, encryption versus identity versus endpoint solution mix, enterprise versus MSSP versus SMB end user, and United States SEC disclosure regime versus EU NIS2 penalty structure versus Japan METI guideline adoption. CAGRs were derived from replacement cycle analysis for post-quantum cryptography migration and zero-trust architecture mandate compliance timelines.
Quantum computing breakthrough acceleration, geopolitical semiconductor export restrictions, and EU AI Act enforcement variance are the dominant revision risks. Deviation in NIST post-quantum standard finalization timing would shift federal contractor procurement outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Latin America Cybersecurity Market
Cybersecurity
Netherlands Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Middle East and Africa Cybersecurity Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
Global Healthcare IoT Security Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Endpoint Security Market
Cybersecurity
Global Bug Bounty Platforms Market