
 Anti-Malware Market | 2026-2036
Anti-Malware Market Size, Share, and Industry Trends Forecast 2026-2036
Anti-Malware Market Outlook
Platform bundling of endpoint, network, and email protection into unified suites is repositioning procurement decisions for enterprise buyers. McAfee leverages its consumer-to-enterprise crossover brand to sustain multi-channel distribution. Trend Micro anchors cloud-native security architectures across Asia-Pacific data center deployments. Bitdefender differentiates through machine-learning detection engines that compete with signature-heavy legacy stacks.
Anti-malware software comprises detection engines, threat intelligence feeds, and remediation tools designed to identify, quarantine, and neutralize malicious code across computing environments; these systems operate through real-time scanning, behavioral analysis, and automated patch deployment to protect data integrity and operational continuity. Endpoint Protection dominates product-type revenue as remote work expands device attack surfaces, while Cloud-based deployment is capturing the fastest growth trajectory among delivery models due to scalability demands from distributed workforces. Behavioral technology is gaining share against signature-based scanning as polymorphic malware strains evade static detection, and Healthcare end users are emerging as a concentrated margin pool given patient-data breach penalties.
FCC guidelines on communications infrastructure security, SEC disclosure rules for material cybersecurity incidents, and HIPAA data protection mandates are collectively elevating baseline anti-malware investment across regulated sectors. GDPR cross-border enforcement by European regulators and the EU AI Act's risk-classification system are further tightening product certification requirements for vendors serving European enterprises. Stakeholders must monitor how zero-trust architecture mandates from federal agencies reshape deployment preferences and vendor qualification criteria.
Market Dynamics
The migration from signature-based detection to behavioral analysis engines is compressing refresh cycles for endpoint protection suites. Financial services and healthcare buyers now mandate AI-augmented threat hunting capabilities in procurement specifications, forcing legacy vendors to re-architect detection stacks or cede enterprise accounts.
Growth Catalysts
- Ransomware Escalation:Manufacturing and logistics operators are expanding endpoint coverage to operational technology networks after Colonial Pipeline-style disruptions. Germany's NIS2 implementation deadlines are accelerating compliance-driven procurement across automotive supply chains.
- Zero-Trust Mandates:US federal agencies now require continuous device verification under CISA guidance, pulling cloud-native anti-malware into civilian and defense contractor stacks. This is displacing perimeter-focused legacy deployments.
- Patient Data Penalties:HIPAA breach settlements exceeding $50 million are concentrating healthcare CISO attention on endpoint detection and response platforms with automated forensic capabilities.
Market Restraints
- Detection Engine Commoditization:Open-source threat intelligence feeds and MITRE ATT&CK framework adoption are eroding proprietary signature database differentiation, compressing pricing power for mid-tier vendors.
- Cloud Infrastructure Concentration:AWS, Azure, and Google Cloud native security controls are absorbing basic anti-malware functions, narrowing addressable market for standalone endpoint agents in cloud-first enterprises.
- EU AI Act Friction:Risk-classification requirements for AI-enabled detection systems are extending product certification timelines by 8-14 months, delaying revenue recognition for European launches.
Strategic Opportunities
- Operational Technology Convergence:Industrial control system operators in Germany and Japan are deploying unified IT/OT anti-malware stacks as IEC 62443 certification becomes mandatory for critical infrastructure tenders.
- Managed Detection Services:Mid-market enterprises lacking SOC staffing are outsourcing endpoint monitoring to MSSPs, creating recurring revenue pools for platform vendors with multi-tenant architectures.
- Post-Quantum Cryptography Preparation:NIST's finalized PQC standards are driving firmware-level anti-malware upgrades in defense and financial sectors to protect against harvest-now-decrypt-later threats.
Industry Challenges
- Adversarial AI Arms Race:Polymorphic malware variants generated via large language models are evading behavioral models trained on historical attack patterns, forcing detection engine retraining cycles measured in weeks rather than quarters.
- Integration Fragmentation:Enterprise buyers operate heterogeneous endpoint fleets spanning Windows, macOS, Linux, iOS, and embedded systems, multiplying agent compatibility testing burdens for vendors.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Anti-Malware Market |
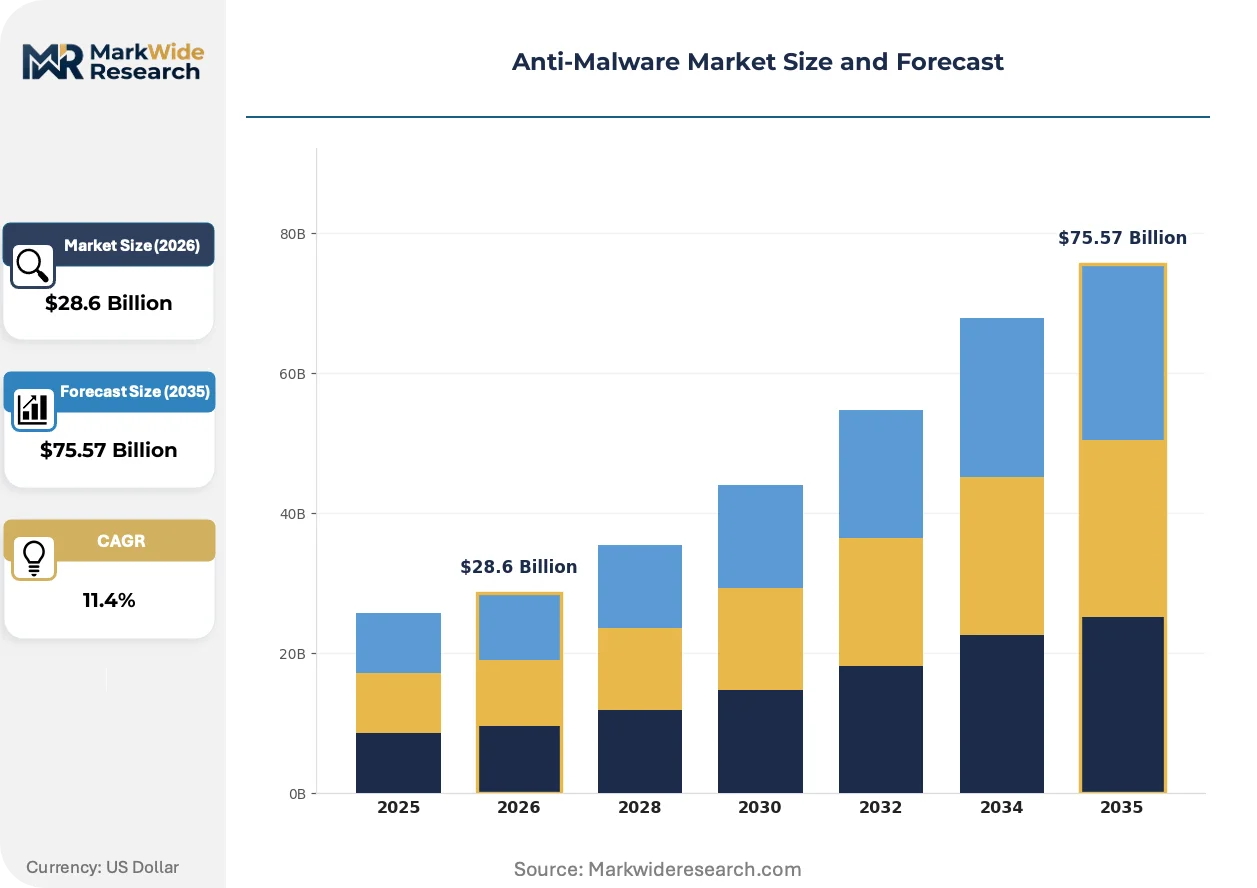
| Market Size in 2026 | $28.6 Billion |
| Market Size in 2035 | $75.57 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Protection, Network Security, Email Security, Mobile Security Deployment: Cloud-based, On-premises, Hybrid, Managed Service End User: Small Enterprises, Large Enterprises, Government, Healthcare Technology: Signature-based, Heuristic, Behavioral, Sandbox |
| Companies Covered | McAfee, Trend Micro, Bitdefender, ESET, Avira, Norton, F-Secure, Malwarebytes, Avast, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Anti-Malware Market Strategic Shifts
Behavioral detection architectures are displacing signature-heavy stacks as polymorphic threats render static hash matching ineffective. This shift is compressing vendor R&D timelines and redistributing competitive advantage toward machine-learning engineering depth.
Extended detection and response platforms are decentralizing security operations by embedding automated investigation and remediation directly at the endpoint. Healthcare systems and financial services firms are deploying these capabilities to reduce mean-time-to-containment below 15 minutes. The architecture is decentralizing tier-1 SOC functions from centralized security operations centers to distributed endpoint agents with local decision authority.
The EU AI Act's risk-classification framework is mandating conformity assessments for AI-enabled threat detection systems before European market entry. Vendors must document training data provenance and algorithmic transparency to obtain CE marking for high-risk cybersecurity products. German automotive and industrial OEMs are prioritizing suppliers with completed EU AI Act compliance to avoid supply chain disruption.
Enterprise buyers are consolidating endpoint, identity, and data protection procurement under unified zero-trust architecture mandates. CISOs at US federal contractors and European critical infrastructure operators are rejecting point-product vendors in favor of integrated suites with shared telemetry fabrics. This consolidation is most visible in US defense industrial base and German automotive supplier networks, where procurement specifications now require cross-product correlation capabilities.
Anti-Malware Market Segmentation
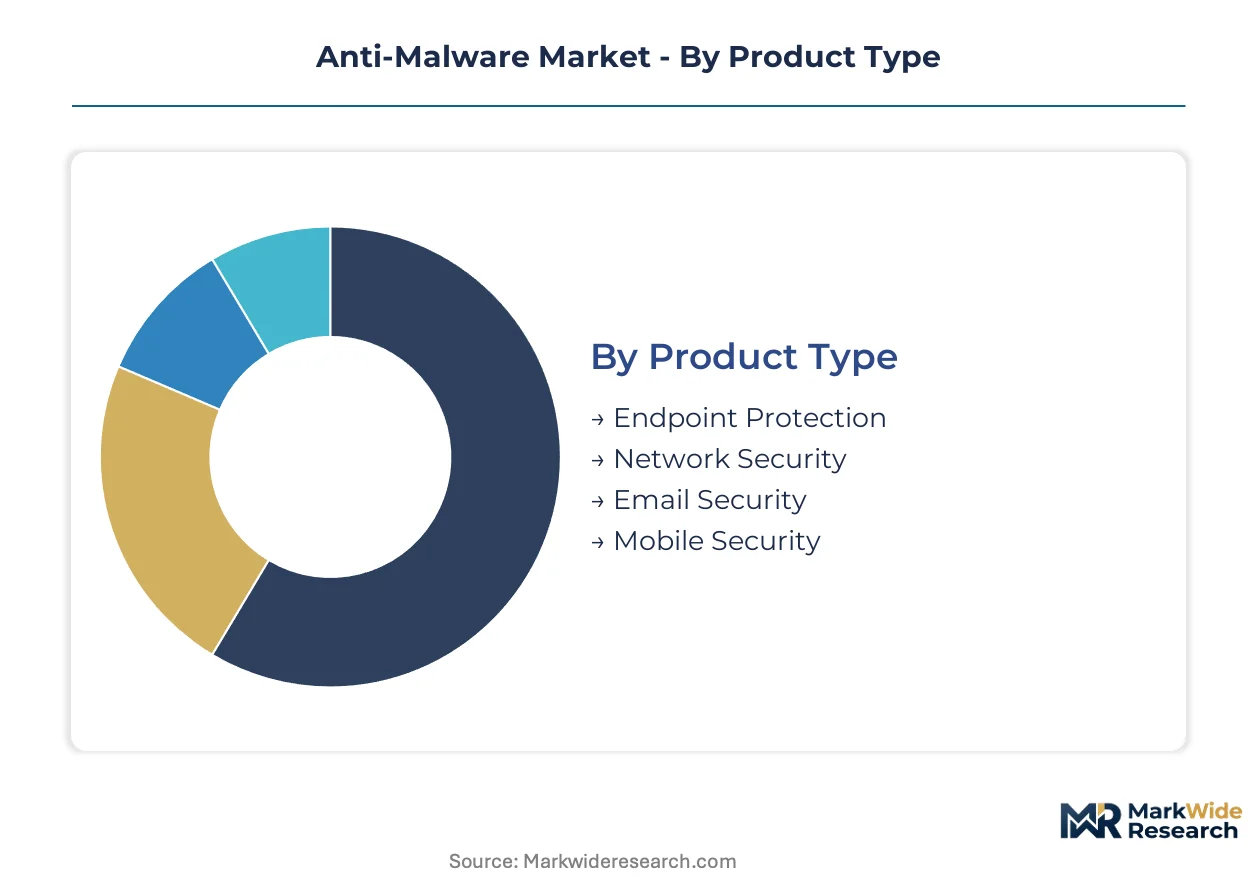
Anti-malware procurement splits sharply between capital-intensive on-premises infrastructure and lighter cloud-native deployments. Buyers weigh upfront hardware investment against ongoing operational complexity when selecting across product, deployment, and technology dimensions.
Product Type:
Capital intensity peaks with network security appliances requiring dedicated hardware, while endpoint protection scales through software licensing models.
- Endpoint Protection:Software agents deployed on laptops, servers, and mobile devices detect malicious code through real-time scanning and behavioral monitoring. Financial services firms in Germany and healthcare systems across the US are expanding seat licenses to cover remote workforces and operational technology networks. The segment absorbs the bulk of installed capacity.
- Network Security:Hardware appliances and virtualized gateways inspect traffic flows for malware payloads at perimeter and internal network segments. Manufacturing operators in Japan and automotive suppliers in Germany require IEC 62443-certified appliances for IT/OT convergence projects. This segment commands the highest upfront capital expenditure per deployment.
- Email Security:Gateway and cloud-based filters block phishing attachments and malicious links before inbox delivery. Enterprises with heavy Microsoft 365 or Google Workspace adoption integrate these capabilities through API connectors rather than standalone appliances.
- Mobile Security:Lightweight agents for iOS and Android devices enforce application sandboxing and network traffic inspection. BYOD policies at US federal contractors and European critical infrastructure operators are expanding addressable device counts.
Endpoint Protection absorbs the bulk of installed capacity; Mobile Security is expanding most quickly.
Deployment:
Customer technical maturity and data residency requirements determine whether buyers favor self-managed infrastructure or outsourced operations.
- Cloud-based:Vendor-hosted detection engines scale elastically without client-side hardware procurement. German automotive OEMs and Asia-Pacific data center operators favor this model for distributed workforce coverage and rapid threat intelligence updates.
- On-premises:Air-gapped or regulated environments in defense, healthcare, and critical infrastructure mandate local malware analysis to prevent data exfiltration. HIPAA-covered entities and US federal agencies require on-premises deployments for sensitive patient and classified data.
- Hybrid:Split architectures route low-sensitivity traffic to cloud engines while retaining high-risk analysis on local hardware. Large European enterprises navigating GDPR cross-border transfer rules favor this compromise configuration.
- Managed Service:Outsourced monitoring and response delivered by MSSPs appeals to mid-market enterprises lacking SOC staffing. Recurring revenue models attract platform vendors with multi-tenant architectures.
Cloud-based deployment captures the steepest expansion trajectory; On-premises retains the largest existing footprint in regulated sectors.
End User:
Budget scale and compliance exposure create divergent procurement patterns across organization types.
- Large Enterprises:Centralized security teams mandate integrated suites with cross-product telemetry and automated orchestration. CISOs at US defense contractors and German automotive networks reject point-product vendors in favor of unified zero-trust architectures.
- Healthcare:HIPAA breach penalties exceeding $50 million concentrate CISO attention on endpoint detection platforms with automated forensic capabilities. Patient-data protection mandates elevate baseline investment regardless of organization size.
- Government:CISA zero-trust mandates and NIS2 compliance deadlines in Europe drive standardized procurement specifications. US federal agencies and EU member state critical infrastructure operators represent concentrated demand pools.
- Small Enterprises:Limited IT staffing drives preference for managed services and simplified cloud-native bundles. Price sensitivity favors vendors with consumer-to-enterprise crossover brands and channel partner distribution.
Large Enterprises absorb the bulk of installed capacity; Healthcare is gaining share fastest on regulatory penalty pressure.
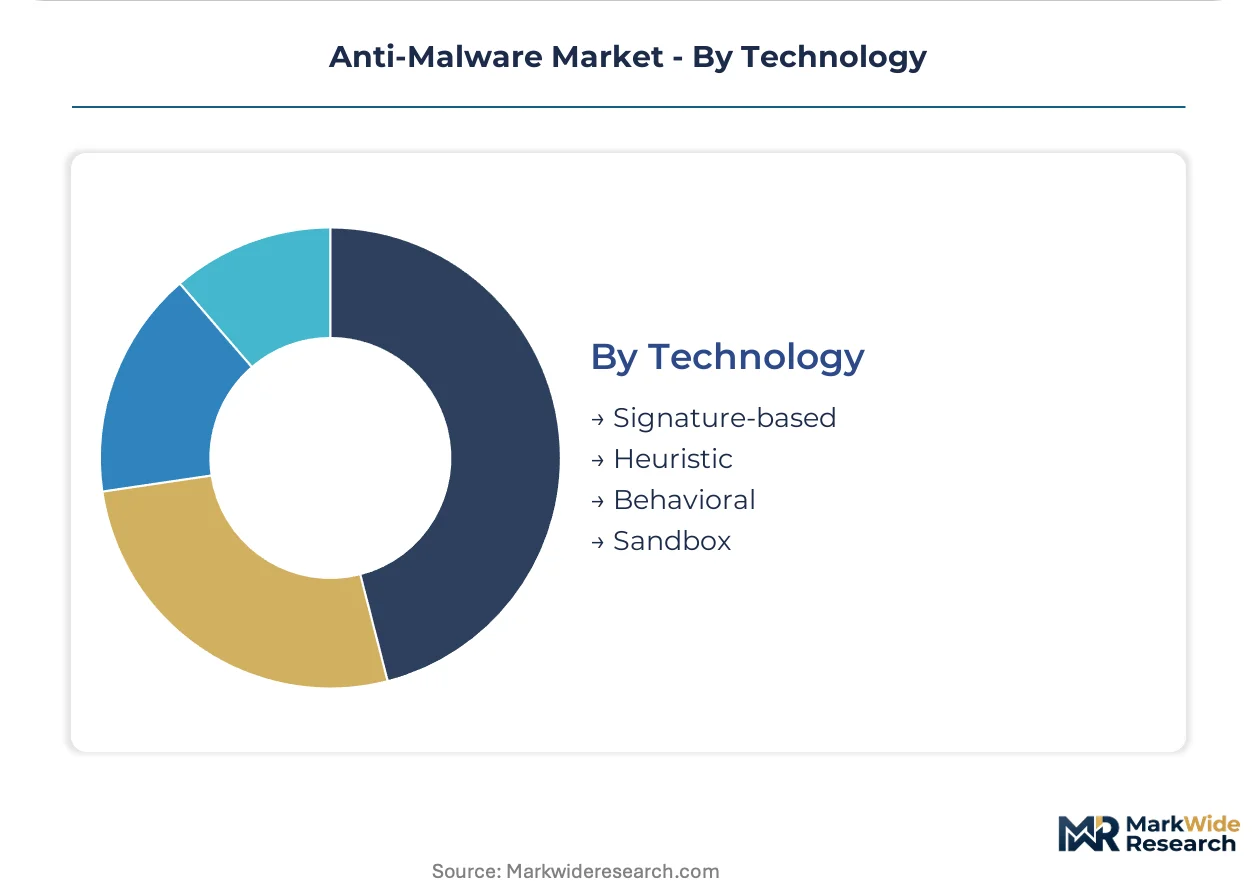
Technology:
Detection methodology determines R&D intensity and refresh cycle velocity for vendor engineering teams.
- Behavioral:Machine-learning models analyze process execution patterns to identify polymorphic malware without prior signature knowledge. Vendors compete on engineering depth as static detection becomes commoditized. This technology is climbing the fastest as polymorphic strains evade signature databases.
- Signature-based:Hash matching against known malware databases remains foundational for high-volume, low-complexity threat categories. Open-source threat intelligence feeds and MITRE ATT&CK framework adoption erode proprietary differentiation.
- Heuristic:Rule-based analysis of code structure and API calls detects variants of known malware families without exact signature matches. Mid-tier vendors leverage heuristics to extend protection between signature updates.
- Sandbox:Isolated execution environments detonate suspicious files to observe behavioral indicators before allowing system access. Financial services and defense sectors mandate sandboxing for advanced persistent threat protection.
Signature-based technology retains the largest installed base; Behavioral analysis is expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Anti-malware solution development concentrates in the United States and Germany, while consumption spreads across financial centers and manufacturing hubs facing escalating ransomware exposure. Regulatory divergence between CISA zero-trust mandates and EU AI Act certification timelines is fragmenting vendor go-to-market strategies. Demand intensity correlates with critical infrastructure density and breach penalty severity rather than pure GDP scale.
United States
Financial services firms in New York and healthcare systems across the Midwest are expanding endpoint detection budgets following HIPAA settlements exceeding $50 million. CISA zero-trust architecture mandates now require continuous device verification for federal contractors and civilian agencies. Defense industrial base clusters in Northern Virginia and California's aerospace corridor are consolidating procurement under unified telemetry fabrics that span endpoint, identity, and network layers.
Germany
Automotive OEMs in Bavaria and industrial machinery builders across Baden-Württemberg are fortifying supply chain cybersecurity ahead of NIS2 implementation deadlines. The EU AI Act's risk-classification framework is extending product certification timelines for AI-enabled detection systems by 8-14 months. Frankfurt's financial services sector and Hamburg's port logistics operators are mandating IEC 62443-certified anti-malware stacks for IT/OT convergence projects.
Japan
Manufacturing operators in Toyota's supply chain and semiconductor fabricators in Kyushu are deploying behavioral detection engines to protect operational technology networks. METI guidance on critical infrastructure protection is elevating baseline security investment across energy and transportation sectors. Tokyo's financial institutions and Osaka's industrial automation clusters are prioritizing vendors with completed conformity assessments for high-risk AI systems.
United Kingdom
London's insurance and professional services firms are mandating automated forensic capabilities in endpoint protection procurement following FCA operational resilience rules. The UK National Cyber Security Centre's guidance on supply chain security is tightening vendor qualification criteria for critical national infrastructure operators. Manchester's healthcare trusts and Scotland's renewable energy projects are expanding managed detection service contracts to address SOC staffing gaps.
India
IT services exporters in Bengaluru and Hyderabad are embedding anti-malware agents across distributed workforce devices serving North American and European clients. RBI cybersecurity guidelines for financial institutions are accelerating compliance-driven procurement among Mumbai's banking sector. Delhi-NCR's government contractors and Pune's automotive suppliers are adopting cloud-native deployment models to bypass capital-intensive on-premises infrastructure.
Anti-Malware Market Competitive Environment
The competitive structure tilts toward platform bundling specialists with cross-product telemetry integration capabilities. Consolidation pressure favors vendors offering unified endpoint, network, and identity protection suites over point-product specialists. Three archetypes dominate: legacy consumer-to-enterprise crossover brands, cloud-native security architects, and machine-learning engineering specialists. M&A activity concentrates on behavioral detection engine acquisitions and managed security service provider partnerships.
Among consumer-to-enterprise crossover specialists, McAfee and Norton occupy positions leveraging brand recognition for multi-channel distribution across small enterprises and individual professionals. Trend Micro anchors cloud-native security architectures for Asia-Pacific data center operators requiring elastic scaling. Bitdefender exemplifies the machine-learning engineering archetype, competing on detection depth as signature-based systems commoditize.
| Leading Market Players |
|---|
| McAfee |
| Trend Micro |
| Bitdefender |
| ESET |
| Avira |
| Norton |
| F-Secure |
| Malwarebytes |
| Avast |
| Others |
Value Chain & Pricing Dynamics
Private-equity-rolled-up endpoint protection vendors anchor supply discipline through centralized threat intelligence infrastructure, translating scale economies into subscription pricing power while compressing margins for standalone signature-based competitors.
Pricing Analysis
Margin tightening in mid-tier endpoint protection reflects open-source threat intelligence commoditizing proprietary signature databases. Three-tier pricing structure across premium, standard, and economy levels segments by AI-augmented detection depth and managed response bundling. Cost compression accelerates because AWS, Azure, and Google Cloud native controls absorb basic anti-malware functions. Small enterprises exhibit highest price sensitivity, favoring consumer-to-enterprise crossover brands, while defense contractors accept premium tiers for zero-trust compliance.
Supply Chain Analysis
Dual-sourcing requirements from German automotive OEMs and US federal contractors mandate multi-vendor qualification for threat intelligence feeds and detection engine components. Supply concentrates in the United States, Germany, and Israel for core machine-learning engineering talent. Raw material dependencies span cloud compute infrastructure, labeled training datasets, and CVE vulnerability databases. Single-source vulnerability in proprietary behavioral model training pipelines threatens vendor differentiation. Distribution runs through direct enterprise sales, MSSP channel partners, and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical integration into managed detection services represents the decisive upstream lever as mid-market buyers outsource SOC functions and vendors capture recurring revenue through multi-tenant architectures.
For Market Incumbents: Anticipate adversarial AI arms race pressures by accelerating behavioral model retraining cycles and acquiring specialist firms with operational technology expertise. Consolidate procurement influence through unified zero-trust telemetry fabrics that span endpoint, identity, and network layers. Certification investment in EU AI Act conformity assessments protects European revenue recognition timelines against compliance-driven disqualification. For New Entrants and Emerging Players: AI-native sandboxing engines for healthcare operational technology networks offer the most penetrable white-space target, given HIPAA breach penalty concentration and limited incumbent OT specialization. Target mid-market German automotive suppliers facing NIS2 implementation deadlines with IEC 62443-certified managed service offerings. Channel partnership with established MSSPs accelerates customer acquisition without direct enterprise sales infrastructure. For Investors and Strategic Acquirers: Distressed-cycle entries favor behavioral detection engine specialists in Israel and Germany with completed EU AI Act documentation and healthcare OT deployment traction. Long-term viability hinges on machine-learning engineering depth rather than signature database scale. Watch NIST post-quantum cryptography standard adoption velocity as inflection indicator for defense and financial sector firmware upgrade cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Managed Detection Service Launch | Captures mid-market SOC outsourcing demand through multi-tenant platform architecture. |
| EU AI Act Certification Completion | Secures CE marking for high-risk AI systems ahead of German automotive procurement deadlines. |
| Operational Technology Integration | Extends endpoint protection into industrial control networks under IEC 62443 mandates. |
| Behavioral Engine Acquisition | Consolidates machine-learning talent as polymorphic malware evades signature detection. |
| Hyperscaler Marketplace Expansion | Distributes cloud-native agents through AWS, Azure, and Google Cloud procurement channels. |
Study Parameters
Multi-period observation of endpoint protection seat license volumes, threat intelligence feed subscriptions, and breach penalty settlements anchored the trend analysis, supplemented by interviews with CISOs at US federal contractors, German automotive procurement officers, healthcare information security directors, MSSP operations leads, and cloud security architects. Secondary validation drew from CISA zero-trust implementation guidance, EU AI Act conformity assessment documentation, HIPAA breach settlement records, and SEC cybersecurity disclosure filings. Bottom-up deployment model sizing and top-down IT security budget allocation analysis were triangulated against vendor revenue segment disclosures.
Segment-weighting across product type, deployment model, end-user organization scale, detection technology methodology, and regional regulatory cluster determined value distribution. CAGRs were derived from elasticity modeling of security budget growth against breach incident frequency and compliance mandate implementation timelines. Forecast inputs incorporated NIS2 directive deadline phasing, NIST post-quantum cryptography standard adoption curves, and hyperscaler security control roadmaps.
Several conditions sit outside the modeled scope, including nation-state cyberattack escalation beyond ransomware patterns, quantum computing cryptanalytic breakthroughs ahead of PQC migration, and vendor consolidation through unannounced M&A activity. Forecasts assume steady-state regulatory enforcement intensity and stable cloud infrastructure pricing. Deviation in EU AI Act risk-classification interpretation or CISA zero-trust mandate acceleration would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Network Security Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Cognitive Security Market
Cybersecurity
Kuwait Cybersecurity Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Thailand IT and Security Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Home Wi-Fi Security Solutions Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Botnet Detection Market