
 Industrial Cybersecurity Market | 2026-2036
Industrial Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Industrial Cybersecurity Market Intelligence
The substitution of traditional air-gapped systems with cloud-integrated Industrial IoT (IIoT) platforms is repositioning the economic calculus for operational technology security. This shift creates new vulnerabilities that require sophisticated defense mechanisms. Siemens AG leverages its deep automation expertise to embed security into its industrial controllers and software. In parallel, Palo Alto Networks specializes in network security, offering advanced firewalls and threat intelligence tailored for industrial environments.
Industrial cybersecurity involves the protection of operational technology (OT) and industrial control systems (ICS) from digital threats. This discipline focuses on securing specific industrial protocols like Modbus and DNP3 to prevent disruption of physical processes. The primary purpose is to maintain the safety, availability, and integrity of critical infrastructure. Among product types, Security Information and Event Management (SIEM) solutions are central for correlating threat data across OT networks. The energy sector represents a critical end-user segment, with investments driven by grid modernization and resilience mandates.
Regulatory frameworks are a significant factor shaping technology adoption and investment priorities. In the United States, guidelines from CISA provide a foundation for critical infrastructure protection. The European Union's NIS2 Directive imposes stringent cybersecurity requirements and incident reporting obligations on a wider range of sectors. Similarly, China's Multi-Level Protection Scheme (MLPS) 2.0 enforces specific security standards for networks operating within the country. The key decision for operators is how to implement a unified security posture that satisfies these diverse and evolving compliance demands.
Market Dynamics
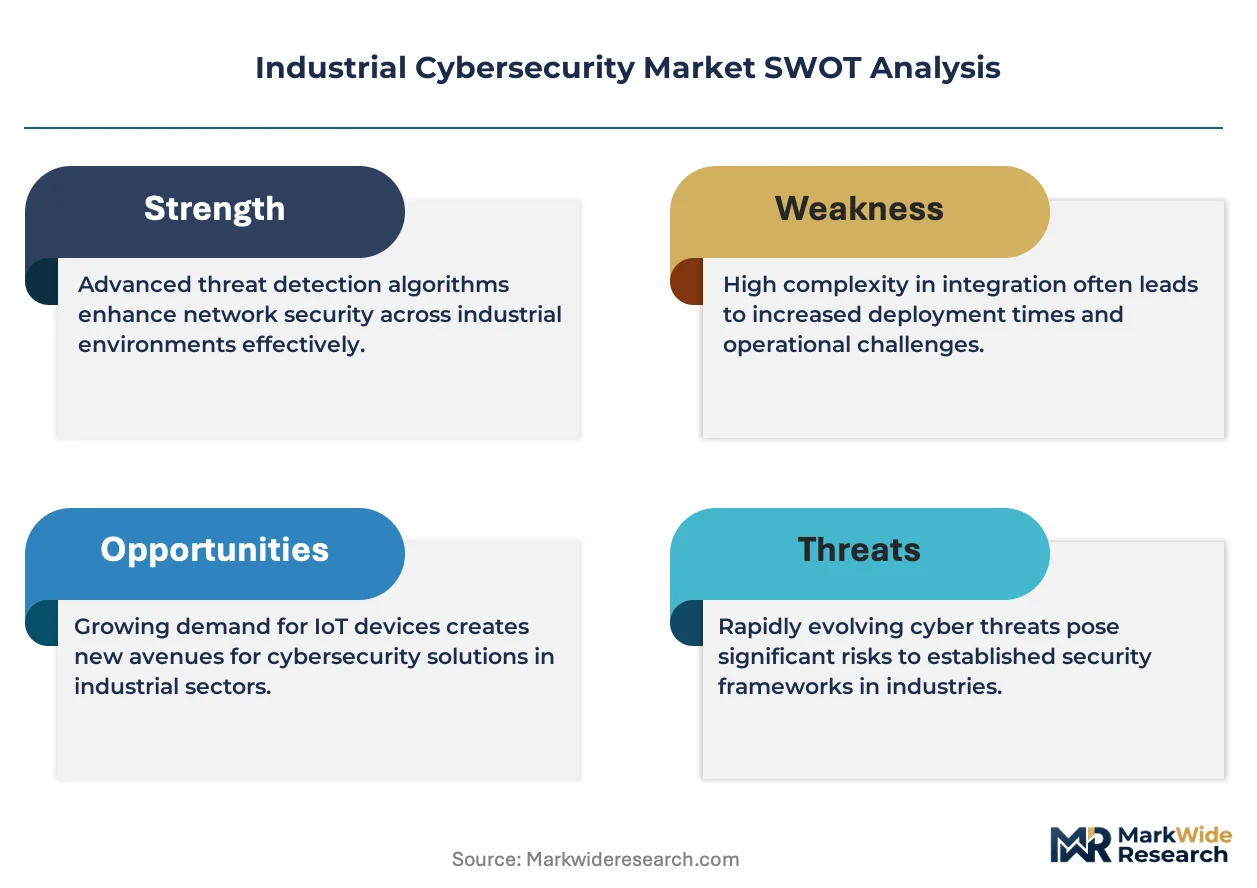
The convergence of operational technology (OT) with information technology (IT) networks is the central force shaping the industrial cybersecurity market. This integration, driven by IIoT adoption, dissolves traditional air-gaps and introduces new attack vectors, compelling a fundamental security paradigm shift.
Growth Catalysts
- Regulatory Mandates:The EU's NIS2 Directive expands security and reporting obligations to more entities in sectors like manufacturing and food production, directly compelling investment in compliant cybersecurity solutions to avoid significant penalties.
- IIoT Proliferation:The deployment of connected sensors and devices across manufacturing floors and utility grids generates vast amounts of data that require protection, creating inherent demand for security platforms that can monitor industrial protocols.
- Grid Modernization Initiatives:In the United States, federal and state-level mandates for enhancing the resilience of the electrical grid against cyber threats are channeling significant investment into advanced security for energy sector control systems.
Market Restraints
- Legacy System Integration:A substantial installed base of legacy industrial control systems running proprietary protocols presents a major barrier, as these systems were not designed for connectivity and are difficult to secure without risking operational disruption.
- Talent Scarcity:A persistent shortage of cybersecurity professionals with dual expertise in both IT security principles and OT engineering processes constrains the ability of organizations to implement and manage effective security programs.
- Compliance Fragmentation:Multinational operators face significant complexity and cost in reconciling divergent regulatory requirements, such as the EU's NIS2, China's MLPS 2.0, and CISA guidelines in the US, into a single, coherent security strategy.
Strategic Opportunities
- Managed Security Services:The complexity of OT security creates a significant opportunity for specialized Managed Security Service Providers (MSSPs) to offer subscription-based monitoring, threat hunting, and incident response tailored for industrial environments.
- AI-Powered Threat Detection:Integrating artificial intelligence and machine learning into SIEM and network monitoring tools enables predictive analytics, allowing for the detection of anomalous behavior and potential threats before they cause physical disruption.
- Securing Digital Twins:As manufacturers adopt digital twin technology for process simulation and optimization, a new opportunity emerges to provide cybersecurity solutions that protect the integrity and confidentiality of these highly detailed virtual models.
Industry Challenges
- Integration with Physical Safety Systems:Ensuring that cybersecurity controls do not interfere with or compromise the functional safety systems designed to prevent physical harm is a critical and complex technical challenge for solution providers and asset owners.
- Supply Chain Vulnerabilities:Securing the industrial supply chain is a major challenge, as vulnerabilities can be introduced at any point from device manufacturing to system integration, requiring extensive vetting and continuous monitoring of third-party components.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Industrial Cybersecurity Market |
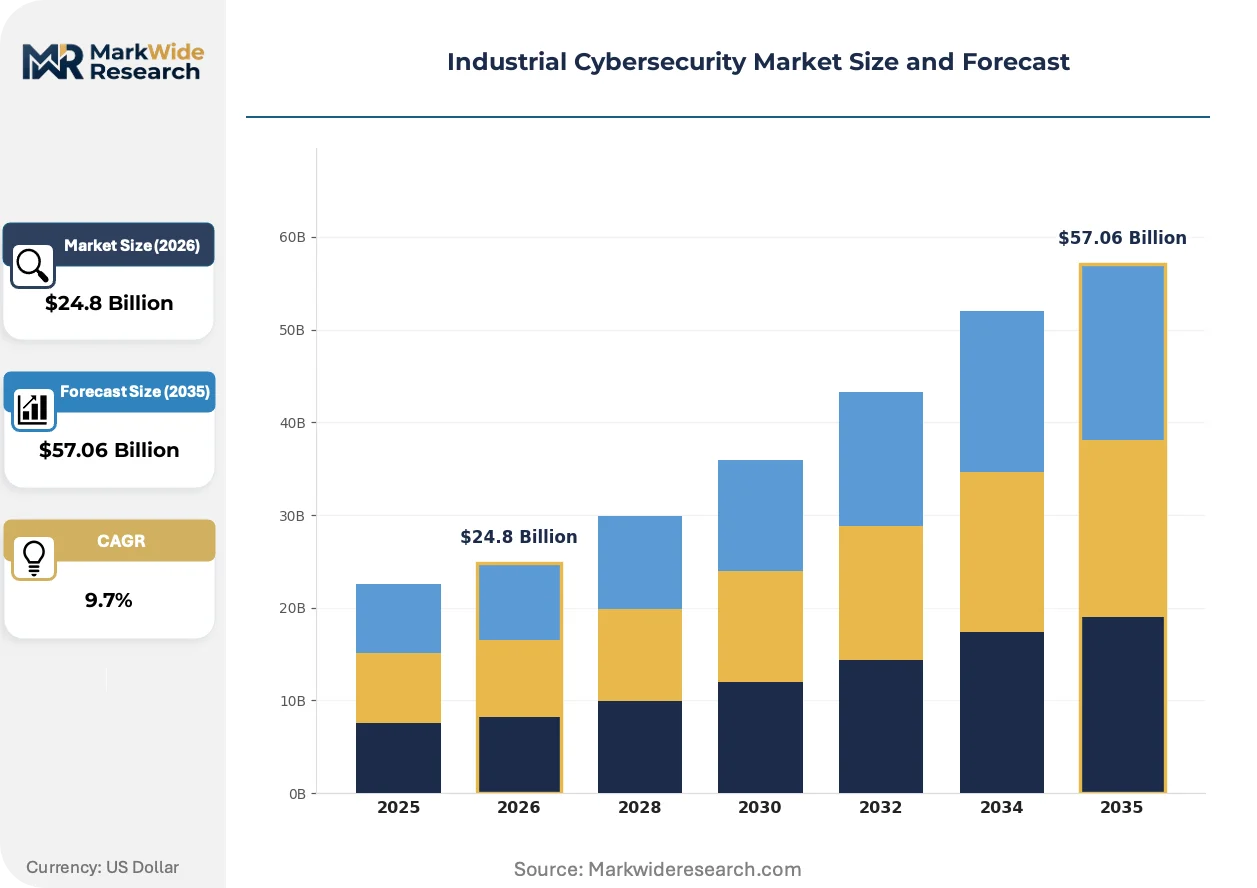
| Market Size in 2026 | $24.8 Billion |
| Market Size in 2035 | $57.06 Billion |
| CAGR (2026 – 2036) | 9.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Intrusion Detection System, Security Information and Event Management, Identity Access Management End User: Manufacturing, Transportation, Energy, Utilities Deployment: Cloud-Based, On-Premises, Hybrid, Managed Services Technology: AI-Based, Machine Learning, Blockchain, Encryption |
| Companies Covered | Siemens AG, Honeywell International Inc., Schneider Electric SE, ABB Ltd., IBM, Microsoft, Cisco Systems Inc., Palo Alto Networks, Fortinet Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Industrial Cybersecurity Market Strategic Shifts & Innovations
The market is defined by a strategic pivot from reactive, perimeter-based defense to proactive, identity-centric security models. This evolution is a direct response to the increasing sophistication of threats targeting critical operational technology environments.
Zero Trust Architecture in OT
Zero Trust Architecture (ZTA) is a security framework that assumes no implicit trust and continuously validates every stage of a digital interaction. Critical infrastructure sectors, including water utilities and chemical manufacturing, are adopting ZTA to mitigate risks from insider threats and compromised credentials. This implementation is decentralizing security enforcement from the network perimeter to individual devices and users, necessitating granular micro-segmentation within OT networks.
China's MLPS 2.0 Enforcement
China's Multi-Level Protection Scheme (MLPS) 2.0 establishes a comprehensive legal framework for cybersecurity. The regulation mandates that operators of critical information infrastructure, including industrial control systems, implement specific security controls and undergo regular government assessments. This policy is compelling both domestic and foreign companies operating in China to invest in compliant security technologies and re-evaluate their data governance strategies for OT environments.
Shift to Managed Service Models
A notable behavioral shift is occurring as asset owners move from capital expenditure on standalone security products to operational expenditure on managed services. Instead of building extensive internal security operations centers, organizations are outsourcing OT threat monitoring and incident response to specialized providers. This trend is particularly visible in the European manufacturing and US energy sectors, where it addresses the persistent shortage of qualified cybersecurity talent.
Industrial Cybersecurity Market Segmentation
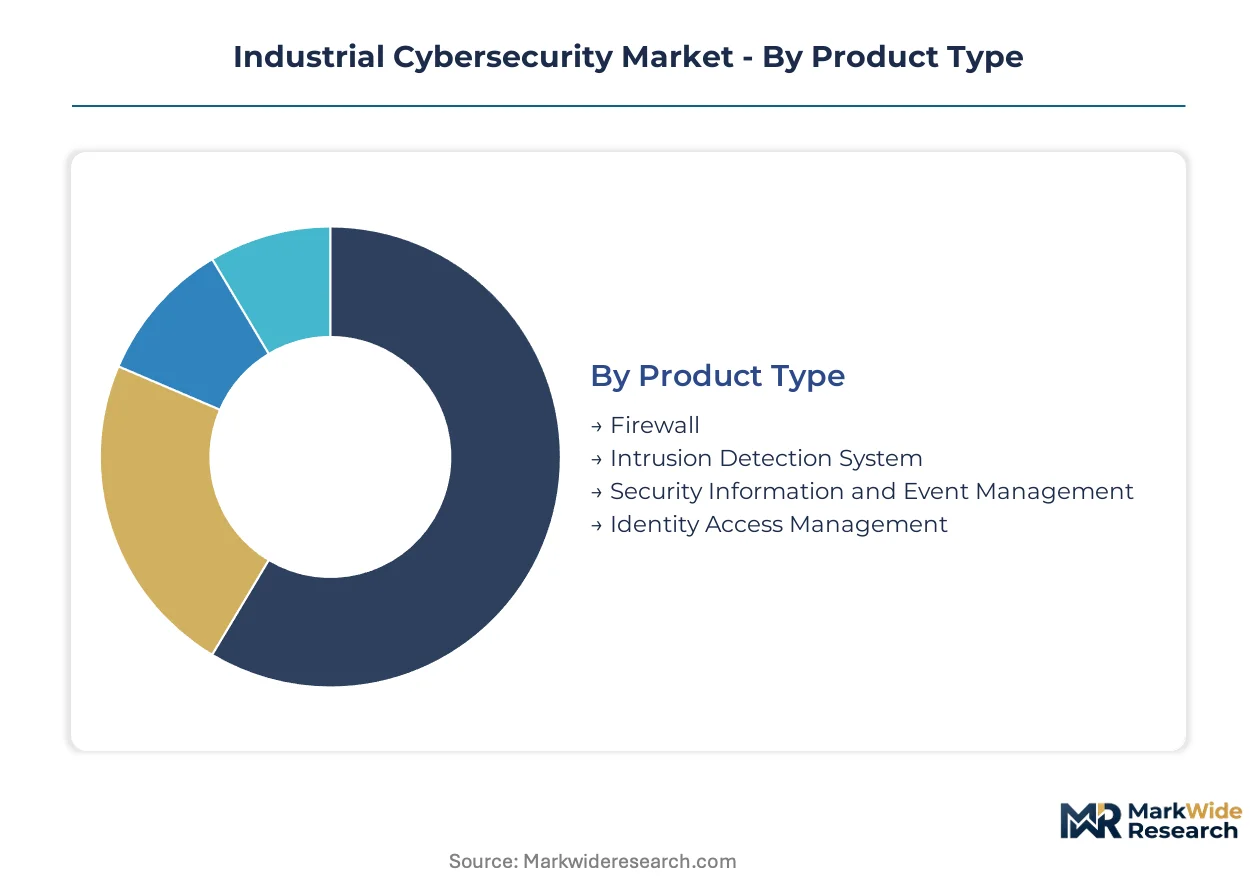
The industrial cybersecurity market segments by how operators safeguard critical infrastructure and industrial processes against digital threats. Understanding these distinctions helps stakeholders address specific vulnerabilities and deploy targeted defense mechanisms across diverse operational technology landscapes.
Product Type:
Operators prioritize specific product types based on their immediate security posture gaps and compliance requirements within complex OT environments.
- Security Information and Event Management (SIEM):Central for correlating threat data across OT networks, providing a unified view of security events. Demand concentrates in critical infrastructure sectors like energy, driven by the need for comprehensive threat visibility and incident response.
- Firewall:Provides fundamental network segmentation and access control, acting as the primary barrier against unauthorized traffic. Its deployment is critical in connecting OT networks to IT systems, particularly in manufacturing facilities adopting IIoT.
- Intrusion Detection System:Monitors network traffic for suspicious activities and known attack patterns, alerting operators to potential breaches.
- Identity Access Management:Manages and controls user access to industrial systems and data, crucial for preventing insider threats and unauthorized configuration changes.
Volume sits with Firewall installations; growth tilts toward Security Information and Event Management solutions.
End User:
The application of industrial cybersecurity varies significantly across different operational domains, reflecting distinct risk profiles and regulatory pressures.
- Manufacturing:This sector integrates advanced automation and IIoT, exposing OT networks to new cyber risks. Investment is driven by the need to protect production lines and intellectual property in hubs like Germany.
- Energy:Securing the electrical grid and power generation facilities is paramount due to critical infrastructure status. Grid modernization initiatives in the United States mandate robust cybersecurity for resilience.
- Transportation:Protecting railway signaling, air traffic control, and port operations from cyber threats ensures public safety and operational continuity.
- Utilities:Safeguarding water treatment, wastewater management, and gas distribution systems is essential for public health and continuous service delivery.
Regulatory mandates, such as the EU's NIS2 Directive, disproportionately influence security investments within the Manufacturing and Energy sectors.
Deployment:
Organizations choose deployment models based on their existing IT infrastructure, resource availability, and specific operational security requirements.
- Managed Services:Specialized providers offer outsourced monitoring, threat hunting, and incident response, addressing the talent scarcity challenge for asset owners. This model is gaining traction in European manufacturing and US energy sectors.
- Cloud-Based:Leverages scalable cloud infrastructure for security operations, supporting remote access and IIoT integration. This model offers flexibility but requires careful consideration of data sovereignty and connectivity risks.
- On-Premises:Traditional deployment where security infrastructure is hosted within the organization's physical facilities, offering maximum control for sensitive OT systems.
- Hybrid:Combines on-premises security components with cloud-based services, balancing control with scalability and advanced threat intelligence capabilities.
Managed Services deployments represent the fastest-growing trajectory, reflecting a strategic shift in operational expenditure.
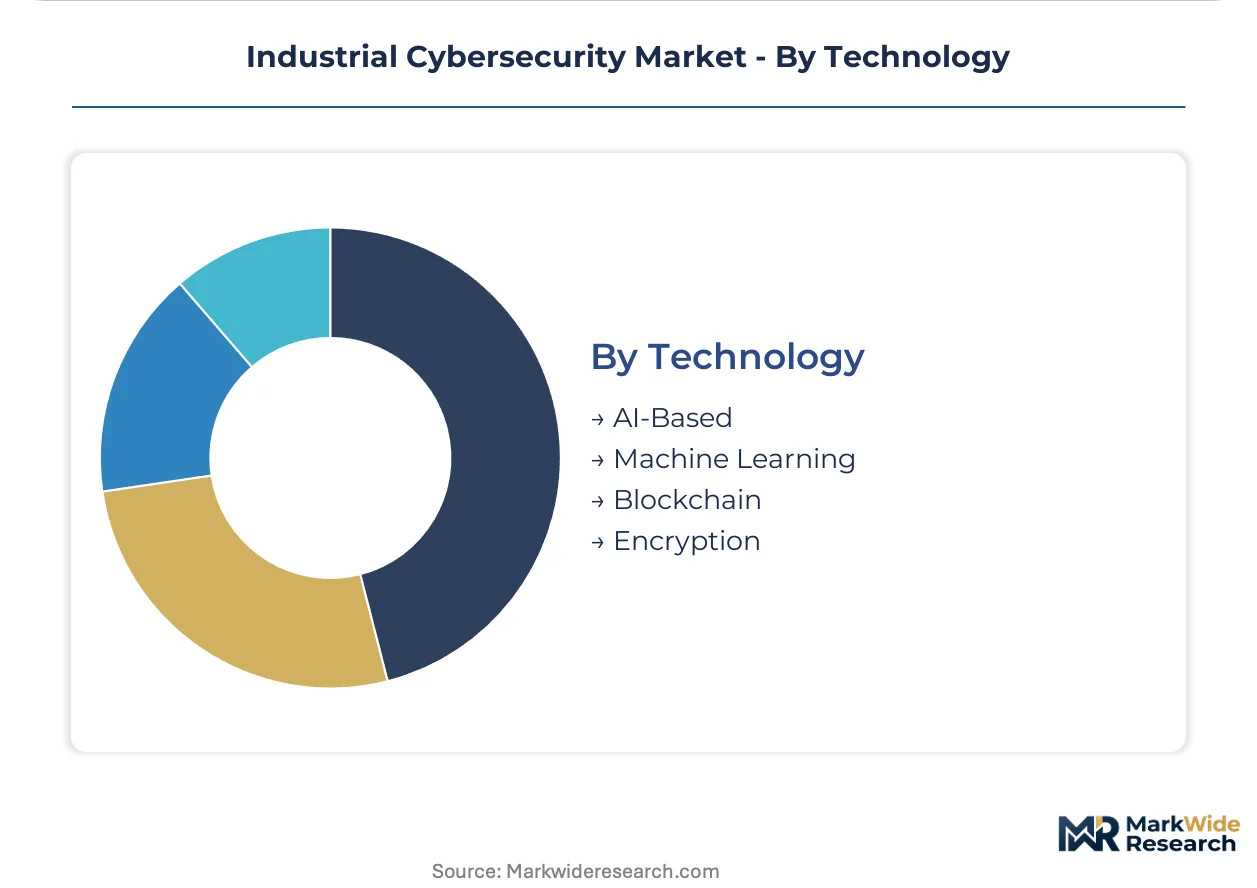
Technology:
Innovation in industrial cybersecurity is driven by the integration of advanced technologies designed to counter sophisticated and evolving digital threats.
- AI-Based:Utilizes artificial intelligence algorithms for predictive analytics and anomaly detection, identifying potential threats before they impact physical processes. This technology enhances SIEM and network monitoring tools.
- Machine Learning:Enables systems to learn from vast datasets of industrial network traffic, improving the accuracy of threat detection and reducing false positives in dynamic OT environments.
- Blockchain:Offers decentralized and immutable ledger technology for securing supply chains and ensuring data integrity in critical industrial applications.
- Encryption:Protects data confidentiality and integrity during transmission and storage within OT networks and across connected IIoT devices.
AI-Based and Machine Learning technologies are profoundly impacting threat detection capabilities, driving new solution development.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand for industrial cybersecurity solutions notably concentrates within Germany's advanced manufacturing hubs and the United States' energy sector. This geographical focus reflects the high value of critical infrastructure and the rapid integration of IIoT in these regions. Global industrial operators prioritize securing complex OT environments against evolving digital threats.
United States
The United States energy sector drives significant demand for industrial cybersecurity due to grid modernization initiatives and resilience mandates. CISA guidelines provide a foundational framework for critical infrastructure protection across various industries. Investment in advanced security solutions is prominent in Texas, where energy production and distribution networks require robust defense.
Germany
Germany's advanced manufacturing sector fuels substantial demand for industrial cybersecurity, particularly in protecting highly automated production lines. The EU's NIS2 Directive mandates stringent cybersecurity requirements for essential entities, compelling German manufacturers to invest. Bavaria's industrial clusters are actively adopting sophisticated defense mechanisms for their connected factories.
China
China's critical information infrastructure, including industrial control systems, necessitates robust cybersecurity measures under MLPS 2.0 enforcement. This regulation compels both domestic and foreign companies to implement specific security controls. The Yangtze River Delta region, a major manufacturing hub, sees significant investment in compliant security technologies.
Japan
Japan's automotive and industrial machinery sectors are key demand drivers for industrial cybersecurity, safeguarding complex supply chains and intellectual property. METI provides guidance for enhancing industrial control system security within critical infrastructure. The Chubu region, home to major manufacturing, focuses on securing integrated OT-IT environments.
France
France's utilities and transportation sectors require advanced industrial cybersecurity to maintain operational continuity and public safety. The NIS2 Directive significantly impacts French entities, expanding security and reporting obligations across a wider range of sectors. The Île-de-France region, with its critical infrastructure and industrial base, prioritizes incident response and threat detection capabilities.
Industrial Cybersecurity Market Key Industry Players
Branded specialists and contract manufacturers split share differently across segments within the industrial cybersecurity market. The market structure exhibits a tiered consolidation, with established industrial automation vendors competing alongside specialized cybersecurity providers. Strategic archetypes include integrated OT security platforms and pure-play network security firms. Companies primarily engage in strategic partnerships to expand their solution portfolios and pursue targeted acquisitions for technology integration.
Within the integrated OT security platform archetype, Siemens AG exemplifies deep automation expertise, embedding security directly into its industrial controllers and software offerings for seamless operational protection. Palo Alto Networks represents the pure-play network security segment, providing advanced firewalls and threat intelligence specifically tailored for industrial environments and network perimeter defense. IBM occupies a position across both domains, delivering comprehensive cybersecurity services and solutions that extend into critical OT/ICS protection, leveraging its broad enterprise security portfolio and consulting capabilities. These players anchor distinct yet interconnected approaches to securing complex industrial operations.
| Leading Market Players |
|---|
| Siemens AG |
| Honeywell International Inc. |
| Schneider Electric SE |
| ABB Ltd. |
| IBM |
| Microsoft |
| Cisco Systems Inc. |
| Palo Alto Networks |
| Fortinet Inc. |
| Others |
Cost & Logistics Intelligence
Venture-backed technology firms, often specializing in niche cybersecurity solutions, influence supply behavior by introducing innovative, focused products. This specialization can impact pricing discipline, particularly in segments requiring advanced threat intelligence or compliance-specific features. Pricing strategies often balance the cost of specialized talent with the value of critical infrastructure protection.
Pricing Analysis
The market exhibits a volume-versus-margin dynamic, where high-volume firewall installations command lower per-unit margins compared to specialized SIEM solutions. Subscription-based models for managed services and project-based pricing for large-scale implementations are common. Brand reputation, such as that of Siemens or Palo Alto Networks, and the level of integration required for complex OT environments drive price differentiation. Pricing softness reflects the persistent talent scarcity, which increases operational costs for solution providers. Smaller manufacturers are more price-sensitive than critical infrastructure operators in the energy and utilities sectors.
Supply Chain Analysis
The requirement for dual-sourcing for critical industrial cybersecurity components often drives diversification among asset owners. Supply concentration resides in the United States, Germany, and China for technology development and specialized hardware. The supply chain draws from highly specialized software libraries, specific hardware components like industrial-grade firewalls, and a global pool of cybersecurity talent. Vulnerabilities within third-party software components pose a significant structural risk. Specialized integrators and managed security service providers (MSSPs) dominate downstream distribution channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The industrial cybersecurity market is fundamentally a cost-of-compliance story. The EU's NIS2 Directive creates a significant barrier-to-entry moat, favoring providers that can demonstrate adherence to stringent security and reporting obligations.
For Market Incumbents: Deepen existing integrations with diverse operational technology (OT) systems. Incumbents should pursue strategic acquisitions of niche AI-powered threat detection firms to counter the new attack vectors from cloud-integrated IIoT platforms. This secures market share against emerging pure-play cybersecurity specialists.
For New Entrants and Emerging Players: The EU's NIS2 Directive in Europe opens a window for new entrants offering specialized managed security services. Focus on under-served small to medium-sized manufacturing facilities that lack internal OT security expertise. A go-to-market angle of outcome-based service level agreements for incident response can build rapid trust.
For Investors and Strategic Acquirers: Distressed-cycle entries favor specialized technology providers in the European manufacturing sector. The long-term viability of industrial cybersecurity is assured, given its essential role in critical infrastructure protection over the next decade. Target acquisition archetypes include AI/ML-driven threat detection startups and specialized managed security service providers. Watch for increasing consolidation among smaller OT security point solution providers as an inflection indicator.
| Strategic Initiative | Industry Significance |
|---|---|
| Strategic Partnership | Expand solution portfolios through collaboration with IT network security specialists. |
| AI/ML Integration | Enhance threat detection capabilities using predictive analytics for OT network anomalies. |
| Managed Service Expansion | Address talent scarcity by offering subscription-based OT security monitoring. |
| Compliance-as-a-Service | Provide tailored solutions to help entities meet NIS2 Directive requirements. |
| Digital Twin Security | Protect integrity and confidentiality of industrial process simulation models. |
Research Approach
Trade association data, regulatory filings, and customs records anchored secondary inputs for this analysis. Primary interviews with OT security managers, CISOs in industrial firms, and solution architects from leading vendors provided critical insights. This was validated against secondary sources including CISA guidelines, NIS2 Directive documentation, and academic cybersecurity research. Bottom-up and top-down triangulation ensured data consistency.
The market was modeled at a granular level across Product Type, End User, Deployment, Technology, and specific industrial protocols. A robust analytical framework applied historical trends and future projections across the analysis window. Compound Annual Growth Rates (CAGRs) were derived from a synthesis of market drivers and restraints. IIoT adoption rates and regulatory compliance expenditure served as key forecast inputs.
The model assumes a particular technology adoption path; alternative pathways for quantum-resistant cryptography would alter the outlook. Forecasts reflect current geopolitical stability and the pace of regulatory enforcement. Deviation in major cyberattack frequency or new zero-day vulnerabilities would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
DNS Security Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Cognitive Security Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Application Security Market
Cybersecurity
Europe Data Exfiltration Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Global Mobile Application Security Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
UK Cybersecurity Market