
 Benelux Cybersecurity Market | 2026-2036
Benelux Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Benelux Cybersecurity Market Outlook
The EU Digital Operational Resilience Act (DORA) is broadening procurement mandates for financial entities across Belgium, Luxembourg, and the Netherlands. Orange Cyberdefense leverages its sovereign European footprint to anchor managed security services for regulated banks in Luxembourg. Palo Alto Networks competes through platform consolidation, while Fox-IT specializes in high-assurance threat intelligence for Dutch government and defense clients.
Cybersecurity in the Benelux denotes the integrated hardware, software, and service stack protecting digital assets across endpoint, network, cloud, and application layers, incorporating zero-trust architecture, encryption protocols, and real-time threat detection with sub-millisecond response parameters. Its primary purpose is ensuring confidentiality, integrity, and availability of critical infrastructure across finance, healthcare, and government operations. Cloud Security within the Solution Type dimension leads absolute spending as Dutch and Belgian enterprises accelerate migration to distributed architectures. Managed Services within the Service Type dimension captures expanding margin pools as skills scarcity pushes enterprises toward outsourced security operations centers rather than in-house builds.
The Dutch Authority for Digital Infrastructure (RDI) enforces NIS2 transposition deadlines, while Belgium's Centre for Cyber Security Belgium (CCB) mandates sector-specific incident reporting for energy and transport operators. Luxembourg's CSSF integrates cybersecurity into financial supervision, creating overlapping compliance obligations for cross-border BFSI entities. Stakeholders must monitor how divergent national implementation timelines for EU-wide frameworks fragment procurement standards and vendor qualification requirements across the three jurisdictions.
Market Dynamics
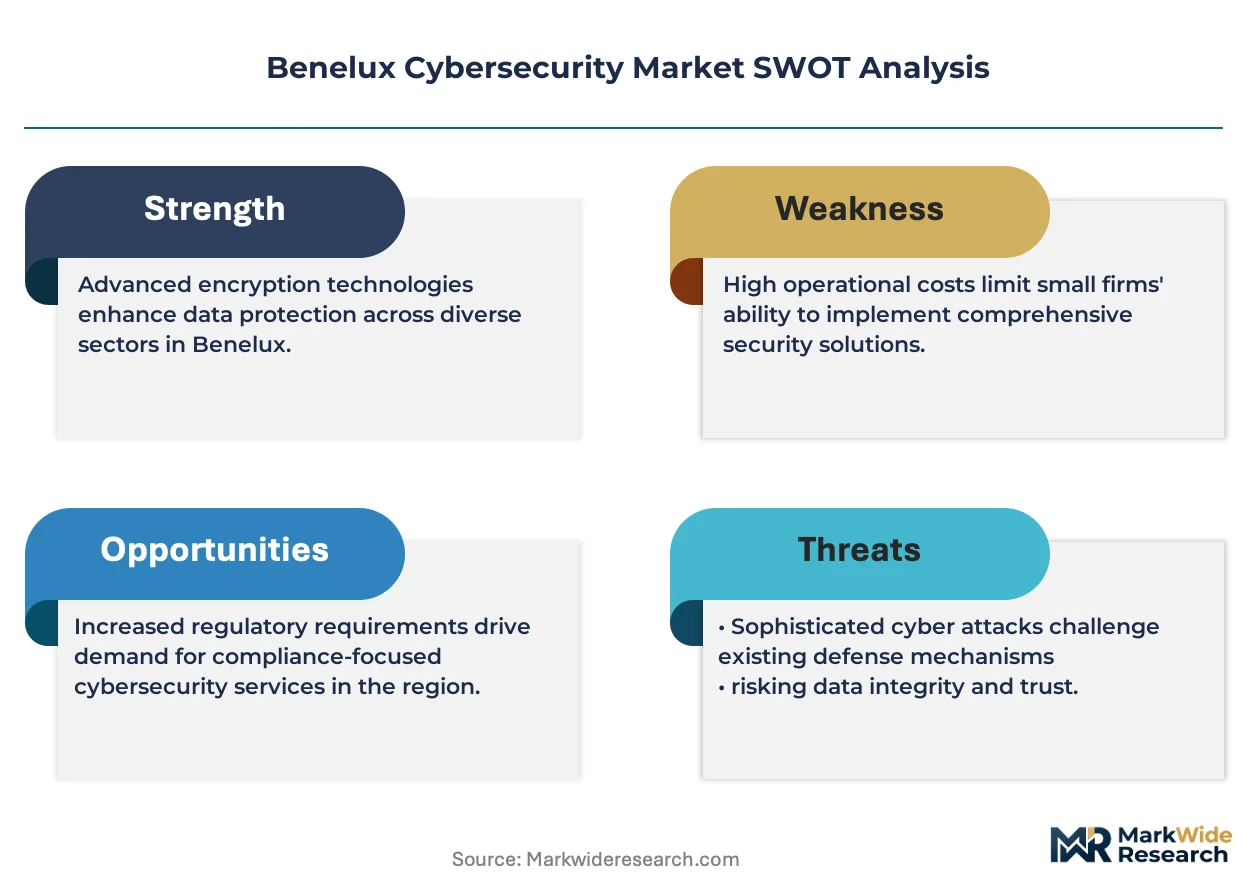
Compliance mandates from the EU AI Act and DORA are compressing procurement cycles across Belgian, Dutch, and Luxembourg financial institutions, forcing security architecture rebuilds ahead of rigid 2025-2026 deadlines.
Growth Catalysts
- DORA Operational Resilience Mandates:Financial entities in Luxembourg must overhaul third-party risk frameworks, expanding managed security service contracts.
- Cloud Migration Velocity:Dutch enterprises are abandoning on-premises data centers, creating demand for cloud-native security tooling and zero-trust network access.
- Amsterdam Data Center Density:The Netherlands hosts Europe's third-largest data center corridor, concentrating endpoint protection and threat detection procurement.
Market Restraints
- Specialized Talent Scarcity:Security operations center analysts with NIS2 compliance expertise command premium wages, inflating service delivery costs.
- Fragmented National Implementation:Belgium's CCB, the Netherlands' RDI, and Luxembourg's CSSF enforce divergent incident reporting timelines, complicating cross-border vendor qualification.
- Legacy Architecture Lock-in:Belgian energy and transport operators face multi-year decommissioning cycles for industrial control systems incompatible with modern encryption protocols.
Strategic Opportunities
- Luxembourg Wealth Management Sector:Family offices and private banks remain underpenetrated by managed detection and response providers despite stringent CSSF oversight.
- AI-Augmented Threat Hunting:Convergence of machine learning inference with security information and event management platforms enables predictive breach identification.
- Sovereign Cloud Certification:Dutch government's EOSN compliance framework creates first-mover advantage for domestic infrastructure providers meeting data localization requirements.
Industry Challenges
- Cross-Border Certification Complexity:Vendors must maintain parallel accreditations under Belgium's CCB, Netherlands' RDI, and Luxembourg's ANSSI schemes, stretching compliance budgets.
- Industrial Control System Integration:Belgian port operators and Dutch chemical manufacturers struggle to overlay modern zero-trust architectures atop decades-old SCADA environments without operational disruption.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Benelux Cybersecurity Market |
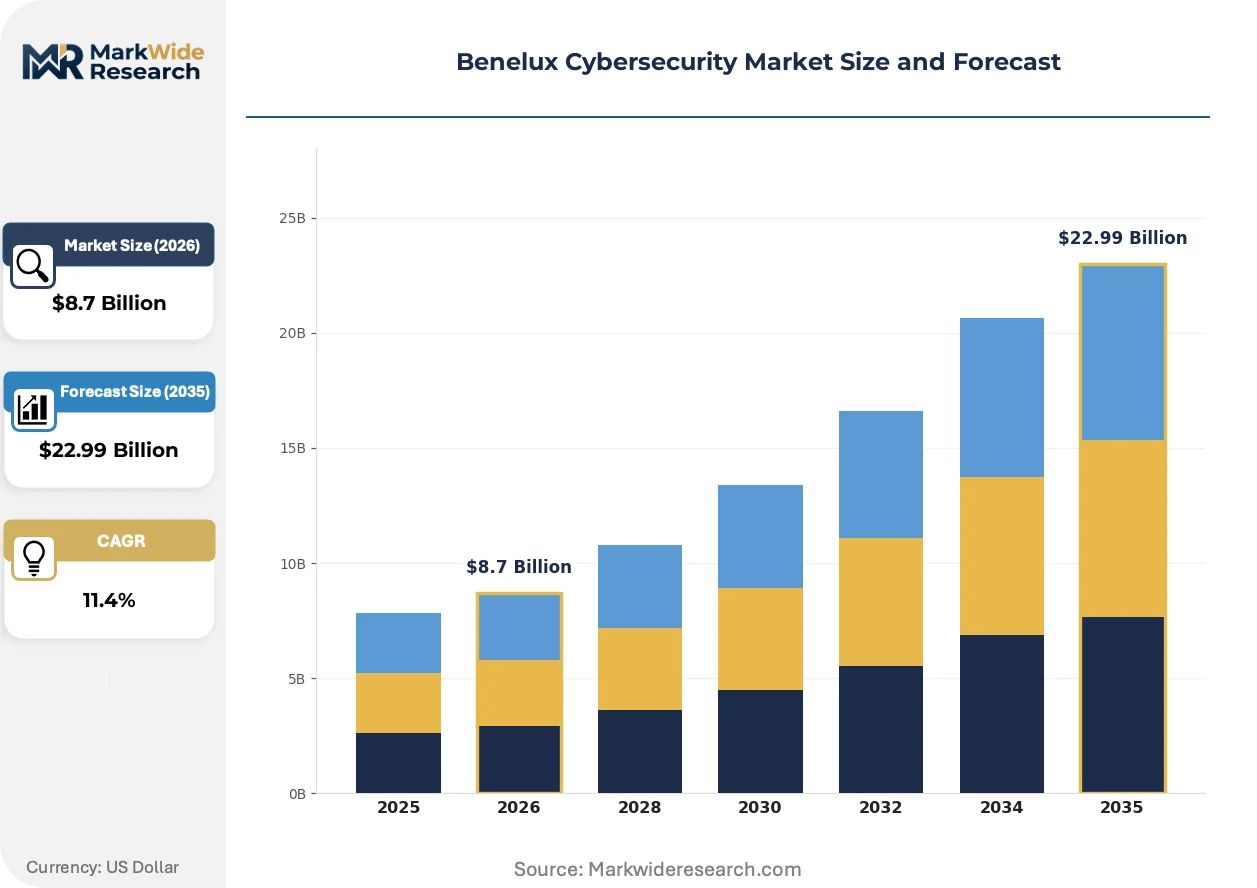
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $22.99 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Security, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Security End User: Government, BFSI, Healthcare, Retail Service Type: Consulting, Managed Services, Incident Response, Training |
| Companies Covered | Palo Alto Networks, Orange Cyberdefense, IBM Corporation, Dell Technologies Inc., Check Point Software Technologies Ltd., Cisco Systems Inc., Fox-IT, Eye Security, Fortinet Inc., Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Benelux Cybersecurity Market Strategic Shifts
Security platform consolidation is displacing point-product procurement across Benelux enterprises, with buyers prioritizing unified control planes over fragmented best-of-breed toolchains.
Extended detection and response platforms are unifying endpoint, network, and cloud telemetry into single-pane-of-glass consoles. Mid-market Dutch financial services firms are adopting these consolidated stacks fastest, compressing vendor counts from twelve to three. This unification is collapsing procurement cycles and marginalizing standalone antivirus vendors.
The EU AI Act's risk classification framework is mandating algorithmic transparency for automated threat detection systems. Security vendors must now document training data provenance and decision audit trails. Dutch critical infrastructure operators face the steepest compliance burden, accelerating investment in explainable AI tooling.
Subscription-based consumption is replacing perpetual licensing for security software across Belgian enterprise buyers. Channel partners are pivoting from resale margins to recurring managed service revenues. This shift is most pronounced in the Netherlands, where cloud-native security startups bypass traditional distribution entirely through direct digital sales.
Benelux Cybersecurity Market Segmentation
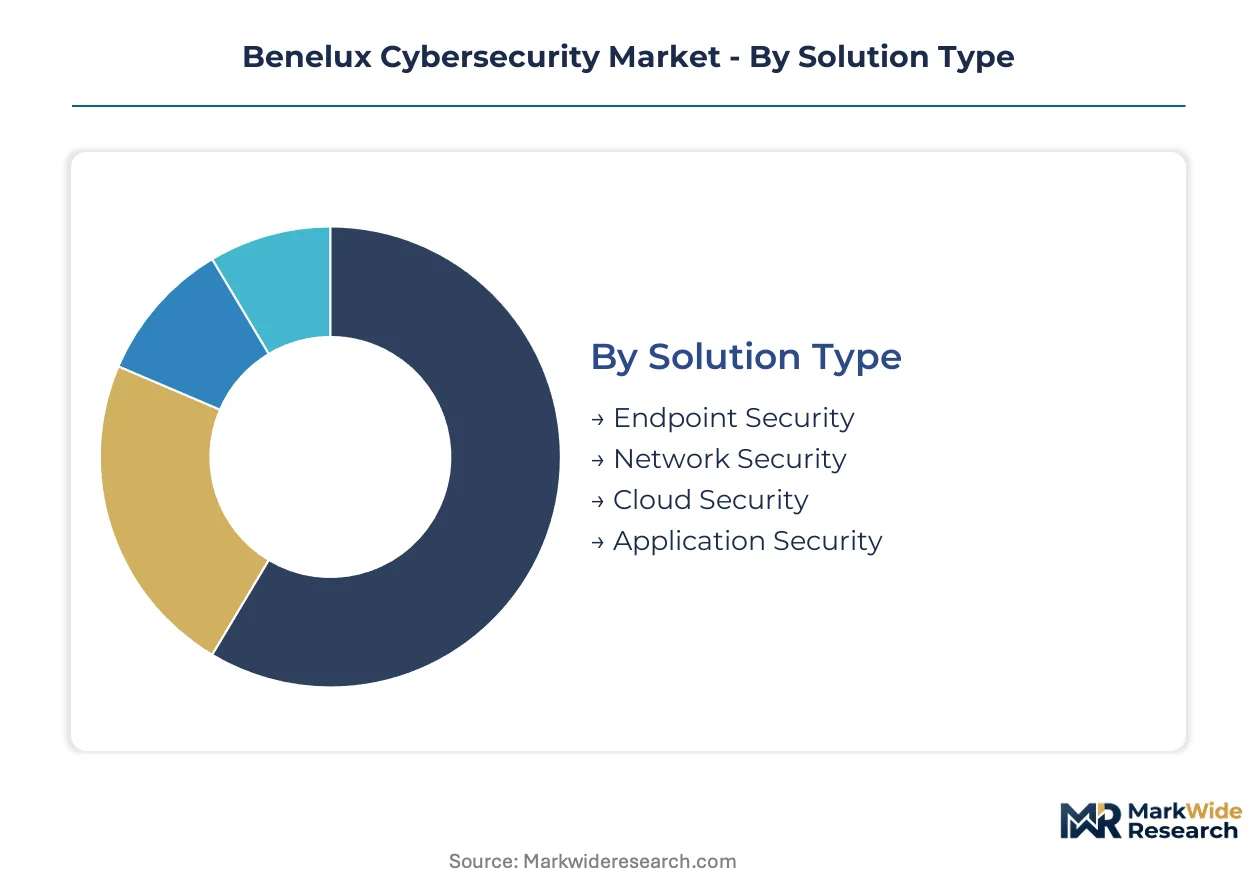
Security procurement across Belgium, the Netherlands, and Luxembourg fragments across four distinct axes, each reflecting divergent compliance pressures and infrastructure maturity. Understanding where spending concentrates within each dimension enables vendors to align R&D and channel investments with actual buyer behavior rather than assumed homogeneity.
Solution Type:
Upgrade cycles vary dramatically by solution layer, with cloud-native replacements outpacing endpoint refreshes by a factor of three in Dutch enterprise accounts.
- Cloud Security:Native protection for distributed workloads spans container scanning, posture management, and zero-trust access enforcement. Dutch financial services firms in Amsterdam and Rotterdam drive disproportionate procurement as they exit owned data centers under CSSF and DORA pressure.
- Endpoint Security:Device-level threat prevention incorporates extended detection and response, behavioral analytics, and automated isolation protocols. Belgian healthcare networks concentrate demand where Windows 7/8 legacy systems in hospitals require agent-based protection without full OS migration.
- Network Security:Perimeter and internal segmentation tools including next-generation firewalls and secure access service edge. Luxembourg wealth management offices prioritize encrypted traffic inspection for client data flows.
- Application Security:Code scanning, runtime protection, and API security for custom software portfolios. Dutch e-commerce platforms in Utrecht and Eindhoven expand investment ahead of EU AI Act algorithmic transparency mandates.
Volume placements concentrate in Cloud Security; the faster expansion belongs to Application Security as DevSecOps pipelines mature across Benelux software houses.
Deployment Model:
Cost tier differentiation separates buyers with captive security operations centers from those outsourcing entire detection and response functions.
- Managed Security:Fully outsourced security operations center with 24/7 monitoring, threat hunting, and incident response. Luxembourg private banks under CSSF supervision favor this model to address chronic analyst shortages without competing for Amsterdam talent.
- Cloud-Based:SaaS-delivered controls with no local infrastructure footprint. Mid-market Belgian retailers adopt fastest to bypass Brussels data center capacity constraints.
- Hybrid:Split architecture retaining sensitive workloads on-premises while bursting analytics to cloud. Dutch chemical manufacturers in the Port of Rotterdam corridor prefer this for SCADA isolation.
- On-Premises:Air-gapped or self-hosted appliances for maximum data sovereignty. Belgian defense contractors and Dutch government agencies maintain this stance despite higher total cost of ownership.
Margin capture favors Managed Security; customer acquisition economics are climbing the fastest for Cloud-Based deployments as direct digital sales displace channel intermediaries.
End User:
Maturity gaps between sectors create divergent purchasing rhythms, with government and BFSI operating on three-year cycles while healthcare extends to five.
- BFSI:Banks, insurers, and payment processors facing overlapping DORA, NIS2, and CSSF obligations. Dutch neobanks and Luxembourg private wealth managers lead cloud security spending.
- Government:National and municipal agencies with sovereign data requirements. Belgian federal ministries and Dutch water management authorities prioritize on-premises encryption.
- Healthcare:Hospitals, clinics, and pharmaceutical distributors with patient data protection mandates. Dutch academic medical centers in Leiden and Utrecht consolidate endpoint vendors under procurement centralization.
- Retail:Physical and digital commerce operators with seasonal demand spikes. Belgian fashion e-commerce platforms invest in application security for payment card environment compliance.
Contract values peak in BFSI; the steepest expansion trajectory sits with Healthcare as ransomware targeting accelerates hospital security budget approvals.
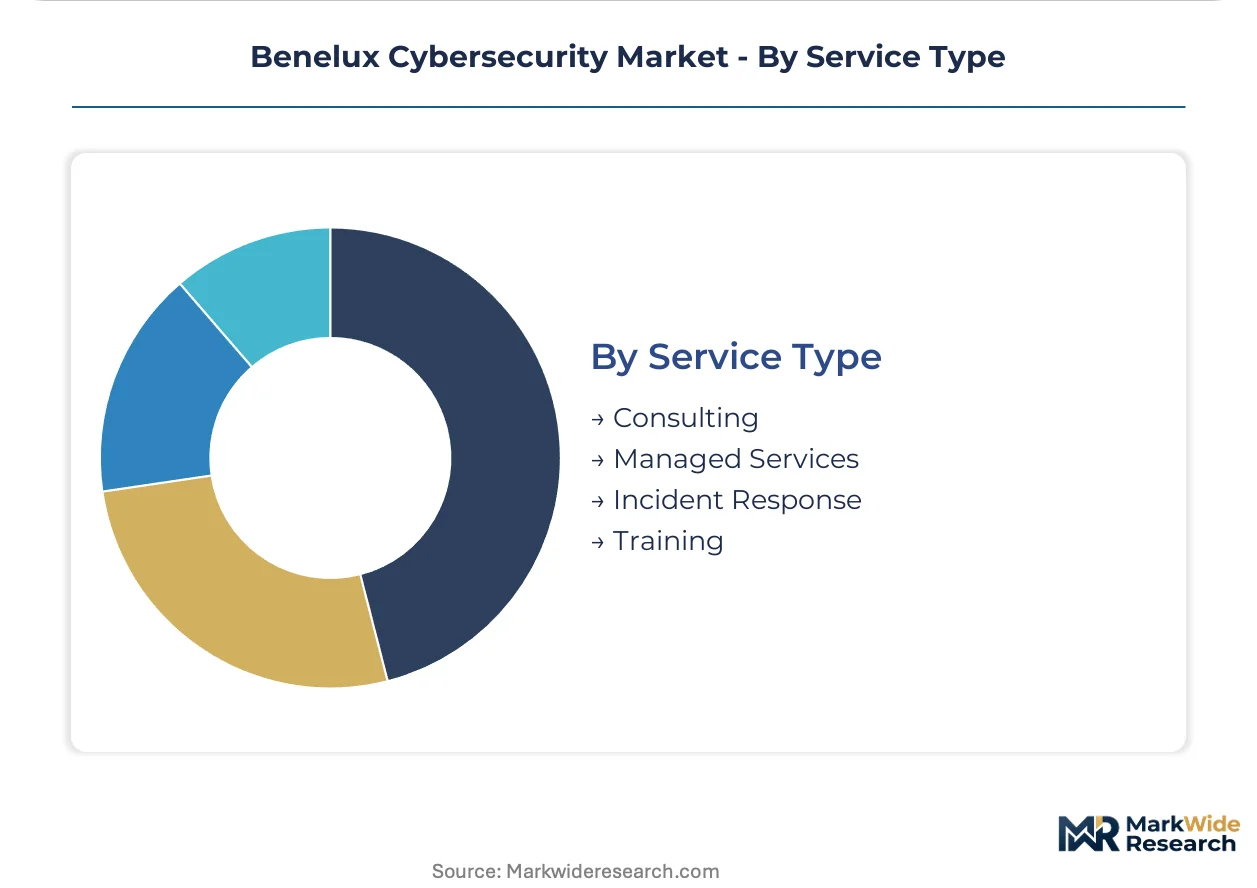
Service Type:
Supply concentration among certified incident response boutiques creates pricing power distinct from commoditized training modules.
- Managed Services:Continuous security operations center operation including detection engineering and threat intelligence integration. Luxembourg's density of regulated entities supports multiple specialized European providers.
- Incident Response:Retainer-based breach containment and forensic investigation. Dutch critical infrastructure operators maintain parallel contracts with domestic and Belgian specialists for cross-border redundancy.
- Consulting:Architecture design, compliance gap assessment, and zero-trust transformation planning. Belgian energy utilities engage consultants for NIS2 implementation roadmapping.
- Training:Workforce certification and phishing simulation programs. Dutch mid-market enterprises purchase through bundled managed service packages rather than standalone.
Recurring revenue concentrates in Managed Services; margin expansion is climbing the fastest for Incident Response as retainer pricing resets post-breach publicity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Amsterdam's data center corridor concentrates the region's densest cybersecurity procurement activity, with Dutch cloud infrastructure providers capturing disproportionate enterprise demand as organizations abandon legacy on-premises architectures.
Netherlands
Dutch financial services firms in Amsterdam and Rotterdam drive cloud-native security spending under DORA compliance pressure. The Authority for Digital Infrastructure enforces NIS2 transposition deadlines that compress procurement cycles. Rotterdam's port operators and chemical manufacturers prefer hybrid deployment models to isolate SCADA systems while bursting analytics to cloud infrastructure.
Belgium
Belgian energy utilities and transport operators face overlapping CCB incident reporting mandates for critical infrastructure protection. The Centre for Cyber Security Belgium mandates sector-specific disclosure timelines that diverge from Dutch and Luxembourg standards. Brussels hosts federal ministries prioritizing on-premises encryption for sovereign data requirements.
Luxembourg
Luxembourg's private banks and wealth management offices under CSSF supervision favor managed security services to address analyst shortages. The Commission de Surveillance du Secteur Financier integrates cybersecurity into financial supervision, creating stringent oversight for cross-border BFSI entities. Family offices remain underpenetrated by managed detection and response providers despite regulatory pressure.
United Kingdom
UK-based cybersecurity vendors serve Benelux enterprises through London financial services corridors, supplying incident response and threat intelligence capabilities. The National Cyber Security Centre provides certification frameworks that Benelux regulators partially recognize for vendor qualification. British consultancies anchor zero-trust transformation planning for Belgian energy utilities navigating NIS2 implementation.
Benelux Cybersecurity Market Competitive Environment
The competitive structure tilts toward platform consolidation over point-product specialization. Mid-market Dutch financial services firms compress vendor counts from twelve to three, collapsing procurement cycles and marginalizing standalone antivirus providers. Two strategic archetypes dominate: sovereign European providers leveraging compliance proximity, and global platform vendors competing through unified control planes. M&A activity concentrates on cloud-native security startups, while strategic partnerships proliferate between domestic infrastructure providers and managed service boutiques.
Within the sovereign European tier, Orange Cyberdefense anchors managed security services for regulated Luxembourg banks, while Fox-IT occupies a position in high-assurance threat intelligence for Dutch government and defense clients. Palo Alto Networks exemplifies the platform consolidation archetype, competing through unified control planes that displace fragmented best-of-breed toolchains across Benelux enterprises. These three entities represent the divergence between compliance-proximate European specialists and scale-driven global platform vendors.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Orange Cyberdefense |
| IBM Corporation |
| Dell Technologies Inc. |
| Check Point Software Technologies Ltd. |
| Cisco Systems Inc. |
| Fox-IT |
| Eye Security |
| Fortinet Inc. |
| Others |
Value Chain & Pricing Dynamics
Certification-grade divergence between sovereign-cloud-compliant and standard SaaS offerings splits both pricing power and vendor sourcing strategies across Belgian, Dutch, and Luxembourg procurement desks. DORA-mandated operational resilience requirements push regulated financial entities toward premium-tier managed security services with embedded compliance documentation, while mid-market retailers in Belgium gravitate toward commoditized cloud-based endpoint protection with minimal implementation support.
Pricing Analysis
Value-based pricing anchored to threat-containment outcomes and compliance audit success dominates managed security service contracts across Luxembourg private banks. Three-tier pricing structure across premium, standard, and economy levels separates DORA-ready bundled offerings with 24/7 SOC coverage from self-service cloud tools with automated alerting only. Pricing pressure stems from Dutch cloud-native startups bypassing traditional channel markups through direct digital sales, compressing margins for established distributors. Mid-market Belgian healthcare networks exhibit highest price sensitivity due to centralized procurement and extended replacement cycles.
Supply Chain Analysis
Direct-to-enterprise channels handle hyperscale demand from Amsterdam-based financial services firms, while value-added resellers serve fragmented Belgian mid-market accounts. Software development concentrates in the Netherlands, Israel, and the United States, with threat intelligence feeds drawing from Estonia, the United Kingdom, and domestic Dutch security researchers. Single-source vulnerability in specialized SOC analyst talent pools creates delivery risk for managed service contracts. Distribution runs through certified channel partners required for CSSF and CCB vendor qualification.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical integration into proprietary threat intelligence generation and captive analyst training programs is reshaping competitive positioning, as vendors seek to escape talent scarcity premiums eroding service margins.
For Market Incumbents: Deepen platform consolidation through native XDR unification of endpoint, network, and cloud telemetry to defend against point-product disintermediation. Prioritize sovereign cloud certification under Dutch EOSN and Luxembourg data localization frameworks to maintain pricing power against global SaaS competitors. For New Entrants and Emerging Players: The mid-market pricing gap between Orange Cyberdefense premium retainers and basic antivirus subscriptions creates entry space for automated MDR offerings with AI-augmented threat hunting. Target underpenetrated Luxembourg family offices through CSSF-aligned compliance packaging with transparent per-user pricing. For Investors and Strategic Acquirers: Re-rating potential sits with cloud-native security startups possessing existing NIS2 implementation track records given regulatory deadline compression across the Netherlands. Monitor Dutch Authority for Digital Infrastructure enforcement actions as inflection signal for compliance-driven procurement acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Consolidation | Unifying XDR, SIEM, and SOAR reduces vendor count from twelve to three for Dutch financial services firms. |
| Sovereign Cloud Certification | Dutch EOSN compliance creates first-mover advantage for domestic providers serving government and critical infrastructure. |
| AI-Augmented Threat Hunting | Machine learning inference integration enables predictive breach identification ahead of EU AI Act transparency mandates. |
| Managed Service Expansion | Luxembourg private banks outsource entire SOC functions to address analyst shortages without competing for Amsterdam talent. |
| Cross-Border Certification | Parallel accreditations under CCB, RDI, and CSSF schemes stretch compliance budgets but unlock multi-jurisdiction contracts. |
Study Parameters
Independent corroboration across primary interviews with CISOs at Dutch neobanks, Belgian energy utility security directors, and Luxembourg CSSF compliance officers, combined with secondary validation through NIS2 implementation guidance documents, DORA regulatory technical standards, and SEC filings of listed cybersecurity vendors, underwrites the qualitative findings. Bottom-up segmentation modeling triangulates against top-down market sizing from cloud infrastructure spending disclosures and managed service contract announcements.
Rate-of-change decomposition across deployment model shifts, solution type upgrade cycles, and end-user sector maturity differentials anchors the analytical framework throughout the projection horizon. Segmentation dimensions modeled include solution type, service tier, deployment architecture, organization size, and national regulatory implementation timeline. CAGRs derive from weighted average of historical procurement velocity and policy-mandated deadline effects. Forecast inputs incorporate SCADA modernization constraints for Belgian port operators and cloud migration velocity indices for Dutch financial services.
Inputs from regulatory authority guidance publications and enterprise security budget disclosures were available through the study window; gaps in real-time contract value transparency for private Luxembourg wealth management firms introduce uncertainty bands around BFSI segment sizing. Forecasts reflect documented assumptions regarding NIS2 transposition timing and DORA enforcement intensity. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
DNS Security Market
Cybersecurity
Cloud Network Security Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Germany Cybersecurity Market