
 Europe Cybersecurity Market | 2026-2036
Europe Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Cybersecurity Market Analysis
Mid-market enterprises is reorganizing Europe's cybersecurity procurement, displacing large-firm dominance as managed detection and response services become affordable. Palo Alto Networks leverages cloud-native platform consolidation to capture this expanding buyer tier. Deutsche Telekom Security GmbH anchors German critical infrastructure contracts through sovereign data residency guarantees. Cisco Systems, Inc. competes across hybrid deployment environments where legacy on-premises investments require gradual cloud migration paths.
Europe cybersecurity encompasses hardware, software, and services engineered to protect digital assets through threat prevention, detection, and response protocols operating across network perimeters, endpoints, and cloud workloads. Encryption tools deploy AES-256 and post-quantum cryptographic standards to secure data at rest and in transit against unauthorized extraction. Cloud-based deployment is capturing fastest growth as GDPR-compliant EU sovereign cloud regions expand, while on-premises solutions retain dominance in classified government and defense installations where air-gapped architectures remain mandatory. Identity and Access Management solutions concentrate margin pools due to recurring subscription revenue and integration complexity that raises customer switching costs.
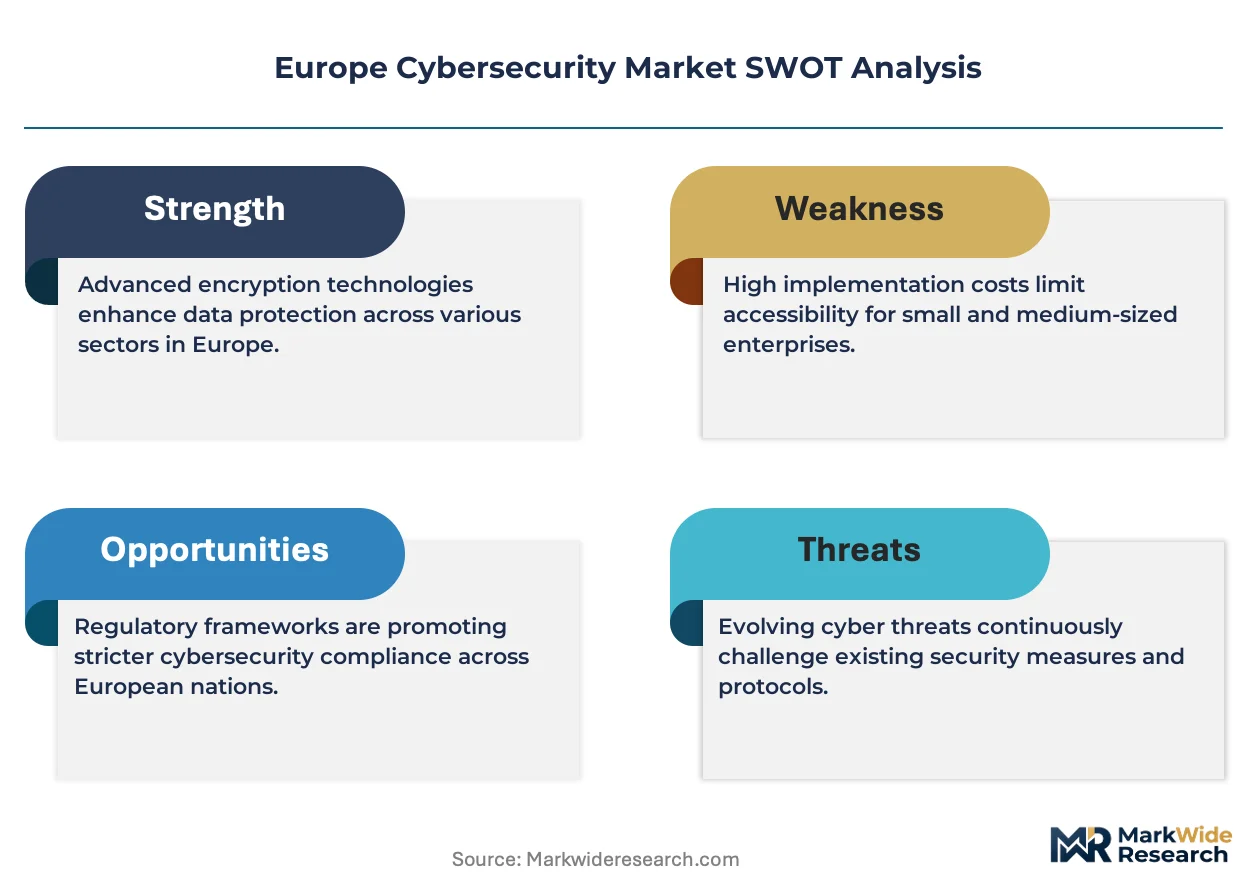
NIS2, GDPR, and the EU Cybersecurity Act collectively mandate baseline security controls, incident notification timelines, and product certification schemes that reshape vendor qualification requirements across member states. EMA and national regulators like Germany's BSI enforce sector-specific standards in healthcare and critical infrastructure that filter market access to certified providers. Stakeholders must monitor ENISA's evolving common criteria certification timelines and member state transposition variances that will fragment compliance obligations before harmonization matures.
Market Dynamics
Zero-trust architecture mandates from the EU NIS2 Directive are compressing procurement cycles and forcing legacy perimeter-defense vendors to requalify under stricter certification timelines. This regulatory pressure is redistributing contract volumes toward sovereign-cloud providers and managed security service operators.
Growth Catalysts
- Critical infrastructure digitization:Energy grid operators and transport authorities across Germany, France, and the United Kingdom are accelerating cybersecurity procurement to meet NIS2 operational resilience mandates.
- GDPR enforcement intensity:National data protection authorities in Ireland and Luxembourg are imposing breach penalties that elevate security spending to board-level priority.
- Post-quantum cryptography transition:ETSI standardization of quantum-resistant algorithms is creating replacement demand for encryption hardware in financial and government installations.
Market Restraints
- Certification backlog concentration:ENISA's Common Criteria evaluation labs face 18-month queues that delay product market entry for non-EU vendors.
- Skilled labor scarcity:The European Cybersecurity Skills Framework documents persistent deficits in SOC analysts and threat intelligence specialists across member states.
- Input cost volatility:Specialized semiconductor components for hardware security modules face supply concentration from Taiwan-based foundries.
Strategic Opportunities
- Eastern European expansion:Poland and Romania exhibit underpenetrated enterprise security markets where EU cohesion funding supports digital infrastructure modernization.
- Healthcare sector convergence:EMA medical device cybersecurity guidance creates certified-service opportunities for endpoint protection vendors serving hospital networks.
- Sovereign cloud regionalization:Gaia-X compliant infrastructure deployments in France and Germany enable data-residency-guaranteed offerings for defense and intelligence clients.
Industry Challenges
- Legacy system integration friction:Industrial control environments in manufacturing and utilities require air-gapped architectures that resist cloud-native security tool deployment.
- Talent pipeline constraints:Universities in Italy and Spain produce insufficient graduates with certified ethical hacking and digital forensics credentials.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Cybersecurity Market |
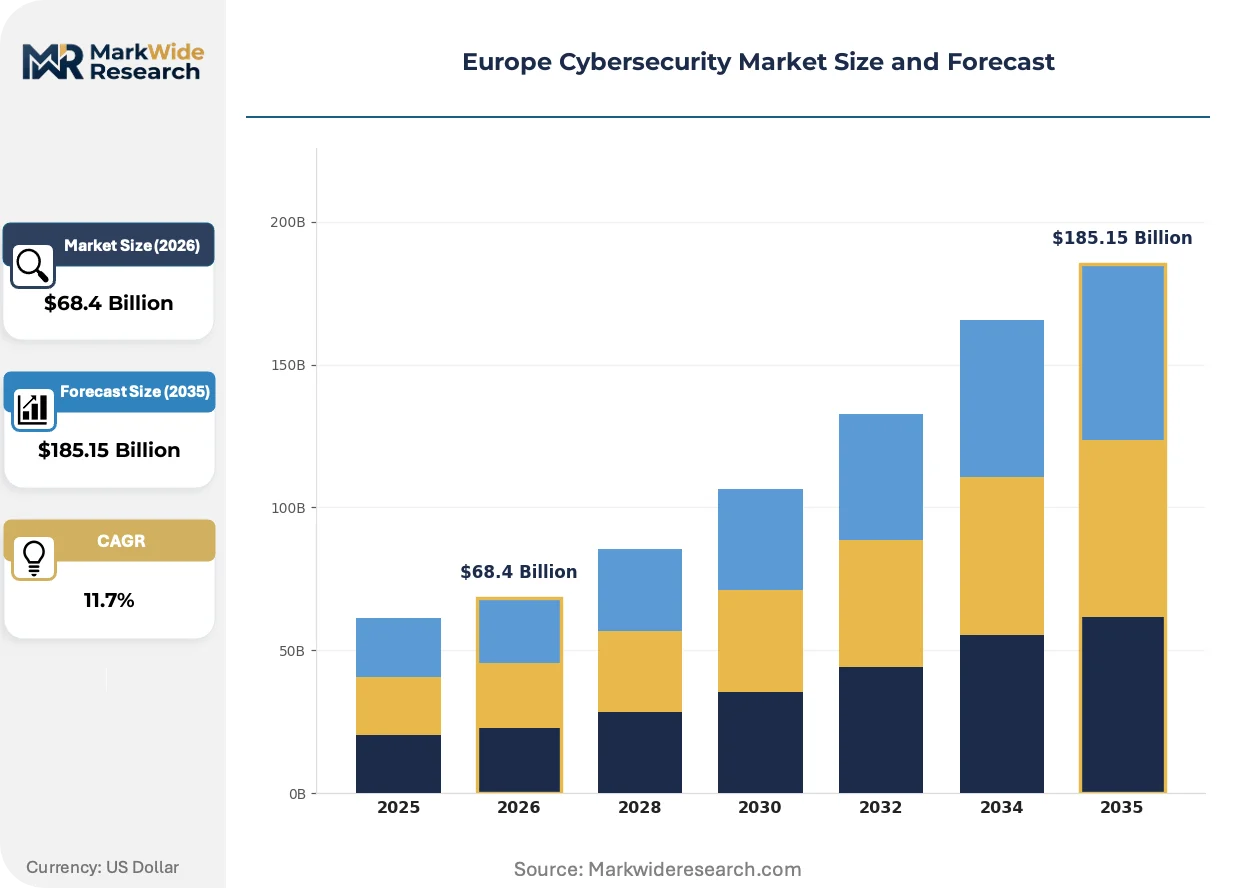
| Market Size in 2026 | $68.4 Billion |
| Market Size in 2035 | $185.15 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Intrusion Detection Systems, Antivirus Software, Encryption Tools Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government, BFSI, Healthcare, Education Solution Type: Identity & Access Management, Incident Response, Risk & Compliance, Threat Intelligence |
| Companies Covered | Dell Technologies Inc., Palo Alto Networks Inc., IBM Corporation, Rohde & Schwarz Cybersecurity GmbH, Deutsche Telekom Security GmbH, Cisco Systems, Inc., Broadcom, Tarlogic Security, Fujitsu Limited, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Cybersecurity Market Emerging Trajectories
Security architecture is fragmenting from monolithic platforms into composable, API-driven services that buyers assemble through modular procurement. This decomposition is redistributing value capture from integrated-suite vendors to specialized point-solution providers.
Extended detection and response (XDR) platforms are decomposing the traditional SIEM market by unifying telemetry across endpoints, networks, and cloud workloads into correlated threat narratives. Mid-market enterprises in the Netherlands and Belgium are adopting these consolidated visibility tools fastest, compressing procurement decisions from multi-year framework agreements to annual subscription renewals.
The EU Cybersecurity Act's certification schemes for ICT products are mandating baseline assurance levels that filter market access. Hardware manufacturers serving defense and critical infrastructure must now obtain Common Criteria or EUCC certifications before national procurement authorities in Germany and France will evaluate bids, extending sales cycles but creating compliance moats for certified incumbents.
Security service procurement is fragmenting from perpetual license models toward consumption-based pricing tied to monitored asset counts or incident response retainer activation. Financial services institutions in London and Frankfurt are piloting these variable-cost structures, transferring operational risk to managed detection and response providers while preserving capital flexibility.
Europe Cybersecurity Market Segmentation
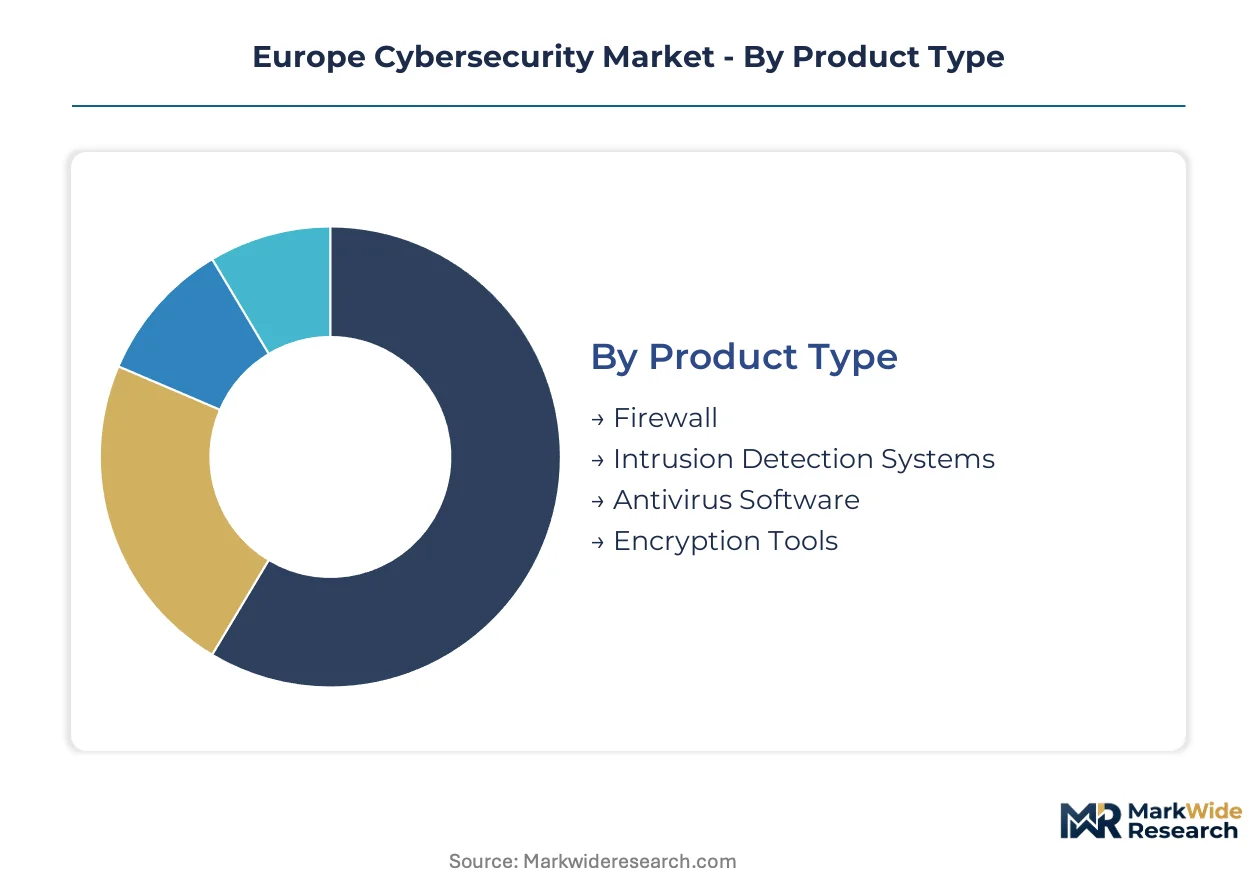
Europe's cybersecurity procurement fragments across four intersecting dimensions that reshape vendor positioning and margin capture. Regulatory mandates from NIS2 and GDPR create divergent compliance burdens across product types and deployment models, while end-user sophistication varies dramatically between German critical infrastructure and Spanish mid-market enterprises.
Product Type:
Firewall and antivirus segments face acute substitution pressure from converged platform vendors bundling these capabilities into broader suites. Specialized point solutions must demonstrate distinct performance advantages to defend procurement volumes against consolidation.
- Firewall:Next-generation firewalls integrate deep packet inspection with application-layer visibility to enforce zero-trust segmentation policies. German energy grid operators and French transport authorities deploy these at network perimeters to satisfy NIS2 operational resilience mandates. Hardware appliances retain dominance in classified defense installations where air-gapped architectures preclude cloud alternatives.
- Intrusion Detection Systems:Network and host-based IDS platforms monitor traffic patterns against signature databases and behavioral baselines to flag anomalous activity. United Kingdom financial institutions in London accelerate deployment to meet Prudential Regulation Authority cyber resilience expectations, though managed detection services increasingly absorb this function.
- Antivirus Software:Endpoint protection platforms deploy heuristic scanning and machine learning classifiers to neutralize malware before execution.
- Encryption Tools:Hardware security modules and software-based key management systems enforce AES-256 and emerging post-quantum standards.
Firewall solutions anchor the volume base while encryption tools gain share at the steepest rate as post-quantum transition deadlines approach.
Deployment Model:
Cost tier differentiation separates capital-intensive on-premises installations from operational-expense cloud subscriptions, with hybrid architectures commanding premium pricing for integration complexity.
- On-Premises:Perpetual-license software and hardware appliances deploy within customer-controlled data centers, satisfying data residency requirements for classified government workloads. German federal agencies and defense contractors mandate these deployments under BSI technical guidelines, though procurement cycles extend to 18-24 months for Common Criteria certification.
- Cloud-Based:SaaS-delivered security services scale consumption through API-integrated dashboards without infrastructure ownership. Netherlands and Belgium mid-market enterprises adopt these fastest, compressing deployment timelines from quarters to weeks while transferring operational burden to specialized providers.
- Hybrid:Split architectures maintain sensitive workloads on-premises while extending policy enforcement to cloud workloads through unified management planes.
- Managed Services:Outsourced security operations centers deliver 24/7 monitoring and incident response through subscription retainers.
On-premises deployments retain the largest installed base while managed services expand most quickly as skills shortages deepen across member states.
End User:
Application-driven segmentation reveals divergent procurement sophistication, with critical infrastructure operators demanding certified solutions while education budgets constrain security investment.
- Government:National and regional public sector bodies procure through framework agreements mandating EUCC or Common Criteria certification. French defense and intelligence services require sovereign-cloud data residency guarantees that filter vendor eligibility to Gaia-X compliant providers.
- BFSI:Banks, insurers, and payment processors face layered supervision from ECB, national central banks, and GDPR authorities that elevate security to board-level governance priority. Frankfurt and London institutions pilot consumption-based pricing models that tie costs to monitored asset volumes.
- Healthcare:Hospital networks and medical device manufacturers navigate EMA cybersecurity guidance for connected equipment.
- Education:Universities and research institutions balance open academic networks against growing ransomware exposure.
BFSI anchors procurement value while healthcare climbs the fastest as medical device connectivity expands attack surfaces.
Solution Type:
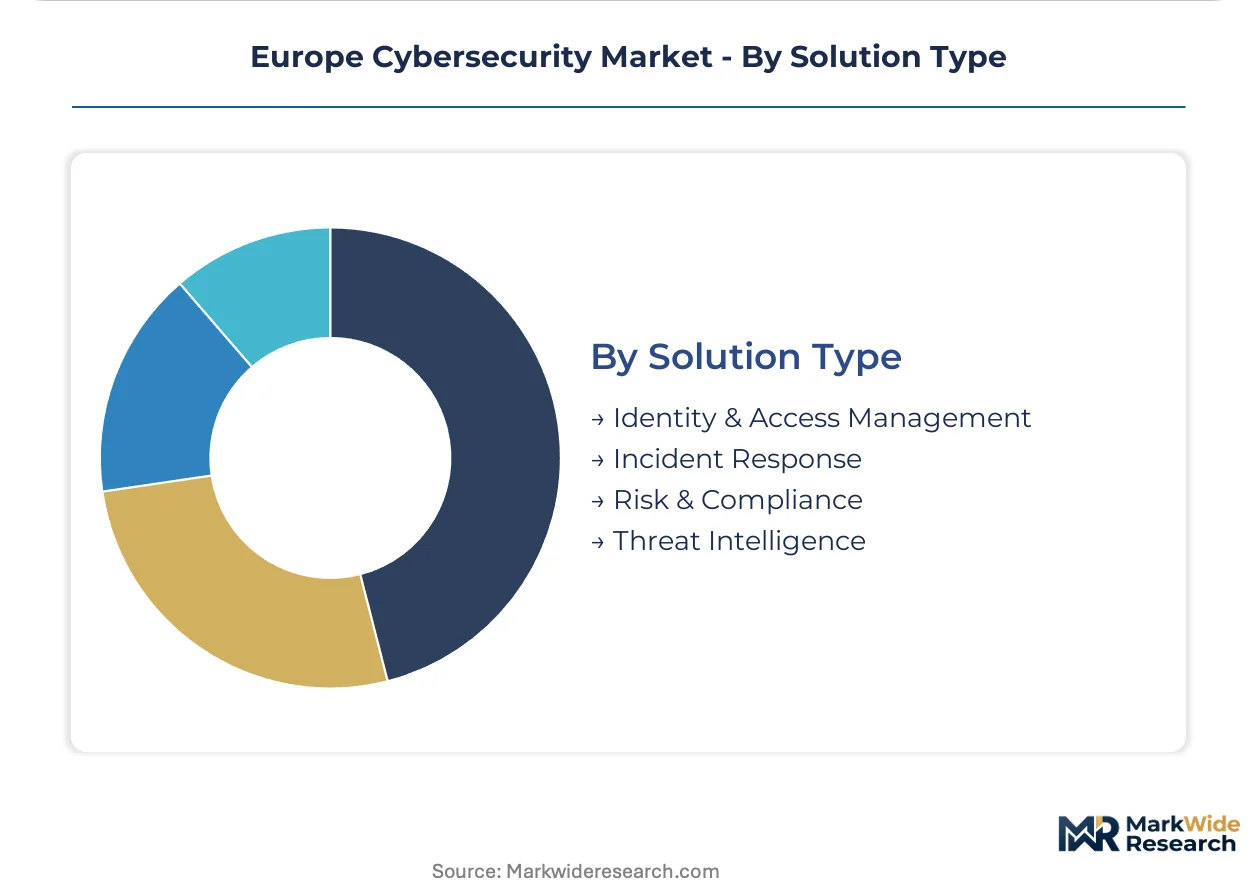
Customer-type segmentation separates integrated-platform buyers from modular procurement patterns, with identity solutions commanding recurring revenue premiums.
- Identity & Access Management:Multi-factor authentication, privileged access management, and identity governance platforms enforce least-privilege principles across hybrid environments. Integration complexity with legacy directories creates switching costs that sustain subscription pricing power.
- Incident Response:Retainer-based services and digital forensics capabilities activate during breach events to contain damage and satisfy regulatory notification timelines.
- Risk & Compliance:Automated assessment tools map control frameworks against NIS2, GDPR, and sector-specific requirements to streamline audit preparation.
- Threat Intelligence:Feed-based services and adversary-tracking platforms deliver contextual indicators to security operations centers.
Identity & Access Management captures the largest revenue pool while incident response demonstrates the steepest expansion trajectory as breach notification penalties intensify.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German cybersecurity vendors export managed detection services to Dutch and Belgian mid-market buyers, establishing a north-south trade corridor that channels continental expertise into underpenetrated Benelux enterprise segments.
Germany
Energy grid operators and automotive manufacturers drive procurement volumes as NIS2 operational resilience deadlines approach. The BSI enforces Common Criteria certification for federal contracts, extending vendor qualification timelines. Munich and Frankfurt clusters concentrate sovereign-cloud deployments where Gaia-X compliance filters provider eligibility.
France
Defense contractors and transport authorities accelerate zero-trust architecture procurement ahead of stricter EU Cybersecurity Act enforcement. ANSM and national regulators mandate sector-specific standards for critical infrastructure operators. The Île-de-France region anchors Gaia-X infrastructure development, with Paris-based providers capturing intelligence-sector contracts through data residency guarantees.
United Kingdom
London financial institutions pilot consumption-based security pricing models tied to monitored asset volumes. The Prudential Regulation Authority elevates cyber resilience to board-level governance priority for banks and insurers. The Thames Valley corridor concentrates managed security service operators serving BFSI clients with hybrid deployment architectures.
Netherlands
Rotterdam port operators and Amsterdam fintech clusters compress procurement cycles through cloud-native security service adoption. National data protection authority enforcement elevates GDPR compliance spending to executive priority. The Randstad metropolitan region leads mid-market enterprise adoption of XDR platforms, displacing traditional SIEM installations.
Poland
EU cohesion funding accelerates digital infrastructure modernization across manufacturing and logistics sectors. The national cyber security agency implements NIS2 transposition measures that reshape vendor qualification requirements. Warsaw and Krakow technology corridors attract managed security service investments serving Eastern European expansion strategies.
Europe Cybersecurity Market Vendor Landscape
Listed leaders compete with private specialists across certification-heavy procurement channels, creating a tiered structure where scale advantages clash with sovereign-cloud agility. The vendor base fragments across integrated-platform providers, point-solution specialists, and telecommunications-anchored security operators. Three archetypes dominate: cloud-native consolidators capturing mid-market subscription growth, infrastructure incumbents defending hybrid deployment accounts, and sovereign-cloud specialists winning classified government contracts. Competitive dynamics center on M&A-driven platform consolidation and strategic partnerships with EU cloud infrastructure providers.
Within the telecommunications-anchored tier, Deutsche Telekom Security GmbH exemplifies sovereign-data-residency positioning for German critical infrastructure contracts. Among cloud-native platform providers, Palo Alto Networks Inc. occupies a scale-driven position targeting mid-market enterprise consolidation. Cisco Systems, Inc. sits within the hybrid-deployment archetype, bridging legacy on-premises investments toward gradual cloud migration paths. These three represent distinct competitive vectors rather than direct substitutes across buyer segments.
| Leading Market Players |
|---|
| Dell Technologies Inc. |
| Palo Alto Networks Inc. |
| IBM Corporation |
| Rohde & Schwarz Cybersecurity GmbH |
| Deutsche Telekom Security GmbH |
| Cisco Systems, Inc. |
| Broadcom |
| Tarlogic Security |
| Fujitsu Limited |
| Others |
Supply Flow & Price Mechanics
Multi-year managed security service retainers lock in both supply access for certified vendors and price visibility for German critical infrastructure operators navigating NIS2 compliance deadlines. These contract structures transfer operational risk to providers while freezing unit economics across the certification backlog period.
Pricing Analysis
Next-generation cloud-native platforms command 40-60% subscription premiums over legacy on-premises equivalents, while post-quantum encryption hardware sits at prototype pricing awaiting ETSI standardization. SaaS-tiered pricing dominates mid-market procurement in the Netherlands and Belgium, with annual subscriptions scaling by monitored endpoint counts. Cost compression in perimeter-defense appliances intensifies as converged platforms absorb firewall and antivirus functions into bundled suites. German federal agencies show least price sensitivity due to sovereign-data-residency mandates, while Spanish universities face acute budget constraints that favor open-source alternatives.
Supply Chain Analysis
Strategic stockpiling of hardware security modules and specialized networking silicon distinguishes defense contractors from commercial buyers facing 18-month certification queues. Taiwan-based foundries anchor semiconductor supply for encryption accelerators, while German and French system integrators dominate final assembly of certified appliances. Single-source vulnerability concentrates in EUV lithography-dependent components, with logistics chokepoints at Rotterdam and Hamburg ports affecting hardware delivery timelines. Distribution runs through national framework agreements in Germany and France, bypassing open market channels for classified workloads.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Market fragmentation creates entry niches as mid-market enterprises displace large-firm dominance through modular, API-driven procurement patterns. Sovereign-cloud specialization and managed service bundling reward focused positioning over platform breadth.
For Market Incumbents: Secure Common Criteria certification moats before ENISA lab capacity expansion dilutes compliance differentiation. Anchor recurring revenue through identity and access management integration complexity that raises customer switching costs. Defend against cloud-native challengers by bridging legacy on-premises investments toward hybrid deployment architectures, preserving installed base relationships during gradual migration timelines. For New Entrants and Emerging Players: Anchor in Polish and Romanian enterprise segments where EU cohesion funding accelerates digital infrastructure modernization and vendor qualification requirements remain less stringent than in Germany or France. Target healthcare endpoint protection as EMA medical device cybersecurity guidance creates certified-service demand from hospital networks. Pursue Gaia-X compliance partnerships as the primary go-to-market angle for defense and intelligence sector access. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among identity and access management specialists with deep legacy directory integration, suggesting superior long-term viability across a 5-10 year holding window. Acquisition targets should display managed detection and response platform capabilities with existing ENISA certification timelines. The signal to watch is NIS2 transposition variance across member states, which will temporarily fragment compliance obligations before harmonization matures.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidates firewall, endpoint, and cloud workload visibility into unified XDR architectures for mid-market buyers. |
| Acquisition of Specialist Firm | Absorbs point-solution providers with ENISA Common Criteria certifications to compress qualification timelines. |
| Strategic Partnership | Gaia-X infrastructure alliances enable data-residency-guaranteed offerings for French defense and German federal clients. |
| Geographic Expansion | Eastern European presence in Poland and Romania captures EU cohesion funding flows for digital infrastructure. |
| Product Launch | Post-quantum encryption hardware aligns with ETSI standardization timelines for financial and government replacement cycles. |
Methodological Framework
Initial hypotheses were tested against primary input from CISOs at German energy grid operators, French transport authorities, Dutch fintech CTOs, and ENISA certification officers, then refined through secondary validation. Primary fieldwork combined structured interviews with security procurement leads at BFSI institutions in London and Frankfurt, alongside technical discussions with sovereign-cloud architects at Gaia-X compliant providers. Secondary sources encompassed ENISA threat landscape reports, national transposition documents for NIS2 implementation, and BSI technical guidelines. Bottom-up endpoint deployment estimates were triangulated against top-down cybersecurity spending forecasts from national statistical offices.
Variance decomposition across product type, deployment model, end user, and solution type segments shaped the analytical framework over the projection horizon. Modeled dimensions included cloud-native versus legacy architectures, mid-market versus enterprise scale, and certified versus uncertified vendor status. CAGRs were derived from segment-level growth rate reconciliation against aggregate market expansion. Industry-specific inputs incorporated ENISA certification queue projections and NIS2 penalty regime severity assumptions.
Material uncertainties — ENISA lab capacity expansion timing, NIS2 enforcement intensity variance across member states, and post-quantum standardization acceleration — sit outside the modeled envelope. Forecasts reflect assumptions about regulatory harmonization trajectories and mid-market SaaS adoption curves. Revision becomes warranted when NIS2 penalty case law crosses thresholds that fundamentally alter board-level security investment prioritization.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Mexico Cybersecurity Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Europe SOC As a Service Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Latin America Cybersecurity Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Network Detection and Response Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Application Programming Interface Security Market