
 AI in Cybersecurity Market | 2026-2036
AI in Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
AI in Cybersecurity Market Analytics
Multi-source procurement of AI security models is restructuring how enterprise buyers evaluate vendor ecosystems. NVIDIA sustains technology leadership through GPU-accelerated inference architectures purpose-built for real-time threat analysis. Palo Alto Networks dominates integrated platform strategies that bundle AI-driven firewall intelligence with cloud-native workload protection. CrowdStrike differentiates via endpoint-centric behavioral models that reduce false-positive rates in large-scale deployments.
AI in cybersecurity encompasses machine learning systems that detect, classify, and autonomously respond to malicious network activity through pattern recognition across telemetry streams exceeding terabyte-scale daily volumes. These systems serve critical infrastructure operators, financial institutions, and government agencies requiring sub-second identification of zero-day exploits and insider threats. Machine learning and deep learning technologies anchor current platform architectures, while natural language processing capabilities are expanding fastest as security teams demand automated parsing of threat intelligence reports and adversary communications. Cloud-based deployment models capture expanding budgets as organizations retire on-premise security operations centers, though hybrid configurations retain strong positioning in regulated industries with data residency requirements.
The EU AI Act classifies certain autonomous cybersecurity systems as high-risk applications, imposing conformity assessments that affect market access for non-European vendors. In the United States, NIST frameworks and SEC cyber disclosure rules shape procurement specifications for publicly traded enterprises. Japan's METI guidelines on AI governance add a third compliance layer for vendors seeking Asia-Pacific expansion. Stakeholders must monitor evolving liability frameworks that assign accountability between AI tool providers and the organizations deploying them.
Market Dynamics
Autonomous threat-response capabilities are compressing detection-to-remediation cycles from hours to milliseconds, forcing security vendors to rebuild architectures around GPU-accelerated inference rather than rule-based detection engines.
Growth Catalysts
- Ransomware Escalation:Critical infrastructure operators in the United States face intensifying extortion campaigns targeting operational technology networks, accelerating procurement of behavioral anomaly systems.
- EU AI Act Conformity Requirements:High-risk classification of autonomous cybersecurity tools creates mandatory third-party assessment demand, expanding addressable market for certified platform providers.
- Natural Language Processing:Security operations centers deploy automated threat intelligence parsing to process adversary communications and dark web chatter at scale previously requiring human analyst teams.
Market Restraints
- GPU Supply Concentration:Inference hardware dependency on Taiwan-based foundry capacity creates vulnerability to geopolitical disruption and allocation constraints.
- Training Data Scarcity:High-quality labeled attack samples remain concentrated within government agencies and large financial institutions, limiting model development for mid-tier vendors.
- NIS2 Directive Compliance Burden:Expanded incident reporting obligations impose operational overhead that slows deployment timelines for European critical infrastructure operators.
Strategic Opportunities
- German Industrial Sector:Manufacturing automation networks remain underpenetrated by AI-native security, presenting first-mover advantage for OT-IT converged platforms.
- Cloud-Native Workload Protection:Containerized application security demands specialized behavioral models that incumbent firewall vendors struggle to adapt.
- Japan METI Governance Alignment:Voluntary AI risk management guidelines create early certification pathway for vendors seeking Asia-Pacific credibility ahead of binding requirements.
Industry Challenges
- Adversarial ML Expertise Gap:Defensive teams lack depth in model poisoning and evasion attack countermeasures, creating vulnerability in deployed systems.
- Legacy SIEM Integration Friction:Enterprises with sunk investment in on-premise correlation engines face complex data pipeline reconfiguration to feed cloud-native AI platforms.
- Cross-Border Data Residency:Hybrid deployment requirements across German, Japanese, and US jurisdictions fragment architecture standardization and increase compliance engineering costs.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | AI in Cybersecurity Market |
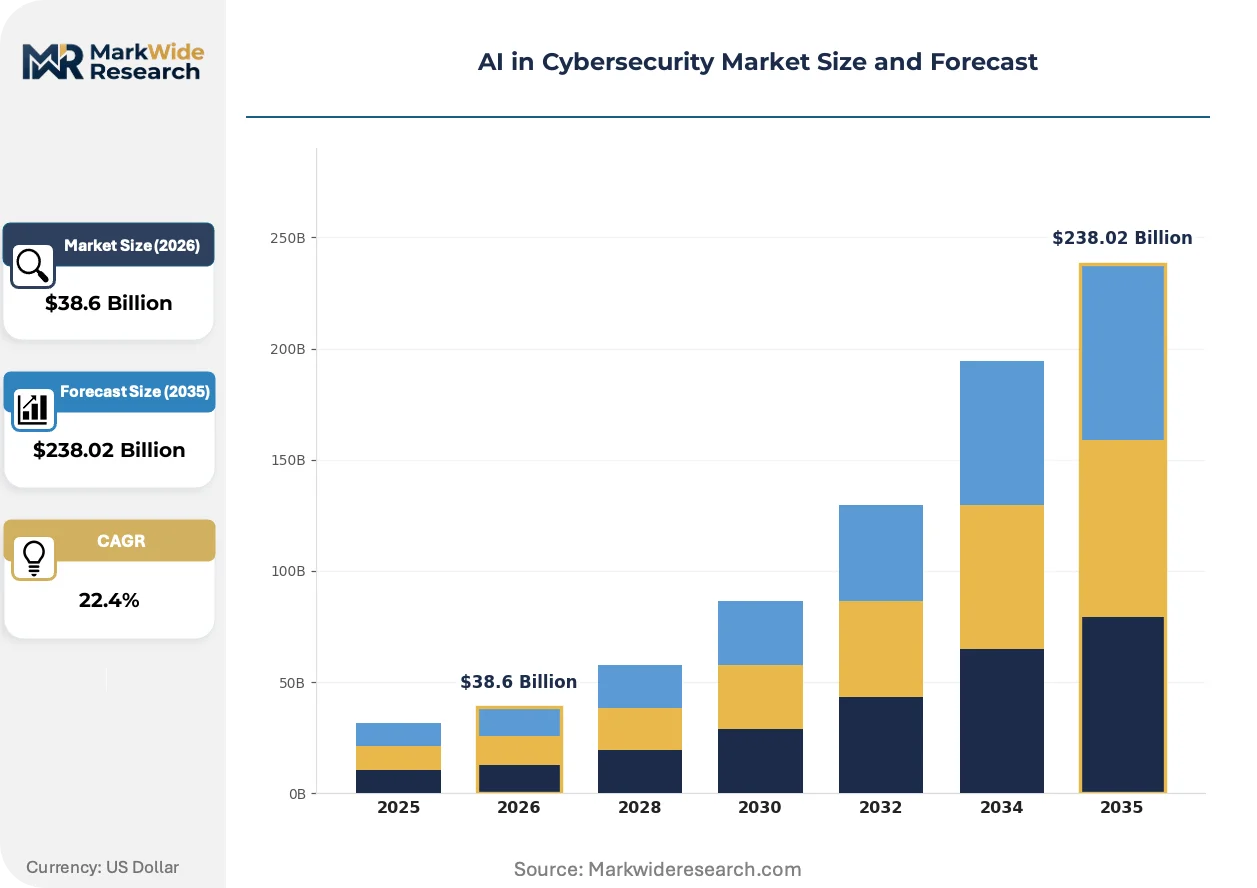
| Market Size in 2026 | $38.6 Billion |
| Market Size in 2035 | $238.02 Billion |
| CAGR (2026 – 2036) | 22.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Machine Learning, Deep Learning, Natural Language Processing, Computer Vision Application: Threat Detection, Incident Response, Vulnerability Management, Security Analytics End User: Financial Services, Healthcare Providers, Government Agencies, Retail Deployment: Cloud-Based, On-Premise, Hybrid, Managed Services |
| Companies Covered | NVIDIA, IBM, Intel, Cisco Systems, Fortinet, Palo Alto Networks, CrowdStrike, Darktrace, Check Point Software Technologies, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
AI in Cybersecurity Market Evolving Landscape
Security architecture convergence is compressing the vendor stack as buyers reject point-solution proliferation, favoring integrated platforms that unify telemetry across endpoint, network, and cloud layers.
Extended detection and response platforms are unifying telemetry ingestion from endpoint agents, network traffic analysis, and cloud workload instrumentation into single correlation pipelines. Large financial institutions in the United States and Germany are consolidating vendor relationships around these architectures, reducing mean-time-to-detect metrics while compressing procurement cycles from multi-year evaluations to single-platform decisions.
The EU AI Act's high-risk system classification is mandating conformity assessments for autonomous response capabilities before European market access. Vendors must now document training data provenance, model performance benchmarks, and human oversight mechanisms, creating compliance differentiation that favors established players with regulatory affairs infrastructure over emerging competitors.
Security operations centers are abandoning annual penetration testing contracts in favor of continuous attack surface validation delivered through software-as-a-service platforms. This consumption shift is most visible among mid-market enterprises in the United States and United Kingdom, where limited internal red team capacity drives outsourcing of adversary simulation to specialized providers with automated campaign orchestration.
AI in Cybersecurity Market Segmentation
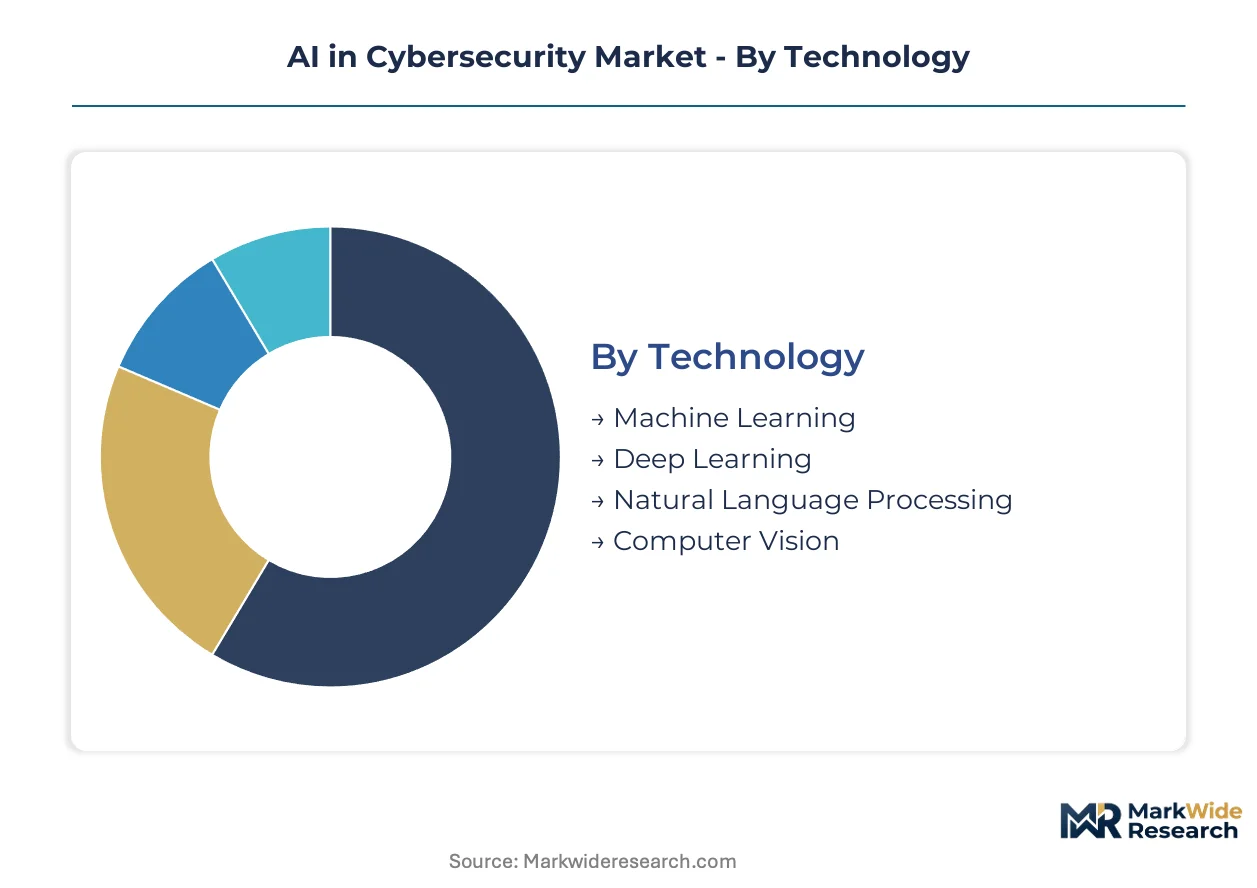
AI cybersecurity platforms fragment across multiple technical and operational dimensions that determine procurement priorities. Buyers evaluate segments based on inference latency requirements, data residency constraints, and integration complexity with legacy security stacks.
Technology:
Capital intensity varies sharply across algorithmic architectures, with foundation model training demanding GPU clusters that strain mid-tier vendor balance sheets.
- Machine Learning:Supervised and unsupervised algorithms power signature-less detection across network traffic and endpoint telemetry. Financial institutions in the United States deploy these systems for real-time transaction fraud identification, though model drift requires continuous retraining pipelines that elevate operational expenditure.
- Deep Learning:Neural network architectures process multi-dimensional attack patterns through automated feature extraction. German automotive manufacturers leverage these capabilities for intrusion detection across connected vehicle fleets, where false-negative tolerance approaches zero.
- Natural Language Processing:Automated parsing of threat intelligence reports and adversary communications accelerates analyst workflows. Security teams in Japan apply these tools to process multilingual dark web chatter at scale.
- Computer Vision:Image-based analysis detects visual indicators of compromise in phishing interfaces and CAPTCHA bypass systems. Retail operators deploy these capabilities to identify fraudulent checkout interfaces.
Machine Learning absorbs the bulk of installed capacity; Natural Language Processing is expanding most quickly.
Application:
Use-case maturity determines pricing power, with automated response commanding premium positioning over passive monitoring functions.
- Threat Detection:Behavioral anomaly systems identify zero-day exploits through deviation from established baselines. Critical infrastructure operators in the United States prioritize these deployments following ransomware campaigns targeting operational technology networks.
- Incident Response:Autonomous containment actions isolate compromised endpoints without human authorization. European banks face EU AI Act conformity assessments before deploying these high-risk capabilities across payment systems.
- Vulnerability Management:Continuous attack surface scanning prioritizes remediation queues through exploitability scoring. Mid-market enterprises favor software-as-a-service delivery to offset internal red team limitations.
- Security Analytics:Cross-telemetry correlation unifies endpoint, network, and cloud data streams into single investigative interfaces. Large institutions consolidate around these platforms to compress mean-time-to-detect metrics.
Threat Detection captures the largest share of current deployment; Incident Response shows the steepest expansion trajectory.
End User:
Regulatory exposure shapes segment profitability, with government and healthcare verticals demanding specialized compliance engineering that smaller vendors cannot support.
- Financial Services:Real-time fraud detection and anti-money laundering compliance drive procurement of sub-second inference systems. SEC cyber disclosure rules mandate board-level accountability for algorithmic security tool performance.
- Healthcare Providers:HIPAA constraints and medical device network protection create hybrid deployment requirements that fragment architecture standardization. Patient data residency rules complicate cloud-native platform adoption.
- Government Agencies:Classified network isolation and supply chain security certifications limit vendor eligibility to domestic providers with cleared personnel infrastructure.
- Retail:Point-of-sale protection and e-commerce fraud prevention concentrate demand among omnichannel operators with high transaction velocity.
Financial Services accounts for the dominant share of enterprise expenditure; Healthcare Providers are climbing the fastest as medical device connectivity expands attack surfaces.
Deployment:
Data sovereignty requirements and latency sensitivity fragment delivery models across regulated and performance-critical environments.
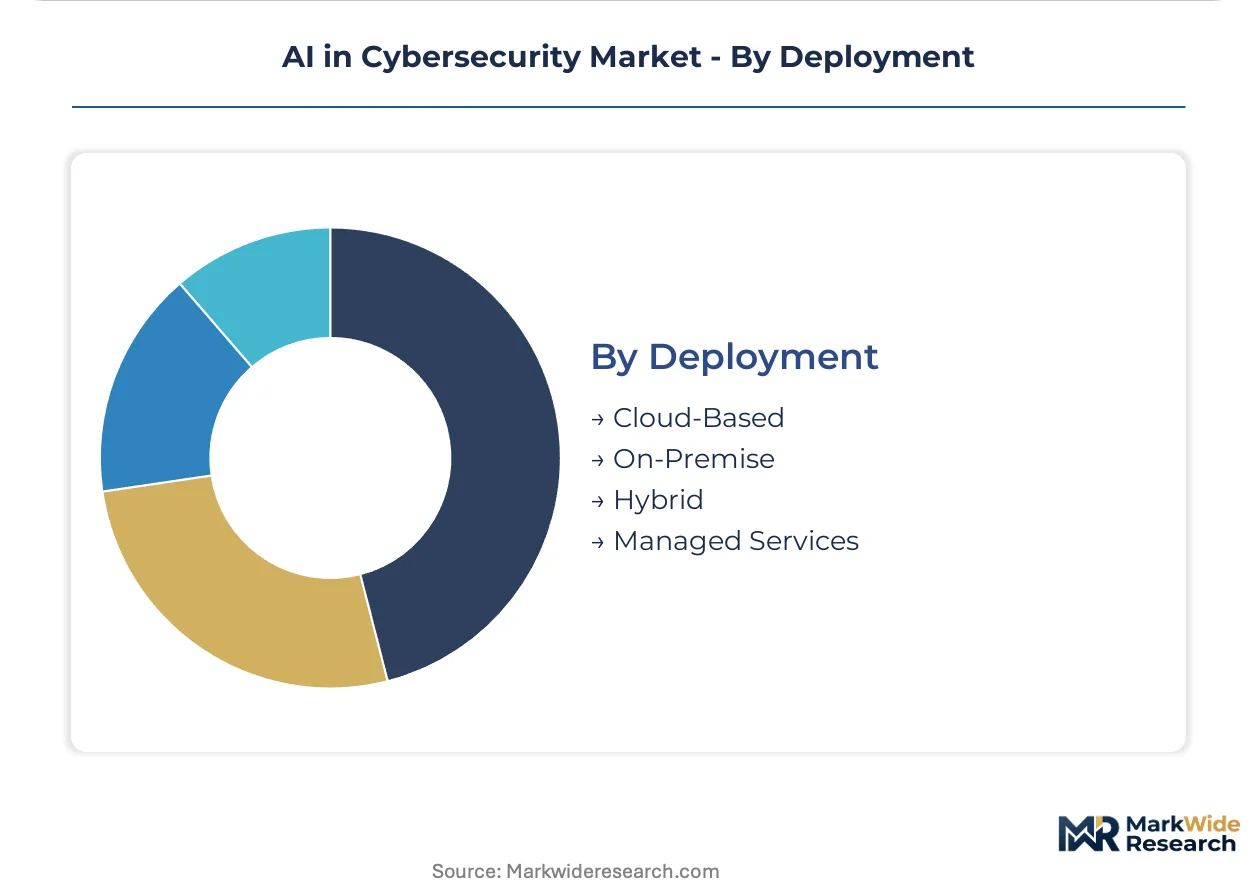
- Cloud-Based:Elastic compute scaling supports terabyte-scale telemetry ingestion without capital infrastructure commitment. United Kingdom mid-market enterprises lead migration away from on-premise security operations centers.
- On-Premise:Air-gapped installations serve classified government networks and financial core banking systems with strict data residency mandates. Hardware refresh cycles extend replacement timelines versus cloud alternatives.
- Hybrid:Split processing routes sensitive correlation to local infrastructure while leveraging cloud scale for global threat intelligence. German manufacturers favor this architecture for operational technology convergence.
- Managed Services:Outsourced security operations deliver continuous monitoring through vendor-staffed analyst teams. Limited internal expertise drives adoption among regional healthcare systems.
Cloud-Based deployments hold the largest installed base; Hybrid configurations are gaining share fastest as regulated industries pursue workload-specific residency controls.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand for AI cybersecurity platforms concentrates in the United States, Germany, Japan, and the United Kingdom, where critical infrastructure operators and financial institutions face intensifying ransomware campaigns and tightening regulatory compliance obligations.
United States
Financial institutions and energy operators drive procurement of autonomous threat-response platforms following SEC cyber disclosure rules. The NIST Cybersecurity Framework shapes procurement specifications for publicly traded enterprises. Silicon Valley clusters host GPU-accelerated inference development centers serving real-time detection requirements.
Germany
Manufacturing automation networks and automotive connected vehicle fleets demand OT-IT converged security solutions. The NIS2 Directive imposes expanded incident reporting obligations on critical infrastructure operators. Bavarian industrial corridors lead deployment of behavioral anomaly systems across production environments.
Japan
Financial services and telecommunications providers prioritize sub-second fraud detection for high-velocity transaction networks. METI guidelines on AI governance create early certification pathways for platform vendors. Tokyo-Osaka metropolitan corridors concentrate security operations center consolidation among large enterprises.
United Kingdom
Mid-market enterprises accelerate migration from on-premise security operations centers to cloud-native platforms. The National Cyber Security Centre frameworks influence procurement specifications across regulated industries. London financial district clusters drive demand for automated threat intelligence parsing at scale.
France
Healthcare providers and defense contractors pursue hybrid deployment models balancing data residency with cloud scalability. ANSM and CNIL guidance shapes algorithmic security tool compliance for patient data protection. Paris-Saclay research clusters advance natural language processing capabilities for multilingual threat analysis.
AI in Cybersecurity Market Competitive Landscape
Platform consolidation dominates the current landscape as enterprise buyers reject point-solution proliferation in favor of unified telemetry architectures. The vendor base stratifies across three tiers: GPU-accelerated infrastructure providers, integrated platform specialists, and endpoint-centric behavioral model developers. Dominant competitive moves include strategic partnerships between hardware and software layers and geographic expansion through regulatory certification acquisition.
Within the infrastructure tier, NVIDIA anchors GPU-accelerated inference architectures purpose-built for real-time threat analysis. Palo Alto Networks and CrowdStrike occupy positions on the integrated platform vector, with the former bundling AI-driven firewall intelligence and the latter differentiating via endpoint-centric behavioral models that reduce false-positive rates in large-scale deployments.
| Leading Market Players |
|---|
| NVIDIA |
| IBM |
| Intel |
| Cisco Systems |
| Fortinet |
| Palo Alto Networks |
| CrowdStrike |
| Darktrace |
| Check Point Software Technologies |
| Others |
Value Network & Pricing Analysis
Adversarial machine learning specialists concentrated in Tel Aviv, Boston, and Singapore command compensation premiums that widen pricing spreads between premium-tier autonomous response platforms and economy-grade signature-based alternatives.
Pricing Analysis
Managed detection and response bundles that include 24/7 analyst oversight, automated remediation playbooks, and compliance documentation command 40-60% premiums over unbundled endpoint agent licenses. Three-tier pricing structure across premium, standard, and economy levels separates fully managed SOC-as-a-service from self-managed cloud consoles and basic on-premise deployments. Pricing pressure stems from GPU compute cost inflation and hyperscaler infrastructure markups that squeeze mid-tier vendor margins. Mid-market enterprises in the United Kingdom exhibit highest price sensitivity due to constrained security budgets, while United States financial institutions demonstrate lowest sensitivity given regulatory penalty exposure.
Supply Chain Analysis
Regional distribution centers in Amsterdam, Singapore, and Dallas maintain hub-and-spoke patterns for threat intelligence feed delivery and model update propagation. Inference hardware fabrication concentrates in Taiwan, South Korea, and the United States, with NVIDIA GPU wafers drawing from TSMC foundry capacity. High-quality labeled attack samples, curated threat intelligence, and specialized ML training frameworks constitute critical input dependencies. Single-source vulnerability in Taiwan-based semiconductor manufacturing creates geopolitical disruption exposure. Distribution runs through direct enterprise sales teams for large accounts and hyperscaler marketplaces for mid-market consumption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The AI cybersecurity market sits in a technology-transition phase as GPU-accelerated inference architectures displace rule-based detection engines that dominated the previous decade.
For Market Incumbents: Anchor platform consolidation strategies around unified telemetry architectures that ingest endpoint, network, and cloud data streams into single correlation pipelines. Invest in EU AI Act conformity assessment infrastructure before binding requirements take effect, as certification delays will cede European market share to prepared competitors. Defend against emerging endpoint-native challengers by deepening integration with legacy SIEM deployments to protect sunk customer investment. For New Entrants and Emerging Players: Begin with German manufacturing automation networks and Japanese connected vehicle fleets where OT-IT converged security remains underpenetrated by established vendors. Target mid-market enterprises in the United Kingdom seeking cloud-native alternatives to on-premise security operations centers. Pursue managed services delivery models that offset internal expertise gaps through vendor-staffed analyst teams. For Investors and Strategic Acquirers: The window for entry favors specialized adversarial ML research teams with demonstrated countermeasure development capabilities against model poisoning and evasion attacks. Long-term viability hinges on regulatory certification moats rather than feature velocity alone. Watch for EU AI Act enforcement patterns as the inflection signal separating compliant platform providers from market-excluded competitors.| Strategic Initiative | Industry Significance |
|---|---|
| GPU-Accelerated Inference Architecture | NVIDIA partnerships enable sub-millisecond threat detection for real-time operational technology networks. |
| EU AI Act Conformity Certification | Third-party assessment documentation unlocks European critical infrastructure procurement pipelines. |
| Managed Detection and Response Bundle | 24/7 analyst coverage addresses talent scarcity among United Kingdom mid-market enterprises. |
| OT-IT Converged Platform Launch | Bavarian industrial corridors demand behavioral anomaly systems across production environments. |
| Natural Language Processing Expansion | Automated threat intelligence parsing reduces analyst workload at London financial district security operations centers. |
Research Methodology
Document review covered regulatory filings from the SEC and EU AI Act implementation guidance, complemented by interviews with chief information security officers, security operations center directors, threat intelligence analysts, and enterprise procurement managers at financial institutions and critical infrastructure operators. Secondary validation drew from NIST framework documentation, ENISA threat landscape reports, vendor SEC 10-K disclosures, and hyperscaler infrastructure investment announcements. Bottom-up deployment estimates across technology segments were triangulated against top-down market sizing from capital expenditure patterns.
Cross-referencing historical adoption curves against panel input from security practitioners established the analytical framework across the analysis window. Segmentation modeling incorporated technology type, application use case, end-user vertical, and deployment architecture dimensions. CAGRs were derived from inference hardware shipment trajectories, cloud security spending patterns, and regulatory compliance investment cycles.
Underlying measurement precision varies by segment; threat detection and cloud-based deployments carry tighter precision than incident response and hybrid configurations due to disclosed contract values and visible infrastructure commitments. Forecasts reflect documented assumptions around GPU supply continuity, regulatory enforcement timing, and ransomware campaign intensity. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Micro Segmentation Technology Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Mainframe Security Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Digital Immune System Market