
 Threat Intelligence Security Market | 2026-2036
Threat Intelligence Security Market Size, Share, and Industry Trends Forecast 2026-2036
Threat Intelligence Security Market Intelligence
ISO/IEC 27001 certification is rotating as the primary gating standard for vendor qualification in enterprise procurement cycles. Palo Alto Networks leverages its platform consolidation strategy to anchor multi-product deployments across Fortune 500 accounts. CrowdStrike differentiates through native endpoint telemetry integration that sustains recurring revenue intensity. IBM competes via managed security services scale and longstanding government contracting relationships.
Threat intelligence security encompasses the systematic collection, analysis, and dissemination of actionable data about emerging cyber threats, typically processed through machine-readable formats such as STIX/TAXII protocols and integrated into SIEM and SOAR workflows for automated response orchestration. Its primary commercial purpose is compressing the mean time to detect and respond to adversarial campaigns before lateral movement or data exfiltration occurs. Cloud-based deployment leads solution delivery as organizations prioritize elastic scalability and reduced capital overhead, while threat hunting represents the fastest-expanding use case as mature security operations centers shift from reactive alert triage to proactive adversary pursuit. Network security maintains the largest margin pool due to persistent infrastructure refresh cycles and bundled firewall-subscription economics.
The EU AI Act, NIS2 Directive, and GDPR collectively mandate stricter breach disclosure windows and supply-chain security audits across European critical infrastructure operators, directly expanding addressable demand for automated threat intelligence platforms. In the United States, SEC cybersecurity disclosure rules and CISA binding operational directives compel publicly traded entities to demonstrate continuous threat monitoring capabilities. Stakeholders must monitor how regulatory fragmentation between jurisdictions affects platform architecture decisions and cross-border data sharing permissions.
Market Dynamics
Machine-readable threat intelligence formats are compressing vendor switching costs and forcing platform consolidation as enterprises demand unified telemetry across endpoint, network, and cloud surfaces.
Growth Catalysts
- EU NIS2 Directive:Mandatory 24-hour incident reporting windows for critical infrastructure operators across member states are accelerating automated threat intelligence platform procurement.
- Financial services threat hunting:Banks and payment processors are deploying proactive adversary pursuit capabilities to preempt lateral movement before data exfiltration occurs.
- STIX/TAXII protocol standardization:Structured threat information exchange formats are enabling seamless vendor interoperability and reducing integration friction in multi-tool environments.
Market Restraints
- Skilled analyst scarcity:The shortage of professionals trained in indicator of compromise analysis and adversary attribution is inflating implementation timelines and service costs.
- Data sovereignty fragmentation:Cross-border intelligence sharing restrictions between the United States, Germany, and Japan are complicating federated threat platform architectures.
- Legacy SIEM sunk costs:Enterprises with substantial investments in on-premises security information and event management infrastructure face high migration friction to cloud-native alternatives.
Strategic Opportunities
- Operational technology convergence:Industrial control system operators in manufacturing and energy are adopting threat intelligence to bridge IT-OT security gaps as attack surfaces expand.
- Japan sovereign cyber defense:Government-funded initiatives to build domestic threat hunting capabilities are creating localized platform deployment opportunities.
- SOAR workflow automation:Security orchestration, automation, and response integration with threat feeds is enabling tier-1 analyst task elimination and response time compression.
Industry Challenges
- ISO/IEC 27001 certification backlog:Vendor qualification delays in enterprise procurement cycles are extending sales cycles and requiring pre-certified partnership strategies.
- Alert fatigue remediation:Security operations centers struggle to operationalize high-volume threat feeds without contextual prioritization engines and automated enrichment.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Threat Intelligence Security Market |
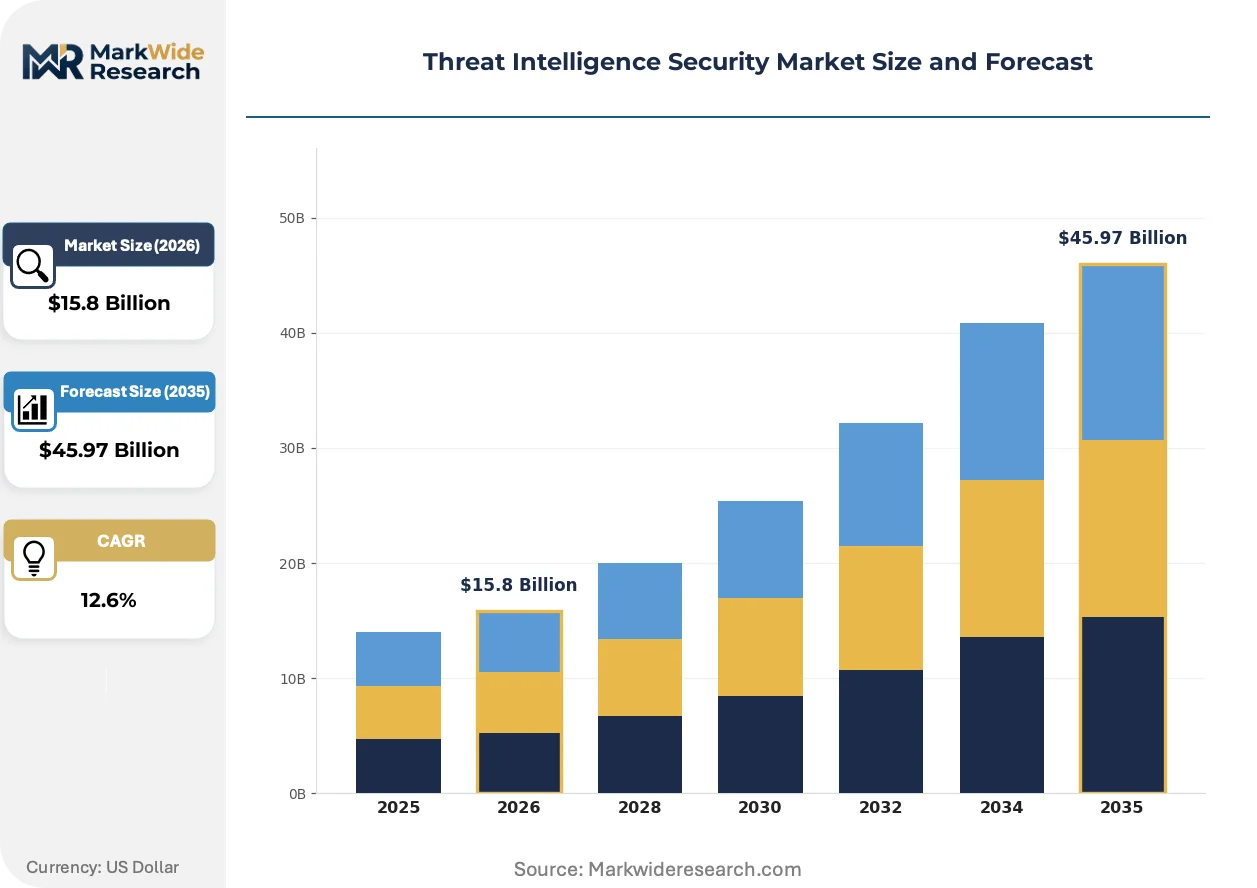
| Market Size in 2026 | $15.8 Billion |
| Market Size in 2035 | $45.97 Billion |
| CAGR (2026 – 2036) | 12.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Managed Services Solution Offering: Network Security, Endpoint Security, Application Security, Data Security, Email Security Use Case: Threat Hunting, Vulnerability Management, Incident Response, Fraud Detection, Risk Assessment End User Industry: BFSI Institutions, Government Agencies, Telecommunications, Energy Providers, Education Centers |
| Companies Covered | Palo Alto Networks, Cisco Systems, CrowdStrike, IBM, Check Point Software Technology, Recorded Future, Google, Fortinet, Trend Micro, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Threat Intelligence Security Market Strategic Shifts & Innovations
Artificial intelligence is rewriting threat detection economics by collapsing the labor intensity of indicator correlation and enabling predictive adversary modeling at previously unattainable scale.
Extended detection and response architectures are decomposing the traditional perimeter-centric security model. Mid-market enterprises and managed security service providers are adopting these consolidated platforms to eliminate point-solution sprawl. The structural consequence is decomposing standalone endpoint protection markets as bundled telemetry subscriptions capture budget share.
GDPR breach notification requirements are tightening disclosure windows to 72 hours across European critical infrastructure. This regulatory compression is forcing operators to deploy real-time threat intelligence ingestion pipelines. Energy and telecommunications sectors in Germany and France are responding by prioritizing automated indicator dissemination over manual analyst workflows.
Security procurement patterns are rotating toward platform consolidation mandates. Fortune 500 chief information security officers are collapsing vendor rosters to reduce integration complexity and improve mean time to respond metrics. This concentration is most visible in United States financial services, where multi-year enterprise licensing agreements now predominate over best-of-breed point solutions.
Threat Intelligence Security Market Segmentation
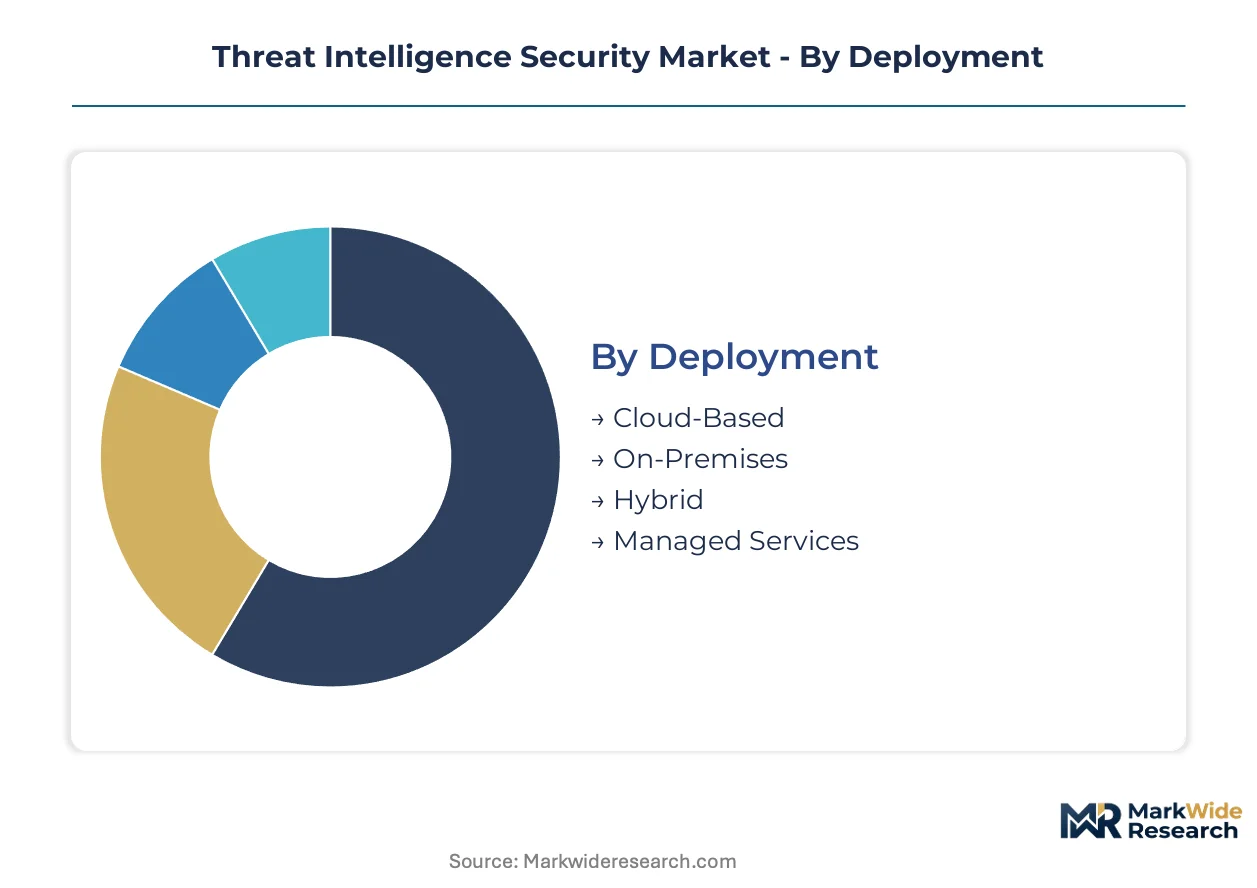
Threat intelligence security procurement patterns diverge sharply across deployment architectures and operational use cases. Enterprise buyers select segments based on regulatory exposure, legacy infrastructure burden, and analyst workforce maturity rather than feature parity alone.
Deployment:
Substitution pressure concentrates heaviest in on-premises infrastructure as cloud-native platforms absorb capital-constrained buyers and managed services capture skill-scarce organizations.
- Cloud-Based:Elastic compute architectures enable real-time threat feed ingestion without capital expenditure commitment. United States financial services institutions dominate procurement as SEC disclosure rules compress detection timeline requirements.
- Managed Services:Third-party security operations centers assume indicator analysis and alert triage burdens. German critical infrastructure operators under NIS2 Directive pressure are expanding managed detection contracts to satisfy mandatory reporting windows.
- Hybrid:Split architectures preserve sensitive data on-premises while leveraging cloud analytics for non-critical workloads.
- On-Premises:Air-gapped deployments persist in defense and intelligence agency environments with data sovereignty mandates.
Cloud-based retains volume leadership; managed services holds the steepest expansion curve.
Solution Offering:
Cost tier stratification separates bundled platform economics from standalone point solutions as procurement mandates consolidate vendor relationships.
- Network Security:Firewall-integrated threat feeds dominate infrastructure refresh cycles with recurring subscription revenue models. Palo Alto Networks and Fortinet bundle intelligence layers into hardware refresh negotiations across Fortune 500 accounts.
- Endpoint Security:Native telemetry integration enables behavioral indicator correlation at the device level. CrowdStrike's platform consolidation strategy captures budget from displaced antivirus vendors through unified agent deployment.
- Application Security:Runtime protection for cloud-native workloads addresses API-layer attack vectors.
- Data Security:Data loss prevention integration with threat intelligence tags exfiltration attempts with adversary attribution context.
- Email Security:Phishing indicator feeds protect the primary initial access vector for enterprise ransomware campaigns.
Network security commands the largest margin pool; endpoint security is climbing the fastest as XDR architectures displace standalone protection.
Use Case:
Application maturity separates reactive compliance-driven deployments from proactive adversary pursuit capabilities in security operations center evolution.
- Threat Hunting:Proactive adversary pursuit shifts security teams from alert response to hypothesis-driven investigation. Japanese government-funded sovereign cyber defense initiatives are expanding domestic threat hunting platform procurement.
- Incident Response:Automated playbook execution compresses mean time to contain through SOAR-integrated threat feeds. EU AI Act and NIS2 Directive disclosure windows are forcing European operators to prioritize response automation over manual workflows.
- Vulnerability Management:Threat-informed prioritization ranks patching queues by active exploitation probability.
- Fraud Detection:Financial services deploy behavioral indicators to intercept payment fraud before transaction settlement.
- Risk Assessment:Adversary capability mapping informs board-level cyber risk quantification.
Incident response retains volume leadership; threat hunting gains share fastest as mature SOCs pivot from reactive to proactive postures.
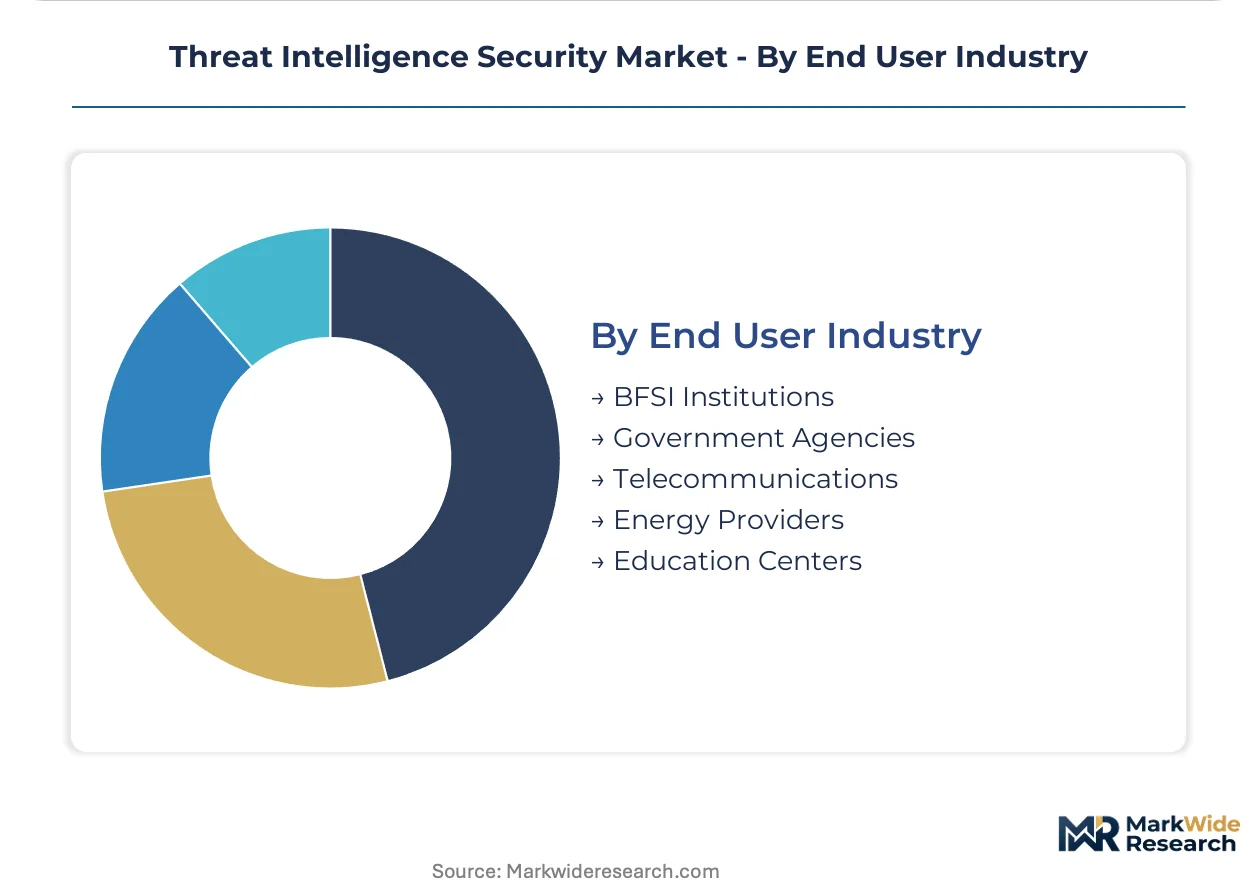
End User Industry:
Customer type concentration reflects regulatory pressure intensity and attack surface exposure across critical infrastructure designation boundaries.
- BFSI Institutions:Banks and payment processors face the strictest supervisory scrutiny and highest ransomware targeting frequency. United States institutions respond to SEC cybersecurity disclosure rules with continuous monitoring platform investments.
- Government Agencies:Sovereign cyber defense mandates drive classified threat feed procurement and domestic platform development. Japan's METI-funded initiatives are accelerating localized threat hunting capability construction.
- Telecommunications:Network infrastructure operators under NIS2 Directive scope deploy real-time indicator dissemination for subscriber protection.
- Energy Providers:IT-OT convergence expands attack surfaces for industrial control system targeting.
- Education Centers:Research institutions with sensitive intellectual property attract nation-state espionage campaigns.
BFSI institutions dominate procurement volume; government agencies are expanding most quickly as sovereign cyber defense budgets accelerate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory compression across critical infrastructure sectors is redrawing procurement geography for threat intelligence platforms. Sovereign cyber defense mandates and mandatory disclosure windows are concentrating demand in jurisdictions with the strictest compliance enforcement.
United States
SEC cybersecurity disclosure rules and CISA binding operational directives compel publicly traded entities to demonstrate continuous threat monitoring capabilities. Financial services institutions in New York and Chicago dominate enterprise platform procurement as ransomware targeting intensifies against payment processors.
Germany
NIS2 Directive implementation imposes 24-hour incident reporting windows on critical infrastructure operators. Energy and telecommunications providers in North Rhine-Westphalia are prioritizing automated indicator dissemination pipelines to satisfy compressed disclosure timelines.
Japan
METI-funded sovereign cyber defense initiatives are accelerating domestic threat hunting capability construction. Government agencies in Tokyo and Osaka are expanding localized platform deployment to reduce dependence on foreign intelligence feeds.
United Kingdom
NCSC guidance on supply chain security audits is tightening vendor qualification requirements for critical national infrastructure operators. Financial services clusters in London and Edinburgh are consolidating vendor relationships under platform-centric procurement mandates.
France
ANSSI certification requirements for critical infrastructure operators are extending sales cycles for uncertified vendors. Energy providers in Île-de-France and Provence-Alpes-Côte d'Azur are deploying real-time threat intelligence ingestion to meet GDPR breach notification windows.
Threat Intelligence Security Market Key Industry Players
Player mix skews toward platform consolidators with bundled telemetry capabilities. The vendor base separates into three distinct tiers: network security incumbents with firewall-integrated intelligence layers, endpoint-native specialists with unified agent architectures, and managed security services operators with government contracting scale. Dominant competitive moves include multi-year enterprise licensing agreements that displace point solutions, and strategic partnerships with cloud hyperscalers to embed threat feeds into infrastructure-as-a-service workflows.
Within the platform consolidation tier, Palo Alto Networks and CrowdStrike exemplify divergent anchoring strategies. Palo Alto occupies a position tied to hardware refresh cycles and bundled firewall-subscription economics across Fortune 500 accounts. CrowdStrike represents the endpoint-native archetype, capturing budget from displaced antivirus vendors through unified agent deployment. IBM sits within the managed services tier, leveraging longstanding government contracting relationships and services scale to compete for classified threat feed procurement.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Cisco Systems |
| CrowdStrike |
| IBM |
| Check Point Software Technology |
| Recorded Future |
| Fortinet |
| Trend Micro |
| Others |
Cost & Logistics Intelligence
Platform-scale economies in cloud-native threat intelligence delivery compress unit economics for hyperscaler-backed vendors while elevating price floors for on-premises specialists serving air-gapped defense contracts. This divergence concentrates supply-side power among multi-product consolidators and fragments procurement leverage for buyers in skill-constrained segments.
Pricing Analysis
Certification level (ISO/IEC 27001, SOC 2 Type II, FedRAMP) creates the primary spread between premium-tier platform subscriptions and commodity threat feed licenses. Three-tier pricing structure across premium, standard, and economy levels dominates, with premium tiers bundling managed detection and response services. Cost compression in standard tiers is intensifying because hyperscaler marketplace distribution reduces customer acquisition overhead. Managed security service providers exhibit highest price sensitivity due to margin pressure from labor-intensive analyst workflows.
Supply Chain Analysis
Semiconductor fabrication chokepoints in Taiwan and South Korea constrain hardware-dependent network security appliance availability for on-premises deployments. Threat intelligence platform supply draws from specialized GPU clusters for AI model training, proprietary sensor networks for indicator collection, and certified security operations centers for analyst enrichment. Single-source vulnerability in cloud infrastructure regions complicates data sovereignty compliance for European and Japanese operators. Distribution runs through direct enterprise sales teams for Fortune 500 accounts and hyperscaler marketplaces for mid-market cloud-native buyers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
EU NIS2 Directive disclosure windows and SEC cybersecurity rules are compressing procurement timelines, creating a high-growth disruption as regulatory enforcement accelerates platform replacement cycles.
For Market Incumbents: Consolidate multi-product telemetry architectures to capture displaced point-solution budgets as Fortune 500 CISOs mandate vendor roster reduction. Deepen backward integration into proprietary indicator collection networks to differentiate from commodity open-source feeds. Anchor platform stickiness through SOAR workflow embedding that raises switching costs for existing accounts.
For New Entrants and Emerging Players: Anchor in operational technology security gaps where industrial control system operators lack mature threat hunting capabilities. Target energy sector deployments in Germany and Japan where sovereign cyber defense mandates create localized procurement preferences. Pursue channel partnerships with managed security service providers to bypass direct sales capacity constraints.
For Investors and Strategic Acquirers: Mid-cycle technology positioning favors endpoint-native platforms with unified agent architectures over hardware-tethered network security incumbents. Long-term viability rests on recurring revenue intensity and API ecosystem breadth rather than one-time licensing. Monitor STIX/TAXII protocol adoption rates as inflection indicator for interoperability-driven consolidation pressure.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and cloud telemetry into single-pane workflows for SOC efficiency. |
| Strategic Partnership | Embeds threat feeds into hyperscaler infrastructure-as-a-service offerings for elastic scale. |
| Acquisition of Specialist Firm | Adds operational technology security expertise to bridge IT-OT intelligence gaps. |
| Geographic Expansion | Establishes data-resident operations in Japan and Germany to satisfy sovereign defense mandates. |
| Product Launch | Introduces AI-powered adversary prediction modules to compress mean time to detect metrics. |
Research Approach
Findings reconcile primary fieldwork against secondary review of SEC cybersecurity disclosures, CISA binding operational directives, EU NIS2 implementation guidance, and hyperscaler marketplace transaction data. Primary sources include chief information security officers, security operations center directors, threat intelligence analysts, managed security service provider executives, and regulatory compliance officers across financial services, energy, and government sectors. Bottom-up demand modeling triangulates against top-down regulatory mandate sizing.
Segmentation dimensions modeled span deployment architecture, solution offering category, operational use case maturity, and end-user industry regulatory exposure. CAGRs derive from elasticity-adjusted adoption curves across the projection horizon, incorporating analyst workforce scarcity constraints and platform consolidation procurement patterns. Forecast inputs include NIS2 Directive enforcement timelines and sovereign cyber defense budget allocations.
Decision-makers should treat outputs as directional under assumptions of sustained regulatory enforcement and stable cloud infrastructure economics; material deviation would warrant model refresh. Practitioners should keep alternative scenarios live as cross-border data sharing restrictions and legacy SIEM migration friction evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia Pacific Digital Forensics Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Germany Endpoint Detection and Response Market
Cybersecurity
Cryptojacking Solution Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
Oman Cybersecurity Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Portugal Cybersecurity Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
Africa Cybersecurity Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Web Filtering Market